Skip to content

What is hybrid cloud security?

As many organizations move to hybrid cloud infrastructures, hybrid cloud security has become a hot topic. This transition allows businesses to leverage the benefits of both cloud environments and on-premises setups combining the best of both worlds.

Yet, as hybrid cloud adoption grows, we’re entering uncharted territory regarding security. The hybrid nature of these environments introduces previously unseen security challenges that must be addressed. At the same time, cyber threats are becoming more sophisticated, and attackers are targeting weak links in the system.

Hybrid cloud security definition

Hybrid cloud security refers to measures, practices, and technologies that protect data and applications in an infrastructure combining on-premises and public cloud services. Its main function is to ensure resource confidentiality, integrity, and availability across both setups.

Key takeaways

  • Hybrid cloud setups pose security challenges because they combine the security concerns of both on-premises and cloud services.

  • Data protection is more complex in hybrid setups as data is scattered across multiple environments.

  • Cloud migration is challenging as organizations must ensure data security during the transition.

  • Hybrid cloud security risks can be addressed with unified access management.

  • Best practices for data encryption, security automation, regular security audits, and employee cybersecurity training are recommended best practices.

  • In a hybrid approach, network segmentation, firewalls, Intrusion Detection Systems (IDS), secure APIs, and MFA are essential for security.

  • Hybrid setups offer enhanced flexibility and various deployment options.

Let’s dig deeper into the most pressing hybrid cloud security concerns and their potential solutions.

Hybrid cloud security issues and challenges

While it’s true that hybrid cloud setups can be a lifesaver for businesses and bring many benefits, there’s the flipside. Hybrid cloud setups make cybersecurity more difficult by combining the challenges of on-premises infrastructure and the cloud counterpart. That way, network administrators need to secure not only each component of the hybrid model but also ensure that the system is safe at the junctions from on-premise to the cloud.

As sensitive data is distributed across multiple cloud providers and joined with on-premise infrastructure, it must be protected at all stages of transfers. Access management also becomes more complex as organizations must consistently apply security policies across all environments. It isn’t easy to achieve — legacy on-premise setups may not support sophisticated identity verification methods or can efficiently encrypt stored data.

Another challenge is endpoint security. In hybrid computing, endpoints, mobile devices and remote machines have direct access to the cloud environments. This expands the attack surface as hackers can target cloud networks directly and use weak endpoint security as an entry point into the company’s network. To ward these threats off, organizations must also consider what security policies should be applied to endpoint security.

Cloud migration itself is also a serious security challenge. Organizations must map out appropriate data protection mechanisms when moving applications and data between cloud providers or on-premises and cloud environments. If they aren’t implemented consistently, this can result in data breaches or losses.

Hybrid cloud security best practices

To address the security risks and challenges of hybrid cloud strategy effectively, there are some recommended strategies and measures that can be taken.

Unified access management

A unified access management system allows users to enjoy a seamless and consistent experience when accessing resources and applications across different cloud environments. They need to authenticate once, and the system handles the rest, providing single sign-on capabilities.

For network administrators, this provides a centralized approach to managing user identities, access rights, and authentication across various cloud environments and on-premises systems. It enables consistent enforcement of security policies, such as multifactor authentication and access controls, reducing the risk of unauthorized access and data breaches.

Data encryption

Encryption ensures that data transmitted or stored in the hybrid cloud remains secure and protected from unauthorized access. Plus, it provides an additional layer of security, safeguarding sensitive information in case of a data breach or data leak. That way, hackers could only retrieve encrypted data nodes, which would still be inaccessible, and, therefore, useless to them.

Many industries have strict data protection regulations, so sensitive information at rest and in transit must be encrypted to comply. So not only does this help to avoid penalties or legal fines, but it strongly improves an organization’s cybersecurity position.

Security automation

A hybrid cloud model often involves multiple environments and platforms, leading to inconsistencies in security controls. With security automation, some of these problems can be addressed and help to establish consistent security policies and controls across the infrastructure.

Security automation can also help to detect and respond to security threats in real-time. It enables businesses to continuously monitor their cloud and on-premise environments, analyze logs and identify potential security incidents promptly. This helps shorten the time span between the threat’s detection and response.

Periodic security audits

Regular security audits can help identify vulnerabilities and weaknesses in the hybrid cloud infrastructure. This includes assessing potential risks associated with the on-premises and cloud components, such as misconfigurations, insecure APIs, outdated software, or inadequate access controls. Left unresolved, these issues can become a loophole for an attacker to gain entry into your network.

This approach helps to mitigate potential risks in a hybrid cloud environment and implement appropriate risk mitigation strategies. This can involve assessing data integrity, backup and recovery processes, disaster recovery plans, and incident response procedures.

Employee training

Cybersecurity training raises employee awareness about potential risks and threats associated with the hybrid cloud environment. Your staff becomes more knowledgeable about the best practices for data protection, recognizing phishing attempts, securing access credentials and handling sensitive information. It’s also more likely that educated staff is more likely to follow security protocols, reducing the risk of human error-related breaches.

In the long run, investing in cybersecurity training can result in cost savings. This is because financial repercussions associated with data loss, reputational damage, legal liabilities, and regulatory penalties can be avoided.

Hybrid cloud security architecture

Hybrid cloud systems security begins with physical access to servers that contain proprietary code, databases, storage files, records, archives, and more. Therefore, hybrid cloud architecture entails globally distributed hardware across multiple data centers. For network administrators, this means that they need to adopt policies to orchestrate access to internal resources securely.

Therefore, the architecture should incorporate the following elements:

Network segmentation

By dividing the network into segments or subnets, organizations can separate different components of their hybrid cloud environment, like production systems, development environments, or sensitive data repositories. This helps to prevent unauthorized access and reduces the potential for lateral movement within the network.

With network segments, a smaller attack surface is left to attackers. Even if some segment is breached, network segmentation prevents them from easily moving laterally to other segments or compromising critical resources. This can help contain the potential breach’s impact, limiting the exposure of sensitive data and critical systems.

Firewalls and Intrusion Detection Systems (IDS)

Firewalls and IDS should be deployed for public and private cloud environments to monitor and block unauthorized access attempts and potential security threats. As a barrier between incoming and outgoing network traffic, firewalls are essential for protecting the on-premises infrastructure and the cloud components from unauthorized access attempts.

Meanwhile, IDS systems monitor network and system activities for signs of malicious behavior or policy violations. They analyze network traffic patterns, log files, and system events to detect potential security incidents. This enables response to cyber threats in real-time, mitigating the risk of data breaches, unauthorized access, or other malicious activities within the hybrid cloud infrastructure.

Secure APIs

APIs act as gateways for accessing and interacting with cloud services and resources. Incorporating security measures like authentication, authorization, and user roles ensures that only authorized users and applications can access hybrid cloud environments. This enforces security policies and prevents unauthorized access.

Hybrid cloud environments involve integrating multiple systems and platforms, both on-premises and in the cloud. Data transmitted between these systems must be encrypted and protected from interception. This also applies to APIs used to connect different cloud services.

Multifactor authentication (MFA)

MFA expands authentication with an extra layer of security to the authentication process by requiring users to provide multiple factors to verify their identity. Typically, these factors include something that the user knows (such as a password), something they have (such as a smartphone or token), or something they are (such as biometric data). By combining these factors, MFA significantly reduces the risk of unauthorized access, even if one factor is compromised.

Passwords are common targets for attackers due to weak security practices, reuse, or data breaches that leak them out in the open. MFA reduces an organization’s reliance on passwords as the sole authentication mechanism, reducing these risks. Even with a compromised password, MFA prevents unauthorized access into the network.

Public vs. private vs. hybrid cloud

Cloud computing can take many shapes; no model’s right for everyone. As such, several different cloud computing types and services have evolved to meet organizations’ rapidly changing technology needs.

There are three different ways to deploy cloud services: on a public cloud, private cloud, or hybrid cloud.

Public cloud

The most prevalent type of cloud computing deployment is known as public cloud. Third-party cloud service providers own and operate servers and storage and deliver these resources over the internet. The cloud provider manages all the hardware, software and supporting infrastructure in this setup. Examples of public cloud include Google Workspace, Amazon Web Services (AWS), and Microsoft Azure.

Multiple organizations or tenants share the same hardware, storage and network devices within a public cloud environment. They’re accessed via a web interface and are commonly used for web-based email, online office applications, storage, testing, and development environments.

Their main benefits include:

  • Lower costs. Public clouds eliminate the need to buy on-house hardware or software. The business is also paying only for the space they’re actually using.

  • No maintenance. The service provider takes care of maintenance, meaning its clients can focus on other areas.

  • Limitless scalability. As resources are available on demand, business operations can be scaled up or down instantly.

  • High reliability. Huge infrastructure acts as a precaution against the chances of failure.

Private cloud

A private cloud is a collection of cloud resources that a single business or organization exclusively uses. It can be located within the organization’s on-site data centre or hosted by a third-party service provider. Regardless of the physical location, the private cloud operates as a private network, with its services and infrastructures dedicated solely to the organization.

The main selling point of a private cloud is the ability to tailor and customize resources to meet specific organizations’ needs. A high level of customization is relevant to government agencies, financial institutions, and other businesses operating under strict requirements or sensitive business operations. By maintaining a private cloud, these entities can exert greater control over their environment regarding hardware and software.

Private cloud advantages:

  • Flexibility. Organizations can customize their cloud environment according to specific business requirements.

  • Greater control. Resources aren’t shared with others, enabling greater control and privacy.

  • Better stability. Private clouds can offer more in terms of scalability compared to on-premises infrastructure.

Hybrid cloud

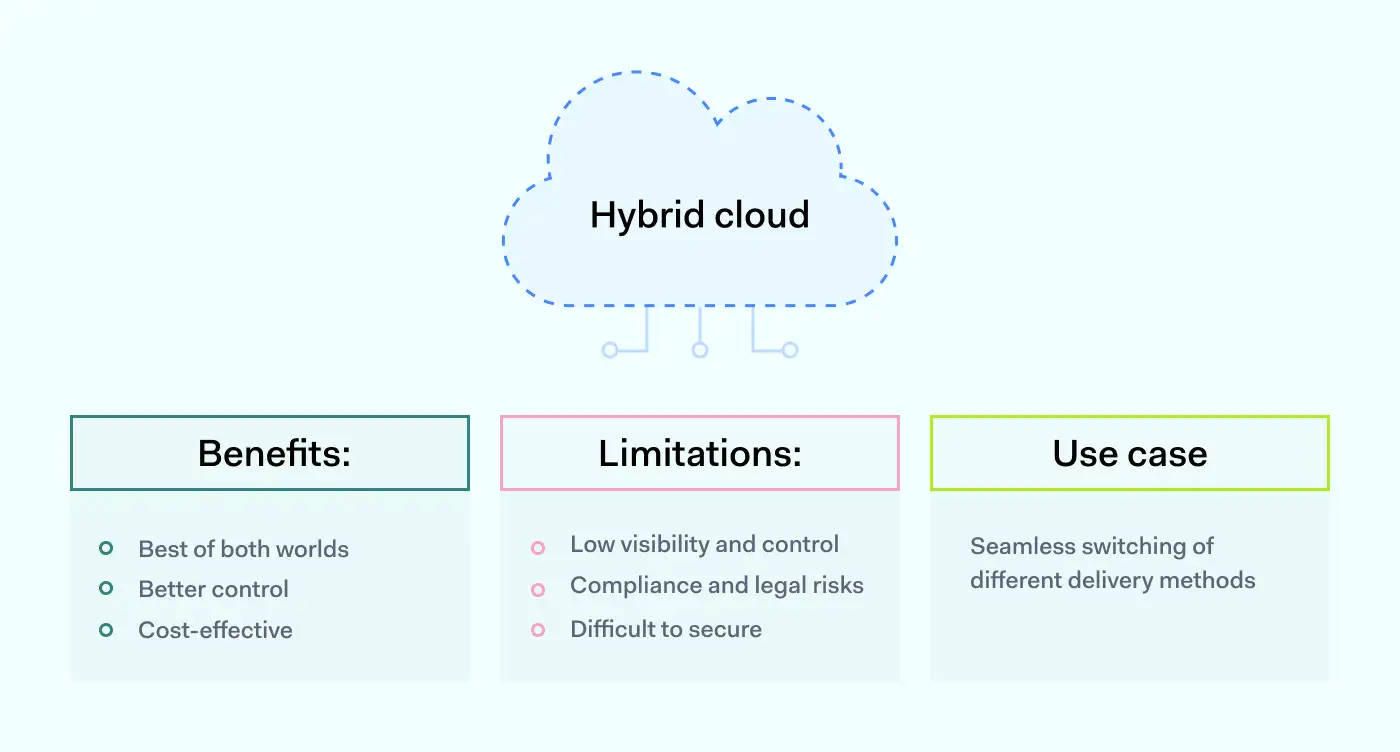
A hybrid cloud platform offers enhanced flexibility and various deployment options. With hybrid cloud computing, businesses can effortlessly expand their on-premises infrastructure to the public cloud when there is a fluctuation in computing and processing demand. This approach allows organizations to handle the excess workload without granting third-party data centers full access to their data.
What-is-hybrid-cloud-security 1400x752

In addition, resource scalability eliminates the need for substantial investments to manage short-term spikes in demand. It addresses situations where businesses must allocate local resources for more sensitive data or applications. Instead of purchasing, programming, and maintaining additional resources and equipment that might remain unused for extended periods, companies only pay for the temporary utilization of resources.

In short, hybrid cloud advantages are these:

  • Control. Your organization can retain a private infrastructure for handling sensitive assets or tasks that demand fast response times.

  • Flexibility. Additional resources from the cloud can be leveraged on demand.

  • Cost-efficiency. Organizations pay for only what they’re using.

  • Simplicity. A hybrid approach allows organizations to gradually transition to a cloud model, migrating workloads over time.

How can NordLayer help?

NordLayer can be a helpful ally when securing hybrid cloud setups. Our solutions include a wide range of features that help to secure remote access and flexibly adapt to ever-changing business work environments.

IP address allow-listing, Site-to-Site tunnels and Smart Remote Access features enable network administrators to allow only NordLayer-using members to access their hybrid cloud resources while blocking everyone else. Single sign-on, multifactor authentication, and biometric authentication ensure that only credible members are allowed into your network perimeter. Centrally implemented security controls will help apply additional security policies consistently across all network environments.

Our suite makes applying best practices to a hybrid work environment easy. Contact our sales team today to learn more about our services and solutions.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Safeguarding digital assets across cloud environments with multi-cloud security

In today’s digital landscape, organizations are increasingly adopting multi-cloud strategies to harness the benefits of multiple cloud service providers. However, with this approach comes the crucial need for robust security measures to protect valuable digital assets across diverse cloud environments.

This article provides readers with a deep understanding of multi-cloud security, shedding light on its importance and exploring the essential measures to ensure comprehensive protection.

What is multi-cloud security?

Multi-cloud security refers to the practices, technologies, and policies employed to secure data, applications, and infrastructure deployed across multiple cloud environments. It involves safeguarding digital assets against various threats and ensuring data confidentiality, integrity, and availability while complying with industry regulations.

Organizations adopt a multiple-cloud approach, utilizing various service providers simultaneously, including public, private, or hybrid clouds in a multi-cloud setup. The flexibility, scalability, and resilience offered by multi-cloud architectures are attractive, but they also introduce unique security challenges that demand specialized security strategies and controls.

A quick check on definitions

☁️ Multi-cloud security refers to the protection and safeguarding of data, applications, and infrastructure across multiple cloud service providers. It involves implementing security measures and practices to ensure the confidentiality, integrity, and availability of digital assets in a multi-cloud environment.

☁️ The aim of multi-cloud security is to safeguard data confidentiality, integrity, and availability while maintaining compliance with regulatory requirements.

Click to tweet

Multi-cloud security challenges

Operating in a multi-cloud environment introduces safety challenges that organizations must address effectively. Some common security risks in multi-cloud environments include:

Data breaches and unauthorized access

Multiple entry points across various cloud platforms increase the risk of data breaches and unauthorized access attempts, which can lead to significant financial losses, reputational damage, and legal consequences.

What is Multi-Cloud Security 1 1400x488

Account hijacking and identity theft

Attackers may target user credentials, exploiting vulnerabilities in authentication mechanisms to gain unauthorized access to sensitive information. Account hijacking and identity theft pose serious threats to the confidentiality and privacy of organizational data.

DDoS attacks and network vulnerabilities

Distributed Denial of Service (DDoS) attacks can disrupt cloud services and cause downtime, impacting business operations. Network vulnerabilities within cloud environments can also be exploited to compromise critical systems and infrastructure.

Data loss and corruption

Multi-cloud setups involve data replication and synchronization across multiple platforms, increasing the risk of data loss or corruption. Technical issues, human errors, or malicious activities can result in permanent data loss or compromise integrity of data security.

What is Multi-Cloud Security 4 1400x488

Compliance and regulatory concerns

Organizations operating in regulated industries must ensure compliance with industry-specific regulations and standards across multiple cloud environments. This becomes complex when dealing with different cloud providers and their specific security requirements.


What is Multi-Cloud Security 5 1400x488

Multi-cloud security best practices

To mitigate the risks associated with a multi-cloud environment, organizations should adopt the following best practices:

1. Implement a comprehensive security multi-cloud architecture. Develop a robust security architecture that spans across all cloud environments, including network security, access controls, encryption, and threat detection mechanisms.

2. Adopt a defense-in-depth approach. Implement multiple layers of security controls, such as firewalls, intrusion detection and prevention systems (IDPS), and security information and event management (SIEM) solutions.  Security monitoring strategy is helpful for securing public cloud and private cloud data.

3. Leverage automation and orchestration. Automate security processes and leverage orchestration tools to ensure consistent, scalable, and efficient management of security controls across diverse cloud platforms. Using compatible Identity and Access Management (IAM) providers for access management and controls facilitates automation processes.

4. Monitor and detect anomalies. Implement real-time monitoring and threat detection mechanisms to promptly identify and respond to security incidents. Continuous monitoring helps detect unauthorized activities, data breaches, and potential vulnerabilities to lower the likelihood of multi-cloud security challenges.

5. Encrypt data and implement key management. Encrypt sensitive data at rest and in transit to ensure its confidentiality. Establish secure key management practices to safeguard encryption keys and control access to the encrypted data.

6. Regularly update and patch systems. Deploy a security monitoring strategy to ensure timely updates and patches for cloud infrastructure components, applications, and security tools and address known vulnerabilities.

7. Educate and train employees. To onboard a multi-cloud security solution is half-job done. Conduct regular security awareness training to emphasize the importance of secure cloud usage and best practices. Promote a culture of security consciousness to empower employees to identify and report security threats.

By implementing these best practices, organizations can enhance their multi-cloud security posture, minimize vulnerabilities, and protect their digital assets from evolving cyber threats in the complex multi-cloud landscape.

Benefits of a multi-cloud strategy

While multi-cloud security presents its own set of challenges, adopting a multi-cloud strategy offers several benefits to organizations. Some of the key advantages include:

Flexibility and vendor independence

By leveraging multiple cloud service providers, organizations have the flexibility to choose the best services and features from each provider. This reduces vendor lock-in and enables companies to customize their cloud infrastructure based on specific requirements.

Improved performance and reliability

Distributing workloads across multiple cloud platforms helps enhance performance and reliability. Organizations can optimize their infrastructure by selecting cloud providers that offer the best geographical coverage, network capabilities, and service-level agreements (SLAs) for their specific needs.

Scalability and elasticity

Multi-cloud environments provide scalability and elasticity, allowing organizations to scale resources up or down based on demand easily. By leveraging the resources of multiple cloud providers, organizations can ensure they have the necessary capacity to meet fluctuating workloads without service disruptions.

Disaster recovery and business continuity

Adopting a multi-cloud strategy strengthen disaster recovery and business continuity capabilities. Organizations can replicate data and applications across different cloud platforms, ensuring redundancy and resilience in the event of a cloud service outage or disaster.

Cost optimization

Multi-cloud strategies help organizations optimize costs by selecting the most cost-effective cloud services for different workloads. Organizations can efficiently manage their cloud expenditures by leveraging competitive pricing models, discounts or promotions from various cloud providers.

How to choose the right multi-cloud vendor?

Selecting an appropriate multi-cloud vendor is a critical decision that impacts an organization’s security and overall cloud strategy. Consider the following factors when evaluating potential multi-cloud vendors:

  • Security capabilities: Assess the vendor’s security measures, including data encryption, access controls, threat detection, and incident response capabilities. Ensure alignment with your organization’s security requirements and compliance standards.

  • Integration and interoperability: Evaluate how well the vendor’s services integrate with your existing systems and applications. Consider the vendor’s compatibility with industry-standard APIs, tools, and technologies for smooth interoperability.

  • Scalability and performance: Examine the vendor’s ability to scale resources and handle increasing workloads. Evaluate their network capabilities, geographical coverage, and SLAs to ensure they can meet your organization’s performance and scalability requirements.

  • Cost structure: Compare pricing models, including pay-as-you-go, subscription-based, and reserved instances, to find the most cost-effective option. Evaluate the vendor’s pricing transparency, potential hidden costs, and the availability of cost optimization features.

  • Vendor reputation and support: Research the vendor’s reputation, reliability, and customer support services. Read reviews, seek recommendations, and evaluate the vendor’s responsiveness to customer inquiries and support requests.

How can NordLayer help?

NordLayer, a leading provider of cloud network security solutions, offers comprehensive features to address the security challenges of multi-cloud environments. NordLayer’s solutions include

Secure network connectivity: NordLayer provides secure and encrypted network connections between cloud environments, ensuring data integrity and confidentiality.

Centralized security management: with NordLayer’s centralized management console, organizations can efficiently monitor and manage security policies across multiple cloud platforms, simplifying the security administration process.

Zero Trust Network Access (ZTNA): NordLayer’s ZTNA, based on the Zero Trust approach, enables organizations to implement precise access controls and authenticate users and devices before granting network access, reducing the risk of unauthorized entry.

Threat detection and response: NordLayer employs advanced threat detection and response mechanisms, using machine learning to identify and mitigate potential security incidents in real-time.

Compliance and regulatory support: NordLayer assists organizations in meeting compliance requirements by offering features like data encryption, secure access controls, and audit logging to ensure regulatory adherence.

By leveraging NordLayer’s robust multi-cloud security solutions, organizations can enhance their security posture and protect their digital assets across diverse cloud environments effectively.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Quantum encryption: a new era of cybersecurity innovations

As we embrace the digital world, the threat of cyber-attacks grows, and so does our need for robust cybersecurity measures. Innovative and powerful solutions like quantum encryption are carving out their cybersecurity niche.

This groundbreaking technology leverages the complex principles of quantum mechanics to offer seemingly impregnable security. But what is quantum encryption, and how does it impact our digital security? Let’s find out.

What is quantum computing?

Quantum computing is a key principle underpinning quantum encryption. Traditional computers use bits (0s and 1s) to process information. However, quantum computers use quantum bits, or “qubits”.These “qubits’ can exist in multiple states at once thanks to a quantum phenomenon known as superposition. This allows quantum computers to process an astronomical amount of data at mind-boggling speeds, far beyond the capabilities of traditional computers.

Let’s use quantum computing in a light switch analogy to understand the superposition better.

classic computing and quantum computing comparison💡 If a regular bit is like a light switch that can be either on (1) or off (0), then “a qubit” is like a dimmer switch that can blend different levels of on and off at the same time. This superposition property allows a qubit to hold and process an enormous amount of information compared to a classical bit.

When a quantum system is in a superposition state, it is in multiple states at once, each with its probability. However, once a measurement is made, the “qubit” collapses from this superposition into one of the probable states and gives an output accordingly.

This unique characteristic of “qubits”—being in multiple states at once—enables quantum computers to process countless outcomes simultaneously, providing them with potentially immense computational power.

What is quantum encryption?

🔑 Quantum encryption is a cutting-edge approach to securing information transfer, built on principles of quantum mechanics. This method utilizes quantum bits, or “qubits”, rather than traditional binary bits, to encrypt and decrypt data.

Click to tweet

Quantum encryption uses another quantum concept – entanglement. Entanglement is a phenomenon where two particles, regardless of distance, are linked so that the state of one immediately influences the other.

This principle is applied in Quantum Key Distribution (QKD), where the key for encrypted data decryption is shared through entangled particles. Any attempt to intercept the particles triggers a change in their state, thus alerting the intended recipients to a possible breach.

Benefits of quantum cryptography

The invulnerability to interference provides quantum encryption with an unprecedented level of security. Because of the complexity, traditional cryptographic systems can’t match the new upcoming standard.

Instant detection of breaches

Eavesdropping, or man-in-a-middle attacks, concerns current encryption methods, become nearly impossible in a quantum encryption setup.

👂 Eavesdropping, in the context of encryption and cybersecurity, refers to an attack where a malicious actor intercepts and listens in on private, encrypted communication without the knowledge or consent of the communicating parties.

Click to tweet

The ultimate goal is to steal sensitive information, such as personal details, login credentials, or encryption keys. Interruption of a third party alters the status of the particles and alerts the sender and receiver about the attempted attack because it’s impossible to observe a quantum system without disturbing it.

The complex power of physics

The sheer computational power of quantum computers could be used to break traditional encryption algorithms, making the development of quantum-resistant algorithms necessary.

Mathematics-based and Physics-based cryptography comparison

Pioneering research is currently underway to develop these quantum-resistant algorithms. The aim is to create encryption techniques robust enough to withstand attacks from quantum computers.

Many organizations, including prominent tech corporations and government entities, invest significantly in these cutting-edge initiatives, preparing for the quantum computing revolution.

Challenges of quantum encryption

The implications of quantum encryption for the cybersecurity industry are profound. It could revolutionize how data is secured when fully realized, making some of today’s most sophisticated cyber-attacks obsolete.

Business adoption to change

Quantum cryptography sets a new security standard, compelling organizations worldwide to adapt or risk becoming easy targets for quantum-powered attacks. Flexibility and easy transition to new technologies become essential requirements.

Early stages of technological development

The path to universal quantum encryption is full of challenges. Quantum computers are still in their developmental stages, with only a handful of operational prototypes. Underdeveloped concepts keep encryption in a premature, almost theoretical stage, meaning quantum cryptography isn’t available any time soon.

Extreme storage conditions

Quantum computers also require frigid environments and careful handling of “qubits” to prevent decoherence – a premature loss of quantum states. Additionally, creating a global network of quantum computers for widespread quantum encryption is a mammoth task requiring substantial investment and technical breakthroughs.

Quantum cryptography and NordLayer

While quantum encryption holds great promise for the future of cybersecurity, its implementation is a significant undertaking. The journey is riddled with technological challenges and substantial costs. However, given the immense potential benefits, pursuing quantum encryption is critical in this ever-evolving digital age. Get ready to witness a quantum leap in cybersecurity innovation.

In the meantime, NordLayer offers services utilizing AES 256-bit encryption, the industry’s highest cryptographic standard. This approach is more accessible as it’s widely implemented, mature and can be operated on existing digital infrastructures. Combined with other network access securing features, AES 256-bit encryption minimizes the risk of a data breach. Reach out to learn more about NordLayer’s security solutions for your organization.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

NordLayer 客戶案例 DataWalk 如何在 20 分鐘之內部署安全網絡

重點內容:

  • DataWalk 是一家位於波蘭、英國和美國的商業情報公司,每天需要處理大量來自企業和政府機構的敏感數據資源。
  • 正尋求一個低維護成本的企業級資訊安全方案,特別是對於初創和快速擴張的企業而言,他們常常面臨資源匱乏的情況。
  • NordLayer 提供了一個快速、輕鬆、有效的解決方案,減輕了 IT 部門的工作負擔。
  • 具有簡單的集成標準,確保與其他系統的兼容性,增強而不是破壞公司的生態系統。
  • 在最終用戶和 IT 管理員之間達到平衡,能夠輕鬆安裝和管理,提高整體效率。
  • 20 分鐘部署網絡基礎架構升級,簡單無縫地融入現有的公司基礎架構中。

資訊安全議題往往只著重於處理惡意行為和威脅解決方案,卻鮮少關注到 IT 經理的角色。然而,IT 經理的決策以及他們對於安全需求的重視,往往會對資訊安全的優先排序和時間管理產生影響。尤其對於初創和快速擴張的企業而言,它們常常面臨資源匱乏的情況,並且將開發可信賴且高效的產品視為當務之急。

DataWalk 是一家位於波蘭、英國和美國的商業情報公司,每天都必須處理大量來自企業和政府機構的數據資源。該公司擁有由 130 多名員工組成的團隊,主要專注於開發數據分析軟件,旨在揭示商業營運中詐欺和洗錢的隱藏模式和聯繫。在追求可信賴和高效產品的同時,他們的DevOps 工程師兼部署架構師 Thomas Vodrazka 分享了他在建立和執行資訊安全路線圖方面的見解,並討論了公司自成立以來所面臨的挑戰。

面臨的挑戰
DataWalk 尋求低維護成本的企業級資訊安全方案

DataWalk 是一家處理相對敏感大數據資訊的公司,因此資訊安全是他們的首要關注項目之一。作為一個軟件供應商,他們在 AWS 雲端服務上運行,並使用各種配置來展示試用、測試和離線資料處理環境。隨著國際團隊成員的增加,公司網絡的流量負載也隨之增加。起初,對於一家小型公司來說,內部的 VPN 和伺服器足以應對需求。然而,隨著公司的服務範圍擴大和內部使用者數量增加,本地 VPN 面臨著流量快速增長的巨大壓力。

在尋找替代方案的同時,DataWalk 選擇將部分流量轉移到共用 IP 環境以減少本地伺服器負載,這是一個合理的快速解決方案。此舉不單成本效益高,且維護工作由第三方負責。然而,儘管公共伺服器可能是最佳選擇,但仍存在與其他伺服器使用者發生腳本衝突的風險。此外,共用閘道器也具有配置限制,對於一家需要安全環境以提供服務的公司來說,這可能成為一個不確定因素。

「作為一名 IT 系統管理員,你必須負責監督許多不同的領域,以確保業務運作和安全政策能夠順利且充分執行。尤其在小型工作團隊中,時間成為至關重要的資源,因此理所當然地,我們會優先尋找能夠保護我們的解決方案。」Thomas Vodrazka 說道。

在安全服務供應商中,提供具有專用 IP 選項的 VPN,介乎於自主維護的本地伺服器和公共閘道器之間。這種解決方案提供了安全性,同時減輕了維護的負擔。然而,如何將額外的安全性整合到公司的基礎架構中,同時不會給內部使用者帶來繁雜的操作和困惑呢?

NordLayer 提供了一個「增強而不是破壞公司的生態系統」的解決方案
以減輕 IT 經理的工作負擔

作為公司開發流程的先驅者,IT 經理在這個過程中擁有最大的自由度,但也承擔相應的責任。他們可以嘗試在企業層面引入有影響力的解決方案。然而,一旦這些解決方案被實施,系統就需要額外的安全措施。因此,DataWalk 最終轉向更為簡單易用的解決方案,以確保系統的安全性。

Thomas Vodrazka 補充說:「我和公司的 CTO 一起開始使用 NordVPN,該服務提供了我們所需的一切功能和界面。這激發了我對商業版本的好奇,我開始向周遭詢問是否有相應的商務解決方案。很快,我們就全面轉向了NordLayer,讓不同地方的員工能夠安全地存取公司的資源。」對於 IT 經理來說,如果新工具的設置對其他員工而言過於複雜,這可能會造成一些不便。

這個解決方案需要在最終用戶和 IT 管理員之間達到平衡,讓他們能夠輕鬆安裝和管理工具,從而提高整體效率。同時,該解決方案需要具有簡單的集成標準,以確保與其他服務供應商的兼容性,並增強而不是破壞公司的生態系統。

NordLayer 解決方案的其他功能,例如遙距桌面協議(RDP),在需要更頻繁地進行遙距疑難排解和存取同事終端的情況下,也顯得非常有價值。當 IT 管理員位於不同地區,且遙距團隊缺乏解決問題所需的知識或技能時,虛擬協助對於 IT 管理員來說是一個極其重要的支援工具。

20 分鐘之內部署安全網絡
快速、輕鬆、有效的網絡基礎架構升級

IT 系統管理員本身就是最終用戶之一,這使得他們能夠輕鬆進行公司系統的技術升級和整合。這種自主性為他們留出更多的空間來規劃和測試定制的資訊安全策略,以應對各種安全場景,包括最佳和最糟的情況。

「只需 20 分鐘的配置時間,就可以封鎖公共存取並更改 IP 地址。它就是那麼簡單。我不再需要擔心 VPN 了,這讓我節省了時間,並能夠更好地運用這段時間。」Thomas 說道。

NordLayer 的一個優勢是它可以在幾分鐘內進行部署,簡單的安裝過程能夠無縫地融入現有的公司基礎架構中。DataWalk 在美國和歐洲使用了兩個虛擬私有閘道器,所有管理員需要做的就是進行一次配置,然後就可以不再擔心它了。透過集中控制面板協助 IT 系統管理員,促進內部審計的進行。此外,如果您的團隊遇到任何問題,他們可以依靠全天候 24/7 的客戶支援團隊提供協助。

產品資料:
https://version-2.com/nordsecurity

下載「DataWalk 如何在 20 分鐘之內部署安全網絡」使用案例:
https://version-2.com/nordlayer-landing-page-datawalk-usecase/


關於 NordLayer
NordLayer 是現代企業的自適應性網絡存取安全解決方案,來自世界上其中一個最值得信賴的網絡安全品牌 Nord Security。致力於幫助 CEO、CIO 和 IT 管理員輕鬆應對網絡擴展和安全挑戰。NordLayer 與零信任網絡存取(ZTNA)和安全服務邊緣(SSE)原則保持一致,是一個無需硬件的解決方案,保護公司企業免受現代網絡威脅。通過 NordLayer,各種規模的公司企業都可以在不需要深入專業技術知識的情況下保護他們的團隊和網絡,它易於部署、管理和擴展。

關於 Version 2 Digital
Version 2 Digital 是亞洲最有活力的IT公司之一,公司發展及代理各種不同的互聯網、資訊科技、多媒體產品,其中包括通訊系統、安全、網絡、多媒體及消費市場產品。透過公司龐大的網絡、銷售點、分銷商及合作夥伴,Version 2 Digital 提供廣被市場讚賞的產品及服務。Version 2 Digital 的銷售網絡包括中國大陸、香港、澳門、台灣、新加坡等地區,客戶來自各行各業,包括全球1000大跨國企業、上市公司、公用機構、政府部門、無數成功的中小企及來自亞洲各城市的消費市場客戶。

A complete guide to WordPress security best practices in 2023

Most of the web content that you come across online is made possible by a content management system (CMS). WordPress is probably one of the best-known CMS platforms, which powers a staggering 43% of all websites globally

Its scalability, user-friendly interface, and robust customization options have catapulted it to the forefront of content management systems. However, as its popularity has grown, so has the interest of cybercriminals.

This article guides you through best security practices for your WordPress site. By adopting beginner-friendly practices such as secure hosting, regular updates, strong usernames/passwords, and two-factor authentication, you can significantly bolster your site’s defenses against threats.

Assessing WordPress security

Just like any other system, WordPress isn’t immune to security vulnerabilities. The distinction should be made between two things: the security of WordPress as a product and various factors like third-party plugins and extensions. While the majority of them are developed by reputable sources, the sheer volume of plugins means that some may have exploitable loopholes.

As an open-source platform, WordPress boasts a vibrant community dedicated to the ongoing mission of patching vulnerabilities and enhancing security. Yet, over the years, numerous threats have emerged, from cross-site scripting (XSS) attacks to SQL injections, placing WordPress security at the top of user priorities.

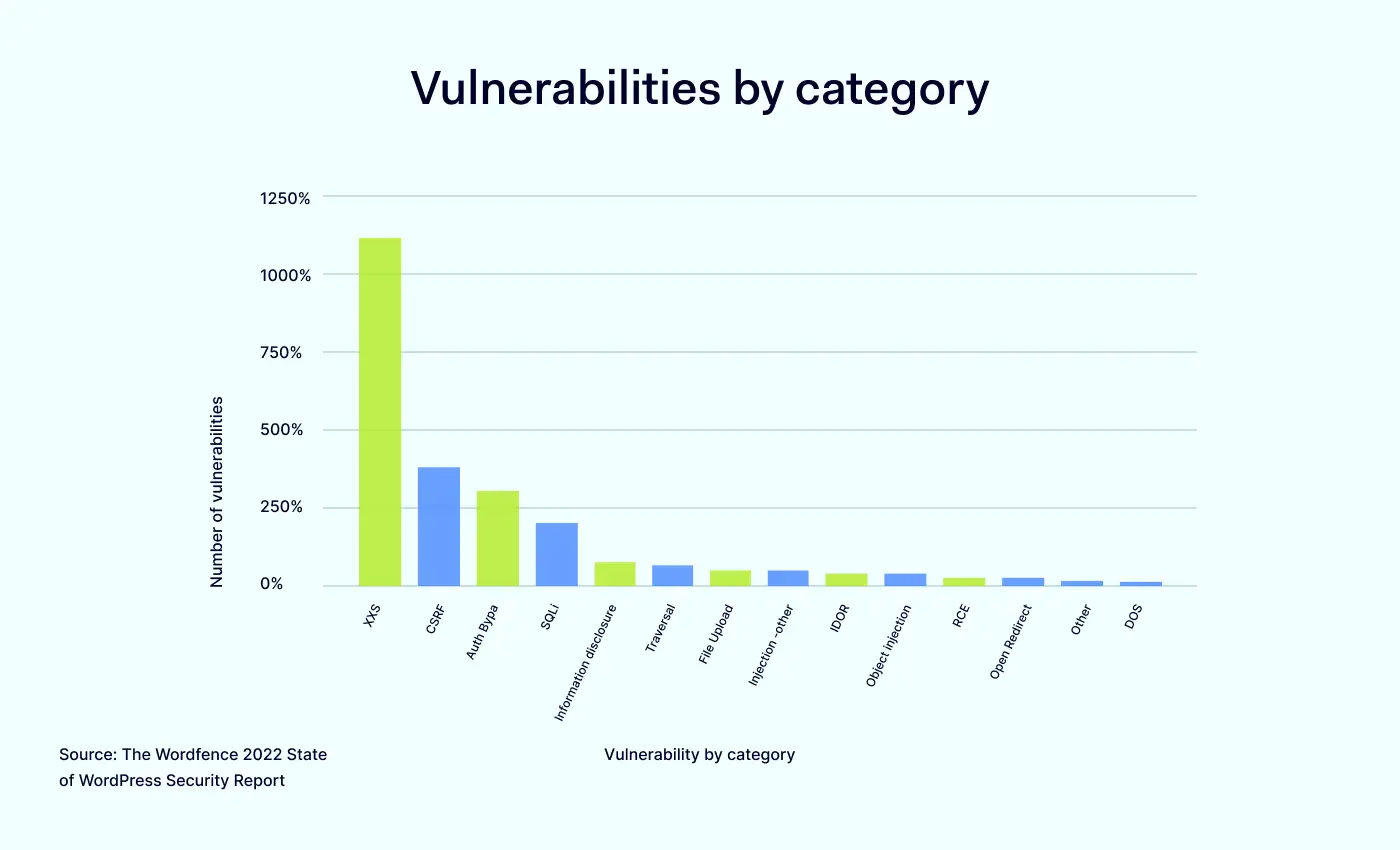
The bad news is that these vulnerabilities aren’t theoretical, and they can bring actual harm, resulting in data breaches and severe reputational damage. A study conducted in 2022 by Wordfence shows that XSS and CSRF vulnerabilities have significantly increased in volume. These statistics are alarming enough to be a wake-up call for network administrators to prioritize comprehensive website protection.

Main WordPress vulnerabilities

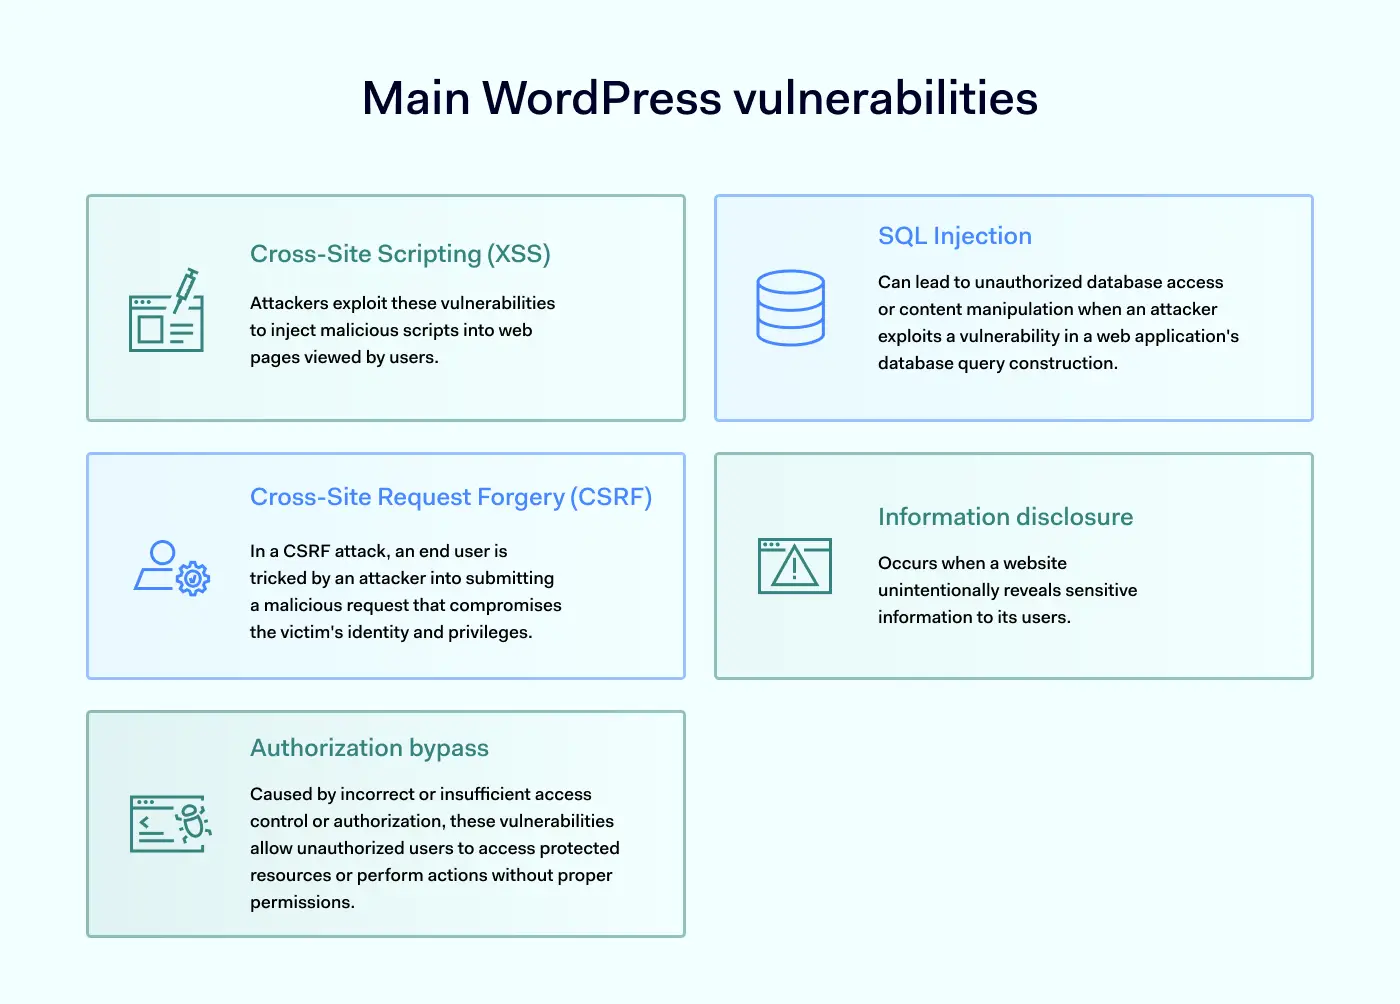
To ensure your WordPress site’s security, it’s important to have a basic understanding of common vulnerabilities. In 2022, several types of vulnerabilities were prominent, and it’s essential to delve deeper into each of them to prepare ourselves against possible threats.

Cross-site scripting (XSS)

Cross-site scripting, or XSS, accounted for nearly half of all vulnerabilities disclosed in 2022, with 1,109 submissions. These types of vulnerabilities can allow attackers to inject malicious scripts into web pages viewed by users. However, it’s worth noting that a significant number of these vulnerabilities, 408 to be exact, required administrative permissions to exploit, making them less severe than typical XSS vulnerabilities.

Cross-site request forgery (CSRF)

The second most common vulnerability was cross-site request forgery (CSRF), with 377 disclosed vulnerabilities. In a CSRF attack, an innocent end user is tricked by an attacker into submitting a malicious request. It inherits the victim’s identity and privileges to perform an undesired function on its behalf.

Authorization bypass

Authorization bypass vulnerabilities ranked third in the list of common vulnerabilities for 2022. This category includes vulnerabilities primarily caused by incorrect or insufficient access control or authorization. They could potentially allow unauthorized users to access protected resources or perform actions without proper permissions.

SQL injection

SQL Injection vulnerabilities were the fourth most common, with 200 cases disclosed. In these types of attacks, an attacker exploits a vulnerability in a web application’s database query construction, leading to unauthorized database access or content manipulation.

Information disclosure

Finally, rounding out the top five is Information Disclosure, with 73 disclosed vulnerabilities. It refers to instances where a website unintentionally reveals sensitive information to its users. This could range from technical details of the web application to users’ personal information.

Understanding the significance of WordPress security

Every WordPress user, from individual bloggers to multinational corporations, must understand what compromised website security means. For businesses, it translates into massive financial losses, a dent in customer trust, and potential compliance penalties. Individuals are also at risk of having their personal information stolen and used by cybercriminals, so the stakes are equally high.

In an era defined by digital connectivity, website security is an absolute necessity, not a luxury. It is time to shift our mindset from reactive to proactive. By taking the initiative and implementing robust security measures, we can significantly lower the risk of our websites falling victim to cyberattacks.

WordPress security best practices

Navigating through the labyrinth of WordPress security can seem daunting at first. This is due to the fact that overall security tips can be categorized into practices involving plugins and without plugins. As a third-party software that can be installed on a WordPress site to extend its functionality, they can provide various additional security measures. However, like any software, security plugins themselves can have vulnerabilities or backdoors that hackers could exploit.

On the other hand, security tips without plugins focus on manual implementation or modifying the WordPress installation directly. Both approaches have their own advantages and disadvantages. Therefore, striking a balance between relying on security plugins and following general security practices is crucial.

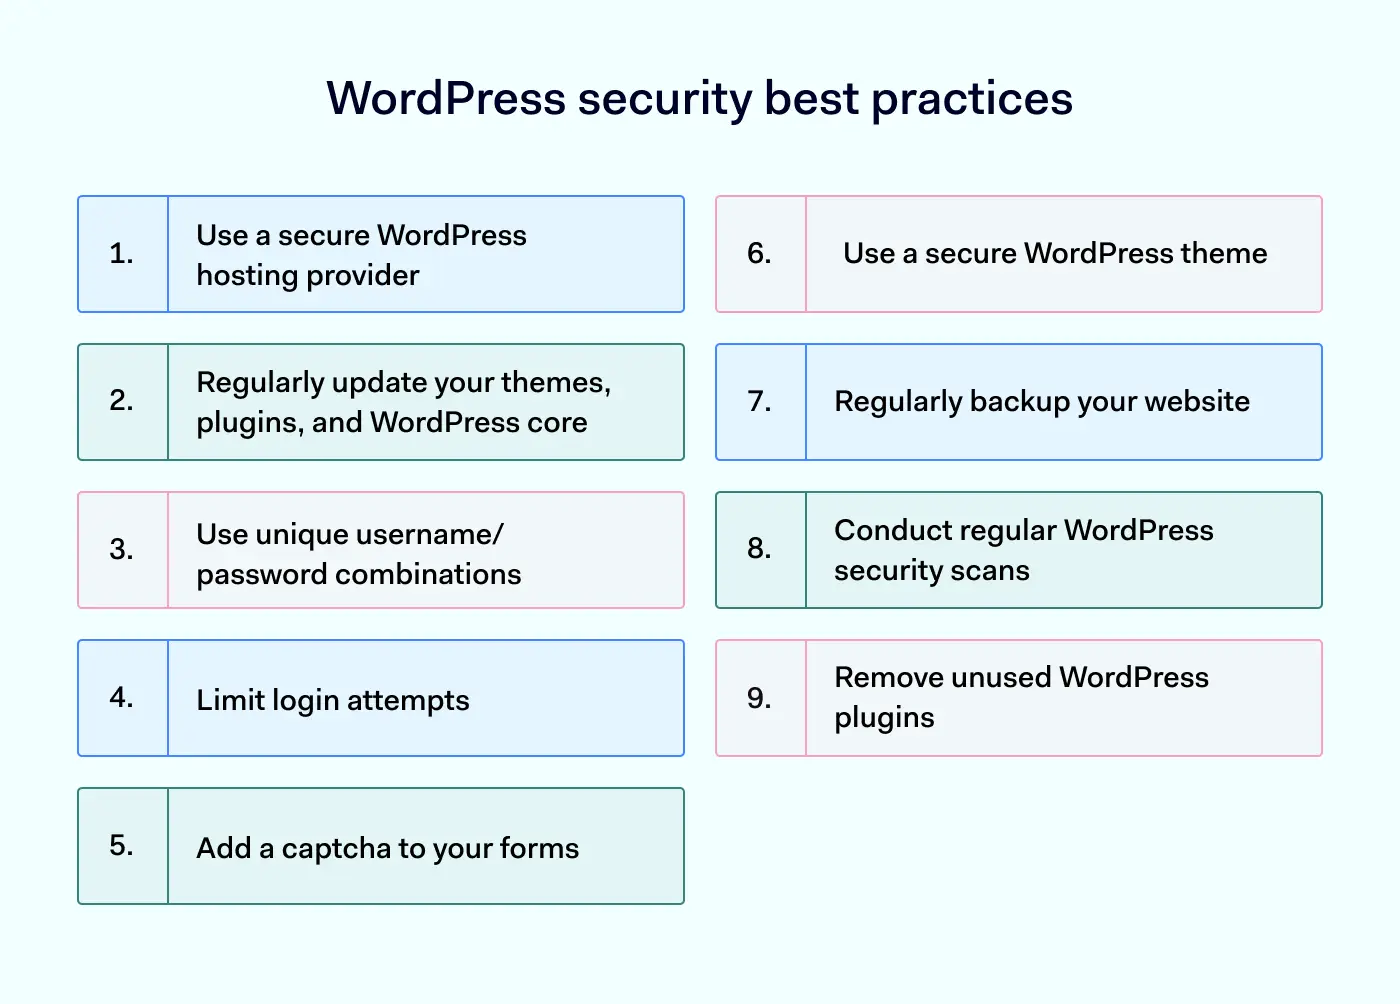
Use a secure WordPress hosting provider

Choosing a WordPress hosting provider is the first line of defense against potential cyber threats. A reputable hosting provider prioritizes data security and implements measures to safeguard your website’s data, including backups, encryption, and secure data storage. A good host ensures that your website is well-protected at the server level.

Regularly update your themes, plugins, and WordPress core

Software, including WordPress themes, plugins, and the core itself, can contain vulnerabilities. Updates often include patches for known security vulnerabilities, so updating all the mentioned components is crucial. This is the only way to ensure that you have the latest security patches and fixes, reducing the risk of your website being exploited by hackers or malware.

Use unique username/password combinations

Simple login credentials can be an open door for hackers. Avoid using ‘admin’ as your username, and ensure your passwords are complex and unique. A good password includes uppercase and lowercase letters, numbers, and special characters. A password manager like NordPass can help you create strong passwords and store these safely.

Limit login attempts

Limiting the number of failed login attempts can prevent brute-force attacks. WordPress offers various plugins that can lock out a user’s IP address after a certain number of failed login attempts is reached. This makes it more difficult for hackers to try username/password combinations to log in.

Add a CAPTCHA to your forms

Adding CAPTCHA (Completely Automated Public Turing test to tell Computers and Humans Apart) to WordPress can help prevent spam and bot submissions on your forms. Bots are often used to launch various types of attacks, such as submitting spam comments, brute-forcing WordPress login page, or submitting malicious code. CAPTCHA makes it harder for automated systems to engage with your site and potentially cause harm.

Use a secure WordPress theme

Not all themes are created equal. Choose themes from reputable sources that prioritize security. Opt for themes that have well-structured, clean, and secure code. Themes that follow coding best practices reduce the likelihood of security vulnerabilities. Always check ratings, reviews and update frequency before deciding on a theme.

Regularly backup your website

Regularly backing up a WordPress website is a safety net. If something goes wrong, you can always revert to a previous WordPress version of your site. Regular backups ensure that your website’s content, including posts, pages, images, and databases, are securely stored and can be recovered. Remember, it’s important to store backups securely, preferably off-site or in a separate location from your live website.

Conduct regular WordPress security scans

Regular security scans help detect vulnerabilities and malware that have slipped through the cracks. Once identified, vulnerabilities and other weaknesses in your website’s security can be addressed with fixes. This process provides a pace of mind and knowledge that proactive measures are being taken to protect not only the website, but also its visitors.

Remove unused WordPress plugins

Like most, you probably have tried different WordPress plugins but didn’t remove them after you tried them out. Yet, outdated or unused plugins can pose a security risk to your website. If a plugin is not regularly updated by the developer, it may contain vulnerabilities that can be exploited by hackers. Going through them and removing unused ones will reduce the number of openings a malicious actor can use to access your site.

How to secure access to WordPress

WordPress security best practices provide a solid foundation for improvements. However, it’s also a good idea to implement a wider range of security features beyond WordPress itself. While plugins and built-in control can help a lot, more sophisticated solutions may sometimes be required. Here are actionable steps you can take when securing your digital environments.

Secure Access with a VPN

WordPress site security can be improved by using a Virtual Private Network (VPN). A VPN encrypts exchanged data traffic, making it difficult for hackers to intercept your information between your user devices and WordPress servers. By routing your traffic through a VPN, you add a layer of security to your WordPress access, protecting your site from potential attacks.

Implement SSO and MFA

Implementing single sign-on (SSO) and multi-factor authentication (MFA) SaaS access control solutions can significantly enhance the security of your WordPress website. SSO allows users to authenticate once and gain access to multiple systems or applications without needing to log in separately. Meanwhile, MFA adds an extra layer of security by requiring users to provide additional verification factors beyond a password to access their accounts. These solutions make it much more difficult for unauthorized users to gain entry into your WordPress resources.

Allow connections only from trusted IP addresses

Restricting access only to allowed connections helps to enhance the security of your WordPress website. By limiting connections only to trusted IP addresses, you prevent unauthorized individuals or bots from gaining access to the WordPress administrative area. IP Allowlisting can play a significant role in adopting a Zero Trust security posture. However, it’s essential to carefully assess your specific security requirements, user base, and potential limitations as not to introduce additional limitations for your user base.

Segment your network into smaller parts

Consider implementing network segmentation, which involves dividing your network into smaller parts. By segmenting the network (for instance, with a web application firewall), you can separate different components of your WordPress infrastructure, such as the web server, database server, and application server. This isolation ensures that if one component is compromised, the attacker’s access is limited to that specific segment, reducing the potential impact on other parts of the network.

Encrypt your held data

Data encryption plays a crucial role in enhancing WordPress security by providing a layer of protection for sensitive information. By encrypting the data, it becomes scrambled into an unreadable format that can only be deciphered with the appropriate decryption key. This prevents unauthorized individuals from intercepting and understanding the data, significantly enhancing the overall security posture.

Implement access management controls

Access management controls allow you to define who can access your WordPress website and what level of access they have. By properly assigning roles, you can limit access to critical functions and sensitive areas of your website. For example, you can have administrators who have full control over the site, editors who can manage content, and subscribers who only have basic access. With such tools you gain granular control over who has access to what within your WordPress site, enhancing your site’s security profile.

FAQ

Can I secure my WordPress website without technical expertise?

Yes, implementing basic security practices like using strong passwords, keeping WordPress updated, and enabling two-factor authentication can be done without extensive technical knowledge. However, for advanced security measures, it is advisable to seek assistance from a professional.

How often should I update my WordPress website?

Regular updates are crucial for maintaining security. Update your WordPress installation, themes, and plugins as soon as new versions become available. Aim to check for updates at least once a week.

Are free themes and plugins safe to use?

Not all free themes and plugins are unsafe, but caution is advised. Stick to reputable sources like the official WordPress repository or trusted third-party marketplaces. Always review user ratings, read reviews, and ensure they receive regular updates and support.

What should I do if my WordPress website is hacked?

If your WordPress website is hacked, take immediate action. Change all passwords, restore your website from a recent backup, and scan your site for malware using security plugins. Consider consulting with a professional to ensure all vulnerabilities are addressed.

Can a security plugin alone protect my website?

While security plugins provide valuable features, they should be seen as part of a comprehensive security strategy. Combine security plugins with other practices, such as regular updates, strong passwords, and secure hosting, to create a robust defense against threats.

How can NordLayer help?

Securing your WordPress site involves an ongoing effort and frequent upgrades. It means taking care of your WordPress core and installing strong protections like IP allowlisting to enhance your resistance against potential cyber-attacks. However, this is only the start, since the security environment is enormous and difficult to traverse alone.

This is where NordLayer can help. One of the features we offer is IP allowlisting, which enables organizations to control access to internal resources by specifying trusted IP addresses. Simultaneously, we also provide fixed IP addresses, ensuring that you can implement IP allowlisting effectively and maintain a more secure environment.

Additionally, we understand the importance of network segmentation to enhance security further. By dividing your network into smaller, isolated segments, we help create barriers limiting potential threats from spreading laterally within your infrastructure. We also offer the ability to provide exclusive access rights for those who specifically need to access your WordPress work environment within your organization.

However, we don’t stop there. We go the extra mile to secure your WordPress environment by implementing a robust two-factor authentication (2FA) process. With 2FA, even if someone has access rights, they will need to undergo an additional layer of verification beyond the standard login credentials.

Contact us now to discover how we can boost the security of your WordPress site while ensuring simplicity of use and seamless operations.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.