Skip to content

Meet Nord People: Insights from our Engineering Managers

Cloud network security is a general term for the measures needed to secure virtualized cloud environments. It covers policies, processes, controls, and technologies. And it applies to private, public, and hybrid cloud deployments.

Basics of cloud network security

Cloud network security resembles traditional on-premises network security but with important divergences related to defending virtualized environments.

Like on-premises security, cloud network security defends network assets against external threats. Security systems for the cloud assess access requests and authorize users to access resources. They provide visibility for security managers, including real-time alerts and audit logs. And they neutralize malware and illegitimate data transfers.

Unlike standard security solutions, cloud defenses are not based on-site. Cloud security systems function via software-defined networking tools. Virtual gateways reside in the cloud, where they can protect applications and data from access requests – wherever users may be.

The context: understanding cloud computing

Cloud computing is the use of virtualized platforms to host applications and store data. The cloud exists as a worldwide network of servers and is accessible via a standard internet connection.

The user’s apps and data reside off-site, removing the need for on-premises hardware. Instead, network resources are “virtualized”. Resources are accessible to the owner or user, but they are hosted by cloud providers.

Users can choose to access software-as-a-service (SaaS) apps. Or they can build customized cloud deployments via platform-as-a-service (PaaS). In all cases, security is a shared responsibility between users and cloud service providers (CSPs).

Providers must secure hardware used to host cloud apps or data. Users must protect any data passing through cloud environments. They are also responsible for managing access to cloud assets.

Elements of cloud network security

Cloud network security solutions vary, but could include:

  • Integrated cloud security stacks – Includes next-generation firewall protection, anti-virus and anti-bot tools, intrusion prevention systems, controls for individual apps, IAM, and data loss prevention tools.

  • Sanitization – Systems can filter low-level traffic and remove potential threats, without the need for full-scale inspection.

  • Exploit protection – Protection against known Zero Day Exploits, with data derived from the latest threat intelligence.

  • Traffic inspection – Inspection of SSL/TLS traffic passing throughout virtualized environments. Analyzes encrypted traffic without compromising speed.

  • Centralized security administration – Solutions cover all cloud applications and storage assets. They integrate seamlessly with existing resources (including on-premises networks), providing total awareness of network activity.

  • Segmentation – Cloud network security applies micro-segmentation to limit user permissions and guard confidential data.

  • Remote access – Ensures secure access for remote workers and third parties. Users can connect to cloud assets safely from any location.

  • Automation tools – Includes automated extension to newly installed cloud services. Automated workflows blend ease of use and security, allowing companies to harness the potential of the cloud.

  • Simple integration – Cloud security tools integrate with legacy applications, operating systems, and third-party security systems.

The importance of cloud network security

The cloud is everywhere in modern life. Businesses, non-profits, and government agencies all rely on cloud infrastructure to deliver services and host workloads. But the rise of the cloud has created new security vulnerabilities. This means that organizations need to rethink their network security policies.

Traditional on-premises networks have simple security architecture. Central resources are protected by the network perimeter. Endpoints are few in number and easy to monitor. Access patterns and user communities change slowly, if at all. In this context putting in place firewalls and threat detection systems is relatively simple.

Cloud network security presents a different set of challenges.

  • In the cloud, there is no standard network perimeter. Users can access cloud gateways anywhere. IT teams rarely manage on-premises resources. Instead, cloud assets are maintained by cloud providers on servers across the world.

  • A public cloud environment can change rapidly. Employees might spin up new SaaS instances or cloud APIs. Staff could bring online new cloud storage containers to backup data or handle overflows.

  • Security teams need to maintain awareness, track user activity, and neutralize threats. Organizations need a cloud network security strategy that locks down critical cloud assets while enabling users to take advantage of cloud computing.

Cloud network security benefits

Adopting a cloud network security strategy has many advantages. The benefits of retooling your security setup for the cloud include:

Improved data security

The most important benefit of cloud network security is enhanced protection for sensitive data.

Cloud security solutions encrypt data at rest on the cloud. If files are stolen, cybercriminals will not be able to read data easily. Encryption of data in transit also makes it harder to track information flows and launch targeted interception attacks.

Micro-segmentation separates confidential data from the rest of an organization’s cloud network. Data resides in software-defined compartments that are accessible with the right credentials. Cloud security systems can define these segments at a granular level.

Better visibility for administrators

IT teams need visibility to monitor threats and user activity. But legacy security solutions are not well-adapted to discovering cloud apps and tracking activity in a cloud environment.

Cloud-native network security systems bring together all virtualized assets. Admins can monitor network activity in real-time via a single pane of glass. And automated alerts deliver information about potential threats before they become critical.

Simplified cloud policy management

Security policies should reflect the security needs of network owners and be delivered to all users. But delivering security policies consistently in cloud settings is a complex task. Unified cloud network security systems solve this problem.

IT teams can automatically deliver updated security policies to endpoints. Cloud-native solutions also make it easier to deliver policies across hybrid or multi-cloud environments.

Threat analysis and neutralization

Cloud resources are vulnerable to data breach attacks. Compromised remote access devices, phishing emails, and credential theft are common entry methods. Cloud-native security controls are the only effective response.

Robust security systems detect, contain, and neutralize malicious threats before they cause damage.

Cloud network security uses threat intelligence to counter the latest threats. Intrusion detection systems guard cloud gateways and scan network traffic. Anti-bot scanners also track emerging DDoS attacks. This prevents downtime from traffic flood attacks.

Security automation

Automation allows IT teams to work efficiently and securely. Users can automatically extend access controls and threat detection to new cloud resources. There is no need for lengthy manual configuration processes. New services receive instant coverage, limiting the risk of human error.

Cloud network security challenges

Cloud network security systems make sense for organizations that manage pure cloud or hybrid networks. But implementing cloud security is not a simple process. Challenges faced by organizations include:

Understanding shared responsibility

Under the shared responsibility model, CSPs and users share responsibility for securing cloud resources. This is accepted by users when they source cloud solutions. But determining areas of security responsibility can be difficult.

  • Cloud users must secure apps and data stored on the cloud. They must manage user access and monitor external threats.

  • CSPs are responsible for securing cloud infrastructure. They harden cloud servers to block data thieves or viruses.

This model leaves scope for overlap and confusion. For example, cloud users may rely on encryption provided by their cloud service provider. As a result, users may not apply encryption for data in transit or use Data Loss Prevention tools.

It’s essential to define areas of responsibility before activating cloud services. Most SaaS providers build security features into their products. But users always have a role to play, and this varies between different cloud contexts.

Managing dynamic cloud environments

Change is a core feature of cloud deployments. Apps come online constantly. Configurations may change to reflect developing workflows. New users connect from home or abroad. And individual employees can connect cloud containers with a few mouse clicks.

Automation can sometimes make this problem worse. For instance, companies may use autoscaling to build cloud deployments quickly. This boosts efficiency, but it also leaves security teams scrambling to catch up.

Cloud network security systems need to adapt to change. Admins must track access requests, respond to alerts, and discover threats if they infiltrate network infrastructure. This is even harder in hybrid environments that mix on-premises systems with extensive public and private cloud deployments.

Cloud network security best practices

Achieving cloud security can be challenging. But managing cloud security is far from impossible, even for small businesses. Follow these cloud network security best practices and build a security solution that meets your goals:

1. Apply Zero Trust principles

Zero Trust Network Architecture (ZTNA) is a security model that teaches users to trust no one. This is a good rule to apply when securing cloud infrastructure.

Avoid situations where users have global network privileges, and adopt a denial-by-default stance. Require more than one authentication factor when allowing user access. And segment cloud environments to limit east-west movement within the network.

Zero Trust changes the focus of security strategies to meet cloud computing needs. Instead of policing the network edge, admins concentrate on managing identities. This is a good fit for dynamic cloud environments. Deployments may constantly change. But user communities are easier to manage.

2. Lock down interfaces between the cloud and the internet

Internet-facing assets are a critical security risk. Access portals, web forms, and email accounts connect with the wider internet. This makes them common vectors for malware and data theft attacks.

Configure cloud apps to minimize contact with the internet. If necessary, leverage threat protection tools to guard vulnerable points. Web Application Firewalls (WAF) can deny access to suspicious network traffic. DDoS and intelligent detection systems handle malicious agents that breach the firewall.

Set automated alerts to inform admins about potential risks. When building cloud network security systems, prioritize internet-facing assets. Carry out enhanced risk assessments, log user activity, and test access controls to secure entry points.

3. Use micro-segmentation to protect critical data

Cloud security systems usually include the ability to micro-segment networks. Micro-segmentation lets you guard critical data with an additional layer of protection. This has security benefits, while also helping companies comply with relevant data security regulations.

4. Use private cloud solutions to enhance security

Private clouds allow users to communicate and collaborate without creating links to the external internet. This limits the scope for attackers, whether they use email phishing or malware injection.

Build networks that blend private and public cloud tools without compromising security. Determine which workflows require internet access. Switch everything else to private access technology that does not require external IP addresses.

5. Work with partners to establish security responsibilities

The principle of shared responsibility divides security functions between service providers and consumers.

Before commissioning new SaaS or IaaS products, be clear about security responsibilities. Create a security policy for each cloud service explaining your areas of responsibility and the security controls you will use. This should complement your cloud partner’s security policy. There should be no areas of ambiguity.

6. Write and deliver clear cloud security policies

Robust cloud network security rests upon good documentation and organization.

Cloud security policies define the controls used to secure cloud resources. This could include multi-factor authentication, Identity and Access Management, and data encryption. Policies also inform users about their security responsibilities.

Every SaaS app or cloud-hosted database should have a security policy. Store policies centrally. And use automated delivery to ensure that policies are implemented consistently and rapidly.

The role of AI and machine learning in cloud network security

Cloud network security is advancing all the time. And one of the most exciting research areas is the application of Artificial Intelligence to secure cloud environments.

AI harnesses machine learning to assess cloud security threats. Also known as User and Entity Based Analytics (UEBA), this technology scans user activity to detect malicious agents. AI engines compare real-time user behavior to logs of previous activity. In theory, this information helps to authenticate legitimate users and unmask intruders.

However, UEBA faces some challenges before becoming mainstream. For example, AI requires structured data sets and huge amounts of information to function properly. Generating useful data takes time and may also breach privacy regulations.

Attackers will also adapt to the use of machine learning. Expect to see Advanced Persistent Threats (APTs) that gather user activity data and build fake profiles to fool UEBA scanners. If IT teams rely too much on AI, this could become a security threat.

Cloud network security: key takeaways

Legacy security systems were designed for on-premises networking. Next-generation cloud security tools are built into the cloud, where they operate alongside SaaS apps and cloud infrastructure.

  • Threat detection systems neutralize malware attacks.

  • Access management tools block unauthorized users.

  • Segmentation keeps high-value assets safe behind additional barriers.

  • Encryption conceals data from external intruders

These features work together to mitigate security risks associated with the cloud. In a world where businesses depend on cloud infrastructure, robust cloud network security is essential.

Looking for a cloud network security solution?

NordLayer will help you build customized cloud network security architecture. Our products include a range of cloud-native features to protect data and enable secure collaboration. For example, users benefit from:

  • Seamless identity management.

  • Threat blocking tools to analyze network traffic and block cloud threats.

  • Secure gateways link remote workers to the cloud

  • Control access with IP allowlisting.

Achieve reliable, comprehensive cloud network security. Get in touch with NordLayer and discuss your options today.
About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Meet Nord People: Insights from our Engineering Managers

As we strive to create a safer cyber future for everyone, our talented engineering team takes center stage. Curious about what it’s like to be at the heart of our operations? We recently caught up with a few engineering leaders at Nord Security: Gerrit Garbereder, Rokas Dambrauskas, and Paulius Kimbartas to discuss their teams, daily tasks, challenges, and skills.

But not everything made it into the video, and we had a few requests for further exploration! So settle back and enjoy, as we delve deeper into the world of Nord Security engineering.

Engineering teams’ role and projects

Hello, Gerrit, Paulius, and Rokas! Thanks for your time today. To start things off, could you tell us how your teams play a role in the success of Nord Security?

Paulius: Hi there. My team at NordVPN is developing the Checkout system, polishing purchase flows so that customers can get our products in the easiest and most secure way possible. So simply enabling people to purchase our products in their preferred way helps grow our user base.

Gerrit: We’re building tools to protect NordPass customers, even when they’re not actively using the app. Further, as the Premium squad, our team concentrates on monetization of the service. We’re driving this by maximizing customer satisfaction and value for money. Delivering high quality tooling will increase premium subscriptions and reduce the churn rate.

Rokas: Our mission is to continuously enhance the NordLocker platform, creating a seamless and efficient experience for everyone who uses it. By doing so, we empower other teams to excel in their work and ultimately drive the success of the entire company.

Awesome! What are some recent interesting projects you’ve worked on?

R: A little more than a year ago, NordLocker made the strategic decision to go serverless and focus on building cloud-based solutions. In recent months, we finally managed to migrate one of our core functionalities to the cloud, which was a very challenging task!

P: On the NordVPN team, we recently added a one-click payment option to enable our existing users to have a seamless purchase experience in a secure way. This feature required multiple components, such as authentication and secure data retrieval.

G: Adding attachments to NordPass was a really challenging project. We had to align the integration with our colleagues at NordLocker while the underlying structure was reworked from the ground up. During this project we created not only new features but also formed new bonds with people across multiple teams.

Work tools and daily operations

And to get these projects over the finish line, which tools do you normally use?

R: Some tools are used across the whole company. GitLab helps us manage our codebase. For snappy communication, we use Slack. Apart from that, engineers are free to use their IDEs and tools of preference.

P: To expand on that, my team uses Docker, Grafana – and those are only off the top of my head! In terms of programming languages, primarily we use TypeScript, PHP, and GO.

G: As a cross-functional team we’re using a whole zoo of tools every day. We provide each guild the tooling that fits their needs. Android, iOS and Backend development is enabled through corresponding IDEs.

What does an engineering manager do on an average day?

R: My day is quite diverse. I spend most of the time communicating with my team, ensuring their projects are on track and addressing any issues that may arise. I also participate in meetings with other teams and help with long-term planning.

P: In one word: dynamic. My primary focus everyday is to enable engineering teams to achieve their goals, so ad-hoc knowledge sharing, brainstorming, and guiding people takes time every day. On the other hand, focus time is really important for me. Planning upcoming features and aligning our goals across teams is a vital part of my work. It contributes to the team’s overall performance and happiness.

G: To add to the above, after the daily scrum in the morning, I typically take care to remove impediments for the team’s current tasks. Once everyone is unblocked I move towards tactical planning together with the Product Owner on upcoming projects and challenges.

R: I always strive to do some hands-on technical work as well, so I can stay connected to my team and the work they’re doing.

Growth opportunities and skills needed

What do you look for in your teammates?

P: It’s all about having an eagerness to learn – the cybersecurity field is very dynamic, new risks arise and our engineers need to be constantly learning and up to date with new technologies and best practices.

R: Strong technical skills are important, but we also look for individuals who are excellent problem-solvers, able to work well in a team, and have a growth mindset.

G: Engineering specialists are of course expected to be experts in their field. However, I believe it’s also necessary for this role to be open-minded with customer success as a focus. And I agree with Paulius, my expectation for any engineer is to be curious and eager to learn.

P: One other crucial thing is to be an honest communicator. If something’s wrong, we don’t wait till the situation develops. We speak about it and solve it.

How does your team grow together?

R: In my team I encourage open communication and knowledge sharing, which helps everyone on the team to continually refine their skills. Also we do regular performance evaluations, 1-on-1 meetings, as well as offering opportunities to attend relevant training and conferences.

P: Yes, 1-on-1 meetings help us to determine how each engineer wants to grow, because growth is such an individual thing. I always plan the team’s work accordingly, and prioritize initiatives that will help us all grow.

G: We benefit from the training possibilities provided through the Tesonet Group, which focus mainly on soft skills. Hard skills are improved through mentorship programs, online courses, and conferences. I encourage my team to spend around 10% of their time learning, which is scheduled into our sprint planning.

Challenges and how we solve them

It sounds like there’s a lot to consider! What challenges do you face as managers?

G: Translating the big picture into actionable items that allow individual contributors to relate their work to the company’s success is a challenge. Making everyone aware of the actual problem we are trying to solve is a difficult task. Often enough engineers tend to dive straight into a sophisticated solution while a simpler solution would have solved the customer’s problem with ease.

R: For me, it’s balancing the needs of my team with the demands of the business. This can include prioritizing tasks, ensuring everyone is on track to meet deadlines, and effectively communicating changes or updates to the team.

P: I agree with that. Alignment across individual, team, and organization goals is a challenge. The ideal situation is when each engineer’s goals are in alignment with what we as a team want to achieve, and the team goals are in alignment with what we as an organization wants to achieve. In such situations any friction disappears and you can simply tackle whatever challenges you have.

How does your team work together?

G: Our distributed team is shaped by people from different nations with a variety of backgrounds. This mixture of people and culture fosters a vivid exchange of experiences. Not every day is joy and laughter, life is full of challenges and we are handling those challenges together. Recent events in Ukraine and Türkiye are two examples of compassion and support within the team beyond professional distance.

P: Smartest restless achievers I’ve ever known. Each person on the team brings ideas on how we can overcome new challenges, which we always have. On top of that some challenges come unforeseen, but that does not stop us. We can simply jump on a call and brainstorm the solution together. Pair programming is a great way to solve problems.

___

Thanks to Gerrit, Paulius, and Rokas for their time today!

If you’re an engineer or manager interested in working with us at Nord Security to create a safer cyber future, check out our job postings below.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Best practices for secure access to Figma

As businesses increasingly shift towards digitalization, secure access to apps cannot be overstated. Today, data breaches and cyberattacks are a constant threat, making cloud security a critical business function. It’s especially difficult with collaborative tools where in-house and external team members work on joint projects.

As a web-based interface design and prototyping tool, Figma allows teams to collaborate in real-time, making various design projects easier to manage and execute. Yet, given its collaborative nature and integration capabilities with other tools, this makes Figma’s security a critical concern for these organizations.

In this article, we’ll look at Figma’s access security and highlight some best practices to prevent various risks.

Why is it important to secure access to Figma?

Figma, a collaborative interface design tool, has become an integral part of the work of designers and developers across industries. As a cloud-based application, Figma allows teams to co-design and manage projects easily, bringing together freelancer help and in-house employees allowing them to create, share, and edit designs in real-time. As many enterprise projects are considered confidential information, its secure access has become a growing concern.

Secure access to Figma projects is essential to ensure the integrity of the designs and limit access to protect the intellectual property of the organization or involved individuals. Therefore, its security is a crucial aspect to consider for all users.

Figma security best practices

Several key features in Figma can help organizations to edit privileges, sharing files securely. Here are some best practices that could help your team to secure their work.

Best practices for secure access to Figma

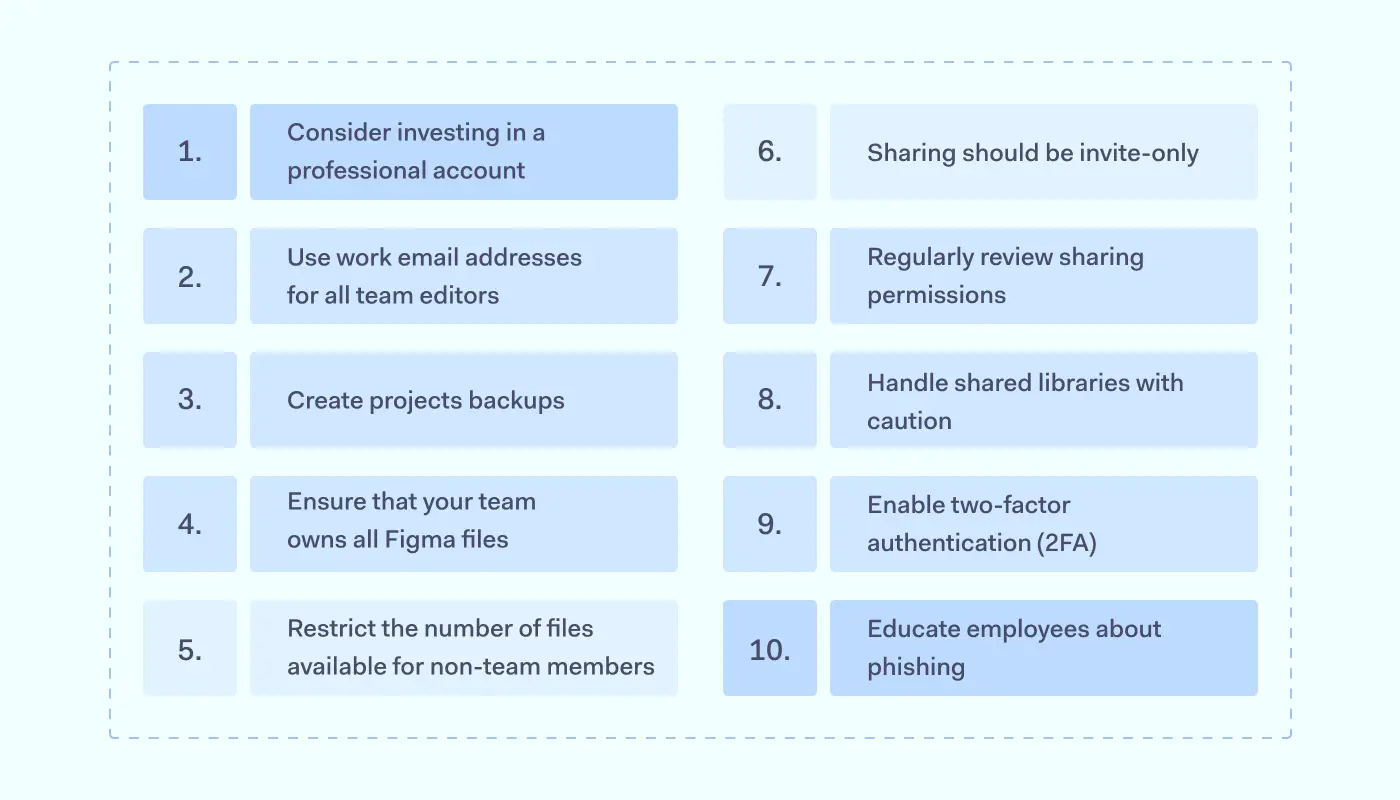
1. Consider investing in a professional account

Figma’s Professional plan enhances security measures to offer finer controls over file and prototype permissions. This enables effective management of teams and grants members access to specific Figma file folders and projects. The Professional account also includes unlimited version history, facilitating the tracking of modifications made to a Figma file and identifying the individuals responsible.

2. Use work email addresses for all team editors

If a team member engages in unauthorized activities, it’s a good practice to use work email addresses for all team editors. It enables your company’s IT or security team to promptly revoke edit privileges, maintaining the security and integrity of your organization. This creates an effective safety net against potential threats and can mitigate risks arising from unauthorized actions (i.e. a freelancer going rogue).

3. Create projects backups

Once a project reaches a significant milestone or is considered complete, consider archiving .fig files in a separate file system from Figma. This might involve exporting the final work as PDFs or prototype videos, followed by exporting source files. When the project is officially concluded, relocating these files to a yearly archive with tighter access controls makes sense. Developers can also use these files as a reference for new projects.

4. Ensure that your team owns all Figma files

The ownership of crucial Figma files should be exclusively retained within the team and not granted to external individuals, freelancer colleagues or clients. Figma files include sensitive and proprietary information, including design assets, user interface components, and collaborative work. Therefore, passing ownership to external parties could not only compromise the project’s confidentiality but also pose the risk of unauthorized modifications, distribution, or misuse of the content.

5. Restrict the number of files available for non-team members

Figma offers some access controls built-in. For example, it allows sending invites at the file level. As a general guideline, it’s advisable to refrain from sending invitations to external individuals at the project level unless it’s absolutely necessary. Furthermore, Figma allows granting access solely to prototypes within files. This feature is a lifesaver when individuals require visibility into the prototype without access to the underlying design work. These functions combined allow careful control and protect the access of their design files, ensuring collaboration while maintaining data privacy.

6. Sharing should be invite-only

Files sharing is one of the key priorities when setting up secure access to Figma. While public share links may seem quick and easy, they often fall short of providing robust protection for sensitive information. That’s why it’s highly recommended that the default setting for file sharing should be set to invite only. This way, an additional layer of control and accountability is added. By curating a precise list of invited individuals, the Figma file owner can rest assured that only trusted parties can access the file’s contents.

7. Regularly review sharing permissions

Figma file owners should frequently review the individuals invited to access their files. This helps keep invite-only lists in check, keeping them consistently updated (focusing on disabling publicly available links when they’re no longer needed). It not only ensures data security but also safeguards the integrity of the design process. Figma file owners can use this as a proactive measure to mitigate potential security breaches and stay up to date in terms of team access.

8. Handle shared libraries with caution

Shared libraries demand an added level of attention and consideration. It’s imperative to minimize edit access permissions when it comes to critical design libraries. In most cases, this means that individuals outside the team should never have the opportunity to change your design system. By adhering to this stringent approach, you can safeguard the consistency and stability of your design libraries.

9. Enable two-factor authentication (2FA)

The default Figma password protection is inherently vulnerable to various risks like password reuse or exposure through data breaches. 2FA adds an extra layer of authentication beyond just a strong password. It requires the team to provide additional information, typically a one-time password (OTP) or a verification code, usually generated on a separate device. This ensures that even if someone manages to obtain or guess a user’s password, they still need access to the second factor to gain entry.

10. Educate employees about phishing

Many phishing and social engineering attempts rely on tricking users into revealing sensitive information or compromising their accounts. Educating team members about these threats increases their awareness of the tactics employed by malicious actors and may help them to recognize potential attacks. As Figma accounts often contain valuable and confidential information, their hijacking could lead to data breaches or unauthorized modification to design files. Better-educated employees can protect their accounts better, use stronger passwords, and be cautious about sharing account information.

How can NordLayer help?

Figma is a modern necessity for most creatives and designers. With flexible tools to connect everyone in the design process, it helps to deliver better products and services faster. From websites, applications, and logos — Figma allows users to improve workflow and get creative. Yet, its security is a concern requiring finding a balance between security and ease of use.

Secure access to SaaS apps can be easily improved by implementing IP allowlisting with NordLayer. Our tools help to manage access securely, secure network edges, and track user actions across endpoints. Providing an encrypted and secure internet connection safeguards your team’s Figma activity.

Contact us today, and discover how to combine the benefits of Figma with airtight security.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Best practices on cybersecurity budget allocation: a research-based guide

Building a cybersecurity strategy is challenging. It requires more than just technical knowledge and managerial skills but also demands financial resources.

Business budgeting tendencies show that cybersecurity investments receive only a small part of the allocated IT budget. Cybersecurity funds must be distributed wisely to ensure valuable outcomes, prove the chosen security direction effective and minimize resources’ waste.

The main challenge is how to achieve effective security spending. How much should businesses allocate to cybersecurity, and what factors like company size or maturity does it depend on?

According to Statista, information security investments in different categories continuously grow. Projections for 2024 indicate worldwide spending on information security will double compared to 2017.

The trend confirms the necessity of considerable cybersecurity funding. To understand it better, let’s dive into research-based data on how businesses of different sizes and cybersecurity maturity distribute their allocated budgets.

Research methodology

NordLayer surveyed 500 non-governmental organizations across Canada, the United Kingdom, and the United States. An external agency conducted the surveys between March 15 and 25, 2023.

Industries and subindustries represented in the research include business management and support services, e-commerce, education, finance and insurance, health care, information and communication, IT, professional and technical services, and consulting.

The survey explored the organizations’ cybersecurity maturity level (Beginner, Basic, and Advanced), their cybersecurity solutions, and the presence of an in-house specialist or responsible department. It also included questions about cyber incident costs and allocated budgeting for IT and security in the period of 2022-2023.

Companies were segmented by size:

  • Small companies: 1-10 employees.

  • Medium companies: 11-200 employees.

  • Large companies: 201+ employees.

Cybersecurity landscape and the importance of budgeting

The mantra “cybersecurity keeps evolving, so do cyber threats” remains relevant today, emphasizing the need for strengthening business protection measures. As the significance of different types of attacks shifts, mitigating one risk at a time is not a practical solution.

For instance, just last year, ransomware attacks held the top position on the threats list, alerting everyone to stay vigilant. This year, according to Statista, the threat outlook for global companies highlights business email compromise and/or account takeovers (33%) as the most prominent cyber risk surpassing ransomware (32%).

Choosing comprehensive cybersecurity tools and solutions helps to achieve the flexibility needed to adapt to dynamic technological and risk change. A sufficient budget is key, so let’s explore how much companies of all sizes invest in building their cybersecurity strategies.

Understanding the context of digital attacks

Data speaks volumes, so let’s begin by analyzing the culprit behind the need for cybersecurity investments. The survey asked companies about any cyber incidents they encountered in 2022.

The list of top 10 cyberattacks starts with phishing (39%) and malware (34%) attacks firmly holding the first two positions. Despite an intense background of cyber incidents, nearly one-fifth of the companies surveyed didn’t encounter any accidents related to digital threats.

Interestingly, ransomware, one of the most menacing threats recently, appears in the last place (16%) on the list, demonstrating how unpredictable and dynamic the nature of the cybersecurity landscape is. Please note that the frequency of a cyber incident doesn’t necessarily indicate the scale of damage inflicted. 

The scope and type of cyber incidents may depend on a company’s size or the cybersecurity maturity of an organization.

Correlation between cyber incidents and company size

Organizational size usually is misinterpreted in evaluating the likelihood of a cyberattack. Small companies tend to argue they lack valuable assets of interest to malicious actors, requiring less protection.

However, from the first glance at the research data, the trend confirms that medium and large companies are exposed to cyber incidents more often. While 42% of small companies claim they didn’t encounter any cyber incidents in 2022, it accounts for less than half of them.

We observe that insider threats and social engineering attacks are much rarer for small businesses, while data breaches or leaked passwords are more common issues. But phishing attacks (39%) on our list of cyber incidents are equally prevalent across all-sized companies

Large enterprises tend to suffer from malware (43%), social engineering (30%), and insider threats (29%). Compared with the other two categories, medium-sized businesses were exposed most to data breaches (34%) and DDos/DoS attacks (27%).

However, identity theft (27%), compromised/leaked passwords (23%), and ransomware (19%) impact companies with either 11 employees or 201+ to a similar extent.

It’s important not to forget that size doesn’t make one immune. Only the form and approach of malicious actors can differ. Frequency is only one of the aspects to consider when analyzing the intensity of attacks but not the overall impact on business continuity.

Cyber preparedness as digital threat prevention

Company size is more of a predetermined factor rather than an easily controllable aspect of the business. Conversely, cyber preparedness is a decision-based measure of whether an organization invests and focuses on cybersecurity awareness.

Interestingly, higher cyber frequency of attacks is recorded for companies with advanced cybersecurity preparedness. Why is that? A few possible reasons explain this trend.

Cybersecurity maturity is tightly connected with the complexities of creating, providing, and maintaining services and/or products within a company. It also relates to business nature, the processing of sensitive data, and active online presence. 

Companies with a cybersecurity awareness mindset are more likely to assess the risks they face. To mitigate identified risks, security managers implement solutions to prevent, detect, or proactively hunt threats. Monitoring provides explicit data on cyber events or existing breaches, implying that organizations at the basic and beginner level of cyber maturity are less aware of what’s happening under the hood.

Digital advancements increase the attack surface of a company. Factors such as zero-day vulnerabilities, lack of sufficient resources, and incompatible effectiveness of cybersecurity strategy can lead to a higher frequency of cyber attacks, particularly when outsourced services and vendors introduce third-party dependency.

Adversary motivation is common to most malicious actors. These attacks are often based on financial gain or political ideology, but some attackers simply seek the thrill of a challenge. Less cyber-advanced and protected companies are an easy catch, making them suitable for training grounds for attackers compared to more well-protected and globally known companies.

Taking a closer look at the comparison between organization size, cybersecurity maturity level, and the frequency of cyber incidents reveals no distinct deviations.

The main insights imply a weak correlation between insider threats and cybersecurity preparedness levels, while the size of an organization doesn’t seem to impact the frequency of data breaches and identity theft.

Despite the size or cybersecurity maturity, businesses depend on the industry dynamics and the services and data they operate on. The human factor, whether as an internal threat or attacker motivation, is purely a wild card in the context of the cybersecurity landscape, irrespective of the company’s size or preparedness.

Real-life scenario: damage incurred to LinkedIn scam victim companies

Let’s take a real-life example to see how LinkedIn scams, common online threats, affect businesses. The critical part is assessing the inflicted damage and exploring what measures can help prevent such risks.

A LinkedIn scam or fake profile aims to gain illicit funds, either through direct transactions or by gathering personal information that can be used to build a pretext for receiving money. Naturally, the question is, how much do businesses lose in such attacks?

Comparing the damages suffered according to company size, tendencies show that all companies are at risk. Small businesses are the least affected (12%), and medium-sized and large enterprises have to pay the price more often — 22% and 24%, respectively.

Financial damages vary from losses of up to 5,000 in local currency for 33% of companies to 10,000 in local currency for 16% of surveyed companies. These numbers should be considered high as a fifth of respondents could not disclose information regarding their financial losses.

Regarding cybersecurity maturity level, losses increase accordingly — 15% of beginner-level enterprises suffer from financial damage, while 19% of basic-level and 24% of advanced-level companies have declared experiencing expenses.

Does it mean that the more prominent and cybersecurity-developed company, the more risks it is exposed to? Not necessarily, as cyber-ready companies tend to allocate a portion of their budget to IT, particularly when improving their cybersecurity infrastructure.

Research findings on cybersecurity budgeting

Budgeting is an abstract and not clearly defined practice that could be followed by pre-defined recommendations to guarantee success. But it is an important part of business planning, although seen differently by organizations.

Research on cybersecurity budget allocations revealed insights into how enterprises of various sizes approach the same challenges. The following findings are based on overall data, considering company size, cybersecurity maturity, and country unless indicated otherwise.

Budget allocation to IT needs and cybersecurity

IT and cybersecurity budgeting are two different segments of financing. The IT covers overall technology investments, including hardware, software, personnel, and cybersecurity. As cybersecurity is just a fraction of the grand scheme, it explains why budgets can be tight and sometimes even non-existent.

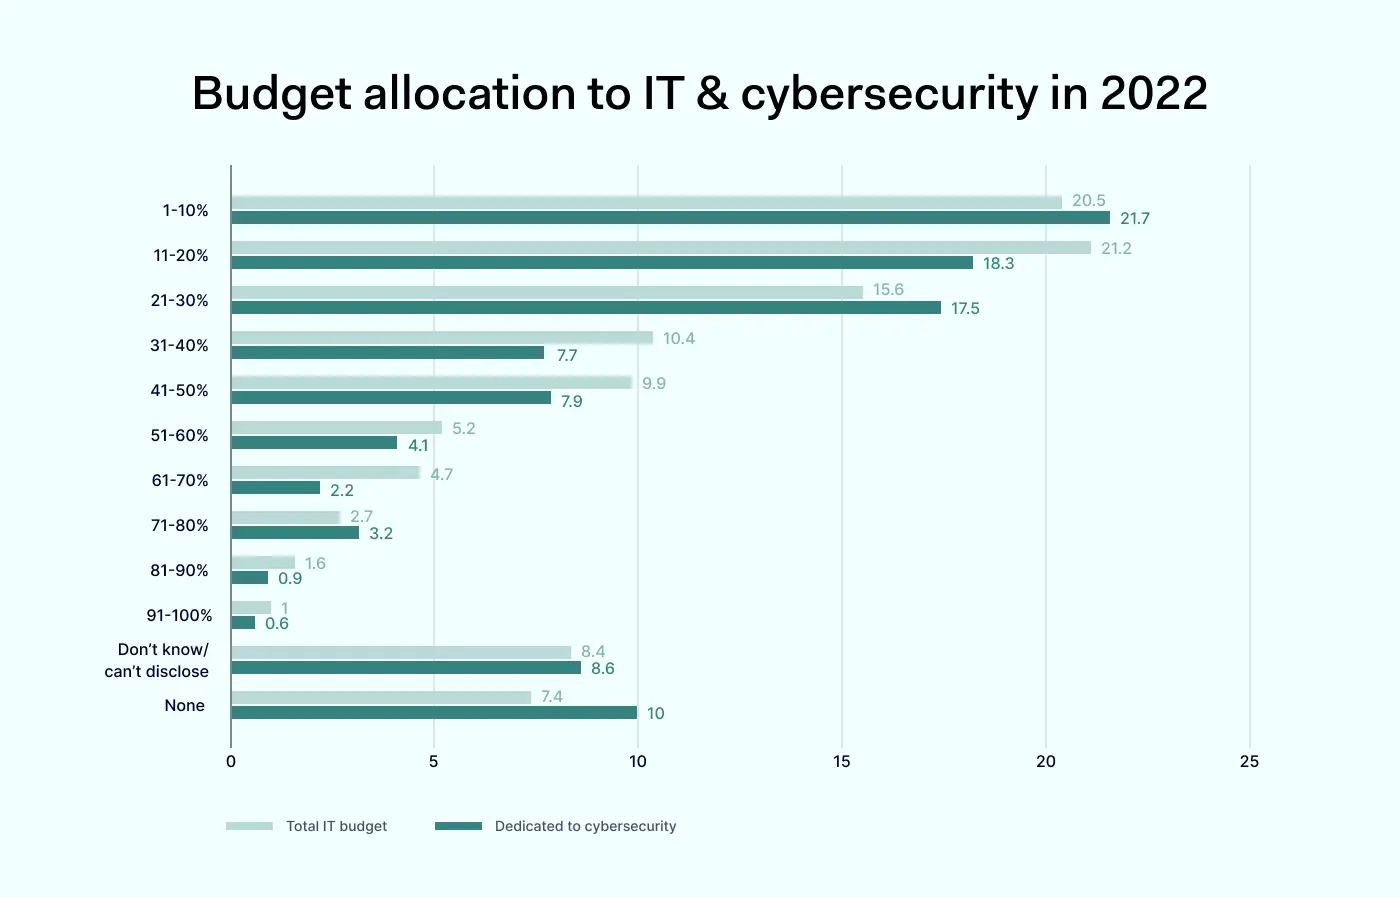
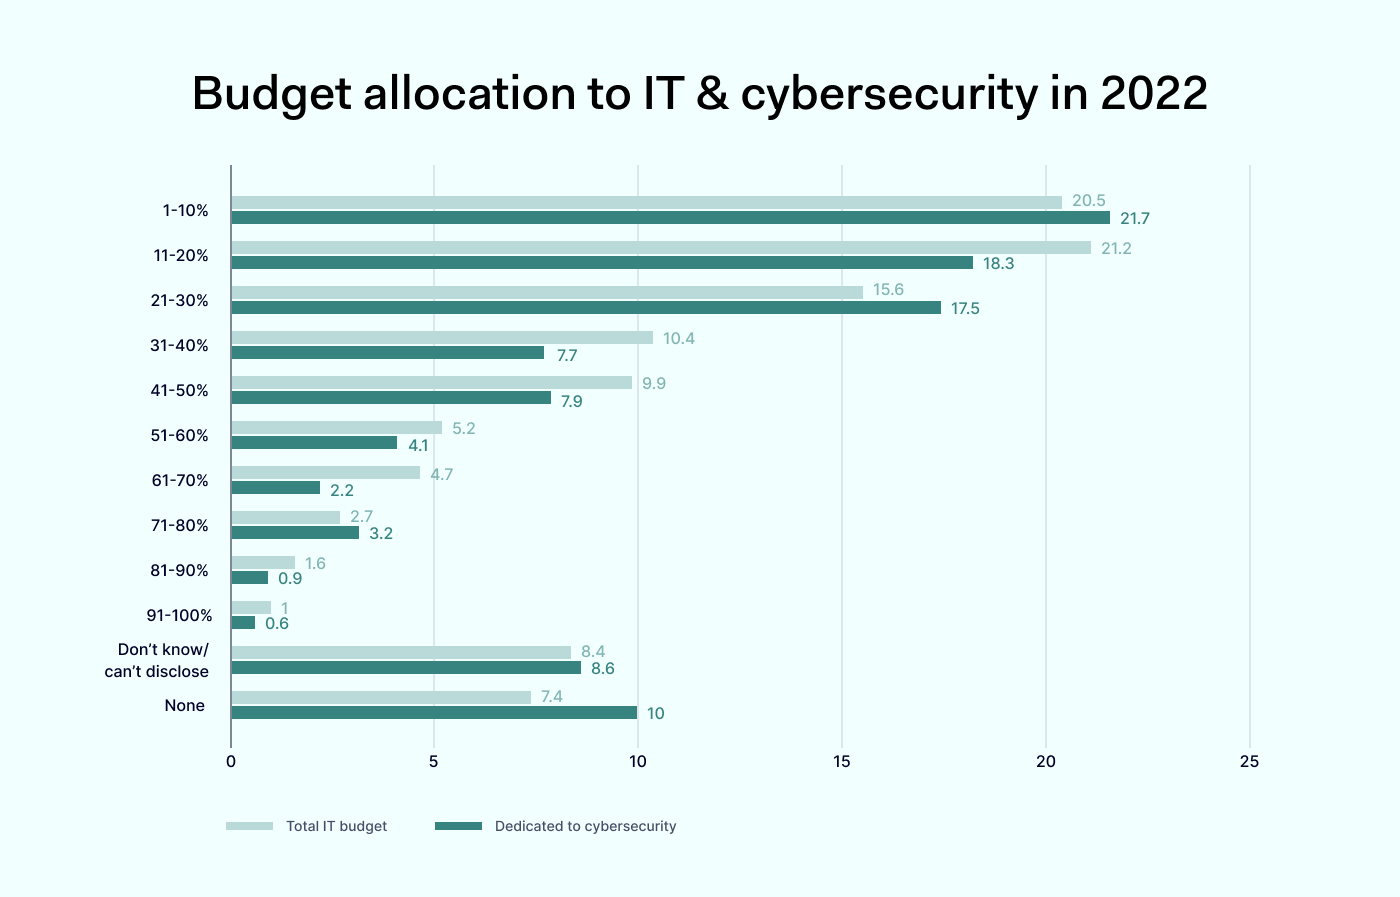
In 2022, over 90% of companies distributed some of their budgets to IT needs. Most companies allocated up to 50% of their financial resources, while only 1% of respondents put all their money into IT spending.

Budget allocation to IT cybersecurity in 2022

Finances allocated directly to cybersecurity spending (besides hardware and software investments) accounted for 84% of received funds in 2022. However, 10% of companies either didn’t find it relevant or had to shift their investing priorities away from cybersecurity. Nearly one-fifth of organizations allocated up to 30% of their funds to digital security.

Half of the small companies mainly invest up to 20% of their budget in upgrading their IT infrastructure. The same tendency appears for beginner cybersecurity maturity-level companies. 14% of small companies and 18% of beginner cybersecurity maturity level organizations chose not to invest in IT needs, while 26% and 31% of these companies did not invest in cybersecurity at all.

On the other hand, large enterprises and advanced cybersecurity maturity level companies tend to allocate more funds to IT, similar to medium-sized companies and basic cyber preparedness level organizations. Large and medium enterprises tended to allocate at least a portion of their budgets to cybersecurity strategy upgrades during the year.

In 2023, the trend shows that fewer companies (88%) distributed company funds to IT needs. Some organizations redistributed their funds to other departments, excluding IT or cybersecurity.

Small and beginner-level cybersecurity maturity companies maintain the trend of investing as little as possible in IT and cybersecurity. In 2023, 16% of small-sized businesses and 19% of Beginner-level companies didn’t allocate funds to IT, which is a negative trend compared to 2022. Yet, 23% of small businesses and 28% of beginner-level companies skipped funding cybersecurity, a decrease compared to last year. 

This leads to the conclusion that although small and unadvanced companies allocate fewer funds to IT, they prioritize cybersecurity to a greater extent.

Medium-sized companies, on average, spend almost 30% of their available budget on IT in 2022. However, this allocation changed to 23% in 2023. Basic cybersecurity maturity level companies maintained a balance of 21-27% of IT funding in the last two years, with a growing tendency. Similar trends can be observed in cybersecurity investments for the same category of organizations.

Large and advanced cybersecurity maturity companies demonstrate stability, consistently allocating an average of 24% of funds designated to IT or cybersecurity needs in 2022-2023.

Investment trends for cyber threats management

Risk assessments and mitigation dictate the cybersecurity strategy of an organization. The strategy is built on security policies, tools, and solutions to implement measures that address the established business protection needs.

The cybersecurity strategy is a process that needs to be monitored, adjusted, and improved for better results. As mentioned earlier, the necessity for flexibility comes from ever-evolving digital environments.

We asked companies which solutions and services they use and what is their future investment focus in cybersecurity.

The list of implemented tools and solutions reveals that companies combine different measures to achieve security. Almost 4 out of 5 companies utilize antivirus software (79%). Secure passwords (65%) and file encryption (64%) are the second-highest priority when creating security policies within organizations.

Virtual Private Networks (VPNs) maintain their popularity in securing organization network connections, with over half (59%) of companies using them. Cyber insurance (45%) is a relatively new solution making its way to business cybersecurity, although its focus is on covering the consequences of an incident rather than preventing it.

Spending on cybersecurity solutions, services, and applications will continue to be a priority (59%) in the 2023 budgets. Raising awareness within organizations is as important as companies providing cybersecurity training and increasing dedicated staff for cybersecurity questions.

Compliance plays an important role in the approach to organizational cybersecurity. External audits and preparation for standard information security certifications are equally in focus (37%). However, 17% of respondent companies weren’t able to disclose their plans for cybersecurity budgeting allocation, and 11% said they had no plans for investing in cybersecurity.

It’s concerning to note that 1 out of 10 companies excluded cybersecurity from their budgeting priorities. 34% of those organizations are at the beginner-level of cybersecurity maturity, and 28% of small-sized businesses. Regarding the country, 8% of companies in the United States, 7% of Canada, and 5% of the United Kingdom companies cut their cybersecurity investments for the ongoing year.

Yearly comparison of cybersecurity investments

Plans for 2023 show a slight change but a clear strategy for businesses with advanced cybersecurity maturity. Purchasing security solutions, services, and/or applications is the top priority, accounting for 70% of planned costs. In addition, there is a strong focus on employee education (70%) and increasing staff for cybersecurity questions (63%).

Attention to organizational preparation for information security certifications grew from 46% in 2022 to 51% in 2023. The data implies that businesses are strengthening their cybersecurity strategies to be more aware and self-sufficient in protecting company assets.

Beginner-level cybersecurity maturity companies fluctuate between 20–30% in the same categories. It indicates awareness present with yet too little security spending allocated.

These companies are smaller, thus easier to manage their scale and exposure to digital threats. For sustainable growth and security, the mindset shift is expected to be cyber-ready for driving large-scale organization protection.

Best practices for developing cybersecurity budgets

Research revealed that cybersecurity spending depends on different factors. It plays a small yet important part in the overall business lifecycle. Investing in cybersecurity is highly recommended to ensure organizational growth and business continuity.

To allocate cybersecurity budgets effectively, evaluate all the components influencing costs, decision-making, and further strategy development. This includes staying vigilant and proactive, planning responsibly, reusing resources (talent, tools, processes) sustainably, and aiming for growth.

Key takeaways: how to identify, estimate, and prioritize security investments

Survey data shows that some companies invest in cybersecurity generously, while others, especially small businesses, tend to refrain from security funding. Naturally, the reason behind it can be related to limited resources, underdeveloped infrastructure and processes, and l time constraints.

Yet poorly protected businesses suffer harder from a cyber incident. Only luck, not size or brand awareness, influences when and how threat actors will target an organization.

Key takeaways

1. Acknowledge the change in the cybersecurity landscape

The first step for all decision-makers in the company, from a Chief Information Security Officer (CISO) to Managing Director, is to be aware of cybersecurity challenges and the vulnerability of their business to cyber threats.

Remember about technology upgrades from hardware to cloud-based environments for more resilience and flexibility. Malicious actors look for security gaps to exploit zero-day vulnerabilities.

2. Assess business-affecting risks

All organizations face the risk of cyber-attacks. Some industries have more red flags than others due to the nature of the data they process. The exposure to cyber threats can vary depending on the type of service or product the organization provides or the company’s maturity.

Understanding what security risks, threats, and scenarios your business is most exposed to is crucial to assess security measures correctly.

3. Investigate internal goals

First, investigate how the company’s budgets are allocated to different needs. What are strategic goals and business development objectives to find the place and role of cybersecurity in the organization?

Examine how the company meets compliance and aligns with stakeholders’ requirements. Are there any plans to seek certification from regulatory compliance providers, such as HIPAA for healthcare providers? Certification is a process that requires dedicated resources and, at the same time, provides guidelines for building a more robust cybersecurity strategy.

4. Audit solutions and best practices

Review your security strategy. To some extent, policies, procedures, and tools should already exist unless it’s the very beginning of a company. See what needs improvement and identify what gaps must be addressed as soon as possible.

Are there any processes that could be consolidated or solutions that aren’t used to the fullest? Companies tend to invest in applications – review what apps are utilized and if they satisfy business and user needs.

5. Plan a cybersecurity strategy

Cybersecurity strategy starts from a mindset within the company. The main elements that require continuous investment planning combine:

  • Tools & solutions.

  • Employee security training and development.

  • Dedicated staff, consultants, and outsourced services.

  • Developing backup plans for different threat scenarios to ensure a stable business lifeline.

6. Implement cybersecurity tools and policies

After evaluating the business needs for security, select solutions and tools that best suit your case. It’s beneficial to have demo calls with vendors and have a trial period to test tool adoption within the organization.

Once chosen, deploy tools, upgrade policies, and onboard the team to the new cybersecurity strategy.

7. Review & adapt to business needs

Implementing a solution and introducing new processes doesn’t end your cybersecurity strategy journey. Test, monitor, and confirm its effectiveness. Ongoing monitoring requires a dedicated team to ensure a smooth transition to a new way of working.

Whether your organization chooses to have an in-house or outsourced dedicated cybersecurity staff, it is important to allocate the necessary investments. It is recommended to choose a solution that is sustainable and easy to manage.

8. Update & make cybersecurity an ongoing process

Work on new and follow-up business initiatives in accordance with your cybersecurity strategy. Investigate what areas need changing, upgrades, and improvements for another implementation cycle.

Coherent tracking and planning help make next year’s cybersecurity budget easier. It is essential to invest in security training, tools, and dedicated employees in the company and view security as continuous learning and growth.

Following recommendations for cybersecurity budgeting

Finances and the effective allocation of limited resources is a sensitive and complex topic for any organization manager responsible for business planning. This research sheds light on the industry trends regarding how companies approach cybersecurity funding, which is ultimately connected to digital threat prevention.

Further investigation and insights are beneficial for informed planning, so explore other materials from NordLayer for a better understanding and planning of the cybersecurity budget:

Cost-benefit analysis of cybersecurity spending

A comprehensive analysis of cybersecurity costs and factors affecting them, benefits of cybersecurity spending, and how to apply it to your organization. In the article, you’ll find more comprehensive information on specific solutions and tools, security spending projections on dedicated cybersecurity staff, and other nuances influencing the cybersecurity strategy.

The study helps better understand the subject and find convincing arguments for discussions with other decision-makers.

Decision Maker’s Kit

This content support platform is dedicated to assisting decision-makers in choosing, explaining, and onboarding their selected cybersecurity solution within their organization. From strategical to explanatory materials, prepared templates, and documentation, the platform provides a better perspective on what’s required and expected when building a cybersecurity strategy for a business.

Projections on security budgeting for 2023

An overview of how much companies plan to allocate to cybersecurity in 2023, considering different factors. The article covers building a budgeting strategy, assessing the expense gap, and exploring investment alternatives such as the cost of a data breach.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

A tour of Nord Security’s new office in Cyber City

It’s official: All Nord Security products have finally moved under one roof at Cyber City. It’s the ultramodern destination for our community that sets a new standard for our employee experience. Dive into this blog to discover what life and work look like at one of the most cutting-edge tech offices in the Baltics.

Our brand-new HQ

In 2020, we started an exciting journey by laying the foundation of a brand-new office that could accommodate our fast-growing community and encourage a collaborative company culture. May 2023 marked the end of this journey as we transitioned over 900 employees from NordVPN, NordLayer, NordPass, and NordLocker to one of the most cutting-edge tech hubs in the Baltics, Cyber City, nestled in the heart of Vilnius, Lithuania.

Tom Okman Eimantas Sabaliauskas


Tom Okman and Eimantas Sabaliauskas, co-founders of Nord Security

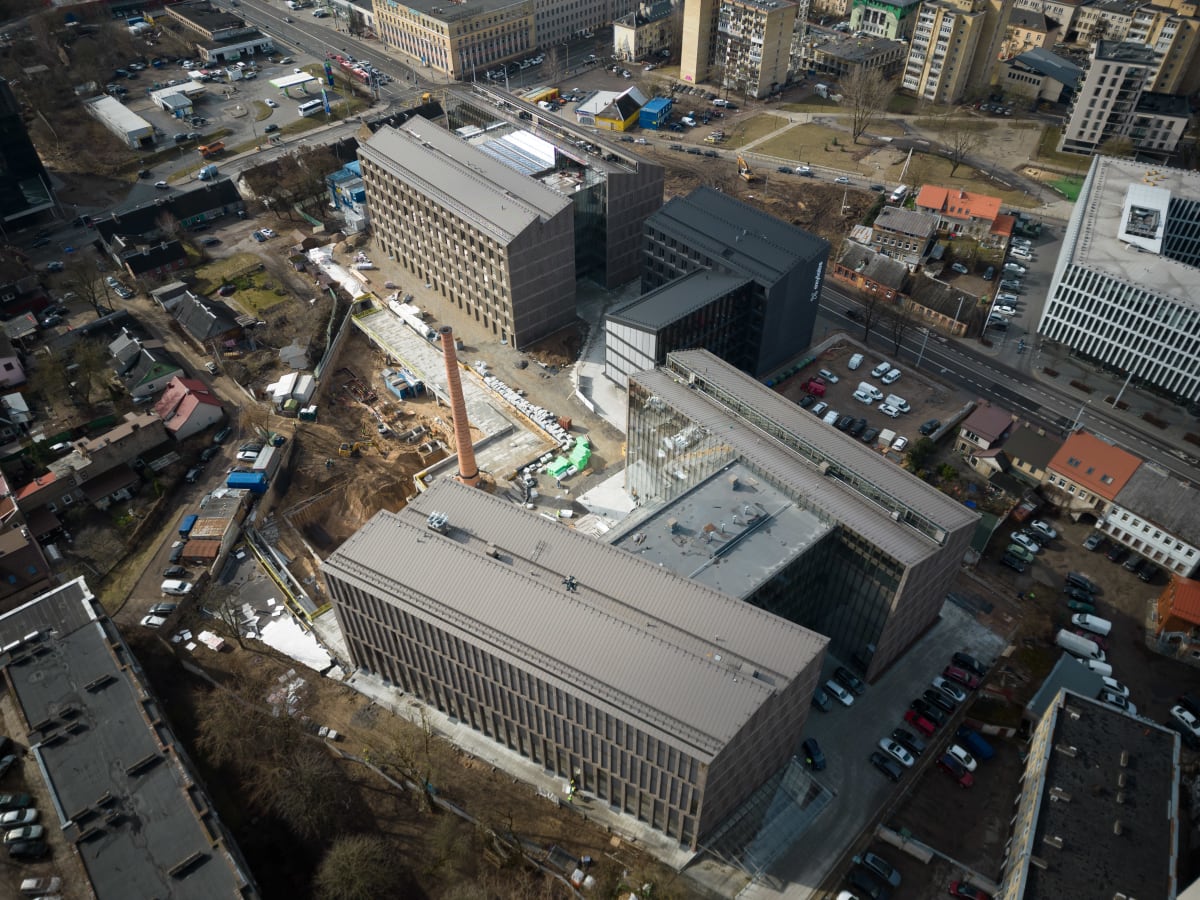
Located on the grounds of the former “Sparta” textile factory, our new headquarters is a testament to its industrial past. The exterior design of our tech hub mirrors textile patterns, while the preserved iconic chimney standing tall in the heart of our business campus serves as a powerful symbol of our relentless ambition – to build future-shaping cybersecurity solutions from the ground up.


Nord Security office is located on the grounds of the former “Sparta” textile factory

Our state-of-the-art HQ building, housing Nord Security, Surfshark, Oxylabs, CyberCare, Hostinger, and other Tesonet community companies, is located on a 35,000 m2 site. Spanning seven floors, our new premises come with a wide range of features (see for yourself below) that raise the bar for our workforce culture.

Cultivating growth and creativity

The Cyber City business hub is the new Silicon Valley of the Baltic states, where the top tech talents and companies meet the best conditions for work, growth, and innovation. With this in mind, our HQ office features:

  • Ergonomic co-working spaces for all-day comfort.

  • 106 meeting rooms built-in with cutting-edge technology (smart cameras, easy room booking, and presentation systems) for seamless onsite and remote collaborations.

  • Modern conference hall and spacious atrium, perfect for hosting internal events, quarterly celebrations, and company-wide festivities.

  • A state-of-the-art production studio for elevating our content creation.

  • Dedicated silent zones for focused, uninterrupted work.

  • Music room equipped with an array of musical instruments for solo improvisation or collaborative jams with colleagues.

  • Hacker and innovation room for team building activities and LAN parties, exploration of groundbreaking tech, captivating video shoots, and immersive tech tours.

  • IQ lounge – a zone full of books and magazines stimulating curiosity and never-ending learning about art, architecture, science, and technology.

Ciber City office premises 4
Ciber City office premises 2
Ciber City office premises 5
Ciber City office premises 1
Ciber City office premises 3
Ciber City office premises 8
Ciber City office premises 7
Ciber City office premises 9
Ciber City office premises 6
Cyber City office premises 10

“What I absolutely adore about our office is the flexibility to work from different locations. Yes, we all have our dedicated spaces, but when you need that extra bit of focus or solitude, you can go and work in silent rooms. You can sit on the couch in the corridor or our spacious atrium if you want more comfort. And if you’re going to discuss your projects with someone in a more informal setting, our kitchen or coffee bar might be just perfect. There’s a place for every mood, every task, and every moment of your working day. Now, if I had to pick a personal favorite, it would be the lighting. I tend to be quite sensitive to harsh, bright lights, which give me headaches and eye strain. But here, it’s all warm, soothing light. It creates a calm and inviting atmosphere that’s just a pleasure to work in,” Ugnė Mikalajūnaitė, Country Manager at NordVPN, Nord Security.

All these forward-looking amenities, coupled with the growth opportunities Nord Security provides, be it internal training, online courses, mentorship programs, or Tech Days knowledge-sharing events – we build an environment that helps our employees stay at the top of their game.

Nord Security events 9
Nord Security events 8
Nord Security events 7
Nord Security events 3
Nord Security events 10
Nord Security events 6
Nord Security events 5
Nord Security events 4
Nord Security events 2
Nord Security events 1

Nurturing a thriving community

At Nord Security, we believe in the power of teamwork. With this in mind, we wanted to have all our products under one roof, so we could foster a sense of community more easily.

Cyber City office Toma Sabaliauskiene


Our open co-working spaces, inviting dining areas, cozy coffee spots, and the iconic “Sparta” bar provide a wealth of opportunities to connect and engage with people from different teams and products. And for some light-hearted fun with colleagues, our game room awaits, packed with board and tabletop games, as well as the most popular gaming consoles.

Cyber City office Rita Sereivaite


At last, Cyber City not only offers a collaborative work environment but also cultivates our community spirit through celebrated events. One such event was the grand opening of Cyber City, marking the official start of our new life in this state-of-the-art tech hub.

Ciber City Opening Party 9
Ciber City Opening Party 5
Ciber City Opening Party 2
Ciber City Opening Party 1
Ciber City Opening Party 3
Ciber City Opening Party 7
Ciber City Opening Party 10
Ciber City Opening Party 8
Ciber City Opening Party 12
Ciber City Opening Party 14
Ciber City Opening Party 13
Ciber City Opening Party 15
Ciber City Opening Party 17
Ciber City Opening Party 18
Ciber City Opening Party 16
Ciber City Opening Party 19

Enhancing work-life balance

A strong focus on work-life balance is what keeps our results and motivation at their peak. As a result, we follow a hybrid work model, giving us the freedom to connect with our colleagues at the office three days a week and enjoy the comfort of remote work for the remaining two. Not to mention flexible working hours when needed and the opportunity to work from abroad.

Having so many people passionate about sports and an active lifestyle, we can enjoy group training and well-being consultations in Cyber City led by in-house Physical Well-Being Team experts, saving us both time and money. And those who prefer individual workouts have free 24/7 access to a fully-equipped gym.

Cyber City office Deividas Armonas


For our working parents looking to strike the perfect work-family balance, we’ve established a dedicated parents’ room. Whether it’s an unexpected school closure or a need to share their workplace with their little ones for a few hours, we’ve got their back. This dedicated space ensures that extra bit of peace of mind when it’s most needed.

Cyber City office Arnas Aukstikalnis


The future starts here

Our brand-new workspace was tailor-made with Nord Security people in mind. Its environment mirrors our values, respects individual needs, and fosters a shared culture, sparking creativity and promoting a collaborative atmosphere.

Plus, it creates ample room for fresh talents ready to join our mission of shaping a safe cyber future. Does that sound like you? Check open positions at Nord Security and learn more.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.