Skip to content

Scaling affiliate marketing: Top tips from Nord Security’s Jonas Kupreščenkovas

Nord Security’s affiliate partnership manager, Jonas Kupreščenkovas, shares a few tips on how to scale affiliate marketing and what to keep in mind when venturing deeper into the affiliate marketing model.Strategic planning is of the essence here, not to mention a deep understanding of the product, the niche, and audience. 

Affiliate marketing has been gaining traction in recent years as a digital marketing strategy and has become one of the more popular ways to generate passive income for affiliates. Affiliate marketing is growing at a 10% rate year over year. It’s important both for potential affiliates and businesses to understand affiliate marketing and the many ways to scale to fully utilize this advertising model. Quick definition: Affiliate marketing is when third-party publishers (affiliates) are compensated for promoting products and services from an advertiser (brand). For each sale or lead made via their channel, the affiliate receives a commission.

1. Narrow your focus on specific niche

A niche is a specialized market segment when it comes to a particular service or product. Keep in mind: Niches are not made equal. What is more general may be easier to market but also has bigger competition. What is more difficult to market has the challenge of being able to reach the target audience. However, choosing a less popular niche doesn’t mean you won’t be able to sell; it just means that you’ll have your work cut out for you.

It may sound redundant, but if you’re starting from scratch, pick something you’re interested in. Not only will you be able to add to your content from personal experience, it will also be easier to build the niche further on. Having specific knowledge on a topic is an advantage.

Moreover, if you choose products to promote based on your niche and interest, it will be more genuine and to the point rather than choosing everything that comes your way.

2. Understanding what your audience wants

One of the main key points when it comes to affiliate marketing is understanding your audience. While some may encourage covering many different topics, products, and services, it is highly important to understand what kind of audience you have. What are their needs and pain points? Also, what kind of platform you run and what your primary topic or field of expertise is.

If you’re selling cybersecurity products and talk only about that, would it make sense to your audience if you started selling socks? The ability to personalize and deepen your audience’s preferences is the ability to effectively maintain their attention. Building an audience that wants to come back and considers you an authoritative source is the most important thing here.

3. Quality content is still king

A flashy thumbnail or ad might draw people to you but quality content is what makes them stay. Therefore, the previously mentioned niche selection and the knowledge of your audience are extremely important. Your audience knows when you understand the topic and provide valuable information rather than just trying to fill a gap. Expertise and genuine interest goes a long way here, and proving it in your content is the first step to gaining substantial visitorship and an audience that keeps coming back for more.

Don’t forget to mix and match when it comes to different content types – informational vs. sales-focused content . Informational content may not earn you millions, but it will strengthen your authority and give you a better chance to rank on SERPs, while various guides, “best” articles, keywords including “review”, “alternatives”, “X vs X” are also great to target those who already have buyer’s intent. SEO knowledge is a big advantage when it comes to driving an audience to your content as it improves the visibility of your website. Close to 80% of affiliate marketers use SEO to bring traffic to their website.

Anything content-related should be of high quality, engaging, and relevant to your niche and audience. Avoiding overly promotional content is recommended; Balance is key, as long as you’re not being spammy or providing empty and useless content, you should be fine.

4. Diversifying your traffic

Want to bring more people to your site and have more stability in your website traffic? Diversification of content is crucial here, not to mention that it will help with scaling your efforts. Paid advertising, social media, and newsletters can help you reach a wider audience. Over 65% of publishers use social media to reach their target audience. From personal experience, we at NordVPN saw recent success with sports teams like Atlético de Madrid, Hibernian FC, and Ipswich Town. Pushing a dedicated newsletter to fans saw significant growth in performance and partnership visibility. A similar situation played out on X, where a single post announcing a partnership drew in almost 200,000 views.

Tailoring your content across a variety of traffic sources works best; don’t forget to A/B test and experiment with content to find what works on certain channels and sources. Depending on your niche, you can find many opportunities, but do some research beforehand to find where your target audience spends time.

If you’re feeling brave, you can expand to new markets and adapt your content as well as affiliate marketing tactics based on the preferences of foreign audiences. However, it’s important to understand that you not only will need to localize your content but also research the buying habits of your target markets. Selling to different countries is not easy and requires an understanding of local market conditions and dynamics. For example, Facebook, X and other well known social networks may not be as popular in Asia, where WeChat and QQ are better known.

5. Tracking your performance

Don’t just slap everything together in the hope that it will work the first time around. Test and track, test and track. Try different promotional strategies, content layouts, and such to see what (or who) works best. Track main metrics like clicks, conversion rate, and impressions to have a better grasp on what works and what doesn’t. Maybe your new theme is confusing? Maybe the radical changes made in content tone put off the audience? Check data and make data-driven decisions to ensure long-term success.

It’s a continuous effort to find what works best, and it’s never set in stone. Constant campaign tracking, conversion rate and content optimization are a must. Why put so much effort into this? To about 30% of web publishers affiliate marketing is one of the top revenue sources. Affiliate marketing keeps you on your toes, and that is one of the most exciting things about it.

6. Working together with your affiliate partnership manager

A dedicated affiliate partnership manager can provide you with valuable information and insights when it comes to scaling. They can provide you with the unique selling points of products and services, come up with various strategies to elevate your marketing efforts, and more. Also, at NordVPN, being up to speed on key global events and time sensitive topics are key for any affiliate strategy. If you’re the first to work with partners on a topic that’s starting to trend, you’re bound to see the best results and the largest chunk of the traffic compared to those that jump on the opportunity second or not at all. Therefore, it’s important both for the affiliate partnership manager and the publisher to always track and be on top of various news and trends.

Affiliate marketing managers are always ready to help you as they want you to succeed in your endeavors and can provide feedback, content opportunities, visuals, and more. Most will provide you with tips and guides that will help you build your content accordingly.

To conclude, scaling affiliate marketing demands a constant thirst for information on part of the content creator, as well as consistent improvement, optimization, and a deep understanding of your niche and audience. These tips can help you out to create a good income source though it all comes down to you and your ability to adapt to constantly shifting trends, new social media appearances, and changes in the marketing and consumer landscape.
 

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

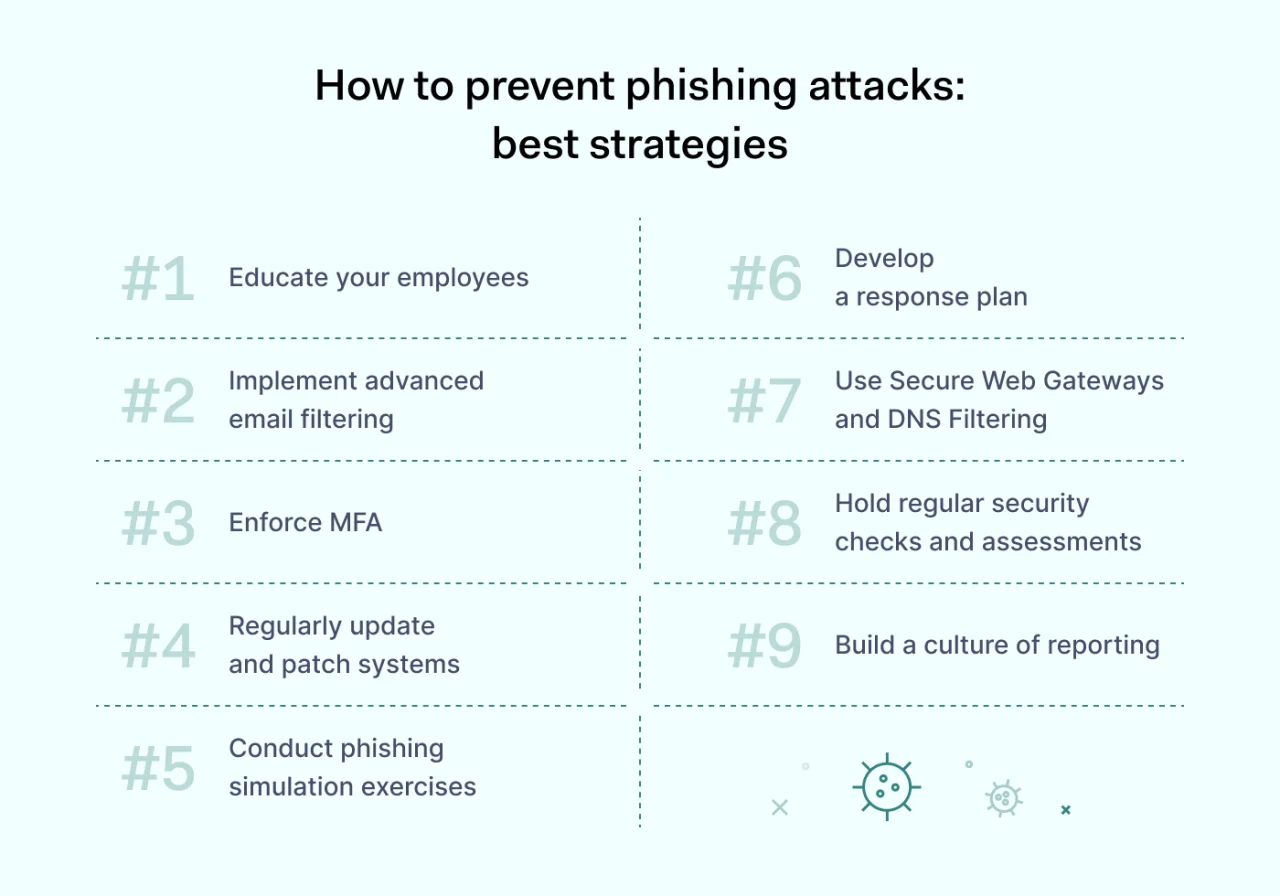
How to prevent phishing attacks: best strategies

The term ‘sandworm’ might make many people think of the ‘Dune’ movie. Yet, it is also the name of a group actively involved in manipulating elections. 

Over the years, Sandworm has meddled with elections to sway outcomes and interrupt political processes. This includes the 2016 US Presidential Election, the 2017 French Presidential Election, and various electoral processes in Ukraine.

Sandworm often begins its attacks with phishing. This technique isn’t just for tricking people into giving away their credit card information on fake websites. It’s a significant threat to businesses and, by extension, to national security, as companies can sometimes be the weaker link.

Learning about phishing is crucial. Let’s discuss it in a way that’s clear, easy to remember, and practical to use.

Key takeaways

  • Phishing comes in various forms, such as email phishing, spear phishing, whaling, smishing, and vishing.

  • To identify a phishing attempt, look for signs such as suspicious email addresses, generic greetings, spelling and grammar errors, urgent language, requests for sensitive information, and dubious links or attachments.

  • Educating your employees about anti-phishing techniques and promoting a culture of security awareness are crucial steps.

  • Enforce multi-factor authentication (MFA) to add a layer of security, making stolen credentials insufficient for accessing sensitive data.

  • Phishing simulation exercises can test your team’s detection skills and significantly improve your anti-phishing defenses.

  • Develop a response plan that outlines clear steps for reporting phishing attempts.

  • NordLayer helps mitigate phishing attacks by assisting in implementing the Zero Trust Network Access (ZTNA) framework and offering Threat Prevention features, which strengthen your organization’s defenses against phishing.

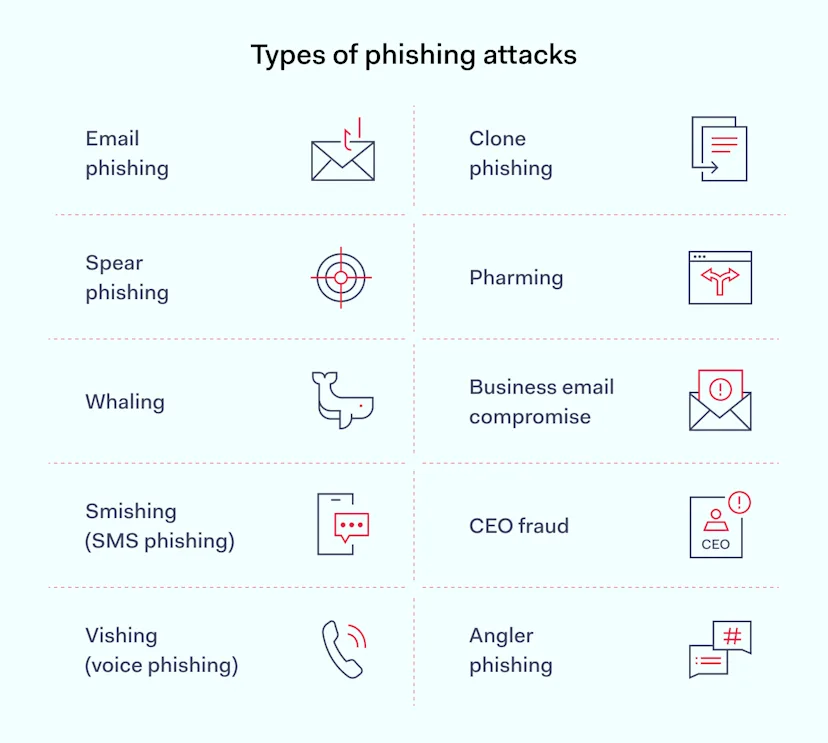
Types of phishing attacks

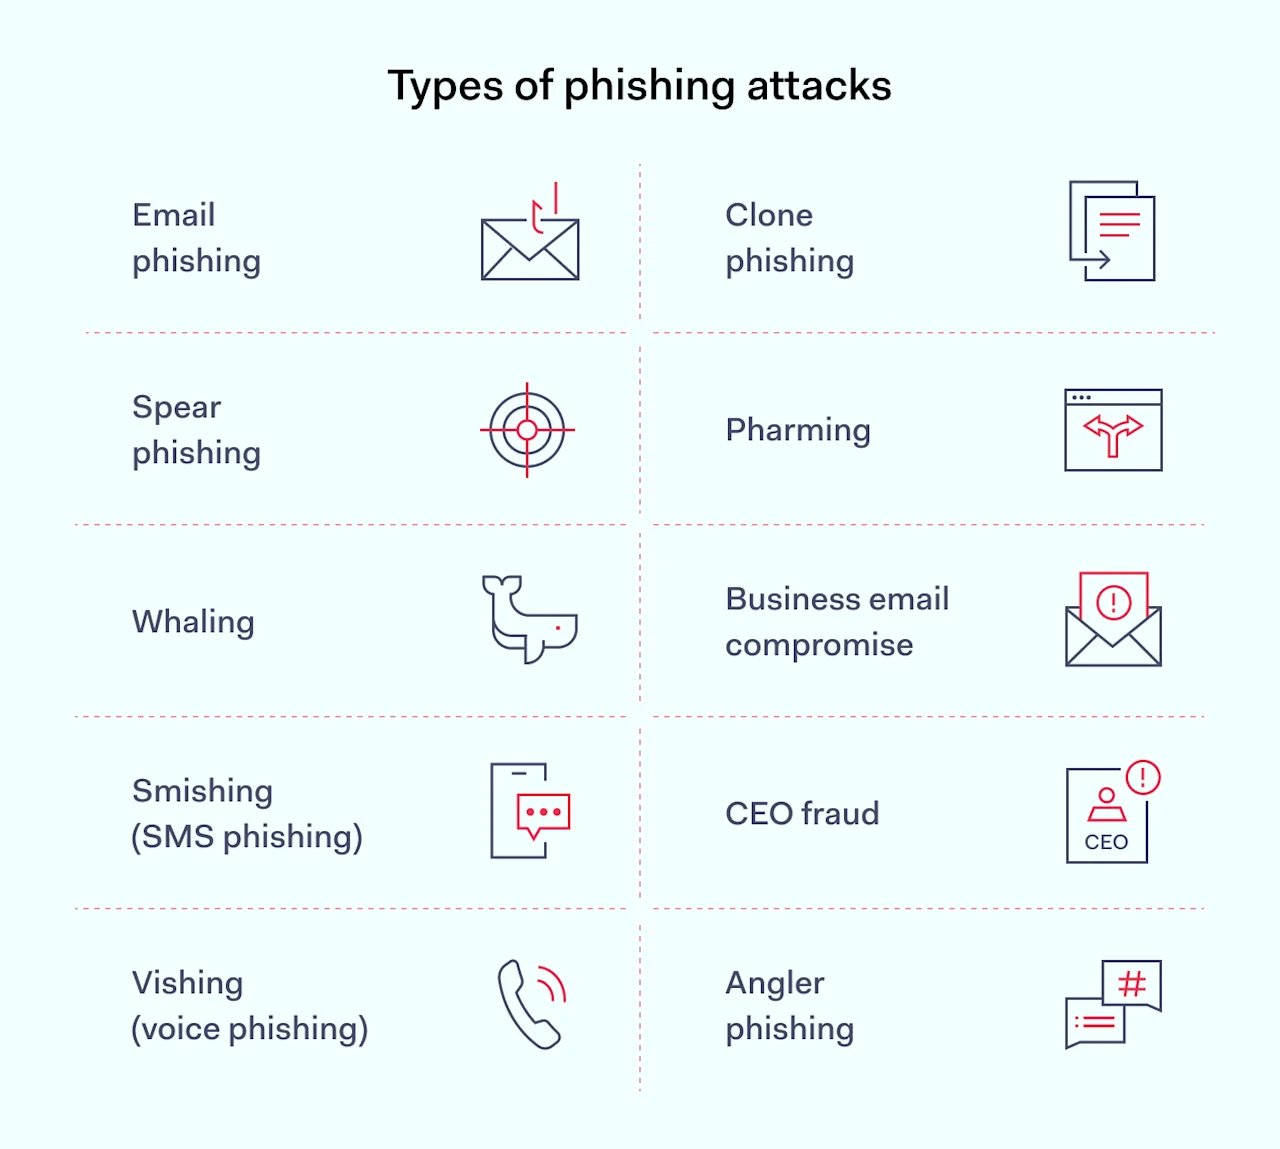
Phishing attacks come in various forms, each with its own tactics to trick victims into sharing sensitive information.

Common types of phishing attacks

  • Email phishing is the most common, where attackers send fraudulent emails, mimicking legitimate organizations to steal personal data.

  • Spear phishing targets specific individuals or companies, using tailored information to seem more convincing.

  • Whaling focuses on high-profile targets like company executives, using sophisticated social engineering techniques.

  • Smishing and vishing involve sending text messages and making phone calls, respectively, to lure victims into revealing information or downloading malware.

Real-life examples of phishing

Phishing continues to be a significant problem. Recent studies show that phishing attacks have hit 94% of organizations, and 96% of them experienced negative impacts from the attacks. Adopting strong anti-phishing strategies is still very important.

  1. In June 2023, a North Korean threat actor launched a sophisticated phishing attack on JumpCloud, a platform for identity management. They tricked a software engineer, which led to a security breach. This gave the attacker access to JumpCloud’s systems, which allowed them to interfere with operations. The team quickly noticed the unusual activities and immediately took steps to limit the damage, including changing credentials and rebuilding systems. However, JumpCloud has not shared details about whether any information was leaked from the affected devices.

  2. In February 2023, Reddit showed how to handle a phishing attack effectively. The company was the target of a phishing attempt that fooled employees with fake alerts, leading them to a website designed to look like Reddit’s own intranet. This phishing attempt obtained some employees’ credentials, which gave unauthorized access to Reddit’s internal documents and source code. Quickly reporting the incident by an employee who got phished was key to Reddit’s swift action and investigation. This situation highlights the importance of quickly reporting phishing emails to mitigate phishing attacks. It also shows how spam filters and multi-factor authentication prevent phishing attacks and protect sensitive information.

  3. In 2019, Magellan Health, a company that provides managed care services in the U.S., experienced a phishing attack. This incident exposed the personal and health-related information of about 270,000 people. It seems an employee, without realizing it, gave away their login details to the attackers. This mistake led to unauthorized access and the spread of spam emails. Magellan Health has decided to settle the claims for $1.43 million, although they don’t admit any fault and state there’s no proof that the information was actually misused.Biggest-data-breaches-of-2023

How to identify phishing attacks

The arrival of generative AI has made spotting phishing attempts tougher. These advanced tools create very convincing messages, so staying alert is more important than ever. However, looking out for specific warning signs is still an essential way to guard against phishing attempts.

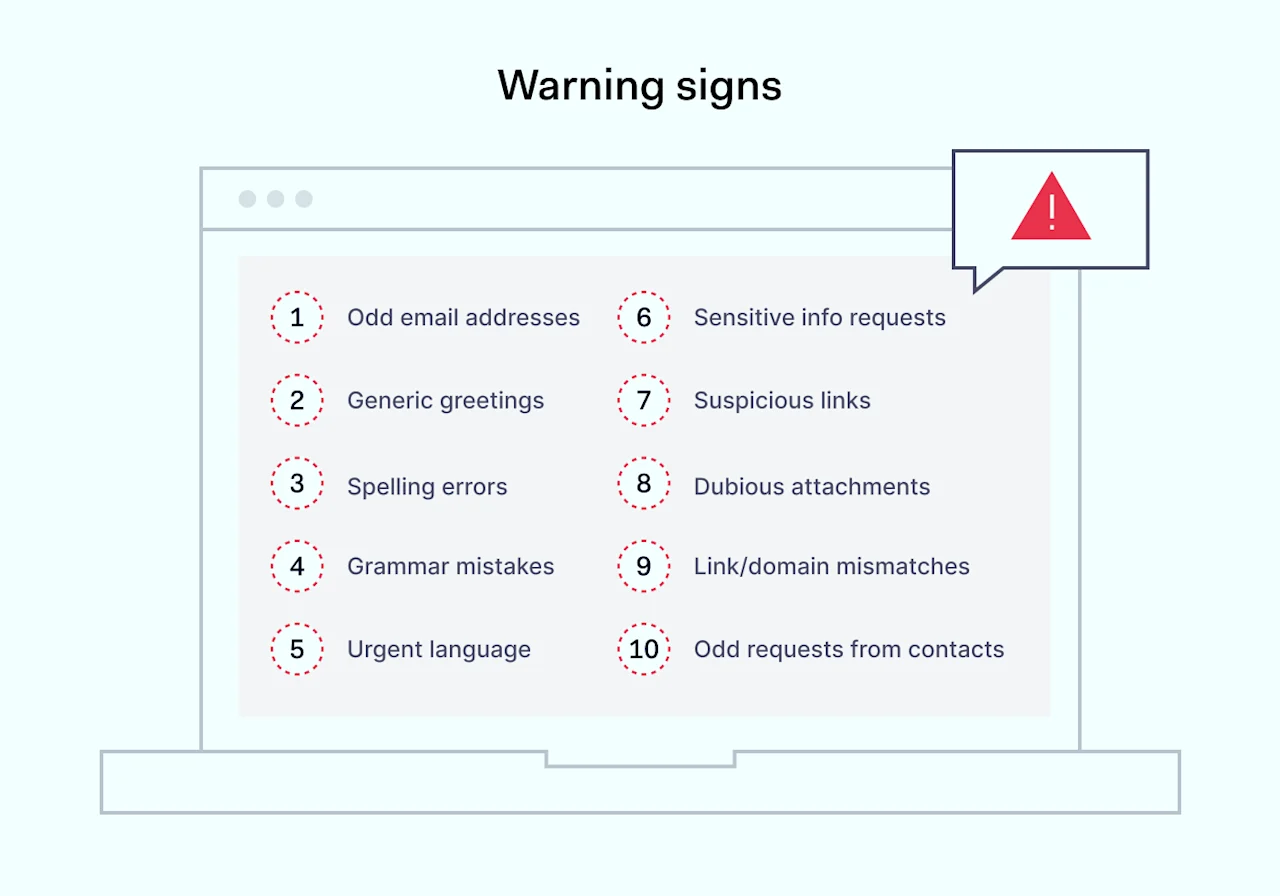
Phishing signs

  1. Email addresses that look slightly off are often the first sign of a phishing attack. Attackers mimic legitimate company addresses with small changes that are easy to miss. For example, getting an email from “support@amaz0n.com” instead of “support@amazon.com” is a clear warning sign.

  2. When an email uses a generic greeting like ‘Dear Customer’ instead of your name, it might be a phishing attempt. Real companies know your name and use it to talk to you directly, making communication more personal.

  3. Mistakes in spelling and grammar are telltale signs of phishing emails. Authentic companies make sure their messages are error-free. An email full of errors should make you pause and think. Also, spotting things like ‘[enter the name]’ or typical ChatGPT commands in an email should alert you. These signs can indicate the email may not be trustworthy.

  4. Phishing emails often use urgent language to make you feel panicked. If an email pressures you to act fast to avoid negative consequences, like losing access to your account, be skeptical.

  5. Requests for sensitive information through email should always be a red flag. Genuine organizations won’t ask for your passwords, Social Security numbers, or credit card details in this way.

  6. Be cautious with links and attachments in emails. Checking where a link goes before clicking on it and being careful with unexpected attachments are smart ways to avoid phishing traps.

  7. Differences in links and domain names can expose a phishing email. If these elements don’t match up with the actual company, it’s likely a scam.

  8. If you get an email from someone you know that doesn’t seem right, like asking for odd things, it could mean their email is part of a phishing scam. This is a tactic to catch you off guard.

How to prevent phishing attacks in your organization

Phishing attacks are common yet serious threats to steal organizations’ sensitive information. To protect against these attacks, combining education, technology, and vigilance into a comprehensive strategy is essential.

Phishing prevention best practices

Educate your employees

Teaching your team about phishing techniques is crucial. Stress the importance of checking for email misspellings, the dangers of clicking on unknown links or attachments, and how to report anything suspicious. Building a security-aware culture helps everyone play a part in preventing phishing attacks.

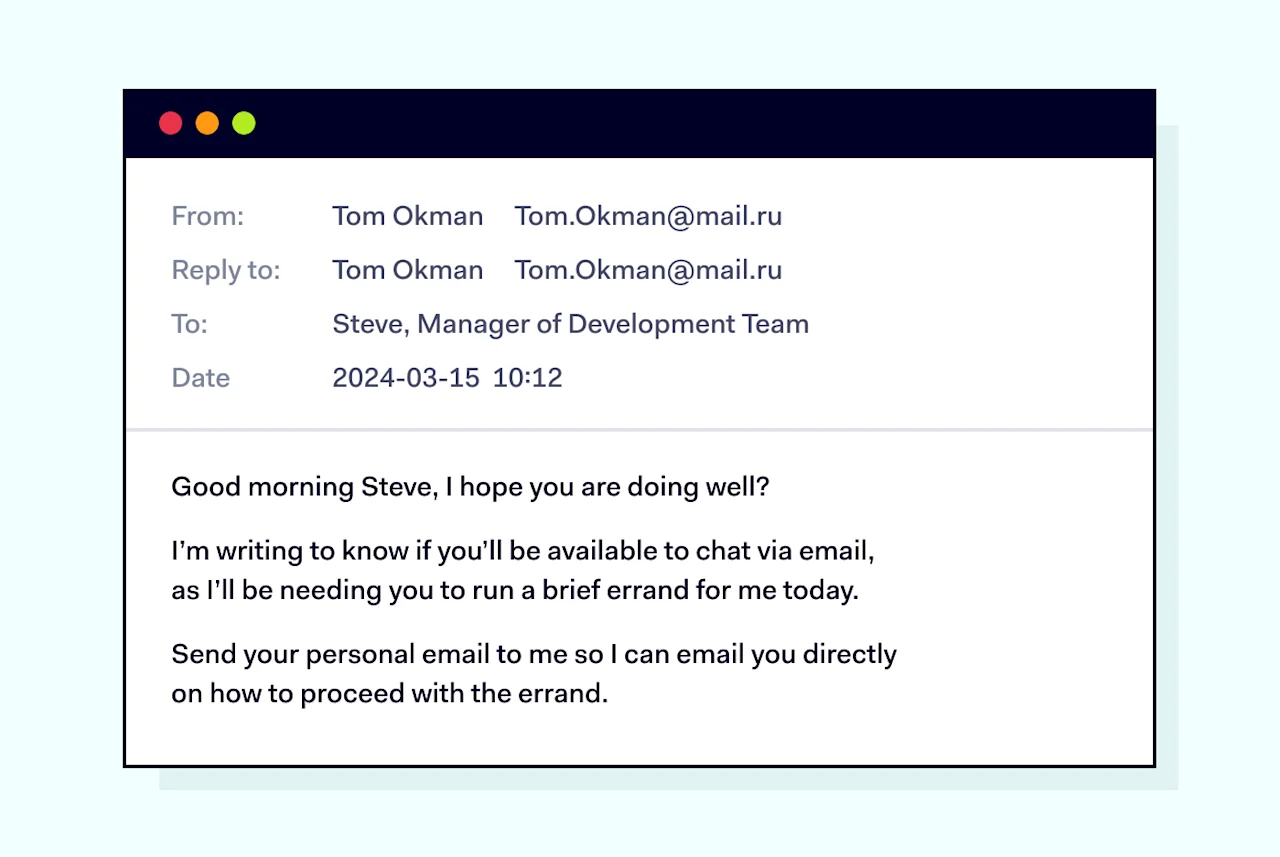
For example, lately, Business Email Compromise (BEC) has become a major cybersecurity concern. This scam involves sending targeted phishing emails to steal money or data from companies. A typical example is CEO fraud, where scammers, pretending to be the company’s CEO, ask employees for urgent money transfers. These requests could be for settling invoices, closing deals, or even buying gift cards, often urging quick action or demanding secrecy.

Some BEC attempts are easily recognized, like the one our colleague got:

Phishing email example

Other attacks can be quite sophisticated. For instance, in 2016, a scam involving a fake CEO of FACC led to a $47 million loss.

Now, the risk is even greater with generative AI, allowing scammers to create realistic deepfake videos or audio of executives. So, remind your employees to be cautious when fending off BEC threats. Encourage people to confirm any urgent requests for money or important information claimed to be from the CEO by directly calling the CEO or messaging them on a different platform.

Implement advanced email filtering

Email filters are crucial in stopping phishing emails before they get to your team. These systems look for clues that an email might be a phishing attempt, and they learn from new threats, greatly reducing the likelihood of a successful attack.

Google has shared that its AI-driven security in Gmail blocks over 99.9% of spam, phishing, and malware, keeping almost 15 billion unwanted emails away from users every day. Keeping these filters up-to-date and properly set up is essential in staying one step ahead of phishers.

Enforce MFA

Multi-factor authentication offers a solid layer of protection, even when other defenses might not work as well. MFA could require something like a code from your phone or your fingerprint. This way, it makes sure that just having stolen credentials isn’t enough to get into your data.

Once, Google aimed to cut down on phishing risks, so they required all their employees to use physical Security Keys, leading to no account takeovers being reported. The company found physical security keys so effective that it introduced its own in 2018. To help with the security of the US election, they also gave out thousands of these keys for free.

Regularly update and patch systems

Updating software is key to phishing prevention. These updates patch security holes that threat actors might use to sneak malware into innocent-looking requests.

They also add new anti-phishing features, like better detection of fake websites, making it harder for phishing attempts to succeed. Plus, keeping software current ensures businesses meet data protection standards and supports the latest defenses against phishing, such as improved email filters and browser warnings.

Conduct phishing simulation exercises

Phishing simulations test how well your team can spot a phishing attempt. For example, Uber tackles cybersecurity risks, including phishing simulations, with a trio of strategies.

Tabletop exercises are like role-playing games for security scenarios, helping leaders practice decision-making and boost their understanding of cybersecurity. Red team operations are more like realistic mock battles, where a team plays the role of attackers to test how well Uber can defend against real threats. Lastly, atomic simulations are bite-sized tests focusing on specific security measures and how quickly the team can respond. Together, these strategies keep the team better prepared for different sorts of cyber challenges.

Develop a response plan

Developing a response plan is essential in the fight against phishing attacks. Start by outlining clear steps that your team should follow when they detect a phishing attempt, including who to notify and how to report the incident. Make sure everyone understands the common phishing techniques and the importance of quick action to minimize damage. Regularly review and update your anti-phishing policies to adapt to new phishing scams. Practice your response plan through drills to ensure that when a real phishing attack occurs, your organization is prepared to act swiftly and effectively.

Use Secure Web Gateways and DNS Filtering

Using Secure Web Gateways (SWG) and DNS filtering is a powerful step in your anti-phishing strategy. These tools act as a first line of defense by blocking access to malicious websites known for phishing attacks before they can do harm. They scan and filter internet traffic to prevent phishing techniques and scams from reaching your network or your team’s devices. Setting up SWG and DNS filtering helps ensure only safe, approved web content gets through, significantly reducing the risk of phishing attempts.

Hold regular security checks and assessments

Regular security checks and assessments help identify vulnerabilities that could be exploited by phishing techniques. By consistently reviewing your security measures, you can stay one step ahead of attackers and adapt to new phishing scams. Incorporating anti-phishing drills and tests into these assessments can strengthen your team’s ability to recognize and respond to threats. Make it a priority to schedule these checks periodically.

Build a culture of reporting

It’s important to make employees feel comfortable reporting any suspected phishing. If people worry they’ll get in trouble or feel embarrassed, they might not report things that could warn you about a phishing threat. Showing that reporting can stop attacks before they happen helps everyone understand why it’s so crucial. Making it easy to report, like having a special email address or a simple button in email programs, encourages reporting. Saying thank you to those who report phishing helps build a culture where everyone wants to keep the organization safe.

How to mitigate phishing attacks with NordLayer

NordLayer offers a straightforward solution to mitigate phishing attacks effectively. It guides businesses in implementing the Zero Trust Network Access (ZTNA) framework smoothly, often without the need for external tech specialists.

ZTNA works on the principle of trusting no one by default, whether they are inside or outside your network. Access is given only after detailed verification, greatly lowering the risk of phishing attacks by making sure only verified users can get into your network resources.

Besides helping with the ZTNA framework, NordLayer has direct features aimed at phishing prevention. The Threat Prevention tool actively spots and stops potential threats, protecting your devices and important data from complex phishing methods and scams.

Using NordLayer’s complete security tools gives your organization strong anti-phishing protection. To find out how NordLayer can help prevent phishing attacks in your organization, feel free to contact sales.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Announcement on Atlas VPN

Atlas VPN, a valued member of the Nord Security family, has made the decision to conclude its services on April 24. 

Atlas VPN was established with the goal of offering secure, accessible, and user-friendly VPN services. Despite its unwavering dedication and the remarkable support from AtlasVPN’s community, the challenges posed by advancing technologies, a competitive market, and the rising costs of maintaining high-quality services have led to this difficult but necessary decision.

The conclusion of Atlas VPN’s journey marks a significant moment for both Atlas VPN and Nord Security. We extend our gratitude to the Atlas VPN team for their dedication to online privacy and security. Their efforts have made a lasting impact on their users and the cybersecurity community.

Recognizing the importance of continuous and secure online protection for Atlas VPN users, we are facilitating their smooth transition to NordVPN. NordVPN’s mission aligns closely with that of Atlas VPN, and we are excited to welcome Atlas users into the NordVPN family. We believe that through NordVPN, Atlas VPN users will experience enhanced online security, privacy, and freedom.

To the Atlas VPN community, we thank you for your trust, support, and for being part of an important mission to make the internet a safer place. As we transition to this next chapter with NordVPN, we are committed to providing you with exceptional service, ensuring the utmost security and privacy online.

Warmest regards,

The Nord Security Team

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

How to prevent data theft by employees

Not all cases of employee data theft come from bad intentions. Lukasz Krupski’s journey at Tesla began heroically. His quick action as he tackled a fire hazard at a Norway Tesla exhibition won him praise from Elon Musk.

But after finding monitoring software on his laptop and being dismissed, Krupski felt compelled to leak safety and data protection concerns, known as the ‘Tesla Files,’ to the media. These leaks, which revealed employee and customer data alongside issues with Tesla’s technology, sparked widespread discussion and legal scrutiny.

Krupski’s actions, motivated by a desire to highlight serious safety concerns, have highlighted the ethical challenges and accountability in technology.

While his case might be somewhat heroic due to his motivations, it’s essential to remember that not all instances of employee data theft are for noble reasons; sometimes, they’re purely for personal gain.

As we explore the topic of preventing data theft by employees, it’s critical to differentiate between the motivations behind such actions and implement robust security measures to safeguard sensitive information.

Key takeaways

  • Employee data theft involves staff taking or sharing company data without permission, posing risks to the company’s security and trust, whether done on purpose or by accident.

  • The theft of sensitive data by employees can lead to financial losses, reputational damage, legal issues, operational disruptions, erosion of trust among team members, and unauthorized access to corporate accounts.

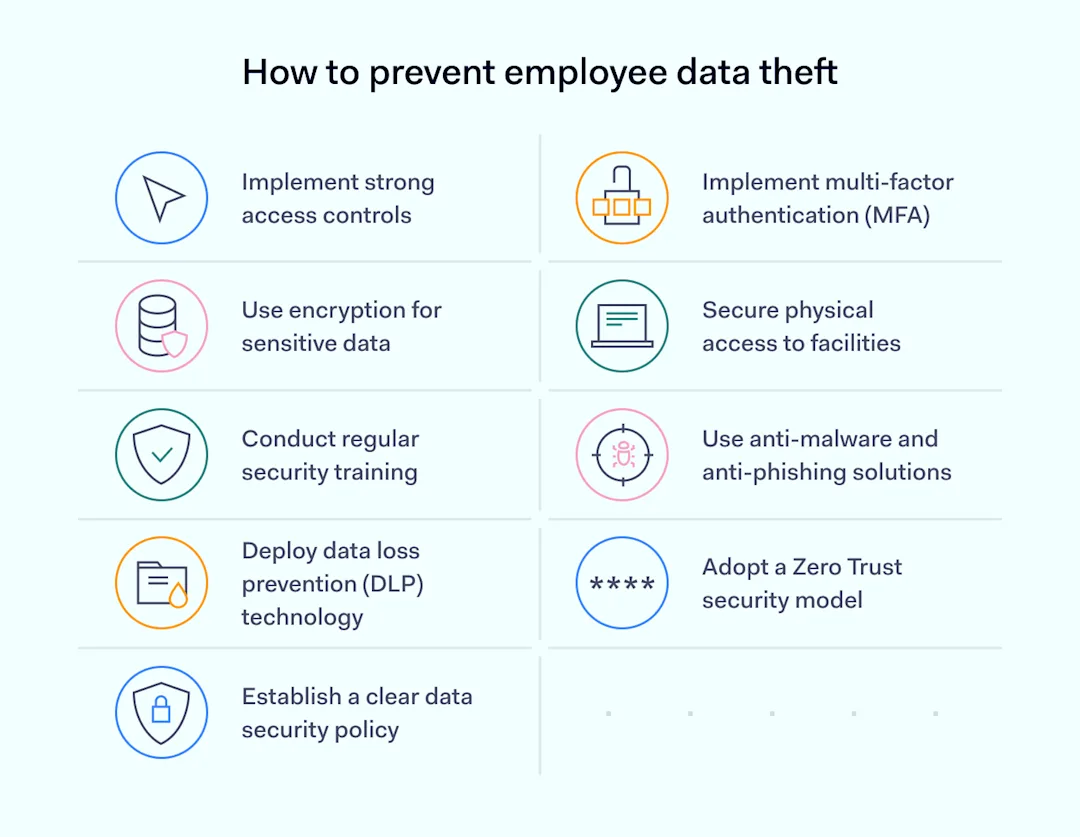
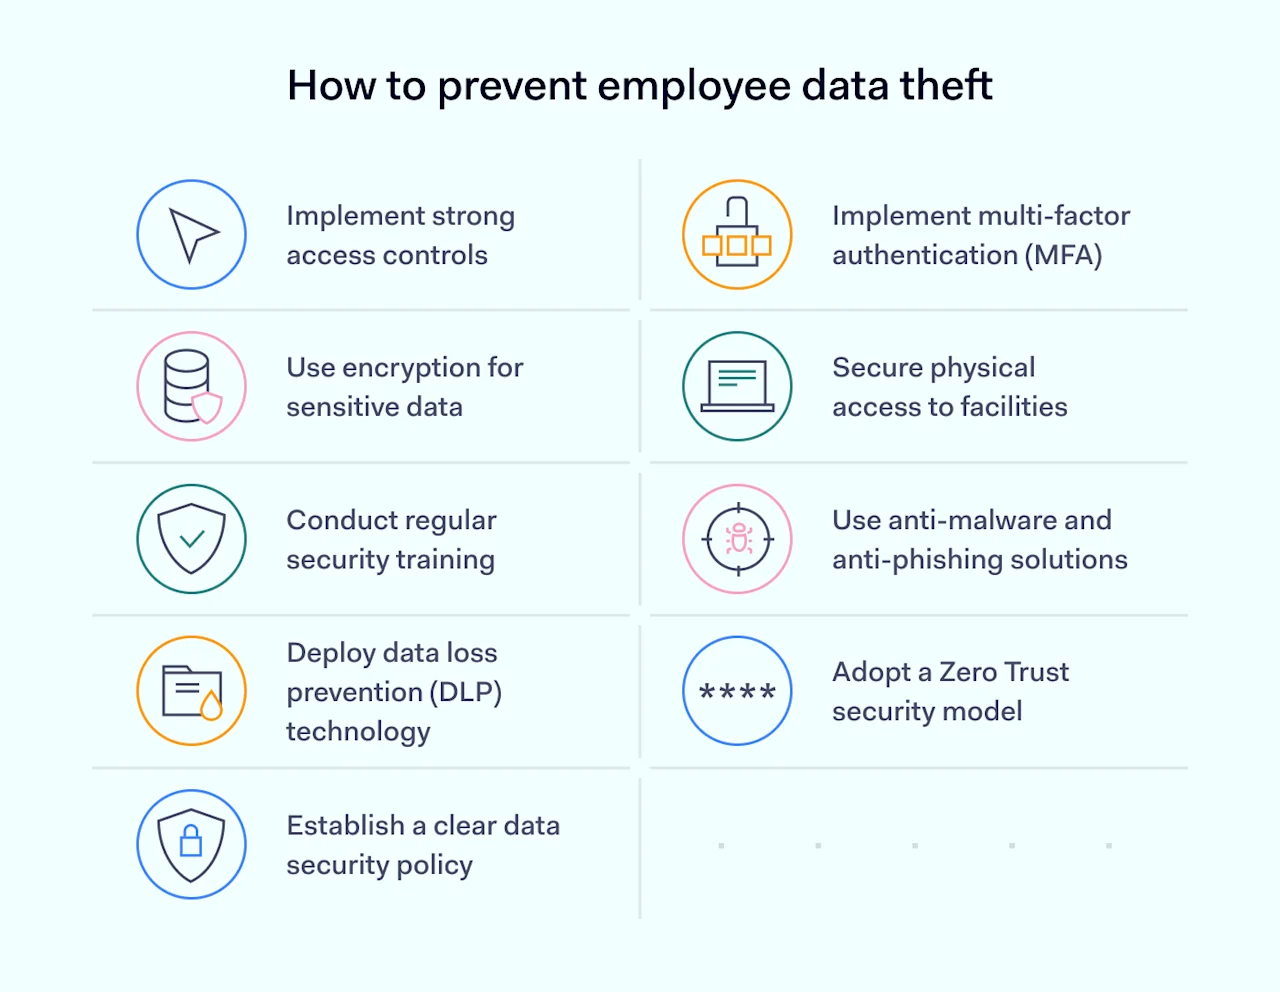
  • To protect sensitive information and prevent data theft by employees, companies should implement robust access controls, use encryption for sensitive data, regularly conduct security training, and establish a clear data security policy.

  • Enhancing data security further involves implementing MFA, securing physical access to facilities, using updated anti-malware and anti-phishing solutions, and adopting a Zero Trust security model that requires continuous verification of all users.

  • NordLayer helps prevent employee data theft through advanced cybersecurity tools like Cloud Firewall and network access control solutions, which help achieve network segmentation and the Zero Trust framework.

What is employee data theft?

Employee data theft happens when an employee takes or shares a company’s data without permission.

Click to tweet

This can be intentional, as in cases where someone decides to steal sensitive information to sell or use against the company. Sometimes, it happens by mistake, like when an employee accidentally exposes information because they weren’t careful. No matter the intent, such theft is a big problem for a company’s safety and credibility.

The risk involves all sorts of sensitive data. This includes personal details about employees and customers, financial information, strategic documents, and passwords to corporate accounts.

There are many ways someone might steal corporate data, such as copying it to a personal device, sending it through unsecured emails, or using harmful software to sneak into a company’s systems.

Another well-known case that highlights the risks of employee data theft involves Anthony Levandowski. He was an engineer at Google’s Waymo, the self-driving car project. Before leaving, Levandowski took thousands of files about Google’s technology for autonomous vehicles. He then founded a self-driving truck company named Otto, which Uber bought soon after. This led to a major legal fight between Waymo and Uber, focusing on accusations that Uber benefited from the stolen secrets. This story shows why it’s so crucial to protect sensitive data.

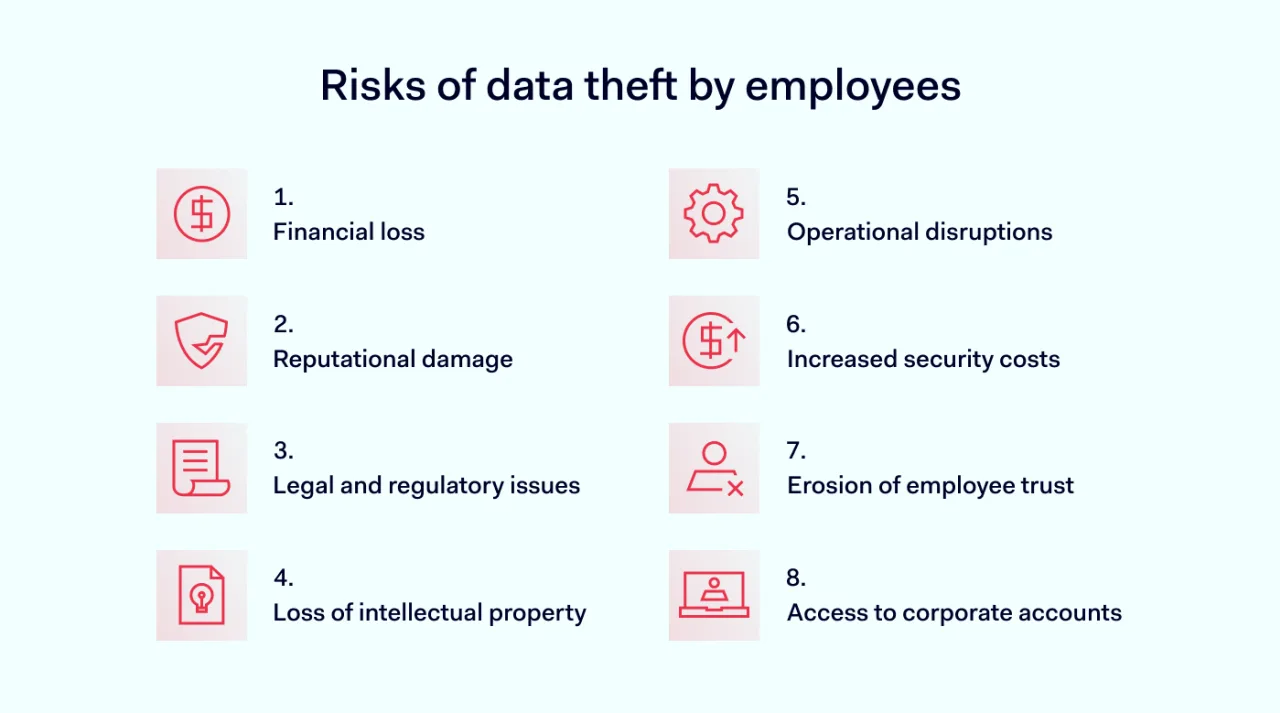
Risks of data theft by employees

A data breach doesn’t just stop at the act of theft; it opens up a Pandora’s box of indirect risks. Here are some consequences companies can face when employees steal data.

Risks of data theft by employees

  1. Financial loss. When employees steal data, companies can face direct financial losses. This is because stolen sensitive information can lead to fraud or the loss of competitive advantage.

  2. Reputational damage. A data breach caused by employee data theft can harm a company’s reputation. Customers and partners may lose trust, which is hard to rebuild.

  3. Legal and regulatory issues. If employees take sensitive data, this can result in legal penalties for the company. This is especially true if the stolen information includes personal data protected by laws.

  4. Loss of intellectual property. Corporate data theft can lead to the loss of proprietary information. This is a serious risk as it can give competitors an unfair advantage.

  5. Operational disruptions. Data theft by employees can disrupt business operations. For example, if critical data is stolen, it might halt production or service delivery.

  6. Increased security costs. To prevent employee data theft, companies may need to invest more in data security measures. This can include adopting a Zero Trust framework, which verifies every access request.

  7. Erosion of employee trust. When corporate data theft occurs, it can create an environment of suspicion. This might reduce collaboration and trust among team members.

  8. Access to corporate accounts. Employees who steal data might gain access to corporate accounts. This risk is particularly high with sensitive information that includes login credentials.

How to prevent employee data theft

The numbers tell us that sales and customer service roles are where we often find the biggest concerns for insider risks, with sales at 48% and customer service at 47%.

But really, keeping our data safe is a job for everyone in the company, not just designated roles. So, let’s explore some clever ways to protect your company.

How to prevent data theft by employees

Implement strong access controls

Setting up strong access controls, like a hardware or cloud firewall, and dividing the network into sections makes sure employees can only get to the data they need for work. This helps in preventing data theft by employees.

It’s important to remember that not everyone needs to see everything in the company. Making it clear what’s confidential can also help stop data from getting out by mistake.

A firewall helps divide the network into sections with clear permissions. This way, you limit who can see sensitive data, helping to avoid accidental sharing.

A cloud firewall (or a Firewall-as-a-Service) makes it easy to set up these divisions, giving specific access rights to certain people or groups. This is great for data security because it helps contain potential problems if something goes wrong. Thanks to how you’ve divided it, employees can only see a small part of the network. This means threat actors can’t do as much damage even if it’s an employee.

Use encryption for sensitive data

Encrypting sensitive data protects it, making the data unreadable to unauthorized users. This is effective even if data is stolen, as the thief cannot use it without the decryption key.

The downside is that managing encryption keys requires careful security measures to prevent them from being stolen as well.

Conduct regular security training

Educating employees about the importance of data security and how to prevent data theft is crucial. Regular training can make employees aware of the risks and teach them to handle data securely. But remember that training alone cannot prevent all instances of data theft, especially if malicious intent is involved.

Deploy data loss prevention (DLP) technology

Using data loss prevention, or DLP technology, is like having a smart security guard that watches over the information being shared in and out of the company. It makes sure that only the right data goes to the right places.

Think of it as having a guard who checks the passes at the door of a secure building. The guard stops people without the right pass (unauthorized data) from leaving.

But, just like any guard might sometimes stop someone by mistake (a false positive), DLP technology can accidentally block information that was okay to share. This means it’s really good at preventing data theft by employees, but it might need a little help sometimes to make sure it doesn’t stop the right information from getting through.

Establish a clear data security policy

A clear data security policy sets out rules for handling sensitive data and the consequences of data theft. This clarity helps prevent employee data theft by setting expectations. These policies must be regularly updated to remain effective and reflect new security challenges.

Implement multi-factor authentication (MFA)

Adding multi-factor authentication (MFA) to our security setup means we’re putting in place an extra step of verification, something more than just the usual password. This makes it much harder for someone to access data they shouldn’t.

If someone tries to sneak into an account or look at data they have no business seeing, MFA steps in. It sends a notification to either another employee or the person who owns the account, flagging that something out of the ordinary is happening.

This quick heads-up gives us a chance to act fast and stop any security problems before they grow, making MFA a really important tool in keeping our data safe.

Secure physical access to facilities

Make sure that only the right people can get into places where sensitive information or important servers are kept. This is especially important when you’ve got crucial servers in your office or when you’re dealing with sensitive data.

It’s essential to keep a close eye on who enters areas with critical data or infrastructure. Set up systems that check if someone is allowed in, like special locks or entry codes that only certain people have.

Use anti-malware and anti-phishing solutions

Adding anti-malware and anti-phishing software is a smart move to keep your data safe. But remember, these tools need to stay updated to fight off the latest cyber tricks. It’s also a good idea to teach your team how to spot those sneaky phishing emails. By keeping everything current and spreading a bit of know-how, you’re building a strong wall that keeps your data secure and out of the wrong hands.

Adopt a Zero Trust security model

The Zero Trust model operates on the principle that no one inside or outside the network is trusted by default. Implementing Zero Trust can significantly reduce the risk of data theft by requiring continuous verification of all users. However, moving to a Zero Trust architecture can be complex and requires significant adjustment for both IT departments and users.

No single method is foolproof, but a layered approach minimizes risks associated with employee data theft.

How NordLayer can protect against data theft by employees

NordLayer offers powerful cybersecurity tools, like Cloud Firewall and Network Access Control (NAC) solutions, to help your organization keep its sensitive data safe.

Network segmentation is an important part of the process. By breaking your network into smaller parts with strict access rules, you make sure only the right people can see important information. This is key to achieving the Zero Trust framework, which checks everyone’s need to access specific data, making it much harder for anyone to steal data or cause a breach. With NordLayer, setting up these secure sections in your network is straightforward and flexible.

Our Identity and Access Management (IAM) solutions add another layer of security by managing who gets access to what, beyond just passwords. The method combines Single Sign-On (SSO) with other checks to make sure every user’s sign-in is legit.

Other Network Access Control (NAC) solutions tighten security further by monitoring access based on IP addresses and device posture, allowing only compliant devices on the network. This approach offers a solid strategy on how to prevent data theft by employees.

For a tailored solution that fits your organization’s specific needs, contact our sales team. They can guide you through the offerings to find the best fit for bolstering your data security.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Shift left: Proactive security, embedded early in development

Sensitive information on your phone, computer, or smartwatch is at risk every time you use an application that isn’t properly secured. To ensure the safety of user data and a robust application, developers and security specialists are increasingly embracing the “shift left” approach. In this blog post, we’ll explore what it means and how shift left isn’t only about integrating tools and testing from the start, but a collaborative mindset that empowers developers and security specialists to build applications together. 

What is shift left?

Shift left is a methodology that aims to prevent software vulnerabilities by integrating security testing and analysis earlier (the “left” on a planning board) in the software development lifecycle. This is opposed to the classical checklist security approach, which usually pushes testing to the end (the “right”) of the process. With shift left, security specialists and developers are able to catch and fix vulnerabilities before they snowball into bigger issues later on in development. Shift left is particularly relevant for organizations involved in cybersecurity, where a secure application is crucial.

Advantages of shifting left

But why bother shifting left? Here are a few of the key advantages:

  • Safer products: By identifying potential vulnerabilities early on and addressing them proactively throughout the entire development phase, security risks are minimized, resulting in a more robust end product.

  • Cost savings: Fixing security issues later in development can be significantly more expensive than addressing them early on. Reworking or recreating parts of the app codebase is costly and a major time sink. With shift left properly implemented, companies can avoid extensive code modification. Additionally, it can save on potential costs associated with security breaches, like fines or lawsuits.

  • Enhanced developer skills: Shifting left also provides opportunities for developers to learn more about secure coding practices, as well as the latest security threats and trends. This can enhance their skills and knowledge, which contribute to better-quality products and improved job performance.

  • Increased collaboration: Shifting left encourages collaboration between developers and cybersecurity experts. Close cooperation leads to more efficient communication, increased knowledge-sharing, and a deeper understanding of the other’s role. The result is a more effective development process.

  • Competitive advantage: By prioritizing security earlier in the software development lifecycle, companies can differentiate themselves from their competitors and build a reputation for creating stable, secure, and reliable products, which attracts more customers and clients.

Where’s the catch?

Fair question. Many companies have been slow to adopt shift left. There are a few reasons for this:

  • Cost: Implementing a shift left approach can require an investment in time, resources, and tools. Some companies aren’t willing or able to make this investment, especially if they haven’t experienced any security breaches in the past.

  • Difficulty measuring ROI: It’s challenging to measure the return on investment (ROI) of a shift left approach because it’s impossible to quantify the impact of preventing security incidents. If an incident never happens, that’s a good result. But that can be a hard sell to stakeholders.

  • Resistance to change: Shifting left requires a change in company culture, as it involves rethinking the traditional development process. This can be a difficult adjustment for some teams.

  • Lack of training: Developers or security experts don’t have the necessary skills or knowledge to implement it. Providing training and resources and time to developers with security specialists can help overcome this barrier.

  • Lack of awareness: Some companies simply aren’t aware of the shift left approach or the benefits it can bring.

Overall, while there are some challenges associated with implementing a shift left approach, the benefits can outweigh the costs in terms of improved security and customer satisfaction. Companies need to consider the long-term benefits and invest in secure coding practices to protect their assets and reputation.

First steps to shift left

There are multiple approaches open to organizations for getting started with shift left. For example, providing developers with interactive learning platforms can enhance their specific programming language or technology knowledge with virtual machines, created labs, and challenges. This helps them learn about secure coding practices and how to incorporate security into their workflow. Additionally, knowledge-sharing sessions and security conferences can help developers embrace best practices for a security-focused culture.

Threat modeling sessions are a useful way to help developers anticipate and prevent security issues. During a threat modeling session, developers work closely with AppSec and WebSec engineers, pentesters, and security architects to identify vulnerabilities and prioritize them based on risk, probability, and potential impact.

Teams can also use automated tools to scan code for potential security vulnerabilities. These tools help identify vulnerabilities early in the development process before they become larger issues. There are a variety of automated security testing tools available, including static analysis tools or dynamic analysis tools.

  • Static analysis tools (SAST) help maintain code quality and identify security vulnerabilities, bugs in the code, libraries before it’s released.

  • Dynamic analysis tools (DAST) help ensure the application behaves as expected under automated conditions, improving user experience and security.

Closing tips

Building a strong team is crucial because properly implementing shift left is no small task. It requires cooperation, dedication, and patience – from all team members. Support and ideas from colleagues are essential to solving emerging challenges, adapting to increased workloads, and sharing the responsibility of ensuring a secure software development process.

If an incident does occur with a product, it shouldn’t be viewed as a failure but rather as an opportunity to learn and grow and take advantage of the chance to use the incident as a catalyst for promoting the shift left idea within the company. Adoption can be accelerated by demonstrating the real-world consequences of security breaches.

In conclusion, embrace the challenges and leverage the opportunities that arise in the process of implementing shift left in companies. Keep pushing forward, knowing that every step you take brings you closer to a more secure and efficient software development process. So let’s get to work and clean up the dust!

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.