Skip to content

Jeff Ready of Scale Computing Honored on CRN’s 2020 Top 100 Executives List and named a Top 25 Disruptor

INDIANAPOLIS, August 12, 2020 – Scale Computing, a market leader in edge computing, virtualization, and hyperconverged solutions, announced today that CRN®, a brand of The Channel Company, has named Jeff Ready, CEO and co-founder of Scale Computing, to its 2020 list of Top 100 Executives, specifically ranking among the “Top 25 Disruptors.” This annual list recognizes the trailblazing technology executives who are shaping, transforming, and disrupting the IT channel.

Despite a challenging global environment, under Ready’s leadership Scale Computing delivered record revenue in Q1, achieving a growth rate of over 30% year-over-year. This included a quick pivot by the company in March to assist customers with a solution that enabled employees to work remotely, leveraging virtual desktop infrastructure (VDI) technology with partner Leostream. In Q2, Scale Computing launched the HC3250DF, a new performance tier of HC3 appliances for databases and VDI, and delivered a Business Resilience Solution to ensure organizations can keep data, applications and workers online when the unexpected threatens operations.

“We strive to deliver products and services that disrupt the IT market by being innovative, easy-to-use and cost-efficient. But it takes more than great products to be truly successful at those things,” said Ready. “That’s why Scale Computing has worked closely with a variety of partners over the years — MSPs, VARs, distributors, OEMs and technology partners — to enable better sales, delivery, deployment, services and solutions to benefit our customers. Scale Computing’s success would not be possible without the incredible support from our partners, and we thank them for that.”

The 2020 CRN Top 100 Executives list honors the tech visionaries who power the IT channel. It is broken down into four sub-lists: The 25 Most Influential Executives, Top 25 Channel Sales Leaders, Top 25 Innovators, and Top 25 Disrupters.

The Top 100 Executives being recognized have demonstrated exemplary leadership and innovative ideas for the IT channel. In doing so, they help vendors, solution providers, and technology suppliers thrive in an IT marketplace that is both fast-changing and ever more complicated.

“As the IT channel becomes increasingly complex, especially when companies have had to shift to an all-remote workforce, it has presented new challenges for solution providers and technology suppliers alike,” said Blaine Raddon, CEO of The Channel Company. “The technology executives on CRN’s 2020 Top 100 Executives list have been able to adapt their channel strategies and continue to provide exemplary leadership to keep their businesses running seamlessly, regardless of today’s challenges.”

The Top 100 Executives list will be featured in the August 2020 issue of CRN Magazine and online at www.CRN.com/Top100.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Scale Computing 
Scale Computing is a leader in edge computing, virtualization, and hyperconverged solutions. Scale Computing HC3 software eliminates the need for traditional virtualization software, disaster recovery software, servers, and shared storage, replacing these with a fully integrated, highly available system for running applications. Using patented HyperCore™ technology, the HC3 self-healing platform automatically identifies, mitigates, and corrects infrastructure problems in real-time, enabling applications to achieve maximum uptime. When ease-of-use, high availability, and TCO matter, Scale Computing HC3 is the ideal infrastructure platform. Read what our customers have to say on Gartner Peer Insights, Spiceworks, TechValidate and TrustRadius.

About The Channel Company
The Channel Company enables breakthrough IT channel performance with our dominant media, engaging events, expert consulting and education and innovative marketing services and platforms. As the channel catalyst, we connect and empower technology suppliers, solution providers and end users. Backed by more than 30 years of unequalled channel experience, we draw from our deep knowledge to envision innovative new solutions for ever-evolving challenges in the technology marketplace. thechannelcompany.com

訊連科技將於「2020台灣機器人與智慧自動化展」中,展出整合口罩偵測及體溫感測的防疫解決方案

20200813日,台北訊】 全球頂尖AI臉部辨識領導廠商訊連科技 (5203.TW) 將參加2020年8月19-22日舉辦之「台灣機器人與智慧自動化展」,於「防疫專區」中,展出專為後防疫時代設計的多款解決方案,包含提供口罩偵測、臉部辨識及體溫量測的FaceMe® Health及整合智慧安控和口罩偵測的FaceMe® Security

後防疫時代來臨,然各國COVID-19疫情仍然嚴峻。衛福部日前宣布進出八大類場所強制配戴口罩,體溫量測亦是進出各式辦公場所、公共運輸及公共場合不可或缺的環節。一般體溫量測站須由專人負責,使用額溫槍或熱感攝影機進行量測,除耗費人力外,亦隱藏潛在的接觸風險。

訊連科技全新推出之FaceMe® Health提供了口罩辨識、身分辨識、體溫量測及即時警訊的一站式健康量測解決方案。透過AI技術,FaceMe® Health可辨別訪客是否配戴口罩,或有口鼻露出、以手摀住口鼻等不當配戴或假冒情況,更可在配戴口罩時進行身分辨識,可達95%之辨識率。FaceMe® Health亦可支援體溫量測,搭配相容的熱感攝影機或具備體溫量測功能之IP攝影機,準確量測訪客之額溫。於偵測到未配戴口罩或發燒等狀況時,FaceMe® Health可透過U Alerts即時警訊功能通知保全人員進行處理,協助辦公場所及公共場合於入口處打造全方位的非接觸性健康偵測站。

FaceMe® Security為一款專為智慧安控設計的加值軟體,可運行於工作站、伺服器或VMS (video management systems)等多種環境。FaceMe® Security可在安控場景中偵測人臉,與資料庫比對,並於偵測到特定人物時,以即時通訊通知相關人員。於自動化展中,訊連科技將搶先公開FaceMe® Security的全新功能,可整合口罩偵測、身分辨識及體溫量測等資訊,為智慧辦公室、智慧製造、智慧零售等場域,打造整合安控、出勤及健康監控等多樣化功能之解決方案。

「後防疫時代來臨,配戴口罩及體溫量測是進出各式場所不可或缺的防疫作為。」訊連科技黃肇雄執行長表示:「訊連科技的FaceMe® Health及FaceMe® Security係採用全球頂尖之FaceMe® AI臉部辨識引擎打造,可有效偵測口罩配戴狀態、量測體溫,並可於戴口罩時進行準確的身分辨識,透過先進的AI技術讓健康量測之流程自動化,並減少接觸的風險。」

「台灣機器人與智慧自動化展」展會資訊

  • 時間:2020年8月19 – 22日
  • 訊連科技展位:南港展覽館一館一樓K510(防疫專區)
  • 預約會議:
    • 業務聯繫請洽FaceMe_TW@cyberlink.com
    • 媒體採訪請洽:Contact_PR_TW@cyberlink.com


FaceMe®產品訊息

關於Version 2

Version 2 Digital 是立足亞洲的增值代理商及IT開發者。公司在網絡安全、雲端、數據保護、終端設備、基礎設施、系統監控、存儲、網絡管理、商業生產力和通信產品等各個領域代理發展各種 IT 產品。透過公司龐大的網絡、通路、銷售點、分銷商及合作夥伴,Version 2 提供廣被市場讚賞的產品及服務。Version 2 的銷售網絡包括台灣、香港、澳門、中國大陸、新加坡、馬來西亞等各亞太地區,客戶來自各行各業,包括全球 1000 大跨國企業、上市公司、公用事業、醫療、金融、教育機構、政府部門、無數成功的中小企及來自亞洲各城市的消費市場客戶。

關於CyberLink
訊連科技創立於1996年,擁有頂尖視訊與音訊技術的影音軟體公司,專精於數位影音軟體及多媒體串流應用解決方案產品研發,並以「抓準技術板塊,擴大全球行銷布局」的策略,深根台灣、佈局全球,展現亮麗的成績。訊連科技以先進的技術提供完美的高解析影音播放效果、以尖端的科技提供完整的高解析度擷取、編輯、製片及燒錄功能且完整支援各種高解析度影片及音訊格式。產品包括:「威力導演」、「PowerDVD」、「威力製片」、「威力酷燒」等。

Monitoring 802.1X EAP: What You Need to Know

First Thing’s First

As we’ve written about previously, the standard authentication protocol used on encrypted networks is Extensible Authentication Protocol (EAP), which provides a secure method to send identifying information for network authentication. 802.1x is the standard that is used for passing EAP over wired and wireless Local Area Networks (LAN), as it provides an encrypted EAP tunnel that prevents outside users from intercepting information. The EAP protocol can be configured for credential (EAP-TTLS/PAP and PEAP-MSCHAPv2) and digital certificate (EAP-TLS) authentication and is a highly secure method for protecting the authentication process.

Throughout this article, we will look at how to monitor 802.1X EAP and why doing so is important from a network security perspective.

MAC Authentication Bypass (MAB)

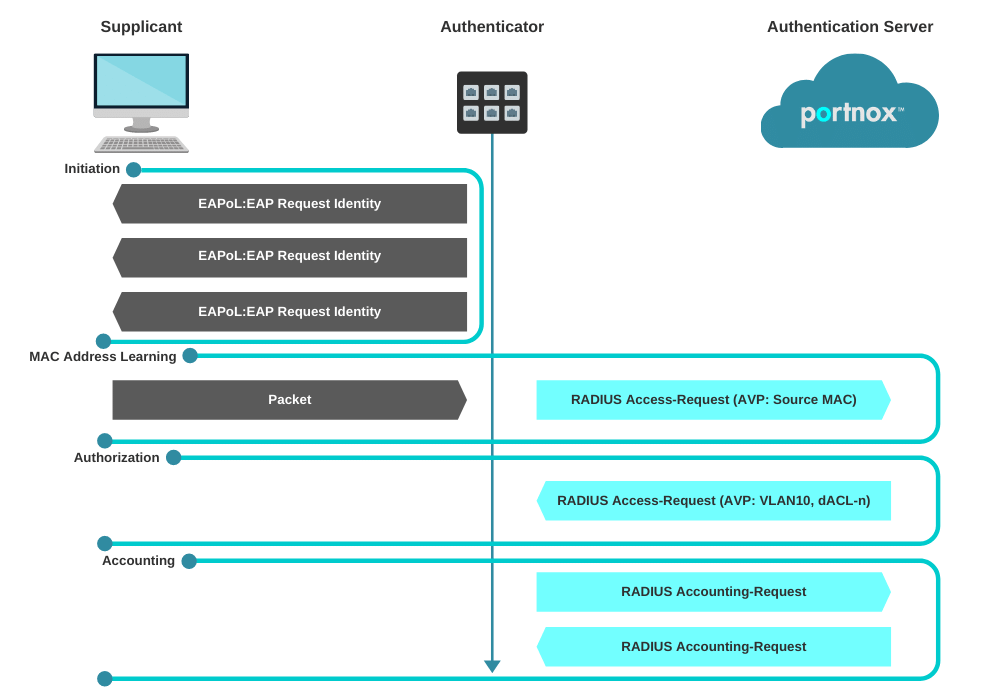
MAB enables port-based access control using the MAC address of the endpoint. A MAB-enabled port can be dynamically enabled or disabled based on the MAC address of the device that connects to it. The below diagram illustrates the default behavior of a MAB-enabled port.

EAP MAC authentication bypass

Session Initiation

From the switch’s perspective, the authentication session begins when the switch detects link-up on a port. The switch will initiate authentication by sending an EAP Request-Identity message to the endpoint. If the switch does not receive a response, the switch will retransmit the request at periodic intervals. If no response is received after the maximum number of retries, the switch will let IEEE 802.1X time out and proceed to MAB.

MAC Address Learning

During the MAC address learning stage, the switch begins MAB by opening the port to accept a single packet from which it will learn the source MAC address of the endpoint. Packets sent before the port has fallen back to MAB (that is, during the IEEE 802.1X timeout phase) are discarded immediately and cannot be used to learn the MAC address.

The switch can use almost any Layer 2 and 3 packets to learn MAC addresses, with the exception of bridging frames such as Link Layer Discovery Protocol (LLDP), Spanning Tree Protocol, and Dynamic Trunking Protocol (DTP). 1

After the switch learns the source MAC address, it discards the packet. Then the switch crafts a RADIUS Access-Request packet. A sample MAB RADIUS Access-Request packet is shown in the snapshot below.

RADIUS Access-Request Packet for MAB

By default, the Access-Request message is a Password Authentication Protocol (PAP) authentication request, The request includes the source MAC address in three attributes: Attribute 1 (Username), Attribute 2 (Password), and Attribute 31 (Calling-Station-Id). Although the MAC address is the same in each attribute, the format of the address differs. This feature is important because different RADIUS servers may use different attributes to validate the MAC address. Some RADIUS servers may look at only Attribute 31 (Calling-Station-Id), while others will actually verify the username and password in Attributes 1 and 2.

Because MAB uses the MAC address as a username and password, you should make sure that the RADIUS server can differentiate MAB requests from other types of requests for network access. This precaution will prevent other clients from attempting to use a MAC address as a valid credential. Cisco switches uniquely identify MAB requests by setting Attribute 6 (Service-Type) to 10 (Call-Check) in a MAB Access-Request message. Therefore, you can use Attribute 6 to filter MAB requests at the RADIUS server.

Session Authorization

If the MAC address is valid, the RADIUS server will return a RADIUS Access-Accept message. This message indicates to the switch that the endpoint should be allowed access to the port. Optionally, the RADIUS server may include dynamic network access policy instructions (for example, a dynamic VLAN or access control list [ACL]) in the Access-Accept message. In the absence of dynamic policy instructions, the switch will simply open the port. No further authentication methods will be tried if MAB succeeds.

If the MAC address is not valid or is not allowed to access the network for policy reasons, the RADIUS server will return a RADIUS Access-Reject message. This message indicates to the switch that the endpoint should not be allowed access to the port based on the MAC address.

If no fallback authentication or authorization methods are configured, the switch will stop the authentication process and the port will remain unauthorized.

Session Accounting

If the switch can successfully apply the authorization policy, the switch can send a RADIUS Accounting-Request message to the RADIUS server with details about the authorized session.

EAP Request Frame

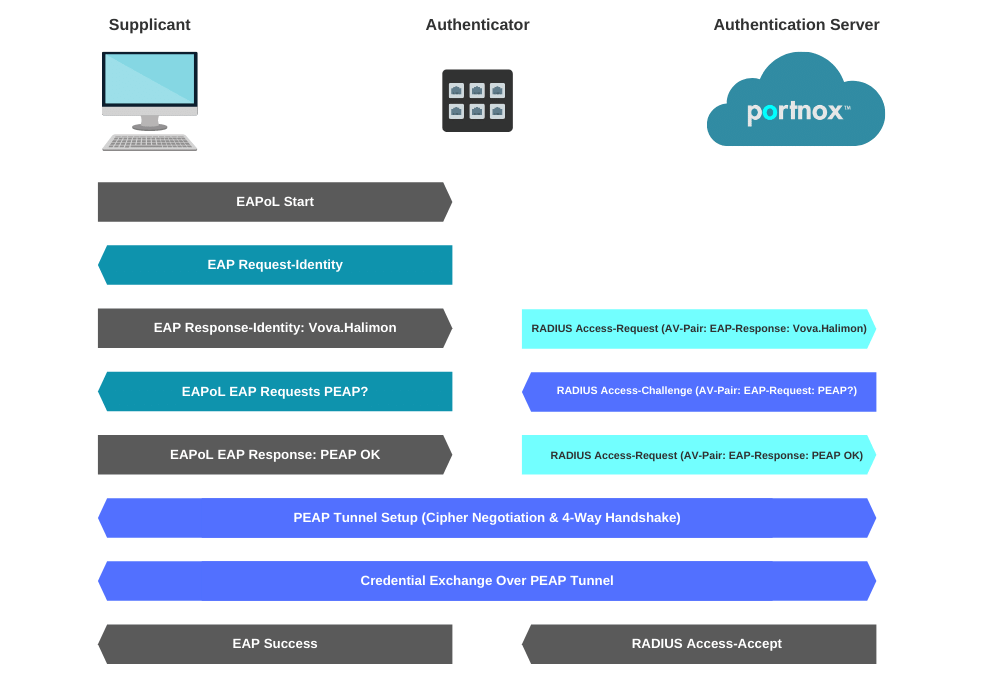
In the diagram above, the first frame sent is an EAPOL-Start frame. This frame is not critical, and the process can be started by the authenticator sending the EAP-Request Frame.

Next, the supplicant responds with an EAP-Response. Messages from the Authenticator to the Radius server use the radius protocol (UDP 1812 for Authentication)When the authenticator receives an Access-Accept packet from the radius server it will authorize the port and allow access to the supplicant. If access is denied by the Radius server an Access-Reject message will be sent to the authenticator and the port will stay unauthorized.

The supplicant can terminate the authentication of the port by sending an EAPOL-logoff frame to the authenticator.

Supplicant to Authenticator (EAPoL)

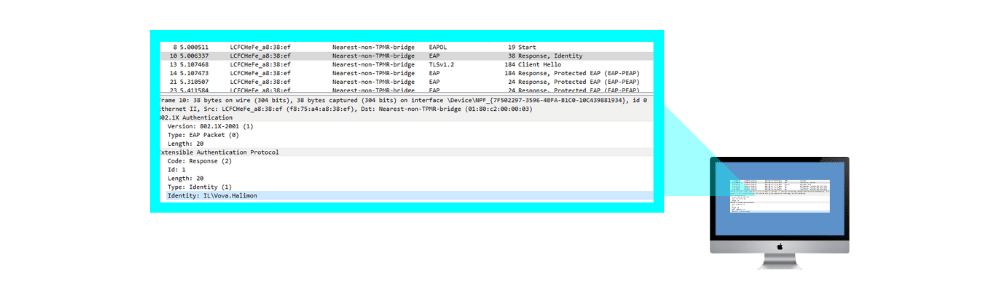
This is the communication method utilized that provides the Authenticator and the Client a line of communication prior to network access. This is what the capture will look like:

EAPoL communication

The EAPoL portion of communication will vary depending on the authentication type. In my examples, we are using EAP-PEAP w/EAP-MsCHAPv2. This is a fairly standard form of authentication.

The useful portions that can usually be derived from a pcap are:

EAP-Identity Response

In this frame, you can see the Client’s (Supplicant) Identity being used of “Vova.Halimon“. This can be extremely useful when trying to determine if the supplicant is going to authenticate as the user or the machine account as well as what the user could be typing into the username prompt.

For more information on EAP types, visit the IANA EAP registry.

EAP-TLS (Certificate Example)

EAP Auth Method Negotiation and Credential Exchange:

EAP Auth Method

The first message in the above screenshot is the server’s proposal of EAP-PEAP (EAP-TLS, EAP-TTLS EAP-FAST, EAP-LEAP, EAP-MD5) then the client’s response with, “EAP-PEAP good for me” In some situations, depending on the RADIUS server configuration, the client may try to propose a method that is not permitted or supported by the server. This is where you would see that negotiation fail, and ultimately an Access-Reject / EAP-Failure.

EAP Success (Wired & Wireless) & 4-Way Handshake (Wireless):

EAP Success

EAP CodeType
1Request
2Response
3Success
4Failure

Once the client has been successfully authenticated and authorized, there is an EAP Success message sent back to signify the end of the process. If this is a wired client, the process is over, and the client is able to start transmitting and receiving data frames. If this is a wireless client, the station will utilize a few EAP attributes and the AP will utilize two MPPE (Microsoft Point-to-Point Encryption – key attributes in the RADIUS Access-Accept response to perform the 4-way handshake and create the encryption keys for secure communication.

Extensible Authentication Protocol (EAP) Authentication Types

  • MD5 isn’t typically used as it only does a one-way authentication, and perhaps even more importantly doesn’t support automatic distribution and rotation of WEP keys so does nothing to relieve the administrative burden of manual WEP key maintenance.
  • TLS, while very secure, requires client certificates to be installed on each Wi-Fi workstation. Maintenance of a PKI infrastructure requires additional administrative expertise and time in addition to that of maintaining the WLAN itself.
  • TTLS addresses the certificate issue by tunneling TLS, and thus eliminating the need for a certificate on the client side. Making this an often preferred option. Funk Software* is the primary promoter of TTLS, and there’s a charge for supplicant and authentication server software.
  • LEAP has the longest history, and while previously Cisco proprietary (works with Cisco Wi-Fi adapters only), Cisco has licensed LEAP to a variety of other manufacturers through their Cisco Compatible Extensions program. A strong password policy should be enforced when LEAP is used for authentication.
  • EAP-FAST is now available for enterprises that can’t enforce a strong password policy and don’t want to deploy certificates for authentication.

The more recent PEAP works similarly to EAP-TTLS in that it doesn’t require a certificate on the client side. PEAP is backed by Cisco and Microsoft and is available at no additional cost from Microsoft. If desired to transition from LEAP to PEAP, Cisco’s ACS authentication server will run both.

EAP-TLS Example

EAP-TLS example

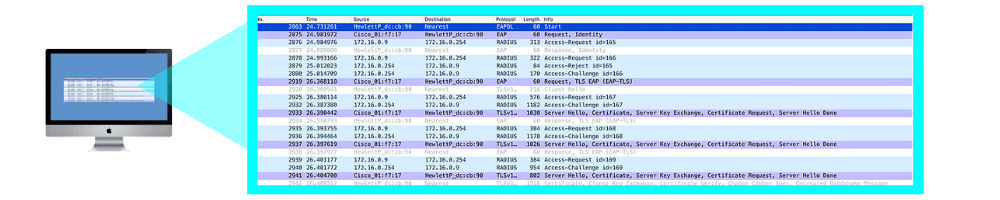
However, in this graphic, you can see the client and server negotiate EAP-PEAP. Once that is completed, the server will present the client with its certificate. If the client does not trust the certificate from the server, and the user does not accept the certificate(The end-user might be presented with a dialog to trust this certificate), the exchange will fail after the first frame or two of the handshake.

In this situation, however, the client trusts the server certificate, and the two endpoints secure the medium with a TLS tunnel. Once secured you should notice that the protocol becomes purely TLS and since the traffic is encrypted, we can only see that the frames are “Application Data”. This is the point at which the client and server are exchanging inner authentication data such as EAP-MsCHAPv2 or EAP-TLS.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

後防疫時代來臨,訊連科技發表全新FaceMe® Health 打造非接觸的智慧健康量測解決方案

全球頂尖AI臉部辨識領導廠商訊連科技 (5203.TW) 發表全新智慧健康量測解決方案FaceMe® Health。FaceMe® Health可建置於各式場所之出入口,如:辦公大樓、零售店、車站等,透過AI技術,自動偵測口罩配戴狀況及量測體溫,或進行身分辨別。於偵測到未配戴口罩人士出入時,以即時訊息通知保全或相關人員,可協助各式場所打造後疫情時代的非接觸性健康偵測站。

後防疫時代來臨,配戴口罩,體溫量測仍是進出各式辦公場所、公共運輸及公共場合不可或缺的環節。一般體溫量測站須由專人負責,使用額溫槍或熱感攝影機進行量測,除耗費人力外,亦隱藏潛在的接觸風險。

訊連科技全新推出之FaceMe® Health提供了一站式的智慧健康量測解決方案,透過AI影像辨識技術,可辨別訪客是否配戴口罩,或有口鼻露出、以手摀住口鼻等不當配戴或假冒情況。更可在配戴口罩時進行身分辨識,可達95%之辨識率。FaceMe® Health亦整合了即時通訊功能,於偵測到發燒或未配戴口罩時,透過U Alerts即時通知相關人員進行應對。「訊連科技的FaceMe® Health係採用全球頂尖之FaceMe® AI臉部辨識引擎打造,可有效偵測口罩配戴狀態、量測體溫,並於戴口罩時進行準確的身分辨識。」訊連科技黃肇雄執行長表示:「透過先進的AI技術,可讓健康量測之流程自動化,並減少接觸的風險,快速打造各式公共場所的智慧健康量測站。」

FaceMe® Health可安裝於最低第八代Intel® Core i3處理器之電腦,如NUS迷你電腦等,可使用USB Webcam及FLIR C3熱感攝影機,或是特定型號、搭載熱感應攝影功能的IP攝影機,即可建置於公共場所出入口進行健康偵測,輕鬆打造非接觸性、自動化的智慧健康偵測站。 


關於Version 2

Version 2 Digital 是立足亞洲的增值代理商及IT開發者。公司在網絡安全、雲端、數據保護、終端設備、基礎設施、系統監控、存儲、網絡管理、商業生產力和通信產品等各個領域代理發展各種 IT 產品。透過公司龐大的網絡、通路、銷售點、分銷商及合作夥伴,Version 2 提供廣被市場讚賞的產品及服務。Version 2 的銷售網絡包括台灣、香港、澳門、中國大陸、新加坡、馬來西亞等各亞太地區,客戶來自各行各業,包括全球 1000 大跨國企業、上市公司、公用事業、醫療、金融、教育機構、政府部門、無數成功的中小企及來自亞洲各城市的消費市場客戶。

關於CyberLink
訊連科技創立於1996年,擁有頂尖視訊與音訊技術的影音軟體公司,專精於數位影音軟體及多媒體串流應用解決方案產品研發,並以「抓準技術板塊,擴大全球行銷布局」的策略,深根台灣、佈局全球,展現亮麗的成績。訊連科技以先進的技術提供完美的高解析影音播放效果、以尖端的科技提供完整的高解析度擷取、編輯、製片及燒錄功能且完整支援各種高解析度影片及音訊格式。產品包括:「威力導演」、「PowerDVD」、「威力製片」、「威力酷燒」等。

Similarities Between Stuxnet And Latest Vulnerabilities Found In Schneider Triconex SIS Controllers


Overview

As the NSA urges companies to secure their industrial networks, two vulnerabilities were found in Schneider Electric Triconex SIS devices. Both of the vulnerabilities reside within the Tricon Communication Module (TCM) which connects the Triconex SIS to Ethernet networks. The first vulnerability (CVE-2020-7486) is a Denial of Service attack that causes the TCM to enter a fault state, and the latter (CVE-2020-7491), a more serious one, is a legacy debug port exposed to the network, that allows attackers to get root style privileges on the TCM, and upload malicious firmware to it.

While the vulnerabilities themselves are severe, exploiting them will not directly impact the SIS operation. In case of a failure in a plant, SIS operations will work normally. 

Most SIS devices use the key switch methodology, where a physical switch controls the state of the SIS. When the SIS is operating normally, this switch should be in the ‘Run’ state. In order to harm the SIS from the TCM by uploading malicious code to it, the SIS key switch must first be physically changed to ‘Program’ or ‘Remote’.


Hiding Malicious Activity, As Seen In Stuxnet

Leveraging CVE-2020-7491, an attacker can write its own firmware to the TCM. Because the TCM resides between the SIS and the OT Ethernet network, malicious code installed on it TCM can be used to hide or modify activity sent or received by the SIS.

SIS HMIs are usually connected to the Ethernet network. These HMIs can be fed incorrect information from the TCM module, causing fake SIS data to be displayed in the HMI. 

Moreover, the TCM could hide the malicious code blocks from the programming software, rendering it undetected from engineers. 

Similar practices have been seen in the past in the Stuxnet campaign, hooking network code to hide malicious activity. A rootkit was installed on PCs with engineering software and a part of its operation was to hide the infected PLC code blocks from being seen in the programming software.
Moreover, Stuxnet prevented operators from noticing its set of instructions sent to peripheral devices (centrifuges, etc) by hiding those instructions from the process image output. These monitoring and HMIs devices were fed incorrect information showing that the PLCs are functioning normally, and no out of the ordinary instructions were sent to them.


Mitigation Recommendations

  1. There are countless vulnerabilities in industrial equipment, and more vulnerabilities are discovered every day. A safety net in the form of a passive, industrial network traffic monitoring system (such as the SCADAfence Platform), will be able to slow down all attacks, enabling you to respond, and will detect most attack vectors. Such products increase the cost of an attack, in a way that makes the attack irrelevant for most attackers. See our webinar on Efficient Industrial Cyber Security Programs for more information.
  2. Update the TCM modules using the latest firmware from Schneider Electric. Updates can be found in the official advisory – Legacy Triconex  Product Vulnerabilities
  3. Make sure SIS devices are behind a firewall and only communicating in ports they should communicate in. Both vulnerabilities were found in undocumented services communicating on non standard ports.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About SCADAfence
SCADAfence helps companies with large-scale operational technology (OT) networks embrace the benefits of industrial IoT by reducing cyber risks and mitigating operational threats. Our non-intrusive platform provides full coverage of large-scale networks, offering best-in-class detection accuracy, asset discovery and user experience. The platform seamlessly integrates OT security within existing security operations, bridging the IT/OT convergence gap. SCADAfence secures OT networks in manufacturing, building management and critical infrastructure industries. We deliver security and visibility for some of world’s most complex OT networks, including Europe’s largest manufacturing facility. With SCADAfence, companies can operate securely, reliably and efficiently as they go through the digital transformation journey.