Skip to content

UX/UI Designers in cybersecurity: An essential role for a safer digital world

While most people associate cybersecurity solutions with complex code, it also involves a significant amount of design work. That’s where UX/UI specialists come in. But exactly what role do these designers play in the cybersecurity field, and where can we see their impact?
To answer these questions, we talked to two UX/UI designers working at Nord Security, Teodora Žvilaitytė and Irma Škuratovaitė. They shared their experiences and some insights on their work in this challenging industry and how it feels to shape a quality user experience for the world’s fastest VPN. So, without further ado, let’s dive in.

Meaningful work

What makes working in the cybersecurity field exciting and fulfilling for you as a UX/UI designer?

Irma: It is really gratifying to know that I’m helping make the online world safer for millions of people across the globe. And it’s even more rewarding to see that our hard work has been recognized by TIME magazine, which listed NordVPN as one of the best innovations of 2022.

While UX/UI design may not be the most crucial part of the product (the tech side is), it still plays an essential role in ensuring that the security features of NordVPN are accessible and user-friendly. This involves designing intuitive interfaces, clear instructions, and helpful features that guide users in managing their security settings.

Teodora: It’s crazy how cyber threats are everywhere and can affect not just companies but also ordinary people, who often think they are too small to become a target of cybercriminals – but they’re not. Knowing this, I’m glad to work for NordVPN, securing people’s digital lives.

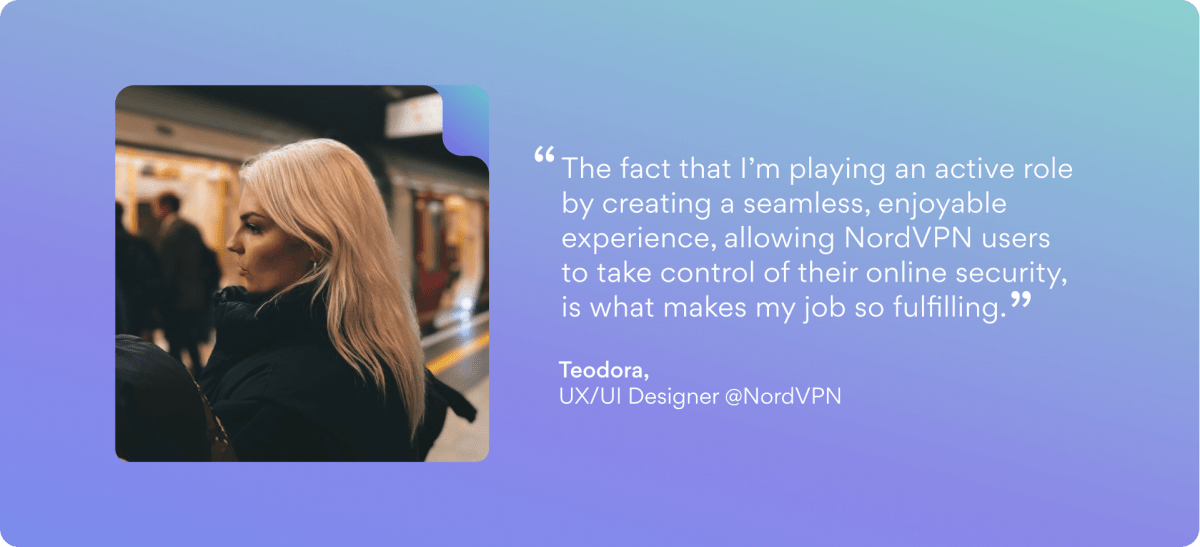
The fact that I’m playing an active role by creating a seamless, enjoyable experience, allowing NordVPN users to take control of their online security, is what makes my job so fulfilling. Seeing how much they appreciate and trust our product is incredibly inspiring, and it gives me a great sense of purpose that is hard to come by.
Skills needed to succeed

UX design is a broad field that covers many areas of expertise. What skills do you need to succeed as a UX pro?

Irma: To work at Nord Security, you need to have open-mindedness, communication, and presentation skills, along with problem-solving abilities. Being open to discussion, feedback, and different viewpoints will help you collaborate more effectively with stakeholders and cross-functional teams and create better design solutions.

Communication and presentation skills are essential for conveying ideas, preparing presentations, and ensuring that the design process runs smoothly. Problem-solving skills are crucial for empathizing with users and finding solutions to their pain points.

Teodora: Besides having strong communication skills, as Irma mentioned, you also need to have a keen attention to detail and a willingness to tackle problems creatively. As a UX/UI designer, you’ll need to balance aesthetics with functionality and security, and sometimes combining these factors can be challenging.

Finally, since the cybersecurity field is constantly changing, you have to be prepared to work in a fast-paced and high-pressure environment, as designers often work on multiple projects and must meet tight deadlines.

Irma: In terms of hard skills, proficiency in Figma is a must, while familiarity with Adobe AI, PS, HTML, CSS, and JavaScript is also important. Creating wireframes and prototypes, knowing user research methodologies, and following accessibility standards are all key. Knowledge of A/B testing and Google Analytics is also beneficial for deeper insights.

Teodora: Figma will definitely be your major tool in this role, along with the web technologies that Irma mentioned. Besides that, knowledge of user experience (UX) design principles, including user research, information architecture, prototyping, and testing, is a must if you want to work in this role. If you’d like to learn more about what UX/UI designer’s job looks like in the cybersecurity field, feel free to reach out to me on LinkedIn.

Irma: Once you join Nord Security, your professional growth will only accelerate. You’ll have access to a supportive community of experts who are always willing to share their knowledge and wisdom. And our learning and development team is absolutely amazing! They provide us with a wide range of learning opportunities, from internal and external training to mentorship programs, workshops, and knowledge-sharing events.

All these resources help us stay up-to-date with the latest trends and technologies in the field and continuously improve our skills. It’s inspiring to work for a company that truly invests in the growth and development of its team members.
Blog inside image girl 2

Exciting challenges

What are the challenges of working as a UX/UI designer at Nord Security?

Irma: As a UX/UI designer on the conversion rate optimization (CRO) team, my main focus is on creating designs that convert. The team helps me to identify pain points, problems, and opportunities for improvement on our website. Based on that, I create wireframes and prototypes and design A/B test variations for our landing pages.

The biggest challenge in this role is to visually communicate and translate complex security concepts and product features into clear, intuitive, and user-friendly designs.

Teodora: Another challenge is ensuring that our products are accessible and easy to use for all users, including those with disabilities. This involves designing interfaces and user experiences in a way that meets accessibility standards and considers their special needs. By doing so, we can provide a secure digital environment that is inclusive and accessible to all.

One more challenge in this role is finding common ground and ensuring that every stakeholder, from product managers to engineers who have different perspectives and priorities, is working towards the same goal. This challenge can be overcome through effective communication, collaboration, and finding a shared understanding of the project goals.

The impact of work

What is the impact of your work on the world’s fastest VPN?

Teodora: Well, my work has a direct impact on the experience of millions of users. One recent project I worked on was introducing a new navigation menu on our global website, which has already improved the user experience for many NordVPN users. Another was optimizing and raising interest for specific audiences in our Amazon (Indirect Sales) store, which has led to increased engagement and sales.

In addition, I am involved in daily suggestions and problem-solving decisions, such as optimizing our landing pages, localizing web content and adapting it to specific countries, etc. It’s amazing to think that my work is visible to millions of people across the globe and that every design decision I make has the potential to impact someone’s online security and privacy. This is a huge responsibility, but it’s also incredibly rewarding to know that I’m making a difference in the world.

Irma: My team and I have a direct impact on the world’s fastest VPN, NordVPN, by creating design solutions that significantly improve landing page conversions. Through data analysis, we were able to redesign sections with better UI and brand compatibility, improve storytelling for clearer communication, and enhance mobile UX on specific components.

Our work is crucial in making NordVPN more accessible to people worldwide, providing them with a secure and easy-to-use digital environment. By constantly improving the user experience, we are helping NordVPN to continue to grow and maintain its position as the leader in the VPN industry, serving millions of users worldwide.

Work in cybersecurity

Want to catch a glimpse of what working with other Nord Security products as a UX/UI designer looks like? Watch the Meet Nord People video. And if you’re ready to take the next step and join our team, explore our UX/UI designer opportunities here!
About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

How nameless malware steals your data (and gets away with it)

Imagine if malware got into your computer. In fact, how do you know it isn’t there already? With some help from third-party researchers, we uncovered and analyzed a database of stolen data. It’s big — and the victims likely never knew their files had been stolen.

The discovery of a stolen database

We want to make it clear: we did not purchase this database nor would we condone other parties doing it. A hacker group revealed the database location accidentally. The analysis of the database was conducted in partnership with a third-party company specializing in data breach research. The cloud provider hosting the data was notified so it can be taken down.

1.2 TB database of stolen data

The stolen database contained 1.2 TB of files, cookies, and credentials that came from 3.2 million Windows-based computers. The data was stolen between 2018 and 2020. The database included 2 billion cookies. The analysis revealed that over 400 million, or 22%, of those cookies were still valid at the time when the database was discovered.

We now know that the virus escaped with 6 million files it grabbed from Desktop and Downloads folders. 3 million text files, 900,00 image files, and 600,000+ Word files made up the bulk of the stolen database, but it also contained over 1,000 types of different files.

Screenshots made by the malware reveal that it spread via illegal software (Adobe Photoshop), Windows cracking tools, and pirated games. Moreover, the malware also photographed the user if the device had a webcam.

The dangers of custom malware

Just like with hurricanes, experts love naming dangerous malware. But computer viruses don’t have to have names to be capable of stealing lots of data. The truth is, anyone can get their hands on custom malware. It’s cheap, customizable, and can be found all over the web.

Dark web ads for these viruses uncover even more truth about this market. For instance, anyone can get their own custom malware and even lessons on how to use the stolen data for as little as $100. And custom does mean custom – advertisers promise that they can build a virus to attack virtually any app the buyer needs.

How to stay safe

Based on the feedback from the researchers, it may be impossible to tell whether a file is infected. If the malware is new, no antivirus can recognize it. The only way to stay safe is to follow good cyber hygiene rules:

  • Web browsers are not good at protecting sensitive data. Use password managers to protect your credentials and auto-fill information.
  • Malware can’t access encrypted files. Services like NordLocker protect your files both on your computer and the cloud, so malware can’t just grab them.
  • Some cookies are valid for 90 days, and some don’t expire for an entire year. Make deleting cookies a monthly habit.
  • Peer-to-peer networks are often used for spreading malware. Only download software from the developer’s website and other well-known sources.
  • All malware gets recognized eventually. Make sure that your antivirus is always updated to prevent old viruses from slipping through the cracks.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

How ScottMadden rolled out security integration with Azure AD

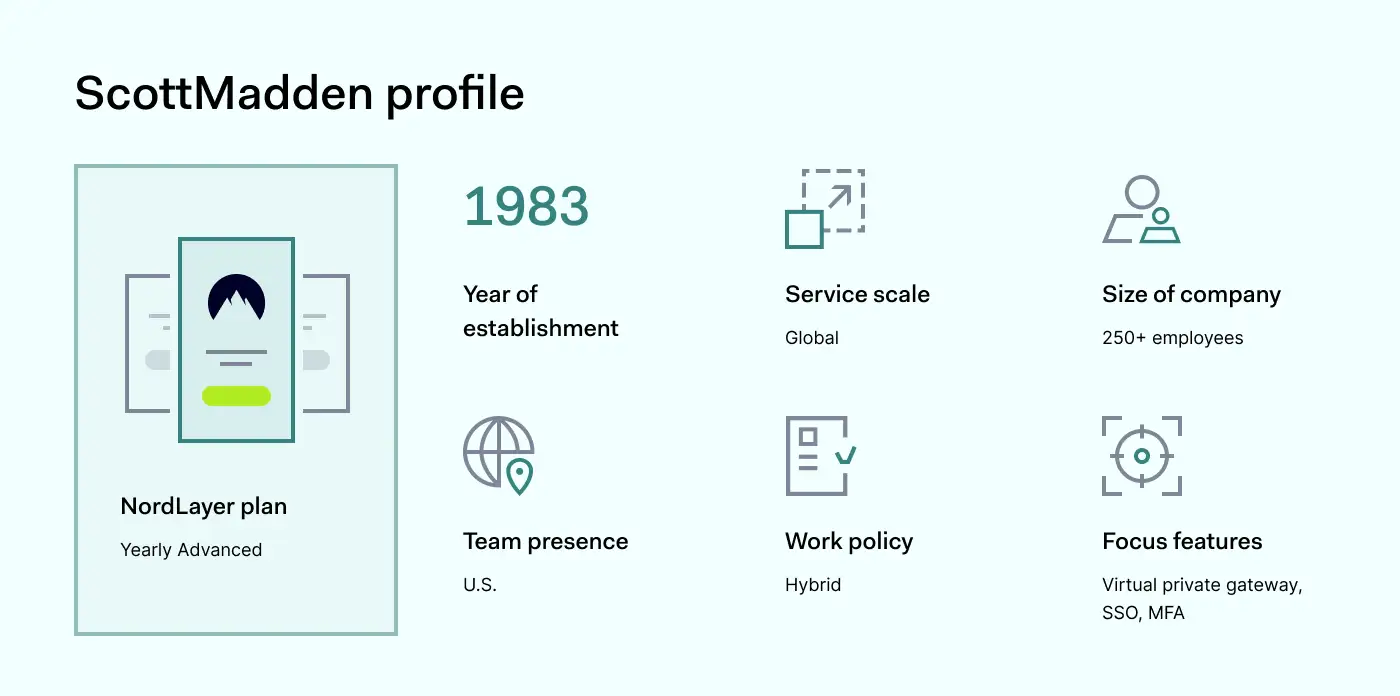
ScottMaden is a management consulting group that supports Fortune 500 companies. The service provider focuses on two primary business areas: the energy sector and corporate & shared services. With 40-year experience in the industry, ScottMadden provides its clients with strategic planning through implementation across different business fields and functions.

Addressing numerous global clientele challenges represents ScottMadden’s expertise in sophisticated planning. Therefore, how does a company with up to 250 full-time employees throughout the United States and three local East Coast offices face internal security issues? Clinton Miller, IT Director of ScottMadden, shares their story on filling in the missing links in the organization’s cybersecurity strategy.

The Challenge

Securing employees on the go the right way

The company consults domestic and international clients — employees travel quite a bit to client sites and work hands-on on their projects. Hence, a hybrid work model wasn’t the new normal for the organization once the pandemic hit.

ScottMadden consultants spend a lot of time in airports and other public spaces where they would connect to the airport or mobile hotspots and hotel wifi. Yet, the company’s solution wasn’t as good for protecting and running smoothly while traveling.

“The concern was to improve the existing security model and ensure our employees had an encrypted connection regardless of which network they were on.”

Click to tweet

Having better performance, following industry best practices, and fulfilling client requirements to protect data outside the office were the driving factors in looking for a change. But is there a solution that can solve the problem effectively and efficiently onboard?

The Solution

Streamlined client drive-out to different environments

The traveling ScottMadden consultants and employees working from home used to rely on browser-based encryption. Using built-in data encoding in Office365 applications allowed them to perform job tasks and communicate with teams with some security levels.

However, the issue was the poor connection flow while video conferencing — latency is a deal breaker for online business meetings in a remote setup.

“Everyone during the pandemic did a lot of video conferencing via Google Meet, Microsoft Teams, or Zoom. We aimed to ensure there was a minimal impact on video calls.”

Click to tweet

One thing is handling latency to elevate employees’ and clients’ experience. But can the transition process administratively have a minimal impact on existing company infrastructure and cybersecurity strategy?

“One of the things we wanted to do was to push out the client fairly easily, operating on an SSO solution already in use.”

Click to tweet

ScottMadden uses solution Azure AD single sign-on solution for user identification within the organization. The company operates in macOS and Windows environments, so the chosen solution had to fit into the criteria for integration and simplicity.

Why choose NordLayer?

NordLayer solution is compatible with major service providers on the market. Thus, the company could integrate with AzureAD IAM solution and roll out organization-wide onboarding to a new solution using existing SSO.

The endpoint management solution allowed remote access in macOS and Windows environments.

“The implementation of NordLayer went a lot easier when we connected clients to Azure AD. It relieved us from setting up new individual accounts for every 250+ people in the organization.”

Click to tweet

The IT Director handled the process — it didn’t require a lot of resources and time to deploy the solution in the organization.

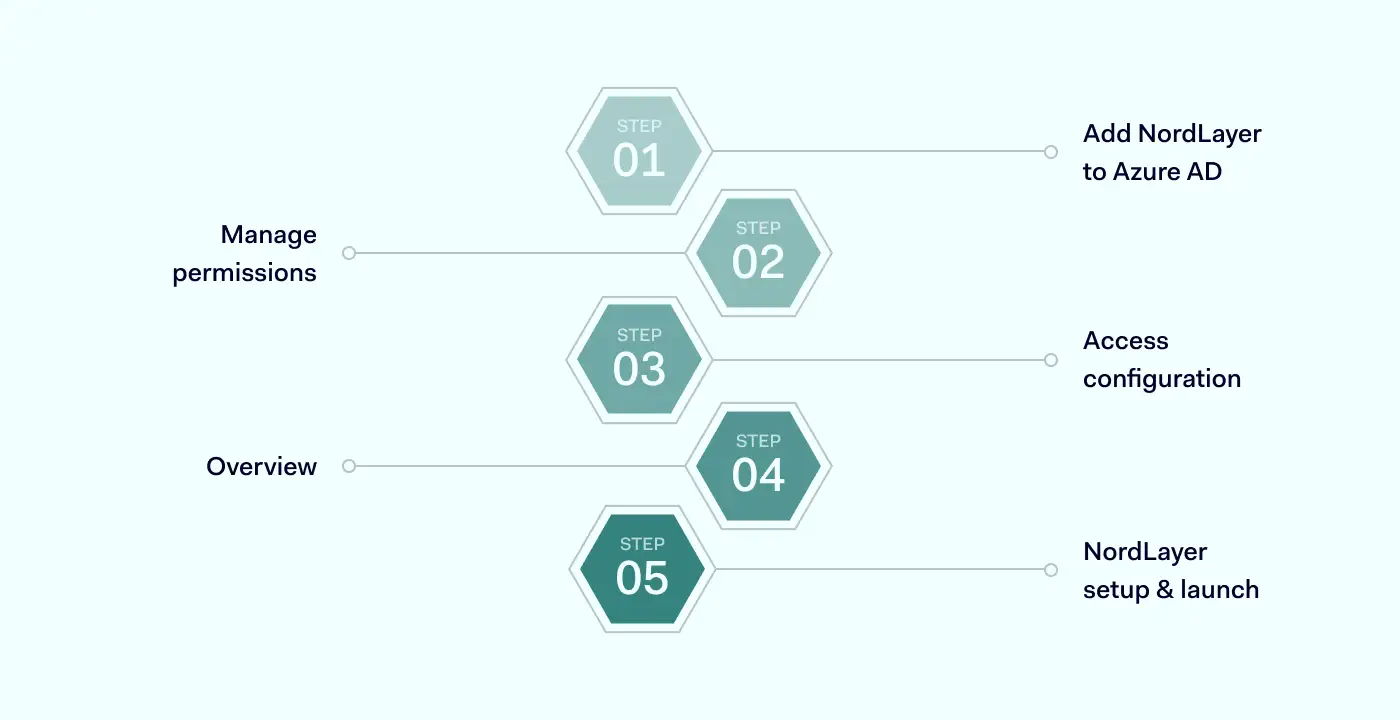
Organization onboarding using Azure AD by ScottMadden

According to Clinton Miller, the IT Director of the company, the longest step was to create an Azure group and add NordLayer. Once it was solved, the complete rollout to NordLayer solution took only a few hours.

The Outcome

Onboarding to a chosen solution enabled the company to secure team connections and extensive access to functionalities that comply with ScottMadden set benchmarks. Achieving data security didn’t have to compromise connection speed and video conferencing quality.

“Anytime employees are outside the office – at home or coffee shop – wherever they might be, we validated that they can reach all the services they needed, and speed wasn’t an issue.”

Click to tweet

The transition to the new tool was heavily based on the company’s SSO. The documentation, knowledge base, and support team are highly responsive with communication to walk IT leaders through the process.

“For other potential decision-makers: onboarding NordLayer isn’t a heavy lift — you have the support and knowledge base ready, so it’s pretty straightforward.”

Click to tweet

Moreover, NordLayer’s Control Panel provides a good cross-reference point for those using the tool while working outside the office by filtering ongoing active connections.

It also delivers another step in the reporting process for the IT admin and the whole organization. For instance, it verifies that the organization follows internal policies by exporting connection data to verify and justify to a third-party audit.

Pro cybersecurity tips

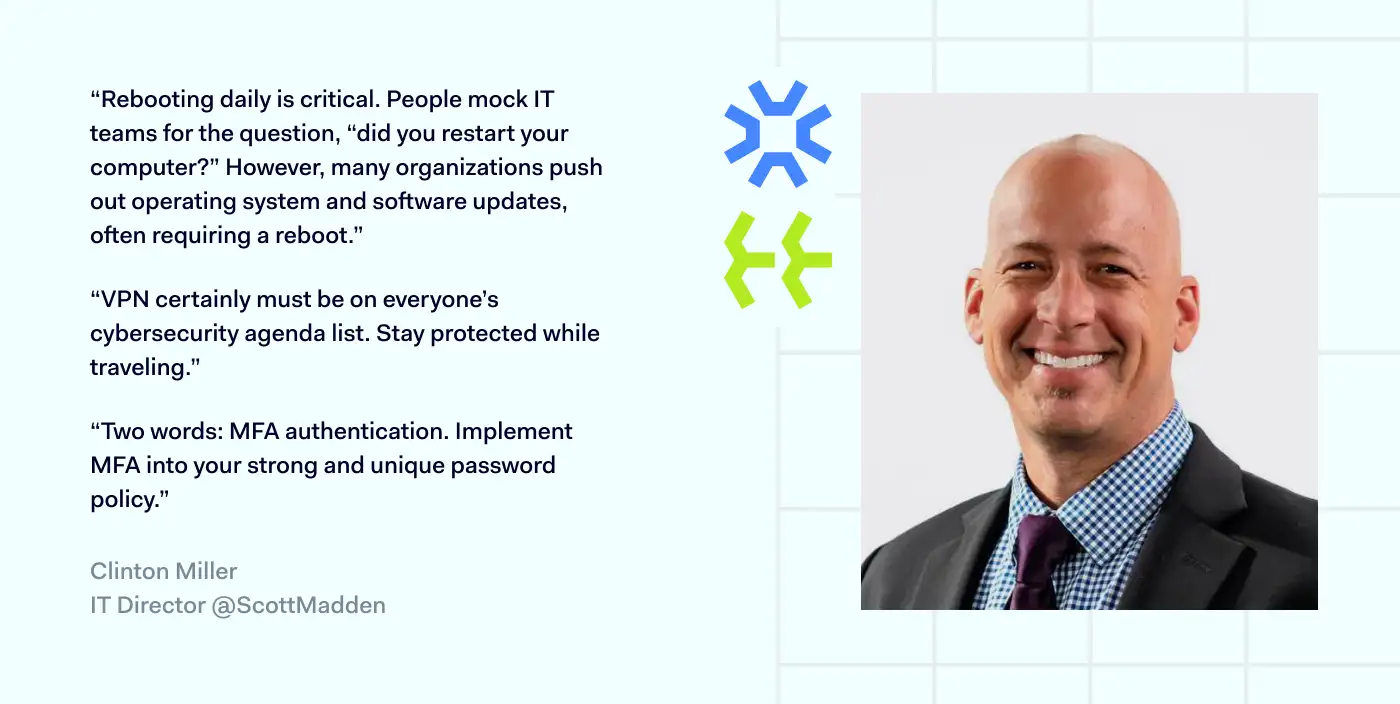
Different sectors, industries, and services, but the same goal unites every organization’s IT leaders — securing their company assets. Following best practices and professional knowledge helps achieve security targets easier. Clinton Miller, the IT Director at ScottMadden, shares his top-on-the-list tips:

Do you need to upgrade existing tools used in your organization to align with best practices in the industry, improve processes and performance for the team, or expand your capabilities of tracking and reviewing the implemented security strategy?

Using NordLayer, you can integrate more features and functionalities with the organization’s preferred tools, service providers, and IAM solutions. It is possible without committing to massive changes and re-organizing current policies and infrastructure. Reach out to find out about your options on how to secure connections for the off-office employees and improve their experience while working online.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Compliance Experts on What to Expect in 2023

The consequences of non-compliance can be devastating.

In 2023, businesses have more to fear than just the formal penalties issued by regulatory or legislative entities. With cybercrime rates at a seemingly all-time high, and even once-trusted cybersecurity companies proving susceptible to breaches, organizations are on high alert.

Failing to comply is more than just a compliance issue or an unchecked box. It can represent an unchecked vulnerability that may give way to a data breach that will have your brand name on consumers’ lips for all the wrong reasons.

That’s why we invited two compliance and security experts to speak on the future and state of compliance. Here’s a short recap of the conversation moderated by Gerald Kasulis, VP of business operations at Nord Security, with:

  • Deena Swatzie, SVP, Cyber Security Strategy and Digital Innovation at Truist,

  • Joy Bryan, GRC/Privacy Technology Analyst, RNSC Technologies, LLC.

Kasulis asked the panelists astute questions about the implications of adopting tech powered by AI, the current corporate climate, and how businesses can prioritize compliance on a shoestring budget.

Watch the webinar recording in full right now or keep reading to find out three takeaways that will help kickstart or support your compliance agenda this year.

Increasingly savvy consumers will hold businesses accountable

When data breaches happen, usually it’s the consumers who suffer. The consequences range in severity and kind, but whether major or minor, reputational or financial, a violation of one’s privacy through personal data exposure is never a welcome outcome.

As businesses become hyperaware of the likelihood of a data breach, consumers are equally tuned in.

quotes


Consumers are getting smarter in that [data privacy] space. They’re going to expect more, they’re going to hold companies accountable. And so that’s why your compliance needs to be in place.

– Joy Bryan

GRC/Privacy Technology Analyst at RNSC Technologies, LLC

Consumers are more likely than ever to want assurances that their personal data will be kept safe as concerns surrounding data privacy become more mainstream. They want to know how their information will be stored and what measures businesses are taking to protect it.

In today’s climate, trust is a linchpin of customer satisfaction. A recent survey revealed that 71% of consumers are unlikely to buy from a company that loses their trust — which is bad news for businesses that have suffered major breaches.

Meeting compliance standards and earning certifications can be a shorthand for establishing (or re-establishing) customers’ confidence: this ensures that businesses are following the agreed-upon best practices in a verifiable way.

At the end of the day, the buck stops with corporations who collect and store personal data. They will be held accountable for their (in)ability to protect the data they keep.

“Consider yourself as the consumer,” says Swatzie. She suggests that businesses should use the golden rule as a framework — treat consumer data as you would hope and expect yours to be treated.

Additional resources may not be the answer

quotes


Even when we talk about talent and the workforce, everyone’s immediate response is ‘we need more resources.’ You don’t always necessarily need more resources.

– Deena Swatzie

SVP, Cyber Security Strategy and Digital Innovation at Truist

Swatzie explained that it’s important to understand what exactly is required to meet compliance standards so that you can balance what you have with what you need. Here, collaboration between teams is key. Security and compliance initiatives will overlap.

Both experts agree that it’s best to start by looking at in-house tech and talent before making an investment. And on the occasion when you do require an additional resource, like software, be sure that you’re adopting tools that serve multiple functions.

quotes


I think that whatever platforms and technologies are implemented should have a collaborative feel — where you’re tackling multiple things at once.

– Joy Bryan

GRC/Privacy Technology Analyst at RNSC Technologies, LLC

NordPass Business, for instance, delivers so much more than password management. Get a powerful data breach scanner, password health metrics, a detailed activity log, company-wide advanced security settings, and multi-factor authentication.

On the topic of breaches, take solace in NordPass’ zero-knowledge architecture which ensures that only you hold the key to your business credentials and vault items. In the unlikely event of a breach at NordPass, your private information will remain encrypted and out of reach to cybercriminals.

New investments in tech solutions should add value to what many teams are likely to prioritize the most: workflow efficiency. Consider how and whether security and compliance tools speak to that need.

Get into the nitty gritty. Take the time to consider your existing and prospective tools’ full scope to avoid overinvesting in overlapping functions.

According to Swatzie, “Privacy is everybody’s responsibility. Security is everybody’s responsibility. Compliance is everyone’s responsibility.” For that reason, it’s important not to take buy-in for granted with a top-down approach.

Ask yourself: will my team be open to adopting this policy or software? Does it promote or detract from their respective top priorities?

The word of the day is “proactive”

If we had to summarize the experts’ advice in just two words: be proactive. Specifically, on the topic of lessons learned from a turbulent 2022:

quotes


I would hope that in terms of lessons learned, it allows businesses to be a little bit more proactive in their approach and in their strategies.

– Joy Bryan

GRC/Privacy Technology Analyst at RNSC Technologies, LLC

If your compliance and security strategy is only reactive, then it shows a lack of forward-thinking, meaning you’re likely to be continuously caught off guard and lagging behind. Swatzie suggests that compliance professionals and business leaders “put on their auditor hat.”

quotes


I’m used to being heavily regulated and audited so I’ve learned enough from the auditors to know exactly what they’re going to ask me before they ask me. So going back to what Joy said earlier, be as proactive as possible.

– Deena Swatzie

SVP, Cyber Security Strategy and Digital Innovation at Truist

Where possible, brace your business for what’s likely to come down the compliance pipeline by studying the standards themselves. With an intimate understanding of the “spirit of the law” you should be able to intuit what’s next and prepare accordingly.

That being said, it’s not a lack of motivation that leaves security and compliance professionals in a reactive position. When it comes to cyber incidents, board and senior leadership members sometimes struggle to see prevention as the cure — waiting until after an event has occurred to implement more stringent security measures.

To learn more about how to get buy-in from colleagues and management before the fact, read our guide on how to campaign internally for cybersecurity.

Summary

Facing increasingly savvy and appropriately demanding consumers, businesses should understand that they will be held accountable for breaches of personal data and plan accordingly.

But, that doesn’t necessarily mean rushing to acquire additional talent and technological resources. Invest wisely and make it count. In particular, security software should be multi-functional.

Finally, the key to success is in forward-thinking. Adopt a proactive strategy to avoid a constant scramble to respond after-the-fact.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

NordLayer features in review: DPI Lite

The lines are blurred in the modern business lifestyle. There’re no boundaries between employees working from the office or anywhere in the world. And technological privilege enables linking personal devices to work applications for user and organization convenience.

This flexibility and ability to be mobile also mean that business matters simultaneously mix with personal activities online. And mobility is not alone to blame — the internet is often a necessary tool to perform job tasks and operate in different organization layers. Uncontrolled access to the internet provides vast resources incompatible with the work environment. How to manage what employees can do online without imposing risks on the company?

Deep Packet Inspection (DPI) is one of the most straightforward tools that limit free roaming online while connected to the company network. Establishing a set of restrictions helps create a secure perimeter for online activities within the company network.

It’s an important feature that supports performance and security efforts. Non-work-related activities can distract and reduce productivity. Moreover, entering various websites and apps can lure employees into malicious activities, so DPI is a choice for IT administrators to get a grip on the company’s traffic flow.

DPI solution using NordLayer

NordLayer solution offers a DPI Lite feature that allows IT administrators to control what user-requested data goes through or gets blocked from entering the company’s network.

The DPI Lite technology at NordLayer works on nDPI open-source protocol classification engine. It offers the most popular and acknowledged services  (ports and protocols) that are used by websites and network apps to operate on the internet.

With NordLayer, admins choose specific ports and protocols they want to include in the custom-defined block list. The policy applies only when a user is connected to the organization’s virtual private gateway. Thus, employees who work on job-related projects can’t simultaneously use blocklisted online resources and network applications with restricted access.

How does NordLayer’s DPI Lite feature work?

The cloud-based feature is available only with a virtual private gateway configuration. It’s set to active within 24 hours upon request. IT admins can add or remove specific ports and protocols open to access through the company’s network. They can do it by submitting an inquiry via NordLayer’s Control Panel.

The IT administrators can navigate and choose from a wide range of alphabetically arranged services (no slot restriction) that cover dual-use online resources, potentially harmful to business operations:

  1. Apple services

  2. Domain Name System

  3. E-commerce

  4. Email client protocol/Email services

  5. File sharing

  6. Gaming

  7. Google services

  8. Hypertext Transfer Protocol

  9. Identity

  10. Infrastructure/Networking

  11. IP tunneling protocol

  12. Messaging protocol/services

  13. Microsoft services

  14. Monitoring/SCIM

  15. Music streaming services

  16. News services

  17. Peer-to-peer file sharing

  18. Remote Access

  19. Social media

  20. Software Development

  21. Streaming services

  22. VoIP protocol

  23. VPN services

  24. Other (miscellaneous)

Our internal data shows the tendency to stop services primarily related to unapproved Peer-to-peer file sharing, Social media, and Gaming categories. It comes as no surprise that customers are particularly interested in limiting access to non-work-related services that impose the biggest risks to company assets and staff performance.

Infographic for employee accessHowever, if an employee needs access to company-level blocked sources, for example, a Social Media Manager working on Facebook and LinkedIn, IT administrators can purchase a separate dedicated Virtual Private Gateway for such employees and configure it with fewer restrictions.
The categories expand to a complete list of 250 available ports and protocols. You can choose only certain types of services, like blocking all messaging services except Slack, used for organizational communication.

NordLayer’s DPI Lite feature is managed only by the IT administrator and doesn’t have an ON/OFF function on the user side. The feature operates on the Application layer (OSI model Level 7) and Browser layer (OSI model Level 3). It means DPI inspects incoming data on the web and within network apps.

Enabled DPI Lite runs when the user, connected to the company’s virtual private network (or VPN), sends a request to access online resources or uses network-dependent applications. Once disconnected from the organizational network, the DPI policy isn’t active. Thus, it’s crucial to permit access to internal resources and applications only when they are connected to the network.

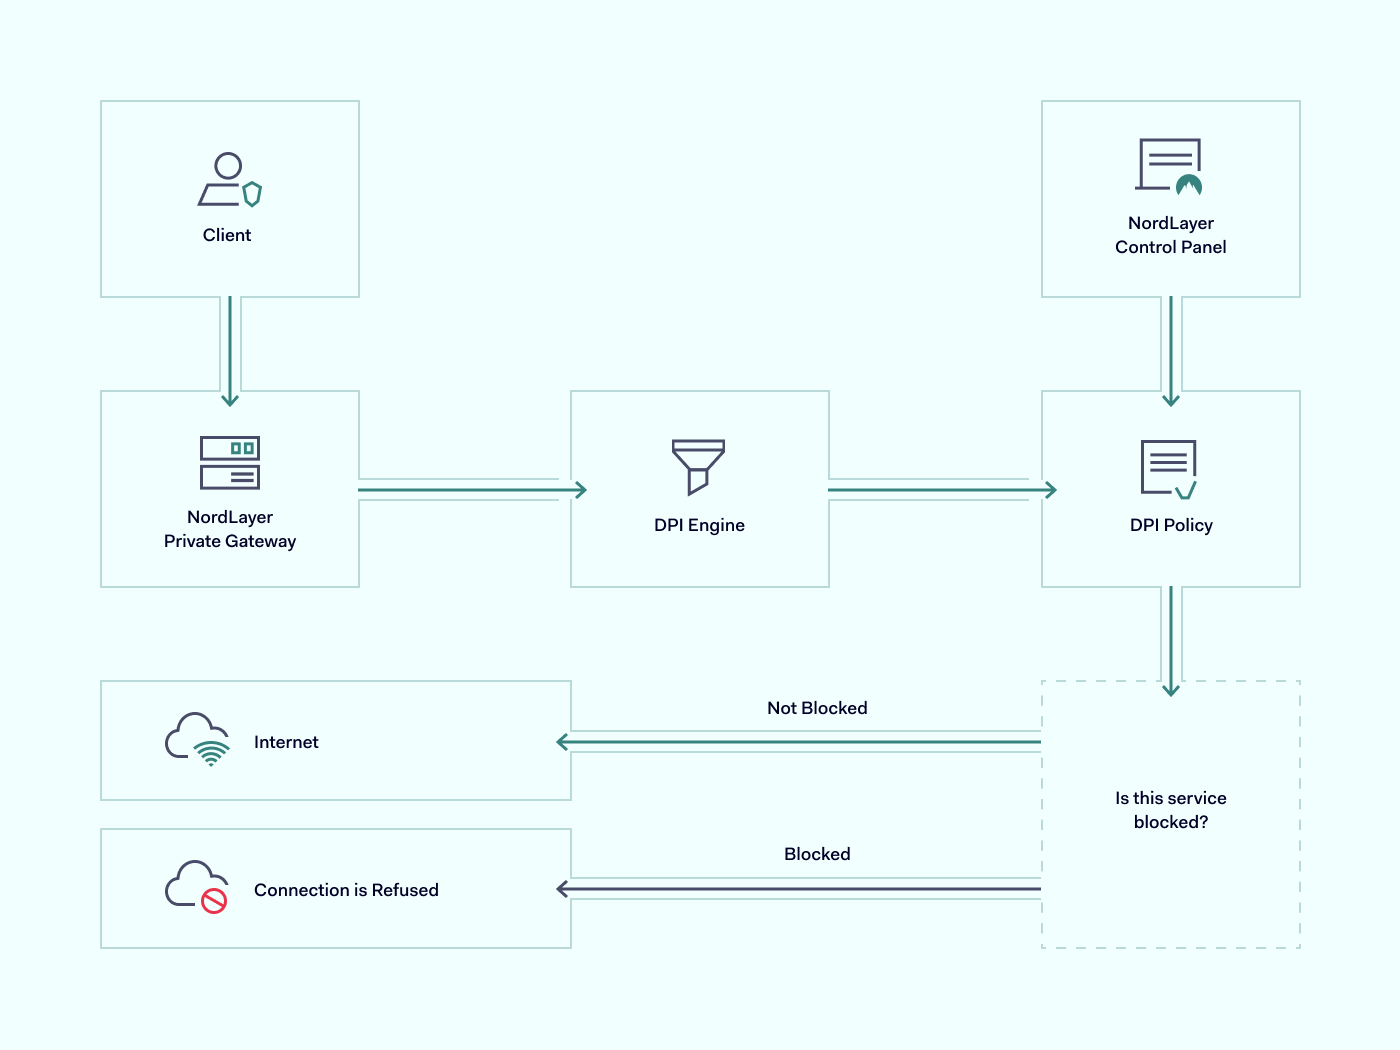
deep packet inspection scheme

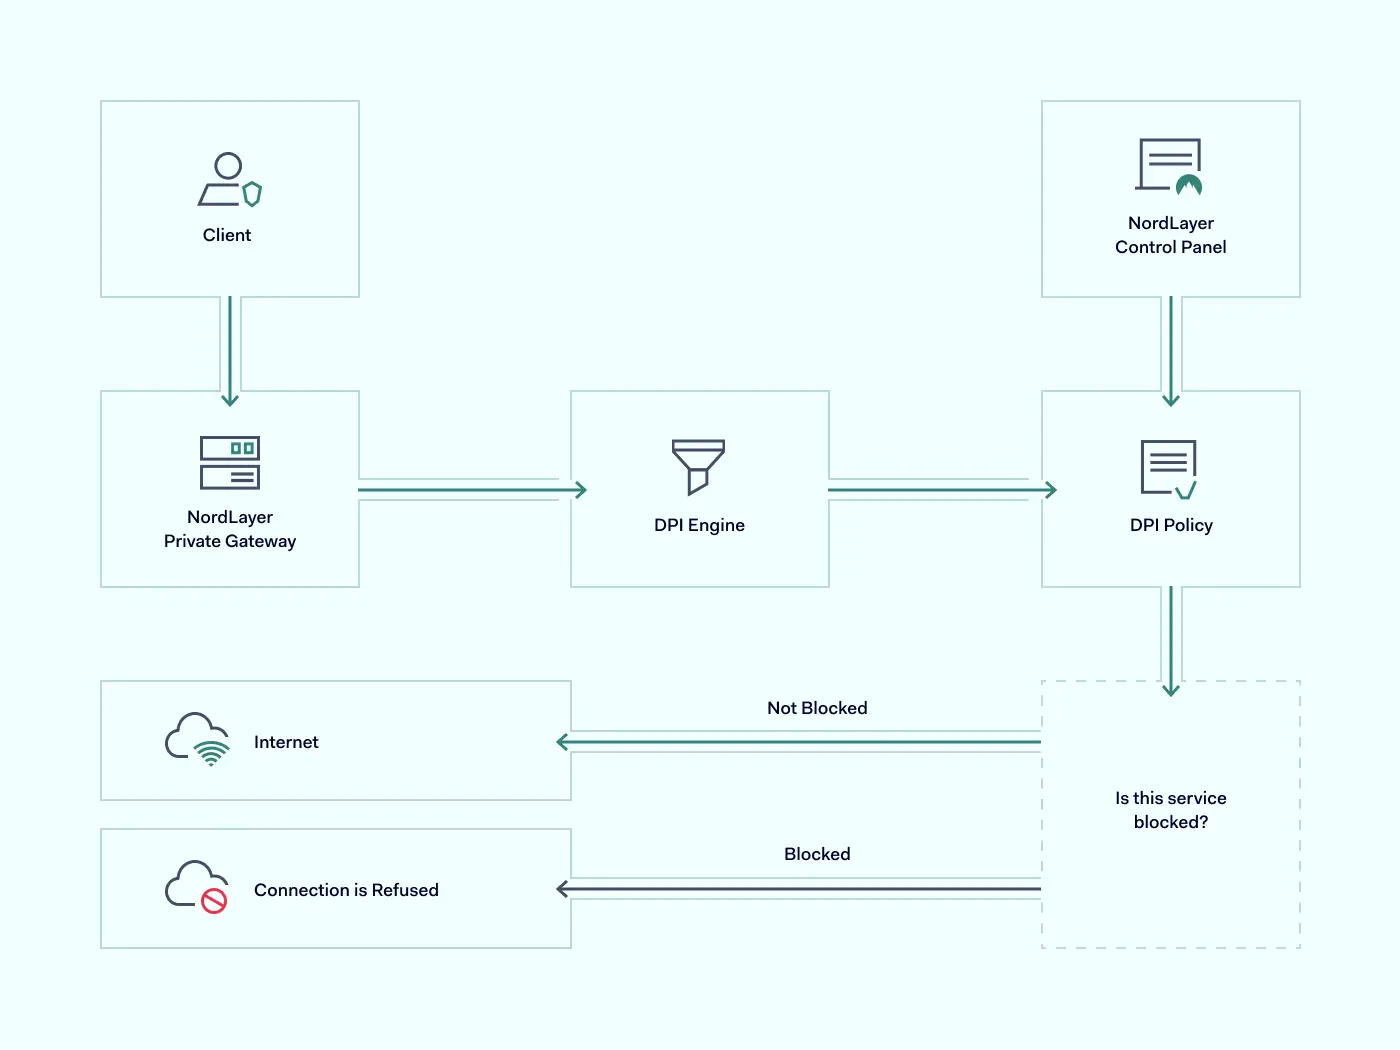
The incoming data is screened and filtered using the nDPI engine against the DPI Policy defined by the company’s IT administrator. The user is connected to a requested website if traveling data packets don’t include blocked services.

However, the connection to the requested online resource is restricted if there is a match between the data packet and the DPI block list policy.

How NordLayer’s DPI Lite is different?

Some solutions allow DPI to incorporate extensive categories and be customizable for every client’s preferences to restrict content online. However, a more complex approach may lead to excessive expenses. It may also require challenging configuration and become limiting to the company’s disadvantage.

Extensive data processing defined with all types of possible keywords can disrupt the connection flow and block access to online resources that initially weren’t intended to be restricted. On the other hand, if the company is set for hardware infrastructure and decides to continue with the same type of DPI technology, it will need to know how to configure and perform in-house maintenance. All these additional steps create an unnecessary workload for IT administrators.

To streamline the DPI implementation to the company infrastructure, NordLayer incorporates an easy-to-launch and control DPI Lite feature. It is cloud-native and easy to add or remove without investing in excessive resources. Its activation takes short notice and can be managed centrally, enabling flexibility and focus to the teams and operations:

  • Keep productivity on point. NordLayer’s DPI Lite feature encloses the company network with work-only online resources within employees’ reach. Leave no space for distractions, so teams are less likely to spend time on their personal activities and decrease the chances of human error.

  • Establish security levels. Entering unsecured websites or downloading data to work-linked endpoints can become a freeway for malicious actors accessing internal data and resources. DPI Lite can help filter out hidden remote computer access and control software planted by cybercriminals.

  • Quick implementation and adoption. DPI Lite, like all the other NordLayer features, is entirely cloud-based and thus simple to integrate into existing infrastructure. Besides short enablement time, it is compatible with other data processing features like DNS filtering by category, constructing a more robust organization security posture.

  • Easy to adhere to business needs. The categories or services of DPI Lite are simple to manage. A complete list or a few exceptions can be added or removed from the DPI Policy as required to suit the company’s service scope.

NordLayer offers a packet inspection solution that doesn’t overwhelm network security strategy and focuses on the most common business pain points. A well-sifted service list doesn’t leave space to overthink data to block or spend time researching what online resources to consider, so no openings are left. Overall, DPI Lite helps organizations handle their teams’ efficiency and activity while at work.

Benefits of DPI Lite

Establishing limits for online activity while working is like a reminder to focus on your tasks. But it’s not just about preventing employees from distractions using company gateways.

Adding DPI Lite as an additional security measure fortifies network security and advances business performance in different ways.

Prevent data leaking

Whether intentional or accidental, data leaks are damaging to businesses. DPI Lite adds to security measures by restricting the download of data-leaking apps or the usage of data-sharing and emailing services. Suppose employees try to send files from the company network via Dropbox or Google Drive. In that case, DPI Lite will recognize data packets containing related ports, protocols, and headers and will stop the action from completing the request.

Eliminate traffic overload

Online activities create traffic on network gateways: the more requests, the more overloaded infrastructure, ultimately resulting in performance issues. DPI Lite implementation to the virtual private gateways helps limit created traffic as users cannot access online resources. Online streaming and seeding services or visual-heavy social media increase network usage a few folds. Hence, with DPI blocking, fewer data packets must be inspected and unclog the network. Out of user sight, out of admin mind.

Protect static IP addresses

Unrestricted internet usage could create convenient conditions for employees to hide behind company IP addresses to perform illegal activities. For example, using torrents on a work network can result in copyright holders initiating blocked IP addresses or even legal prosecution for piracy on the organizational level.

With open internet access, scam attempts have a free pass. If law enforcement authorities identify IP during their investigation of a crime done by your employee from the company’s IP address, it might lead to the company’s liability and even hardware confiscation. Hence, whether the network is managed internally or via a vendor like Internet Service Provider (ISP), deep packet inspection as an additional security measure can help establish internal online activity limits to prevent any illicit acts from happening under the company name.

Entering NordLayer’s DPI Lite

Organization-first mindset while at work or dealing with company-related content can be seen as restricting user activity. Although it’s a strong push toward cybersecurity strategy implementation, preventing possible gaps and openings.

Deep packet inspection is part of the bigger picture when combined with other NordLayer security features like DNS filtering by category, ThreatBlock, and Jailbroken/rooted device detection. Enforcing our remote network access solution into your company infrastructure and activating the DPI Lite feature is a matter of a couple of days or less. Organization administrators need to access NordLayer Control Panel, navigate to Servers or Gateways under the Network tab, and configure it by selecting Deep Packet Inspection (Lite) categories as required.

Utilizing simple and affordable tools like NordLayer’s DPI Lite doesn’t overcomplicate the existing cybersecurity strategy and upgrades team productivity, network performance, and company security for better business performance.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.