Skip to content

ESET Research discovers new China-aligned APT group Blackwood that uses advanced implant to attack within China, Japan, and the UK

  • ESET Research has discovered the NSPX30 implant being deployed via the update mechanisms of legitimate software, such as Tencent QQ, WPS Office, and Sogou Pinyin, and attributes this activity to a new China-aligned APT group ESET named Blackwood. 
  • ESET has detected the implant in targeted attacks against both Chinese and Japanese companies as well as against individuals located in China, Japan, and the United Kingdom. The aim of the attack is cyberespionage.
  • The implant was designed around the attackers’ capability to conduct packet interception, enabling NSPX30 operators to hide their infrastructure.

BRATISLAVA, MONTREAL — January 24, 2024 — ESET researchers have discovered NSPX30, a sophisticated implant used by a new China-aligned APT group, named Blackwood by ESET. Blackwood leverages adversary-in-the-middle techniques to hijack update requests from legitimate software to deliver the implant. It has carried out cyberespionage operations against individuals and companies from China, Japan, and the United Kingdom. ESET mapped the evolution of NSPX30 back to an earlier ancestor – a simple backdoor we have named Project Wood. The oldest sample found was compiled in 2005.

ESET Research named Blackwood and the backdoor Project Wood based on a recurring theme in a mutex name. A mutex, or mutual exclusion, is a synchronization tool used to control access to a shared resource. The Project Wood implant from 2005 appears to be the work of developers with experience in malware development, given the techniques implemented. ESET believes that the China-aligned threat actor we have named Blackwood has been operating since at least 2018. In 2020, ESET detected a surge of malicious activity on a targeted system located in China. The machine had become what is commonly referred to as a “threat magnet,” as ESET Research detected attempts by attackers to use malware toolkits associated with multiple APT groups.

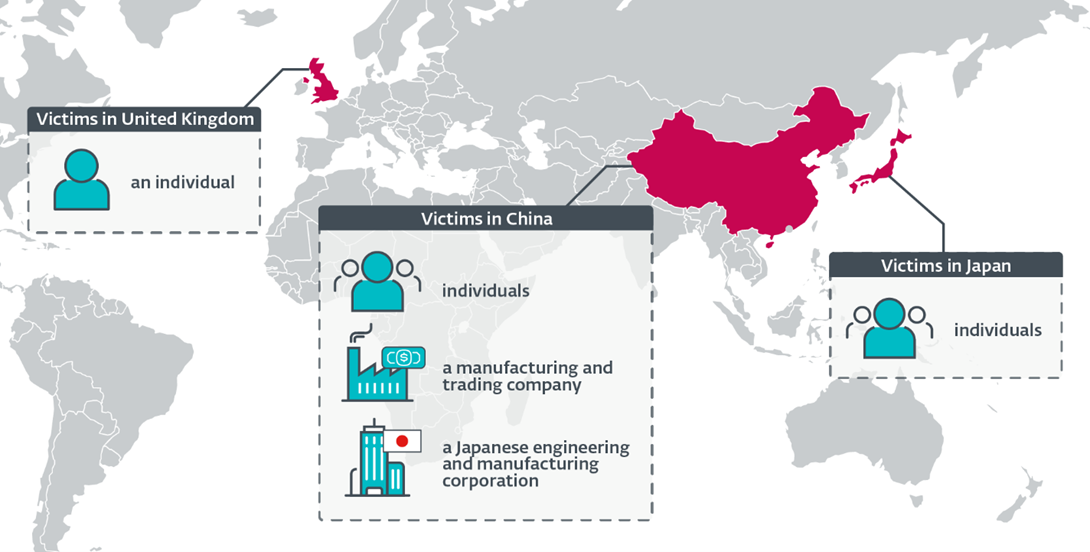
According to ESET telemetry, the NSPX30 implant was recently detected on a small number of systems. The victims include unidentified individuals located in China and Japan, an unidentified Chinese-speaking individual connected to the network of a high-profile public research university in the United Kingdom, a large manufacturing and trading company in China, and China-based offices of a Japanese corporation in the engineering and manufacturing vertical. ESET has also observed that the attackers attempt to re-compromise systems if access is lost.

NSPX30 is a multistage implant that includes several components, such as a dropper, an installer, loaders, an orchestrator, and a backdoor. Both of the latter components have their own sets of plugins that implement spying capabilities for several applications, such as Skype, Telegram, Tencent QQ, and WeChat, among others. It is also capable of allowlisting itself in several Chinese antimalware solutions. Using ESET telemetry, ESET Research determined that machines are compromised when legitimate software attempts to download updates from legitimate servers using the (unencrypted) HTTP protocol. Hijacked software updates include those for popular Chinese software, such as Tencent QQ, Sogou Pinyin, and WPS Office. The basic purpose of the backdoor is to communicate with its controller and exfiltrate collected data; it is capable of taking screenshots, keylogging, and collecting various information.

The attackers’ capability for interception also allows them to anonymize their real infrastructure, as the orchestrator and the backdoor contact legitimate networks owned by Baidu to download new components or exfiltrate collected information. ESET believes that the malicious but legitimate-looking traffic generated by NSPX30 is forwarded to the real attackers’ infrastructure by the unknown interception mechanism that also performs adversary-in-the-middle attacks.

“How exactly the attackers are able to deliver NSPX30 as malicious updates remains unknown to us, as we have yet to discover the tool that enables the attackers to compromise their targets initially,” says ESET researcher Facundo Muñoz, who discovered NSPX30 and Blackwood. “However, based on our own experience with China-aligned threat actors who exhibit these capabilities, as well as recent research on router implants attributed to another China-aligned group, MustangPanda, we speculate that the attackers are deploying a network implant within the networks of the victims, possibly on vulnerable network appliances, such as routers or gateways,” explains Muñoz.

For more technical information about the new China-aligned APT group Blackwood and its latest NSPX30 implant, check out the blog post “NSPX30: A sophisticated AitM-enabled implant evolving since 2005.” Make sure to follow ESET Research on Twitter (today known as X) for the latest news from ESET Research.

Geographical distribution of Blackwood victims
About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

ESET achieves the Champion position in Canalys Global Cybersecurity Leadership Matrix 2023

BRATISLAVA, — January 22, 2024 —  ESET, a global leader in digital security, maintains its Champion status for the fifth consecutive year in the latest Cybersecurity Leadership Matrix from Canalys. With this milestone, it reaffirms its position as a world-renowned vendor of digital security and a top security provider for global partner networks.

According to Canalys, a leading global technology market analyst firm providing an overall assessment of the leading cybersecurity vendors with established channel programs, ESET is “one of a few full-spectrum cybersecurity vendors that cover consumer, SMB, enterprise, and MSP segments, giving it access to extensive threat intelligence.”

“Since beginning this company more than 30 years ago, we have been focusing on helping our partners develop their cybersecurity businesses and working to protect their customers against all types of threats by consistently innovating and reinforcing the protections offered by our multilayered technology. Focused improvement of our offering and being named a Champion for the fifth consecutive time affirm the impact of our efforts. We’re pleased to be rated highly by our partners, recognizing the value they place on the investments we’ve made to our platforms and systems,” said Miroslav Mikuš, President of Global Sales.

ESET’s ability to centrally plan and coordinate its go-to-market strategies and its policy of empowering both partners and country offices to run campaigns and sales executions relevant to local strengths are key contributors to its Champion status. Other key areas that have maintained high ratings among ESET´s partners are the quality of account management and technical support, together with overall ease of doing business.

ESET’s network now consists of more than 10,000 active MSPs and 24,000 active resellers. The MSP segment, with its 30% revenue growth, remains a core part of ESET’s strategy. The company has strengthened its proposition by enabling MSPs to offer Inspect and Inspect Cloud XDR solutions and both the ESET Professional and Security Services portfolios, including health checks and MDR.

“ESET’s consistency of engagement and support, as well as focused partner enablement to run campaigns and execute sales initiatives relevant to local strengths, were key contributors to its success in the channel,” said Matthew Ball, Chief Analyst at Canalys. “Partners highly rated its commitment and ease of doing business, as well as the quality of account management.”

The Canalys Cybersecurity Leadership Matrix assessed 29 cybersecurity vendors on their global channel and market performance over the latest 12-month period. The matrix combines three primary types of inputs: partner feedback from Canalys’ Vendor Benchmark ratings with an independent analysis of each vendor’s momentum in the channel based on their investments, strategy, execution and market performance metrics as the vendor´s growth and market share within the peer groups.

To find out more about the Canalys Leadership Matrix Awards, visit the website here.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

ESET Launches a New Managed Detection and Response (MDR) Service to Elevate Cybersecurity for Small and Medium-Sized Businesses (SMBs)

  • ESET launches new 24/7 SMB-focused MDR service.
  • The new ESET MDR service provides threat monitoring, detection and hunting, incident response, and robust detection and response capabilities.
  • Available in select countries as an add-on to ESET PROTECT Enterprise and ESET PROTECT Elite.

BRATISLAVA — January 17, 2024 —  ESET, a global leader in cybersecurity, has announced the launch of ESET MDR, an innovative solution aimed at addressing the evolving cybersecurity challenges faced by SMBs. This launch marks a significant stride in expanding ESET’s security services portfolio with another MDR solution.

In a rapidly changing threat landscape, organizations seek MDR service providers to enhance their security postures, reduce false positives and fortify their threat detection, investigation, and response capabilities. The ESET MDR service for SMBs is designed specifically to meet these needs and bring immediate benefits, including immediate response to incidents.

ESET’s MDR service offers a range of key features and benefits to enhance organizations’ cybersecurity postures. It combines AI-powered automation with human expertise and comprehensive threat intelligence knowledge for unmatched threat detection and incident response. The access to 24/7/365 security service ensures a bridge for expertise gaps and relieves pressure on internal security teams, allowing them to focus on strategic initiatives — all while facilitating regulatory compliance, helping businesses achieve key cyber controls necessary for insurability.

Delivered through the renowned ESET PROTECT Platform and the ESET XDR offering, the ESET MDR service is crafted to promptly investigate and disrupt malicious activities and thwart adversaries. The service is tailored to meet the challenges of hybrid work environments by conducting threat hunting, monitoring, and response, enforcing robust cybersecurity measures that address SMB customers’ needs.

ESET MDR can quickly detect and respond to threats within a 20-minute time frame. To do so, ESET uses its own innovative cybersecurity technologies to collect unique data, particularly from regions under attack from sophisticated cyber-criminal groups. To ensure effective threat defense, customers also have access to a library of predefined patterns and the ability to create custom rules patterns, which trigger appropriate actions in response to both specific detections and suspicious behaviors, executables, and processes.

“Dynamic — that is what the threat landscape is. It’s one where adversaries increasingly target SMBs, who are in many cases defenseless due to their lack of expertise, capacity, or both — often they are simply busy doing “their day jobs.” ESET, a long-standing expert in cybersecurity with an exceptionally strong position among SMBs and more than 500 000 SMB customers, sees tremendous potential in offering an affordable, scalable service. Our approach significantly reduces the risk of SMBs falling victim to ransomware attacks and other forms of security incidents and can help them meet various compliance regulations. Launching ESET MDR for SMBs represents a simple upgrade path for existing customers of our ESET PROTECT Platform, integrating all of our security modules with a 24/7 MDR service, one powered by our long-lasting threat intelligence expertise,” said Michal Jankech, vice president of the SMB and MSP segment at ESET.

The ESET MDR service will be available in selected countries as an add-on or stand-alone offering, packaged with ESET PROTECT Enterprise and ESET PROTECT Elite.

For more detailed information about ESET and its MDR solutions for SMBs, please read here.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Understanding the Power of Managed Detection and Response (MDR) for Small and Medium-Sized Businesses (SMBs)

How an MDR service can enhance the cybersecurity of SMBs

The 2022 SMB Digital Security Sentiment Report shows that the majority of small and medium-sized businesses (SMBs) perceive themselves as more susceptible to cyberattacks compared to larger enterprises. These SMBs express concerns regarding the potential consequences of such attacks, particularly emphasizing data loss, financial ramifications, and a drop in customer confidence and trust. Interestingly, despite these concerns, their investments in cybersecurity have not yet aligned with the evolving dynamics of their operational models.

The continued adoption of cloud computing, still-emerging hybrid workplace practices, and increased digital supply chain complexities all have led to a rise in data breaches and, thus, a more pressing need for enhanced cybersecurity measures. However, a purely reactive approach isn’t enough; critically, preventive measures are required  as cybercriminals have become more sophisticated in finding ways into corporate networks. Here, traditional security measures may fall short, highlighting the critical need for advanced solutions tailored to the specific requirements of businesses. One such solution gaining prominence is Managed Detection and Response (MDR).

MDR: A Trusted Partner for SMBs

As mentioned in Gartner® latest report, Gartner [Emerging Tech: Security — Adoption Growth Insights for Managed Detection and Response, Matt Milone, Travis Lee, Mark Wah, Published 30 June 2023]:
“MDR growth will continue as customers of all sizes embrace providers’ ability to effectively deliver managed threat disruption and containment. An increasing number of MDR customers of all sizes demand that providers are able to remotely initiate measures for active containment or disruption of a threat. Provider-delivered response actions and not just simple alert communications assist clients with their lack of security personnel and expertise. Factors including trust, geography and the security maturity of the consuming organization affect adoption of provider-led or guided response activities.”
MDR presents a favorable solution for SMBs by outsourcing the management of Extended Detection and Response (XDR) to cybersecurity providers.

Let’s delve into the core needs of SMBs related to threat detection and response and how MDR services answer them:

1. Access to additional security expertise

MDR serves as a bridge, helping you overcome expertise gaps in your security capacity by providing access to industry-leading cybersecurity professionals. Make sure your MDR partner offers local language support with a global presence. Attain top-tier protection without requiring internal security experts, or remove bottlenecks in your security operations team that may impede efficient detection and response. MDR services can be tailored to fit the specific needs and size of your business, ensuring you get the right level of protection without unnecessary complexities.

2. Enhanced detection and response capabilities

MDR goes beyond traditional cybersecurity measures, actively seeking and identifying potential threats before they can cause harm. They are tailored to detect cybersecurity breaches in the complex realm of hybrid work and enhance your capabilities to respond effectively to evolving cyber threats, such as ransomware as a service (RaaS). Opt for providers with immediate AI-powered threat detection and response, known for high detection rates, low false positives, and a light overall footprint, as validated by independent analyst appraisals and customer reviews.

3. Always-on approach

Cyber threats are constant. MDR services operate around the clock, providing continuous monitoring and rapid response to security incidents, always ensuring incidents are addressed promptly. The 24/7/365 security capabilities of experts eliminate the need for an in-house security team and monitor the threat environment around the clock.

4. Regulatory compliance

If you are looking for regulatory compliance, MDR can help you achieve key cyber controls necessary for insurability, meeting critical components of cybersecurity insurance programs and regulatory compliance and, with that, reducing the risk of penalties and legal issues.

MDR is not just for enterprises

Despite lacking the extensive resources of their larger counterparts, smaller businesses possess confidential and valuable information that requires protection. And doing nothing costs more than protecting your business. MDR tailored for smaller businesses serves as a valuable addition to existing security and IT measures, enhancing overall protection and defense. This enables organizations to proactively identify, thwart, and respond to online threats before potential damage occurs. By leveraging an MDR service, small businesses can not only fortify their security but also gain the freedom to focus on essential aspects, such as expanding their businesses.

According to a report from Gartner [Emerging Tech: Security — Adoption Growth Insights for Managed Detection and Response, Matt Milone, Travis Lee, Mark Wah, 30 June 2023]:

  • “Overall MDR mind share increased 29.14% year over year with MDR adoption growth increasing 67% from 2021 to 2022.
  • Growth is highest in education and steady across most industries, with a marked decline in energy and utilities.
  • Mind share increases with the largest companies, while adoption interest increases across private- and public-sector companies of most sizes.
  • Executive buyers have shown a significant increase in commitment through adoption interest, but the technical job role remains the dominant persona.
  • The largest market remains North America with a notable decrease in adoption interest in the Latin American market.”

This data suggests that there continues to be strong MDR demand regardless of company size and industry vertical. This is then highlighted and confirmed by the above-mentioned report, which says, “This is a trend we should expect to see continue over the next two to five years as the demand for MDR services continues to grow.”

Having an MDR service that offers capabilities beyond what a business can independently manage and has considerations for all business configurations and verticals, is, therefore, particularly important for SMBs. This is due to their varying size and focus, as they need a service that can go a step beyond conventional protection.

About ESET MDR

Our MDR service for SMBs is specifically designed to meet the above outlined needs and bring immediate benefits, especially to SMBs.

Delivered via our renowned ESET PROTECT Platform and ESET Inspect, the XDR-enabling component, we designed our ESET MDR service to swiftly examine and disrupt malicious activities and counteract adversaries. Specifically adapted for the intricacies of hybrid work settings, the service conducts threat hunting, monitoring, and response, ensuring the implementation of strong cybersecurity measures suitable for customers across varying sizes and security maturity levels.

Leveraging the knowledge of security professionals, ESET MDR can rapidly identify and counter threats within a 20-minute window. We utilize our proprietary antivirus software to gather exclusive data, especially from regions targeted by advanced hacker groups. As a customer, you can also leverage the signal hunting library, which contains pre-built behavior patterns for robust threat defense.

The ESET MDR service is available as an add-on or stand-alone offering, packaged with ESET PROTECT Enterprise and ESET PROTECT Elite.

Conclusion

Numerous cyberattacks continue to target many small organizations, posing a persistent threat regardless of business size. Unidentified threats always loom, ready to compromise systems. In the quest for security, every organization, regardless of size and industry, can benefit from the assistance and mitigation apabilities offered by MDR.

MDR emerges as a trusted ally for you, empowering you with powerful cybersecurity solutions that overcome traditional limitations. The combination of advanced technology, expert support, and a focus on compliance positions MDR as a beacon of security in the complex digital landscape. As cyber threats continue to evolve, embracing MDR services becomes not just a choice but a strategic imperative for your business.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

ESET AI’s advantage in Threat Detection, Investigation and Response (TDIR)

In the ever-evolving landscape of cybersecurity, the role of Artificial Intelligence (AI) has become indispensable, particularly in the realms of threat detection, investigation, and response (TDIR). At ESET we have been harnessing the power of AI for over three decades providing real-world solutions that meet the dynamic challenges of cybersecurity.

What is TDIR?

Threat, detection, investigation and response is a risk-based strategy for effectively mitigating cybersecurity threats and enhancing the efficiency of threat detection. The foundational capabilities of TDIR are pivotal in shaping how tools within a Security Operations Center (SOC) contribute to the overall mission and strategy of the SOC. TDIR capabilities empower contemporary SOC staff to adeptly design, configure, and manage security detection use cases. Notably, the top use cases for Artificial Intelligence (AI) in the TDIR process underscore the persistent requirement for human engagement, reinforcing the symbiotic relationship between advanced technology and human expertise.

AI in TDIR

As a representative vendor we have been interviewed for Gartner’s latest report “Emerging Tech – Top Use Cases for AI in Threat Detection, Investigation and Responses”. The emphasis was on exploring how providers plan to leverage AI to augment and support analysts in the Threat Detection, Investigation, and Response process. Gartner’s report provides valuable insights into the advancements made in enhancing TDIR services or products through the integration of AI.

Supervised ML for Enhanced Threat Detection:

One of the key takeaways from the Report is the increasing reliance on supervised Machine Learning (ML) by security providers: “For years, security vendors have been integrating AI into their products and threat detection processes, to enable them to identify anomalies and patterns that surpass human capabilities at scale. In fact, over 50% of interviewed security service and tech providers claim to already be using supervised ML-based AI coupled with supervised training to enhance their threat detection abilities.” [Source: Gartner: Emerging Tech: Top Use Cases for AI in Threat Detection, Investigation and Response. Travis Lee, Matt Milone, Elizabeth Kim, John Collins. [27 October 2023] ID: G00790125]

With a legacy dating back to 1990, ESET has been a forerunner in the integration of AI into its security solutions. Recognizing the evolving nature of cyber threats, we embraced the potential of AI early on, leveraging its capabilities to not only detect but also block threats in real-time.

ESET LiveSense, our versatile set of proprietary, multi-layered technologies, surpasses the capabilities of standard solutions. We use machine learning to combat new threats and can ensure continuous threat intelligence updates through the early adoption of cloud technology that powers our global ESET LiveGrid reputation & response system.

At ESET we employ two distinct forms of Advanced Machine Learning, comprising a high-powered detection engine in the cloud and a lightweight version deployed on the endpoint. These utilize a carefully selected set of classification algorithms, including deep learning and boosted trees, ensuring swift and precise analysis crucial for thwarting emerging threats.

Furthermore, the latest enhancement to our product ESET Inspect introduces an AI-powered detection correlation engine. This innovative feature automatically generates incidents, empowering security engineers to significantly minimize the time dedicated to investigation and incident management.

In conclusion, our pioneering journey with AI in TDIR represents a paradigm shift in cybersecurity.  Security vendors aim to differentiate themselves by improving detection results and reducing false positive/negative rates, adopting a “go fast and be safe” approach.

By leveraging the power of modern AI-techniques, we not only stay ahead of emerging threats but also set new standards for efficiency and accuracy in threat detection and response. As thought leaders in the cybersecurity space, we aim to continuously empower you with valuable insights, innovative solutions, and strategic recommendations, ensuring you are well-prepared to navigate the dynamic challenges of the digital age.

Objectivity Disclaimer
Gartner does not endorse any vendor, product or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.