

Skip to content

Don’t let your desire for love turn into lust for data


Asking for money or intimate photos is out of date. Romance scams are getting more sophisticated.

Valentine’s Day is coming up, but this holiday is not always a simple celebration of love with bouquets, chocolate, and romantic dinners. For those who are still on a quest to find the right partner, it may be a day highlighting how sad and lonely they feel. This feeling of loneliness, combined with a desire for a partner, is what many scammers prey upon.

With cybersecurity finally getting well-deserved attention in recent years, chances are that you’ve already noticed warnings about romance scams long before now. Using social networks and chat applications, scammers can pretend to be potential lovers, and after they open their victim’s heart, they also try to open their wallet.

However, with increasing levels of general digital security awareness, scammers’ tactics have evolved. Some no longer directly ask for money because, for example, their imaginary relative needs surgery. Instead, they send you just one risky sentence: “Let’s go chat somewhere else.”

Often, the victim is led down a path to a new unknown app, one that is offered on third-party app stores or websites that prompt you to download spy tools that are capable of reading your private data stored in your smartphone like it’s an open book. In these cases, your only defense is to have a reliable cybersecurity solution that can detect the app’s suspicious activities running in the background while you two lovebirds are chatting.

From connecting people to spying

Since ICQ, “I Seek You,” one of the most popular online messaging apps to hit the internet in the mid-1990s, introduced its service globally, the popularity of messaging apps has seen constant growth.

Let’s take one of today’s most popular messaging apps, WhatsApp, as an example. Since its launch on February 24, 2009, WhatsApp has been constantly growing, reaching 2.49 billion quarterly users in Q3 2023.

Overall, the number of people using messaging apps surpassed 3.3 billion in 2023, with the vast majority using three services: WhatsApp, Facebook Messenger, and WeChat.

However, scammers have also been looking at those numbers amorously, and messaging apps have quickly become a platform for both phishing and online romance scams, amongst other threats.

In just three years – from 2019 to 2022 – the amount of losses attributed to romance scams reported to the U.S. Federal Trade Commission (FTC) rose from $493M to $1.3B. Social networks and messaging applications were the first contact platform for 59% of those who said they lost money to a romance scam in 2022.

These numbers get even more serious when considering that the vast majority of fraud isn’t even reported to the government. A study conducted in 2021 found that only 4.8% of people who experienced mass-market consumer fraud bothered to complain to the non-profit Better Business Bureau or a government entity.

Love in a military uniform

Some recent cases show that romance scammers are not only going after your money but also lusting for data. Spyware inserted in apps has become a serious issue, and the latest ESET Threat Report calls attention to a surge in Android spyware detections, which have risen by 88.9%.

In the past, spying chat apps were often nonfunctional, and a targeted person could quickly figure out that something was not right and delete it immediately. Nowadays, these malicious apps are actually doing what victims expect them to do. For example, threat actors make a copy of a legitimate open-source functional chat app and just change its visuals. This means that the targeted person may not get suspicious and can be monitored for a long period of time.

In June 2023, ESET researchers published a blog about Android GravityRAT spyware being distributed within malicious but functional messaging apps BingeChat and Chatico, which were both based on the OMEMO Instant Messenger app. The spyware can exfiltrate call logs, contact lists, SMS messages, device location, basic device information, and files with specific extensions such as jpg, PNG, txt, pdf, etc.

The apps mentioned above were only available on phishing websites, not via official or third-part app stores, but how potential victims were tricked to go there and download them remains a mystery. However, when researchers at Qihoo 360, a Chinese cybersecurity company, analyzed different fake but functional chat apps bundled with spyware, they found that the motivation behind victims downloading these apps was due to “matters of the heart.”

In this case, attackers created multiple accounts on Facebook pretending to be love-seeking female users and added relevant Pakistani military personnel as friends to further obtain their contact information. Then, with the fake profiles and their hidden agenda, they wrote to victims that they were interested in pursuing a relationship, and had “found” a great new app where they could chat further.

While the individuals targeted probably thought they were falling head over heels in love, they were in fact unwillingly feeding threat actors sensitive personal information, along with military intelligence.

Don’t give your heart and data away so readily

To avoid being scammed, let’s begin with the basics and go through common romance scam red flags.

  • Making excuses to avoid meeting: The scammer will avoid a meeting in person despite repeatedly stating that they are willing to do so.
  • Things are moving too fast: Your new “partner” will express deep interest/affection and perhaps a desire for intimacy despite your having been chatting for only a few days.
  • Asking for money: Romance scammers often come with a heartbreaking story concerning why they need money as soon as possible. They can also pose as rich people who can pay their debts with interest but “right now, cannot access their funds.”
  • Leaving secure communication: The scammer may ask to leave a dating service or social media site to communicate directly.

Your chances of being scammed will also rapidly decrease when you use only trustworthy app stores with strict app review policies.

Your mobile’s chaperone

In case you’ve downloaded a malicious app, it’s good to have a powerful antivirus operating on your phone. This may be especially useful in cases where the app is fully functional and does not raise any obvious red flags.


ESET Mobile Security (EMS) can detect and block threats during the download process, even before installation occurs. This means that the threat never reaches the user. EMS can also be used to scan already existing apps to double-check that you haven’t bought the devil in disguise.

Moreover, EMS provides the user with real-time file system protection that scans all files in download folders for malicious code when opened, created, or run.

In the case of a malicious app or download, EMS alerts users that malicious code has been detected – as seen in the picture below.

You can also perform an on-demand scan anytime you want with two possible options:

1. Smart Scan goes through installed applications, executable files, SO files (SO stands for shared libraries), archives with a maximum scanning depth of three nested archives, and SD card content.

2. In-depthScan will check all file types, regardless of file-extensions, both in internal memory and on SD cards.

When ‘follow your mind’ advice won’t help you

When it comes to discussion of how to avoid disappointments in love, you often hear tips like “follow your mind, not your heart.” But if you are targeted by a sophisticated romance scam, chances are that such advice won’t help. This is true even for those who aren’t in a sad mood on Valentine’s Day.

In cases where your perception fails, you need reliable software equipped with advanced scanning capabilities to show you what your new chat app and new wannabe partner truly are.
About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

[重要通知] 伺服器將於 2024-02-17 (04:00 pm) 至 2024-02-18 (04:00 am) 進行定期維護

重要通知!

ESET 計劃在總部進行網絡核心基礎設施維護工作,將於香港時間 2024 年 2 月 17 日(星期六)下午 4 時至 2024 年 2 月 18 日(星期日)上午 4 時之間進行,維護時間大約為 12 小時。

此次維護將幾乎影響所有 ESET內部和外部服務。在此段期間,客戶可能無法進行購買訂閱、啟動及生產授權。

請注意,訂單系統、檢查授權詳細資料、啟動授權和網上商店等所有服務均將受到影響。

IMPORTANT !

ESET planned Network Core Infrastructure maintenance in ESET HQ which will take place on
Saturday, February 17th, 2024, from 4:00 PM to Sunday, February 18th, 2024, 4:00 AM, Hong Kong Time lasting 12 hours.

The impact of this outage covers ALMOST ALL ESET services, regardless internal or external.
It means in certain time within the maintenance window, customers might not place orders, activate license or generate license, etc.

That means Order System, Check Key, Key activation and eStore all affected.

關於Version 2

Version 2 Digital 是立足亞洲的增值代理商及IT開發者。公司在網絡安全、雲端、數據保護、終端設備、基礎設施、系統監控、存儲、網絡管理、商業生產力和通信產品等各個領域代理發展各種 IT 產品。透過公司龐大的網絡、通路、銷售點、分銷商及合作夥伴,Version 2 提供廣被市場讚賞的產品及服務。Version 2 的銷售網絡包括台灣、香港、澳門、中國大陸、新加坡、馬來西亞等各亞太地區,客戶來自各行各業,包括全球 1000 大跨國企業、上市公司、公用事業、醫療、金融、教育機構、政府部門、無數成功的中小企及來自亞洲各城市的消費市場客戶。

ESET Research joins global operation to disrupt the Grandoreiro banking trojan operating in Latin America and Spain

  • ESET worked alongside the Federal Police of Brazil in an attempt to disrupt the Grandoreiro botnet.
  • ESET contributed to the project by providing technical analysis, statistical information, and known command and control (C&C) server domain names and IP addresses.
  • This disruption operation was aimed at individuals who are believed to be high up in Grandoreiro’s operational hierarchy.
  • Further investigation performed by the Federal Police of Brazil led to the identification and arrest of the individuals in control of the botnet.
  • Grandoreiro has been active since at least 2017.
  • Grandoreiro targets Brazil, Mexico, Spain, and Argentina.
  • Grandoreiro can block a victim’s screen, log keystrokes, simulate mouse and keyboard activity, share the victim’s screen, and display fake pop-up windows.

BRATISLAVA, PRAGUE — January 30, 2024 — ESET collaborated with the Federal Police of Brazil in an attempt to disrupt the Grandoreiro botnet. ESET contributed to the project by providing technical analysis, statistical information, and known command and control (C&C) server domain names and IP addresses. Due to a design flaw in Grandoreiro’s network protocol, ESET researchers were also able to get a glimpse into the victimology.

This disruption operation was aimed at individuals who are believed to be high up in Grandoreiro’s operational hierarchy. The investigation by the Federal Police of Brazil led to multiple arrests. ESET researchers provided data crucial to identifying the accounts responsible for setting up and connecting to the Grandoreiro C&C servers.

Grandoreiro is one of many Latin American banking trojans. It has been active since at least 2017, and ESET researchers have been closely tracking it since then. Grandoreiro targets Brazil, Mexico, Spain, and, since 2023, Argentina.

Functionality-wise, Grandoreiro hasn’t changed very much since the last ESET Research blog post about the group in 2020. Despite that, Grandoreiro has been undergoing rapid and constant development. Occasionally, we even observed several new builds a week; for example, this has amounted to a new version on average every four days between February 2022 and June 2022.

The operator still has to interact manually with the compromised machine in order to steal a victim’s money. The malware allows the following actions:

  • Blocking victims’ screens
  • Logging keystrokes
  • Simulating mouse and keyboard activity
  • Sharing the victims’ screen(s)
  • Displaying fake pop-up windows

“ESET automated systems have processed tens of thousands of Grandoreiro samples. The domain generation algorithm (DGA) that the malware has used since around October 2020 produces one main domain per day, and it is the only way Grandoreiro is able to establish connection to a C&C server. Beside the current date, the DGA accepts a huge static configuration as well,” says ESET Researcher Jakub Souček, who coordinated the team that analyzed Grandoreiro and other Latin American banking trojans. “Grandoreiro is similar to other Latin American banking trojans mainly via its obvious core functionality and in bundling its downloaders within MSI installers.”

Grandoreiro’s implementation of its network protocol allowed ESET researchers to take a peek behind the curtain and get a glimpse of the victimology. Grandoreiro’s C&C servers give away information about victims connected at the time of the initial request made to each newly connected victim. By examining this data for more than a year, we conclude that 66% were Windows 10 users, 13% used Windows 7, Windows 8 represented 12%, and 9% were Windows 11 users. Since Grandoreiro reports unreliable geographical distribution of its victims, we refer to ESET telemetry: Spain accounts for 65% of all victims, followed by Mexico with 14%, Brazil with 7%, and Argentina with 5%; the remaining 9% of victims is located in other Latin American countries.. We also note that in 2023, we saw a significant decrease of Grandoreiro’s activity in Spain, compensated with increased campaigns in Mexico and Argentina.

For more technical information about Grandoreiro, check out the blog post “ESET takes part in global operation to disrupt the Grandoreiro banking trojan” on WeLiveSecurity. Make sure to follow ESET Research on Twitter (currently known as X) for the latest news from ESET Research.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

ESET Research discovers espionage apps on the attack in Pakistan, utilizing romance scams

  • ESET Research discovered a new cyberespionage campaign that, with a high level of confidence, ESET attributes to the Patchwork APT group.
  • The campaign leveraged Google Play to distribute six malicious apps bundled with VajraSpy RAT code; six more were distributed in the wild.
  • The apps on Google Play reached over 1,400 installs and are still available on alternative app stores.
  • Patchwork probably used a honey-trap romance scam to lure their victims into installing the malware.

BRATISLAVA, MONTREAL — February 1, 2024 — ESET researchers have identified 12 Android espionage apps that share the same malicious code; six were available on Google Play. All the observed applications were advertised as messaging tools, apart from one that posed as a news app. In the background, these apps covertly execute remote access trojan (RAT) code called VajraSpy, used for targeted espionage by the Patchwork APT group. The campaign mostly targeted users in Pakistan. Based on ESET’s investigation, the threat actors behind the trojanized apps probably used a honey-trap romance scam to lure their victims into installing the malware.

VajraSpy has a range of espionage functionalities that can be expanded based on the permissions granted to the app bundled with its code. It steals contacts, files, call logs, and SMS messages, but some of its implementations can even extract WhatsApp and Signal messages, record phone calls, and take pictures with the camera.

Based on available numbers, the malicious apps that used to be available on Google Play were downloaded more than 1,400 times. During the ESET investigation, weak operational security of one of the apps led to some victim data being exposed, which allowed researchers to geolocate 148 compromised devices in Pakistan and India. These were likely the actual targets of the attacks. ESET is a member of the App Defense Alliance and an active partner in the malware mitigation program, which aims to quickly find Potentially Harmful Applications and stop them before they ever make it onto Google Play. As a Google App Defense Alliance partner, ESET identified the malicious apps and reported them to Google, and they are no longer available on the Play store. However, the apps are still available on alternative app stores.

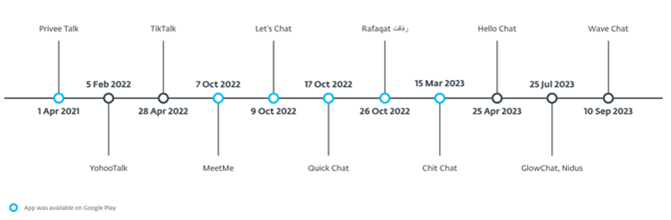
Last year, ESET detected a trojanized news app called Rafaqat being used to steal user information. Further research has uncovered several more applications with the same malicious code. In total, ESET analyzed 12 trojanized apps, six of which (including Rafaqat) had been available on Google Play, and six found in the wild – in the VirusTotal database. These apps had various names, such as Privee Talk, MeetMe, Let’s Chat, Quick Chat, Rafaqat, Chit Chat, YohooTalk, TikTalk, Hello Chat, Nidus, GlowChat, and Wave Chat.

To entice their victims, the threat actors likely used targeted honey-trap romance scams, initially contacting the victims on another platform and then convincing them to switch to a trojanized chat application. “Cybercriminals wield social engineering as a powerful weapon. We strongly recommend against clicking any links to download an application that are sent in a chat conversation. It can be hard to stay immune to spurious romantic advances, but it pays off to always be vigilant,” advises ESET researcher Lukáš Štefanko, who discovered this Android spyware.
According to the MITRE ATT&CK database, Patchwork has not been definitively attributed and only circumstantial evidence suggests the group may be a pro-Indian or Indian entity. This APT group targets mostly diplomatic and government entities.

For more technical information about VajraSpy and the spying apps from the Patchwork APT group, check out the blog post “VajraSpy: A Patchwork of espionage apps” on WeLiveSecurity.com. Make sure to follow ESET Research on X (formerly known as Twitter) for the latest news from ESET Research.

Timeline showing the dates when the trojanized apps became available 

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Understanding the Power of Managed Detection and Response (MDR) for Small and Medium-Sized Businesses (SMBs)

The 2022 SMB Digital Security Sentiment Report shows that the majority of small and medium-sized businesses (SMBs) perceive themselves as more susceptible to cyberattacks compared to larger enterprises. These SMBs express concerns regarding the potential consequences of such attacks, particularly emphasizing data loss, financial ramifications, and a drop in customer confidence and trust. Interestingly, despite these concerns, their investments in cybersecurity have not yet aligned with the evolving dynamics of their operational models. 

The continued adoption of cloud computing, still-emerging hybrid workplace practices, and increased digital supply chain complexities all have led to a rise in data breaches and, thus, a more pressing need for enhanced cybersecurity measures. However, a purely reactive approach isn’t enough; critically, preventive measures are required  as cybercriminals have become more sophisticated in finding ways into corporate networks. Here, traditional security measures may fall short, highlighting the critical need for advanced solutions tailored to the specific requirements of businesses. One such solution gaining prominence is Managed Detection and Response (MDR).

MDR: A Trusted Partner for SMBs

As mentioned in Gartner® latest report, Gartner [Emerging Tech: Security — Adoption Growth Insights for Managed Detection and Response, Matt Milone, Travis Lee, Mark Wah, Published 30 June 2023]:
“MDR growth will continue as customers of all sizes embrace providers’ ability to effectively deliver managed threat disruption and containment. An increasing number of MDR customers of all sizes demand that providers are able to remotely initiate measures for active containment or disruption of a threat. Provider-delivered response actions and not just simple alert communications assist clients with their lack of security personnel and expertise. Factors including trust, geography and the security maturity of the consuming organization affect adoption of provider-led or guided response activities.”
MDR presents a favorable solution for SMBs by outsourcing the management of Extended Detection and Response (XDR) to cybersecurity providers.

Let’s delve into the core needs of SMBs related to threat detection and response and how MDR services answer them:

1. Access to additional security expertise

MDR serves as a bridge, helping you overcome expertise gaps in your security capacity by providing access to industry-leading cybersecurity professionals. Make sure your MDR partner offers local language support with a global presence. Attain top-tier protection without requiring internal security experts, or remove bottlenecks in your security operations team that may impede efficient detection and response. MDR services can be tailored to fit the specific needs and size of your business, ensuring you get the right level of protection without unnecessary complexities.

2. Enhanced detection and response capabilities

MDR goes beyond traditional cybersecurity measures, actively seeking and identifying potential threats before they can cause harm. They are tailored to detect cybersecurity breaches in the complex realm of hybrid work and enhance your capabilities to respond effectively to evolving cyber threats, such as ransomware as a service (RaaS). Opt for providers with immediate AI-powered threat detection and response, known for high detection rates, low false positives, and a light overall footprint, as validated by independent analyst appraisals and customer reviews.

3. Always-on approach

Cyber threats are constant. MDR services operate around the clock, providing continuous monitoring and rapid response to security incidents, always ensuring incidents are addressed promptly. The 24/7/365 security capabilities of experts eliminate the need for an in-house security team and monitor the threat environment around the clock.

4. Regulatory compliance

If you are looking for regulatory compliance, MDR can help you achieve key cyber controls necessary for insurability, meeting critical components of cybersecurity insurance programs and regulatory compliance and, with that, reducing the risk of penalties and legal issues.

MDR is not just for enterprises

Despite lacking the extensive resources of their larger counterparts, smaller businesses possess confidential and valuable information that requires protection. And doing nothing costs more than protecting your business. MDR tailored for smaller businesses serves as a valuable addition to existing security and IT measures, enhancing overall protection and defense. This enables organizations to proactively identify, thwart, and respond to online threats before potential damage occurs. By leveraging an MDR service, small businesses can not only fortify their security but also gain the freedom to focus on essential aspects, such as expanding their businesses.

According to a report from Gartner [Emerging Tech: Security — Adoption Growth Insights for Managed Detection and Response, Matt Milone, Travis Lee, Mark Wah, 30 June 2023]:

  • “Overall MDR mind share increased 29.14% year over year with MDR adoption growth increasing 67% from 2021 to 2022.
  • Growth is highest in education and steady across most industries, with a marked decline in energy and utilities.
  • Mind share increases with the largest companies, while adoption interest increases across private- and public-sector companies of most sizes.
  • Executive buyers have shown a significant increase in commitment through adoption interest, but the technical job role remains the dominant persona.
  • The largest market remains North America with a notable decrease in adoption interest in the Latin American market.”

This data suggests that there continues to be strong MDR demand regardless of company size and industry vertical. This is then highlighted and confirmed by the above-mentioned report, which says, “This is a trend we should expect to see continue over the next two to five years as the demand for MDR services continues to grow.”

Having an MDR service that offers capabilities beyond what a business can independently manage and has considerations for all business configurations and verticals, is, therefore, particularly important for SMBs. This is due to their varying size and focus, as they need a service that can go a step beyond conventional protection.

About ESET MDR

Our MDR service for SMBs is specifically designed to meet the above outlined needs and bring immediate benefits, especially to SMBs.

Delivered via our renowned ESET PROTECT Platform and ESET Inspect, the XDR-enabling component, we designed our ESET MDR service to swiftly examine and disrupt malicious activities and counteract adversaries. Specifically adapted for the intricacies of hybrid work settings, the service conducts threat hunting, monitoring, and response, ensuring the implementation of strong cybersecurity measures suitable for customers across varying sizes and security maturity levels.

Leveraging the knowledge of security professionals, ESET MDR can rapidly identify and counter threats within a 20-minute window. We utilize our proprietary antivirus software to gather exclusive data, especially from regions targeted by advanced hacker groups. As a customer, you can also leverage the signal hunting library, which contains pre-built behavior patterns for robust threat defense.

The ESET MDR service is available as an add-on or stand-alone offering, packaged with ESET PROTECT Enterprise and ESET PROTECT Elite.

Conclusion

Numerous cyberattacks continue to target many small organizations, posing a persistent threat regardless of business size. Unidentified threats always loom, ready to compromise systems. In the quest for security, every organization, regardless of size and industry, can benefit from the assistance and mitigation apabilities offered by MDR.

MDR emerges as a trusted ally for you, empowering you with powerful cybersecurity solutions that overcome traditional limitations. The combination of advanced technology, expert support, and a focus on compliance positions MDR as a beacon of security in the complex digital landscape. As cyber threats continue to evolve, embracing MDR services becomes not just a choice but a strategic imperative for your business.

GARTNER is a registered trademark and service mark of Gartner Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.