Skip to content

How to access a company network from different locations

Secure and easy access to workplace networks isn’t just a perk in the remote work era. Yet, remote work brings security and connectivity challenges businesses can’t ignore. We’ve all have come across the term Virtual Private Networks or VPNs in our work, whether we’re technology professionals, IT administrators, or just everyday remote employees. 

In this article, we’ll break down the A-Z of VPNs. From secure access to a company’s network from different locations to understanding why free VPNs might cost you more than you think. Plus, we’ll explore why business VPN might be one of your best business decisions.

What is a VPN?

A simple yet profound technology

Understanding what a Virtual Private Network (VPN) is the first step in learning how to access and share data on many branches of a company network from different locations.

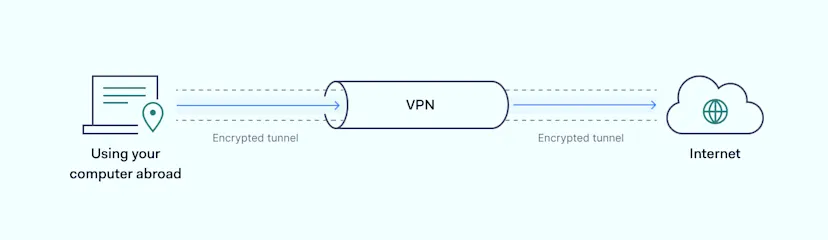
A VPN creates a secure tunnel between your device and the internet, using advanced encryption algorithms to safeguard data in transit. This tunnel acts as a secure conduit through which data such as usernames, passwords, and sensitive files are sent and received.

This encrypted tunnel ensures that even if someone could intercept your data, they would not be able to decode it.
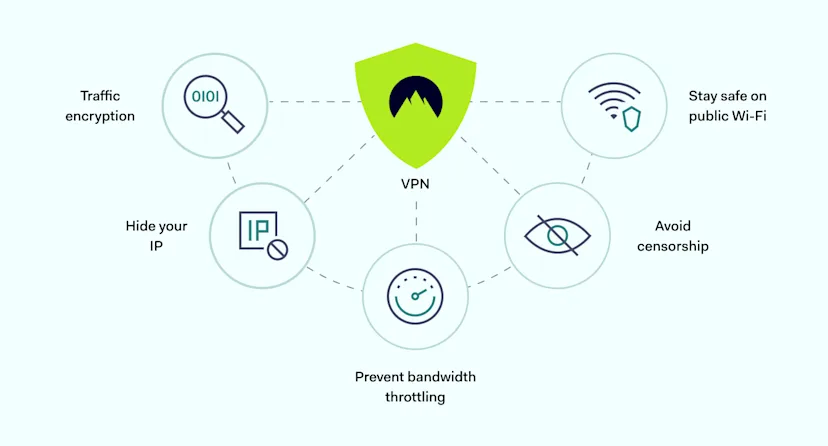
The secondary but equally important aspect of VPNs is masking your IP address. Every time you connect to the internet, your device is assigned an IP address, a unique identifier that can reveal your location.

A VPN replaces your IP address with one from its server, shielding your true location. This dual functionality of encryption and new IP address masking makes VPN both straightforward and robust. And it helps companies protect their privacy, data, and assets.

Role of VPNs in internet safety and remote work

VPNs: the gatekeepers of internet safety

VPNs create a digital barrier that protects your data from cyber threats like ransomware attacks, phishing scams, and data breaches. Given the alarming rise in cybercrime, their role in preventing business disruption and financial loss is crucial.

VPNs standardize technology processes for organizations spread across many locations, even internationally.

Businesses can use VPNs to securely share data and connect various locations to different network nodes, such as branch offices, cloud-based services, or mobile employees.

This standardization ensures uniform security across the entire organization, reducing vulnerabilities that cybercriminals could exploit.

Remote access facilitating offsite connection in business

Before, secure remote work was difficult due to complex security protocols and the limitations of traditional WANs. VPNs have dramatically simplified this process by offering secure, seamless remote access to a company’s internal network from anywhere in the world.

With a VPN, remote employees can securely access many company resources, like files, applications, on-site servers, and internal communications tools.

For most businesses operating under a remote or hybrid work model, a VPN is indispensable. It ensures that employees can work as efficiently from home—or any global location—as they could if they were present at the office.

3 risks of free VPN services: why quality matters
1. Compromised speed and limited server choices

The appeal of free VPN services often hinges on the absence of initial costs. Yet, these services frequently limit the internet speed available to users. These speed caps can significantly hamper productivity and efficiency for many businesses that need fast and uninterrupted access to data and communication tools.

Moreover, free VPN services usually offer a restricted range of server locations. This limitation can be problematic for businesses that need to connect to servers in specific geographic locations for compliance or operational reasons. The lack of server choices may also lead to network congestion, further slowing your connection.

2. Security risks: lax encryption and data logging

One of the most critical drawbacks of free VPN services is their inadequate security features. Many free VPNs lack state-of-the-art encryption protocols, leaving your data vulnerable to interception and unauthorized access. This compromised security is a severe issue, especially for businesses handling sensitive or confidential information.

Some free VPN services may log your browsing activities, a practice that contradicts the purpose of using a VPN for enhanced privacy.

These logs can be susceptible to data breaches or be sold to third parties for marketing purposes, putting your data and privacy at risk.

3. Suitability for businesses: high stakes, higher risks

Regarding business applications, relying on a free VPN can be a grave mistake.

The risks include slower internet speeds or fewer server choices. More seriously, they can extend to more consequential matters like compromised data integrity and potential breaches of customer information.

Businesses face greater risks in a cyber-incident, such as financial losses and damage to their reputation and customer trust. Given their many limitations, free VPN services aren’t appropriate for corporate use, where data security and privacy stakes are significantly higher.

Elevating enterprise security with a business VPN

Ensuring business infrastructure security

If you are serious about business data security, an enterprise VPN is the way to go.

These VPNs provide tailor-made solutions for businesses, unlocking capabilities such as IP allowlisting for secure resource access and offering more robust encryption protocols. This enables businesses to securely access company networks from various locations.

This technology setup ensures the security of your central server, and the software safeguards cloud computing services, on-site servers, remote offices, local area networks, and even individual computers at various business locations.

Distance entry: the future of work

The COVID-19 pandemic showed us that remote work is not just a trend—it’s here to stay. A corporate VPN is essential for companies that have embraced this shift.

With this software setup, employees can securely access company networks from home and seamlessly share and receive data with colleagues globally.

The glue keeps your dispersed team on the same page: secure file sharing, one office environment, and one network.

Enabling remote access: bridging on-site servers with cloud services

Businesses nowadays are not just confined to physical office spaces or two offices—they also operate in virtual private networks in the cloud. So, how do you access the company network from different office locations, and can you bridge these two worlds? And what about static IP addresses?
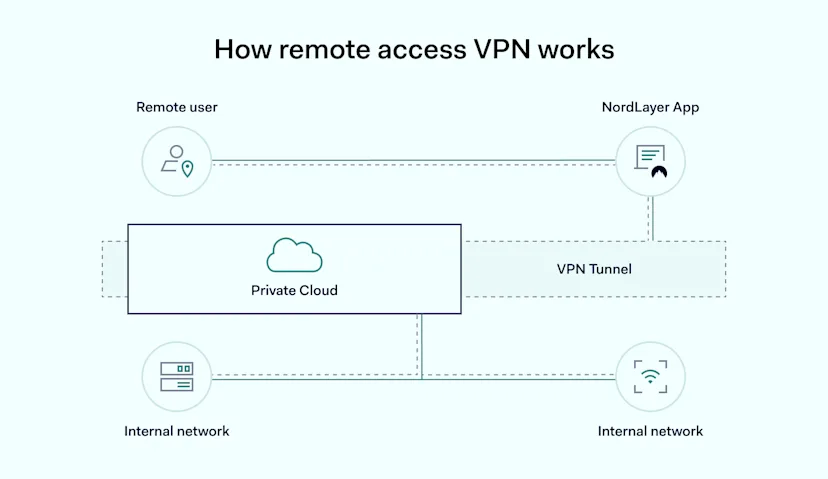
Remote access VPNs are essential for cloud computing, requiring static IP addresses to establish connections to on-site servers and other cloud resources. These addresses aren’t just for enhanced security, they’re fundamental for any remote connection to a physical network or device. By following these prerequisites, users can significantly minimize risks associated with remote access, allowing employees to work securely, no matter where they are.

Boosting your business security with a VPN

The importance of wireless connection safety

While convenient, public Wi-Fi networks are a breeding ground for various cybersecurity threats. There are numerous vulnerabilities, from Man-in-the-Middle (MITM) attacks to cybercriminals eavesdropping on your data to unauthorized access.

These are not just fears—they’re real threats. They can translate into concrete security breaches involving sensitive personal or business data. This has been particularly underscored by the increasing cyber-attack incidents targeting users on public Wi-Fi networks.

Beyond the basics: advanced VPN features for enhanced online protection

Beyond the essential security features, corporate VPNs offer additional layers of protection. Advanced features like:

  • Split tunneling

  • Zero-knowledge architecture

  • Multi-hop connections

What does all of this mean for businesses? More options for keeping your internet connection safe, secure, and tailored to your needs. The saying goes, “The best defense is a good offense.”

Conclusion: why a business VPN is an essential digital protection tool

Remote work demands robust security beyond standard business applications and software. Just as NordLayer’s VPN sets the bar high for a secure connection for remote work, your choice of a business VPN should meet similar standards. It’s not just about better secure connections in remote offices, it’s also about comprehensive data protection, user management, and ease of use, all while enabling all ways of working.

Don’t settle for basic security features. Elevate your business operations with NordLayer’s Business VPN solution. Move today to ensure a secure, virtual private network and efficient remote office work environment tailored to your needs.

Contact us today, and let us help you create a security solution that fits your business needs.
About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Enabling remote access to the office network without security compromises

After the pandemic, the shift to working from home and hybrid work models increased severely. Most office employees were allowed to choose where they wanted to work. The problem was that security was often left as an afterthought regarding remote access. This also meant that cyberattacks increased on an unprecedented scale, threatening businesses even more. 

Ensuring that work networks are reachable from the convenience of the employees’ homes is still crucial for business continuity. However, this also means navigating the complex and intricate world of network security, which can be a challenge. Therefore, this article will guide you through various techniques and solutions for achieving remote work with proper attention to data security.

Key takeaways

  • Secure network access to internal systems for remote employees and third-party vendors is crucial.

  • VPN software helps keep your connection secure, hides your IP address, and lets you access the company’s network from anywhere in the world.

  • To ensure you can safely access your system from anywhere, it’s important to use a list of approved users and set up multiple verification forms.

  • Regular check-ins, routine upkeep, and staying informed about security can help reduce cyber risks for remote teams.

How to safely access the company network from any location?

Remote and hybrid work provides unparalleled flexibility for remote workers to figure out how to tackle their tasks. The challenge is to figure out network access control mechanisms for third-party vendors, clients, and remote employees working from home. It’s a paradox: the resources must be made available but not too available so that it becomes a security liability.

Without proper precautions, unauthorized users might take advantage of weak security. For this reason, businesses seek to improve their network security stance by implementing various network access control solutions or adopting good practices for their IT infrastructure management. Here are some examples of how secure remote access could be arranged.

Protect your network with a Virtual Private Network

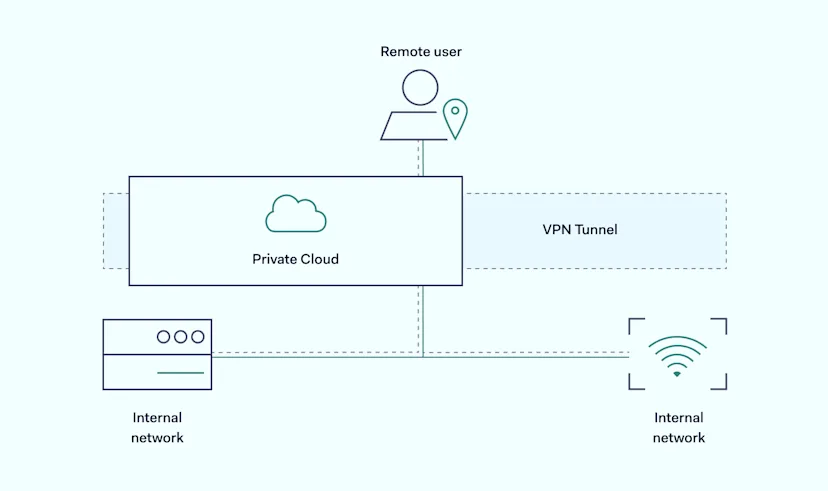
A Virtual Private Network (VPN for short) is an online security staple in remote access. It encrypts users’ connections, securing them from any potential external eavesdropping. This helps ensure that the data transmitted between the device and the company network remains secure. Data encryption stops criminals from capturing the data in transit as they don’t have the decryption key. It’s invaluable for remote employees working from public Wi-Fi or other unsecure networks.

In addition, business VPN software helps to maintain the anonymity of your employees’ identities by masking the user’s IP address. This can help prevent third-party tracking and ensure that sensitive information about the company’s operations remains confidential. Hiding the remote worker’s IP address also makes it more difficult for hackers to monitor their online behavior or exploit any vulnerabilities in the network.

Finally, VPNs allow employees to connect to the company’s network from anywhere worldwide. This can be particularly useful in remote work scenarios where resources must be shared securely with a large group of people. It helps to maintain the privacy, integrity, and availability of the data and services essential for the company’s operations and stay productive.

Secure access to cloud storage

Safeguarding cloud-stored assets goes beyond mere passwords. A holistic security strategy requires methods like IP whitelisting, network segmentation, and advanced authentication techniques such as MFA and biometrics to secure access to cloud resources.

Allow Remote Access To Your Office Network Without Compromising Security 2 1400x722

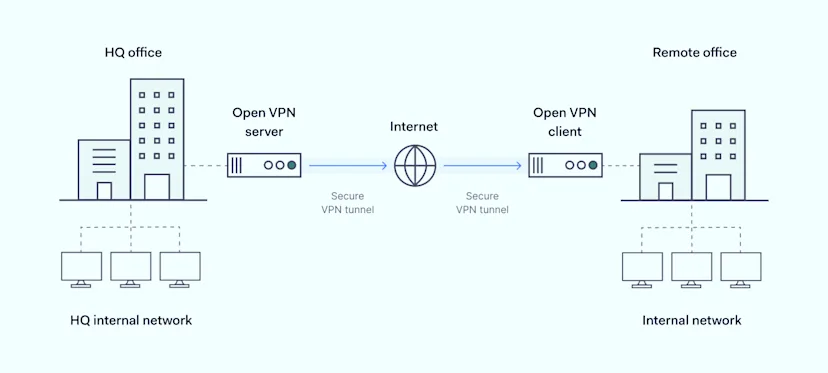
These measures protect data and ensure that tools like Confluence, Jira, and Salesforce are accessed solely by authorized users. When it comes to remote work, the challenge amplifies. Solutions like site-to-site VPNs have become invaluable, allowing employees to securely connect to the office network from afar, guaranteeing a secure and seamless connection to essential data.

Use cases for secure remote access

Secure remote access has grown exponentially in importance, particularly during the shifts of digital transformation, remote working, and global collaboration. Here are some key use cases for secure remote access that organizations and individuals are leveraging.

Remote work and collaboration

With the rise of remote work, employees across the globe need secure access to their organization’s network and resources. It allows staff to work outside the office, accessing files, applications, and internal systems without compromising security. Businesses must keep sensitive information only to authorized users, maintaining its confidentiality and integrity.

Remote monitoring and management

In our globally connected environment, keeping a close eye on devices everywhere is more important than ever. This goes beyond just watching; it means having the ability to access and manage these devices securely. It’s a vital tool, especially when teams are spread across different locations, helping maintain strict security standards. This includes setting specific security guidelines, regulating access based on these rules, and getting timely alerts about any non-compliant connections.

Adopting remote monitoring ensures smooth operations and can quickly address potential issues, no matter where they arise, keeping your business running seamlessly and efficiently.

Disaster recovery and business continuity

In the event of natural disasters or unexpected disruptions that affect your physical network or infrastructure, flexible remote access solutions enable organizations to continue their operations. Employees can connect to the cloud tools and resources safely, and IT teams can remotely manage and restore systems to maintain business continuity.

How to enable secure remote workers’ network access?

For the remote workforce, secure access to the company’s network is essential for productivity. Here are a couple of things you can do to ensure that remote access is secure for your employees.

Establish secure connections to your network

Secure remote access is vital in today’s network security, ensuring both digital and physical aspects of networks and devices are safeguarded. There are two primary use cases: site-to-site access, which connects separate locations securely through VPNs, authentication, monitoring, and firewalls, and smart remote access, which allows to connect to devices that don’t support VPN applications.

For site-to-site access, the goal is to encrypt, monitor, and authorize data exchange between locations. In contrast, smart remote access emphasizes dynamic access based on context, seamless maintenance, and timely security updates. Both approaches aim to provide secure and efficient remote connections in our ever-evolving digital landscape in which SaaS access control is key.

Implement IP allowlisting

Allowlisting gives specific applications, IP addresses, or devices permission to access certain resources. This boosts security by only allowing trusted sources. However, managing varying IPs can be tough when remote workers from different global locations access resources.

For easier management, this works best when IP allowlisting is combined with Virtual Private Gateways with a fixed IP. This means only one fixed IP to handle, reducing complications. It helps to filter out unverified connections and ensure that only authorized personnel can access sensitive information.

Use multi-factor authentication (MFA)

MFA is vital for remote work, enhancing security by requiring at least two types of identification before access is granted. This can be a combination of a password, a device like a phone, or even a fingerprint.

With remote work, there are increased risks compared to an office environment. Devices are more susceptible to theft, and ensuring physical workspace security is challenging. MFA serves as a barrier against unauthorized access. Simple tasks might need a password and a text code, but sensitive data requires stronger authentication, like combining a password, fingerprint, and a smart card. This extra security helps counteract the risks of remote work.

Strict authentication is essential

Weak passwords can often be guessed or cracked through brute force or dictionary attacks. Yet even strong passwords can fall pretty to cyberattacks if they’re reused. It’s much more secure to use single sign-on (SSO) and phase out email-password logins, which can be vulnerable.

SSO provides centralized control over user access, making it easier to manage permissions and revoke access when needed. This is especially crucial in organizations where employees or users come and go. As technology advances, it’s crucial to stay ahead of the curve and prioritize security measures that adapt to the changing threat landscape.

Enable endpoint security

Endpoint security is super important today. It ensures that devices like laptops and phones are up to security standards. Since everyone’s personal device can be different, some might not be as secure as others or even be at risk.

That’s where endpoint security tools come in. They keep an eye on these devices and help tech teams spot and handle risks. This stops unwanted access and keeps our data safe. As more people work remotely and use their own devices, having good endpoint security is like having a protective shield for our digital workspace.

Monitor and log access

Regularly monitoring and logging who is accessing your network helps detect any unusual behavior or unauthorized access patterns. This may indicate external hackers trying to breach the network and internal users trying to access resources they shouldn’t have permission to access.

All the logs help to check and ensure that all those who ‘should’ be using secure connections are actually doing so. This provides visibility into network activities, supports incident response, and enables proactive security measures.

How to provide secure access to your network for third parties?

Businesses often need to give third-party vendors, consultants, or partners access to their networks. While third-party collaboration is unavoidable, it comes with the risk of compromising the network’s security. Implementing proper protocols and safeguards is vital to ensure the system’s integrity.

Here’s how you can give third-party network access without jeopardizing security.

Clearly define access requirements

Before providing access to your third-party partners, you must outline what resources need access and why. This tailored approach to data access minimizes the total attack surface and leaves hackers less wiggle room. In the long run, this helps to minimize the risk of unauthorized access, data breaches, and potentially malicious activities.

Still, the company that wants to initiate this access model will require a structured approach. All held networks and their resources must be well-documented for them to work. After that’s done, third parties can be joined within the infrastructure with lesser privileges.

Create separate subnetwork for external partners

Breaking networks into smaller segments can help stop hackers from moving around easily if they get in. It also lets us design specific areas of the network just for outside groups. This means the main system is safer if an outsider’s system is hacked. If an internal system breach happens, it stays within that smaller area and doesn’t spread everywhere.

Use role-based access controls (RBAC)

RBAC restricts system access to authorized users. It’s essential for managing and controlling access within an organization’s network, especially when third parties are involved. By setting up roles, it’s possible to limit third-party access only to the areas necessary for them to fulfill their functions. This minimizes the risk of accidental or intentional data misuse, enhancing security.

Additionally, RBAC provides a clear record of who has access to what. This can be crucial for auditing and monitoring purposes, making it easier to track who accessed certain resources and when. If an incident does occur, the organization can easily trace back actions to spot individuals or roles.

Draft a Comprehensive Security Agreement

A Comprehensive Security Agreement (CSA) outlines the responsibilities and obligations of both parties. It establishes what the third party expects regarding security protocols and clarifies what the organization will provide in return. This agreement should include how data is handled, stored, and destroyed and what actions will be taken if there’s a security breach.

The agreement serves as a legally binding pact that holds both parties accountable. This ensures that both sides have taken necessary precautions and can be used in legal proceedings.

How can NordLayer help

In today’s dynamic business landscape, providing remote access to your office network is crucial. However, it must be done cautiously to protect sensitive data and ensure business continuity. Cybersecurity shouldn’t be left for a chance. Finding trustworthy allies is important, as malicious actors aren’t showing any signs of slowing down.

NordLayer is perfect for businesses shifting to a mix of office and home work. As more companies adopt this hybrid work style, NordLayer provides easy-to-use services that ensure remote work is both safe and convenient for everyone.

Virtual Private Gateways with a dedicated server by NordLayer can help a lot. It keeps your online data safe by encrypting traffic, adjusts easily to your needs, and lets you control who gets access by setting role-based privileges. Plus, it pairs seamlessly with all major login providers, ensuring only the right people get in.

We provide tools that make your local networks and Cloud resources super secure. Enjoy top-notch VPN protection, extra security with multi-factor authentication, and always-on network monitoring. The best part? Our solutions don’t require any hardware and can be adjusted easily to fit your business needs.

If any of these challenges sound familiar to your organization, reach out to our team. We’re here to help you explore various ways to strengthen your network’s cybersecurity.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Creating a successful remote work policy: examples and best practices

Remote work is now a key part of how many businesses operate. It offers new ways of working, like flexible hours and the chance to save money on office space. Because of this, it’s important to have a clear plan for remote employees and those who work both in the office and at home. 

In this article, we’ll take a look at how to put together a remote work agreement for your company. We’ll cover why you need one, what should be included, and some helpful tips for making it work. By planning ahead, businesses can make the move to remote work smoothly, leading to a successful and energetic work environment.

What is the remote work policy?

A remote work policy is like a set of rules that bosses and workers follow when working from home or outside the office. It explains everything you need to know about working remotely, like your job duties, when you should be working, the technical help you can get, and other important information.

This policy helps to protect both the company and the workers so nobody gets into legal trouble. It sets fair rules for everyone and ensures all employees understand what they need to do when working remotely.

A remote work policy might talk about things like:

  • What equipment you’ll need

  • Making sure you have a good internet connection

  • How you’ll talk to your co-workers

  • Ways to keep computer information safe

Having a remote work policy helps businesses be more flexible, letting people work where they want while ensuring everyone does their job right and keeps information secure.

The details of a remote work policy can change depending on things like what kind of business you’re in, how big your company is, and what laws you have to follow. But no matter what, certain things are always important regarding remote work policies.

Why does your company need a remote work policy?

After the COVID-19 pandemic, there was a shift in employees’ view of remote work. A well-defined remote work agreement becomes crucial with the increasing prevalence of remote workers. Here are the main arguments for it:

Work flexibility is not a bonus but an expectation

Work flexibility is in greater demand than ever before. According to the American Opportunity Survey, when people have an opportunity to work flexibly, 87% of them take it. This is noticeable across occupations, demographics, and geographies. The data shows that the remote work trend continues to shape the future of work relationships.

According to the same research, the third most popular reason for workplace changes was a search for more flexible work arrangements. This means businesses that have already adopted remote work policies have the advantage of attracting top talent. Yet, it’s first necessary to form a remote work policy to move forward with remote work as a practice.

Remote work brings value to the company

There are tangible business benefits directly attributed to flexible working conditions. Working from home did increase productivity by 5%. This shows that giving employees the freedom to choose how they work enables them to be more efficient regarding their work scope. In this case, the business wins, as it reaps the productivity benefits.

Additionally, remote work expands the pool of potential employees. This means that the workplace can attract global talents while fostering innovation, ultimately leading to improved profitability. Far from just being something that exists to please employees, remote work has direct and quantifiable effects on business performance. Yet, it also needs a remote work policy to be viable.

Compliance must remain a priority

Remote work, just like any other job, has to follow specific laws and rules. Employers need to know where their employees are working to avoid legal and tax problems. Since these rules can be very different in various places, it can be tricky for companies with remote workers in different regions or countries.

They also have to think about things like health insurance, which plays a big part in shaping remote work policies.

It’s crucial to regularly check and update remote work rules with the help of legal, HR, IT, and other important departments. This helps to keep everything running smoothly and legally. There may be limits on where or for how long employees can work remotely, and these rules should be part of your remote work policy. By putting these rules in place, you can protect your organization against future misunderstandings and communication breakdowns.

Data security and confidentiality

Employees working from home or elsewhere can create security risks for the company’s information and digital assets. To keep everything safe, the company needs a clear policy for remote work. This policy should spell out the rules everyone must follow to protect sensitive data and other important information.

The remote work policy should also include other safety measures, like:

  • Making sure that remote workers are using safe, up-to-date software.

  • Requiring them to use virtual private networks (VPNs) to keep their connections private.

  • Making them use multi-factor authentication to access company systems, which means they have to provide more than one piece of information to prove who they are.

  • Requiring encrypted communication tools for sensitive conversations.

  • Regularly updating and patching remote devices to guard against possible weaknesses.

By following these steps, the company can keep its valuable assets safe and maintain the trust of its clients, partners, and stakeholders in a world where more and more work is being done remotely.

Working from home best practices

Remote work policy components and examples

To help you create your remote work policy, we drafted a potential structure that could be used as an example.

Objective

This guide outlines the conditions and regulations for staff members working from places other than designated work locations such as [office, building, floor, etc.]. It aims to ensure that both employees and supervisors know the remote work conditions and guidelines.

The relevant authorities must first approve all remote work requests [supervisor, manager, Human Resources, etc.]. This remote work regulation stays effective until [an end date is set or the policy is reviewed].

Applicability

This policy is relevant only to [full-time employees, suitable part-time employees, staff not in training, etc.].

Guidelines

Eligible staff members are required by [Company name] to work remotely on a [temporary or permanent] basis. Work can be carried out [anywhere, specific city or state, etc.].

The following criteria must be outlined for positions that qualify for remote work:

Work timing and presence

Specified times when remote employees must be working

Example: “Remote employees should be actively working according to the schedule outlined in their contract. If an alternative work schedule is desired, written consent from a supervisor must be obtained, and the new schedule must be communicated to the team.”

Remote work setting

Standards related to the remote working space

Example: “To ensure optimal productivity, remote workers must select an environment without distractions, with stable internet access, and conducive to focused work during working hours.”

On-location work

Steps remote employees need to follow when working on-site

Example: “If planning to work at the office, remote employees should use [Company Name] ‘s reservation system to check and reserve available workspaces to prevent overcapacity.”

Communication expectations

Preferred methods of communication and expected response times

Example: “Remote employees should be accessible through Slack or phone during working hours and should reply to emails within a day unless specified differently in the client’s statement of work. Regular check-ins with teammates and attendance at mandatory meetings are also required.”

Tools and technology

What will the company supply in terms of hardware and software

Example: “[Company Name] will furnish remote employees with the necessary tools and technology tailored to their roles and responsibilities. This equipment must be used exclusively for business and kept secure.”

Information security

Instructions for safeguarding confidential information

Example: “Remote employees are expected to follow the company’s acceptable use policy (AUP) and bring your device (BYOD) policy, taking necessary measures to reduce cybersecurity risks and safeguard sensitive and proprietary information.”

We made a helpful template for remote work guidelines

Best practices for implementing a remote work policy

Best practices for implementing a remote work policy 1400x495Implementing a remote work policy benefits employees and employers, allowing flexibility and the ability to tap into a broader talent pool. However, to ensure success, it’s a good idea to consider the following best practices.

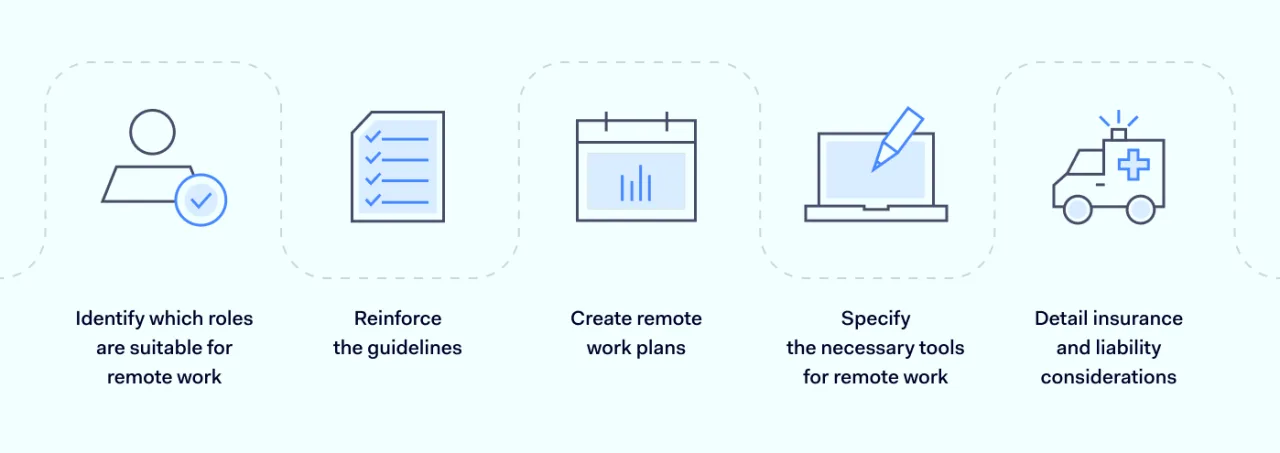
1. Identify which roles are suitable for remote work

Not every position in an organization can seamlessly transition to remote work arrangement. While a software developer may easily work from home, an office administrator may not fulfill all job obligations remotely. Therefore it’s necessary to outline which roles can function in a home environment without decreasing employee performance.

Secondly, it’s also important to look at the tasks themselves and determine whether they can be done remotely, even when factoring that some job roles are more suited to remote work. In those cases, setting a fixed amount of time for in-person and remote work is a good compromise.

2. Reinforce the guidelines

It’s important to know which company rules and guidelines need to be followed, even if employees are working from home. All the usual company rules still apply, but we need to make sure everyone understands that these rules aren’t put on hold just because they’re working remotely.

By providing clear and easy-to-understand guidelines, we can set clear expectations for everyone. This will help prevent confusion and make managing remote work much easier. It creates a level of openness and trust that will make remote working a smooth and efficient process for all involved.

3. Create remote work plans

Company goals need to be broken down into clear and achievable targets. Department heads can help turn these big objectives into practical tasks and responsibilities. This gives employees a clear path to follow, making their jobs easier during changes or transitions.

Managers should make it a habit to lay out these plans and talk them over with their teams. They should also keep an eye on progress to make sure everyone is on track to meet the goals. This helps prevent confusion, especially when shifting to a remote work model that may require more effort from employees outside the office. It keeps everyone on the same page and ensures a smooth transition.

4. Specify the necessary tools for remote work

Remote workers need the right technology and help to do their jobs and work together with their team. This means making sure they have what they need to do their tasks from home or elsewhere. Sometimes, you might even need to buy extra software or tools to help remote workers handle the special demands of working away from the office.

Remote work often causes communication problems and mix-ups. But by supporting remote employees with different tools, you can help them stay in touch in real-time. This makes it easier to sort out any problems that might come up.

5. Detail insurance and liability considerations

If you’re working from home, it’s essential to know your rights and how things like injuries or losses will be dealt with. A good remote work policy will cover all these details, including benefits, insurance, and liability considerations. It’s not just important for employees; employers need this too, to make sure that everyone’s working in a safe and secure way.

What does all this mean in practice? Well, it helps create a positive work environment and makes sure that the company is following the law, reducing legal risks. Plus, it shows that the company really cares about its employees’ well-being and safety. By being clear and open about the rules and policies, it can help build trust and make remote workers feel like a part of the team, boosting productivity and inclusion within the company culture.

Easier cybersecurity with NordLayer

Remote working is quickly transforming traditional employment models. Yet, in this arrangement, the company and its employees share the responsibility of maintaining security and the well-being of company data. Achieving this may only be feasible with the right tools and solutions for network management.

NordLayer offers a package for hybrid work security that enhances the safety of working remotely. We enhance collaboration between remote employees and modern businesses allowing them to control access to company resources and safeguard critical assets.

Without needing any special hardware, NordLayer provides an accessible solution suitable for businesses of all sizes and easily enables secure remote work from anywhere. Solve your remote work challenges with effective solutions to make your setup safer.

Contact our sales department to learn more about our solutions and uplift your remote work capabilities today.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Remote workforce technologies for secure work

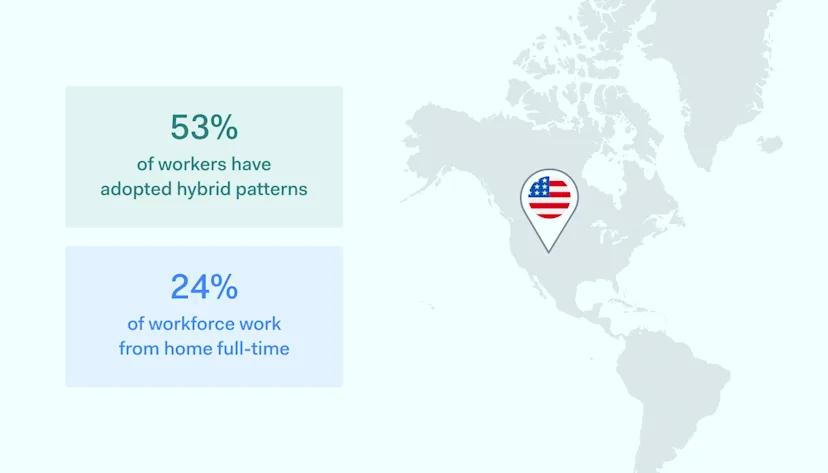
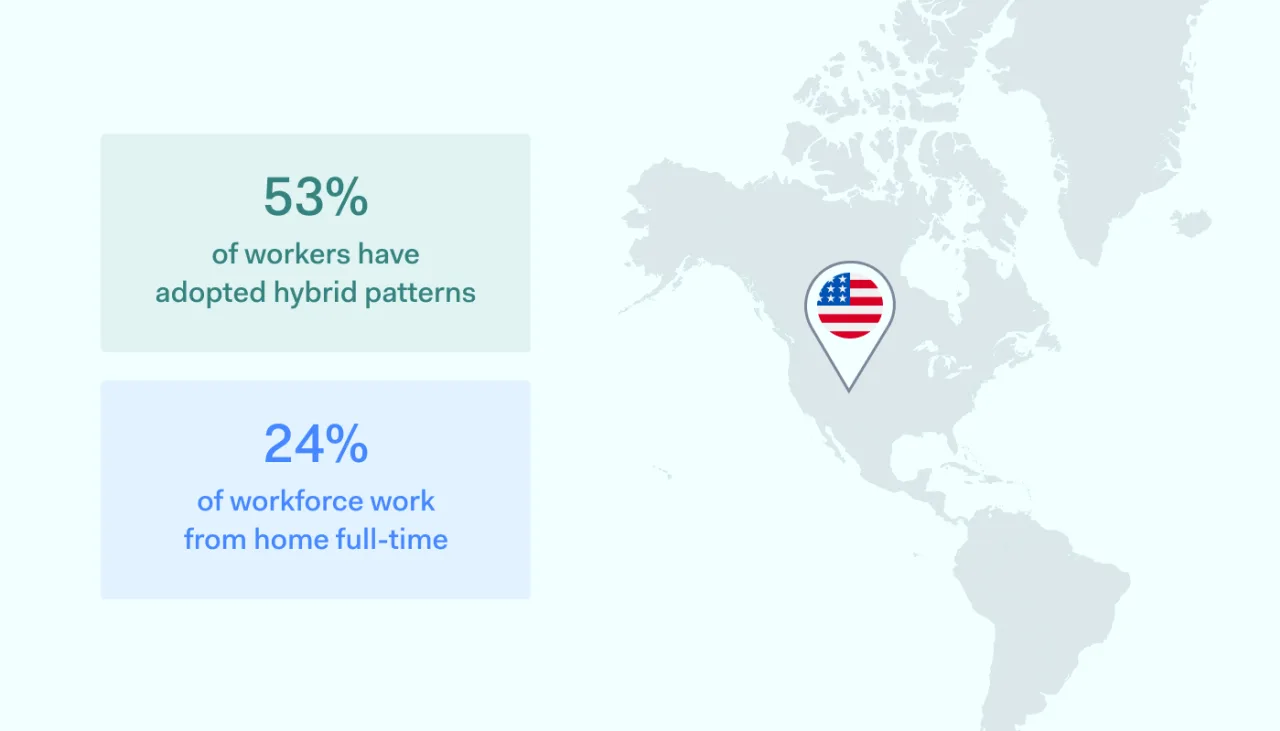
The traditional office is becoming harder to find these days. Across the world, millions of people have shifted to hybrid or fully remote work lifestyles. In the USA, 53% of workers have adopted hybrid patterns, and 24% work from home full-time. Those numbers are likely to rise with employee expectations drifting towards flexible working. 

But how should companies respond? Enabling remote working can be risky, but it comes with many benefits. In this article, we’ll introduce the best security tools for remote work, making it easier to relocate employees without creating extra cybersecurity risks.

Key takeaways

  • Remote working is more popular than ever. Choosing the right software and hardware tools allows off-site workforces to operate safely and productively.

  • Efficient video conferencing solutions connect team colleagues, managers, and third parties seamlessly. And they secure communications against eavesdroppers.

  • Messaging apps ensure consistent information flows between remote employees. They should allow regular updates, quality assurance checks, and assist with team building.

  • Project management systems make it easier to control dispersed teams. Managers can monitor remote workforces and set schedules for project delivery.

  • Secure storage solutions keep critical data safe. Access controls and encryption make data available for team members while preventing illegitimate access.

The evolution of remote work

Remote work is not a new phenomenon. And in the past 20 years, remote work has become routine for occupations like IT support.

However, the number of remote employees was relatively small until the Covid pandemic. When it hit, millions of workers were suddenly barred from workplaces. But companies needed to continue operations, which sparked a search for remote solutions.

Apps like Zoom became household names overnight. And organizations suddenly had to adapt their working practices to accommodate working remotely.

Fortunately, Covid-19 coincided with technological developments that made remote working easier. Internet bandwidth is increasing at a rate of around 29% per year. This allowed employees to collaborate via video conferencing without lag issues. And remote security solutions like Virtual Private Networks (VPNs) and multi-factor authentication enabled companies to create secure remote work connections.

The pandemic and technological change have paved the way for an age of flexible remote working. And this change is mainly driven by employees.

As the Covid pandemic receded, many people didn’t return to their workplaces. Workers became accustomed to spending more time at home. Now, as many as 65% of workers seek full-time remote work, and the employers need to adapt fast.

country statistics for remote work 1400x800

However, not all sectors have embraced remote work. Healthcare and care professions still generally rely on face-to-face contact. Manual trades like mining or construction may always require employees to be present on site. Despite that, many industries support remote work strategies.

The IT sector has the highest proportion of home workers right now. But jobs as diverse as accounting, non-profit administration, tutoring, and graphic design are also compatible with home working.

Recent years have also seen the emergence of remote workforce technologies that enable productive and secure remote work. Project management tools, VPNs, collaboration and video conferencing apps, and cloud storage platforms make remote work easier than ever. Thus, the future of remote working seems bright.

Evaluating remote work effectiveness

Remote work is already mainstream. But it isn’t necessarily the best solution for all companies and employees.

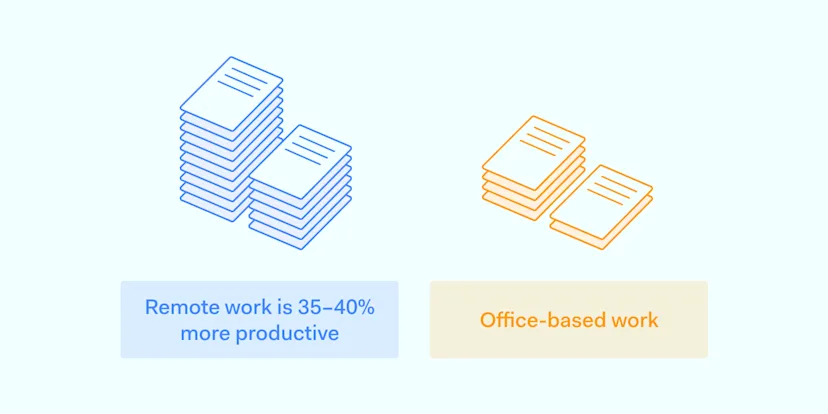
On the positive side, statistics suggest that working from home boosts productivity and streamlines corporate operations. Additionally, major companies say that remote work is 35-40% more productive than office-based alternatives.

This increase could be due to the absence of distractions. Remote employees put time spent on commutes to better use. Or they might just be happier and energized by controlling their working lives.

On the other hand, remote work isn’t suitable for many occupations. As this list from the New York Times shows, this trend has barely touched plenty of jobs. Education, medicine, and construction are just a few good examples.

The pandemic forced teachers to run classes remotely. Such a method led to frustration and stress for educators and damaged educational outcomes for learners. Therefore, organizations should think long and hard before relocating any jobs involving face-to-face contact.

Companies must be aware of potential problems with remote or hybrid work models. Researchers report that remote work can come with a “promotion penalty.” Employees away from managers and offices may lose out during internal recruitment.

On-site staff also benefit from the assistance of more experienced colleagues. Younger remote workers may be disconnected from sources of knowledge. Isolation hurts productivity and dents the career prospects of remote employees.

Poorly-organized remote working systems can also lead to problems with managing them. As a result, managers may gradually extend surveillance reach to track projects and productivity. Because of that, surveillance can negate the feeling of freedom that makes working remotely so appealing.

To sum up, there are good reasons to embrace remote work. But companies should be careful when designing home working setups as this comes with new risks. Let’s explore some tools to simplify this critical task.

The best remote workforce technologies in 2023

Organizations should employ a suite of technologies for working remotely. These cover critical areas like cloud storage, project management, communication, data security, and secure remote access. Let’s see what are the top options in each category.

Cloud storage tools

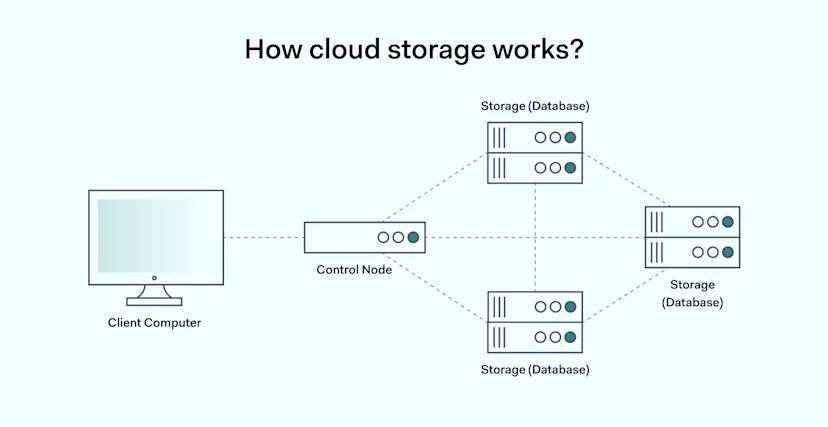
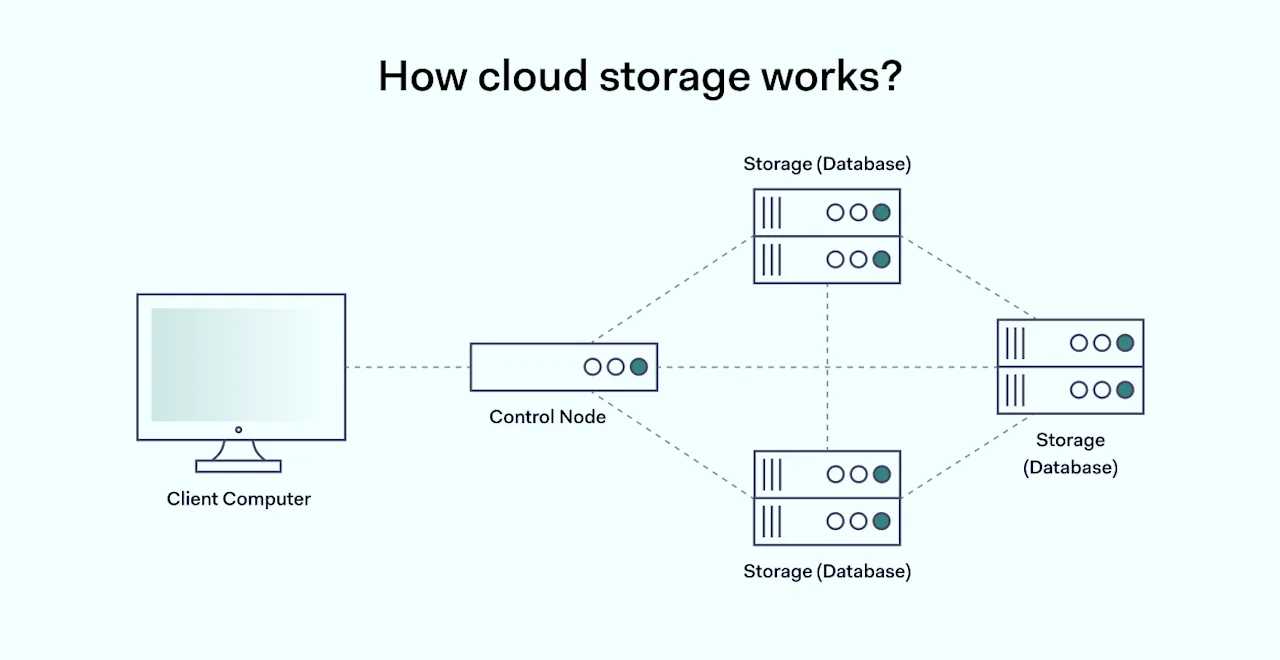
Remote work teams should use secure cloud storage to host workloads and communication apps. Secure platforms apply encryption to protect data at rest. Furthermore, firewalls block illegitimate external access, and physical controls protect data centers.

data centers banners 1400x750

Cloud platforms couple security with ease of use, meaning remote users can share files and databases instantly. Moreover, teams can update work documents, client databases, or code bases in real time. And cloud data protection tools keep the workloads safe from external intruders.

It usually makes sense to build remote work setups around cloud environments. But which cloud services provider should you choose?

Microsoft Azure

This is a popular option for cloud storage. Azure Bastion provides secure shell access for remote connections. It also features the ability to create virtual desktop infrastructure with ease. That way, remote employees can access central resources without storing data locally.

Microsoft’s cloud platform has other remote security benefits. Learn more by reading our Azure best practices guide.

Amazon Web Services (AWS)

AWS is another good cloud storage option and virtual workspace. For instance, it’s ideal for creatives working remotely who need virtual workstations for graphic design or video production.

Users can encrypt data easily and manage data retention policies. And they can track data movements between home and cloud locations.

Finally, cybersecurity is very tight if you follow AWS security best practices.

Google Cloud

Google Cloud offers excellent document storage and editing features. Flexible bucket storage is a core feature of Google’s platform. When cloud services fail in one region, remote workers can access workloads hosted elsewhere.

Google’s storage systems scale smoothly. They are fitted with critical remote security tools like encryption, cloud-native access controls, signed URLs, and data retention locks. By following Google Cloud security best practices, you can design a remote work solution that secures data and serves employee needs.

Project management

Managing projects is a crucial aspect of any remote workplace. Managers need to set targets and monitor employee progress. They need awareness of project achievements. Finally, they require the ability to change plans as projects develop.

Project management tools make these tasks much more manageable. What’s more, they give an overall awareness to their users. Also, some solutions enable detailed worker surveillance via time-tracking tools.

Jira

Atlassian’s Jira platform is a good solution for creating a flexible remote team. Targeted at code developers, Jira enables complete awareness of production status. Managers can track progress with productivity reports and timeline tools. In the meantime, task management hubs allow them to set flexible workflows for each team member.

Jira is a solid option for DevOps teams that depend on distributed remote workers. That’s because it blends flexibility and security. For instance, users can encrypt data at rest and in transit, and they can set permissions for each object. NordLayer’s guide to Jira security best practices offers a comprehensive overview of the product’s remote security features.

Microsoft Teams

Teams is the most popular platform for remote work operations. However, it doesn’t include native project management features.

Instead, users can create integrations with third-party management tools like Monday or Brightworks. These tools link together the video conferencing and messaging functions that make Teams useful. And they let managers schedule events and track progress easily.

Microsoft Teams is part of Office 365. This suite allows easy assimilation of Excel or Word into remote workflows. But this solution might come with security vulnerabilities. Learn more by reading our blog about Office 365 best practices.

Figma

Product designers rely on Figma to collaborate and develop ideas. The platform’s Juncture tool enables in-depth project management for every team and product. Co-creation spaces bring workers together to share prototypes or test apps. And tools like FigJam provide online whiteboards for real-time collaboration.

Figma is an excellent development platform for remote teams. But as with Microsoft Teams, it’s not entirely secure. Therefore, be sure to implement Figma security best practices before teams go online.

Communication and collaboration tools

Communication and collaboration are critical to the success of every remote team. And for that, there are many different tools to choose from.

communication tools for teams

The most secure options are end-to-end encrypted messaging apps. Troop Messenger and Element are designed to suit business communications. They encrypt messages between remote team members without compromising performance.

Other communication tools bring team members together to discuss ongoing projects. For example, Slack features customizable one-to-one, enterprise-wide, or departmental group chats, including live voice communications. It includes encryption, key management, audit logs, and data loss prevention.

Video collaboration is another must-have for most remote work operations. Zoom is optimized for distributed teams, with collaborative whiteboards, up to 100 meeting attendees, and instant team meetings for spur-of-the-moment contact. Zoom Events is another neat feature that helps build togetherness within a distributed workforce.

Video communication tools improve collaboration, but they can bring remote security risks. During the Covid pandemic, there were many cases of attackers recording Zoom calls. That’s because threat actors can steal credentials or hijack calls over insecure connections.

Companies should couple collaboration tools with a reliable B2B VPN and access management systems. They ensure that calls are private and only legitimate invitees will be present.

Access control and data security tools

Remote work setups should always include filters to exclude unauthorized users from corporate resources. Therefore, authentication and access control solutions are critically important. After all, managers will probably want to give the IT admins more freedom than a trainee.

authentication and authorization tools

Authentication

Authentication compares user access credentials to secure credentials databases. The gold standard for remote access is multi-factor authentication (MFA). This demands more than one unique identifier when users access work resources.

MFA can involve passwords and one-time codes sent via SMS or email. But more secure versions deliver encrypted codes to mobile apps. This avoids security issues related to email and SMS. Organizations can also switch from passwords to hardware tokens provided to remote workers.

Access management

Access control portals complement authentication tools. Identity and Access Management (IAM) systems verify users’ identities and connect them to the correct privileges.

Remote workers can access resources needed by their team or project. However, under the Zero Trust model, IAM tools limit access to all other network assets. This strengthens the network perimeter and boosts cybersecurity.

Encryption

Encryption is another critical aspect of secure remote working. Companies should leverage encryption features on apps and cloud platforms to safeguard sensitive information. And they should use encrypted channels to connect remote devices and central resources.

Data Loss Prevention (DLP)

DLP tools can also help businesses a lot with their remote workforce. They track sensitive data and prevent misuse by remote users. This way, managers can protect the most important databases and documents. As a result. extracting valuable data will be much more difficult.

In summary, strong encryption is essential when designing remote work setups. Insecure user devices can become entry points for malware and data thieves. Moreover, weak authentication and authorization systems make access easy for anyone with a functioning user ID and password.

Secure remote access solutions

Remote access workforces expand the threat surface and create new cybersecurity risks. This makes it critical to secure every remote connection. Encrypting cloud platforms and implementing MFA is not enough. Companies must lock down connections between remote devices and network assets.

Virtual Desktop Infrastructure (VDI) is one way to do so. It creates centralized servers on the cloud. These servers host workloads and data, meaning nothing is stored locally on employee devices. However, users can run apps hosted on the VDI in their home office.

VDI tools create encrypted connections between local devices and the virtualized environment. This is relatively secure. Unfortunately, attackers can still gain network access if they have legitimate credentials.

Companies can also use Virtual Private Networks (VPNs) to create encrypted tunnels for remote connections. VPN providers operate servers across the world, which can even improve connection speeds.

They apply cutting-edge encryption that is virtually impossible to crack. Moreover, your IP address will stay hidden, increasing anonymity. This makes it harder for hackers to mount interception and other types of attacks.

VPNs are a flexible security and privacy option for on-site and remote workforces. What’s more, these tools can secure access points in public locations. In the meantime, access company networks or attend client meetings while traveling.

NordLayer’s VPN solutions make creating safe remote work setups easier. Our Remote Access VPN encrypts connections via a simple client interface. Users can protect their devices instantly, whether they are accessing cloud platforms or central offices.

Make remote work secure with NordLayer

Remote work should always be protected. However, companies may struggle to secure data as employees shift away from centralized offices. This blog post has introduced key technologies and tools for keeping remote workers safe and boosting productivity.

Businesses should always choose the most secure project management and communication tools. While Azure or Zoom have their own security features, they alone are not enough. Organizations must be able to create gateways, use MFA authentication, protect remote access, and manage team member privileges.

It’s time to make your remote and on-site work safe. Get in touch with NordLayer, and we’ll help you create a solution that fits your business needs.
About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Minimizing external risks: a step-by-step guide to third-party risk assessment

What is a third-party risk assessment? 

Third-party risk assessments consider supply chain risks associated with third parties. They cut external risks while onboarding third parties to support business processes.

Any third party can introduce supply chain risks. This makes company assets and systems more vulnerable. Integrating third-party risk assessments into your risk management strategy is essential.

This article will explain why third-party risk assessments matter. And we will provide a simple, practical guide to assessing suppliers.

Key takeaways

  • Third-party risk assessment is a critical part of general risk management. Companies should carry out risk assessments for all external partners. Risk assessments protect sensitive data. They cut operational disruption. And they ensure that third-party relationships are compliant.

  • Due diligence is essential when assessing third-party risks. Risk assessments should include comprehensive evaluations of external suppliers. Critical areas include data security, geographical location, compliance history, and incident recovery processes.

  • Assessors should grade third parties. Assessments should focus on operational importance and the ability to access sensitive data. Concentrate on partners with the capacity to compromise security or damage internal systems.

  • Third-party risk management is a continuous process. Companies should update risk assessments and check that they cover relevant risks.

What is a third party?

A third party is an external agent that contracts with another company to supply goods or services. Many companies rely on third parties. External partners support their work and make operational savings. Sometimes, companies rely on thousands of external partners. Common examples include:

  • Professional office services.

  • Marketing partners.

  • Call centers and customer support services.

  • Freelancers like coders, secretarial support staff, technicians, writers, videographers, and corporate trainers.

  • Financial support. Includes accountants and partners for storing financial and customer data.

  • Cloud service providers

  • Security vendors

  • Travel and employee services

  • ISPs.

Importance of third-party risk assessment

Companies should never cut corners when assessing external partners. There are many reasons to implement a comprehensive third-party risk management strategy.

Meeting regulatory requirements

Many data security regulations demand third-party risk assessments. Regulations with third-party requirements include:

  • European Union’s General Data Protection Regulation (GDPR)

  • Payment Credit Industry Data Security Standards (PCI-DSS)

The Health Insurance Portability and Accountability Act (HIPAA) Companies that assess third parties will strengthen compliance. And they will reduce their exposure to regulatory risks.

Certainty about cybersecurity risks

Most third-party vendors introduce cybersecurity risks. Comprehensive third-party risk assessments provide information about the cybersecurity practices of external partners. They allow companies to choose secure partners. Risk assessments also help companies improve general cybersecurity. They can put in place appropriate internal security controls that manage critical risks.

Avoiding reputational damage

Customers trust companies with a commitment to security and transparency. Organizations that lose data or suffer regular downtime due to poor security struggle. A third-party risk assessment filters out partners with poor operational or security records. Screening partners improves the customer experience. It guards against attacks that ruin corporate reputations.

Financial protection

Supply chain attacks are a common source of data breaches and malware infections. And cyber-attacks can have a devastating impact on your corporate bottom line. Data breaches cost money to compensate customers. Companies must pay regulatory fines, and invest in updated security technology. And you can prevent these costs by risk-assessing every third-party relationship.

Strategic efficiency

Robust vendor management allows companies to move forward. With dependable long-term partners in place, organizations can plan their mid-range goals. There should be no need to swap partners every six months.

Solid risk assessment processes lead to long-term relationships. And these relationships are the basis for an effective corporate strategy.

Third-party risk types

Dividing risk allows assessors to generate more precise outcomes. It also gives managers a fuller picture of risks that each third party poses. Critical types of third-party risk include:

Cybersecurity risks

Third-party vendors often have access to internal networks and customer data. Partners with network access could expose your company to cybersecurity risks. A supplier risk assessment must establish which cybersecurity risks apply. It must also suggest appropriate action.

For example, you might use a third-party Customer Relationship Management (CRM) system. This supplier could pose an information security risk. The third party could expose customer data through poor cybersecurity controls.

Operational risks

Operational risks threaten everyday company operations. This category includes business continuity threats to network infrastructure and applications. But operational risks also cover the physical integrity of office spaces. And they include the ability of remote workers to connect. Third parties can also pose operational risks when their systems or products fail.

Compliance risks

Third parties pose a compliance or regulatory risk. This happens when their products or services breach regulatory rules. For example, HIPAA demands tight information security and privacy for patient records. But an email filtering service with poor security controls could put this data at risk. Risk assessors should consider every relevant regulation when analyzing potential suppliers.

Financial risks

Financial risk or organizational risk affects revenues and profits. Third-party relationships often help companies become more efficient. But the failure of vendor-supplied solutions can harm your finances. Vendor failure may immobilize payment portals. Or it could leave employees without access to critical resources. Vendors can also go out of business, leaving partners in limbo.

Strategic risks

Strategic risks refer to long-term effects on how a company operates. Third-party relationships should be durable. But supplier quality can decrease. Security practices can lapse, or partners may stop operations. Companies must consider business strategy 2 or 3 years into the future. Will third parties still be reliable partners?

Consequences of neglecting third-party risk assessment

What happens if you fail to assess third-party risks properly? In reality, the consequences can be damaging. Common results include:

  • Regulatory breaches and penalties

  • Lost customer trust and market share

  • Increased downtime and network integrity

  • Escalating cyber-attacks and security costs

  • Loss of strategic control with constant changes in supplier arrangements

  • Poor relationships with third parties as disagreements mount

  • Inflexible supplier management if risk assessments are not updated

Case-Study Board-of-innovation

Steps to conduct a third-party risk assessment1 steps for risk assessment 1400x915

Assessments must be comprehensive. And they should focus on risks that matter. Vendor risk assessments that consider outdated or irrelevant issues are useless. So how can you carry out effective supplier assessments?

1. Decide the scope of the risk assessment

Start by creating a risk assessment team. Bring in expertise from different areas of the company. Broader expertise will help identify relevant risks that compliance teams might miss. Executive support is also critical to managing third-party risk across the enterprise.

Determine what forms an acceptable level of risk. Some third-party risk is unavoidable. Assessment teams should be clear about identifying risks that need action and monitoring.

2. Document third parties and identify critical risks

The second step in the assessment process is inventorying current third parties. Document all partners and create separate vendor risk assessments for each one.

Next, decide which risks apply to each supplier. The following questions are helpful when understanding vendor risk levels:

  • Does the supplier have access to internal networks and company data?

  • Are there specific regulatory risks associated with the supplier? For example, HIPAA compliance.

  • What security controls against cybersecurity threats does the third party operate?

  • Does the supplier have an incident response plan and a risk management program?

  • What certifications does the supplier have?

  • What is the security record of the third party? Have they been subject to regulatory intervention?

  • Where is the third party located? Does location matter?

  • Are business partners likely to subcontract operations to other vendors?

At this stage, you may need to request information from third parties. Create a risk assessment form for suppliers that covers relevant areas. Or request information about security certifications if this is available.

3. Classify risks on a third-party risk matrix

The next stage involves assessing the severity of each vendor risk. The best way to do this is by using a matrix to generate risk scores.

A risk matrix generally includes two axes with five entries on each axis:

  • The X-axis grades the “impact” of an event and runs from “negligible” to “catastrophic”. Scores double from left to right.

  • The Y-axis assesses the likelihood of the event occurring. It runs from “extremely unlikely” to “extremely likely.” Again, scores double from bottom to top.

Scores rise as events become more likely and severe. For example, a CRM provider might steal customer data to sell on the Dark Web. We would classs this risk as “unlikely”. But the consequences would be “severe” giving it a score of eight.

In another scenario a supplier fails to meet GDPR privacy standards. This would have a different score. In that case, the likelihood might be “likely” and the impact “major.” This results in a score of 12.

This system makes it easy to focus on the most urgent risks. And it also makes it easier to revisit risk assessments during risk audits.

4. Select third-party suppliers

Use risk classifications to grade potential or existing suppliers. Choose third parties that provide services according to your company strategy. But only pick partners with solid risk management practices.

With a robust risk assessment in place, you should be able to choose reliable and secure partners. Security teams will also know how to put in place controls to mitigate third-party risks.

5. Put in place continuous risk assessment

Risk assessment does not end when controls and smooth relationships are in place. Third-party risk assessment is a continuous process.

Revisit each third-party assessment on at least an annual basis. Check that the initial process identified critical risks. And make adjustments to reflect changes in the risk environment. For example, a supplier may have suffered a data breach. Or they may have started subcontracting services. Both changes could affect the supplier’s risk score.

Best practices for third-party risk assessment

2 best practices for risk assessment 1400x930

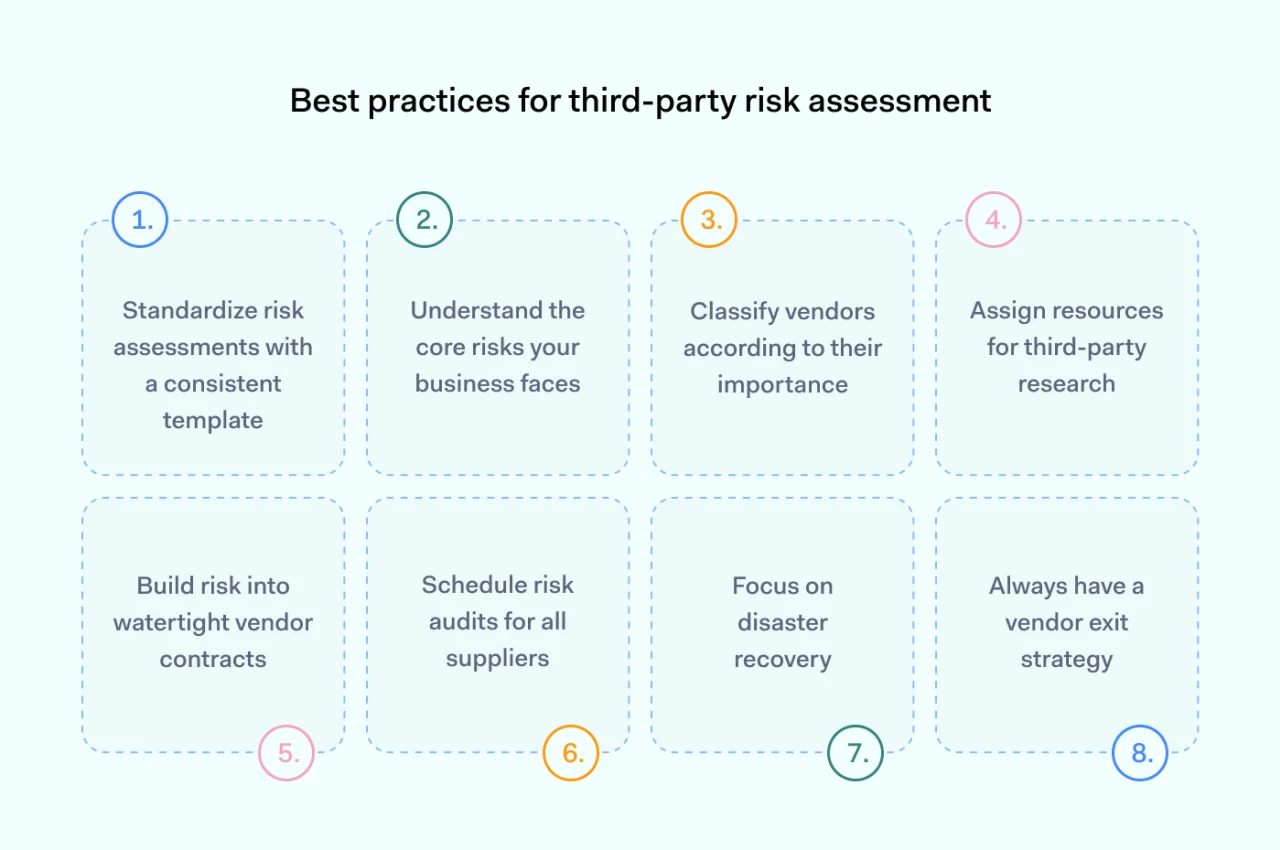
1. Standardize risk assessments with a consistent template

Third-party risk assessments should be comparable. Companies must assess many suppliers. And they need the ability to pick a partner that meets their risk requirements.

Create standard risk assessment and questionnaire templates for each supplier. Document risk assessments. Create a risk framework that enables informed decision-making when onboarding external partners.

2. Understand the core risks your business faces

Not all risks are equal. Focus on critical risks. These risks can damage your company’s operational, compliance, and security posture.

Risks vary between sectors. Healthcare companies must follow HIPAA guidelines. Merchants need a robust PCI-DSS compliance framework. Select the risks that suit your business profile.

3. Classify vendors according to their importance

Vendors carry different amounts of risk. For instance, food delivery services are less critical than partners hosting financial data. Clarify the most important external relationships. Make them a priority when carrying out third-party risk management.

4. Assign resources for third-party research

Third-party risk assessments should identify the strengths and weaknesses of suppliers. Research vendor security processes, compliance histories, and client support services.

5. Build risk into watertight vendor contracts

Risk assessments should feed into third-party contracts or Business Associate agreements. Make sure contracts include core compliance requirements. State areas of responsibility for external partners. Track contracts as part of ongoing vendor risk assessment.

6. Schedule risk audits for all suppliers

Risk assessments should be dynamic. Revisit each supplier assessment annually and check that previous risk classifications remain relevant. Assess data security issues, including any data breaches. Ensure suppliers are compliant with any new regulations. And assess new risks that arise as regulations change.

7. Focus on disaster recovery

When assessing third parties, always request information about their incident recovery processes. Find partners that cut downtime and restore services without compromising security.

8. Always have a vendor exit strategy

Onboarding vendors is only half the challenge. Companies should always change suppliers that fail to meet risk-based requirements. Set a minimum service level and include this in vendor contracts. And enforce this policy to avoid using non-compliant partners.

How can NordLayer help?

NordLayer’s security products will help you manage supply chain risk. IP allowlisting enables access for legitimate partners but blocks unknown identities. Users can apply multi-factor authentication (MFA). This ensures that internal employees and third parties verify their identities.

Network segmentation also allows organizations to protect confidential data and critical applications. Attackers targeting your supply chain may manage to gain network access. But NordLayer’s micro-segmentation tools restrict their ability to move between assets. As a result, the scope to extract data and damage systems is much lower.

Create a risk management program that minimizes external risks. Contact us today. Explore how NordLayer’s solutions can supplement your vendor risk management strategy.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.