Skip to content

Scale Computing and Mustek announce partnership to bring HCI and edge computing solutions to market in South Africa

Midrand, ZA – June 18, 2020 – Scale Computing, a market leader in edge computing, virtualisation and hyperconverged solutions, today announced a strategic partnership with Mustek, one of the largest assemblers and distributors of personal computers and complementary ICT products in South Africa. The agreement will enable Mustek to provide Scale Computing’s hyperconverged infrastructure (HCI) series, including the HC3, to partners throughout South Africa. Scale Computing are currently Mustek’s only HCI vendor and are well placed to service Mustek’s needs throughout South Africa with its local presence, and the expertise of Regional Sales Manager MEA at Scale Computing, Jaco Delport.

Established in 1987, Mustek is a technology reseller to SMEs, large corporates, and complex enterprises across many verticals, from telecommunications to public sector, in South Africa. Built to satisfy the growing need for information technology solutions in the South African market, Mustek expertly supports a passionate customer base of resellers, who in turn supply products that Mustek assembles and distributes to all parts of the consumer, business, and public sector market, including the retail industry. With 100% commitment to customer satisfaction, Mustek will work with its dealers to take advantage of Scale Computing’s edge computing, virtualisation, servers, storage, and backup/disaster recovery solutions in one complete, easy-to-use platform.

With all components built-in, including the hypervisor, Scale Computing’s HC3 customers have no need for third-party components or licensing. This all-in-one configuration simplifies management and maintenance, which helps to streamline tasks, saving time and money. This makes the technology ideal for industries that require IT infrastructure with high performance and minimal management, especially during the current uncertain circumstances around COVID-19.

The partnership will enable businesses in South Africa to build affordable, high performance HCI and edge solutions where existing technologies were previously too complex to deploy and manage.

“We are very excited to be working with Mustek, who have a long and proven reputation as one of the easiest and most professional distributors for South African resellers to do business with,” said Johan Pellicaan, Vice President and Managing Director EMEA at Scale Computing. “Their team has an unwavering commitment to customer satisfaction, and adherence to the highest quality standards and benchmarks, that will bring our HCI technology to market and meet demand in the channel for affordable, deployable solutions for businesses looking to innovate at the edge.”

“We are honoured to introduce Scale Computing as not only one of our latest brands, but as our sole supplier of HCI,” commented Marina Lancaster, Enterprise Product Manager at Mustek. “We expect to see a high volume of demand for HCI and edge solutions from our channel partners, as their customers across various verticals look to digitalise and modernise amidst the current climate.”

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Scale Computing 
Scale Computing is a leader in edge computing, virtualization, and hyperconverged solutions. Scale Computing HC3 software eliminates the need for traditional virtualization software, disaster recovery software, servers, and shared storage, replacing these with a fully integrated, highly available system for running applications. Using patented HyperCore™ technology, the HC3 self-healing platform automatically identifies, mitigates, and corrects infrastructure problems in real-time, enabling applications to achieve maximum uptime. When ease-of-use, high availability, and TCO matter, Scale Computing HC3 is the ideal infrastructure platform. Read what our customers have to say on Gartner Peer Insights, Spiceworks, TechValidate and TrustRadius.

About Mustek
Mustek combines the best of local assembly capabilities with the multinational product portfolio by affording its customers a choice of the renowned Mecer brand of computing equipment and a broad range of top-tier ICT brands which address every level of the technology stack.

This strategy enables Mustek to offer its customers a perfect match for their technology needs, whether driven by configuration and customisation requirements (as is the case with the Mecer brand), or through tried and trusted best industry practices and competitive pricing (as is the case with the multinational brands which Mustek distributes).

Mustek’s position in the South African market has been built on an unwavering commitment to customer satisfaction, the development of some of the most sought-after relationships in the international ICT market, adherence to the most stringent international quality standards and benchmarks, and a staffing policy that sees it retaining staff that are trained and accredited to the highest possible level.

All of this culminates in Mustek being one of the easiest and most professional distributors for South African resellers to do business with.
Cyber ​​Attack on Twitter

Last Saturday (18), the digital world was shocked by another episode of data leaks, and the protagonist this time was Twitter. That’s right, hackers were able to steal data from users of the microblogging platform. And it was not ordinary users, but celebrities, public people and even organizations with millions of followers who had their data exposed, including the use of bitcoin wallets in the scheme. Although it is still under investigation, it is already clear that this episode exposed a major vulnerability of Twitter.

But what were the dynamics of this attack? Also, in times of elections, can we trust the process of choosing future leaders?

By targeting the accounts of world leaders and celebrities on Twitter, hackers managed to orchestrate an attack based on social engineering, and thus promote a scheme involving cryptocurrencies through administration tools of the social network itself. According to the Verizon Data Breach Investigations Report 2020, 22% of the nearly 4,000 incidents and security attacks surveyed involved social engineering. Bill Gates, Elon Musk, Barack Obama, Warren Buffet, and even US presidential candidate Jon Biden were some of the hacked profiles. Not to mention the Apple and Uber accounts.

But how did these hackers manage to perform this well-orchestrated attack?

The answer comes in the form of two words: SIM Swapping. SIM Swapping is a technique used by malicious agents that aim to transfer the number and data of the victim’s SIM chip to another one in their possession. In this case, through social engineering attacks, the hacker convinces a telephone line’s user that a problem has occurred with their chip and needs to transfer the number to another. This type of attack requires that some information, such as the number, name, and other data, is already in the attacker’s hands. Depending on the situation, it is not that difficult to obtain this information if it has already been leaked, for example. Similarly, agents can also persuade operators to perform this transfer, since they have access to all data required for the swap.

Through Social Engineering techniques, malicious attackers deceive their victims to gain improper access to credentials and administrative tools. By obtaining this access, hackers changed their victims’ email addresses on the microblogging network. Then, the attackers disabled the two-factor authentication. This makes it possible to prevent any account modification alerts from being received by its legitimate user. With absolute control of the accounts, hackers start promoting the cryptocurrency-based scam scheme.

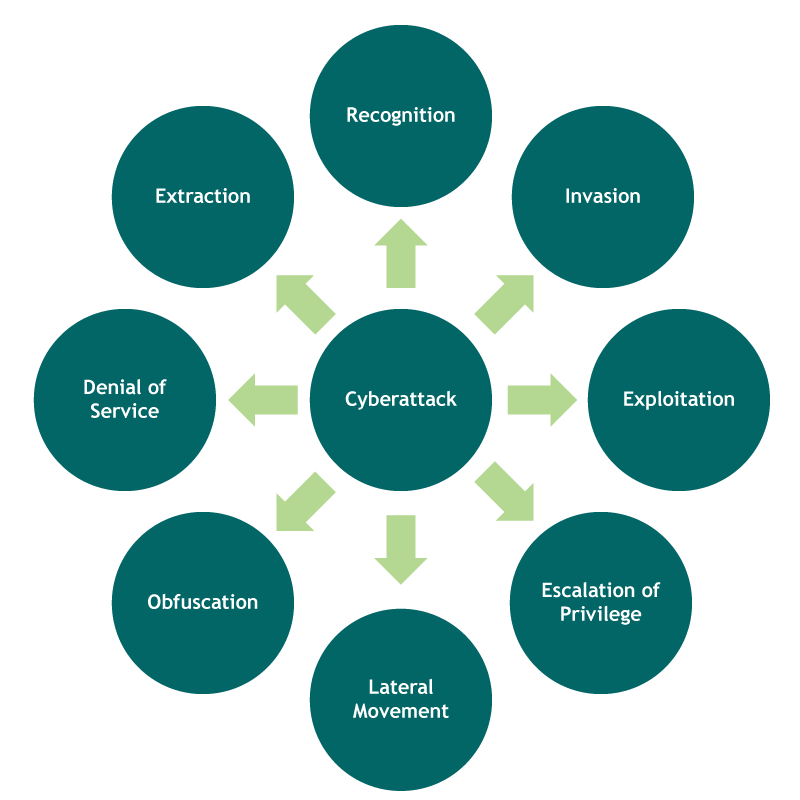
Typically, the logic of a cyberattack like this involves several phases:

  1. Recognition: In this first phase, malicious attackers try to identify IT routines, as well as security measures and data traffic flow. Also, hackers scan the entire environment to get a clear view of network resources, as well as privileged credentials and services. Domain controllers, Active Directory, and servers are the attackers’ first targets to find other privileged credentials and complete the cyberattack. In many cases, this prior knowledge may exist due to some previous link between the attacker and the victim organization. 
  2. Invasion: based on what was discovered in the Recognition phase, hackers are able to enter the environment normally through malware or exploitation of vulnerabilities.
  3. Exploitation: This phase involves the act of exploiting vulnerabilities to compromise the environment.
  4. Escalation of Privilege: attackers usually need more privileges on systems to gain more access and privileges. This is usually done by escalating administrator privileges.
  5. Lateral Movement: Once in the infected environment, attackers can move laterally to other devices and credentials, in order to obtain more data and more access.
  6. Obfuscation: For a cyberattack to be successful, attackers need to erase all tracks left in the environment. At this point, it is even possible to change log data and confuse the incident investigation team.
  7. Denial of Service: disruption of the normal access by users and systems to prevent the actions of the attack from being monitored or blocked.
  8. Extraction: when the malicious user is able to improperly extract the data.

A unanimity among cybersecurity professionals is that this attack on Twitter involved privileged or administrative credentials. According to the Data Breach Investigations Report, the use of privileged credentials occurs in 20% of the attacks. This type of credential, also called “keys to the kingdom”, allows access to add, remove, and modify settings in accounts, applications, and systems. In this specific case, the hacker was able to compromise a credential from the Twitter administration tools. By gaining access, the attacker was able to move around the environment, compromising other privileged accounts. 

According to confirmation by Twitter itself, the nature of the attack was an insider threat. When it comes to data breaches, employees themselves can be one of the biggest risks to the organization. According to Verizon, these threats can be: accidental, when personnel is only poorly trained; negligent, when employees try to bypass the implemented policies; or malicious – the most dangerous – when an employee is motivated by financial gains, espionage, or revenge. An important fact, according to Verizon, is that 30% of cyberattacks performed in 2019 involved insider threats.

But how to prevent this type of attack?

It is complicated to deal with an attack coming from someone inside the organization. This is mainly because this insider threat knows (very) well the organizational environment, the mechanisms, and tools installed. So, it is easy for these attackers to deceive these control mechanisms. In this case, using Zero Trust-based controls can be a good way to mitigate the risks associated with a cyberattack. In terms of credential protection, the implementation of this strategy must not only be focused on identity only, such as access and permissions, but also on the aspect of user behavior. So much so that, in this specific case, the compromised credentials had protection mechanisms, as two-factor authentication. Finally, Zero Trust-based policies recommend the implementation of policies to allow people to take only the necessary actions, based on the concept of Least Privilege.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Segura®
Segura® strive to ensure the sovereignty of companies over actions and privileged information. To this end, we work against data theft through traceability of administrator actions on networks, servers, databases and a multitude of devices. In addition, we pursue compliance with auditing requirements and the most demanding standards, including PCI DSS, Sarbanes-Oxley, ISO 27001 and HIPAA.

SigRed: A Wormable Microsoft DNS Server RCE Vulnerability

SigRed Overview

SigRed is a vulnerability that was exposed yesterday (July 14th 2020) by the security firm Check Point. Successful exploitation of the vulnerability could lead to a malicious actor gaining control of the organizational DNS server, often leading in turn to domain administrator privileges, allowing the attacker complete control of any domain-joined Windows machine.

The vulnerability lies in Microsoft’s DNS server and could be triggered from either inside the network, by an attacker controlling an internal asset, or, in some conditions (as stated below), from outside the network, making it even more dangerous.

As Microsoft Active Directory is deeply integrated with DNS services, the DNS service is virtually always enabled on domain controllers. An attacker gaining control of a domain controller through the DNS service could lead to a complete compromise of the network, allowing the attacker complete access to all Windows machines joined to the domain, whether patched or not, using the domain administrator privileges of the compromised domain controller. Even if the compromised DNS server does not serve as a domain controller, It is likely that the Domain administrator credentials are stored locally and can be retrieved by a tool such as Mimikaktz. Furthermore, the attacker is also able to return custom responses to DNS, allowing man-in-the-middle for unencrypted protocols, such as HTTP, FTP and others.

Exploitation Methods

The precondition for this exploit is that the local organization’s DNS server is configured to recursively resolve queries to external domains using root-hints. This configuration is the default configuration when the DNS service is installed.

Exploitation is either impossible or further complicated in the following cases:

  1. The DNS server is an authoritative server of a DNS zone and does not recursively resolve queries to other domains.
  2. The DNS server is part of an independent DNS infrastructure, such as an air-gapped network. In such a case, the attacker will need either write access to the DNS server or existing control over an authoritative DNS server serving an arbitrary zone on the network.
  3. The DNS server is configured to use a forwarder server (such as 8.8.8.8 or 1.1.1.1) instead of directly using root hints. In such a case, the attacker will need to propagate the attack through the chain of recursive calls, which has not yet proven possible but cannot be completely discarded.

The vulnerability can be exploited in two ways:

  1. From inside the network:
    An attacker that has a hold of an asset inside the network, can compromise the organization’s local DNS server by sending queries for external domain records which are controlled by the attacker (e.g. http://www.evil.com). Such a request will cause the local DNS server to communicate directly with the attacker’s DNS server. A malicious crafted response from the attacker’s server could lead the attacker to compromise the local DNS server.
  2. From outside the network:
    An attacker can send a malicious link to a user inside the network to a website it controls (via e-mail, for example). Once the user opens the link in either Microsoft Edge Legacy or Internet Explorer (does not apply to Google Chrome, Mozilla Firefox or Microsoft Edge Chromium, not tested on other browsers), a malicious web page is sent back to the client that causes the client itself to perform a series of DNS queries to the local organization’s DNS server, that in turn, would query the attacker’s DNS server, at which point the DNS server can be compromised in the same manner as presented above.


Exploitability in OT Networks

Most OT networks have Windows endpoints that are used for process control, technical maintenance and others. An attacker successfully exploiting this vulnerability from either inside or outside the network can gain domain administrator privileges, allowing full access to all domain-joined workstations and servers even if already patched.
At this point, the attacker will be able to install ransomware, malware, steal information, disrupt OT operations and/or access any machine in the domain for any purpose.

As many OT networks are slower to patch systems than IT networks, they are exposed for a longer period of time, allowing attackers to exploit this vulnerability. As a successful exploitation often results in domain administrator privileges, a single unpatched DNS server is sufficient to compromise the entire network, even if all other DNS servers are already patched.

Mitigation Recommendations

Microsoft has released a patch (July 14th 2020) to the vulnerability. We urge everyone to update their Microsoft Windows Servers as soon as possible.

If for any reason one is unable to currently patch its Windows Servers, running the following command would limit the DNS response size to 0xFF00 (65280), and will prevent the vulnerability from running


reg add “HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\DNS\Parameters” /“TcpReceivePacketSize” /t REG_DWORD /d 0xFF00 /f && net stop DNS && net start DNS

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About SCADAfence
SCADAfence helps companies with large-scale operational technology (OT) networks embrace the benefits of industrial IoT by reducing cyber risks and mitigating operational threats. Our non-intrusive platform provides full coverage of large-scale networks, offering best-in-class detection accuracy, asset discovery and user experience. The platform seamlessly integrates OT security within existing security operations, bridging the IT/OT convergence gap. SCADAfence secures OT networks in manufacturing, building management and critical infrastructure industries. We deliver security and visibility for some of world’s most complex OT networks, including Europe’s largest manufacturing facility. With SCADAfence, companies can operate securely, reliably and efficiently as they go through the digital transformation journey.

ESET reaffirms ‘Champion’ position in global Cybersecurity Leadership Matrix 2020

BRATISLAVA – ESET, a global leader in cybersecurity, has achieved Champion status for the second year in a row in the latest Cybersecurity Leadership Matrix 2020 from Canalys, improving upon 2019’s Matrix position with a focus on vendor growth and momentum beyond Europe.

Canalys is a leading global technology market analyst firm with a distinct channel focus that strives to guide clients on the future of the technology industry and to think beyond the business models of the past.

The Canalys Cybersecurity Leadership Matrix assessed 17 cybersecurity vendors on their global channel and market performance over the last 12 months. The Matrix combines partner feedback from Canalys’ Vendor Benchmark tool with an independent analysis of each vendor’s momentum in the channel based on their investments, strategy, market performance and execution.

ESET achieved the highest score benchmarks in the categories of product availability and supply, and ease of doing business. ESET’s improved position in the Matrix is reflective of the launch of an MSP enablement module to drive growth through 7,000 MSPs, as well as incorporating feedback from local Partner Councils on product roadmaps, technologies and customer needs. This collaborative approach ensures that regions across the globe are operating innovatively and efficiently and are tuned in to the pulse of the global cybersecurity landscape.

ESET was one of only seven vendors to be awarded Champion status, and one of four to reaffirm said status, alongside Cisco, Palo Alto Networks, and Fortinet. Champions have the highest scores in the Canalys Vendor Benchmark and exhibit common characteristics, including making improvements to and simplifying channel processes, and demonstrating a commitment to growing partner-generated revenue. Champions must also show that they are making sustainable investments in the future of their channel models, including channel programs and initiatives.


Ignacio Sbampato, chief business officer at ESET, commented: “We have been a channel-focused company since the beginning of our existence and our channel partners know that, so this recognition of ESET as a ‘Champion’ two years in a row is a confirmation that we are doing a great work together based on an honest and straightforward approach towards building strong and long-lasting collaborations all over the world. We are constantly innovating and improving on our offerings, and it is extremely rewarding to know that our partners rate us highly, and our increased support for MSPs is valued. A safer internet experience for all is central to our core mission, the foundation of which is our strong relationships with our partners.”

To find out more about ESET’s offerings, visit our website.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Ripple20: Mixed Results in SCADAfence’s Exploitability Lab Tests

As part of our mission to secure the world’s OT, IoT and Cyber Physical infrastructures, we invest resources into offensive research of vulnerabilities and attack techniques.

Ripple20 are 19 vulnerabilities revealed by Israeli firm JSOF that affect millions of OT and IOT devices. The vulnerabilities reside in a TCP/IP stack developed by Treck, Inc. The TCP/IP stack is widely used by manufacturers in the OT and IoT industries and thus affects a tremendous amount of devices.

Among the affected devices are Cisco Routers, HP Printers, Digi IoT devices, PLCs by Rockwell Automation and many more. Official advisories by companies who confirmed having affected devices can be found here, in the “More Information” section.

The most critical vulnerabilities are three that can cause a stable Remote Code Execution (CVE-2020-11896, CVE-2020-11897, CVE-2020-11901) and another that can cause the target device’s memory heap to be leaked (CVE-2020-11898).

On behalf of our customers, we set out to explore the real impact of these vulnerabilities, which we’re now sharing with the public.

The research has been conducted by researchers Maayan Fishelov and Dan Haim, and has been managed by SCADAfence’s Co-Founder and CTO, Ofer Shaked.

Exploitability Research
We set out to check the exploitability of these vulnerabilities, starting with CVE-2020-11898 (the heap memory leak vulnerability), one of the 19 published vulnerabilities.

We created a Python POC script that is based on JSOF official whitepaper for this vulnerability. According to JSOF, the implementation is very similar to CVE-2020-11896, which is an RCE vulnerability that is described in the whitepaper. Also mentioned about the RCE vulnerability: “Variants of this Issue can be triggered to cause a Denial of Service or a persistent Denial of Service, requiring a hard reset.”

Trial Results:
Test 1 target: Samsung ProXpress printer model SL-M4070FR firmware version V4.00.02.18 MAY-08-2017. This device is vulnerable according to the HP Advisory.

Test 1 result: The printer’s network crashed and required a hard reset to recover. We were unable to reproduce the heap memory leak as described, and this vulnerability would have been tagged as unauthenticated remote DoS instead, on this specific printer.

Test 2 target: HP printer model M130fw. This device is vulnerable according to the HP Advisory.

Test 2 result: Although reported as vulnerable by the manufacturer, we were unable to reproduce the vulnerability, and we believe that this device isn’t affected by this vulnerability. We believe that’s because the IPinIP feature isn’t enabled on this printer, which we’ve verified with a specially crafted packet.

Test 3 target: Undisclosed at this stage due to disclosure guidelines. We will reveal this finding in the near future.

Test 3 result: We found an unreported vendor and device, on which we can use CVE-2020-11898 to remotely leak 368 bytes from the device’s heap, disclosing sensitive information. No patch is available for this device. Due to our strict policy of using Google’s Responsible Disclosure, we’ve reported this to the manufacturer, to allow them to make a patch available prior to the publication date.

Key Takeaways
We’ve confirmed the exploitability vulnerabilities on our IoT lab devices.

On the negative side: The vulnerabilities exist on additional products that are unknown to the public. Attackers are likely to use this information gap to attack networks.
On the positive side: Some devices that are reported as affected by the manufacturers are actually not affected, or are affected by other vulnerabilities. It might require attackers to tailor their exploits to specific products, increasing the cost of exploitation, and prevent them from using the vulnerability on products that are reported as vulnerable.

SCADAfence Research Recommendations
Check your asset inventory and vulnerability assessment solutions for unpatched products affected by Ripple20.
The SCADAfence Platform creates an asset inventory with product and software versions passively and actively, and allows you to manage your CVEs across all embedded and Windows devices.
Prioritize patching or other mitigation measures based on: Exposure to the internet, exposure to insecure networks (business LAN and others), criticality of the asset.
This prioritization can automatically be obtained from tools such as the SCADAfence Platform.
Detect exploitation based on network traffic analysis.
The SCADAfence Platform detects usage of these exploits in network activity by searching for patterns that indicate usage of this vulnerability in the TCP/IP communications.
If you have any questions or concerns about Ripple20, please contact us and we’ll be happy to assist you and share our knowledge with you or with your security experts.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About SCADAfence
SCADAfence helps companies with large-scale operational technology (OT) networks embrace the benefits of industrial IoT by reducing cyber risks and mitigating operational threats. Our non-intrusive platform provides full coverage of large-scale networks, offering best-in-class detection accuracy, asset discovery and user experience. The platform seamlessly integrates OT security within existing security operations, bridging the IT/OT convergence gap. SCADAfence secures OT networks in manufacturing, building management and critical infrastructure industries. We deliver security and visibility for some of world’s most complex OT networks, including Europe’s largest manufacturing facility. With SCADAfence, companies can operate securely, reliably and efficiently as they go through the digital transformation journey.