
Skip to content

Malware Threat Research 2020-2023

If you ask Google or AI what malware is, they’ll likely break it down as software meant to disrupt your systems, networks, or devices — but this description alone might not convince you of its significant threat.

Your perspective on malware is likely to change when you engage with someone who has suffered greatly because of it or once you delve into the latest facts on cyber attacks. It’s in these moments that you truly grasp the reality of malware as a legitimate and substantial threat.

In collaboration with independent third-party researchers, we analyzed cybersecurity incident data from January 2020 to September 2023 to assess and show you how big of a threat malware is today.

Here’s what we discovered…

Key findings from the research

1. With nearly 3 million attacks in 2023, malware has spread like a biological virus

While you may not find it surprising that the number of malware attacks has increased over the last few years, the speed at which this issue has been escalating might catch you off guard.

In 2020, approximately 614,144 malware-related incidents were reported. However, this number surged to 2,898,142 in 2021 and nearly doubled again in 2022, reaching 4,858,963. As you can see, these are not minor differences but massive leaps highlighting a substantial increase in the scale of the problem.
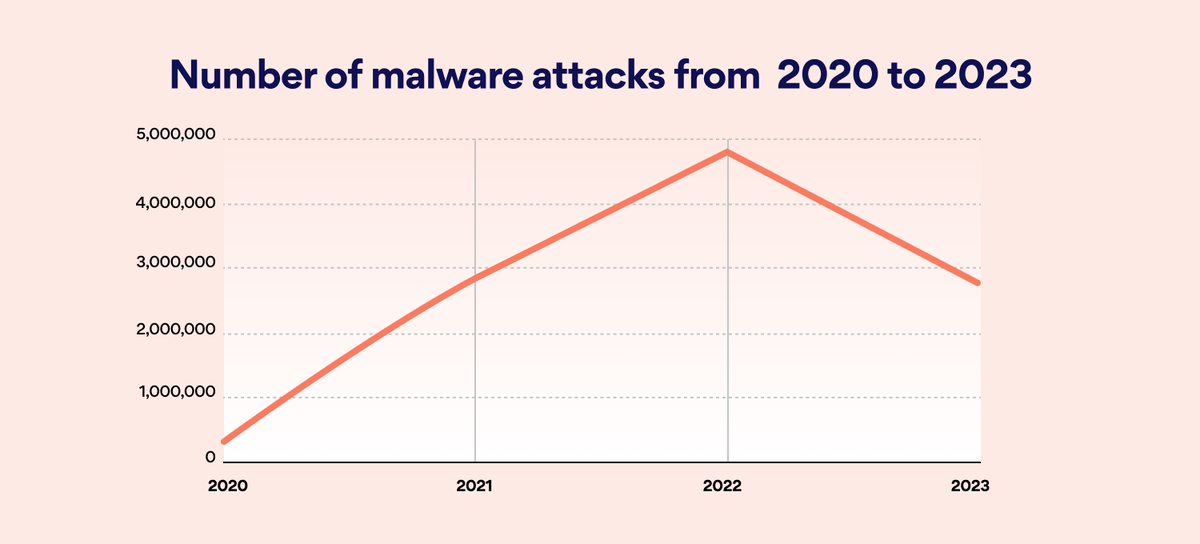
number of malware attacks 2020-2023 graph

In 2023, there were 2,678,841 malware attacks reported. However, before you assume that this signals a gradual resolution of the problem, let us highlight some details that — unfortunately — indicate it’s not yet time to celebrate.

To start, the malware incident data we’ve examined covers only the first 9 months of 2023, implying that the total number of cases for the entire year will more than likely be higher.

Moreover, a troubling trend observed by numerous IT experts is the increasing frequency of successful attacks. This indicates that cybercriminals are employing more and more sophisticated hacking methods and focusing on more targeted approaches. Simply put, this means we’re observing fewer malware attacks overall, but more of them are accurate. This is further evidenced by the continuous growth in the number of successfully executed unique email attacks, as depicted in the graph below.

number of successful unique email attacks graph

How does malware spread? Email is a common culprit, where spam and phishing tricks convince users to click on harmful links or download infected attachments. Careless browsing, like clicking on pop-ups, can also lead to visiting malicious websites that stealthily download malware.

Within organizations, coworkers clicking on malicious links can spread malware through the internal network, infecting multiple devices at the same time. Another risk comes from bundled software, where malware sneaks in with seemingly trustworthy downloads, causing users to unknowingly install various harmful programs — from annoying adware to data-stealing spyware.

2. Brazil, the USA, and India have the most malware-affected users

In the analysis of cybersecurity incidents, the focus was also on examining the global distribution of cases related to malware. Presented below are the top 15 countries with the highest number of malware-affected users (drawing from data spanning from October 2020 to November 2023):

  1. Brazil — 9,659,846 affected users

  2. USA — 6,966,426 affected users

  3. India — 6,914,742 affected users

  4. Indonesia — 5,354,246 affected users

  5. Vietnam — 3,611,798 affected users

  6. Egypt — 3,516,376 affected users

  7. Mexico — 3,042,467 affected users

  8. The Philippines — 2,926,483 affected users

  9. Turkey — 2,888,663 affected users

  10. Pakistan — 2,849,788 affected users

  11. Columbia — 2,655,695 affected users

  12. Thailand — 2,523,671 affected users

  13. Argentina — 2,300,732 affected users

  14. Peru — 2,215,622 affected users

  15. France — 2,142,316 affected users

Despite securing the top rank in the 2020 Global Cybersecurity Index (GCI) with a score of 100 index points, the United States of America holds second place for the most users impacted by malware — with a staggering number equivalent to the entire population of Massachusetts. Notably, five other nations in the Americas and seven in Asia are grappling with the impacts of the malware situation.

The study also reveals that France takes the lead for the highest number of users affected by malware in Europe. This may be attributed to several factors, such as the country’s substantial internet usage (82% of the population) and the increased likelihood of economically and politically charged cyberattacks against French users.

3. RedLine is the most common type of malware

Malware comes in various types and forms like adware, spyware, ransomware, trojan horses, and keyloggers. Each one possesses specific functionalities that can compromise one’s digital security. However, certain types of malware are more popular than others.

According to the research, the most prevalent types of malware in the last four years have been:

  1. RedLine

    RedLine is a type of malware designed to collect data from web browsers, applications, email and messaging apps, and cryptocurrency wallets. In simple terms, it functions as a remote access trojan, enabling cybercriminals to steal and transfer sensitive user data, which is later sold on the dark web. The research reveals that RedLine attacks constitute 59% of the total records collected — surpassing the runner-up Vidar by 3.2 times.

  2. Vidar

    Vidar is malicious software designed to steal sensitive information, including login credentials, credit card details, cryptocurrency wallets, and browser history, from infected systems. The stolen data can be used for identity theft or financial fraud — or it can be sold on the dark web. As previously noted, RedLine constituted nearly two-thirds of all the analyzed attacks. However, Vidar remains a considerable threat, comprising 18% of the total number of attacks.

  3. Raccoon

    Raccoon, also known as Raccoon Stealer, is a type of information-stealing malware designed to extract sensitive data from the computers of its victims. This includes, but is not limited to, login credentials and credit card information.
    Raccoon Stealer typically spreads through malicious websites, phishing emails, or other deceptive methods. Once it infects a system, it can covertly send the stolen information to a server operated by cybercriminals.
    Raccoon cases account for 12% (21% between July 2022 and April 2023) of malware attacks analyzed for this research.

Other common types of malware include AZORult, CryptBot, Taurus, and Meta.

incidents by malware type graph

Why have these malware types become more widespread? One reason might be that they are easier to create and deploy. Furthermore, using these types of malicious software may offer greater financial rewards for cybercriminals compared to other methods. The popularity of specific malware is also influenced by the constantly evolving landscape of cyber threats, technological vulnerabilities, and shifts in the digital environment.

4. Tens of millions of credential records were stolen from social media and entertainment platforms

Given the widespread practice of storing sensitive data on cloud servers, email accounts, and social media, it comes as no surprise that these platforms are prime targets for cybercriminals. However, the actual numbers will raise a few eyebrows.

So brace yourself for some eye-opening statistics as we explore the top domains associated with the biggest number of data theft incidents caused by malware and unveil the staggering number of records that fell into the wrong hands.

Most targeted domains*:

  1. accounts.google.com – 8.2 million of stolen records

  2. facebook.com – 5.9 million of stolen records

  3. login.live.com – 5.6 million of stolen records

  4. m.facebook.com – 3.2 million of stolen records

  5. Instagram.com — 3.1 million of stolen records

  6. discord.com – 3.1 million of stolen records

  7. netflix.com – 3 million of stolen records

  8. roblox.com – 2.8 million of stolen records

  9. com.facebook.katana – 2.5 million of stolen

  10. records amazon.com – 2.4 million of stolen

  11. records paypal.com – 2.3 million of stolen records

  12. twitter.com – 2.3 million of stolen records

The information above indicates a consistent trend of cybercriminals stealing data from widely used digital platforms. This highlights the necessity for enhanced cybersecurity measures to ensure secure data storage and access.

However, it is ultimately up to the user to take proactive steps to actively educate themselves on protecting their credentials and take appropriate follow-up measures.

*NordPass is not endorsed by, maintained, sponsored by, affiliated, or in any way associated with the owners of the mentioned domains. Domains are listed solely for the purpose of accurately reporting information related to cybersecurity incident data.

What you can do to protect yourself from malware threats

First and foremost, protection against malware – whether for individual users or entire organizations – relies on awareness and a sense of responsibility for implementing appropriate security measures for systems, platforms, and data in use. Therefore, everyone needs to take proactive steps in this regard, as without such engagement, achieving adequate protection becomes challenging.

Here are four actions you can take to enhance your protection against malware:

  1. Raise awareness: By learning about different types of malware and sharing this knowledge with others, you can effectively reduce the risk of being targeted. Awareness campaigns, for example, play a crucial role in helping people identify suspicious activities like phishing emails or dubious website links.

  2. Use antivirus software: Using antivirus software is essential for detecting and removing malware from your devices. A good antivirus constantly scans your system for known malware signatures and behaviors, offering a vital layer of defense against various threats.

  3. Update your systems regularly: Regularly updating your operating system, applications, and firmware is vital as it addresses known security vulnerabilities frequently targeted by malware. These updates typically include security patches and bug fixes, bolstering your system’s defenses against potential cyber threats.

  4. Use a password manager: Using a password manager allows you to create and store unique, complex passwords for each of your accounts, lowering the risk of unauthorized access. By securely storing your credentials, password managers help prevent malware from stealing your login information and accessing sensitive accounts.

How NordPass can help protect your sensitive data and account access

NordPass is a cybersecurity solution designed to help businesses and individuals protect their data and minimize the threat of malware attacks. How so?

First, NordPass is an end-to-end encrypted credentials manager. This means you can use it to securely generate, store, manage, and share passwords, passkeys, credit card information, and personal data — and do so knowing that they are all protected by advanced encryption algorithms.

Second, NordPass facilitates the implementation of single sign-on (SSO) and multi-factor authentication (MFA). You can use it to present employees with a convenient yet highly secure method of logging in to the company accounts.

Third, organizations can use NordPass as an identity and access management (IAM) tool to control and monitor access to company resources in real time. In other words, with NordPass, a company can see exactly who accessed what and when and manage access privileges with ease.

In addition, NordPass goes the extra mile by utilizing a Master Password. Most browser password managers lack this feature, making them more susceptible to malware attacks.

Naturally, our product is equipped with many other features like Autofill, Data Breach Scanner, and Password Health, all designed to enhance your cybersecurity and help defend against malware-related attacks. If you’re interested in exploring these features and gaining a comprehensive understanding of our platform, we invite you to visit our website.

Stay safe!


Methodology

NordPass, in partnership with third-party researchers, analyzed various sets of credentials sourced from a 6.6TB database. The study involved examining the source website and the type of malware used to steal the data (such as Redline, Vidar, Taurus, Raccoon, Azorult, and Cryptbot). No personal data was acquired or purchased by NordPass to conduct this study.


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

How secure are your company’s social media, really?

Social media — the missing piece in a cybersecurity puzzle

When asked about why cybercriminals target passwords, most people typically think of common motives like stealing sensitive data, hijacking accounts for ransom, or infecting systems with malware to disrupt operations. But in an exclusive interview for NordPass, Dennis-Kenji Kipker, a Professor of IT Security Law and Research Director at cyberintelligence.institute, brought to light a sometimes overlooked aspect — that some attackers may steal credentials just to get access to a company’s social media platforms and wreak havoc. He said:


As an attacker, I could also try to attack the whole social media system of a company and have the company’s communications under control. […] Data, if disclosed, could cause very considerable damage not only to the company as an abstract legal entity, but also to all people involved in business relationships with that company and, of course, the employees.

Dennis-Kenji Kipker

Professor of IT Security Law and Research Director at cyberintelligence.institute

Simply put, Professor Kipker points out that mishandling passwords for social media accounts can lead to more than just losing access. It can also result in losing the trust of partners and customers, which can then lead to financial losses. How do we know things like these could happen? Because similar incidents have occurred in the past.

Real-life examples of huge social media takeovers

A major corporation stuns everyone by announcing its acquisition by a primary rival; a government agency spreads fake news causing chaos in the cryptocurrency market; a renowned music label reports the passing of one of its top artists — these are not plot ideas for the next season of Black Mirror. They are real instances where false information was shared through the official social media channels of popular organizations, leading many people to believe it was true.

That’s right. The first situation refers to the 2013 Twitter hack of Burger King, where cybercriminals seized control of the company’s Twitter account to spread false news alleging that Burger King had been acquired by McDonald’s. The second incident occurred in 2024 and involved the Twitter hack of the Securities and Exchange Commission (SEC). In this case, cyber attackers exploited the SEC’s account to falsely announce the approval of spot-Bitcoin exchange-traded funds, leading to a significant surge in Bitcoin’s price. The third example pertains to the 2016 incident involving the hacking of Sony Music’s Twitter account, during which cyber attackers circulated a hoax about the death of the pop star Britney Spears.

While not officially confirmed, it’s widely suspected that these social media takeovers stemmed from compromised passwords or actions leading to password breaches, such as phishing or malware. As expected, each incident damaged the affected company’s reputation, occasionally resulting in significant consequences and, at other times, causing less severe repercussions.

Of course, as you can imagine, these are but three out of hundreds, if not thousands, of other similar cases. This begs the question: why did these events occur in the first place? 

Why do social media takeovers happen?

The first reason, as hinted earlier in this article, is that businesses often overlook the security of their social media accounts. While they focus on protecting their internal systems from malware and other threats, they sometimes neglect the security of their social media presence.

Another factor may be businesses’ tendency to prioritize their core operations over social media security, assuming these platforms are inherently safe and require no additional steps to safeguard against potential risks.

The next critical aspect is when organizations overlook the necessity of removing access to social media accounts when employees leave their positions. This creates a dual risk: first, if ex-employees are dissatisfied, they can post damaging content, harming the company’s reputation. Second, inactive accounts can become targets for hackers, allowing them to use them as gateways to take over the company’s social media channels.

Then, there’s the issue with passwords. At NordPass, we use the phrase, “For almost every task at work, there’s a password.” This rings true as most business operations necessitate the use of password-protected accounts. However, as highlighted in our Top 200 Most Common Passwords report, many individuals — regardless of their job title or position within the company — use weak passwords that can be easily cracked. Moreover, many employees use the same password across multiple accounts and services, amplifying the risk of a breach.

We also need to touch upon the irresponsible sharing of passwords among company members, often done through chat, email, or… written notes (yikes!). If some business leaders were to inquire about how their staff members share passwords for company social media accounts like LinkedIn, Instagram, or Facebook, they might be alarmed by the lack of security practices in place.

Of course, losing access to company social media accounts can also happen due to phishing, malware attacks, or other cyber intrusions targeting unsuspecting employees. However, ensuring passwords are strong and securely managed at all times decreases the chances of falling victim to such cyber threats, thus protecting the integrity and security of company social media accounts.

What if your company’s social media gets hacked?

Although it’s not overly challenging to imagine the outcomes of a social media takeover, being informed about the potential consequences can provide stronger motivation for us all to take action. 

First and foremost, a social media takeover can lead to severe reputational damage. Malicious actors have the power to tarnish an organization’s reputation by posting damaging content or spreading false rumors. This could result in the loss of key business partners and clients. Even when it’s clear that the content in question is the work of cybercriminals, rebuilding relationships with partners and customers can be more challenging than expected.

Another major risk, closely tied to reputational harm, is financial loss. When cybercriminals hijack a company’s social media channels and spread false information, it can cause existing customers to turn away and deter potential customers from engaging with the brand. As a result, the company may experience a significant decline in sales revenue, and face heightened difficulty in securing investments or loans. Not to mention the fact that the time and resources required to address the aftermath of a social media takeover can impede the company’s focus on growth.

A hostile social media takeover can also result in a loss of privacy for the company’s members. In other words, it opens the door to personal information being exposed or misused, potentially resulting in identity theft or attempts to exploit someone’s private image. Repairing such damage could require years of effort and resources beyond what the company initially anticipated.

Yes, social media takeovers can be prevented

Let’s shift our focus away from discussing the reasons and dangers of social media takeover and concentrate on solutions to the problem at hand — of which there are a couple.

To effectively prevent social media takeovers, a company must first recognize the threat. As highlighted earlier, many individuals may not even realize that cybercriminals target passwords to seize control of business social media channels. Therefore, the first step is to raise awareness across the organization and establish clear guidelines for accessing and sharing social media platform credentials among company members. This includes determining who can access the credentials, specifying who they can be shared with, and deciding what actions to take when a social media manager or anyone with access to company social media leaves the organization.

Step two involves utilizing today’s available technology to allow employees to securely handle the company’s social media account credentials. This can be achieved by adopting a robust password manager like NordPass. How so?

How NordPass can help your company in this regard

First, NordPass is an easy-to-use yet technologically advanced password manager that allows organization members to securely store, manage, and share passwords, passkeys, credit card details, and other sensitive information.

Beyond that, NordPass is a cybersecurity tool that allows you to monitor access to your company resources, including social media channels. Plus, it enables you to quickly identify weak, old, and re-used passwords in your company, and check whether company credentials have been compromised in a breach. 

As a result, NordPass can be a valuable tool for organizations looking to protect their social media accounts from misuse by outsiders  — all while enhancing performance and efficiency.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Set and protect. A cybersecurity road map for small and home offices

In the evolving world of cyberthreats, small and home offices share a single need: a reliable security solution.

If you’re leading a small office, you are likely no stranger to working 12 hours a day. It might even feel like 24/7, doing taxes, communicating with clients, and marketing your business on social media platforms.

You likely have also personally installed a firewall on your laptop, but still, one day, you find out that your bank account got breached or your business data has been compromised. This might mean losing money or the trust of your clients, and it definitely means losing precious time to put the wheels back on your business. 

Today, basic protection doesn’t just mean having a firewall; it requires endpoint security with scanning tools, a password manager, and data encryption. Simply put, many businesses who invested into separate products over time to address basic risks just aren’t equipped to handle today’s threats.

This is the reality for a massive number of small offices/home offices around the world that face growing risks from digital threats.  For example, 31% of businesses with fewer than 10 employees surveyed in the UK during the winter of 2022-2023 experienced a cyber-attack or a security breach. To understand the full scope of the situation, there are 5.28 million such businesses in the UK.

These cyberthreats leave users facing a diversity of complex security challenges – challenges for which individual solutions like firewalls, well-suited to block malicious traffic, are simply not built to counter. Today’s online tools and business processes require cybersecurity solutions that layer multiple advanced technologies for detection, browsing protection, anti-phishing, and botnet protection, as well as exploitation, ransomware, and network protections supported by artificial intelligence and machine learning to stop threats.

The backbone of the economy makes for an interesting target

The small offices and home offices discussed in this blog are tiny when taken individually, but collectively, they comprise a massive workforce. For example, according to the latest data gathered back in 2019, 78.5% of U.S. businesses had 1-9 employees.

The situation is similar elsewhere. Businesses with 1-9 employees make up 74.1% of Canadian businesses and 82% of all UK businesses.

This makes these small offices/home offices sit nicely in the sweet spot user group for ESET’s Small Business Security offering; they’re the second largest source of wealth, right behind home equity. This also means that this group is substantial enough to factor into cybercriminal campaigning and simultaneously poses easy targets even for what have become common risks like simple password spraying attacks.

These businesses are often easy targets for cybercriminals because:

• They do not believe they are an interesting target for cybercrime because they are too small.

• They believe they cannot afford comprehensive high-tech security solutions.

• They often use outdated and unsupported software.

• Heads of small offices/home offices often don’t have IT education, don’t have time for cybersecurity awareness trainings, and lack finances to hire IT staff.

What threats are out there?

The complexity and scale of these threats are global, but let’s take Australian farmers as an example. In the first half of 2022, farmers fell victim to a series of cyberattacks with an accumulated loss of AUD 1.2 million (USD 792,026).

Some of those farmers fell victim to fake livestock sellers on Facebook or phishing websites pretending to sell machinery, while in reality farmers were sending money for nothing.

Here are some of the most common attacks threatening small offices and home offices:

  • (Banking) Data breaches – Losing sensitive data, especially banking and payment information, is the most feared cyberattack among small offices/home offices participating in an ESET internal survey. This can often happen due to phishing or an account breach.     
  • Compromised personal devices – Attackers can abuse employees’ personal devices to compromise business systems. According to the Samsung 2023 survey, 48% of organizations with a Bring Your Own Device (BYOD) policy witnessed malware introduced through an employee’s personal phone.
  • Physical theft – Almost 60% of small offices/home offices participating in an ESET internal survey expressed concerns about lost devices and data. Over 2 million laptops are reported stolen each year in the U.S., with the associated data losses estimated at over $7 billion.

Setting up defenses

Such a long list of threats can be a headache considering how much should be done to protect your business: backing up your data, protecting servers, having a good password policy ideally combined with MFA, installing endpoint protection on all your devices, an anti-theft solution, and taking cybersecurity awareness training to identify common red flags for prevalent scams.

However, alongside their normal duties and responsibilities, it is quite understandable that small offices/home offices don’t find time to worry about cyberattacks. And trying to deal with all these threats by setting up a VPN, password manager, firewall, mobile security solution, data encryption, and banking protection in a piecemeal fashion is unsustainable.

Some of those businesses openly admit this: “We’re a small company. The biggest issue is trying to survive on a week-by-week basis. We can’t afford to allocate sums to cybersecurity. I’ll spend it as and when I have it, or when I need to,” said a participating managing director surveyed by the UK Department for Science, Innovation & Technology in 2023.

But there is a better way. Digital security doesn’t have to mean a long and complicated shopping list composed of individual cyber defenses. You can get one affordable subscription that covers them all.

ESET Small Business Security presents an all-in-one solution coming with ESET HOME as the complete security management platform and support that won a 2023 SC Award for delivering best-in-class customer support and services.

ESET Small Business Security offers:

  • Reliable, easy-to-use security, with a minimum system footprint
  • Multi-OS protection including Windows, Android, MacOS and Windows Server
  • Safe Banking
  • Safe Browsing
  • Password Manager
  • VPN
  • Ransomware Shield
  • Anti-Theft
  • Botnet Protection
  • Network Inspector
  • Safe Server – The protection of company and customer data stored on a file server running on Windows Server operating system; it also automatically scans all inserted USB flash drives, memory cards, and CDs/DVDs
  • Support for 5 up to 25 devices

Let someone else put in the effort

Considering the previously mentioned surveys, it is safe to say that globally, millions of small offices/home offices fall victim to cybercrime every year. And it looks like some of those people just accept their fate. The truth is that when businesses put effort into cybersecurity, it is rarely ever appreciated. However, when something goes wrong, that failure is always criticized.

However, there is a way to mitigate those cyber risks without spending too much time and money. ESET can put in the effort instead of you with its reliable and multilayered functionalities all packed in one solution. Simple, isn’t it?

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

24.3.5 Voyager released

Changes compared to 24.3.4

Enhancements

  • Added retrying for intermittent errors that occur when restoring data to UNC paths

Bug Fixes

  • Fixed sorting of logs on the Server Logs page on the Comet Server web interface
  • Fixed an issue which caused the user detail page to fail to load for usernames with certain lengths in the Comet Server web interface
  • Fixed an issue where the Comet Server web interface failed to remember column selections for usernames containing an @ symbol
  • Fixed an issue with missing hints for valid usernames in the Comet Server web interface
  • Fixed a cosmetic issue with missing or misplaced loading animations in the Comet Server web interface
  • Fixed an issue with remote-controlled restores from the Comet Server web interface being unable to write to user home directories
  • Fixed an issue with backup job progress bars being left below 100% after the job completed
  • Fixed an issue with searching for items in Office 365 backup snapshots
  • Fixed an issue with unusable content when attempting to restore EFS-encrypted files to an archive
  • Fixed an issue with failing to restore directory timestamps
  • Fixed a cosmetic issue with EFS-encrypted files appearing as directories in the Comet Server web interface

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Comet
We are a team of dedicated professionals committed to developing reliable and secure backup solutions for MSP’s, Businesses and IT professionals. With over 10 years of experience in the industry, we understand the importance of having a reliable backup solution in place to protect your valuable data. That’s why we’ve developed a comprehensive suite of backup solutions that are easy to use, scalable and highly secure.

Remote virtual machine access using port forwarding and SSH private/public keys

Virtualization technology allows us to create multiple virtual machines (VMs) on the same physical machine.

A virtual machine operates like a software program running on a computer, simulating the behavior of an independent machine.

In essence, it establishes a computer within another computer.

When operating within a window on the host computer, a virtual machine offers users an experience that’s nearly identical to using a separate computer.

For many software developers, using a virtual machine is preferable for easy cross-platform compatibility purposes; they also offer greater security, flexibility, and scalability.

When setting up your virtual machine, you can access its graphic user interface (GUI) to interact with the virtual machine separately from the other machine(s) or operating systems on your physical computer.

However, relying solely on the GUI may not always be practical if you’re a software developer, especially if you need to access a VM remotely.

In such cases, you should use the Secure Shell protocol (SSH) to execute remote logins or commands securely over an unsecured network.

Parallels Desktop enables remote access to virtual machines with SSH and port forwarding.

By default, Parallels Desktop operates in shared network mode, which works “out of the box” and does not require any specific configuration.

Parallels Desktop will work as a virtual router for your virtual machines when you use this networking mode. However, it also means that the VMs cannot be accessed from external computers.

The port forwarding (also known as port mapping) functionality allows computers on your local network and the Internet to connect to any virtual machines that use the shared networking mode.

According to the port-forwarding rule, the connection to a specific port on your Mac will be redirected to a specific port of your virtual machine.

To gain remote access to a VM via port forwarding, you must first configure Parallels Desktop to accept the connection using a port forwarding rule.

This is achieved by following the process outlined below.

Establishing port forwarding rules

Note: Port forwarding is only available in Parallels Desktop for Mac Pro and Parallels Desktop Business Edition.

1. Open the Parallels Desktop Command Center

2. Select the VM you want to access remotely 

Then, click the Configure button.

3. Once the Configuration window opens, select the Hardware tab

Then the Network option on the left side, then click “Advanced.”

4. Click on the “Open Networking Preferences” button

5. Click the Add (+) button below the Port forwarding rules list

6. In the displayed window, perform the following actions

  • In the Protocol field, specify the port type you want to establish network connections. You can choose between the TCP or UDP port types.
  • In the Source Port field, type the incoming port number on your Mac.
  • In the Forward to section, indicate the name or IP address of the virtual machine you want to connect to.
  • In the Destination Port field, type the port on the virtual machine to which the data will be transferred.

  7. Click OK to add the rule

Checking port forwarding

To check that the rule works properly, enable, e.g., SSH on your virtual machine (some Linux distributions have it enabled by default).

As an example for SSH, use the following rule:

Protocol TCP
Source PortChoose a different port number between 1024 to 49151 for each VM
Forward toChoose your virtual machine
Destination Port22

To make sure that port forwarding is enabled from your Mac inside a virtual machine, use one of the following scenarios (in these examples, port 8081 is redirected to a Linux VM, and port 8888 is to a Windows VM) :

Scenario 1: connect from the same Mac

In Terminal, type in the following command and press Enter:

ssh -l <your_VM_username> -p <source_port> 127.0.0.1

Enter the password for the user in the virtual machine and press Enter:

Scenario 2: connect from another Mac or PC in the same network

In Terminal (on Mac) or PowerShell (on Windows), type in the following command and press Enter:

ssh -l <your_VM_username> -p <source_port> <host_machine_IP_address>

Enter the password for the user in the virtual machine and press Enter.

To check that you logged into the virtual machine, execute the following command in Terminal:

uname -a

If you successfully log into the virtual machine, you will see a Linux kernel version.

The same method can also be used to set up an SSH port forward for a Windows machine by adding that to the port forwarding list:

You can run a “systeminfo” command to verify the system you are on.

Using SSH key pairs

Now we have the systems tested and working using password authentication, we can make them more secure.

SSH public/private keypairs offer a more secure, convenient, and scalable authentication mechanism than traditional password-based methods.

By leveraging SSH keypairs, organizations can strengthen their security posture and ensure secure remote access to their systems, eliminating the need to transmit passwords over the network.

With keypairs, the private key remains securely stored on the user’s computer.

In contrast, the public key is stored on the server, significantly reducing the risk of interception by malicious actors.

Because the keypairs are generated using cryptographic solid algorithms, they are much longer than passwords, making them highly resistant to brute force attacks.

Once SSH keypairs are set up, users can seamlessly log in to SSH-enabled systems without entering a password, adding convenience for automated processes and scripts.

Generating SSH public/private keys

The SSH key pair consists of two cryptographic keys: public and private keys.

These keys are mathematically related but are designed so that it is computationally infeasible to derive the private key from the public key.

The public key is shared securely with the server or system you want to access.

It can be freely distributed and stored on several servers or systems and is provided when you attempt to connect to a server.

The private key is kept securely on your local computer or device. It should never be shared with anyone else.

This key is used to decrypt encrypted messages with the corresponding public key, and when you attempt to connect to a server, your local SSH client uses your private key to prove your identity.

When you attempt to connect to a server using SSH, the server sends a message encrypted with your public key.

Your SSH client decrypts this message using your private key and sends back a response.

If the server can successfully decrypt your response using your public key, it knows you possess the corresponding private key, allowing you to access the system.

SSH keypairs are typically generated using cryptographic algorithms such as RSA or DSA.

Your local SSH client software can generate these keys for you. The keys are often stored in files (e.g., “id_rsa” for the private key and `id_rsa.pub` for the public key) in a hidden .ssh directory in your user’s home directory.

Creating SSH keypairs

To explain how to generate and use the SSH keypairs, I have three systems: a Mac, which is my local machine; an Ubuntu VM, which will be the remote machine; and a Mac VM, which will use the port forwarding rules.

Each system has a different theme for the terminal windows to make it easier to follow.

First, I will check my local machine to ensure no local keys exist, using the command:

ls ~/.ssh/id_*

As no matches were found, no keys were present on our local machine. If they are present, you should back them up in case they are accidentally removed or lost.

Next, we can generate our SSH key on the local machine.

To do this, type in the command:

ssh-keygen

The command replies that it is generating a public/private keypair using rsa as the default encryption.

If you wish to use a different algorithm you can use the -t flag to select from the following alternatives: dsa, ecdsa, ecdsa-sk, ed25519, ed25519-sk.

I will also add a comment using the -C flag so that I can quickly identify what the key is for.

My command line would look like this:

ssh-keygen -C "Test for SSH Keys on Mac & Ubuntu"

By default, the file is saved in my user directory in the .ssh folder, so I hit enter to accept that.

I also hit enter for the passphrase question, which adds an extra layer of security but also means I would have to enter it each time I connect. I am trying to avoid that in this example.

Retrieving the public key

If we rerun the ls command, we can see two files in the .ssh directory: the private and public keys.

Move into the .ssh directory, open the contents of the public file, and copy them so that we can add them to the remote machine in a file called authorized_keys.

cd .ssh 

ls -la 

cat id_rsa.pub

Adding the public key to the remote machine

To enable SSH access to a remote machine, you must upload the public key from your SSH key pair onto the remote server. This allows the remote machine to decrypt connections initiated by your local computer, which uses its corresponding private key for encryption.

On the remote machine, go to your home directory and check if the .ssh subdirectory exists:

cd ~
ls -al ~

If it does exist cd into that directory, and if it doesn’t, create the subdirectory, and then go into it and check to see if the authorized_keys file exists:

mkdir .ssh
cd .ssh
ls -al

If the authorized_keys file does not exist, create one using the following command:

touch authorized_keys

Then edit the file using your editor of choice to add the public key copied from the local machine.

If you already have an authorized_keys file in the directory with content, add your new key on a new line and save the file.

Putting it all together

Now that our private and public keys are created, we need to check that they work.

Check the IP address of your virtual machine from the Parallels devices-> networking tab

Now ssh into that system from your local host that has the private key installed on it:

ssh <user>@<ip address>

And as you can see, we are logged in without providing a password.

As we have set up port forwarding on our local host, we should also be able to access the Ubuntu VM from a different system, but going through the host machine and using the port that was assigned at the beginning of this article, that being 8081 of the Mac system.

If I go to my Mac VM running on the same host, I can copy a key to the Ubuntu box, but this time, instead of cut/paste, I will use the ssh-copy-id command to add to my authorized_keys file on the Ubuntu system, but using port 8081 of my host system:

ssh-copy-id -p <port> <user>@<ip address>

We can check the key was correctly added by going back to the Ubuntu VM, and checking the authorized_keys file:


The text highlighted in red is the new key from the Mac on the VM. If we return to that VM, we can execute the ssh command displayed at the end of the ssh-copy-id command message to access the Ubuntu VM system from my Mac’s VM system via my host Mac:

And as you can see from the command prompt at the end, I am back on the Ubuntu System.

Ready to try it yourself? Sign up now for a free 14-day trial to see how easy it is to implement port forwarding and secure key pairs using Parallels Desktop Pro. 

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Parallels 
Parallels® is a global leader in cross-platform solutions, enabling businesses and individuals to access and use the applications and files they need on any device or operating system. Parallels helps customers leverage the best technology available, whether it’s Windows, Linux, macOS, iOS, Android or the cloud.