Skip to content

How to detect SSH key reuse

The Secure Shell (SSH) protocol is an encrypted network protocol used to access an interactive shell and perform file transfers between systems over untrusted networks. SSH is the de facto management protocol for non-Windows machines (and even some Windows systems), replacing the Telnet protocol from days past.

The most recent version of the protocol, SSH-2, was standardized in 2006 and provides a high level of security when configured correctly. runZero analyzed aspects of SSH in the ecosystem to explore how SSH is being deployed in the real world.

My voice is my passport. Verify me.

The Secure Shell protocol consists of three phases. First, a secure transport is negotiated, similar to TLS. After the transport key negotiation is complete, the client attempts to authenticate, specifying one of a handful of known methods, and the server replies indicating whether the authentication succeeded and what remaining authentication methods are available if not. Finally, after successful authentication, a session is opened. This session enables access to channels, which in turn provide interactive shells, port forwarding, agent forwarding, and file transfer capabilities, among other options.

The three most common authentication mechanisms are:
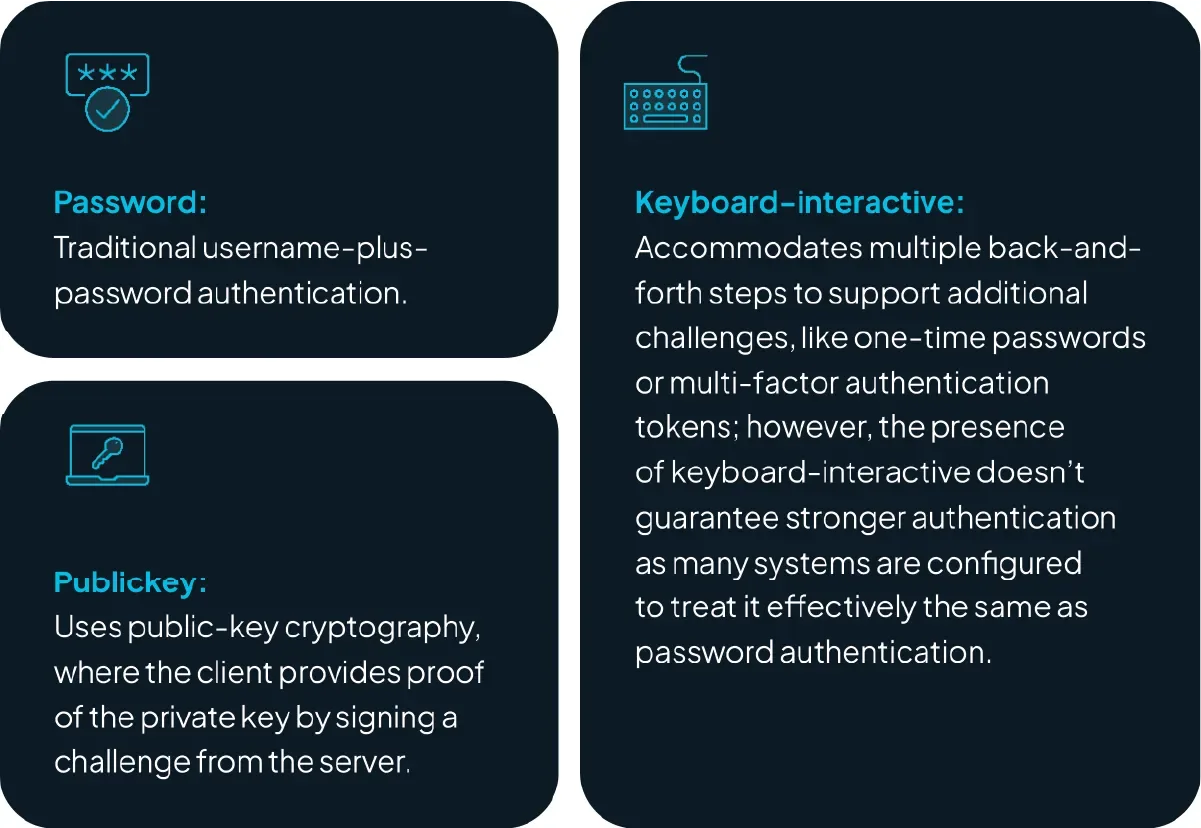
Of the three mechanisms, publickey is by far the most secure and considered best practice. This type of authentication also supports key certificates, which provide even stronger security for key issuance and revocation. In publickey authentication, a user’s public key is stored in their profile on the destination system and only someone with the corresponding private key can authenticate. This prevents compromise through password-guessing attacks.

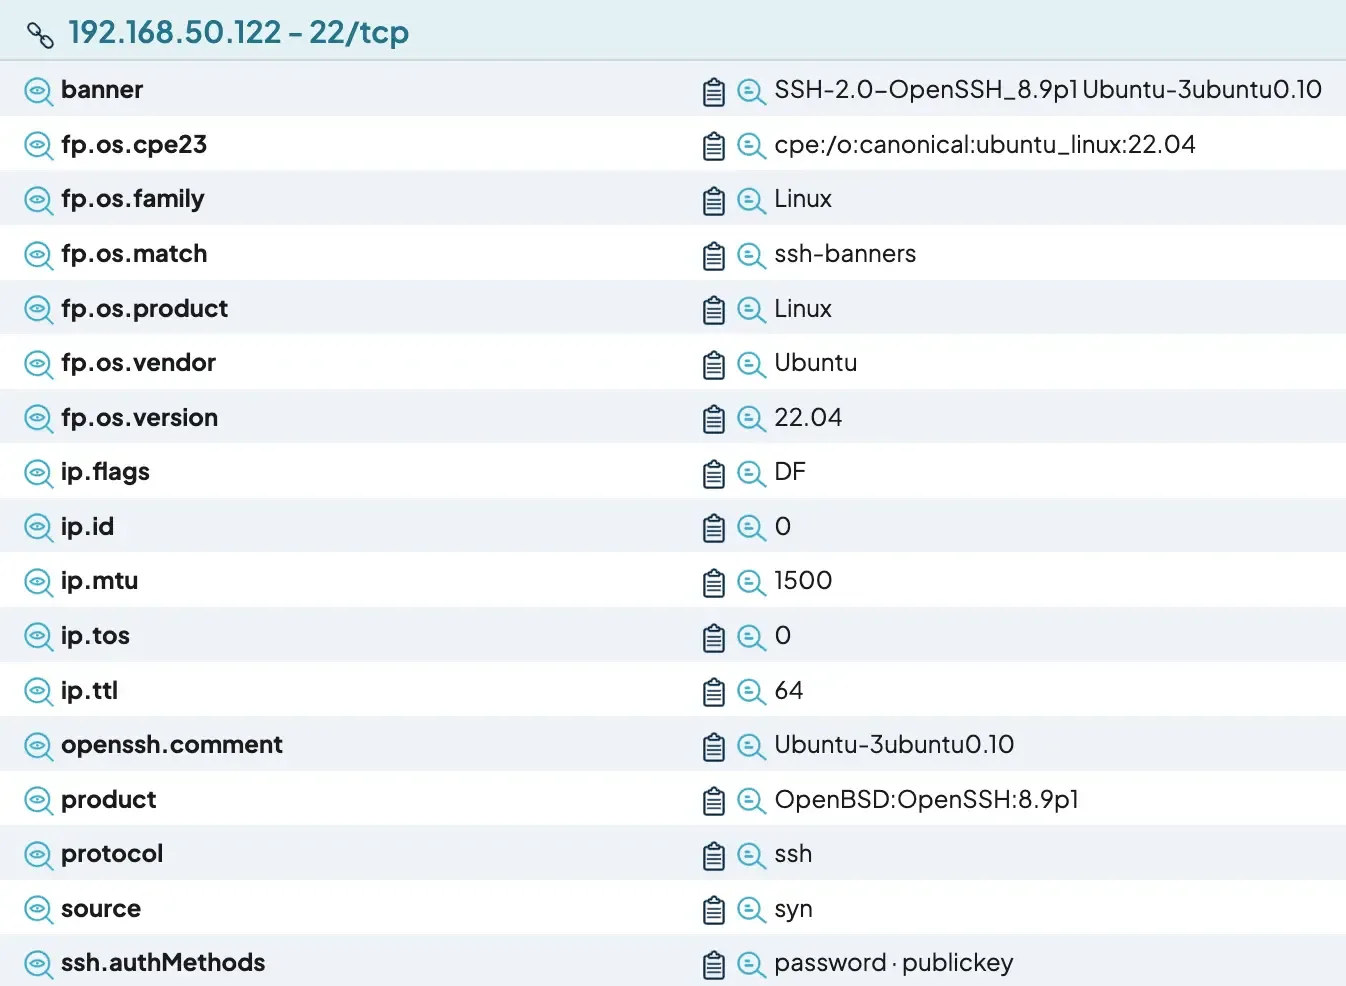
FIGURE 1 – A partial screenshot of runZero showing the results of an SSH scan.

In our survey of SSH endpoints, 54% support both password and publickey authentication. This is the default for many modern SSH services, and allows the optional use of a strong public key while allowing for the ease of password setup. In general, best practices recommend that the password mechanism be used only to set up public key authentication, after which it should be disabled. Leaving password authentication enabled exposes systems to password enumeration attacks and the potential for weak passwords set by users.

Password authentication is more common on storage and networking devices, where accounts are less likely to be associated with individual persons. Often, though, these systems still support publickey authentication, which should always be preferred over password authentication where possible.

Looking at the big picture, 95% of SSH endpoints offer publickey authentication. Whether these systems are configured to use it is another question entirely. What is perhaps somewhat disheartening is that, while 95% of endpoints support the most secure mechanism, approximately 92% still support some form of password authentication as well.
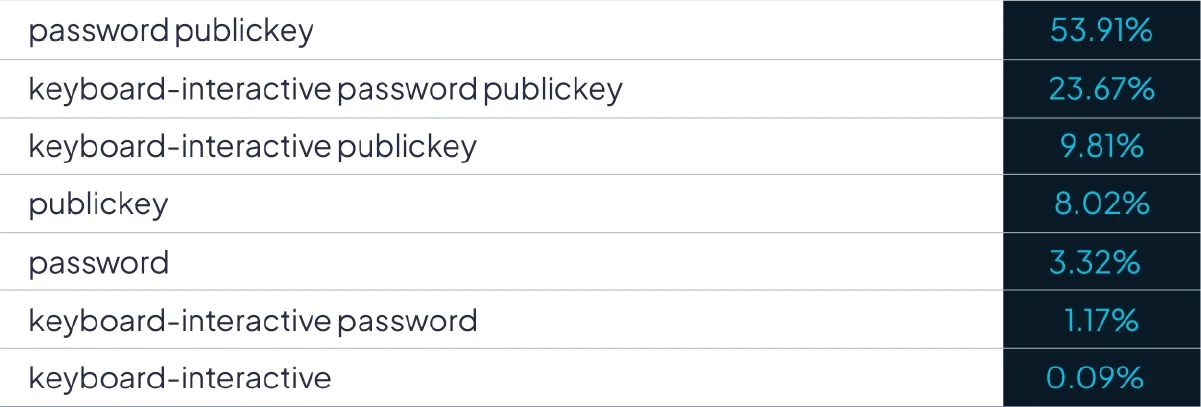
FIGURE 2 – Distribution of SSH authentication method combinations.

Dupes and Duplicity

SSH servers identify themselves by way of an SSH host key pair. Just as key pairs allow users to prove their identity, so too do host keys allow servers to prove their identity to users. Or at least prove their possession of the correct key.

This functionality is critically important. Without it, users could be tricked into thinking that they had logged into a totally different, possibly spoofed or malicious, system, with obvious security ramifications. However, unlike TLS, most SSH servers are not configured to use any form of Public Key Infrastructure (PKI) or other chain-of-trust to establish proof of server identity. Such functionality is available, but is not in widespread use.

Instead, most SSH clients will use a technique called Trust on First Use (TOFU). In this scheme, the client will trust a host key the first time it receives it for a given host. Going forward, if the host key changes, the SSH client can alert the user to the problem. While this doesn’t allow the user to confirm the host’s identity, it at least allows them to confirm that the host’s identity hasn’t changed.

ubuntu@u2404-infra-02: ̃$ ssh 192.168.50.127 
The authenticity of host ‘192.168.50.127(192.168.50.127)’ can’t be established.
ED25519 key fingerprint is SHA256:wdNLQA-2vyp6Qv+8T7Ac2rF6vRJz34P5RCQo9VJAa+Ms.
This key is not known by any other names.
Are you sure you want to continue connecting
(yes/no/[fingerprint])? █

While host keys are ostensibly used to uniquely identify a host, oftentimes multiple hosts have the same host key. This is sometimes intentional, such as when automatically provisioning many ephemeral systems. Unfortunately, it can also happen accidentally, such as during virtual machine image cloning, and this can have very undesirable consequences since it undermines the concept of key trust.

We performed a limited audit to see how frequently host keys were being reused across our data set. We identified more than 350 instances where the same host key was shared across unrelated environments. Further exploration across the wider Internet revealed thousands of additional shared host keys. These are often the result of a vendor generating keys as part of an operating system (OS) image instead of regenerating them when the OS first boots or is provisioned for the customer. In the case of publicly available VM images or hardware, malicious actors could collect the key pairs from the images and use them in attacks. The real world impact would be that malicious actors with certain network access could perform spoofing or meddler-in-the-middle attacks to force users or automation to interact with them instead of the intended targets.
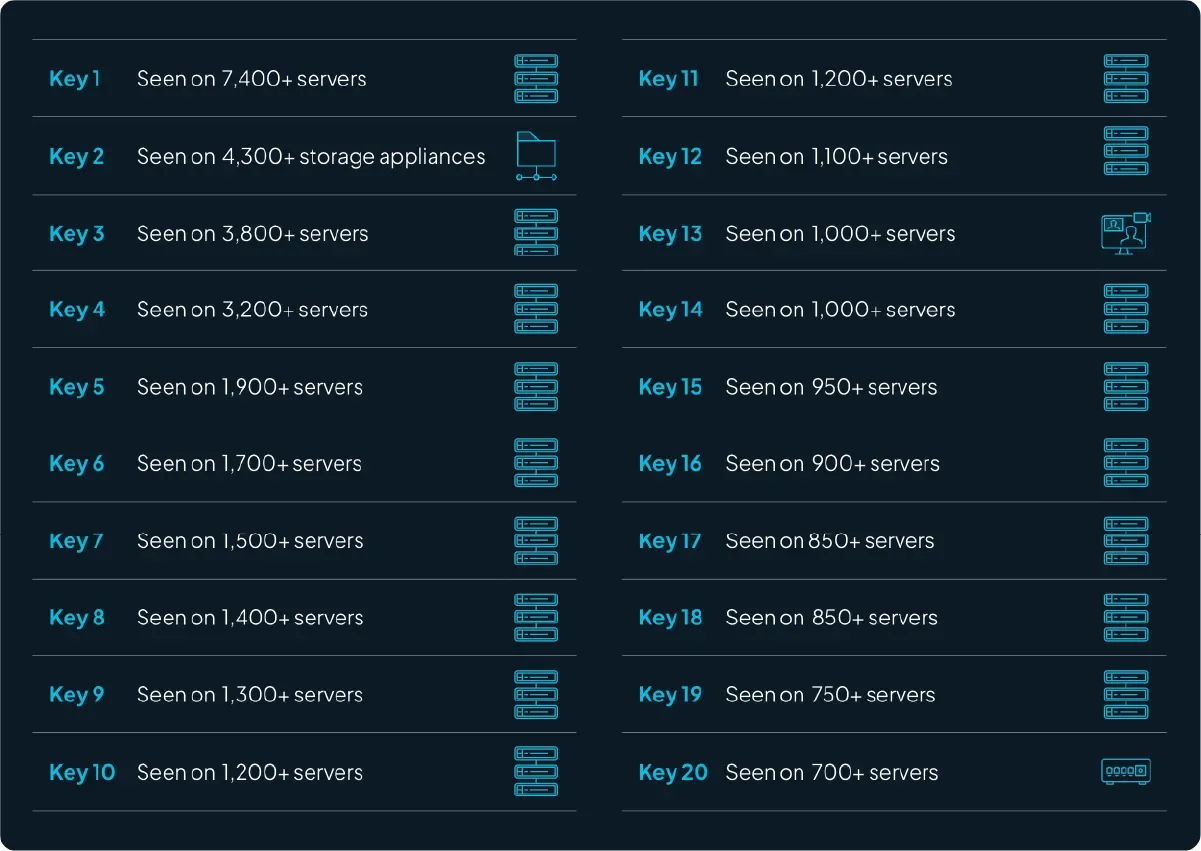
FIGURE 3 – Reuse of individual keys across our data set by device type.

Auditing SSH key reuse

runZero scans attempt to collect information for all SSH key types. This allows our customers to audit the keys types in use as well as how the specific keys are used across their environments.
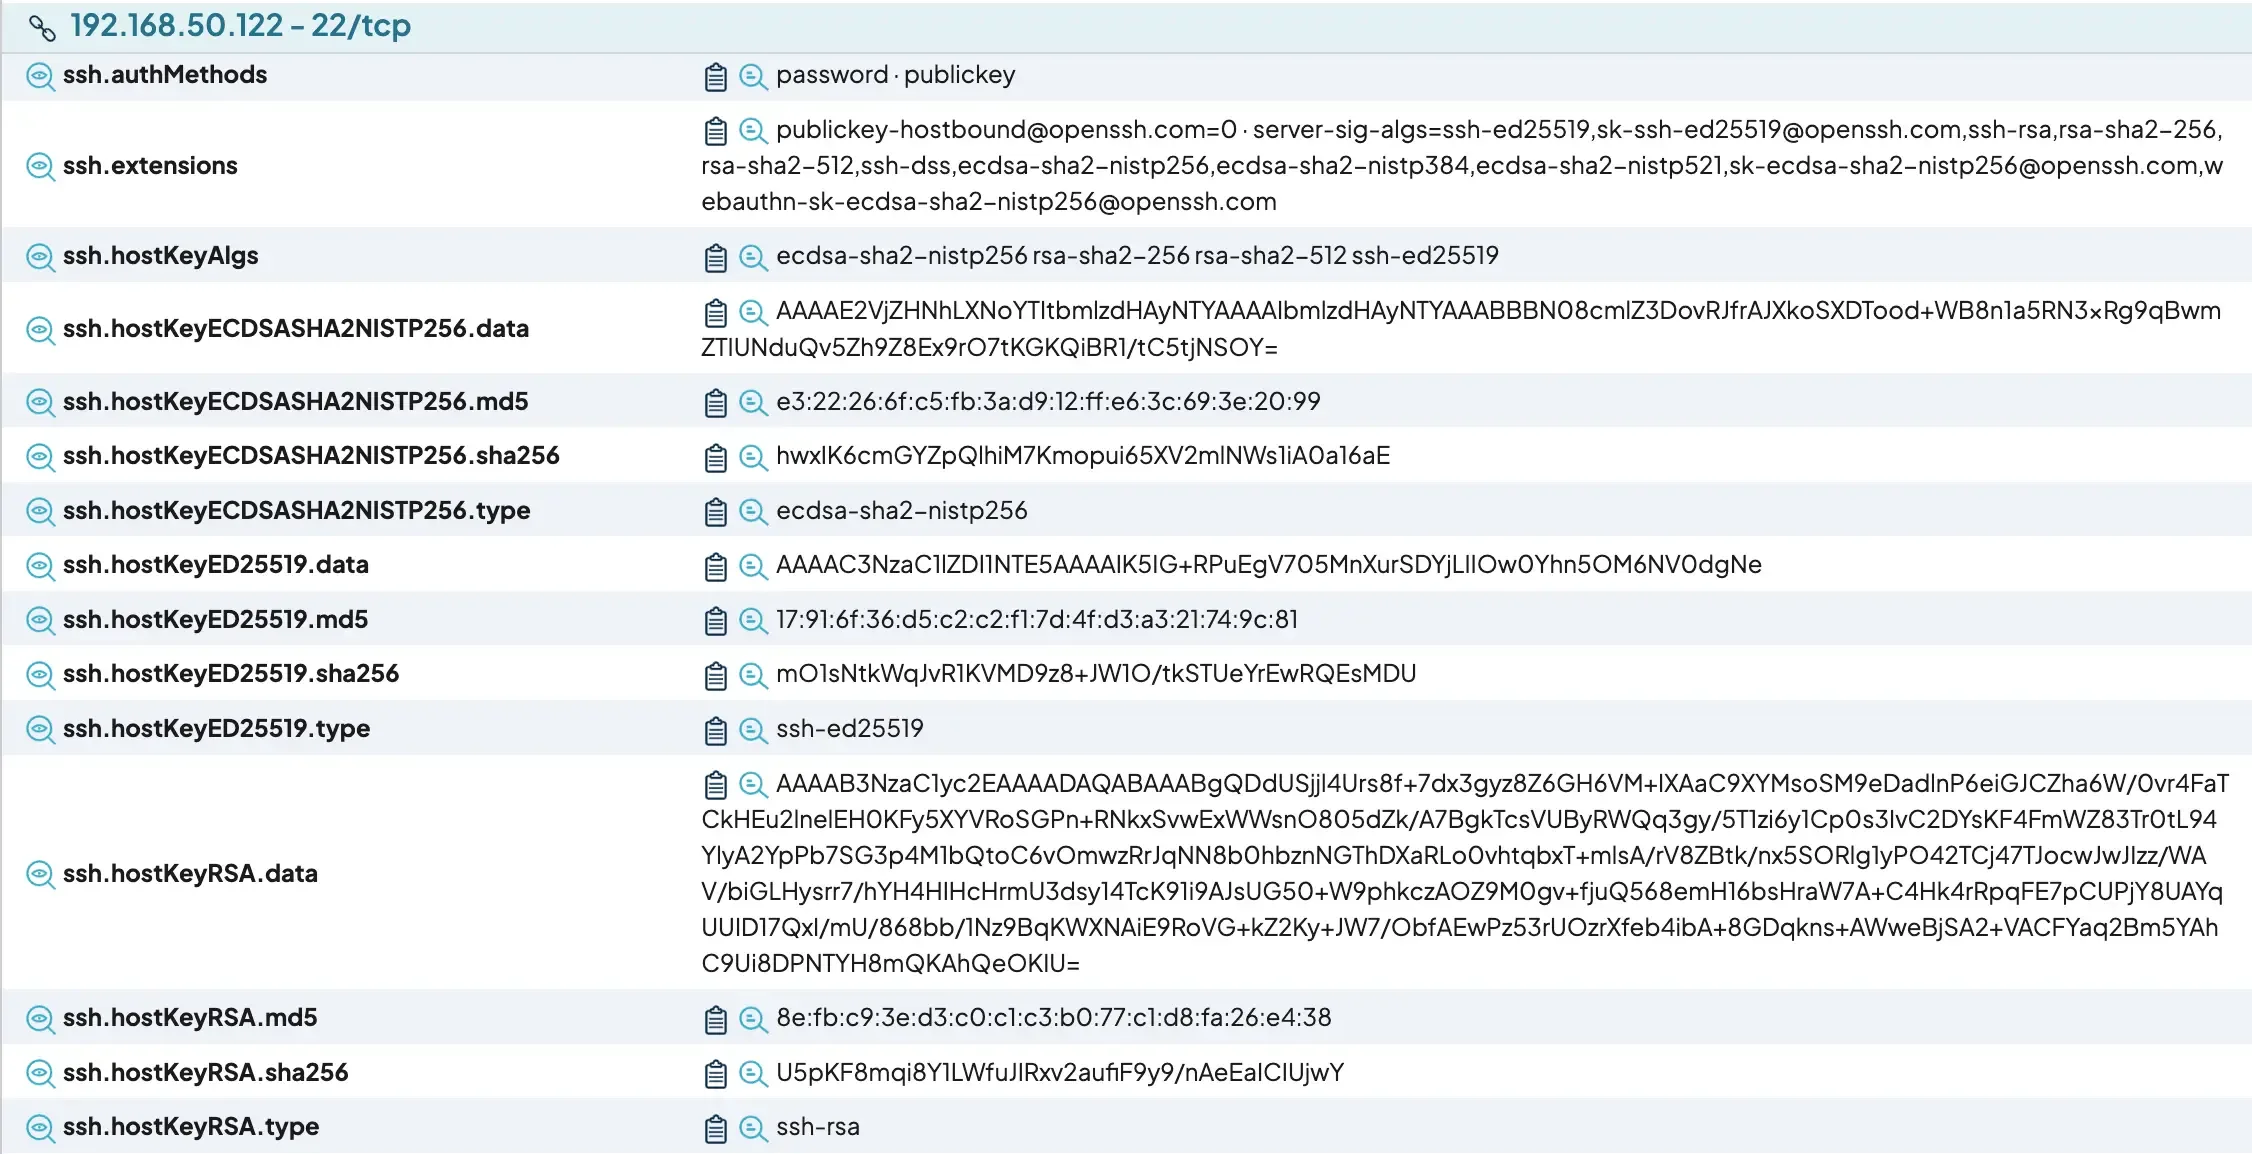
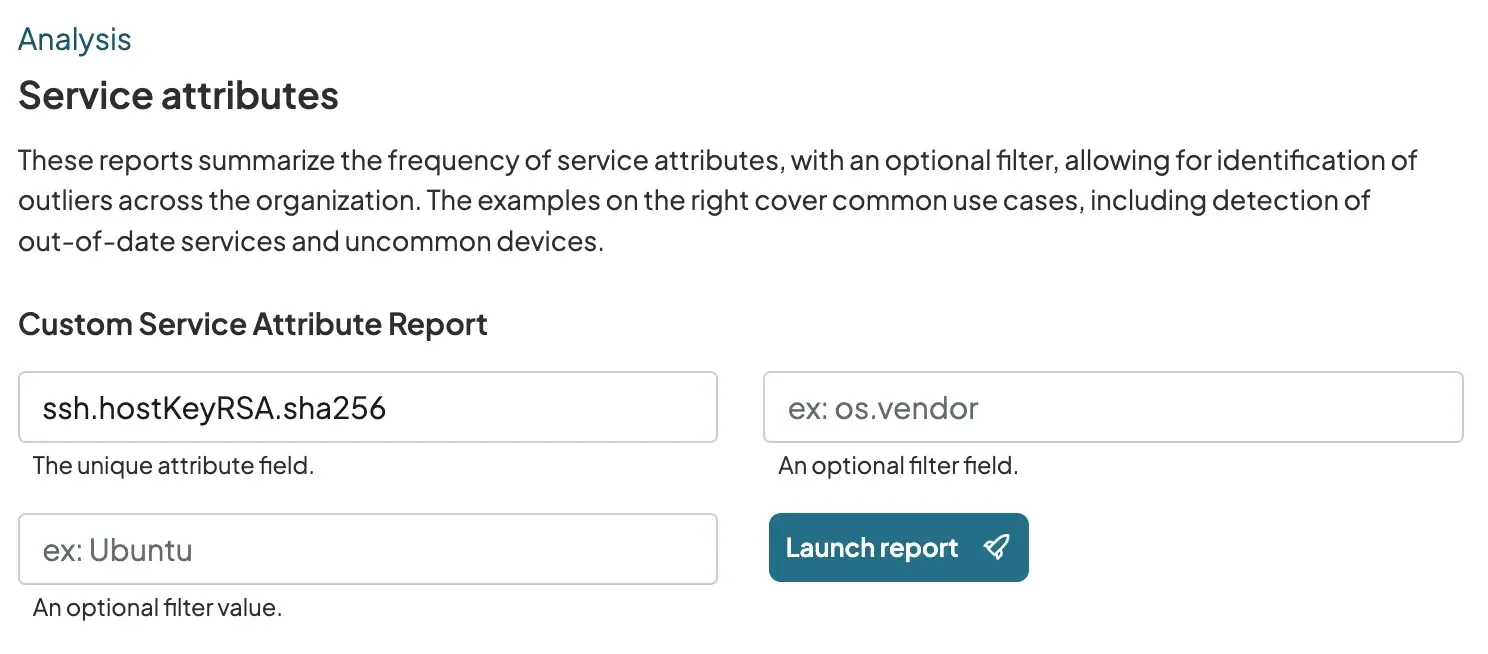
FIGURE 4 – A partial screenshot of runZero showing the SSH key information collected. runZero has a Service attributes report that can help our customers audit key reuse. There are two ways to access this report. The first way is to go to the Reports section and run the Service attributes report for a specific key field. We recommend using the sha256 hash for the key type. For example, in the case of RSA keys the service attribute ssh.hostKeyRSA.sha256.
FIGURE 5 – A partial screenshot of runZero showing how to launch the Service attributes report.

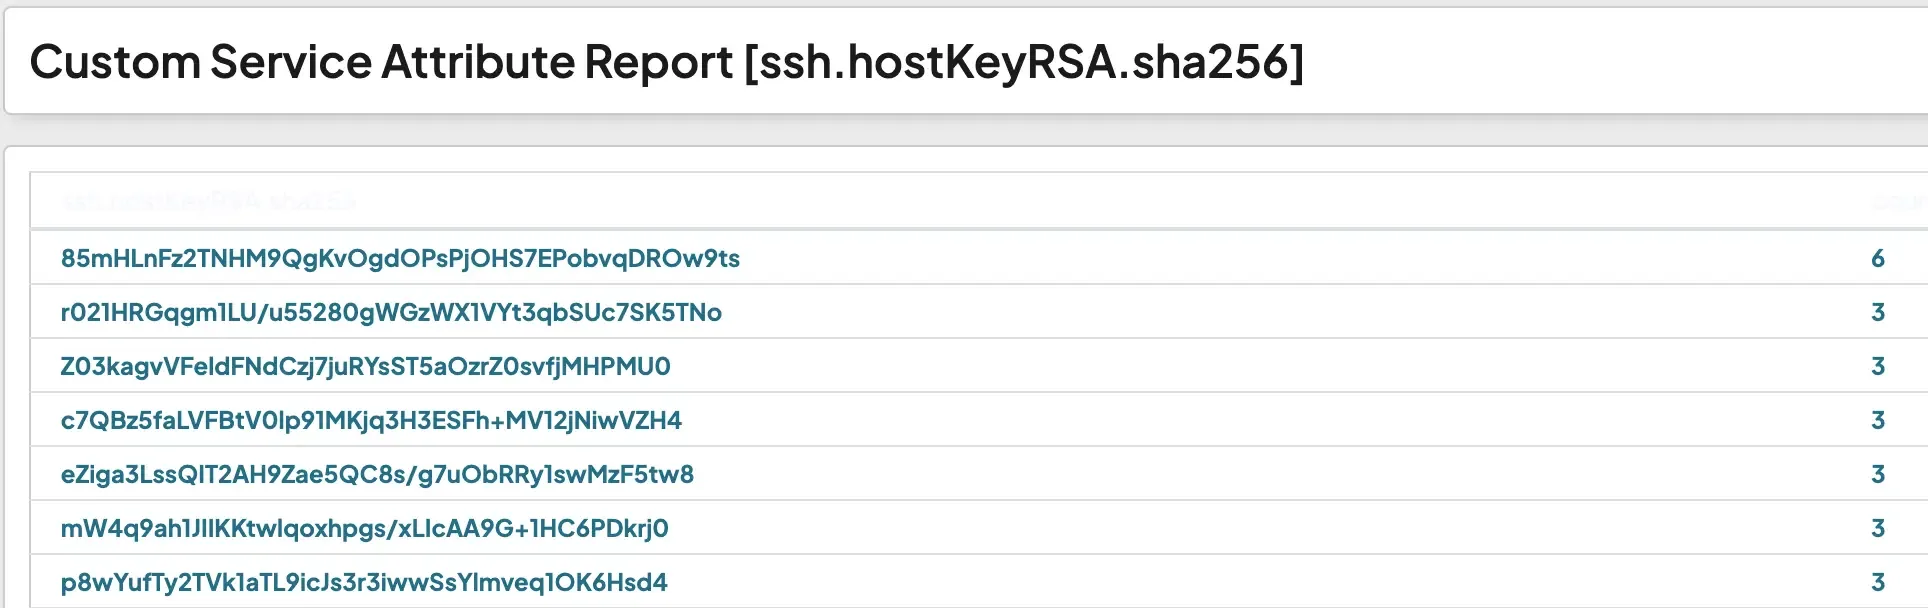
FIGURE 6 – A partial screenshot of runZero showing the output of the Service attribute report for ssh.hostKeyRSA.sha256.

Customers can then click on the key hash on the left to see where it is used. This is a Service report so it is important to keep in mind that the same key may be seen across multiple services or addresses on the same asset.

The second way to view the report is by viewing the SSH service on an asset and clicking the magnifying glass next to the attribute name (green square in Figure 7). This will take customers directly to the report.

FIGURE 7 – A partial screenshot of runZero showing the attribute name and value. Clicking on the magnifying glass next to the value (blue square in Figure 7) will show every place that this particular key is used.

Remember to download the runZero Research Report to learn more about the state of asset security.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About runZero
runZero, a network discovery and asset inventory solution, was founded in 2018 by HD Moore, the creator of Metasploit. HD envisioned a modern active discovery solution that could find and identify everything on a network–without credentials. As a security researcher and penetration tester, he often employed benign ways to get information leaks and piece them together to build device profiles. Eventually, this work led him to leverage applied research and the discovery techniques developed for security and penetration testing to create runZero.

The Emergence of the Zero Trust Program Manager: A New Role in Cybersecurity

Cybersecurity roles and responsibilities are in a constant state of flux. Just as the defenders adapt, so do the adversaries. Enter the latest evolution in the cybersecurity workforce: the Zero Trust Program Manager. If you’ve been in the cybersecurity field for more than a hot minute, you’re likely aware that “Zero Trust” has become a buzzword so pervasive that it’s now almost as ubiquitous as the phrase “we take your security seriously” in every corporate breach apology letter. But unlike the latter, Zero Trust is more than just lip service. It’s a paradigm shift in how we think about securing our digital environments. And it’s precisely this shift that has given rise to the need for a dedicated role to manage it.

What Exactly is a Zero Trust Program Manager?

At its core, the Zero Trust Program Manager (ZTPM) is the strategic leader responsible for implementing and overseeing an organization’s Zero Trust architecture. This role isn’t just about managing technology; it’s about orchestrating a cultural shift in how an organization approaches security. The ZTPM is tasked with ensuring that no entity—be it user, device, or application—is inherently trusted, whether inside or outside the organization’s perimeter. Instead, everything and everyone must be continuously authenticated and authorized.

This role is a blend of project management, cybersecurity expertise, and change management. The ZTPM must work closely with various stakeholders across the organization, from IT and security teams to business leaders, to ensure that the principles of Zero Trust are understood, embraced, and effectively implemented. They are the evangelist, the educator, and the enforcer of this new security mindset.

Why Does This Role Exist Today?

The rise of the ZTPM is not just a random blip on the cybersecurity radar; it’s a direct response to the changing threat landscape and the realization that traditional perimeter-based security models are no longer sufficient. The days when securing the castle walls could keep the bad guys out are long gone—primarily because the castle doesn’t even have walls anymore. Today, organizations operate in a borderless environment where users and data move fluidly across cloud services, mobile devices, and remote locations. The traditional model of “trust but verify” has been replaced with “never trust, always verify.”

Moreover, the acceleration of digital transformation, spurred on by global events like the COVID-19 pandemic, has further blurred the lines between internal and external networks. As organizations rapidly adopted remote work models and cloud services, the attack surface expanded exponentially. In this new reality, the concept of a trusted internal network is not just outdated; it’s downright dangerous.

Enter Zero Trust—a model that doesn’t assume that anything or anyone is trustworthy just because they’re inside the network. Every request, every access attempt, every interaction is scrutinized. This approach requires a fundamental shift in how security policies are designed, enforced, and managed. And that’s where the ZTPM comes in. Their role is to steer this transformation, ensuring that Zero Trust principles are not just a checkbox on a compliance form, but a living, breathing part of the organization’s security fabric.

Scope of Responsibilities

The responsibilities of a Zero Trust Program Manager are as wide-ranging as they are critical. Here’s a closer look at what this role entails:

  1. Strategy Development and Implementation: The ZTPM is responsible for developing a comprehensive Zero Trust strategy that aligns with the organization’s business objectives. This includes defining the scope, setting milestones, and ensuring that all security policies and technologies are aligned with Zero Trust principles.
  2. Cross-Functional Collaboration: Implementing Zero Trust is not a one-department job. The ZTPM must work closely with IT, security, compliance, and business units to ensure that the Zero Trust framework is understood and adopted across the organization. This includes leading workshops, training sessions, and regular check-ins to ensure alignment.
  3. Technology Oversight: While the ZTPM isn’t necessarily the person configuring firewalls or deploying MFA solutions, they are responsible for overseeing the technology stack that supports the Zero Trust model. This includes evaluating and selecting the right tools, ensuring they are properly integrated, and monitoring their effectiveness.
  4. Change Management: Moving to a Zero Trust model is as much about changing mindsets as it is about changing technology. The ZTPM must manage the human side of this transformation, addressing resistance, ensuring proper training, and fostering a culture that supports continuous verification.
  5. Risk Management and Compliance: The ZTPM plays a crucial role in identifying and mitigating risks associated with the transition to Zero Trust. They must ensure that the organization remains compliant with relevant regulations and industry standards while adopting this new security model.
  6. Continuous Improvement: Zero Trust is not a set-it-and-forget-it approach. The ZTPM is responsible for continuously assessing the effectiveness of the Zero Trust framework, making adjustments as needed, and staying ahead of emerging threats.

Qualifications and Skills

Given the breadth of responsibilities, the ideal ZTPM is a cybersecurity Renaissance person—a Jack or Jill of many trades, with a deep understanding of security principles and a knack for project management. Key qualifications might include:

  • Experience: A strong background in cybersecurity, with experience in implementing security frameworks and leading cross-functional teams.
  • Certifications: Relevant certifications such as CISSP, CISM, or specific Zero Trust certifications can be a strong indicator of expertise.
  • Communication Skills: The ability to articulate complex security concepts to non-technical stakeholders is crucial.
  • Leadership: Proven leadership skills, particularly in driving organizational change, are essential.
  • Strategic Thinking: The ZTPM must be able to see the big picture, aligning security initiatives with broader business goals.

Zero Trust, the ZTPM & Network Access Control (NAC)

One of the critical areas where the Zero Trust Program Manager (ZTPM) must exert influence is in the realm of Network Access Control (NAC). NAC plays a pivotal role in the enforcement of Zero Trust principles, acting as one of the frontline defenses against unauthorized access. In the context of Zero Trust, NAC is not merely a gatekeeper that decides who gets in; it is a dynamic system that continuously assesses and verifies the trustworthiness of every device and user attempting to access the network.

The ZTPM must work closely with network administrators and security teams to ensure that NAC solutions are tightly integrated into the broader Zero Trust architecture. This involves configuring NAC policies to align with the Zero Trust mantra of “never trust, always verify.” For example, NAC policies may need to be updated to enforce strict access controls based on user roles, device health, and contextual factors such as the location and behavior of the device. The ZTPM oversees this integration, ensuring that the NAC system not only blocks unauthorized devices but also actively participates in the continuous monitoring and assessment of devices already within the network.

Furthermore, the ZTPM must consider how NAC fits into the overall user experience. While security is paramount, the role requires balancing stringent access controls with the need for operational efficiency. Implementing NAC in a Zero Trust environment is not just about adding layers of security; it’s about creating an adaptive, intelligent system that can respond to threats in real-time without unnecessarily hindering legitimate business activities. This means the ZTPM must ensure that NAC is fine-tuned to minimize disruptions while still providing robust protection, making it an essential tool in the Zero Trust toolkit.

By effectively managing NAC within a Zero Trust framework, the ZTPM helps to create a more resilient and responsive security posture, one where access is always under scrutiny and never taken for granted.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

Feel The Flow With Autofill

Why is Autofill so cool?

Nothing is more annoying than manually typing out online forms. Usually, when you sign up for an online service, you need to type out your username, password, personal information, and sometimes even your credit card details. If the website takes security seriously, it may also ask you to prove your identity with additional authentication methods. This is especially true when it comes to online shopping.

So, say you reach the final steps of purchase and you’re already pretty annoyed. Fortunately, Autofill effectively deals with the nuisance of filling out online forms, making it a smooth and seamless experience.

Powered by machine learning, Autofill constantly evolves and adapts, accurately identifying and filling fields in various forms, including sign-ups, logins, credit card details, and personal information. This ensures Autofill remains highly reliable, aiming to deliver perfect accuracy over time.

Pro tips: How to make the most of Autofill

Log in with a single click

Thanks to the Instant Login feature on desktop, NordPass allows you to skip all the annoying steps required to log in to a chosen website: landing on the page, selecting credentials, and performing on-page actions. Now, a single click is all it takes. All you have to do is follow a prompt to log in with NordPass.

If you choose not to log in using the Autofill feature, you’ll be asked if you want to enable it for future access to the website. Choose yes to ensure an effortless login experience. Alternatively, you can leave it disabled or even turn Instant Login off altogether in the NordPass settings section.

If you have multiple accounts on the website, select the account you want to use first. In such a case — let’s be honest — logging in with Instant login takes two clicks.

how to login with nordpass pop up screen

Autofill all credit card details and personal information

Some websites require additional information to authenticate the user or confirm transactions. You may know the case from Amazon asking for an ID to verify your address or an online shop requiring a billing address or security questions regarding your company credit card. We salute every solution that enhances your online security, but looking for and writing down all these additional details can be quite annoying.

Luckily, the Custom Field feature — previously available with password items — is now expanded to credit cards, personal information, and secure notes on desktop and Android devices. NordPass will autofill the data from custom fields added to your items. This way, you won’t have to look for your ID or credit card (if you even have it in a physical form, which is not always the case with business cards) whenever you want to buy something. Handy, right?

how to add custom fields Nordpass dashboard view

Bundle your websites or apps

Having separate password entries for apps from the same company, like Facebook and Messenger, even if you use the same credentials for all, can clutter your NordPass vault. It also takes extra time and effort to manage, especially with multi-domain websites like Microsoft that are frequently used at work.

At NordPass, we focus on the simplicity of use. That’s why we let you combine website addresses on your desktop, or app names on your mobile device, into a single password entry. This feature improves domain matching, making it easier to access your accounts across related domains. For example, NordPass can recognize microsoft.com and live.com as related, so you can access both without duplicating passwords. Instead of searching for each site individually, you’ll find the login details for login.live.com under “Microsoft,” and autofill will take care of the rest.

This feature, available on desktop and Android devices, helps simplify credential management. If you have multiple entries for related accounts with the same password item, you can merge them into one and delete the extras. Just be sure to manually remove the unnecessary entries.

how to add asset with multiple urls nordpass dashboard view

Experience undisturbed flow

The best-in-class user experience takes constant improvements. Take a look at how Autofill makes accessing online accounts easier and quicker.

  • Subdomain matching

The Subdomain Matching feature — available on desktop and Android devices — will prove invaluable if you use multiple subdomains at work (like department-specific sections of a company website). It’s designed to identify and autofill correct login information for each subdomain, ensuring a seamless access experience by removing the hassle of having to select from multiple login options every single time. You can enable or disable Subdomain Matching in the NordPass settings section according to your needs.

how to autofill via subdomain nordpass dashboard view
  • Customizable autofill

You can adjust the autofill settings at any time by clicking the three dots in the autofill drop-down list. This allows you to choose a different item to autofill, search for the right one, or change how NordPass interacts with specific fields. Plus, you can use this feature to give direct feedback to the NordPass team.

customizable autofill feature in Nordpass dashboard view
  • Disable autofill

To disable autofill on specific pages or fields, just right-click the input field and choose “Don’t autofill on this website” or “Don’t autofill this field.” This way, you can control when autofill is used, keeping your workflow smooth and uninterrupted.

how to manage autofill Nordpass dashboard view

What else to expect?

The Autofill may have already suggested using Email Masking or a Password Generator tool during the login process. Please note, that you can take advantage of both without leaving the page; NordPass will automatically save your new strong passwords as well as email masks.

email massking input field Nordpass dashboard view

On Desktop, we’ve introduced prompts to inform you in case you enter an unprotected website or log in with weak or reused passwords. The prompts can also warn you about breached websites to help you secure your accounts and resolve the breach on NordPass. However, if you don’t want to get these, you can now turn them off permanently in the “Notifications” settings section.

data breach scanner and password heath checker features

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Feature Round-up: July and August 2024

Exciting updates have arrived from July and August 2024! 

We’ve introduced a range of new features and enhancements designed to take your Scalefusion experience to the next level. Discover how streamlined Apple device management, advanced OneIdP SSO configurations, and innovative solutions for Windows and Android devices can make your device management more efficient and intuitive.

Explore the latest updates and see how they can transform your operations!

Scalefusion Feature Updates

1. OneIdP SSO Configuration for Linux

Now leverage Single Sign-On (SSO) for Linux devices. Set up conditional access for users accessing SAML-based web apps from unmanaged Linux devices, ensuring they enroll to continue access.

2. New Updates to Apple Device Management

  • Pre-Stage Setup for Account Creation for macOS: Configure account creation during the ADE/DEP enrollment process, making the initial device setup smoother and more intuitive for end-users. You can customize the primary account settings using custom properties or create an admin account during enrollment.
  • System Logs for macOS: Collect the Device Console logs of your managed devices right from the Scalefusion dashboard.  Collect complete logs or define specific filters and predicates, adding multiple search properties.
  • Updates to Password Policy: Set a specific duration after which a disabled account can log back into macOS devices using the “Reset Time After Max Failed Attempts” option. Additionally, you can now configure a 45-day password expiry period for both iOS and macOS devices.
  • Profile changes: Easily find the deprecated settings under the macOS device profile section and configure essential and available policies with our UI enhancements. Prevent accidental data sync issues with the default enable of iCloud settings for new profiles.

3. What’s New on Scalefusion Dashboard

  • Policy & Actions Report: You can now receive a report whenever a policy change is pushed or an action is performed, detailing whether or not the action was executed.  You can access the summary of the last 5 events per device and the complete Policy and Action Report in the device details section.
  • Multi-Group Selection in DeepDive: Select multiple groups in DeepDive and view a combined report encompassing all selected groups.
  • Policy and Profiles as PDF: Obtain the details of policies and actions performed on any device. Download the applied profile and policy settings as a PDF. This option can be accessed via the Print button in the list of profile actions. You can also download Android BYO and Apple AUE profiles as PDFs.
  • Auto-Renewal for Subscriptions: Managing subscriptions just got easier with our new Auto-Renewal feature! Set subscriptions to auto-renew at the time of purchase or renewal and disable it anytime. You can also associate and update credit cards for auto-renewal as needed
  • Admins and Roles: Streamline company information and configure and update the billing address, Point of Contact, key contacts for billing, and email notifications from Scalefusion as well as the Apple Bussiness Manager Email Notification settings. Control these settings via RBAC and customize access for custom roles.

4. Updates to Windows Device Management

  • Compliment your modern management with Scalefusion for Windows: Enroll Windows devices managed using any other modern management tool on Scalefusion and leverage Scalefusion’s advanced features such as Remote Control, Kiosk Mode, Script Execution, and MSI installation for Windows without migrating from your existing solution.
  • Custom Properties in Windows Add Application: Use custom properties when adding application details in Windows profiles. You can configure applications based on device-specific paths, ensuring that each device gets the correct application setup.

5. Updates to Scalefusion OneIdP

  • Integrate Reddiffmail for work with Scalefusion OneIdP:  Import users from the Rediffmail service to the OneIdP directory, create SSO configuration, enable conditional access, and authenticate and authorize users with their Rediffmail IDs on work apps.
  • Make way for Exceptions: Define exceptions for conditional access, right from enrollment exceptions to user exceptions and exceptions for Linux devices. Enforce administrators accessing the Scalefusion dashboard to enroll their respective devices into Scalefusion.
  • User Account Activation: Track user account activations when users reset their passwords via invitation emails or enroll devices. The updated Directory page now displays the activation status,  no of users that have activated accounts, and the pending accounts. Send reminders to pending users directly from this page, facilitating a smoother transition to SSO powered by OneIdP.

6. What’s New for Android Device Management

  • SCEP CA Server Integration for Android: Automate certificate deployment on Android devices by integrating a SCEP-based CA server. SCEP is a simple certificate enrollment protocol that helps generate certificates from a template.
  • Addition of New Device Properties: Access additional device properties with $device. Obtain more detailed device information and improve asset management.
  • OEM Config Duplicity Issue in Android Profiles: Prevent issues with duplicating OEM configurations when cloning Android profiles. The OEM Configs are no longer cloned when profiles are duplicated.
  • Customizable screen for kiosk devices: Explore an all-new customizable Scalefusion Kiosk/launcher screen. Add multiple pages, and position icons at exact locations on the device screen or group the apps and browser shortcuts into folders.
  • New Workflows: Leverage network compliance workflow to define network-based device access rules based on IP Address, Wi-Fi SSID, or metered networks. With the enhancements to battery compliance workflow, automate actions to reduce battery consumption:
  • Updates to password policy: Reduce password reset requests with password self-service. Allow end-users to reset their device password/PIN locally on the device if they forget the password/PIN.
  • New Report for Pitstop: Download the Distance Traveled Summary, a comprehensive day-wise breakdown of distances traveled for all devices. The Distance Traveled Summary report can also be scheduled for regular updates.
  • Version Update Utility for PfW Apps: Keep your PfW apps up-to-date with our new Version Update Utility.
  • Scalefusion Android MDM Agent: Try the updated Scalefusion Android MDM agent using the most recent SDK version following Google’s guidelines. Manage accounts that can be added to the Gmail app with a new remote command. Prevent users from adding personal accounts using Gmail in both CO and BYO modes.

Closing Lines

These updates showcase our dedication to enhancing your Scalefusion experience with the latest features and improvements. From advanced SSO configurations and streamlined Apple device management to innovative solutions for Windows and Android, we’re committed to making your device management more efficient and intuitive. We’re eager to hear your thoughts on these new features and how they’re impacting your operations.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Scalefusion
Scalefusion’s company DNA is built on the foundation of providing world-class customer service and making endpoint management simple and effortless for businesses globally. We prioritize the needs and feedback of our customers, making sure that they are at the forefront of all decision-making processes. We are dedicated to providing comprehensive customer support services, and place emphasis on customer-centric thinking throughout the organization.

Ensuring Node Resilience: SafeDNS’s Commitment to 100% Uptime

Reliability and uptime are the most critical aspects of DNS resolution. At SafeDNS, we are proud to be the most sustainable DNS resolver worldwide—providing unmatched reliability and making sure that all of our nodes are operational with 100% uptime. Overviews of how this level of resilience and security is achieved are shown below. 

Understanding Node Reliability and Uptime
Node reliability simply means that any DNS resolver should be up and available all the time. This becomes a highly relevant metric since most businesses and organizations require continuous, uninterrupted services. Uptime means the fraction of the time a node has spent being up versus its total time in operation. Our guarantee of 100% uptime means our nodes are always on and never off.

Managing Node Attacks: Ensuring Service Continuity and Stability
If a node comes under attack, several mechanisms are put into place to protect and maintain service continuity. The system detects abnormal traffic patterns and automatically initiates defense protocols, such as blocking spammers entirely. Common types of attacks include Distributed Denial of Service (DDoS) attacks, which flood the node with excessive traffic, and Denial of Service (DoS) attacks, which target vulnerabilities to overwhelm resources.

Our Commitment to 100% Uptime
At SafeDNS, we ensure that our nodes are up and running 100% of the time. This commitment involves rigorous measures and continuous monitoring to maintain the highest levels of operational efficiency. Our approach to achieving 100% uptime includes:

Rigorous Security Protocols: To maintain high uptime, we implement multi-layered security measures to protect our nodes and ensure uninterrupted service. This includes:

  • Closed Ports: By securely closing all unnecessary ports, we minimize vulnerabilities and prevent unauthorized access, directly contributing to system stability and uptime.
  • IP Address Monitoring: We constantly monitor for any unfamiliar IP addresses attempting to access our systems. Early detection and response help maintain operational continuity.
  • Secure Passwords and Authentication: Our use of strong, secret keys and advanced authentication methods prevents unauthorized access, ensuring that our systems remain secure and reliable, contributing to consistent uptime.

Ensuring Continuous Operation: Our dedication to 100% uptime means that we maintain continuous operation, even in the face of unforeseen circumstances. We utilize advanced technologies and best practices to ensure uninterrupted service, including:

  • Regular System Checks: We conduct frequent system checks and updates to keep our infrastructure secure and fully operational.
  • Robust Failover Systems: In the event of a failure, our failover systems seamlessly take over, ensuring there is no interruption to our services.
  • Proactive Monitoring: Our team of experts continuously monitors our nodes for potential issues, addressing them before they impact our uptime.

Tier IV Security Standards: Our infrastructure is implemented according to factory model classification of Tier IV, providing the highest possible availability and security.

Uninterrupted Service with Anycast: With the implementation of Anycast technology, we ensure flawless service continuity and 100% uptime. Our nodes operate around the clock, providing uninterrupted service and maintaining seamless performance at all times.


In addition, To elevate the quality and resilience of our service, we’ve recently transitioned to NetActuate, renowned for their exceptional network and infrastructure solutions. NetActuate offers a dynamic, ultra-low-latency, and highly available network that covers every major global market. Their cutting-edge services maximize performance and reliability, allowing us to uphold our unwavering commitment to delivering top-notch service with unparalleled excellence.

In the field of DNS, it’s essential to keep things reliable and ensure that services are always up and running. At SafeDNS, we’re all about being the most dependable DNS resolver out there, with a promise of 100% uptime and unbeatable resilience. Through meticulous implementation of security protocols, adherence to Tier IV standards, and seamless integration of Anycast technology, we ensure that our nodes remain operational and responsive at all times.

About SafeDNS
SafeDNS breathes to make the internet safer for people all over the world with solutions ranging from AI & ML-powered web filtering, cybersecurity to threat intelligence. Moreover, we strive to create the next generation of safer and more affordable web filtering products. Endlessly working to improve our users’ online protection, SafeDNS has also launched an innovative system powered by continuous machine learning and user behavior analytics to detect botnets and malicious websites.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.