Skip to content

Optimizing your business IT processes

In today’s fast-paced business environment, information technology shapes the way companies operate, compete, and grow. The pace of technological advancements adoption can play a deciding role in a company’s success or failure. However, how this can be achieved within an organization may not always be clear.

For this reason, we’ve invited co-founder and CPO at Kubernetes automation, optimization, security, and cost management platform CAST AI, Laurent Gil. Additionally, our Head of Platform Engineering at NordLayer, Carlos Salas, for his take on improving the current organization’s IT infrastructure.

Let’s take a deep dive into your current IT infrastructure assessment, automation areas identification, the right automation tools selection, its implementation, and the best practices.

Assessing your current IT infrastructure

Laurent Gil shared his valuable insights on how businesses can optimize their IT infrastructure to drive efficiency and productivity. According to him, one crucial step in this process is conducting a comprehensive assessment of your current infrastructure.

“A successful IT optimization strategy always starts with a gaining clarity around the current state of the infrastructure. A thorough assessment helps to identify issues and bottlenecks that are good candidates for automation – and where automation will make the biggest impact. Quick wins are just as important as long-term strategy and keeping your eye on the bigger picture, considering your company’s specific needs and direction.”

Click to tweet

Here’s how your current IT infrastructure could be evaluated in 8 steps:

  1. Define assessment objectives. Assessment objectives can be diverse, and they should focus on particular areas that could use improvements. For some businesses, it may be ironing out security vulnerabilities, while for others, it may be performance improvements. 

  2. Gather information. Regardless of assessment objectives, the next step will always be data collection. This will form a solid foundation for the evaluation process providing useful insights in later steps.

  3. Evaluate your used hardware and software. All used servers, storage devices, routers, switches, as well as operating systems, databases, applications, and security software should be reviewed. Check for potential bottlenecks and clunky setups that are slowing down your operations. 

  4. Perform network checks. Analyze your network topology, bandwidth, and latency. Evaluate your network security measures, such as firewalls, intrusion detection, and prevention systems.

  5. Look into data backups and disaster recovery. Verify that your data backup and recovery plans are up-to-date, reliable, and effective. Test your disaster recovery procedures to ensure that they meet your recovery time objectives.

  6. Analyze your security setup. Assess your security policies and procedures, including access controls, authentication, and authorization. Test your security controls to identify weaknesses or gaps.

  7. Consider the IT budget. Evaluate your IT budget and spending to identify areas for improvement or cost savings. Identify potential areas where technology investments can drive business value and growth.

  8. Document your findings. Document your findings and recommendations in a detailed report. This will serve as a reference document providing actionable recommendations for improving your IT infrastructure.

Identifying areas for automation

Findings from the IT infrastructure assessment should help you identify areas that could benefit the most from automation. As different companies have different IT struggles, going through this process should be a highly individualized approach. That said, here are some common areas that could be easily automated.

Data entry and data processing. Routine maintenance tasks like data entry, migration, and validation can be easily automated using macros, scripts, and other robotic processes.

Network and system administration. Tasks like server monitoring, backup, and patch management can be time-consuming and repetitive. Automations enable the creation of templates to perform the tasks identically, leaving less room for human error. In addition, this frees the staff from manual processes allowing them to focus on strategic activities.

Software deployment. Every software deployment instance involves a lot of repetitive tasks to ensure that it’s deployed correctly and without errors. Automating them can help reduce the time and effort required for deployment and improve the reliability of the process.

Customer support. Simple customer support tasks like answering frequently asked questions, providing account information, and processing routine requests can be solved without human involvement. Leveraging chatbots and virtual assistants can combine convenience and efficiency for businesses and their customers.

Choosing automation tools

When it comes to selecting automation tools, Laurent Gil highlights the significance of putting business needs at the forefront.

“I’ve seen the benefits automation can bring to organizations of all sizes firsthand. However, not all automation tools are created equal, and choosing the right one for your business can be a daunting task.

What you need to consider are first and foremost your specific business requirements. Understanding business needs and matching them to the right automation offering ensures that what you invest in represents the best fit for your company.”

Click to tweet

Here’s a brief overview of the approach that businesses can take when selecting automation tools:

Research what’s available on the market 

Clear business objectives and defined areas for improvement will allow you to fill in the gaps with automation tools. This can involve various routes like reviewing industry publications or consulting with vendors directly.

Evaluate select tool features 

Once a list of potential features has been compiled, it’s important to evaluate its features. Depending on needed functionalities, this can involve scalability, customizability or other ease of use adjustments.

Consider integrations

Industry expert and Head of Platform Engineering Carlos Salas highlighted the importance of considering the bigger picture when selecting automation tools, highlighting their interoperability.

“Whatever automation tools you select won’t exist in a vacuum, so thinking about potential integrations with existing systems and processes isn’t a bad idea.”

“Data security is paramount. Before implementing any automation tool, it’s imperative to thoroughly evaluate its capabilities in protecting sensitive information and adhering to established security protocols.”

Click to tweet

This paves the way for seamless automation implementation without hiccups and ensures optimal performance down the line.

Test and trial 

Before making a final decision, businesses should take chosen automation tools for a test drive. Various methods like setting up a proof of concept or pilot project to evaluate the effectiveness of the tool in real-world scenarios will help to realistically evaluate its usefulness.

Implementing automation

Implementing business IT automation can be a complex task that requires careful planning and execution. Here are some general steps that you can follow to implement business IT automation.

  1. Design the automation process. Start by creating a plan for automation, including a timeline and a list of tasks to be automated. It also helps to break the process into smaller tasks and identify the rules and conditions that must be followed.

  2. Deploy the automation. The exact route of automation deployment will depend on whether it’s an in-house built tool or a third-party provider was chosen. Still, it’s best to test in a production environment initially and, after testing, move on to full-scale implementation.

  3. Train employees. Expect that your workforce will only know how to use it after a while. Expect that there will be a transitionary period during which various training will help staff to familiarize themselves with the tool better.

  4. Evaluate the results. After the automation has been implemented and employees get used to it, it’s worth checking its impact on productivity, efficiency, and accuracy. This information can be highly useful when identifying shortcomings in your current setup as well as planning and identifying new areas for automation.

Best practices for automating IT

To maximize your chances that your automation process goes smoothly, it can be good advice to follow the best industry practices. These include:

Focusing on standardization 

Standardization is critical when it comes to automating IT processes. It also makes it easier to automate routine tasks, reduces the chances of errors, and helps ensure consistency across your IT infrastructure.

Make use of automation platforms

Laurent Gil quote

According to Laurent Gil, automation platforms have the power to enhance business efficiency and streamline operations.

“Automation platforms enable businesses to accelerate and streamline their workflows and processes. Gone are the days of tedious manual tasks and complex coding requirements. With intuitive dashboards and user-friendly interfaces, these platforms empower users to design, create, and implement automation workflows without the need for in-depth technical expertise. And that’s a very good thing.”

Click to tweet

Gil’s words highlight the significant shift brought about by automation platforms in the business landscape. With these powerful tools at their disposal, organizations of all sizes can leverage automation to optimize their workflows, freeing up valuable time and resources for more strategic endeavors.

Adopt a DevOps approach 

Adopting a DevOps approach to automation can help streamline the IT development and deployment processes. Integrating development and operations teams allows the entire software development lifecycle to be automated. This can help you deliver software faster and with fewer errors.

Involving stakeholders 

Stakeholders are the personnel that the automation process will directly impact. Therefore, their input can help to identify potential pain points in advance. This can lead to more effective automation that addresses real problems and is designed to meet the organization’s specific needs.

Bottom line

Optimizing your business IT requires a systematic approach based on evaluating your current setup. The thorough analysis of the current businesses’ IT environment allows them to identify potential automation areas.

The process is finalized by choosing appropriate automation tools and going through the implementation process. It’s important to consider specific needs, evaluate tool features, integration, and test and try the solutions before fully committing. Automation adoption has the potential to make businesses even better adjusted to the current digital landscape.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Elevating healthcare: a definitive guide to robust cloud security in the industry

When compared to other industries, healthcare has remained quite reluctant to digitalization. However, as technology evolves, cloud computing has become vital in streamlining operations and enhancing data accessibility. On the flip side, this also introduces various security concerns that demand attention.

This comprehensive guide delves into the importance of robust cloud security in healthcare. It provides valuable insights to safeguard sensitive patient information, maintain regulatory compliance, and fortify the industry against evolving threats. Join us as we explore all the essential information regarding cloud security in healthcare.

The growing importance of cloud security in healthcare

After the COVID-19 pandemic, the healthcare industry experienced a heightened demand for improved and more modern services. Distributed care and telemedicine pushed healthcare organizations to move to cloud computing, meaning data security had to be considered. The problem is that the same techniques that were valid for data security on-premises don’t translate well into externally kept data.

Some of the challenges facing the healthcare industry transitioning to cloud infrastructure included:

  • Resource and budget strains. Most healthcare providers work with limited IT budgets, so major infrastructure overhauls are long and tedious.

  • Continuity of operations. Data migrations to the cloud shouldn’t disrupt everyday operations, which isn’t something that all healthcare providers can allow.

  • Regulatory compliance. Patient data is highly confidential information so various local regulations sanction its security.

Generally, healthcare organizations want to move to cloud computing to make their services more effective while avoiding unnecessary or unmanaged risks. As patient data is one of the most sensitive data types, ensuring robust security measures is a top priority.

Types of healthcare cloud security solutions

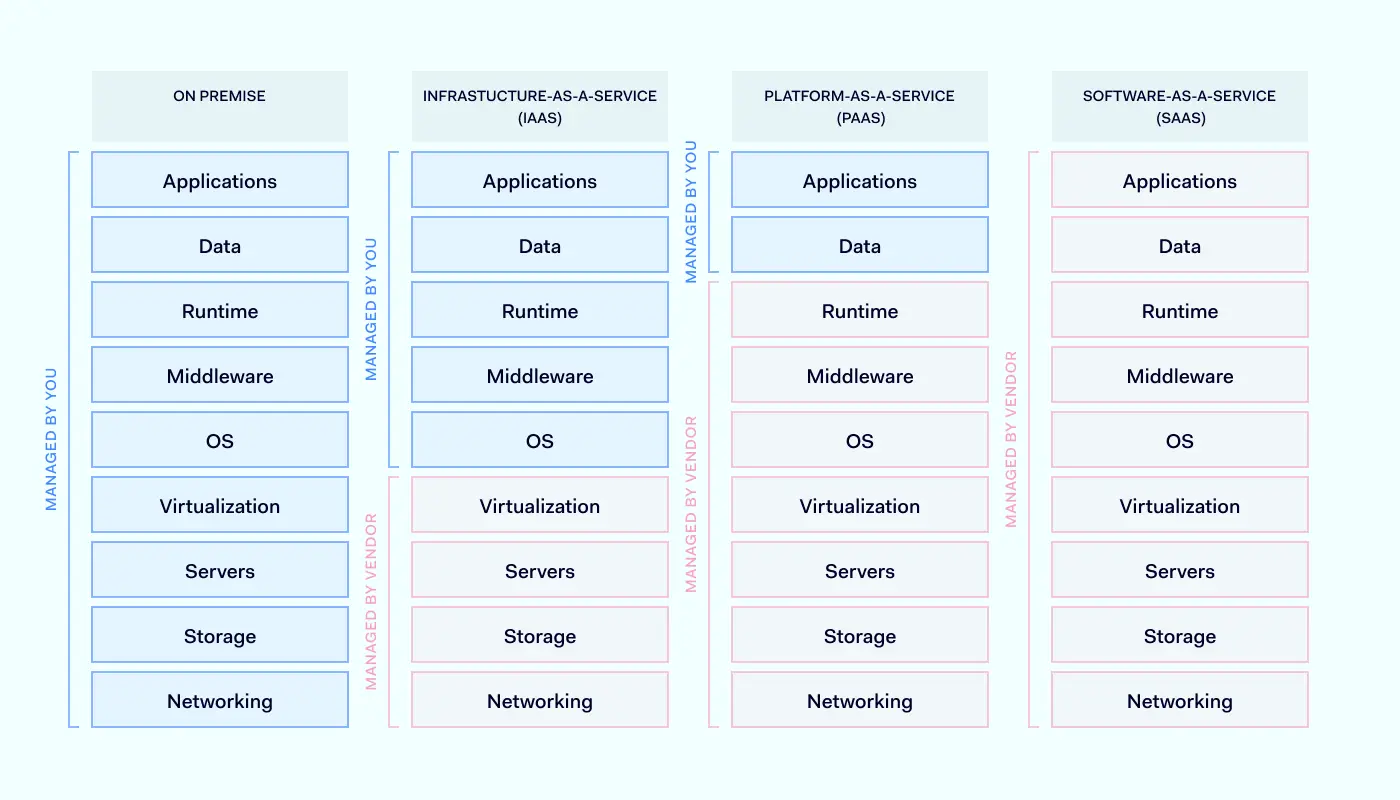
Healthcare providers (and, by extension, most industries) rely on three main types of cloud computing services. This includes Infrastructure-as-a-Service (IaaS), Platform-as-a-Service (PaaS), and Software-as-a-Service (SaaS).

Infrastructure-as-a-Service (IaaS)

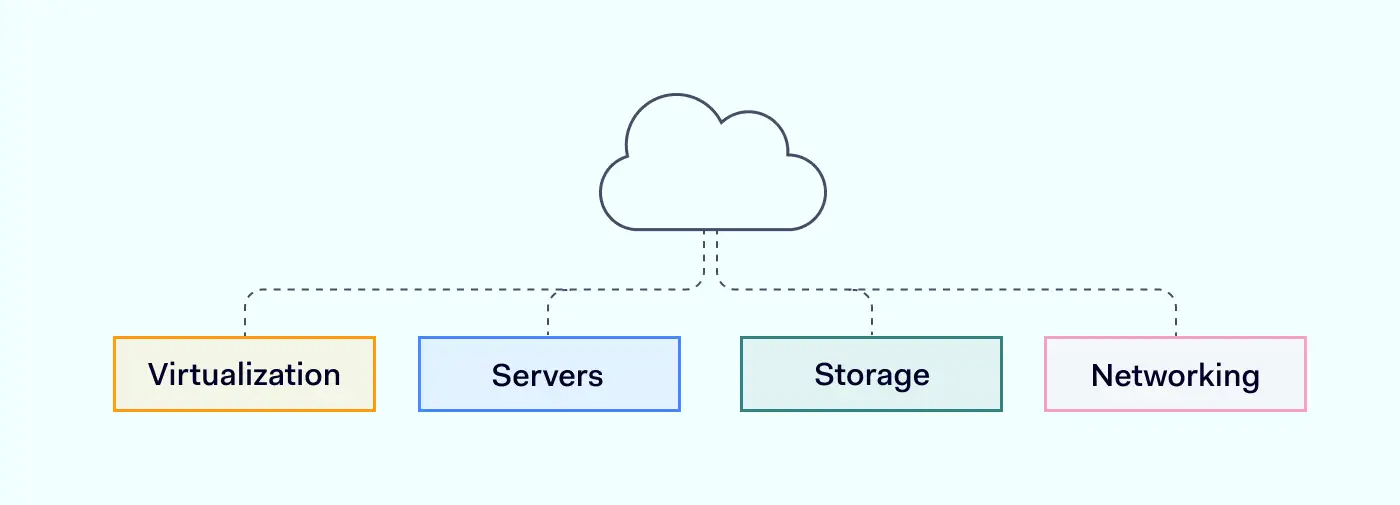
Infrastructure-as-a-Service provides virtualized computing resources as services over the internet. In IaaS, the service provider manages and delivers all associated hardware and software components: servers, storage, networking, and virtualization resources. With IaaS, users can provision and control these resources on-demand, scaling them up or down as needed.

Benefits of IaaS in healthcare

Aside from the fact that cloud computing makes it easier to deploy workloads, IaaS has a range of benefits that could be useful for healthcare companies.

  • Scalability and flexibility. By leveraging IaaS, users can rapidly deploy and configure virtual machines, storage, and network components. This allows healthcare organizations to scale their infrastructure up or down based on their actual needs.

  • Disaster recovery. IaaS enables organizations to back up and recover their critical data and remote machines. As critical data and applications are kept in cloud storage, this ensures their availability and integrity.

  • Cost efficiency. IaaS service providers use a flexible pay-as-you-go pricing model allowing users to pay only for the resources they use. This enables cost optimization, eliminating the need for upfront hardware and infrastructure maintenance investments.

Security challenges and how to address them

IaaS security is shared between the service provider and the user. While the service provider is responsible for managing underlying networking, storage, servers, and virtualization, the user is responsible for managing the security of everything running on top of the infrastructure. This involves operating systems, middleware, data, and applications. This setup is not without cybersecurity challenges.

  • Data protection. Sensitive patient data must be protected using encryption and access controls. As the data is physically located in third-party data centers, unauthorized access or breaches are the primary concern.

  • Compliance. Patient data falls under government-protected information, so regulatory compliance applies to it. Organizations must ensure that their IaaS providers adhere to sensitive patient data from unauthorized access or breaches.

For these reasons, IaaS provider selection is crucial to avoid collateral damage. Implementing multi-factor authentication, regular vulnerability assessments, and proactive monitoring can enhance security.

Platform-as-a-Service (PaaS)

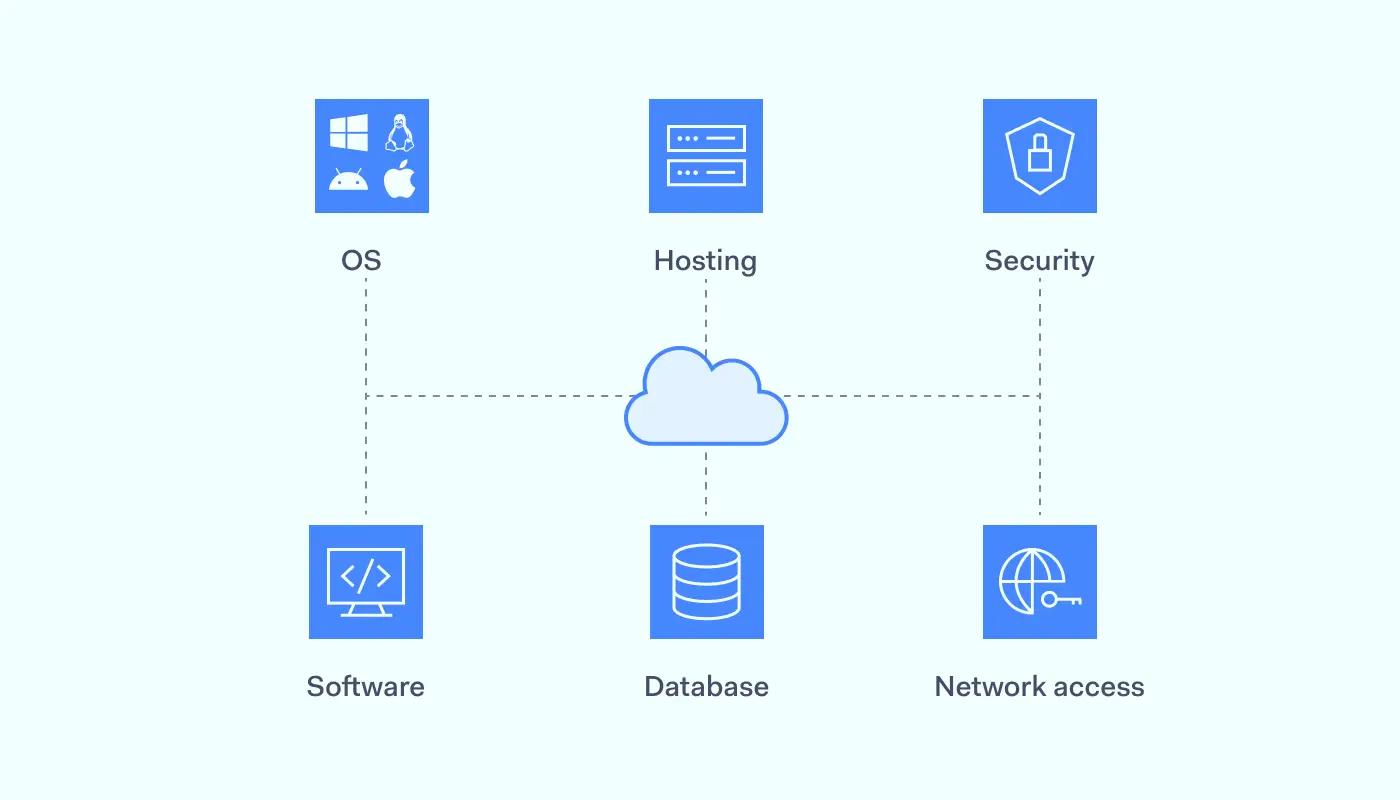
Platform-as-a-Service includes everything from IaaS with a dedicated environment for developing, deploying, and managing applications over the internet. It offers tools, frameworks, and services that enable developers to build, test, and run applications. Much like a physical data centre, PaaS providers handle hardware provisioning, operating system management, and network setup, allowing developers to focus solely on application development.

Benefits of PaaS in healthcare

With PaaS, healthcare providers get a platform for developing, testing and deploying applications in the cloud. Here are its main benefits:

  • Rapid application development. PaaS simplifies the application development process, allowing one to skip multiple setup steps and go directly to the deployment. This can accelerate innovation and provide new solutions quickly.

  • Scalability and performance. As with all cloud-based tools, they can automatically scale based on demand, ensuring high availability and optimal performance.

  • Collaboration and integration. PaaS is compatible with existing systems, meaning currently used tools can be integrated into a unified system.

Security challenges and how to address them

When adopting PaaS, organizations need to be wary of its security challenges. Here are some examples:

  • Application security. PaaS environments involve the deployment and running of custom applications. Therefore, businesses should conduct regular code reviews, implement secure coding practices, and perform vulnerability assessments.

  • Secure configuration. Businesses need to make sure that used PaaS platforms are properly configured. This includes firewalls, network access controls, and encryption protocols.

  • Incident response and monitoring. PaaS environments require ongoing monitoring and timely incident response capabilities. By establishing robust logging and monitoring systems and employing detection and prevention mechanisms, we can have a ready system in case of an intrusion.

Software-as-a-Service (SaaS)

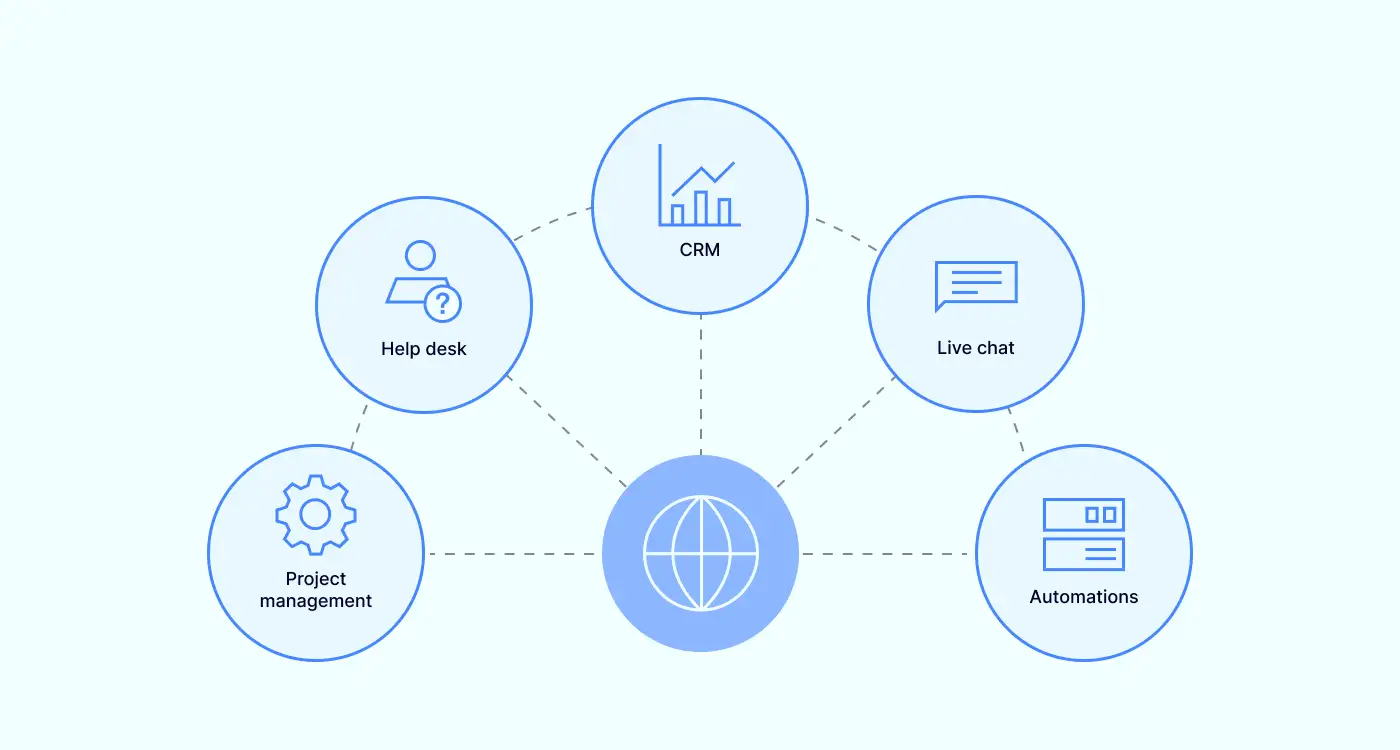
Software-as-a-Service is a cloud computing model in which hosted software is delivered over the internet instead of installed on local premises. In this model, the software is centrally hosted by a provider who manages and maintains the underlying infrastructure, database, and updates. Users only pay a subscription fee to access and use the software on a pay-as-you-go basis.

Many healthcare-related applications are delivered via SaaS, including healthcare picture archiving and communication systems (PACs), electronic health records (EHR), telehealth services, and more.

Benefits of SaaS in healthcare

With SaaS, healthcare organizations are provided with the service directly without the need to handle setup and maintenance. Here are its main benefits:

  • Accessibility and mobility. SaaS applications can be accessed from everywhere, enabling healthcare professionals to securely access patient information on various devices, enhancing workflow efficiency.

  • Automatic updates. The responsibility to handle software updates and patches fall on the service provider, meaning that healthcare applications are always up to date and protected against emerging security threats.

  • Fast deployment. SaaS applications are provided instantly and with minimal setup compared to on-premises software. Software updates and maintenance are handled by the SaaS provider, ensuring smooth operation.

Security challenges and how to address them

The problem is that SaaS brings healthcare organizations not only benefits. It does have some security challenges that need to be addressed by IT personnel.

  • Access control. As SaaS applications are externally hosted, managing user access and authentication is critical. This is the only way to prevent unauthorized intrusions.

  • Third-party integrations. Some SaaS applications need to be integrated with third-party services or APIs. These integrations can introduce security risks if not properly managed or if they have exploitable vulnerabilities.

  • Multi-tenancy risks. The same SaaS application can serve multiple consumers, sharing the same underlying structure and resources. This is why logical separation and isolation between tenants are crucial to prevent data leakage or unauthorized access to customer data.

Compliance and regulatory landscape in cloud security

Regulatory landscape and compliance are critical considerations for organizations across various industries. Most countries have recently implemented various data protection and cybersecurity laws. The government regulates the privacy protection of medical data, and breaching the law ensues grave consequences.

Here are some prominent regulations, guidelines that could impact cloud security, and strategies for ensuring compliance.

HIPAA and HITECH

The Health Insurance Portability and Accountability Act (HIPAA) and the Health Information Technology for Economic and Clinical Health (HITECH) Act are crucial regulations in the healthcare industry. They both perform different functions:

HIPAA — sets standards for protecting sensitive patient health information

HITECH — promotes the adoption of electronic health records

Compliance with both is essential when leveraging cloud computing services in the healthcare sector. Organizations need to take care of security measures like data encryption, access controls, and regular audits to safeguard patient data and meet the requirements outlined in these regulations.

GDPR

The General Data Protection Regulation (GDPR) is a comprehensive data protection framework that affects organizations operating in European Union countries or handling EU citizen data. It emphasizes individual privacy rights, consent management, and data breach notification.

Cloud service providers and organizations utilizing cloud computing services must comply with GDPR by implementing appropriate security measures, conducting data protection impact assessments, and ensuring cross-border data transfers adhere to GDPR guidelines. Encryption, pseudonymization, and privacy-by-design principles are critical for achieving compliance with GDPR in cloud computing.

Other regional regulations and guidelines

In addition to HIPAA, HITECH, and GDPR, other regional regulations and guidelines impact cloud security in specific industries or geographic locations. Examples include the Payment Card Industry Data Security Standard (PCI DSS) for the payment card industry and the Federal Risk and Authorization Management Program (FedRAMP) for U.S. government agencies.

Compliance with these regulations requires organizations to align their cloud security practices with specific requirements. Depending on the regulation and area, this may include data encryption, access controls, vulnerability management, and incident response protocols. Staying informed about relevant regional regulations is crucial to ensure compliance and avoid potential penalties or reputational damage.

As it was mentioned previously, cloud services adoption would involve collaboration with third parties. Here are some key considerations of security responsibilities between the cloud service provider and the customer:

Vendor risk assessment

A thorough vendor risk assessment helps to make sure that a cloud provider will be a matching fit for a healthcare organization’s needs. The cloud service provider’s market is saturated, but not everyone has compliant security controls, certifications, incident response capabilities, and data protection practices. The same strict requirements for healthcare organizations also apply to their third-party partners.

By assessing vendor risks, organizations can make informed decisions and select providers aligning with their security requirements and compliance obligations. Provider’s failure to secure the underlying infrastructure can open the gap in the security set up by the healthcare provider.

Understanding the shared responsibility model

The shared responsibility model defines the division of security responsibilities between cloud service providers and customers. While providers are responsible for securing the underlying infrastructure, customers are accountable for securing their data and applications within the cloud.

Organizations must understand and fulfill their share of responsibilities, which may involve tasks such as configuring access controls, encrypting sensitive data, applying patches and updates, and regularly monitoring for security incidents.

Key cloud security strategies and solutions for healthcare

While cloud computing is appealing to make operations more modern and effective, the downside is the potential cybersecurity risks. Safeguarding sensitive patient data and navigating regulatory compliance requirements are the primary concerns for healthcare providers. There are three main cloud security strategies and solutions to consider.

Advanced threat prevention

Advanced threat prevention is one of the key cloud security strategies for healthcare. It involves deploying sophisticated security measures to identify and mitigate potential threats before they cause any damage. Relying on technologies like machine learning algorithms, behavior analysis, Deep Packet Inspection, and real-time monitoring, organizations aim to detect and respond to suspicious activities.

As a proactive approach to cybersecurity, advanced threat monitoring allows healthcare organizations to identify and effectively neutralize threats. This helps businesses to reduce the risk of data breaches and unauthorized access to patient information.

Cloud-based security operations and monitoring

Monitoring is critical in ensuring the integrity and confidentiality of healthcare data stored in the cloud. By providing continuous oversight and proactive detection of potential security breaches or unauthorized access attempts, monitoring enables organizations to secure against security incidents promptly.

In addition, by leveraging cloud-based security tools, healthcare organizations can centralize security operations, streamline incident response, and gain insights into potential vulnerabilities. The systems can be automated, helping organizations detect and mitigate security breaches on time and enhancing overall security posture without human involvement.

Secure remote work

During the COVID-19 pandemic, the adoption of remote work in the healthcare sector accelerated. Secure remote access became critical as healthcare professionals needed to access patient data and collaborate remotely.

Cloud security solutions enable secure sensitive data storage, ensuring healthcare providers can work efficiently while adhering to strict security protocols. Implementing secure virtual private networks (VPNs), multi-factor authentication, and encryption technologies safeguard data transmission and prevent unauthorized access, mitigating risks associated with remote work.

Cloud security in action: enabling new healthcare capabilities

Cloud security not only performs the function of safeguarding patient data, it also empowers healthcare organizations to embrace new capabilities and innovate. Here are some routes in which cloud security can facilitate advancements.

Redundancies to prevent ransomware attacks

Ransomware attacks use malware that encrypts data stored in the device’s hard drive rendering it inaccessible until a payment is made to the attacker. This is extremely disruptive to organizations relying on on-premises infrastructure as this can completely shut down all operations and compromise patient data.

The only solution to this issue is data replication in multiple dispersed locations. That way, there’s no centralized storage that could be tampered with. In an accident, data can be restored from unaffected backups, minimizing downtime and ensuring continuity of care. Cloud servers enable effective mirroring solutions allowing distributed backups.

Delegation of security responsibilities to third-party firms

Cloud security can catalyze operations outsourcing, allowing better work distribution in your organization. Managing and maintaining robust cloud security infrastructure requires specialized expertise. That’s one of the key reasons why many healthcare organizations delegate their security responsibilities to reputable third-party vendors.

Cloud computing partners already possess the knowledge and resources to implement industry best practices, conduct regular security assessments, and respond to emerging threats promptly. This allows organizations to enhance the cloud security posture and focus on quality patient care.

Automation to free up healthcare resources

Cloud security can be improved by adopting various innovations to improve the setup. By automating vulnerability scanning, log analysis, and security policy enforcement, healthcare providers can free up their workforce from manual and time-consuming tasks.

Automation improves efficiency, reduces the risk of human error, and ensures consistent application of security controls. As IT professionals aren’t burdened with recurring manual tasks. This leaves them more time to focus on advanced security measures and stay updated with evolving threats.

Expert insights and resources for healthcare cloud security

Several organizations provide expert insights and resources for healthcare cloud security. Cloud Security Alliance (CSA), the European Union Agency for Cybersecurity (ENISA), and the National Institute of Standards and Technology (NIST) are the main ones providing various recommendations for cloud security in healthcare companies.

CSA

CSA has established requirements for healthcare organizations to ensure secure cloud computing practices. These requirements mainly focus on several key areas:

  • Implement strong access controls and authentication mechanisms to protect sensitive data.

  • Regularly monitor and audit cloud services for security vulnerabilities and incidents.

  • Encrypt data both in transit and at rest to maintain confidentiality.

  • Conduct regular risk assessments and threat modelling to identify and mitigate potential risks.

  • Establish incident response and recovery plans to handle security breaches effectively.

  • Stay updated with the latest security best practices and standards.

By adhering to these CSA requirements, healthcare organizations can enhance the security of their cloud computing environments and protect patient information from unauthorized access or data breaches.

ENISA

ENISA lays out comprehensive requirements for healthcare organizations in the European Union to enhance their cybersecurity measures. These requirements encompass multiple aspects of cloud security:

  • Develop and enforce robust security policies and procedures for cloud adoption.

  • Perform thorough risk assessments to identify and address potential security threats.

  • Ensure the secure configuration and hardening of cloud computing environments.

  • Employ strong access controls and authentication mechanisms to protect sensitive data.

  • Regularly monitor and log cloud computing activities to detect any suspicious behaviour.

  • Establish incident response plans and conduct regular security audits.

Adherence to these ENISA requirements is vital to safeguarding patient data, protecting critical healthcare systems, and maintaining the resilience and trustworthiness of healthcare services within the EU.

NIST

NIST provides guidelines and requirements and guidelines for healthcare organizations to ensure the security and privacy of patient information. These requirements include:

  • Follow the NIST Cybersecurity Framework for risk management and cybersecurity best practices.

  • Employ strong identity and access management controls to protect data and resources.

  • Use encryption to safeguard data both in transit and at rest.

  • Regularly update and patch cloud infrastructure and applications to address security vulnerabilities.

  • Implement robust network security controls, such as firewalls and intrusion detection/prevention systems.

  • Conduct continuous monitoring and log analysis to promptly detect and respond to security incidents.

Healthcare companies must review and adapt these recommendations to their organizational needs and regulatory requirements.

How can NordLayer help?

Securing cloud infrastructure can be challenging for healthcare companies. Still, the benefits outweigh the risks, so it’s worth considering digitally transforming an organization and improving its services. It’s not a bad idea to turn to third-party partners that could help to take a leap.

NordLayer streamlines network access controls to ensure only authorized users can access confidential data. Access to cloud resources happens using encrypted tunnels using AES 256-bit and ChaCha20 cyphers. The service is also compatible with major cloud platforms like Azure and AWS, allowing seamless integration with other solutions and services.

With correct control mechanisms, NordLayer is a valuable ally to follow through with the best cloud environment security practices. With an extensive set of centrally implemented features and monitoring controls that are all managed via the Control Panel, NordLayer allows the implementation of security policies reducing various risks.

Contact NordLayer and discuss your security options today to ensure safe access to patient data and protect your cloud infrastructure.

FAQ

How can healthcare organizations ensure compliance in the cloud?

Healthcare organizations can ensure compliance in the cloud by understanding applicable regulations. Familiarizing with regulations like HIPAA and GDPR will allow organizations to identify specific compliance requirements. This will serve as a basis for cloud provider choice and guide what access controls and other cybersecurity functionalities must be implemented to align with requirements.

What are examples of cloud security?

Cloud security is an umbrella term encompassing various technologies to protect data and systems in the cloud. This includes encryption, access controls, firewalls, intrusion detection and prevention systems, security information and event management, and data loss prevention.

How does the shared responsibility model work in healthcare cloud security?

The shared responsibility model defines the division of security responsibilities between the cloud service provider (CSP) and the healthcare organization. While the specifics entirely depend on the cloud service model, the cloud service provider usually takes care of the underlying cloud infrastructure. At the same time, the healthcare organization is responsible for application data security and access control.

What steps can healthcare organizations take to mitigate third-party risks?

To mitigate third-party risks, healthcare organizations must establish clear contractual agreements outlining security expectations, data handling procedures, breach notification requirements, and liability provisions. Then, a good plan is to perform ongoing maintenance with regular risk assessments. This should help organizations minimize risks associated with third parties.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Cost-benefit analysis of cybersecurity spending

As new data breaches are making the headlines, cybersecurity is becoming one of the most critical elements of a long-term business strategy. To protect their sensitive data and mitigate potential risks, businesses are actively looking for ways to move into the 21st century in terms of their infrastructure. However, as many soon discover, cybersecurity integration within an existing business is rarely a one-click solution.

Even putting all the technical questions aside, cybersecurity raises many questions regarding return on investment. This article will provide a broad overview of how to approach cybersecurity spending. We’ll briefly cover what makes up cybersecurity costs, what factors could affect them, the financial impacts of cyberattacks, potential benefits, and some guidelines on approaching cybersecurity estimates in your company.

Costs of cybersecurity

Cybersecurity spending can mean several things. The exact route will depend on the actual business case and the risks that the company is trying to mitigate. Still, no matter which options your company is considering, this is something where budget constraints will have to become a consideration.

Let’s look at the costs from different cybersecurity ecosystem components: solutions, services, personnel, and training.

Solutions

One of the go-to routes for organizations looking to shield themselves against cyberattacks is purchasing cybersecurity hardware or software solutions. This allows companies to flexibly integrate them into the infrastructure, strengthening the areas needing attention.

As such, businesses have numerous options available. Cybersecurity hardware and software provide easy access to firewalls, antivirus, access control mechanisms, intrusion detection and prevention systems. When used collectively, these technologies work together to halt cyberattacks or mitigate their impact if they do occur.

While it’s also true that their costs depend on various factors (which we will address later on), let’s look at the average industry costs associated with various cybersecurity solutions. Please note that the distinction between solutions and services isn’t as set in stone as it used to be due to modern service delivery models (like SaaS) and the popularity of cloud computing.

Firewalls

If an organization relies on a network, a firewall is a must as it monitors and controls network traffic. Acting as a barrier between the internet and/or other untrusted networks and your private network, it’s the first defense against malicious connections based on predefined rules.

The tricky part for the comparison is that they can be implemented at different levels of the network stack, i.e., from the network layer (filtering packets) to the application layer (proxy servers). Finally, they can be hardware or software-based, or a combination of both, affecting the final price tag.

Therefore, an average firewall configuration can range between $450 and $2,500 (as a one-off investment not factoring in its maintenance which costs extra). That doesn’t take into account setup or maintenance costs, so the final cost can be higher.

Antivirus software

Antiviruses are still staples to protect computer systems from malware, viruses, and other security threats. As an essential component of comprehensive cybersecurity strategy, they can be used as the last line of defense. Usually, in business settings, they’re deployed across an organization’s network to protect all connected devices.

It’s often the case that antiviruses also include additional features like firewalls, intrusion prevention systems, and email filtering to provide further protection against cyber threats. This also makes our comparison more difficult.

Still, if we’re looking for rough estimates, which is what we’re doing here: basic antivirus usually costs between $3 and $5 per user and $5 to $8 per server monthly. While the final price tag will entirely depend on your organization’s size, the estimate could be at least $30 a month if you have around five users.

Spam filters

Business communication primarily still takes place over emails. This is something that hackers are exploiting in phishing attacks. For this reason, having spam filters is essential to identify and block harmful emails before they end up in employees’ inboxes. Spam filters rely on various technologies to analyze the content and metadata of incoming messages to determine whether they are legitimate.

Some email providers offer spam filters already integrated into their suite. Meanwhile, for other cases, it’s required to set up a spam filter on top of it. It’s estimated that the price for this ranges between $3 – $6 per user per month.

Services

What makes cybersecurity services different from cybersecurity solutions is that they’re typically provided by a third-party provider, who may offer the service on a subscription basis. While a cybersecurity service may include various cybersecurity solutions, the two concepts are not interchangeable. Cybersecurity service by definition encompasses ongoing protection against cybersecurity threats.

Frequently this also means that cybersecurity services can help against threats of greater sophistication. This makes them a good pick for organizations looking into securing their digital assets and preventing unauthorized access, theft, and exploitation of sensitive information.

VPN

With plenty of employees working remotely, businesses need a secure way for their employees to access company resources. VPN encryption seals the sensitive data in a secure tunnel, enabling secure exchanges to the company’s network. This additional protection layer also helps mitigate cyber threats by masking the user’s IP address.

Yet, as with most cybersecurity components, there are multiple routes to consider here. A VPN could be set up as a hardware stack with ongoing third-party maintenance fees or a software-only solution. This is something that can skew the price.

While the software-only is cheaper and can be up to $10 per user, the hardware setup can range up to $3,500 per device. That’s a significant gap between them, while both options provide similar functionality. The particular business case will be a deciding factor.

Consulting and testing

Cybersecurity consulting and testing service providers have a high level of expertise in identifying and mitigating security risks. This is something that few companies can manage to achieve out of their own resources. Specialized cybersecurity professionals perform various checks to properly evaluate the used cybersecurity measures’ effectiveness and outline the most critical areas.

Due to the nature of their services, this can be a pretty expensive endeavor. A vulnerability assessment for a network with up to three servers would cost $1,500 to $6,000. It goes without saying that if the scope of investigations needs to be broader, this will only add up to the final price tag.

Endpoint detection and response

Businesses turn to endpoint detection and response (EDR) services because they provide high protection against cyber threats by monitoring and detecting potential security breaches. This allows businesses to detect and respond to cyber threats quickly and before they cause significant damage to the organization’s assets, reputation, and financial standing. EDR solutions typically operate through a combination of software agents and cloud-based systems.

Endpoint detection and response solutions cost around $5 to $10 per month per device. Yet, as with most subscription-based services, there are discounts: with more devices, EDR usually becomes cheaper per single device. Still, EDR solutions come in different depths and feature sets, so the final cost can be higher.

Personnel

Personnel is one of the most important cybersecurity assets at any company’s disposal. These specialists will protect your data from various forms of cyberattacks and ensure the risks are minimal. Whatever cybersecurity solutions or services you’ve purchased, the IT personnel will set up and maintain those tools.

Cybersecurity doesn’t become an integral part of an organization’s DNA just by purchasing some subscriptions. It needs to be cultivated. One way to ensure this is sustainable is to develop security policies and protocols — exactly what cybersecurity personnel will do.

Network administrators

Network administrators are responsible for setting up and maintaining the organization’s network infrastructure. They must ensure the network is secure from unauthorized access and that all transmitted data is protected from interception and other potential threats. The administrators will be configuring and managing firewalls, blocking specific ports, managing user permissions, monitoring the network, and patching system components.

As for their cost, you can look at conflicting data sources: depending on the region, experience, market saturation, and other factors. Still, if we’re looking for a broad view based on data from Payscale, this should be within $63,244 per year.

Compliance officers

Compliance officers are specialists who ensure an organization’s cybersecurity by implementing policies and procedures to align compliance with regulations and industry standards. They identify risks, monitor security measures, and ensure employees follow security protocols. These key people outline how an organization should handle sensitive data, access controls, and incident response.

A compliance officer’s salary is $73,255 a year based on publicly available data. Mind you, compliance is one of the trickiest landscapes to navigate, so these specialists must periodically refresh their knowledge to stay updated with the latest policy changes.

Security analysts

Security analysts identify potential threats to an organization’s network, systems, and data. They’re using various tools and techniques to detect and prevent cyberattacks before they can cause damage. Security analysts identify vulnerabilities in an organization’s systems and infrastructure by conducting risk assessments.

Security analysts are crucial in protecting an organization’s assets and cyber threats. Based on Glassdoor data, their salaries, on average, are around $90,283 a year. Due to the increased frequency and complexity, professional cyber security analysts are in high demand, which can further increase their salaries.

Trainings

The cybersecurity landscape is constantly changing. Therefore employees’ skills and knowledge need to be periodically refreshed. This is where cybersecurity training and certifications ensure that employees know the best practices for protecting this information and can identify potential threats. These trainings can be expensive, and organizations must ensure they are effective.

Courses

Cybersecurity courses can be an invaluable resource in helping to understand the importance of protecting company data from cyberattacks. By teaching employees how to identify potential security threats and how to take preventative measures, companies can reduce the risk of data breaches and protect their sensitive information. Nowadays, there are plenty of resources, ranging from in-person training to online lectures.

For this reason, cybersecurity training costs vary significantly and can range from freely available online resources to $5,000 or more. Mind you that the price is affected by factors like depth and competencies. Courses intended for niche specializations will always cost more than a basic introduction.

Certifications

Cybersecurity certifications provide credibility to professionals working in the field, demonstrating that they have met rigorous standards and have the necessary knowledge and skills to protect against cyber threats. Using certification as a standardized measure allows aligning the team and ensuring that best practices are applied when making organization-level cybersecurity improvements.

There are several popular cybersecurity certifications widely recognized in the industry. For example, the Certified Information Systems Security Professional (CISSP) exam costs around $699. Certified Ethical Hacker (CEH), another important pick for cybersecurity professionals, costs around $1199. Along with GIAC Security Essentials (GSEC) certification and exam, it’s priced around $1699, which makes it one of the more expensive courses.

Factors that affect cybersecurity costs

It’s important to note that the cybersecurity costs provided in the previous section are only rough estimates. The final price will depend on numerous factors, which will be the key differentials from business to business when calculating cybersecurity costs. Let’s look at some of them to see how they factor into the final price tag.

Size

The size of an organization is one of the most important factors which can drastically alter cybersecurity costs. As larger companies have more complex IT infrastructures, more employees to train, and a higher risk of cyber attacks due to their visibility and financial resources — their security naturally costs more. When compared to smaller organizations, the difference might be night and day.

Keep in mind that, in some cases, some cybersecurity tools will need to be adjusted. They cannot operate that well when used in corporate settings, which are within a completely different pricing category. However, numerous reports confirm that small businesses are three times more likely to be targeted by cybercriminals than larger companies. So while the risks remain high, not all companies are as well equipped to tackle the potential risks.

Industry

The industry in which an organization operates and any regulatory requirements it must comply with can impact its cybersecurity costs. Organizations working in highly regulated industries like healthcare and finance will have higher cybersecurity costs because more regulations apply to the data they’re holding.

As a side note, the industry determines an organization’s risk tolerance. Different industries can have very different thresholds for acceptable risk levels. This means that security’s scope will have to be aligned, which will also, in turn, affect cybersecurity costs. In addition, businesses in certain industries seem to fall victim to more cyberattacks than others, which is also a factor.

Financial impact of cyber attacks

While up until this point, you got the impression that cybersecurity is expensive, let’s move on to an overview of the financial impact of cyber attacks. Depending on what business operations are targeted, the attack scope, and the kinds of data leaking to the public, all constitute significant financial losses. Let’s look at revenue losses, legal fees, and reputational damage.

Revenue

Cyberattacks can disrupt normal organizations’ day-to-day operations and compromise sensitive data. This can easily make an organization’s systems and networks inaccessible or unusable. The downtime when the IT team is trying to patch together a solution and get the operations back up and running costs time, which also translates into lost revenue.

2 financial impact of cyberattacks

The recovery costs can also be factored in as damaged equipment needs to be replaced, and systems need to be restored from the backups. It’s not a coincidence that a quarter of companies that have experienced a cyber attack have lost between $50,000 and $99,999 in revenue. These are steep numbers, and they don’t factor in the costs of getting the operations back up and running.

Legal fees

After data breach remediation and operations restoration, the trouble isn’t over. Especially in cases of a large data breach, companies need to hire legal counsel, forensic experts, and other professionals to help manage the aftermath. So there’s the precedent of estimation and cleaning up.

3 post-breach legal fees breakdown

Additionally, depending on the data breach’s severity, the company may also be held responsible for the damage suffered by affected customers or clients. If there are lawsuits, this can quickly mount legal fees, including settlement costs. For smaller companies, that’s an instant endgame as they often just aren’t equipped to handle such expenses. For instance, it’s estimated that legal costs range from $50,000-$148 million, with a median of $1.6 million and a mean of $13 million.

Reputational damage

A data breach leaves a permanent black mark on a company’s reputation. Companies will need to spend a lot of resources to repair their image and reassure the customers that they have learned from their mistakes and won’t happen again. This long process involves public statements and social media management and should be an aspect of long-term customer trust remediation.

4 cybersecurity reputational costs

According to various reports, the proportion of the total costs that can be attributed to reputational costs like abnormal customer turnover and loss of goodwill was around $1.57 million. Mind you that this is something that affects companies for a long time, provided that a company even makes a recovery from a data breach.

Benefits of cybersecurity spending

Cybersecurity spending can minimize various risks associated with revenue, reputation, or legal fees. While this is a solid argument advocating for cybersecurity solutions, this is far from the only benefit. Having a functioning infrastructure with a cybersecurity-focused mindset also generates a positive outcome for organizations. Let’s look at some of the indirect benefits of cybersecurity spending.

Better compliance alignment

Many compliance regulations, like General Data Protection Regulation (GDPR) and the Health Insurance Portability and Accountability Act (HIPAA), require organizations to implement specific security measures to protect sensitive data. Therefore, investments in cybersecurity help to achieve two goals simultaneously:

  • The risk profile is contained, and the organization is more resistant to cyberattacks.

  • The organization ensures that it has all the necessary technologies and policies in place to meet compliance requirements.

Reports confirm that achieving substantial compliance goals require holistic and integrated security solutions, ensuring that every aspect of an organization is covered. For this alone, cybersecurity investments should be at the top of the business manager’s list.

Increased productivity

Cybersecurity matters can often be a catalyst for workplace modernization. While this may not always be a seamless transition, the change often allows the work to be performed more efficiently and securely. A good example of this is the remote and hybrid work trend, which became very popular after the global pandemic.

In fact, securing identities and endpoint devices enables users to do their work quickly and securely from anywhere. Nowadays, there are many ways of working, and cybersecurity can be a good contributor to breaking the cycle of outdated tech and enabling all ways of working.

How to apply cost-benefit analysis for your organization

Our rough estimates demonstrate that data breach costs outweigh cybersecurity expenses. While this is a valid statement, this doesn’t provide clear guidelines on what actionable steps should be taken when considering cybersecurity spending. Businesses have finite resources, and cybersecurity is just one area that needs to be addressed. Thankfully, there are some models that we can use as a basis to evaluate cybersecurity costs and benefits.

Let’s start by looking at one of the most widely used schemes: the National Institute of Standards and Technology (NIST) Cybersecurity Framework. This is a helpful document consisting of standards, guidelines, and best practices to manage cybersecurity risks. It’s especially useful because it’s applicable to companies from all industries.

The problem with it is that while it recognizes that management of cybersecurity risks is always organization-specific, which will also shape how the final cost-benefit evaluation will look, it doesn’t outline how the cost-benefit analysis should be provided. For this reason, some researchers suggest integrating mathematical models Lawrence A. Gordon and Martin P. Loeb developed into the NIST Cybersecurity Framework. The model calculates an optimal investment in cybersecurity based on the cost of an attack, the expected probability, and the effectiveness of the security measures put in place.

The basic premise of the Gordon-Loeb model is that there is a tradeoff between the cost of an attack and the cost of investing in cybersecurity. Organizations want to minimize the total cost, including the cost of an attack and the security investment. The model assumes that the cost of an attack is proportional to the value of the information assets that could be compromised.

The model also considers the probability of an attack occurring, which is a function of the number of potential attackers, the likelihood that they will attempt an attack, and the effectiveness of the security measures. The effectiveness of security measures is assumed to be proportional to the level of investment in cybersecurity.

To calculate the optimal investment in cybersecurity, a balance needs to be found between the level of investment and the expected total cost. This relies on the relation between the expected cost of an attack and the cost of the security investment. This leaves us with a four-step approach:

  1. The value of protected information should be estimated as it represents the potential loss (L)

  2. The probability of the information being breached should be estimated (v)

  3. These first two values should be combined to derive the expected loss (vL)

  4. Cybersecurity investments should be allocated to the information based on the productivity and cost of the investments, so an optimal investment level (z)

Putting this data in the graph gives us some perspective on the diminishing returns. If the values of v and L are small, for instance, when v equals 0.1, and L equals $1M, extensive investments in cybersecurity aren’t optimal, as the expenses are higher than the benefits.

However, as the values of v and L increase, the optimal investment amount (z) and the expected loss resulting from a cybersecurity breach (vL) increase in this scenario.

5 graph showing optimal cybersecurity spending

In other words, the more valuable data an organization has, the more it has to lose. Once that threshold is met, not investing in cybersecurity is sitting on a powder keg. It’s a simple exercise to go through to better evaluate your organization’s standing in terms of cybersecurity. As a rule of thumb, the authors of the study suggest that organizations should generally invest less than 37% of the expected loss from a cybersecurity breach. The actual number will then need to be individually calculated based on your organization’s specifics.

How to improve your cybersecurity with NordLayer?

Cybersecurity is unavoidable in the current business environment because cyber threats aren’t going anywhere. This also has associated costs: solutions, services, personnel, and trainings. Organizations aren’t left alone without help, so for those willing to team up with cybersecurity providers — the market offers numerous opportunities that could make your company more resistant to cyber threats.

When it comes to the price, though, there are numerous factors that can also affect cybersecurity costs, like industry and size. As most cyberattacks are financially motivated, the companies with the most sensitive data are the prime targets. Although, it’s always fair to assume that no matter the industry or size, no one is immune to them.

That is why organizations need modern cybersecurity solutions that adapt to changing complexities of today’s working environments. All organizations have information that needs protecting, so all communication channels are interesting to hackers.

With NordLayer’s solutions, organizations can secure access to sensitive information and prevent reputational, legal, and financial damage. No matter what industry, NordLayer can be a reliable ally to help you stay secure. Contact us, and let’s discuss your cybersecurity journey together.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Using artificial intelligence (AI) in cybersecurity

Artificial intelligence (AI) has made remarkable progress in recent years and has proved its value in various fields, including cybersecurity. With the rise of cyber threats and the increasing complexity of cyberattacks, AI has become a central tool for protecting against cybercrime.

Integrated artificial intelligence systems have the potential to be trained for the automatic identification of cyber threats, alerting users, and safeguarding sensitive information of businesses. Therefore, this article explores AI in cybersecurity, its benefits, use cases, and solutions, and addresses some frequently asked questions.

How is AI used in cybersecurity?

Artificial intelligence combines large data sets and uses them with intuitive processing algorithms. As the scope of networks and systems expands, AI in cybersecurity helps to automate operations by processing large amounts of data much faster than a human ever could. For this reason, most cybersecurity tools integrate deep learning and other capabilities intended to work with big data. Here are the main ways in which AI is used in cybersecurity:
  • Threat detection. AI can act as a filter for analyzing files and software code to identify potential malware threats while avoiding false positives. Machine learning algorithms can be trained for threat detection to recognize patterns and characteristics of known malware and flag any new code that matches these patterns.

  • Network security. AI algorithms can analyze network traffic data to detect patterns and anomalies indicating an attempted intrusion or attack. AI can flag any deviations from this baseline as potential threats by learning what normal network traffic patterns look like.

  • Behavioral analysis. AI can be used to analyze user behavior and detect anomalies that may indicate unauthorized access or malicious activity using machine learning. This allows for more effective user activity monitoring and detection of potential threats while limiting false positives.

  • Automated incident response. AI-based systems can be used to automatically respond to detected threats, like shutting down connections, quarantining infected machines, and disabling user accounts. Advanced machine learning models help to contain hacking attempts and minimize potential damage.

  • Vulnerability assessment. AI can identify potential vulnerabilities in systems and networks. This allows for proactive measures to be taken to mitigate potential threats before they can be exploited.

AI can be a powerful tool that can contribute in real-time, which can be essential in today’s rapidly evolving cyber threat landscape and lowers the odds that an organization will be affected by a data breach.

Benefits of AI in cybersecurity

AI solutions are versatile and can be applied in various scenarios. However, it requires preparation and feeding the deep learning models with plenty of data that could be used as a reference when identifying patterns. AI for cybersecurity does bring benefits, creating a more secure environment. Here are some of them that are noteworthy in a business setting.

1. Better vulnerability management

Considering the scope of threats that organizations face daily, network administrators need all the help they can get for endpoint protection. AI can analyze existing security measures to identify potential gaps, enabling businesses to focus on the most critical areas. This makes troubleshooting more efficient and provides in-depth oversight of the security level faster than any human ever could.

2. Self-correcting models

AI models can use deep and machine learning techniques to analyze network behavior and identify deviations from the norm. This allows further adjustments, enabling them to trigger various response actions when something odd is detected. This system adjusts its model over time, making it more accurate.

3. Limits process duplication

Some cybersecurity tasks are repetitive and monotonous, adding to personnel frustration and increasing the chances that some threats will slip by. AI-driven tools can perform all those recurring tasks automatically and only require confirmation before making the final changes. This allows security against potential gaps by consistently implementing the best network security practices.

4. Secure authentication

The industry is moving away from passwords and looking for ways to make security smarter. AI can be a helpful addition to implementing multiple authentication layers to verify a user’s identity. Using tools like fingerprint scanners, facial recognition, and other AI solutions helps identify fraudulent login attempts. This creates a much tighter security mechanism when allowing users in.

5. Helps to cover more ground

AI tools can perform multiple tasks simultaneously. At the same time, AI can scan and identify disguised threats while prioritizing prevention, even when dealing with multiple threats simultaneously. This versatility positively translates in terms of cybersecurity. Human attention can be limited to a single task at once, while AI can cover them in all other areas, which helps to expand network visibility and ensure appropriate security.

6. Helps to balance out workloads

Cybersecurity personnel isn’t cheap to hire or maintain, so it’s in a business’s best interest to ensure their experience is spent on tasks with the highest complexity. While AI can take care of manual tasks, human personnel can think of other ways to improve the cybersecurity posture in the organization. In the long run, this creates a greater value.

The limitations of traditional methods

The main difference between traditional cybersecurity tools and AI is their flexibility. Conventional cybersecurity tools like antiviruses or firewalls function based on strictly predetermined rule sets. A tool comes equipped with a list of malware types or blacklisted websites, which must be manually updated over time — it’s a very static system.

Meanwhile, AI can detect and respond to threats in real-time. Its ability to process large amounts of data when making decisions is unparalleled and extremely valuable. Cybersecurity threats are becoming more complex, so cybersecurity tools must react quickly if they want to stop them, which is why static models are too slow in today’s cyber landscape.

Hackers are also following developments of AI, which puts a lot of pressure on traditional cybersecurity solutions, as well. That’s another reason why AI in cybersecurity can level the playing field and provide a more well-rounded security solution.

AI cybersecurity solutions

The current cybersecurity market is saturated with solutions that integrate AI capabilities. Their advanced models allow them to process large amounts of data in real-time. Here’s a broad overview of cybersecurity technologies that integrate AI for cybersecurity.

Endpoint security

Endpoint security uses AI integrating network and device security to provide holistic protection against various threats. Tracking and analyzing processes on laptops, desktops, and mobile devices before the execution of malicious code allows the solution to shut down threats before they cause damage. Additionally, the models are expanded with additional input from past threats as they’re actively updated as they’re used.

Intrusion detection systems (IDS)

AI-powered IDS systems are capable of autonomously identifying threats using machine learning models. With enough data to work with and thorough training (and enough computational power), the model can be very accurate when discerning potential threats. This can help identify signs of intrusion moments from when it started. When combined with the remaining cybersecurity suite, the solutions can also help automate certain tasks, i.e., alert security teams or shut down network parts.

Data Loss Prevention (DLP)

DLP tools automatically encrypt data before it’s transmitted or restrict unauthorized users from accessing sensitive information. It’s no wonder that modern DLP tools are using AI and machine learning to improve their functionality and performance. AI can monitor and analyze organizational data flows to prevent unauthorized or accidental data leaks. Identifying sensitive information, enforcing data handling policies, and detecting potential data exfiltration attempts in a blink of an eye.

Security Information and Event Management (SIEM)

AI-powered SIEM tools use machine learning, user behavior analytics, and cybersecurity threat feeds to detect abnormal activities. This contribution to threat hunting can help automate many time-consuming manual tasks that network administrators must perform by using AI. This allows for balancing automation with cost-effectiveness and efficiency, improving the organization’s overall security posture. Automatic events correlation, suspicious activity detection, and real-time insights into potential threats enable faster incident response and threat hunting.

FAQ

What is the future of AI in cyber security?

Recent developments have shown that AI will continue to be closely integrated into cybersecurity solutions as attacks become more sophisticated. Many experts believe that using AI will be one of the main directions in which cybersecurity solutions will evolve. This will allow them to identify threats and potential vulnerabilities before they cause damage.

What are AI-enhanced cyber threats?

AI is used not only by cybersecurity specialists but by hackers, as well. This allows them to evade detection and cause more damage. The whole process can be automated — hackers are already writing convincing phishing attack emails using AI and natural language processing. Malware development can also be enhanced using AI, allowing hackers to write sophisticated malware that effectively bypass security measures. Various freely available chatbots are already contributing to the already saturated malware development.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

What is static IP? How it differs from dynamic IP?

IP (Internet Protocol) addresses work like digital street addresses that let devices find each other on the internet. Every internet device has a unique IP address. All of these addresses can be converted into text formats via the Domain Name System (DNS) format. This forms the basis of the World Wide Web.

There exist two types of IP addresses: static and dynamic. Both versions have specific roles. Both have strengths and weaknesses, and it’s important to choose the right type for your networking needs. This article will explain how they work and help you choose the right one for your needs.

What is a static IP address?

The word “static” means unchanging, and this is a good description of how a static IP address works. The static IP meaning refers to an IP address that is assigned to a device and remains constant, as opposed to a dynamic IP address that changes each time the device connects to the internet. Users assign them to individual devices or resources. The address then applies for as long as users desire.

Static IP address types are typically found in devices like web servers. This form of IP address is usually utilized by businesses that need to communicate globally and want a fixed identity.

Because they are finite and must be assigned individually, static addresses come with monthly fees. This is not the case with a dynamic IP address.

Benefits of static IP addresses

  • DNS functionality. Website managers need to couple IP addresses with DNS information. A static IP address provides a better fit for DNS servers because it never changes. The DNS server can connect consistently with the same static IP address, resulting in smoother operations.

  • Website hosting. A static IP address comes into its own when used with web servers. With a static address, site visitors will find it easier to locate a website on the internet. Connection speeds may also be slightly quicker. This can be an advantage in areas like finance where rapid transactions make a major difference.

  • Voice communication. Voice-over-IP (VoIP) works much better with static IP addresses. This benefits companies that rely on teleconferencing or any type of video transmission.

  • Remote access benefits. Static IPs make it possible to establish consistent connections between remote workers and central networks. Wherever employees need to work, they can use the same IP address. This identifies their devices to network servers – a simple remote work solution.

  • Reliable geolocation. Static addresses make it easier to identify where you are. This is a big advantage to any services that depend on geolocation, such as weather or traffic updates.

  • IP allowlisting. If remote workers have a static IP address, security teams can use that address to filter legitimate traffic. Allowlisting supplements firewalls and VPNs. It effectively hides network resources from outsiders whose IP is not allowlisted. As a result, it also promotes better data security.

How to set up static IP addresses

Users can easily set up a static IP address in Local Area Network by changing their network settings. However, you will need to request a static address from your ISP if you want to have fixed external IP.

After the request, external fixed IP will be assigned and the setup will automatically be applied on your router. If you manually configure the settings on your devices, you will need to enter the assigned IP address, subnet mask, default gateway, and DNS server information into the network settings for each device that will use the static IP address.

Alternatively, if you use a Dynamic Host Configuration Protocol reservation, you can set up your router to assign the static IP address automatically to a specific device on your network. This method ensures that the device always receives the same IP address, even if it is restarted or disconnected from the network temporarily.

Note that this isn’t the same as configuring a private IP address that is reserved for use within a private network, such as a home or office network.

What is a dynamic IP address?

Dynamic IP addresses constantly change. The IP address is not connected to an individual user or company.

There is usually no financial charge for using a dynamic IP address. ISP servers assign them as needed. Using a dynamic IP address is generally cost-effective for service providers compared to assigning static addresses.

Dynamic IPs are the standard identifier for consumer devices. They are routinely used in home networks to identify tablets, laptops, and digital boxes. But a dynamic IP address is not always the best option for businesses, who may prefer an IP address that does not change.

Benefits of dynamic IP addresses

  • Cost. A dynamic IP address is usually cheaper to use than static alternatives. There is no regular fee. Addresses are assigned in the background as part of ISP packages.

  • Simple configuration. Users do not need to manually configure a dynamic IP address. The address changes without users knowing. DHCP will automatically switch addresses, leaving users with no additional admin tasks.

  • Fewer device conflicts. Static IPs can conflict if used for one or more devices. For example, you may add extra workstations to a corporate network. Dynamic addresses are unlimited and reusable. So any new devices will immediately gain unique identifiers.

  • Security benefits. Hackers may obtain static IPs and use them to breach network resources. Because a dynamic IP address changes regularly, it presents a moving target. This makes life harder for potential attackers, especially when combined with VPN protection.

  • Privacy. Static IPs provide constant evidence of your physical location. This can be useful for external snoopers and thieves. With a dynamic IP address, it’s harder to pin down your device location. This results in enhanced physical security.

How does it work?

When you receive a dynamic IP address, it is assigned by a system called Dynamic Host Configuration Protocol (DHCP).

ISP companies maintain reserves of unused IP addresses and assign users the next available IP address when they connect to the internet. The dynamic IP address is re-assigned to someone else when their session ends.

It’s important to remember that DHCP assigns dynamic addresses temporarily. Users “lease” the dynamic IP address on a short-term basis. The same IP address could be reused hundreds of times in a single day.

Dynamic addresses also present a different identity to the services you use. This can cause problems when websites expect a single IP address to identify users. Features like autofill passwords may not function correctly.

Comparison of static and dynamic IP addresses

Static IP address:

  • Doesn’t change

  • Has a higher maintenance cost

  • Used for handling lots of connections simultaneously

  • Helps to maintain uninterrupted access

  • Ensures availability for outside devices and networks

Dynamic IP address:

  • Is continuously rotated

  • Doesn’t additionally increase the cost

  • Used for user devices like smartphones and laptops

  • Helps to maintain online access when changing networks

  • Ensures that all devices are always assigned an IP address

When comparing Static IP vs Dynamic IP addresses, it helps to keep their different features in mind. Here are some handy pros and cons of both IP address varieties:

Static IP pros

  • Geolocation – Static addresses work well with IP-based geolocation services. They are a good fit for users who need to be precisely located.

  • Voice-over-IP – Static IP is preferable for VoIP teleconferencing.

  • DNS hosting – Static addresses are a much better option for hosting DNS-based web assets. Website data will be available to users across the world, with minimal IP address conflict.

  • Security – Static addresses make allowlisting easier, boosting security. Users can route static VPN traffic through a single IP address, protecting traffic and enabling safe remote working.

Static IP cons

  • Hacking risks – Because they never change, static IPs can be prone to hijacks. And static addresses can give away geographical details to snoopers.

  • Ease of Use – Users must configure a static IP address manually after an initial request to their ISP.

  • Costs – Static IP addresses come with an extra charge, so tend to cost more.

Dynamic IP pros

  • Security – Constantly changing IP data makes hacking more difficult. IP address holders are also harder to track down via geolocation tools.

  • Costs – Dynamic IPs are generally free of charge for the duration of contracts from Internet Service Providers.

  • Ease of Use – Dynamic addresses require virtually no configuration, so are generally easier to use.

Dynamic IP cons

  • Reliability – Dynamic addresses can sometimes be unavailable. They do not function well with DNS servers, and they deliver less precise geolocation information.

  • VPN functionality – Virtual Private Networks work much better with static IPs, especially when applied to business settings.

  • Website issues – Using the web may be less convenient. For example, sites may fail to auto-fill fields if IP addresses constantly change.

When to use a static or dynamic IP address?

Comparing static IP vs dynamic IP addresses shows that the two IP address types have very different use cases.

When to use a static IP address

Static IP is generally preferred by businesses. Unchanging IP addresses are ideal for hosting websites because they suit DNS server architecture.

With a static IP, your web or email server will be easier to find. External partners can use a single point of contact to interact with servers or databases. And that address does not change unless you want it to.

If you are planning to connect an email server or are designing a remote work system, static IP addresses will probably work best.

It is also easier to apply IP allowlisting with a static IP address. Allowlisting adds an extra layer of network protection. Security teams can add static addresses to firewall rules, and block everything else. Remote workers can identify themselves easily. Wherever they are, the network will recognize them as authentic users.

Additionally, static addresses benefit users of critical SaaS applications. Companies benefit from more reliable VPN and Voice-over-IP services.

When to use a dynamic IP address

Dynamic IP is generally found in home and consumer settings. The low cost and convenience are a good fit for everyday device usage. Dynamic addresses also have a slight security edge for private settings and organizations that cannot invest in enterprise security solutions.

Some device types also tend to use dynamic IP for reasons of convenience. For instance, routers may not need a static address. Dynamic DHCP-assigned addresses can be cheaper and simpler to configure.

As IPv6 becomes mainstream, the cost of static IPs may come down. The stock of IP addresses has been limited by the Ipv4 format. In the future personal and business use of static IP addresses may well be routine.

How can Nordlayer help?

Choosing the right IP address format is an important part of network architecture. Businesses can optimize their web presence, improve app performance, and realize security benefits by applying static IPs.

However, these benefits require careful implementation. Nordlayer is ready to help companies as they secure their network assets.

Our dedicated IP services make it possible to conceal traffic and filter access requests. Assign a static IP to your VPN coverage, and block unauthorized traffic without denting network performance. Users can combine static IPs with network segmentation, access controls, DNS filtering, and many other security features.

With Nordlayer, you can build a user-friendly security architecture that makes life easy for authenticated users and blocks malicious traffic when connected to internet gateway. To find out more, contact the Nordlayer team today.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.