Skip to content

The evolution of cyber threats: looking back over the past 10 years

Over the past decade, the world has witnessed a dramatic increase in cyber threats. The digital age has brought about new opportunities for innovation and growth but has also created new avenues for cybercriminals to exploit. The rise of new technologies, such as artificial intelligence, has enabled attackers to become more sophisticated in their methods.

In this blog, we will look back at the evolution of cyber threats over the past decade and explore how businesses can adapt to these changes. We will also discuss how NordLayer protects your data and resources ahead of the curve.

Upsurge of cyber threats

The past decade has seen a rise in various types of cyber threats, from ransomware attacks to social engineering tactics. One of the most notable threats is ransomware, where attackers encrypt a victim’s files and demand a ransom payment to restore access.

In 2020, ransomware attacks rose by 150% compared to the previous year, according to The Harvard Business Review. Another common threat is phishing, where attackers use social engineering tactics to trick victims into revealing sensitive information. Phishing is an effective and dangerous cybercrime because it relies on people’s inherent trust in the internet. The idea that criminals would be able to fool you into giving up private information is hard for most people to believe, which makes it easy for even well-meaning people to fall victim to a phishing attack.

Impact on businesses

The impact of cyber threats on businesses cannot be overstated. Cyber attacks can result in significant financial losses, reputational damage, and legal consequences. According to a study by IBM, the average data breach cost in 2020 was $3.86 million.

According to Forbes, small and medium-sized businesses are especially vulnerable. The impact of cyber attacks on businesses extends beyond financial losses, with reputational damage and loss of trust among customers also being significant concerns.

2009-2012: rise of advanced persistent threats (APTs)

The period between 2009 and 2012 saw a rise in advanced persistent threats (APTs). APTs are long-term attacks that focus on stealing data from a specific target and are highly sophisticated. The attackers would spend months or even years gathering information about their target before launching an attack. The goal was to steal sensitive information without being detected.

One of the biggest examples of this type of threat during this timeframe occurred in 2010, where Google and other companies were targeted in a series of APT attacks known as Operation Aurora. Attackers gained access to sensitive data and intellectual property by exploiting company software systems vulnerabilities.

Some ways to protect against APTs include:

  1. Secure VPN: A secure virtual private network (VPN) that encrypts all data transmitted between the user and the internet. This ensures that sensitive information is kept confidential and protected from cyber attackers.

  2. Next-generation firewall: A next-generation firewall can detect and block malicious traffic, including APTs. It also allows for granular control over network traffic, enabling administrators to restrict access to sensitive resources.

  3. Intrusion Prevention System (IPS): IPS uses advanced techniques to detect and prevent APTs from infiltrating the network. This includes detecting and blocking attempts to exploit network and software vulnerabilities.

  4. Threat intelligence: Ideally, a threat intelligence platform continuously monitors global threat activity and automatically updates security policies and rules to protect against new and emerging threats.

  5. User behavior analytics (UBA): A UBA solution can identify and flag abnormal user behavior that may indicate a security threat, such as an APT. This helps administrators quickly detect and respond to potential attacks.

2013-2016: ransomware and business email compromise (BEC)

Between 2013 and 2016, ransomware and Business Email Compromise (BEC) attacks rose. Ransomware is a type of malware that encrypts a victim’s files and demands payment in exchange for the decryption key. On the other hand, BEC attacks involve impersonating a senior executive and tricking employees into transferring money to a fraudulent account.

These attacks proved to be highly profitable for cybercriminals, with ransomware payments reaching billions of dollars annually. BEC attacks have also been on the rise, with the FBI reporting losses of over $1.7 billion in 2019 alone.

The WannaCry ransomware attack affected hundreds of thousands of computers in over 150 countries. The attackers demanded ransom payments in exchange for unlocking the affected systems. Another good example of these threats during this timeframe was the CEO Fraud in 2015, where tech company Ubiquiti Networks fell victim to a BEC attack that cost the company $46.7 million. The attackers posed as Ubiquiti executives and convinced employees to transfer funds to overseas accounts.

Some ways to protect against ransomware and BEC attacks include:

  1. Email filtering: This service can help protect against BEC attacks by blocking suspicious emails that may contain phishing or malware links. This helps prevent employees from falling for social engineering tactics and inadvertently giving hackers access to sensitive information.

  2. Anti-malware: A solution to detect and block ransomware before encrypting files on a company’s network. This helps prevent data loss and minimize the impact of a ransomware attack.

  3. Backup and recovery: Automated backup and recovery services can help restore data and systems during a ransomware attack. This helps minimize the damage caused by an attack and reduces the likelihood of paying a ransom to recover data.

  4. User awareness training: Employee training and awareness programs help educate staff on recognizing and reporting potential security threats such as BEC attacks. This helps employees understand how to protect themselves and the company from cyber threats.

  5. Access control: This feature allows administrators to restrict access to sensitive data and systems, helping prevent unauthorized access and reducing the risk of a successful ransomware attack.

2017-2020: Internet of Things (IoT) and artificial intelligence (AI) threats

The period between 2017 and 2020 saw the rise of Internet of Things (IoT) and Artificial Intelligence (AI) threats. This time frame saw the first cases of this type of attacks.

IoT devices are becoming increasingly popular for on-site and remote businesses, making them a prime target for cybercriminals. These devices often lack proper security measures, making them vulnerable to attacks.

Artificial intelligence plays an increasingly significant role in the evolution of cyber threats. On the one hand, AI is being used by businesses to improve security measures, such as detecting anomalous behavior and identifying potential threats. On the other hand, cybercriminals are also using AI to create more sophisticated attacks.

For example, cyber-criminals can use AI to generate realistic phishing emails that are more likely to trick victims into revealing sensitive information. AI is also being used to create deep fake videos and audio, which can be used for social engineering attacks.

The Mirai Botnet was a massive cyberattack in 2017 that compromised hundreds of thousands of IoT devices, turning them into a network of bots used to launch DDoS attacks on various websites. The botnet primarily targeted vulnerable IoT devices such as security cameras, routers, and DVRs that had weak or default login credentials.

According to a report from Wired, “Mirai was responsible for the largest DDoS attack in history, which peaked at 1.1 terabits per second and brought down the DNS provider Dyn, taking down popular websites including Twitter, Netflix, and Reddit in the process.”

Another example was the 2018 DeepLocker; a type of AI-powered malware that is designed to evade traditional cybersecurity measures by using AI algorithms to hide and remain undetected until it reaches its target.

The malware is designed only to activate when it detects a specific target, such as a particular person’s face or voice. The malware was created as a proof-of-concept by IBM’s X-Force Red team to demonstrate the potential risks of AI-powered attacks.

Some ways to protect against AI attacks include:

  1. Network segmentation: This feature can segment the company’s network, separating IoT devices from other devices and systems on the network. This can help prevent an attacker from using an IoT device as a backdoor to access the company’s sensitive data and systems.

  2. Device management: This service ensures IoT devices are configured with the proper security settings and updated with the latest firmware and security patches. This helps prevent IoT devices from becoming a vulnerability and potential targets for attackers.

  3. Behavioral analysis: Behavioral analysis detects abnormal activity in the network, which can help detect and prevent AI-based attacks. This includes monitoring the behavior of IoT devices and detecting anomalies that may indicate a potential attack.

  4. Machine learning: Machine learning utilizes algorithms to analyze network traffic and identify potential threats. This includes the ability to detect anomalies in the behavior of IoT devices, which can help identify potential AI-based attacks.

  5. Threat intelligence: Ideally, a threat intelligence platform continuously monitors global threat activity and automatically updates security policies and rules to protect against new and emerging threats, including those targeting IoT and AI systems.

2021-2022: supply chain attacks and Ransomware-as-a-Service

In 2021 and 2022, there has been a significant increase in supply chain attacks and Ransomware-as-a-Service (RaaS) attacks. Supply chain attacks involve targeting a third-party vendor to gain access to their customers’ networks. These attacks have been highly successful, with cybercriminals targeting software providers, IT companies, and cloud service providers.

RaaS attacks involve renting out ransomware to other cybercriminals for a percentage of the profits. This business model has made it easier for cybercriminals to launch attacks, resulting in a surge of ransomware attacks worldwide. According to a report by SonicWall, there were over 304.7 million ransomware attacks in the first half of 2021, a 151% increase from the same period in 2020.

One of the biggest related incidents took place In 2020. The SolarWinds supply chain attack affected multiple U.S. government agencies and corporations. The attackers compromised SolarWinds’ software updates and used them to distribute malware to their customers.

Another case worth studying is the Colonial Pipeline, a ransomware attack in 2021 that shut down a major fuel pipeline in the United States. The attackers demanded a ransom payment in exchange for restoring access to the company’s systems.

Some ways to protect against Supply Chain Attacks and Ransomware-as-a-Service attacks include:

  1. Vulnerability scanning: This service can detect vulnerabilities in software and systems that may be exploited in a supply chain attack. This includes identifying outdated software, unpatched systems, and other potential vulnerabilities.

  2. Access control: This feature allows administrators to restrict access to sensitive data and systems, helping prevent unauthorized access and reducing the risk of a supply chain attack.

  3. User awareness training: Employee training and awareness programs help educate staff on recognizing and reporting potential security threats, including supply chain attacks and ransomware-as-a-service. This helps employees understand how to protect themselves and the company from cyber threats.

  4. Anti-malware: This solution can detect and block ransomware before encrypting files on a company’s network. This helps prevent data loss and minimize the impact of a ransomware attack, including those delivered as a service.

  5. Backup and recovery: Automated backup and recovery services can help restore data and systems during a ransomware attack. This helps minimize the damage caused by an attack and reduces the likelihood of paying a ransom to recover data.

2022-present: deepfake and synthetic identity fraud

In 2022, deep fake and synthetic identity fraud attacks became increasingly prevalent. Deepfake technology involves creating realistic videos or audio recordings that can be used to spread misinformation or conduct social engineering attacks. On the other hand, synthetic identity fraud involves creating fake identities using real and fake information.

These attacks have proven to be highly effective, with cybercriminals using deep fake technology to impersonate high-level executives or political leaders to spread false information. Synthetic identity fraud has also been on the rise, with losses estimated to reach $1 billion in 2022, according to the 2022 Internet Crime Report of the Federal Bureau of Investigation.

In the article TOP 5 cyber attacks of 2022, the best examples of this type of threat can be further analyzed.

How can NordLayer help?

Cybercriminals constantly evolve their tactics, making it essential for businesses to stay up-to-date with the latest threats. Cybercriminals use fileless attacks, which do not leave a footprint on the system, and supply chain attacks, where attackers target third-party vendors to gain access to a network. By understanding these tactics, businesses can take steps to protect themselves.

The past decade has seen a rapid evolution in cyber threats, with attackers becoming more sophisticated and their tactics becoming more advanced. Businesses must adapt to these changes by implementing robust cybersecurity measures to protect their data and resources. NordLayer remains committed to providing top-notch security solutions that evolve with the changing cyber threat landscape.

Our Zero Trust Network Access solution provides secure access to resources and data, while our ML-powered (machine learning) threat detection system prevents end users from accessing potentially harmful websites that may affect business operations.

As the cybercrime landscape develops, NordLayer continues to evolve its products to protect access to data and resources. Our security solutions include access control features, network segmentation, and secure VPN.

We continuously monitor the latest threats and adapt our products to provide the most robust protection possible.

Contact NordLayer and learn how we can help you secure your business.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Product agent release: NordLayer Browser Extension

The amplitude of online scams is outraging on the internet. Malicious actors always seek original and convincing ways to catch their victims off-guard. LinkedIn creates a perfect environment for social engineering and other types of fraud, and that’s why scams have populated the platform.

Let’s start from the beginning. The LinkedIn platform is incredibly popular, with over 930 million members globally, making its scams an intriguing topic not only from a consumer perspective but from businesses.

Do only small companies or large enterprises fall victim to LinkedIn threats? Does it depend on a country or organization’s maturity? And what are the most common approaches that get employees’ trust?

To answer these questions and dig deeper into the source of businesses-linked LinkedIn scams, NordLayer researched the fraudulent activity tendencies.

LinkedIn scam — is a fraudulent scheme on the LinkedIn platform that aims to trick people into giving money or personal information, often through a fake job or business opportunities, requests for payment, or impersonation.

Click to tweet

These scams usually target individuals. Yet, due to the peculiarity of LinkedIn, they are often connected to organizations the targeted people are employees of. A LinkedIn scam poses personal threats but also puts a company at risk, making it an interesting case from a B2B security point of view.

Research methodology

NordLayer surveyed 500 respondents in Canada, the United Kingdom, and the United States. An external agency conducted the surveys between the 15th–25th of March, 2023.

Respondents (adult population, 18+) of non-governmental organizations were asked what kind of scams they encountered on the LinkedIn social media platform and what aftermath effects it had on their business. Subindustries represented included business management and support services, e-commerce, education, finance and insurance, health care, information and communication, IT, professional and technical services, and consulting.

The survey covered questions about the organization’s cybersecurity maturity level (Beginner, Basic, and Advanced), their cybersecurity solutions, and whether they had an in-house specialist or responsible department.

Companies by size were segmented by:

  • Small companies: 1-10 employees

  • Medium companies: 11-200 employees

  • Large companies: 201+ employees

Typical LinkedIn scams

The professional nature of a LinkedIn platform opens unique opportunities to vary the approach to encounter platform users. With a focus on job and industry topics, LinkedIn is no less than a social networking platform for making connections, communicating, and finding think-alikes.

The primary function of LinkedIn – building a career – introduces one of the most common LinkedIn scams, fake job offers. With 117 job applications submitted per second on the platform, fraudsters have an ideal environment for creating a legitimate-looking job posting to collect personal information or money.

Another popular scam is LinkedIn phishing, where an actor impersonates a well-known company or professional using fake profiles to send unsolicited messages or emails that ask for sensitive information.

Also, receiving an invitation to connect is common on the platform. Fraud actors use this connection culture to start a conversation and share a link with malicious content expecting LinkedIn users will click on it.

The NordLayer research on LinkedIn scams affecting the business sector confirmed the dominating tendencies of fraud types among the respondents, as the leading ones match the general statistics:

It’s safe to assume that most fraud attempts impacting businesses are social engineering based on public or personal information. On the one hand, LinkedIn is an environment where everyone shows their or their organization’s best side.

Yet, politeness, eagerness to sell oneself, and prospect opportunities tend to create an unintentional smoke screen for LinkedIn members leading to the most bizarre scams that might even involve lotteries or romance fraud.

Research findings on LinkedIn scams

Many businesses acknowledge the significance of being present on LinkedIn. 77% of respondents confirmed that their organization has a profile on the platform. Yet, 82% of medium-large companies tend to register more often than 54% of small (up to 10 employees) businesses.

The scams fall under two main categories. One is targeting individuals or pretending to be LinkedIn users. Another one is on a company level — operating under false organization pretext or impersonating an existing company to build more credibility. The research data shows that over one-third of survey respondents were aware of multiple LinkedIn frauds using their organization name. 

Frequency and scope of LinkedIn scams

According to the research, over half of the respondents encountered a scam attempt or fake account on LinkedIn.

Interestingly, the least active scam outreach was noticed in small companies — 52% of respondents confirmed that no one in their organization had such an experience. Fewer organizations with LinkedIn company profiles can explain such deviation from general tendency.

The rest of the respondents (47%) indicated their organization employees are likely to be engaged in a scheme. The trend corresponds with companies with Advanced cybersecurity maturity (46%).

Advanced cyber-maturity and medium-large companies are the first to fall victim to phishing attempts (52%) and fake tech support (45%) scams. It implies that large and mature companies have higher cyber awareness levels and, at the same time, more often outsourced assets like technical help vendors or a vast yet difficult-to-unravel network of colleagues, which brings everyone to an eye of a storm.

It is also worth mentioning that companies of all sizes get a lot of fault-line messages inviting them to connect. The frequency of receiving such requests varies by around 40% of companies.

Offerings to purchase non-existent or fake products or services are more prominent for mid-sized businesses — 34% compared to an average of 26% of such encounters with small and large enterprises. Medium-sized companies also lead fake lotteries (30% compared to 24%) and dating/romance scams (28% compared to 18%).

Target geography of LinkedIn scams

The distribution of research data is almost even among different countries participating in the survey. Attention-grabbing information shows that most active LinkedIn users are in the United States, with 83% of respondents having a profile on a platform (72% in Canada and 76% in the United Kingdom). 

However, the engagement rate of scams is lower in the States than in the other two countries. Only 38% were contacted by a fake LinkedIn profile or attempted to be scammed more than once, compared to 43% in Canada and 44% in the UK.

Looking closer at the tendencies of each surveyed country, the United Kingdom is attacked mainly by fake job offer scams (63%) and fake get-rich-quick offers (43%).

The United States leads in receiving a request to connect with a suspicious link — even 47% of respondents confirmed getting one, and 29% received an invitation to take part in a fake survey.

LinkedIn scams in Canada are focused on offering to buy a non-existing/fake product or service (36%) and getting involved in dating/romance fraud schemes (30%).

Despite the country, results were distributed almost equally for cases of phishing attempts (47%) and fake tech support (38%). It’s also important to note that if one scam is more popular than the other in different countries, it doesn’t mean that companies and their employees are safe from getting attacked or should expect only trending attacks.

The aftermath of LinkedIn scams

The scam attempt effects on organizations vary from harming reputation to imposing physical infrastructure damage. Regardless of the size of the business, they may experience the following:

Small businesses are impacted the most by cyber attacks, compared to larger organizations. They are more likely to experience financial loss (67%), stolen IP, and operation disruption (each 58%). Additionally, half of the organizations surveyed had their reputation damaged. Due to attacks, small businesses lose more employees (42%), while medium and large enterprises lose fewer employees (16% and 22%, respectively).

Medium-sized enterprises have to deal with reputation damage the most (47%), stolen and/or damaged data, and customer contacts (each 43%). Compared to other size businesses, mid-sized organizations are more likely to experience infrastructure damage (25%).

On the other hand, large organizations tend to suffer from reputation damage the most (41%), as well as compromised data and financial loss (each 40%). Additionally, 37% of all organizations deal with business operations disruption. Based on the data from respondents, it’s clear that small businesses are affected the most with LinkedIn scams and large enterprises the least.

How to avoid falling for a LinkedIn scam?

To avoid falling for a LinkedIn scam, it’s important to be cautious and alert. Start with making sure any job posting or business opportunity you’re interested in is legitimate before you apply or accept an offer. You can do it by researching the company or person offering the opportunity and only providing personal or financial information if you are confident they are not fake.

It’s also essential to protect your privacy on LinkedIn by adjusting your account settings to limit who can see your LinkedIn profile and send you messages. Be careful of unsolicited messages or connection requests from people you don’t know, and always watch out for signs that the message may be a scam, such as poor grammar, spelling mistakes, and overly aggressive or pushy language.

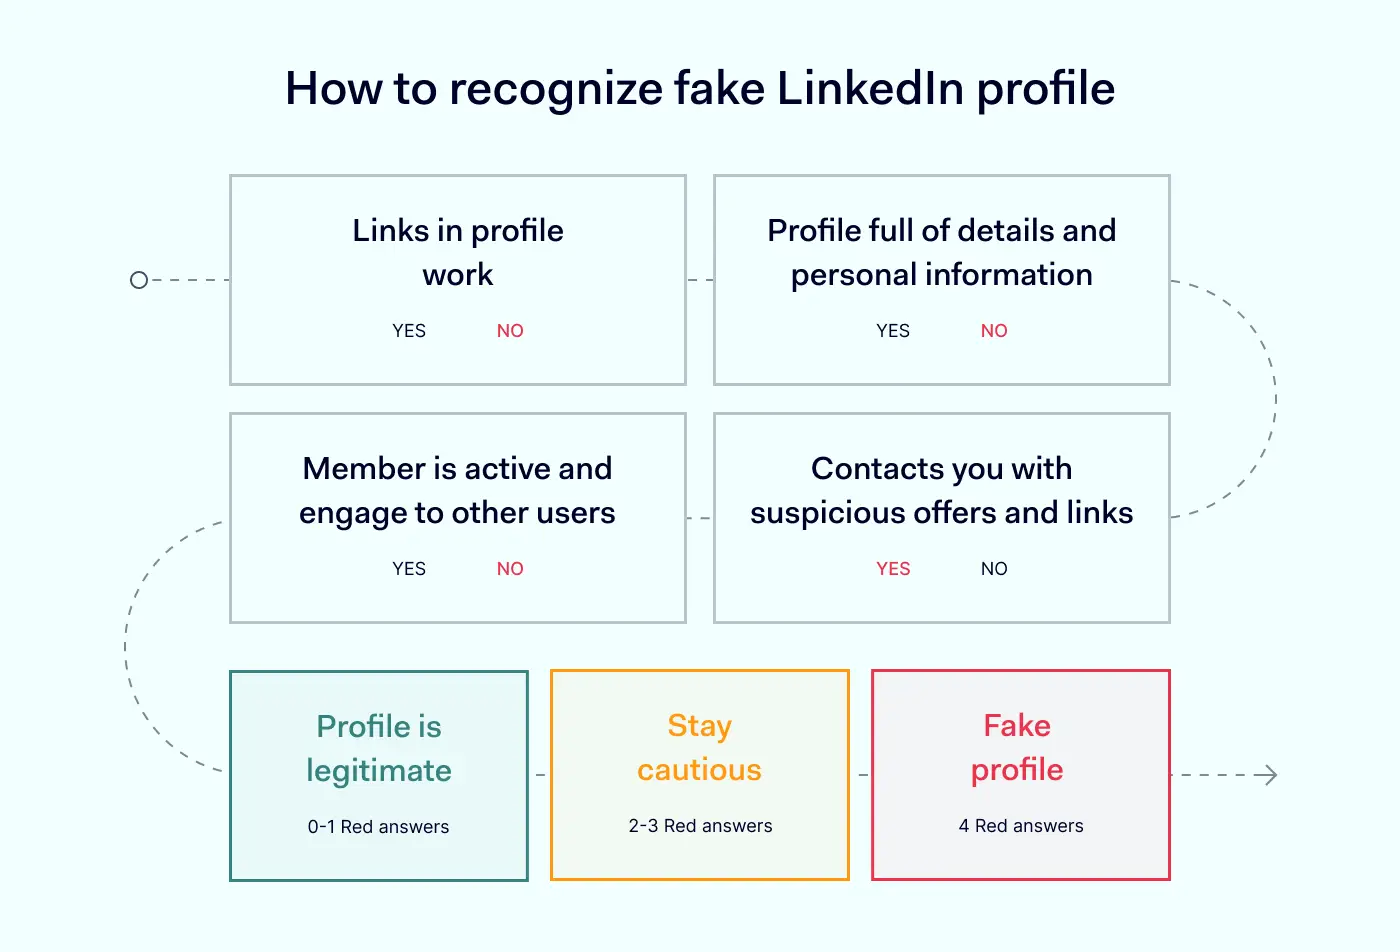
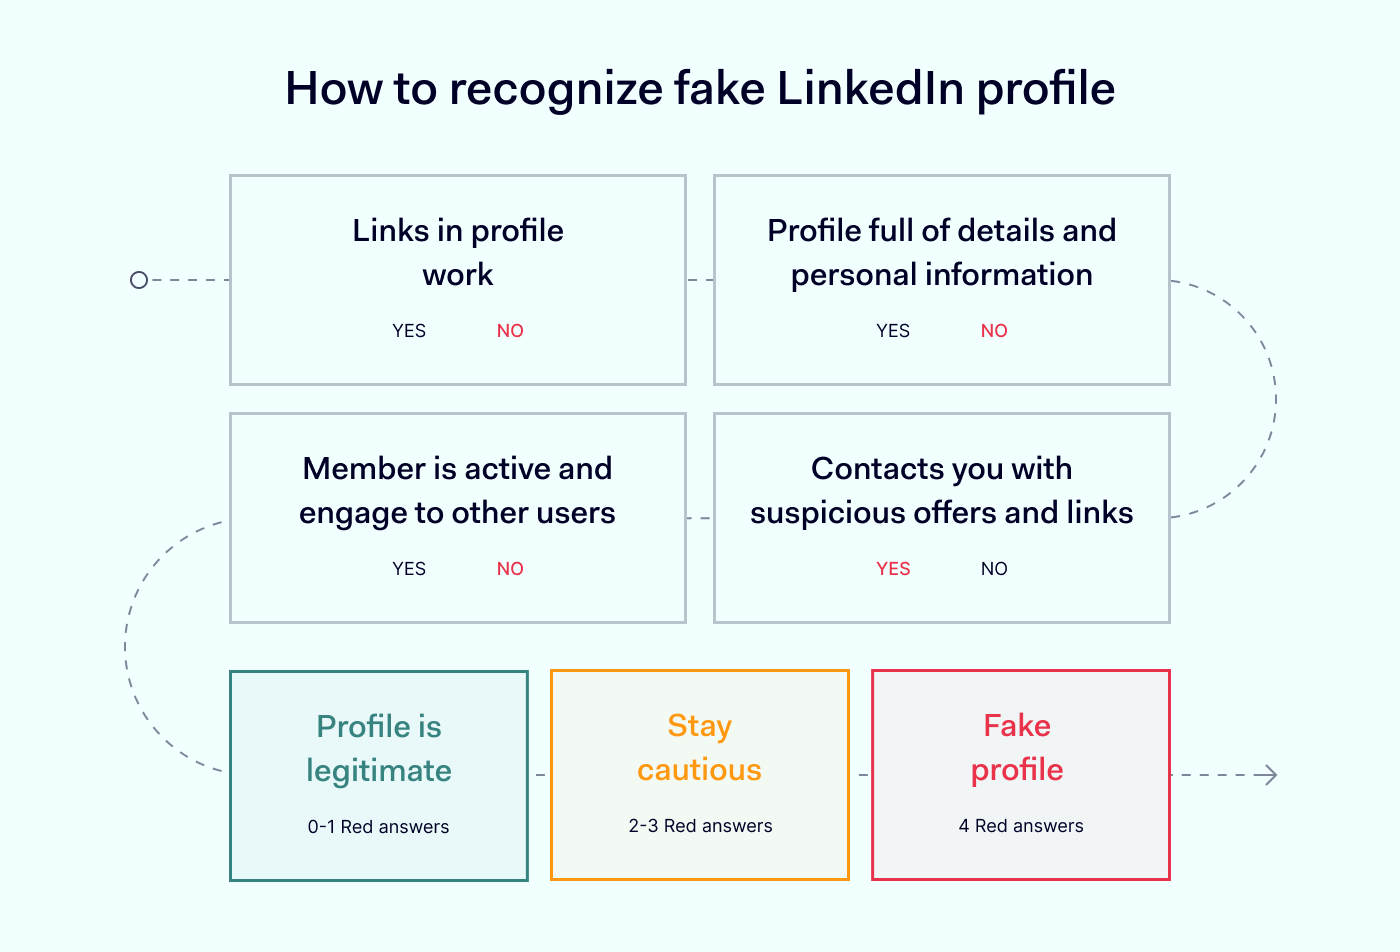
Tips for recognizing fake LinkedIn profiles

  1. Check the links present in the profile. Real profiles link to the person’s company website or their professional social media profiles. Be careful of shortened links or links that redirect you to another website, as these may be used to disguise fraudulent websites.

  2. Look for inconsistencies or lack of detail in the profile. A legitimate profile usually has a lot of information about the person’s professional history, education, and skills. Fake profiles typically have very little information or no profile picture.

  3. Investigate the activity of the LinkedIn profile. If the profile has very little activity or engagement with other users, likely it’s one of the fake LinkedIn accounts. Additionally, suppose the allegedly fake profiles send connection requests to many people, particularly those without connection to the profile. In that case, it may be part of phishing attacks.

  4. Be cautious of suspicious or irrelevant job offers, promotions, or messages from the profile. Fake LinkedIn profiles often use these tactics to lure users into scams, identity theft, or other harmful activities.

How to recognize fake LinkedIn profile

What to do if you’ve been scammed on LinkedIn?

If you think you’ve been scammed on LinkedIn, don’t panic. The first thing to do is to report the fraud to LinkedIn or the Internet Crime Complaint Center (IC3). Follow the instructions on LinkedIn’s Help Center page to report the scam. You should also contact your bank or credit card company if you have been charged for a fraudulent transaction.

To avoid getting scammed in the future, consider enabling two-factor authentication for your LinkedIn account, checking your account settings regularly, and changing your login details from time to time to ensure your account is secure.

FAQ

Are you worried about scams on LinkedIn? Sadly, LinkedIn is not completely safe from scams like many other online platforms. However, there are things you can do to spot and report scams to protect yourself and others.

How to report a scam on LinkedIn?

If you come across a scam on LinkedIn, first, you should report it to LinkedIn. Here’s how:

  1. Go to the profile of the person or company involved in the scam

  2. Click the “More” button below their profile picture

  3. Select “Report this profile” or “Report this company”

  4. Follow the prompts to provide details about the scam and submit your report

LinkedIn’s Trust & Safety team will review the submitted report and take appropriate action, including removing the scammer’s account and preventing them from creating another one.

How to identify a scammer on LinkedIn?

Scammers on LinkedIn may use a variety of tactics to trick people into giving them money or personal information. Some common signs of a scammer include:

  • A profile that appears to be fake or incomplete

  • Unsolicited messages offering a job or business opportunity that seems too good to be true

  • Requests for money, personal information, or account credentials

  • Pressure to act quickly or keep the opportunity secret

If you encounter any of these signs, it’s a good idea to investigate further before engaging with the person. You can also report the profile to LinkedIn as described above.

How can I check if a job offer on LinkedIn is legitimate?

Before accepting a job offer on LinkedIn, it’s a good idea to make sure it’s real. Here are some ways to check:

  • Research the company offering the job. Look for their website and social media profiles to learn more about them.

  • Check the job description for any red flags, such as vague or unrealistic requirements.

  • Ask for more information from the person offering the job. Legitimate employers will likely provide more details about the position and the company.

  • Look for reviews or ratings of the company on LinkedIn or other online platforms.

LinkedIn scams are a reality, but knowing how to recognize and report them can protect yourself and others from harm. If you encounter a scam on LinkedIn, report it to LinkedIn’s Trust & Safety team, and remember to be cautious when engaging with people you don’t know online.

How can NordLayer help?

NordLayer remote network access solution, by its design, protects digital company assets and their employees. By deploying functionalities for secure online browsing, organization administrators can bring more peace of mind in limiting company exposure to external threats.

Organizations can enforce ThreatBlock functionality that lowers the chances of employees potentially landing on malicious websites. This NordLayer feature helps reduce the risk of accessing publicly enlisted phishing sites, making it forbidden to access them.

To make security even stronger, the DNS filtering by category feature allows administrators to block access to the social media category and restrict access to certain websites for the whole organization.

If the blocking is exclusively required only for the LinkedIn site, admins can select and customize Deep Packet Inspection (DPI) Lite functionality for the organization’s network security. DPI Lite blocks specific ports and protocols from accessing when connected to a company network.

If you believe securing a team’s online activity is important for protecting your company, reach out to our team to discuss your options for creating a secure way of working in your organization.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

B2B LinkedIn scams: trends & how to prevent them

The NordLayer team is happy to announce the launch of a new and one-of-the-kind NordLayer Browser Extension. A now-available extension introduces another layer to increase and reinforce connection and access security for web-based resources.

The extension, operating within browser limits, is a lightweight option for organizations to substitute the NordLayer desktop solution and maintain the security of virtual private gateways. Moreover, utilizing the extension on top of the NordLayer desktop solution allows connecting two gateways simultaneously.

Feature characteristics: what to expect

  • Simple deployment & configuration via browser

  • Available for Advanced plan with a virtual private gateway.

  • Compatible with Google Chrome, Mozilla Firefox, Microsoft Edge browsers

Problem to solve: Seamlessly elevate the user experience by eliminating operating system compatibility issues with a lightweight solution that doesn’t negatively impact internet speed and performance, whichever – remote or hybrid – working setup there is, also enabling more flexible geo-based capabilities.

How does it work?

Generally, a standard connection to the internet is not encrypted if additional security measures are not enforced. Therefore, the implementation of solutions like NordLayer address such security issue. The established encrypted and secure connection to the company network protects online activities on the device level.

However, in some cases, there’s a need for an alternative solution that can replace a full Cloud VPN solution to secure connections just while browsing. Therefore, browser extensions operate as a midway alternative for non-existent and fully deployed security solutions.

NordLayer Browser Extension enables the remote workforce to have Secure Web Gateway (SWG) capabilities to access protected internet and cloud resources. Deployed on a browser, the add-on can run without or on top of the NordLayer application.

Establishing ThreatBlock, DNS filtering, or Deep Packet Inspection (DPI) features for filtering malicious websites from user-generated internet traffic enables SWG capabilities via the browser extension. This way, it protects the user, company network, and sensitive data from exposure to threats.

What problem does it solve?

The browser add-on fills a security and usability gap for organizations’ daily challenges of various working setups. Issues like latency or solution incompatibility with some operating systems (OS) are now resolved when installing the NordLayer browser add-on.

Configured for a company virtual private gateway, NordLayer Browser Extension allows IT admins to rest assured that malicious online traffic is restricted from entering the company network only on a browser level.

From the user’s perspective, the extension is seamless and intuitive to deploy and use. Being 15 times smaller than the NordLayer application, the extension runs in the background without disrupting business workflow.

Browser Extension objectives include:

  1. Protection of the internet and cloud resources accessible by remote and/or hybrid workforces

  2. Replace the setup of a third-party (proxy) browser extension for the end user with a login of organization-defined single sign-on (SSO) and two-factor authentication (2FA) solutions

  3. Introduce a widely available add-on to increase online security

NordLayer Browser Extension is an SWG proxy for organizations to secure connections to web-level resources without encrypting all desktop network traffic.

Security by design

NordLayer Browser Extension defines a simple, intuitive, and effective security approach developed by NordLayer. The add-on is an alternative solution to enrich existing security features provided by the solution for online activities.

Easy to launch and quick to set up, the browser extension provides instant network security for web-based company resources when accessed via the browser.

The extension is effective as a solution alone — it sorts availability and compatibility issues of various OS. It downgrades the network’s connection traffic load – but not the security – when accessing the company’s virtual private gateways, resolving latency and performance problems for the organization.

Moreover, it is a solid addition to web-level security when combined with DNS filtering and routing traffic via custom DNS and implemented with Deep Packet Inspection (Lite). Altogether, browsing security–related features and the browser agent introduces a layered security grid to the organization’s network security strategy.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

5 key business apps for startup success in 2023

Starting a business is in itself a daunting task, but keeping it successful on top of that requires immense effort and skill. A tight budget and so many choices when it comes to managing said business can take a toll on any startup. Moreover, a huge part of maintaining that success is having the right tools. 

Woman sits on sofa and uses her smartphone with a smile on her face.Nowadays, enterprise applications and software play a vital role when it comes to having a flourishing business as they help keep organizational and scaling headaches to a minimum. From office management to cybersecurity solutions, we’ve compiled a list of apps that will take your startup to the next level!

Flanco – for your office and property management

Flanco introduces itself as “the future of workspace” – and for good reason! It’s an office app that helps manage desk space and workplace resources. Need to easily book a desk or meeting room? Flanco has got you covered. Need to know which meeting rooms are booked in real time? Flanco comes to the rescue once again. Not to mention that the app itself has an intuitive interface and is fairly simple to use. For startups, it’s an all-in-one property manager. Effortlessly manage assets, accounting, vendor contracts, parking – Flanco has it all.

Slack – for your organizational communications

Slack is definitely king when it comes to communicating with the team, and doing so quickly and efficiently. A rock-solid communication platform will always be a crucial cog in the successful startup, especially when so many things are discussed on the go. Message people directly, create project-focused channels, or break into smaller chats to share key information with relevant stakeholders. Slack has searchable history and numerous app integrations that just make the job easier. In addition, you can set up reminders, add team members in the middle of conversations to keep them in the loop, and that’s only the tip of the iceberg when it comes to this app.

NordLayer – for your business privacy and security

Business cybersecurity is a must, period. In this day and age, when it comes to protecting your assets, customers, and team, there can be no shortcuts. Having your business fortified is essential – and NordLayer does just that and more. A robust network access security tool, it has numerous useful features like shared gateways for employees, DNS filtering, and other tricks to keep you secure. NordLayer will ensure that your company’s resources are protected and employees can securely access their work from anywhere. Furthermore, it offers a centralized control panel for convenient payment, features, and user management. Already have an existing company infrastructure? No worries, NordLayer can be easily integrated into Azure, Google Workspace, AWS and more.

Notion – for your docs and project management

Project management is no easy task, especially when there are multiple projects, deadlines and stakeholders involved. Want to keep track of the status of your project? Need to know what’s already been done? Notion is the tool you need. It’s useful for keeping tasks in order, and having workflows, docs, and guidelines in one place. You can create your own Wiki, and Notion even helps with building roadmaps and planning sprints. It’s a great tool for a neat and uncomplicated visual workflow in general. Another excellent feature is the ability to integrate it with Jira, Slack, Google Drive, and other apps for a truly seamless workflow.

Hootsuite – for your social media management

Let’s face it, competition is everywhere. If you’re running a business, social media is a tried-and-trusted approach to being seen, heard, and having a place under the sun. Social media is important for numerous reasons – increasing brand awareness, receiving direct feedback, customer engagement, and posting relevant content. However, managing multiple social media accounts can be a bit of a hassle. This is where Hootsuite comes in. This tool helps to schedule and publish content, monitor trends, and understand your audience. Everything can be done from a single handy dashboard, saving you precious time and resources.

Just the tip of the iceberg

This apps list for startups only scratches the surface of the myriad of possibilities out there. Depending on the category and profile of your business, there are dozens if not hundreds of apps and tools that could help you raise and maintain a successful business. These are just a few of what we think would be a good base to start out with, as they cover the most fundamental of needs. As mentioned previously, having the right tools can immensely help to stay on track, meet your goals, and simply be better organized – this is what tools are made for!


5 business apps for startup success in 2023

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Dumpster diving application memory

Penetration testers hunt for weak spots in applications so vulnerabilities can be fixed before bad actors find them. One way to find those weak spots is to inspect application memory to see if sensitive data is being stored in a way that hackers can access. In this article, we’ll explain how pen testers use the memory inspection process to strengthen app security.

What is memory inspection? Applications have memories — data that is generated from application processes is then stored within the app’s files, either on a device or in the cloud. If an app hasn’t been set up securely, a hacker could dive into those files and retrieve sensitive data.

White hat hackers — the people who hunt for vulnerabilities so they can be patched — can also use these same methods for good. By searching through the memories of mobile and desktop apps, as well as inspecting the installer file contents, they can unearth potential risks and keep users safe.

Dumping the memory

The first step in the inspection process is extracting the memory from an application. This is easily done on a Windows OS — we just open the task manager and create a dump file. On a Unix operating system, the relevant information is kept in /proc/<PID>/mem and /proc/<PID>/maps.

MacOS, on the other hand, requires us to boot into recovery mode and disable System Integrity Protection. This feature protects processes from being modified or tampered with. Having done this, we can then make a process dump.

Memory dumping gets a bit trickier when we approach mobile applications. Mobile devices usually require root privileges in order to extract the contents from an app’s memory with the help of the Frida tool.

After this step, we should be left with a “.txt” or a “.dmp” file which contains the extracted memory. It is a good idea to run this file through the “strings” utility to filter human-readable strings of a particular length because the dump might contain non-ASCII characters.

Searching for secrets

Once we have dumped the memory, we can start working with what we have. Primarily, we are now searching for information that reveals the following:

  • Session identification values

  • Access tokens

  • Service account credentials

  • Personally identifiable information

  • Authentication passwords

  • Database connection strings

  • Encryption keys and other master secrets

  • Data of a higher security classification than the logging system is allowed to store

  • Commercially sensitive information

  • Information that is illegal to collect in the relevant jurisdictions

  • Information a user has opted out of collection, or not consented to

The sensitive information listed above could be used by malicious actors for their own benefit. If this information is available through memory inspection, that’s a problem that needs to be fixed.

It would also be a good idea to use automated scripts that are able to pick out various access tokens, API keys, and any other values. For example, the following regex rule can be used to find AWS keys:

((‘|\”)((?:ASIA|AKIA|AROA|AIDA)([A-Z0-7]{16}))(‘|\”).*?(\n^.*?){0,4}((‘|\”)[a-zA-Z0-9+/]{40}(‘|\”))+|(‘|\”)[a-zA-Z0-9+/]{40}(‘|\”).*?(\n^.*?){0,3}(‘|\”)((?:ASIA|AKIA|AROA|AIDA)([A-Z0-7]{16}))(‘|\”))+

Source: I scanned every package on PyPi and found 57 live AWS keys | Tom Forbes

Understanding the risks

With many applications now storing data and running processes in the cloud, the risks posed by hackers who dumpster dive app memory are even greater. If bad actors can find service account credentials, Google API keys, and Firebase URLs in the dump, they could use these to their advantage.

Usually, service account credentials are used to retrieve an application’s remote configuration. If an attacker gets hold of valid credentials to access cloud systems that are improperly configured, no amount of firewalls can keep them from accessing the computing, network, and storage assets in that cloud environment.

It should be noted, however, that leaving account keys in the memory is not a problem as long as the IAM is configured correctly and the principle of least privilege is applied.

A penetration tester should pay close attention to the scope of tokens left in app memory as well as privileges to service accounts, both of which can be as dangerous as the exposed service account credentials.

Even if we do not find any security vulnerabilities, memory inspection is still worthwhile. We might discover unused tokens or accounts that are no longer needed, and deleting these can cut costs in addition to reducing security risks.

Fixing the vulnerabilities

The purpose of memory inspection is to find possible vulnerabilities and sensitive data that might be exposed. Afterwards, such vulnerabilities have to be fixed.

The principle of least privilege should be applied when resolving memory issues. Keep only absolutely necessary data and throw out everything else. This is a simple concept that will limit the potential for you to disclose sensitive information.

Checking application memory may be considered low hanging fruit in the cybersecurity world. However, any information stored or processed in a client’s memory is available to administrators and should be regularly checked from the vendor’s side.

We all make mistakes, and it is useful to carry out an inspection periodically. Doing so not only helps us to find and fix the errors but also deepens our understanding of the application’s inner workings.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.