Skip to content

How to reset your Nintendo password

Picture this: your evening is free, and you’re ready for some gaming to relax and unwind. But you can’t remember your Nintendo password. Just like that, your perfect gaming moment is spoiled. It’s a common frustration many gamers face.

However, there’s no need to worry. Resetting your Nintendo account password is straightforward and quick. In just a few steps, you’ll be back to your gaming world. Let’s dive into how you can regain access to your Nintendo account without any hassle.

Nintendo password reset guide​​

Let’s tackle the situation we’ve just described: you’ve forgotten your Nintendo password. The solution? A password reset. This guide will lead you through each step to creating your new password. Here’s how it’s done.

  1. Go to the Nintendo homepage

  2. In the upper right-hand corner of the screen select “Log in/Sign up.”

  3. Select “Log in.”

  4. In the login screen, click “Forgot your password?”

  5. Now enter your email address and click “Submit.”

  6. You’ll receive a password reset link in your inbox. Click the link.

  7. Before you can create a new password you will need to enter the birthdate or nickname associated with your Nintendo account.

  8. Now enter your new password and confirm it by reentering it once more.

  9. Click “Submit.”

That’s it! You’re all done and once again have access to your Nintendo account.

How to change your Nintendo password

Now, let’s consider a different situation. Perhaps you remember your Nintendo password but want to change it, maybe as a proactive security measure. Here’s how you can change your Nintendo password in just a few steps.

  1. Go to the Nintendo homepage.

  2. In the upper right-hand corner of the screen select “Log in/Sign up.”

  3. Select “Log in.”

  4. Once you’ve accessed your Nintendo account, select “Sign-in and security settings.”

  5. Under the “Password” section, select “Edit.”

  6. You may be prompted to confirm your identity by re-entering your password, re-authenticating with your passkey, and/or by verifying your email address.

  7. Now enter your new password and reenter it to confirm it.

  8. Click “Submit” to finalize the changes.

That’s it, you’re all done!

Set up a passkey for your Nintendo account

Passkeys are a new and more secure way for accessing apps and websites, including your Nintendo account. Moving away from the traditional username and password setup, passkeys enable authentication and access via biometrics like face scans, fingerprints, or screen lock PINs – similar to unlocking a personal device. The advantage of passkeys is in their simplicity: there’s nothing to remember, reducing the risk of forgotten login details.

If you’re interested in using a passkey to secure your Nintendo account, setting it up is simple. Let’s go through the process step-by-step.

  1. Go to the Nintendo homepage.

  2. In the upper right-hand corner of the screen select “Log in/Sign up.”

  3. Select “Log in.”

  4. Once you’ve accessed your Nintendo account, select “Sign-in and security settings.”

  5. Now select “Passkeys” and click “Edit”

  6. You may be prompted to confirm your identity by re-entering your password, or by verifying your email address.

  7. Now select “Register a new passkey.”

  8. When prompted, enter your Nintendo account password and select “OK.”

  9. Select “Register.”

  10. Follow the instructions on the screen to use your device to register the passkey.

  11. That’s it. Now you can start using that passkey when signing in to your Nintendo account.

Enhancing online security with NordPass: Password and passkey management

Every online account, no matter how insignificant it may seem, holds sensitive information. Consider your Nintendo account: it contains personal details like your date of birth, legal name, location, email, and payment information. In the wrong hands, such data could wreak havoc on your personal life. This is where a robust password manager like NordPass becomes invaluable.

NordPass offers advanced features such as password generation, two-factor authentication, and Password Health to ensure the safety and security of your passwords and — by extension — online accounts. More than just a password manager, NordPass allows for the secure storage of passkeys, payment details, personal information, secure notes, and files.

For anyone seeking to streamline password management and level up their online security, NordPass is an essential tool. It not only secures your digital life but also makes it more efficient and manageable.

FAQ

What are the requirements for my Nintendo password?

The Nintendo password requirements are as follows:

  • The password must be 8 to 20 characters long.

  • The password must contain a combination of at least two of the following categories: uppercase or lowercase letters, numbers, and punctuation.

  • The password cannot have the same letter or character more than twice in a row.

Is it necessary to change my Nintendo password regularly?

Opinions vary on the frequency of changing passwords. However, regularly updating your Nintendo password is a good practice to maintain its strength and security and generally can form great security habits.

Can I reset my Nintendo password without access to my email?

If you’ve lost access to the email associated with your Nintendo account, the password reset process becomes more complex. In such cases, you should reach out to Nintendo’s support team for assistance.

What should I do if I receive a suspicious activity alert?

If you receive an alert about suspicious activity in your Nintendo account, immediately change your password and activate additional security measures. Vigilantly monitor your account and report any further suspicious activities directly to Nintendo.

How does two-step verification enhance account security?

Two-step verification, also known as two-factor authentication (2FA), can significantly enhance account security by adding an extra layer of protection beyond the traditional username and password.

This method requires users to provide two different types of information to access their accounts. The first factor is defined by something they know, like a password or PIN, and the second is something they have, such as a smartphone app generating a code or a physical token.

The dual-layer approach makes it much harder for unauthorized individuals to gain access, as compromising two authentication factors is significantly more challenging than just one. Even if a hacker obtains a user’s password, they still need the second factor to break into the account.

Here’s how you can set up two-step verification on your Nintendo account.

  1. Go to the Nintendo homepage.

  2. In the upper right-hand corner of the screen select “Log in/Sign up.”

  3. Select “Log in.”

  4. Once you’ve accessed your Nintendo account, select “Sign-in and security settings.”

  5. Now select “2-Step Verification,” and click “Edit.”

  6. Click “2-Step Verification setup.”

  7. You may be prompted to confirm your identity by re-entering your password, or by verifying your email address.

  8. Install the Google Authenticator app on your smart device.

  9. Use your smartphone app to scan the QR code displayed on your Nintendo account screen.

  10. A 6-digit verification code will appear on your smart device. Enter the verification code and then select Submit.

  11. A list of backup codes will appear. Click Copy to copy all the codes, and save them somewhere safe.

  12. Select “I have saved the backup codes,” then click “OK.”

That’s it, 2-step verification has been successfully set up for your Nintendo account

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Is ChatGPT safe?

For many, artificial intelligence was a somewhat theoretical concept until OpenAI introduced ChatGPT. Released at the end of 2022, it needed only five days to surpass 1 million users. Within a year, over 180 million people around the globe now use this chatbot. For sure, plenty of people registered on openai.com simply out of curiosity. However, the number of ChatGPT daily users for private and work purposes is growing exponentially.

Usually, it’s the OpenAI tool answering our queries, but let’s do things differently today and actually ask ourselves two fundamental questions: “How does ChatGPT work?” and “Is ChatGPT safe to use?”

What is ChatGPT, and how does it work

ChatGPT, short for Chat Generative Pre-trained Transformer, is a chatbot that uses artificial intelligence to mimic human language and conversations. It’s a large language model that pulls data from large datasets. It uses deep-learning algorithms, including neural networks, to process the information and generate almost-human-like text answering users’ queries.

ChatGPT is not the first AI-based tool that made its way into our lives. However, there’s a significant difference between OpenAI’s child and Siri or Google Assistant: ChatGPT learns from us, humans. It may sometimes produce inaccurate or even biased information, but it gets smarter and more reliable with every prompt and piece of user feedback.

Now, let’s dive into the concerns related to ChatGPT security.

ChatGPT security concerns

We can put the safety concerns related to ChatGPT into a few different categories:

  • Data security risks

To talk with ChatGPT, a user must register on the creators’ website, chat.openai.com. The platform requires your name, email address, password, and phone number to create an account, and – if you’re going for the paid version – payment details. All the mentioned data will be available to and stored by OpenAI, possibly putting you at risk in case of a data breach.

OpenAI also collects chat history, which became available for other users during the ChartGPT 9-hour outage in March 2023. Later, OpenAI released a report stating that the bug in the open-source library also allowed unauthorized users to see the beginning of someone else’s conversations, account details, and payment information (including the four last digits of credit card numbers)! The company states: “The full credit card numbers were not exposed at any time,” but the leaked data may have put the chatbot’s users in danger of social engineering or phishing attacks. And there’s no guarantee that similar data breaches won’t happen again.

  • Misuse of ChatGPT

ChatGPT can produce many lines of code at a speed humans can only dream of. No wonder it became an everyday tool for many programmers, hackers included. The chatbot can generate code to create malware or detailed instructions on how to hack a computer, which, combined with dark web forums and programming skills, may be a powerful weapon in the hands of cybercriminals.

As another example of possible misuse, the tool created by OpenAI is also known for creating text in many different styles. If it can mimic an acclaimed writer, and it can easily generate a huge number of perfectly crafted phishing emails.

  • Scam ChatGPT applications

Before releasing an Android app at the end of July 2023, ChatGPT was only available on desktops and iPhones. However, apps masquerading as ChatGPT flooded the internet, spreading malware or making people pay for services OpenAI provides for free.

Since the roll-up of legitimate apps and the removal of scam ones, the risk connected with fake ChatGPT apps has decreased. Still, if you’re asking yourself, “Is ChatGPT safe to download?”, the answer is “Yes, but only from a reliable source.”

  • Spreading misinformation

ChatGPT is trained with vast amounts of data, including books, articles, and websites, and it reflects the opinions shared by the authors. It can generate text containing false or misleading information that may lead to prejudice and bias. In times of “fake news,” it’s vital to cross-check data. ChatGPT is no exception.

ChatGPT security measures

OpenAI seems to take ChatGPT security seriously. The company has implemented several measures to ensure the safety of chatbot users and their private information.

Access control: OpenAI limits access to its models and data to a select group within the organization to prevent data breach or misuse.

Encryption: Communication and data storage related to ChatGPT and other OpenAI models are encrypted to protect against unauthorized interception or access.

Monitoring and logging: OpenAI monitors ChatGPT usage and responds to any unusual or unauthorized activity.

Regular audits and assessments: The creators of ChatGPT conduct regular security audits and assessments to identify and address vulnerabilities, including internal and external reviews, to ensure a comprehensive evaluation.

Collaboration with security researchers: OpenAI also collaborates with the broader security research community, encouraging responsible disclosure of identified vulnerabilities.

User authentication: Users interacting with OpenAI’s most famous creation are required to authenticate their identities.

Compliance with regulations: OpenAI complies with relevant data protection and privacy regulations that ensure appropriate and secure data handling. Details and the company’s policies can be found on trust.openai.com.

Addressing bias: Bias in AI models can emerge from the data they are trained with and can reflect and perpetuate existing societal biases. OpenAI claims to train ChatGPT on diverse data sets that represent a wide range of perspectives and backgrounds. It also develops bias mitigation methods to identify and reduce biases in the chatbot’s answers.

How to use ChatGPT safely

ChatGPT’s security raises many questions and it certainly is not bulletproof. Check out our tips on how to stay protected while using OpenAI’s chatbot.

1. Avoid fake websites and apps

Always interact with ChatGPT via its website chat.openai.com, or its official mobile app. The fake applications may harvest your data, make you pay for functions that are supposed to be free, or even install malware on your device.

2. Secure your account with a strong password

Your account information and chat history are only as safe as your password. It should always contain more than eight characters, including upper- and lowercase characters and symbols. Use the online Password Generator to create complex and random login credentials and check how secure your current password is. Or, choose the easier way to safety: set up and manage login credentials in the NordPass password manager.

3. Don’t share personal information or content

Interactions with ChatGPT are not private. OpenAI can use your chat history for research and model improvement purposes which is why you should never share your personal, confidential, or sensitive information, such as passwords or financial details. Also, be cautious when discussing personal or sensitive topics, especially if they can lead to identifying you.

4. Cross-check the information and be aware of bias

ChatGPT reflects the opinions and biases of the data sets it’s been trained with. That’s why you should always cross-check the information the chatbot serves you with reliable sources and approach them with a healthy dose of skepticism.

5. Report issues

Provide feedback to OpenAI if you encounter any issues, biases, or inappropriate behavior with ChatGPT. To do that, log in to your account and use the “Help” button to start a conversation. If you don’t have an OpenAI account or can’t log in, go to help.openai.com and select the chat bubble icon in the bottom right.

FAQ

What is ChatGPT doing with my data?

OpenAI uses personal information to provide, maintain, improve, and analyze ChatGPT. The company also develops new programs and services based on user data and carries out business transfers. Note: According to its privacy policy, OpenAI may, in some instances, provide user data to third parties without further notice.

Does ChatGPT record data?

Yes, ChatGPT saves and stores user data, including:

  • Usage data (location, the time, and the chatbot version).

  • Log data (user’s IP address, the browser).

  • Device data (user’s type of device and operating system).

  • Content produced during the conversations with the chatbot.

Does ChatGPT sell your data?

OpenAI claims not to sell or share user data for marketing and advertising purposes. However, its privacy policy states that the company may share users’ private information with third-party vendors and service providers, which raises some concerns.

Is ChatGPT confidential?

No, ChatGPT is not confidential. The app logs users’ conversations and other personal data to train its model. OpenAI can also share users’ private information with third parties like vendors or legal authorities. The company claims to put a lot of effort into privacy policies, but there’s already been an incident when users’ data and conversation history were exposed.

Is ChatGPT safe to use at work?

The most considerable risk for enterprises is that people think ChatGPT is a tool to cut mundane tasks, something like a cutting-edge calculator. However, the information employees share with the free OpenAI chatbot can go into the cloud or be logged into its servers and revealed to different users during the conversation.

OpenAI offers an app for business, ChatGPT Enterprise, with dedicated privacy and security features. It doesn’t train on the company’s data, making it more secure for work.

Keep in mind that the business version of the chatbot doesn’t solve issues related to processing unreliable information or bridging the property rights of books, articles, and websites on which ChatGPT is being trained.

Is ChatGPT safe for kids?

ChatGPT is available for users over 13, and it’s unsafe for younger children to use it unsupervised. Despite the safety mitigations OpenAI implemented, there are many examples of the chatbot producing content not suitable for children.

Parents should also be wary of ChatGPT reproducing unreliable or biased information.

Is ChatGPT safe for students?

ChatGPT can be helpful for research but lacks critical thinking and analysis abilities. It can provide false information, so you should always cross-check it with reliable sources.

The OpenAI chatbot is being trained on books and articles whose ownership it doesn’t acknowledge, which can lead to copyright issues, plagiarism, and incorrect source quotations.

Should I use my real name on ChatGPT?

You should avoid sharing any private information while interacting with ChatGPT. Consider using a pseudonym or removing your name from the queries.

Why does ChatGPT need my phone number?

OpenAI needs your phone number for authentication purposes, to ensure you’re a real person, and to secure your account.

Remember, your private information, including the phone number, is unavailable to the chatbot itself. And you should never share this kind of info with it!

Can ChatGPT access any information from my computer?

ChatGPT is a text-based model that processes interactions on its servers. The model generates responses based on the input it receives, but it cannot access files on your device, or retrieve personal data from your computer.

There is some technical data that OpenAI automatically collects, like your log and usage data and device information. To find out more, check the company’s privacy policy.

How do I delete my chat history on ChatGPT?

To delete your chat history:

  1. Sign in to ChatGPT.

  2. Click your account icon on the bottom left corner of your screen (desktop) or in the menu bar (app).

  3. Choose “Settings.”

  4. Select “Data controls.”

  5. Click “Clear chat history” and then “Confirm.”

You can also remove a specific conversation by clicking its entry on the left hand-side and then choosing the trash can icon.

Can you delete your ChatGPT account?

You can submit a request to delete your account through privacy.openai.com or do it yourself.

To delete your ChatGPT account manually:

  1. Sign in to ChatGPT.

  2. Click your account icon on the bottom left corner of your screen (desktop) or in the menu bar (app).

  3. Choose “Settings.”

  4. Go to “Data controls.”

  5. Then, choose “Delete account” and “Confirm.”

Remember that after deleting the account, you won’t be able to create a new one using the same email address.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Quiz for Cybersecurity Awareness Month: 10 good-to-know facts about digital safety

Welcome to our Cybersecurity Awareness Month quiz! 

In an age where our digital footprints are larger than ever, understanding the importance of cybersecurity is vital. This quiz is designed for companies and their teams to enhance their digital safety knowledge, adopt new practices, and remain vigilant against evolving digital threats.

Are you ready to test your cybersecurity knowledge and learn some essential facts along the way? Let’s go!

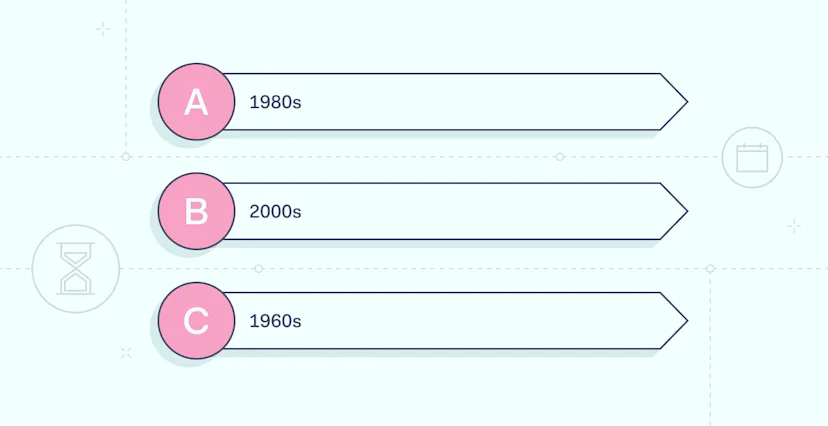
1. When was Cybersecurity Awareness Month first celebrated?

Cybersecurity Awareness Month quiz 10 1400x720

Correct answer: October 2004

Cybersecurity Awareness Month was first celebrated in October 2004. Two decades ago, the President and the Congress of the US declared October the official Cybersecurity Awareness Month.

The idea behind it is to dedicate a month to raising awareness about the importance of cybersecurity, educate individuals and organizations about online threats and best practices, and promote a safer digital environment.

Over the years, this initiative helped individuals become more vigilant about online security, encouraged organizations to invest in cybersecurity measures, and fostered collaboration among governments, businesses, and the public in addressing cyber threats.

2. What’s the name of the first cyber attack?

Correct answer: Morris Worm

In November 1988, a graduate student named Robert Tappan Morris created the Morris Worm, one of the first computer worms.

Originally intended to measure the size of the internet, a coding error caused it to replicate uncontrollably, infecting thousands of computers.

This incident exposed vulnerabilities in early internet systems, led to the Computer Emergency Response Team (CERT) creation, and underscored the need for improved cybersecurity practices in the digital world.

3. When was the first antivirus software created?

Correct answer: 1980s

The first antivirus software, known as “Elk Cloner,” was created in 1982 by a high school student named Rich Skrenta.

Unlike modern antivirus tools, Elk Cloner was designed to protect Apple II computers from a playful prank: it spread by attaching itself to floppy disks and displayed a humorous poem upon activation.

While it was more of a benign experiment than a comprehensive antivirus solution, Elk Cloner marked the early beginnings of efforts to protect computers from malicious software.

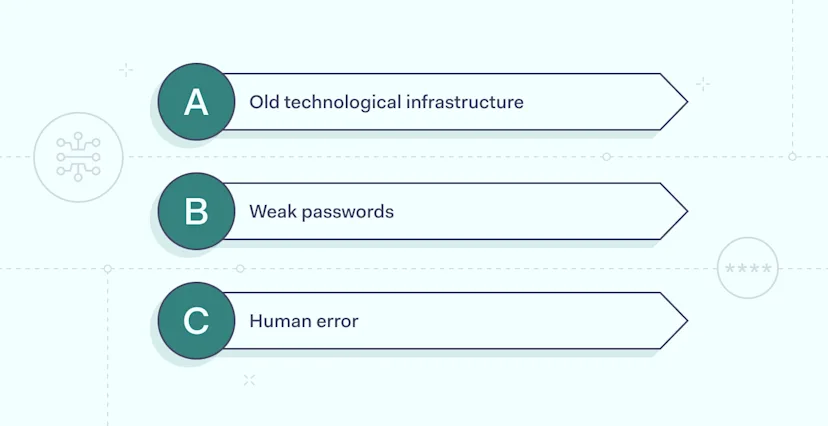
4. What is the most common cyber threat?

Correct answer: Human error

Human error is the most common and pervasive cybersecurity threat. It occurs when individuals inadvertently make mistakes that compromise the security of digital systems and data. These errors can range from clicking on malicious links in phishing emails to unintentionally sharing sensitive information on public forums.

Human error is responsible for 85% of data breaches and security incidents, often leading to financial losses, reputational damage, and legal consequences for individuals and organizations.

Mitigating this threat requires a combination of user education, training, and implementing safeguards such as multi-factor authentication (MFA) and robust data protection policies based on the Zero Trust model.

5. How much did a ransomware attack cost for businesses on average in 2023?

Correct answer: $4.54 million

According to the IBM Data Breach Report of 2023, the average cost of a ransomware attack was $4.54 million. It’s challenging to pinpoint it precisely due to the many factors involved. However, it is commonly estimated to be in the hundreds of thousands to several million dollars.

These costs encompass the ransom payment (if made) and expenses related to data recovery, cybersecurity improvements, legal assistance, regulatory fines, and the significant operational disruptions that often follow such an attack.

Ransomware is one of the most malicious types of cyber attack, as the true cost can also be considerably higher when considering the long-term reputational damage and loss of customer trust.

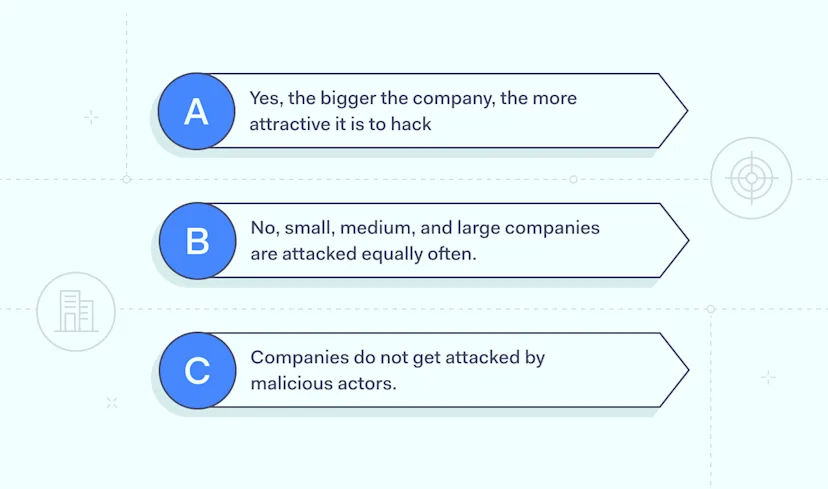
6. Does company size matter for a malicious actor wanting to attack?

Correct answer: No, small, medium, and large companies are attacked equally often.

The size of a company doesn’t necessarily deter malicious actors from targeting it. In fact, small and medium-sized businesses are often targeted because they may have weaker cybersecurity defenses compared to larger enterprises.

Additionally, attackers might exploit smaller organizations as stepping stones to reach more substantial targets in supply chain attacks. Ultimately, cybercriminals consider factors such as vulnerabilities, potential rewards, and ease of access more than company size when deciding whom to target.

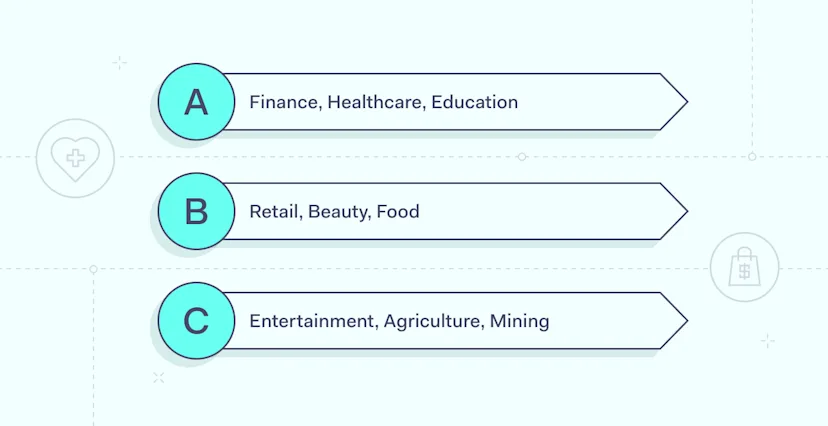
7. Top 3 industries that are the most vulnerable to cyber attacks?

Correct answer: Finance, Healthcare, Education

The finance industry is highly vulnerable to cyberattacks due to the vast amounts of valuable financial data it handles. Cybercriminals target banks, payment processors, and stock exchanges to steal funds and sensitive information.

In healthcare, the sensitivity of patient data and the increasing use of interconnected medical devices make it a prime target. Breaches can lead to identity theft, medical fraud, and even endanger patients’ lives.

The education sector faces threats as it increasingly relies on online learning platforms and stores student information. Cyberattacks in this industry can result in data breaches, educational disruptions, and the theft of personal information. Proactive cybersecurity measures are crucial for safeguarding the vulnerable education sector.

8. What does a strong password look like?

Correct answer: m#P52s@ap$V.

Strong passwords should mix upper and lower-case letters, numbers, and special symbols. Avoid easily guessable information like birthdays or common words. Never reuse passwords across multiple accounts. Each account should have its distinct, strong password to prevent a breach in one account from compromising others.

Change your passwords periodically, especially for sensitive accounts. This minimizes the risk in case a password is ever compromised.

Best cybersecurity strategies strongly recommend considering a password manager. It can generate and store complex passwords for you, making it easier to manage multiple secure logins without remembering them all. To make it even more resilient for breaches, combine passwords with MFA use.

9. What do you do if you receive an email from an unknown sender?

Correct answer: Don’t open it. If you did, don’t click on anything.

Phishing is leading the Top cyber incidents list of 2022. Phishing usually starts from an email. So, learning to recognize one is extremely important.

Here’s what to do if the email seems suspicious. First, avoid clicking on any links or downloadable attachments – they could be malicious. Then, take a close look at the sender’s email address. If it looks suspicious or doesn’t match the supposed sender, be cautious. Finally, always check for strange language, misspellings, or urgent requests. These can be signs of phishing attempts.

If the email claims to be from a company or organization, verify it independently by contacting the sender directly via alternative channels. Don’t use contact information from the suspicious email.

Mark the email as spam or junk to help train your email provider’s filters. If you’re unsure, it’s safest to delete the email. You can report it to your email provider or IT manager if it seems like a phishing attempt.

10. What does the acronym VPN stand for?

Correct answer: Virtual Private Network

A VPN, or Virtual Private Network, is like your digital secret tunnel to the internet. It keeps your online activities private and secure.

It does two cool things. First, it hides your online footprints from the snoopy eyes of malicious actors and advertisers. Second, it makes you look like you’re browsing from a different place, which is awesome for unlocking content or staying safe on public Wi-Fi.

Think of a VPN as your digital disguise. When you connect to one, it encrypts your data and sends it through a secure server in another location, masking your true identity and protecting your data from prying eyes like an online invisibility cloak.

Well done!

Congratulations on completing our Cybersecurity Awareness Month quiz! Your dedication to improving your digital safety knowledge is commendable. Remember, the world of cybersecurity is ever-evolving, and staying one step ahead of digital threats is an ongoing journey.

We encourage you to keep learning, stay vigilant, and explore additional resources to deepen your understanding of cybersecurity. Share what you’ve learned with your colleagues, friends, and family to help create a safer digital environment for all.

By working together and remaining proactive, we can strengthen our collective defenses against cyber threats and continue to adapt to the continuously shifting digital landscape. Thank you for taking the quiz and being a cybersecurity champion!

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Evolution of cyber law: how the NIS2 Directive shapes Europe’s security landscape

Ever wondered why even tech giants like Google approach European internet laws with caution? The answer is the Network and Information Systems (NIS2) Directive, a beacon in the world of internet safety.

The old rules, laid down in 2016 by the NIS Directive, fell short of safeguarding against cyber threats. While they addressed sectors like healthcare and energy, many industries remained uncovered. But now, the tables are turning. The new NIS2 Directive creates a unified EU front against cyber risks, rewriting the rules for this new digital age.

In this piece, we’ll explore how the NIS2 Directive reshapes the cyber security landscape in Europe and what it means for businesses and governments. Learn how to navigate this evolving terrain and stay compliant without incurring penalties.

The need for evolving cyber law in Europe

It’s no secret that online threats have transformed into something far more sinister than we could have imagined. The time has come for Europe to embrace new cybersecurity legislation that will effectively combat the complexities of these threats. This section will explain how online risks have evolved and why new laws are required.

The changing face of cyber threats

In the past, cyber threats were mainly the work of individual cybercriminals. They were like digital graffiti artists, tagging websites and perhaps swiping some data for their bragging rights.

Now, things are more severe. We face organized groups, and sometimes even governments, harnessing the power of cyber attacks. The objective? Stealing vast amounts of data or causing disruption of critical services.

These aren’t just one-off events anymore. Cyber threats have turned into ongoing campaigns targeting sectors like energy or healthcare. With the omnipresence of the internet in everything from our refrigerators to our cars, the risks have infiltrated every nook and cranny of our lives. The cybersecurity landscape has changed, and Europe needs to update its legislative arsenal to counter these digital dangers effectively.

Time for an upgrade: why the old NIS Directive isn’t enough

Back in 2016, the European Union took its first step in the battle for cybersecurity with the Network and Information Systems (NIS) Directive. It was a start, but it soon became evident it had limitations.

For one, it only covered specific sectors, like energy and healthcare. Many other industries that could be vulnerable to cyber-attacks were left out.

Moreover, the directive’s implementation was a patchwork quilt. Each EU country adopted its own interpretation of the rules. This inconsistency meant that while one nation might be doing a great job fortifying its cybersecurity defenses, its neighbor might lag behind.

In short, the old rules weren’t enough, and it was time to bridge the security gaps. This is where the NIS2 Directive stepped in to address them.

Far-reaching impact of the NIS2 on cybersecurity

NIS2: fixing the flaws of its predecessor

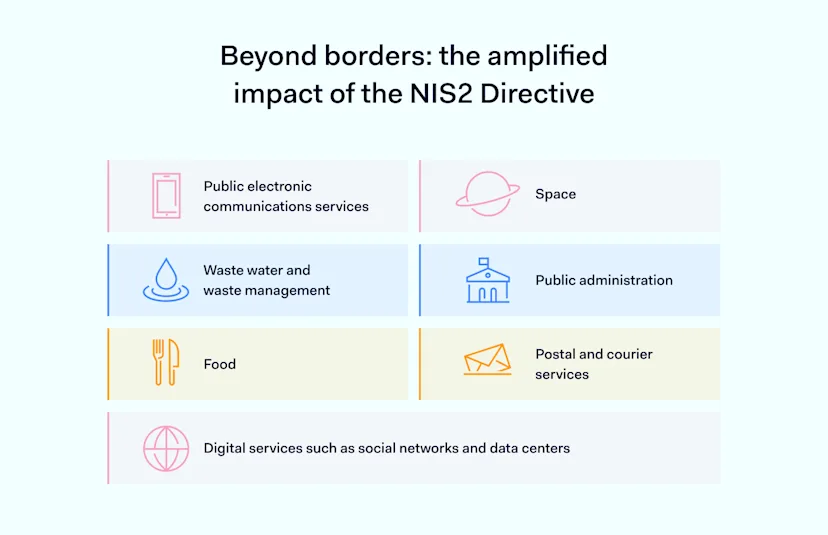
The new and improved NIS2 Directive is Europe’s upgraded plan to make the digital world safer. Unlike the old rules, NIS2 covers a lot more ground. Financial services, public administration, and digital platforms all come under its umbrella.

That means more types of companies have to follow the rules and take measures to safeguard their digital assets. But it’s not just about adding more sectors. NIS2 also brings greater unity among EU countries regarding cybersecurity.

Instead of each country making its own rules, NIS2 established baseline requirements that apply everywhere. This way, the EU can act like one big team in defending against cyber threats, making everyone’s digital life safer.

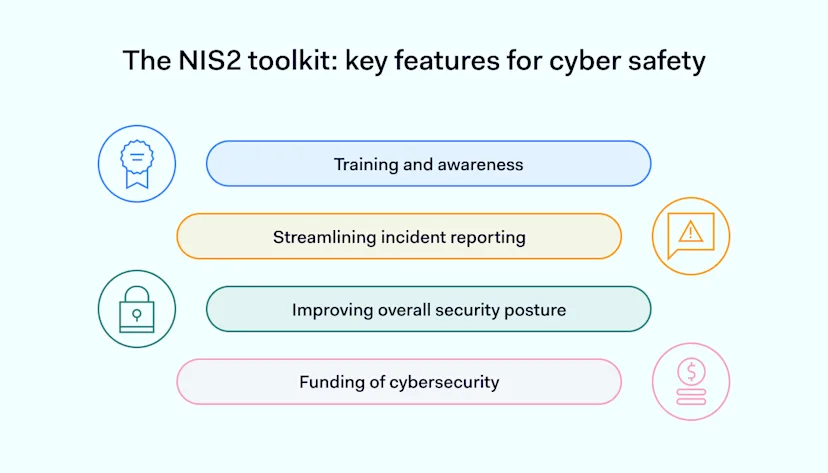
The NIS2 toolkit: key features for cyber safety

So what’s new in NIS2? First, companies must put in specific security measures that match the cyber risks they face. It’s not a one-size-fits-all solution, but it’s more about adapting to the situation at hand.

Training and awareness

While NIS1 has a nod to raining and awareness-raising, NIS2 takes up a notch, possibly requiring more structured training programs. Organizations must show evidence of ongoing training and be subject to audits to ensure that employees are well-prepared.

Streamlining incident reporting

While NIS1 encouraged incident reporting, the requirements weren’t very specific. Organizations were generally advised to have some form of incident reporting but were given more latitude in implementing it.

But NIS2 steps up its game in incident reporting. It aims to standardize procedures with specific timelines, formats, and more detailed reporting requirements. The goal is to make incident reporting more efficient, ensuring quicker response and better mitigation.

Improving overall security posture

Previously, organizations were encouraged to improve their cybersecurity measures continuously, but the directive wasn’t very prescriptive about how this should be done.

NIS2 pushes organizations to enhance their security posture continuously. This could mean more frequent audits, detailed reporting, and specific milestones to demonstrate progress.

Funding of cybersecurity

While NIS1 hinted at the importance of adequate funding for effective cybersecurity, NIS2 goes further, emphasizing the need for ample financial resources for cybersecurity. Organizations may be required to allocate a specific percentage of their budget to cybersecurity or meet minimum spending requirements.

Plus, NIS2 has stiffer penalties for companies that fall short of compliance. This gives companies a solid reason to take cybersecurity seriously.

Now that we’ve uncovered what NIS2 brings to the table, let’s explore how it impacts businesses and government offices in the next section.

The NIS2 impact: what businesses need to know

The legal framework

The NIS2 Directive isn’t just another set of guidelines, it’s the law. Medium-sized and large enterprises should understand that compliance isn’t an option but a legal requirement. And it’s not just about avoiding penalties. It’s about fortifying your business infrastructure to protect valuable assets and customer data.

Cost of compliance vs. cost of non-compliance

Yes, implementing the NIS2 Directive requires an investment in time, personnel, and resources. But think about it this way: the cost of non-compliance, including legal repercussions and potential loss of consumer trust, can be much more damaging to your bottom line and reputation.

The Directive is designed to create a safer digital environment that can serve as a unique selling proposition for customers who value data privacy.

Long-term gains: beyond just avoiding penalties

NIS2 compliance is an investment in the future. While the initial setup may demand resources, robust cybersecurity measures can significantly reduce the risk of data breaches and cyber-attacks, both financially devastating and detrimental to a company’s reputation.

Maintaining a secure digital ecosystem can become your competitive edge in a world where data leaks or breaches make headlines.

Cybersecurity is a public concern: the NIS2 Directive mandates it

For public administration entities, cyber security isn’t just about protecting sensitive data. It’s about safeguarding the lives and well-being of millions. A cyber-attack on a government body isn’t just a headline, it could lead to a national emergency.

Under the NIS2 Directive, these organizations must improve their cybersecurity to prevent such potential disasters.

Layers of government: everyone is affected

It’s not a one-size-fits-all solution. Public administrations, from central to regional and local levels, must go beyond mere software upgrades. The NIS2 rules demand a comprehensive review and transformation of how these entities manage data, deploy security protocols, and respond to incidents. No matter the size or scope of the government body, compliance with these new measures is essential.

Holistic approach to cybersecurity

Public administration entities must adopt a holistic cybersecurity strategy that addresses risk assessment, preventive measures, and contingency planning. This comprehensive approach ensures that damage can be minimized in the event of an attack, and normal operations can swiftly resume.

Even if your company is not based in Europe, you can’t ignore Europe’s online safety rules if you’re doing business there. The rules are like a digital handshake, mandatory for anyone offering digital services or handling data in the EU.

Crossing borders: NIS2’s reach beyond Europe

So, what does it mean for global businesses? If your company has its headquarters halfway across the globe, you’re in the spotlight, too. You must follow these new rules when operating in Europe. But don’t worry, it’s a fantastic opportunity. Following these guidelines can signal to European customers that you take security seriously, boosting your appeal. But, word of caution: getting the details right is crucial because the penalties for messing up can be steep.

Global players: future implications and representative requirements

Under NIS2, you can’t simply wing it. If you’re a foreign company doing business in the EU, you need a representative in the EU. They’re your go-to for ensuring all these rules are followed. And it’s not just a formality, it’s a crucial role.

But here is the exciting part: the implications for the future are significant. Global standards like NIS2 might become the norm as the digital world grows. Companies that get it right in Europe now will be a step ahead of the game when similar laws start popping up in other parts of the world.

Now that we’ve covered the new rules and who they apply to, our next section will dive into best practices for organizations to ensure they stay on the right side of the new guidelines.

NordLayer: your NIS2 compliance partner

Navigating the complex world of NIS2 compliance is like solving a puzzle. And while NordLayer may not be the whole solution, it can help you tick off several boxes on your compliance checklist all at once.

NIS 2 legislation, in Article 5, calls for digital service providers to employ suitable technical and organizational measures to secure their networks and information systems. Virtual Private Networks (VPNs) can be particularly helpful in meeting the “appropriate and proportionate” security measures outlined in Article 5.

Specifically, NordLayer offers a secure tunnel between an employee’s device and the corporate network. This ensures that sensitive data, like customer information or intellectual property, is shielded from unauthorized access. This is a powerful step towards managing network and information system security risks, as NIS2 demands.

Article 16 of NIS 2 emphasizes secure data transmission as a core compliance aspect. And here is where VPNs play a crucial role. They encrypt data during transit between different locations or systems. This encryption aligns directly with the article’s requirements to protect against unauthorized access and data tampering. With NordLayer, you’re well on your way to meeting the “technical and organizational measures” stipulated in this article of NIS 2.

In conclusion

We’ve discussed the necessity for Europe to modernize its cybersecurity laws through the NIS2 Directive. This transformation impacts not just IT teams but entire businesses. As the EU unfolds these comprehensive new guidelines, the responsibility falls on organizations to adapt accordingly.

Don’t hesitate to reach out and explore how NordLayer can be a valuable addition to your cybersecurity arsenal, assisting you on your journey toward alignment with the EU’s evolving digital laws.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

How to manage passkeys on Apple devices

Apple’s entrance into the world of passkeys began with iOS 16, which marked the introduction of this technology within the ecosystem. By the time iOS 17 rolled out, Apple had seamlessly woven passkey support for Apple ID and started allowing third-party apps such as NordPass to manage passkeys on mobile devices.

Now Apple users no longer need to remember their Apple ID password and can access and use passkeys outside the ecosystem, on any device, at any time.

This progression isn’t just about technological milestones. It paints a picture of a future where our digital interactions are both more secure and more intuitive.

Today we’ll unpack the nuances of the passkey technology and explore and showcase how easy it is to enable, store, and manage passkeys on the NordPass iOS app.

How passkeys work

Before we get into the ins and outs of passkeys, let’s start with passwords. Passwords, while familiar, come with a set of challenges, issues, and potential risks. Weak or reused passwords have been behind more than 80% of security breaches in the past few years. Passkey technology, however, offers a much more secure and hand alternative to traditional passwords.

At the heart of this technology is a dual-key mechanism. When you opt for a service that supports passkey authentication, two cryptographic keys work in tandem: a public key, which is stored on the service’s server, and a private key, kept securely on your device. The beauty of this pairing is its dependency — one key is ineffective without the other.

The authentication process is multi-layered. During login, the server sends a request to your device, which responds with the corresponding passkey. Your identity is then verified at the device level, often through extra layers of authenticity such as biometrics like Face ID or Touch ID. Access is granted only when both keys match and biometric verification succeeds.

This approach offers enhanced security on multiple fronts. Passkeys are resilient to phishing and eliminates the issues of password reuse or forgetfulness. Yes, with passkeys you don’t need to remember or type out crazy strings of characters. The added layer of biometric verification ensures that even if your device is compromised, your data remains out of reach. Passkeys are here and they are taking over for good reason.

How to enable passkeys on iOS devices

With the introduction of iOS 17, Apple has made it even more convenient for users to embrace the security of passkeys. Integrating this feature into your daily routine is simple, especially with the help of NordPass. Keep in mind that support for passkey management on NordPass is available only for devices running iOS17 and iPad OS17 or later.

Here’s a step-by-step guide to enabling passkeys of your iOS device:

  1. Download and install NordPass on your iOS devices.

  2. Go to the “Settings” on your device.

  3. Scroll down and select “Passwords.”

  4. Authenticate your identity as prompted.

  5. Now, tap on “Password options.”

  6. Browse and select “NordPass.” A checkmark will appear, indicating it’s enabled.

  7. Finalize the process by unlocking the NordPass vault.

That’s it, you’ve enabled passkey-based authentication on your iOS device.

How to save and use passkeys with NordPass on iPhone

Harnessing the power of passkeys through NordPass on your iPhone is a step towards a more secure and smooth online experience. This feature simplifies the login process, ensuring both convenience and protection. Here’s how you can make the most of it.

Saving a passkey in NordPass:

  • Navigate through websites or apps as you typically do.

  • Be attentive to sites or apps offering passwordless login options.

  • When presented with an option to use a passkey or integrate one into an account, choose it.

  • A NordPass prompt will emerge, guiding you to save the passkey.

  • Follow the provided steps to ensure it’s securely stored.

Logging in with a stored passkey:

  • Access the website or app where you’ve saved the passkey.

  • Select the passwordless login feature.

  • NordPass will prompt you to use the stored passkey.

  • Adhere to the on-screen guidelines to authenticate and access your account seamlessly.

By joining the passkey revolution, you position yourself at the center of the seamless and secure online life. Try it today!

How to manage passkeys in NordPass

Navigating the online world can be a daunting experience. However, with the introduction of passkeys, the process has become not only more secure but also more user-friendly and instant. Let’s delve into how you can manage passkeys using NordPass.

What can you do with a passkey in NordPass?

  • View passkey creation date. NordPass allows you to see when a particular passkey was created. This feature provides an added layer of transparency, ensuring you always know the age of your digital keys.

  • Share passkeys safely. With NordPass, sharing passkeys is quick and intuitive. Whether it’s for business or personal use, you can securely share your passkeys with trusted individuals without compromising security.

  • Add secure notes. Alongside your passkeys, NordPass provides the option to add secure notes. This feature is especially useful for adding extra information or reminders related to a particular service or account.

Why choose NordPass for passkey management?

NordPass isn’t just another password manager. It’s a comprehensive digital life manager for those on the go. With the introduction of passkeys, NordPass further pushes the envelope of what a password manager can be.

All NordPass users can now store and manage passkeys, ensuring they can access apps and websites securely. NordPass also syncs your passkeys across all devices and operating systems. Unlike many other password managers, NordPass offers seamless sharing of passkeys, making it a top choice for those who prioritize both security and convenience.

Furthermore, NordPass is actively working towards a passwordless future. We support passkey storage but are also in the process of introducing passwordless access to the NordPass app. This means you will soon be able to access your Nord Account and NordPass with just a tap, thanks to biometrics.

In a rapidly evolving online world, it’s crucial to stay ahead of the curve. With NordPass, you are not only equipped with the latest in security technology but are also prepared for the inevitable shift towards a passwordless future.


Login experience
Now that you’re signed-up for an online service with a passkey, logging in is quick, easy and secure. All you need to do is tap the suggested passkey for that account and you are logged in.

How do passkeys work? 
Understanding passkeys and how this technology works can be somewhat tricky, mostly because passwords have been an integral part of our digital lives for so long. So first let’s recap the old and familiar before getting into passkeys. By the end we should understand the whole passkeys vs. passwords deal and why passkeys are the way of the future.

Password technology explained
Passwords — we know them all too well, and most of us have some idea of how they work. But let’s quickly recap.

Password-based authentication is relatively simple and straightforward. Say you create a password for a new online account. That password is then stored in an encrypted format on a server. When you use the password to access that account, the system compares the password you enter with the one in its database. If the two match — you’re good to go.

Simple, right? Well the catch is that this kind of user authentication presents quite a few serious security concerns. People tend to reuse simple and easy-to-crack passwords for multiple accounts, which is a hacker’s dream — crack a single account and you have access to a person’s entire digital life. Databases that store passwords can be breached. In fact, Verizon’s Data Breach Report notes that up to 80% of successful breaches are attributed to weak or stolen passwords.

Passkey technology explained
You can think of passkeys as a new and improved type of password. Both are used to verify a user’s identity upon sign up and login. However, the technology behind passkeys operates in a different way.

Whenever you sign up for an online service which supports passkey authentication, two keys are generated — public and private, both of which are used to authenticate the user when logging in.

The public key is stored in the website’s server, while the private key is stored on your device, whether it’s a phone, tablet, desktop, or laptop. Without each other the two keys are useless.

Upon logging in, the server sends a request to your device, and that request is then answered by a related passkey. The user’s identity is also verified on the device level via biometrics. Finally if the pair of keys match you’re granted access to your account.

Passkeys are widely considered to be a more secure and convenient form of authentication compared to passwords, as they reduce the risk of forgetting or reusing passwords. Passkeys are also resistant to phishing attacks as they can’t be stolen from your device by a third-party.

Store passkeys with NordPass 
All NordPass users now have the ability to store and manage passkeys in NordPass and use them to access apps and websites. NordPass syncs your passkeys across all of your devices as well as operating systems and enables you to safely share passkeys whenever needed. It is important to note that sharing passkeys is not as easy with alternative systems as it is with NordPass.

We’re excited to let you know that with the release of iOS 17, passkey storage is now available on NordPass app for iOS devices. This is a monumental step for us, ensuring that you, our users, enjoy a seamless experience across all platforms and devices.

In addition to mobile access, you can also reach your passkeys on NordPass via the desktop app, web vault, Firefox, and Chrome-based browser extensions. We’re also thrilled to share that support for the Safari extension is on the priority list and will be launched later this year.

Password managers are highly reliant on platform vendors when it comes to passkey technology. Therefore, we welcome the latest move from Apple because it serves as a huge milestone in replacing passwords with more advanced online authentication solutions. With tech giants allowing third-party integrations, internet users will get more user-friendly services and, as a result, will be more keen to stick to using passkeys

– Sorin Manole,

Product Strategist @ NordPass

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.