
Skip to content

NordLayer use case: internet access security

Modern businesses heavily rely on internet access for communication and collaboration. This also makes it the #1 channel for cybercriminals trying to access sensitive data. This modern threat landscape is a critical cybersecurity challenge that businesses must be aware of and be prepared to defend against.

Therefore, in this blog post, we’ll discuss the importance of internet access security for businesses operating in all work models, including remote, office, and hybrid. With the number of cyberattacks ramping up, it’s crucial not to hope for the best and believe it will never happen to your company.

What internet access security challenges affect businesses?

Businesses hold and manage large amounts of sensitive data, including customer information, financial data, and trade secrets. If this information isn’t properly secured, unauthorized users can obtain access to it, causing a data breach.

Now, these challenges are even harder to avoid because after the pandemic many businesses have adopted different work models. As a result, secure internet access can mean completely different approaches and unique sets of challenges.

Remote work challenges

During the COVID-19 pandemic, remote work has been the norm for many companies. Even after the quarantines had ended, many businesses kept working from home. While remote work brings benefits and flexibility, it also comes with challenges.

Use of personal devices

The practice of employees bringing their own device for work-related tasks, known as (BYOD), became widespread during the pandemic. Employees hired remotely usually had no personal contact with IT administration, so they worked with their home devices.

The risk lies in the fact that they’re unmanaged and may lack the same level of security as company-issued devices. These circumstances leave them vulnerable to all kinds of attacks, with limited capabilities for IT administrators to stop them.

Unsecure networks

Home networks may not have the same level of security as properly managed corporate networks. Employees using outdated or vulnerable network devices are more susceptible to exploits that hackers could use to gain entry into company systems.

Remote employees are solely responsible for securing their own devices, but they may not always have the necessary knowledge to do it effectively. This also allows hackers to initiate phishing messages or cause disruptions.

Access control

When allowing employees to work remotely, a security policy should clearly state how and who can access sensitive data. Without such a policy, organizations may fall into the trap of being unable to verify who is accessing their networks or data. This is a sure route to costly data breaches and reputational damage.

In addition, compliance regulations like GDPR and HIPAA require organizations to have robust access control policies to protect sensitive data. Failure to do so may result in legal liabilities and hurt business financially.

Office work challenges

While working in the office seems more secure than remote work in most managers’ eyes, it’s not immune to various security threats. In fact, several cybersecurity risks may be more prevalent for employees working in an office than in other models.

Social engineering

Social engineering attacks target the human aspect of security, making them harder to detect and prevent. Very little stands in a dedicated hacker’s way if they plan out a fake identity, impersonating legitimate employees, and using other psychological tactics. For example, tailgating is based on following a genuine employee through the door without authorization.

Employees in an office environment have physical access to sensitive documents and data. This can mean that once a hacker is inside the building, all the sensitive data can be compromised (or stolen).

Insider threats

While network segmentation helps to introduce boundaries that prevent users’ lateral movement in the network, all these boundaries are much more fluid in an office setting. Employees may write their passwords on sticky notes and leave them on their desks, which is something that malicious colleagues could exploit.

In-office identity thefts and malicious leaks may be harder to stop or detect. Additionally, deliberate leaks or theft of physical documents and devices by someone working on-premises are scenarios that an IT manager should prepare for.

Hybrid work challenges

Hybrid work, which combines remote and office models, adds up challenges from both approaches. Employees must be provided with secure methods to connect to hosted resources when working remotely. Meanwhile, when they’re back in the office, they need to be vigilant about risks they could be lurking in shared spaces. This makes the hybrid model the most difficult to secure.

Double the maintenance

Hybrid work puts a huge strain on IT administrators. They must simultaneously support and manage two fronts: office employees must be provided with secure network access when working on-premises and remote employees must be provided with secure routes into their network.

Both modes must be compatible, operate without interruptions, and be secure. It’s an intricate system with many moving parts, so naturally, it’s much harder to supervise.

Increased physical security risks

Hybrid employees carry work devices back and forth between the office and their homes, increasing the risk of theft or loss. A lost device may not be a serious risk if properly secured with strong passwords or encryption. However, if not, it could easily lead to a data breach.

Additionally, working in public areas or during transit increases the potential for shoulder surfing attacks, when an attacker can physically view the device screen. As the attacker needs to be physically close to their victim, this has become quite prevalent with the growing popularity of hybrid work models.

Why is internet access security important for businesses?

Modern-day enterprises heavily rely on the internet to enable all kinds of their operations. As a result, its secure access is important, regardless of the connection method an organization uses. Achieving secure internet access also enables businesses:

  • Protecting sensitive information. Unsecured communication channels may lead to the loss of sensitive information, which could be disastrous for a company’s reputation and cause legal complications.

  • Mitigating cyber threats. Mostly, the internet is a publicly used platform, and it exposes businesses to various risks like malware, phishing, and hacking attempts.

  • Complying with regulations. Many industries are subject to regulations requiring them to maintain strict security measures. Failure to comply can result in heavy fines or legal repercussions.

  • Ensuring business operations continuity. Cyberattacks have the potential to disrupt day-to-day business operations, leading to downtime and lost revenue.

By tackling internet access security challenges, businesses can avoid risks and establish a proper foundation for uninterrupted growth and operational continuity.

How do businesses secure their internet access against various threats?

Securing work environments against threats can vary depending on the business size and risks faced by businesses. Some companies have the manpower and resources to build their own in-house solutions. Others take the simplest approach and turn to a third-party provider adopting their already established tools. Here are two real-life examples.

Whatagraph

A digital marketing reporting platform, Whatagraph transitioned to a hybrid work model when faced with the challenge of local talent shortage. This also meant that they needed to figure out how to allow their remote hires to connect securely to their infrastructure. A comprehensive cybersecurity solution establishing a private gateway to the company’s data and applications was an obvious choice. As Whatagraph is a rapidly scaling company, the solution must also integrate admin features and provide uncomplicated scaling.

To address their needs, Whatagraph turned to NordLayer, using it mainly as a business VPN back when it was still called NordVPN Teams. They leveraged NordLayer’s Virtual Private Gateways with dedicated IP addresses to securely connect to their company network, sealing the sensitive data in an encrypted tunnel.

What also helped was that NordLayer seamlessly integrated with their existing solutions, eliminating the need for additional technical integration. This provided Whatagraph with optimal internet access security within minutes.

Atlantis Games

A mobile game development company, Atlantis Games, found themselves trapped in a corner when manual user handling ways weren’t keeping up with their growth. Initially, their setup was manually allowlisting individual users’ IP addresses, which worked for a small team. However, once a business expanded and developers and customer support specialists needed multiple IP addresses, the manual approach proved to be too much of a task.

NordLayer came to the rescue by providing a smoothly running client with uninterrupted connections. By using Virtual Private Gateways with IP allowlisting for organization members, Atlantis Gamest eliminated the need for manual maintenance or in-house hardware purchases. Plus, they were able to segment teams by projects and allowlist their IP addresses accordingly. The setup mitigated the data breach risk and introduced more granular data access controls.

As the tool seamlessly integrated with their existing company cloud systems, the transition was smooth and freed them from tedious manual management. This resulted in a more efficient and secure connectivity model with additional NordLayer features.

Actionable tips and best practices

Businesses must handle the data that they hold responsibly, not only to fulfill their promise to their clients, but also to meet requirements from the government bodies. By following best industry tips and practices, organizations can help prevent cybersecurity incidents and mitigate the risk of lawsuits and financial penalties.
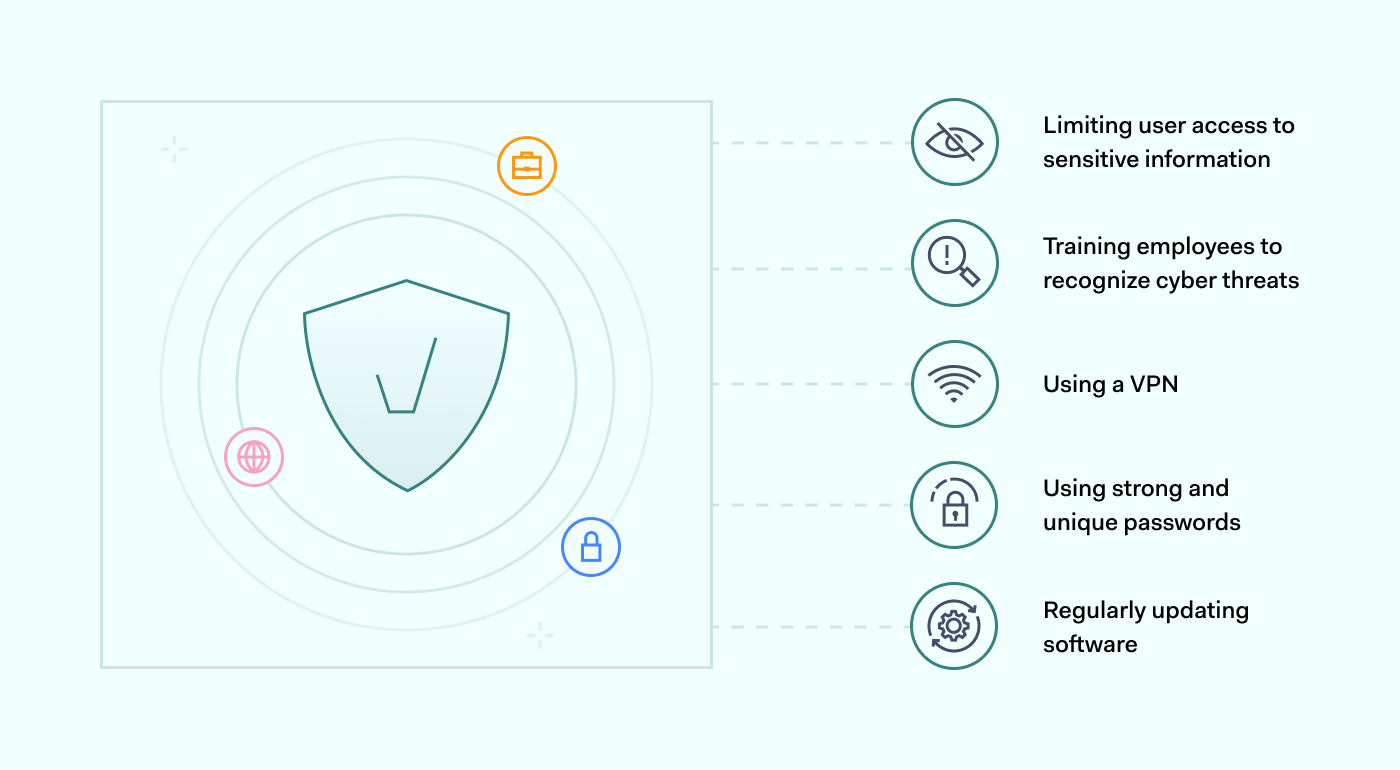
Organizations can take several steps to improve internet access security in all working environments. These include: 
  • Using strong and unique passwords. Online account protection largely rests on the strength of your users’ passwords. Reusing passwords makes it easier for hackers to gain entry into multiple accounts with the same set of credentials. Therefore, requiring a strong and unique password is a simple yet effective way to secure against the simplest threats.

  • Regularly updating software. Periodically updating software is crucial to maintaining a secure system and protecting against cyber threats. As vulnerabilities are discovered daily, using outdated software makes it easier for hackers to exploit known flaws. The only way to avoid those exploits is to patch vulnerabilities to reduce your system’s susceptibility to attacks.

  • Using a VPN. When a user connects to a VPN, its internet traffic is encrypted, protecting all exchanged information under a seal. VPNs also mask your real IP address, making it more difficult for websites and services to track your online activity or location. This alone can make remote working risks less severe.

  • Limiting user access to sensitive information. Enforcing a need-to-know basis for accessing all data. By restricting access to only those who require it, you can reduce the risk of unauthorized access or exposure to confidential information. This can minimize the likelihood of insider threats and ensure accountability for information access.

  • Training employees to recognize cyber threats. Cybercriminals often target employees through phishing emails to gain access to sensitive information. This makes employees a key component of the organization’s defense system. For this reason, they should be equipped to recognize and stop hacking attempts, alongside our technical systems.

How can NordLayer help?

Internet access security is a priority for most companies, no matter what industry they work in. Nowadays, it poses unique security challenges businesses need to address due to various work models like remote, office, and hybrid.

NordLayer can assist enterprises in protecting their connections over the public internet. This is achieved by encrypting the connection between the user’s device and the middleman server using advanced ciphers. It ensures that all data exchanged is kept secure and cannot be read by outsiders.

With cutting-edge security technologies, NordLayer can block access to malicious websites and control entry to specific content categories. Using Public Shared Gateways, NordLayer expands browsing capabilities, allowing global business exploration and guaranteeing the confidentiality of users’ and resources’ true location.

Businesses can enhance their internet access security by implementing best industry practices and regularly training employees on security threats. This is a sure way to protect sensitive information from data breaches, no matter what work model your organization is.

Contact our sales team and discover how to achieve greater internet access security.
About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

ESET Research deconstructs Asylum Ambuscade: group focused on cybercrime, cyberespionage and attacking countries bordering Ukraine

  • Asylum Ambuscade has been operating since at least 2020.
  • It is a crimeware group that targets individuals, small and medium businesses, bank customers, and cryptocurrency traders in various regions, including North America and Europe.
  • Asylum Ambuscade also performs espionage against government entities in Europe and Central Asia: in 2022, the group reportedly targeted government officials in several European countries bordering Ukraine.

BRATISLAVA, MONTREAL — June 8, 2023 — Today, ESET Research released its analysis of Asylum Ambuscade, a cybercrime group that has been performing cyberespionage operations on the side. The group has been running cyberespionage campaigns since at least 2020. ESET found previous compromises of government officials and employees of state-owned companies in Central Asian countries and Armenia. In 2022 the group reportedly targeted government officials in several European countries bordering Ukraine. ESET Research assesses that the goal of the attackers was to steal confidential information and webmail credentials from official government webmail portals. Asylum Ambuscade usually targets small- and medium-sized businesses (SMBs) and individuals in North America and Europe.

“It appears Asylum Ambuscade is branching out, running some recent cyberespionage campaigns on the side, against governments in Central Asia and Europe from time to time. It is quite unusual to catch a cybercrime group running dedicated cyberespionage operations, and as such we believe that researchers should keep close track of its activities,” explains ESET researcher Matthieu Faou, who investigated the activities of the group.

In 2022, when the group targeted government officials in several European countries bordering Ukraine, the compromise chain started with a spearphishing email containing a malicious Excel spreadsheet or Word document attachment. If the machine was deemed interesting, the attackers eventually deployed AHKBOT, a downloader that can be extended with plugins to spy on the victim’s machine. These plugins provide various capabilities, including taking screenshots, recording keystrokes, stealing passwords from web browsers, downloading files and executing an infostealer.

Even though the group entered the spotlight because of its cyberespionage operations, it has mostly run cybercrime campaigns since early 2020. Since January 2022, ESET Research has counted more than 4,500 victims worldwide. While most of these are located in North America, it should be noted that we have also seen victims in Asia, Africa, Europe and South America. Targeting is very wide and mainly includes individuals, cryptocurrency traders, bank customers, and SMBs in various verticals.

“Asylum Ambuscade’s crimeware compromise chain is, overall, very similar to the one we see for their cyberespionage campaigns. The main difference is the compromise vector, which could be a malicious Google Ad redirecting to a website delivering a malicious JavaScript file or multiple HTTP redirections,” adds Faou.

For more technical information about Asylum Ambuscade, check out the blogpost “Asylum Ambuscade – A curious case of a threat actor at the border between crimeware and cyberespionage” on WeLiveSecurity. Make sure to follow ESET Research on Twitter for the latest news from ESET Research.

Geographical distribution of victims since January 2022.


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Setting your office to autopilot

How do you want your IT team to spend their valuable time?

Do you want them to prioritize the big ticket, business critical projects such as keeping your business secure and optimizing your internal systems, continuing to add value to your company?

Or do you want them to spend hour after hour (after hour) responding to the backlog of little time sync tasks that stack up through the day? The “can you add my new job title to my email?” or the “John’s just joined but he can’t access…”

With CloudM Automate, you can put thousands of tasks a year on autopilot, saving days worth of work hours and allowing your team to concentrate on the important, interesting challenges keeping your organization moving forward.

Onboarding

When a new employee joins the business, or an employee moves to a new role, we want them to hit the ground running. Nothing stalls this enthusiasm more than having to wait for access to the resources that they need.

With CloudM Automate, you can make sure that they have access to all the shared documents, drives and calendars required for their role and department, on day one. All you have to do is make sure they are added to the correct dynamic user group.

You don’t need to go into each resource that they need and share it with the new starter. A 30 minute slog is now down to 2 minutes, at most!

Offboarding

When it comes time to say goodbye to an employee, a lot of individual tasks land in your IT team’s inbox. For example, you need to secure the user’s account (including changing passwords), transfer the ownership of Docs, Sites, Calendars and Groups, migrate emails, and claim back licenses. Even a simple manual offboarding process can take up roughly 30 minutes of your IT team’s valuable time.

CloudM Automate allows you to craft bespoke offboarding workflows of up to 30 individual tasks, automatically assigned to users based on group membership, all triggered with the press of a single button. No more delays, no more errors, no more manual tasks.

Archive

You need to keep your leavers data – It’s as simple as that. Whether it’s to comply with domestic or global data regulations such as GDPR, or just so you can recall a piece of crucial evidence as part of a legal or HR issue.

CloudM Archive allows you to make sure you are always sending your user’s data to a secure cloud storage bucket, 100% owned and managed by you, as part of an offboarding workflow. When it comes time to delete archived data, in accordance with data retention laws, CloudM Archive automatically purges it based on retention policies.

You will be 100% compliant with none of the manual hassle.

***Added Bonus*** Storing your data in the cloud with CloudM Archive is up to 75% cheaper than using Google Archive User licenses so you will save time AND money.

Integrations

CloudM Automate plays well with a host of other SaaS applications including Slack, Box, Dropbox, Bamboo HR and ADP, giving you even more ways to put menial tasks on autopilot.


The first way we do this is to allow you to secure and delete SaaS licenses assigned to a leaver as a simple, single step in your offboarding workflows. This is great for making sure that leavers no longer have access to your company data, but will also save you money on used SaaS licenses.

Then, secondly, we have integrations that allow you to make changes to a user’s profile in one SaaS application and have them automatically sync to CloudM Automate. Even better, these changes can automatically trigger onboarding and offboarding workflows, and email signature changes.

Email Signature Management

Any recently promoted or hired employee needs to update their email signature, but instead of hassling the IT department with a ticket, what if it was all done automatically? We use “variable” labels in our templates that take the latest synced information from a user’s CloudM profile or your organization profile.

In fact, with the integrations mentioned in the section above, your HR team can even change the details directly in Bamboo HR or ADP (as they would have to do normally), with the changes syncing over to CloudM Automate, and triggering changes to the user’s email signature. With ZERO interaction from your IT team required.

Also, our role permissions means you can give the right people the right access to our platform. IT admins can give a Marketing or HR team the permissions to create and assign email signatures, without allowing access to any other administrative features, such as onboarding, offboarding and archive.

Streamline your business with CloudM Automate, the award-winning platform that gives you the ability to automate your office, saving you time, stress and money. 

Contact us today and discover for yourself just how valuable office automation can be.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About CloudM
CloudM is an award-winning SaaS company whose humble beginnings in Manchester have grown into a global business in just a few short years.

Our team of tech-driven innovators have designed a SaaS data management platform for you to get the most from your digital workspace. Whether it’s Microsoft 365, Google Workspace or other SaaS applications, CloudM drives your business through a simple, easy-to-use interface, helping you to work smarter, not harder.

By automating time-consuming tasks like IT admin, onboarding & offboarding, archiving and migrations, the CloudM platform takes care of the day-to-day, allowing you to focus on the big picture.

With over 35,000 customers including the likes of Spotify, Netflix and Uber, our all-in-one platform is putting office life on auto-pilot, saving you time, stress and money.

23.6.0 ‘Voyager’ released

Changes compared to 23.5.0

NOTICE: The “Run when PC Starts” option will now also apply to devices waking up from Sleep

New Features

  • Protected Items defined by Policy can now optionally remain linked for future changes
  • Added several new admin permissions to allow a global admin to help prevent a tenant admin from seeing the Comet service or storage provider types in use. The global admin can hide server history and server info widgets on the dashboard, prevent creation of storage via templates or custom storage, and can also filter the list of allowed cloud storage providers

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Comet
We are a team of dedicated professionals committed to developing reliable and secure backup solutions for MSP’s, Businesses and IT professionals. With over 10 years of experience in the industry, we understand the importance of having a reliable backup solution in place to protect your valuable data. That’s why we’ve developed a comprehensive suite of backup solutions that are easy to use, scalable and highly secure.

Stellar Cyber Named a Strong Performer in Gartner Peer Insights™ Voice of the Customer for Network Detection and Response

Stellar Cyber Open XDR receives 4.8/5-star rating from customers on Gartner Peer Insights

Stellar Cyber, the innovator of Open XDR technology, today announced that it has been named a Strong Performer in the Gartner Peer Insights Voice of the Customer for Network Detection and Response. Network Detection and Response is just one of the core capabilities built into Stellar Cyber’s AI-driven Open XDR cybersecurity platform, which also includes NDR with next-generation SIEM, TIP and bi-directional integration with any third-party EDR solution.

As the report explains, “The “Voice of the Customer” is a document that synthesizes Gartner Peer Insights’ reviews into insights for IT decision makers. This aggregated peer perspective…focuses on direct peer experiences of implementing and operating a solution.” In the report’s detailed vendor summary, 100% of Stellar Cyber’s customers responded that they were willing to recommend the company’s Open XDR platform, and gave it a composite rating of 4.8 stars out of five across the product’s capabilities, sales experience, deployment experience, and support experience based on 20 reviews submitted as of March 2023 on Gartner Peer Insights.

“We have a strong commitment to our customers and partners to ensure they have successful deployments and utilize the full value of the Stellar Cyber Platform as their Open XDR Security Operations Platform,“ says Paul Levasseur, Vice President of Customer & Partner Enablement at Stellar Cyber. “We’re very happy that our customers are reporting their satisfaction through the Gartner Voice of the Customer report.” 

Gartner, Voice of the Customer for Network Detection and Response, Peer Contributors, 29 May 2023

Resources

Gartner and Peer Insights are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Stellar Cyber
We deliver an easy-to-use Open XDR platform built to meet the needs of lean security teams, providing security functionality anyone can use.
Our Mission: Deliver world-class security products for the 99%