Skip to content

ESET Recognized as a Representative Vendor in the 2024 Gartner® Market Guide for Managed Detection and Response

  • ESET has been named a Representative Vendor in the Gartner® Market Guide for Managed Detection and Response report.
  • The 24/7 MDR service offers direct access to ESET’s cybersecurity experts and technology, helping customers to rapidly detect, analyze, investigate, and respond to cyberthreats proactively.

BRATISLAVA – August 2, 2024 — ESET, a global leader in cybersecurity solutions, is proud to announce its recognition as a Representative Vendor in the latest Gartner® Market Guide for Managed Detection and Response report. We believe that this acknowledgment underscores ESET’s commitment to delivering cybersecurity services in the managed detection and response (MDR) landscape.

MDR services are crucial in today’s cybersecurity landscape. According to the Gartner report, “MDR services provide customers with remotely delivered, human-led, turnkey, modern SOC functions, ultimately delivering threat disruption and containment. Security and risk management leaders should use this research to identify MDR services that meet their business-driven risk requirements.”

ESET’s MDR services offer cybersecurity protection, providing access to experts without needing internal staff, enhancing and simplifying security workflows by adding functionalities such as the ESET AI Advisor, which contextualizes detections and helps both novice and mature admins more easily protect their environments. Furthermore, the company’s core AI-powered MDR identifies threats early, ensuring high detection rates and minimal false positives. Operating 24/7/365, the services guarantee continuous monitoring and swift incident response even in hybrid work settings, leading to a competitive response time of as little as 20 minutes. With its offering, ESET helps organizations achieve essential cyber controls for insurability and regulatory compliance, reducing legal risks and penalties.

“With our MDR portfolio, we offer something that answers the needs of businesses of all sizes. The stakes have never been higher, which is recognized by regulators and cyber insurance providers as well. If a business is genuinely committed to strengthening its security posture, tackling threats while staying compliant, ESET MDR is what can give it that competitive edge. We are proud to be recognized as a Representative Vendor in the 2024 Gartner Market Guide,” said Pavol Balaj, Chief Business Officer at ESET.

MDR services should help businesses reduce their time to respond to threats, as well as help detail their current exposure to such threats. The right MDR service is speedier than in-house SOC efforts, and it’s much more comprehensive and flexible than generalist business IT administration; hence, to answer both these challenges collectively, ESET offers its MDR services in two subscription tiers to cater to different business needs. For small and medium-size businesses, ESET PROTECT MDR offers robust security features and expert support, ensuring top-tier protection without unnecessary complexities. For enterprises, ESET PROTECT MDR Ultimate provides enhanced security capabilities, proactive threat detection, and comprehensive response services, ensuring optimal protection and regulatory compliance.

According to the report, you can “use MDR services to obtain 24/7, remotely delivered, human-driven security operations capabilities when there are no existing internal capabilities. MDR services also should be used when the organization needs to accelerate or augment existing security operations capabilities.”

Find more information about ESET’s MDR services here.

Gartner, Market Guide for Managed Detection and Response, By Pete Shoard, Andrew Davies, Mitchell Schneider, Angel Berrios, Craig Lawson, 24 June 2024.

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.

Gartner does not endorse any vendor, product, or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Penta Security 榮獲 Frost & Sullivan 高度讚譽 讚揚其全面的網絡安全解決方案和市場領導地位

Penta Security 因其全面的網絡安全解決方案和在市場中的領先地位,獲得了 Frost & Sullivan 的高度讚譽。該公司推出的網絡應用防火牆(WAF)具備高度的可擴展性和易用性,尤其在南韓本地客戶中表現出色,超越了無法支援其國內雲端環境的國際競爭對手。

Frost & Sullivan 最近對網絡應用防火牆市場進行了評估,並根據分析結果授予 Penta Security 2024 年度南韓年度公司獎。Penta Security 專注於提供網絡及數據安全產品和服務。與傳統的入侵防禦系統或不夠全面的新一代防火牆不同,Penta Security 的 WAPPLES 系列(包括 WAPPLES SA 和 Cloudbric WAF+)提供了 API、SSL 和 L7 安全保護功能。Penta Security 的 WAPPLES 以其專利的邏輯檢測引擎 —— 內容分類與評估處理 (COCEP™) —— 在市場中脫穎而出。與依賴簽名匹配檢測的傳統 WAF 不同,WAPPLES 不需要頻繁的簽名更新或長時間的學習期,因此能夠快速修補安全漏洞並進行程式修補更新。

作為南韓 WAF 市場的領導者,Penta Security 以卓越的性能與應用安全相結合。其 WAF 適用於不同部署環境,包括本地設備 WAPPLES、雲端軟件設備 WAPPLES SA 以及雲端解決方案 Cloudbric WAF+,這些產品均支援亞太地區的公共及本地雲端服務。Penta Security 的成功在於它能深刻理解並滿足本地客戶的需求,並且其 API 安全功能、威脅 IP 和機械人檢測等先進技術,能有效抵禦各種基於惡意 IP 的網絡威脅。

Frost & Sullivan 的行業分析師 Ying Ting Neoh 表示:「Penta Security 展示了在南韓 WAF 行業中的領導力,憑藉與內部及第三方安全方案的整合,及其不斷的技術創新,該公司為客戶提供了全面的應用安全解決方案。」

Penta Security 擁有超過 200 名員工,提供 24 小時技術支援,通過網上通訊系統及時解決客戶的問題。除了為當地客戶提供領先的技術和世界級的服務外,Penta Security 也透過其廣泛的合作夥伴和渠道網絡,擴展了其全球業務,滿足了不同客戶群體的需求。這不僅加強了 Penta Security 在南韓 WAF 市場中的領導地位,也使其市場份額超過 50%。WAPPLES 在引入客戶環境後,仍能保持卓越的網絡性能,進一步鞏固了該公司的市場優勢。

「近年來 Penta Security 業務穩定增長,已經確立了其在南韓市場的領導地位。該公司的前瞻性策略在於其實施最佳實踐的承諾,並積極利用雲端行業的快速發展,推出基於雲的 WAF,為其應用安全產品組合增添了重要資產,並促進了公司的增長。」Neoh 補充道。憑藉其強大的綜合表現,Penta Security 榮獲 Frost & Sullivan 頒發的 2024 年度南韓 WAF 行業年度公司獎。

Frost & Sullivan 每年都會頒發年度公司獎,表彰那些在增長戰略和實施方面表現卓越的企業。該獎項特別肯定了在技術創新、產品開發及客戶價值等方面展現出領導地位的公司。

Frost & Sullivan 的最佳實踐獎旨在表揚在區域或全球市場中展現卓越成就的企業,這些企業在領導力、技術創新、客戶服務及產品開發等方面有著優異表現。行業分析師透過深入訪談、數據分析和廣泛的研究,對市場參與者進行全面比較,確定業界最佳實踐。

關於 Frost & Sullivan
六十年來,Frost & Sullivan 一直致力於幫助投資者、企業領導者和政府應對經濟變化,並識別顛覆性技術、大趨勢及新商業模式,從而帶來持續的增長機會,推動未來成功。

關於 Penta Security

Penta Security 採取全方位的策略來涵蓋資訊安全的每個面向。本公司持續努力,透過廣泛的 IT 安全產品,在幕後確保客戶的安全。因此,Penta Security 總部位於韓國,並已在全球擴展,成為亞太地區的市佔領導者。

作為韓國最早進入資訊安全領域的公司之一,Penta Security 已經開發出廣泛的基礎技術。我們將科學、工程與管理相結合,擴展自身的技術能力,並以此技術視角做出關鍵決策。

關於Version 2

Version 2 Digital 是立足亞洲的增值代理商及IT開發者。公司在網絡安全、雲端、數據保護、終端設備、基礎設施、系統監控、存儲、網絡管理、商業生產力和通信產品等各個領域代理發展各種 IT 產品。透過公司龐大的網絡、通路、銷售點、分銷商及合作夥伴,Version 2 提供廣被市場讚賞的產品及服務。Version 2 的銷售網絡包括台灣、香港、澳門、中國大陸、新加坡、馬來西亞等各亞太地區,客戶來自各行各業,包括全球 1000 大跨國企業、上市公司、公用事業、醫療、金融、教育機構、政府部門、無數成功的中小企及來自亞洲各城市的消費市場客戶。

24.6.6 ‘Voyager’ released

Changes compared to 24.6.5

New Features

  • Added an option to have failed backup jobs retry after a configurable period of time
  • Added ability to bulk convert Storage Vaults created with S3-backed Storage Role templates to direct S3 Storage Vaults
  • Added support for restoring a Windows Disk Image backup from a Linux device
  • Added a Linux ISO option when using the Create Recovery Media feature

Enhancements

  • Added an automatic clean up of stale Storage Vault locks immediately when a device reboots, or wakes from sleep
  • Added support for custom prefix directories for IAM-compatible Storage Template providers
  • Added an explanation tooltip for unavailable features in the Create Recovery Media dialog in the Comet Backup desktop app
  • Added safeguards to ensure the Hyper-V Protected Item “Latest VM state” mode is only used with supported Windows versions, in the Comet Server web interface and the Comet Backup desktop app
  • Improved the performance of evaluating the “if last job was missed” schedule option

Bug Fixes

  • Fixed an issue when restoring Disk Image Protected Items to VMware virtual disk files with ZERO extents present
  • Fixed an issue with “Converting PfxData: pkcs12: unknown attribute” error messages when Comet Server uses some types of SSL certificate
  • Fixed an issue with unclear error messages when running a Hyper-V Protected Item using “Latest VM state” mode on unsupported Windows versions
  • Fixed an issue with the Comet Backup desktop app not allowing you to create an IDrive Storage Vault with a bucket name that is five characters long
  • Fixed an issue with the Create Recovery Media dialog not allowing moving to the next page when manually typing a path to create an ISO file
  • Fixed a cosmetic issue with misleading appearance of the Create Recovery Media dialog if the image generation failed

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Comet
We are a team of dedicated professionals committed to developing reliable and secure backup solutions for MSP’s, Businesses and IT professionals. With over 10 years of experience in the industry, we understand the importance of having a reliable backup solution in place to protect your valuable data. That’s why we’ve developed a comprehensive suite of backup solutions that are easy to use, scalable and highly secure.

SafeDNS introduces advanced DoH and DoH policy features to ensure traffic security

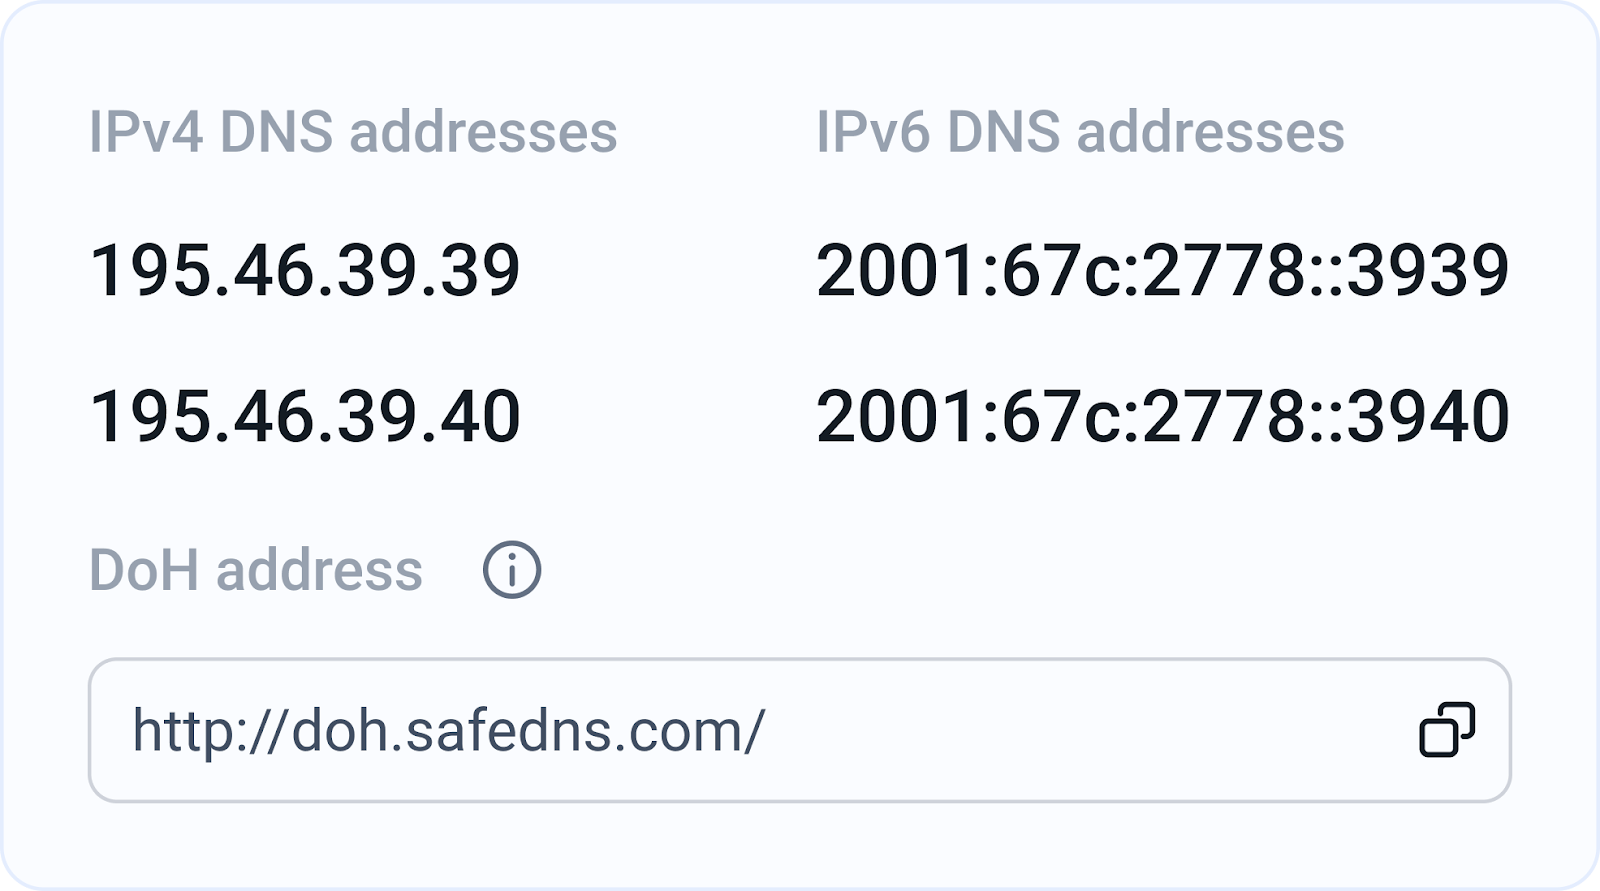
We are extremely glad to announce the release of our brand-new DNS-over-HTTPS feature, which reaffirms our commitment to secure and private Internet experiences for all users. DNS-over-HTTPS (DoH) is a higher-level protocol designed for performing remote DNS resolution using the HTTPS protocol. This development marks a spectacular leap ahead in making user privacy and security better.

DNS-over-HTTPS (DoH) is a protocol for performing remote DNS resolution via the HTTPS protocol. DoH significantly enhances user privacy and security by encrypting DNS queries, preventing third parties from eavesdropping on user activities, and intercepting data. By encapsulating DNS requests within HTTPS traffic, DoH prevents unauthorized entities from snooping on users’ browsing activities and intercepting sensitive data. This encryption ensures that only the intended recipient, the DNS resolver, can decode and respond to the queries, maintaining the confidentiality and integrity of internet requests.

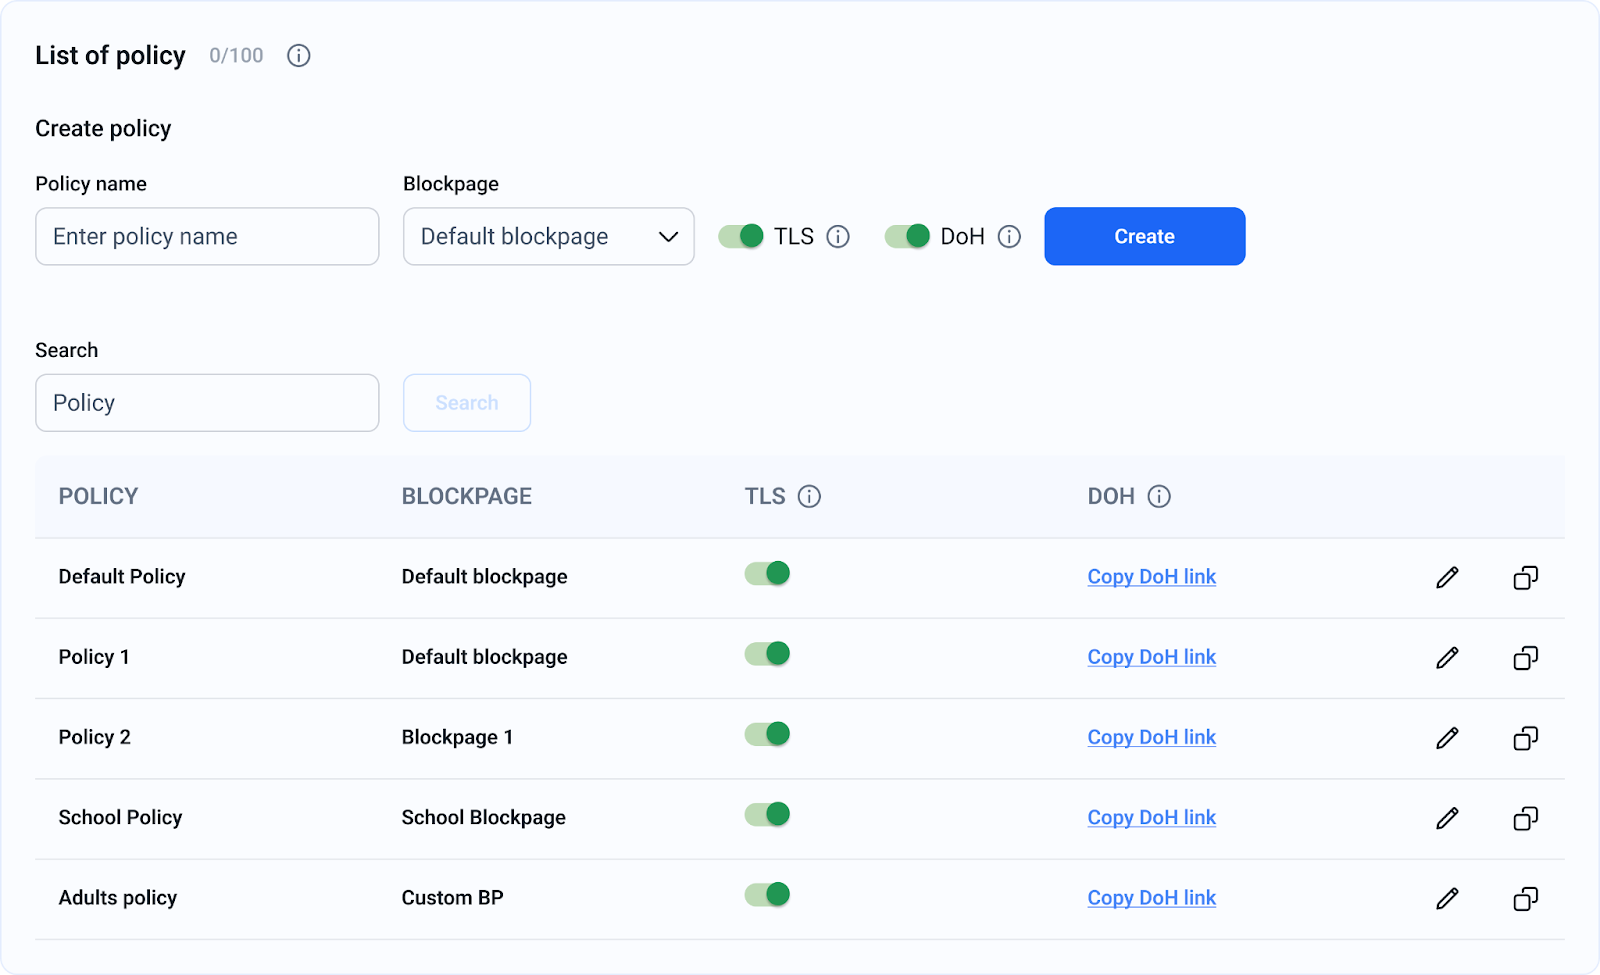
In addition to the core DoH functionality, SafeDNS is introducing the DoH policy feature. This advanced tool helps users generate their unique DoH link embedded with a policy token for applying certain filtering policies without having to manually add an IP address to the SafeDNS dashboard. The integration of this feature simplifies the management process for users, allowing them to enforce specific filtering rules effortlessly and efficiently.

This feature is particularly beneficial for managing and protecting roaming clients without our agents. In other words, such clients will always be protected by the high level of filtering and protection provided by SafeDNS, regardless of their geolocation. It’s important to note that filtering operates within the browser where this setting is applied. We still recommend installing agents for comprehensive protection because when using only DNS over HTTPS, traffic from certain apps and services may remain unencrypted, leaving some vulnerabilities.

The DoH feature is available in all new SafeDNS plans, thus providing a guarantee of enhanced safety and privacy for all its users. However, the DoH Policy feature is exclusively available on our Pro, Pro+, and Education plans, offering advanced policy management and filtering capabilities for enhanced and comprehensive protection. With the DoH Policy feature incorporated in these upper-tier plans, we can deliver a more robust solution for customers that need the very finest level of protection and advanced policy management, ensuring that our users enjoy unparalleled internet security and privacy.

At SafeDNS, our mission is clear: to provide powerful, reliable Protective DNS solutions for safe internet use while attentively preserving users’ privacy and control. On this note, the introduction of DoH and the DoH policy feature underline that SafeDNS continues supplying its clients with all tools necessary to browse the web safely and securely, staying up-to-date with the latest DNS security technologies.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About SafeDNS
SafeDNS breathes to make the internet safer for people all over the world with solutions ranging from AI & ML-powered web filtering, cybersecurity to threat intelligence. Moreover, we strive to create the next generation of safer and more affordable web filtering products. Endlessly working to improve our users’ online protection, SafeDNS has also launched an innovative system powered by continuous machine learning and user behavior analytics to detect botnets and malicious websites.

NIS2 implementation: Is your SaaS prepared?

The revised Network and Information Systems Directive (NIS2) signifies the European Union’s strengthened commitment to enhancing cybersecurity measures across the region. Scheduled to take effect in October 2024, NIS2 broadens the scope of its predecessor, the original NIS Directive from 2016. It imposes stricter requirements to elevate the overall information security and posture in Europe.

As a cornerstone of the digital economy, Software-as-a-Service (SaaS) providers must thoroughly examine the implications of NIS2 and take timely action to ensure compliance.

What is the NIS2 Directive? 

NIS2 is designed to build upon the foundation laid by the original NIS Directive. It aims to foster greater collaboration between entities and harmonize cybersecurity standards across all European Union member states. At its core, NIS2 emphasizes a risk-based approach, proactive monitoring, and corporate accountability.

The directive introduces more stringent reporting obligations, enforcement measures, and management training requirements. Non-compliance with NIS2 can result in substantial fines of up to €10 million or 2% of global turnover, whichever is higher.

These penalties underscore the importance of adhering to the directive’s mandates and prioritizing cybersecurity.

Who does NIS2 apply to?

The NIS2 Directive targets “essential” and “important” entities operating within critical sectors such as digital infrastructure, healthcare, energy, and transport. This comprehensive scope extends to many SaaS providers, even if they do not have a physical presence within the European Union, as long as they offer digital services to EU customers.

Who does NIS2 apply to: essential versus important entities

Given the nature of SaaS models, which typically involve handling sensitive data and ensuring continuous availability, these providers are significantly affected by NIS2’s risk management measures and business continuity planning provisions. As remote work trends increase reliance on cloud-based solutions, SaaS providers need to understand and address the potential implications of NIS2 implementation.

NIS2 for SaaS: its scope and impact

Due to its expanded scope and rigorous requirements, NIS2 will substantially impact SaaS providers. The Directive mandates that providers implement comprehensive risk management measures, including regular risk analysis and continuous monitoring, to detect and mitigate cyber threats. Providers must also establish robust incident response procedures to address any security incidents swiftly.

NIS2 enforces stricter reporting obligations, requiring SaaS providers to promptly notify relevant authorities and customers during a significant cyber incident. This enhances transparency, trust, and accountability within the digital ecosystem.

Additionally, NIS2 emphasizes the importance of cybersecurity training and awareness programs for management and staff. SaaS providers must invest in ongoing education to ensure their teams are prepared to handle evolving cyber threats and maintain compliance with the directive.

Why NIS2 compliance matters

Ensuring compliance with NIS2 is not just about avoiding penalties; it is a critical step toward enhancing your SaaS operations’ overall security and resilience. Here are key reasons why compliance with the European Directive is vital:

  • Protects sensitive data. SaaS providers often manage large volumes of sensitive and personal data. Compliance with NIS2 helps protect this data against cyber threats, reducing the risk of data breaches and the associated financial and reputational damage.

  • Maintains customer trust. Customers expect their data to be handled securely. By complying with NIS2, SaaS providers demonstrate a commitment to high standards of information security, thereby maintaining and potentially increasing customer trust and loyalty.

  • Avoids financial penalties. Non-compliance with NIS2 can result in hefty fines. Ensuring compliance helps avoid significant financial penalties and their negative impact on your business.

  • Enhances competitive advantage. In a market where information security is a significant concern, compliance with NIS2 can provide a competitive edge. SaaS providers prioritizing compliance can differentiate themselves by offering more secure and reliable services.

  • Ensures business continuity. NIS2 mandates robust risk management measures and incident response procedures. By adhering to these requirements, SaaS providers can minimize downtime and ensure continuous service availability, which is crucial for maintaining operations and customer satisfaction.

  • Strengthens corporate accountability. NIS2 emphasizes the role of senior management in cybersecurity. Compliance ensures that executives know their responsibilities and actively manage and mitigate cyber risks, leading to better governance and oversight.

  • Mitigates supply chain risks. With NIS2’s focus on the supply chain, compliance ensures that all third-party services and partners adhere to high-security standards. This reduces the risk of vulnerabilities introduced through external parties.

  • Aligns with global standards. As information security threats become increasingly global, aligning with the NIS2 Directive positions SaaS providers to meet international security standards, facilitating smoother operations across different regions and markets.

Compliance with NIS2 is a proactive measure that goes beyond regulatory obligations. Building a robust, secure, and trustworthy digital infrastructure that can withstand the constantly evolving cyber threats environment is essential.

By prioritizing compliance, SaaS providers safeguard their operations and contribute to enhancing cybersecurity across the European Union.

Challenges of the NIS2 Directive for SaaS providers

As SaaS providers prepare to implement NIS2, they may encounter several challenges that require careful planning and strategic action. Below there is a list of potential hurdles that providers should be aware of:

  • Complex compliance requirements: Navigating the extensive and detailed requirements of NIS2 sectors can be challenging, especially for smaller SaaS providers with limited resources

  • Enhanced reporting obligations: Meeting the directive’s stringent reporting requirements may require significant changes to existing processes and systems

  • Increased costs: Implementing the necessary security measures and training programs can be costly, impacting the provider’s budget and resource allocation

  • Risk management: Establishing effective risk management measures involves continuous monitoring, regular assessments, and timely updates to security protocols

  • Corporate accountability: Ensuring that senior management is adequately trained and aware of their responsibilities under NIS2 can be demanding

  • Data sovereignty & localization: Adhering to data sovereignty and localization requirements, especially for providers operating across multiple jurisdictions, adds another layer of complexity

  • Supply chain vulnerabilities: Managing and securing the supply chain to ensure that all third-party services comply with NIS2 can be a daunting task

Prepare your SaaS for NIS2 compliance

To help SaaS providers navigate the complexities of NIS2 compliance, we have outlined a list of essential steps.

NIS2 compliance steps for SaaS

1. Conduct a comprehensive risk assessment

Perform a thorough risk analysis to identify potential vulnerabilities and threats within your network and information systems. Regularly update this assessment to reflect new risks and changes in the threat landscape.

2. Implement robust security measures

Ensure that your security measures align with NIS2 requirements, including Always-On VPN and Multi-Factor Authentication (MFA) for secure access, as well as dynamic firewalls and network segmentation to isolate environments and enforce least privileged access.

3. Establish incident response procedures

Develop and implement a robust incident response plan that includes procedures for detecting and responding to security incidents and clear communication protocols for notifying authorities and affected parties.

4. Invest in continuous monitoring

Utilize advanced monitoring tools such as cloud-delivered Intrusion Prevention Systems (IPS), Intrusion Detection Systems (IDS), and Web Application Firewalls (WAF) for continuous surveillance and protection.

5. Train management & staff

Provide regular cybersecurity training for management and staff to ensure their awareness of their responsibilities under NIS2 and their ability to respond effectively to cyber threats and security incidents.

6. Ensure data sovereignty & localization

Adhere to data sovereignty and localization requirements by using dedicated servers with fixed IP addresses to ensure data remains within the specified jurisdiction.

7. Engage expert compliance consultants

Consider partnering with compliance consultants to strategize and validate your NIS2 preparedness and ensure thorough attention to all aspects of the Directive.

Embracing the future of cybersecurity

As we move towards an increasingly digital future, the importance of robust cybersecurity cannot be overstated. Implementing NIS2 represents a significant transition in approaching security across the European Union, setting a new standard for resilience against cyber threats.

This directive is both a challenge and an opportunity for SaaS providers. By embracing NIS2’s requirements, providers protect their operations and build trust with their customers, enhance their competitive edge, and contribute to a safer digital ecosystem.

Compliance with NIS2 is more than a regulatory obligation; it is a commitment to excellence in cybersecurity. As cyber threats evolve, staying ahead requires proactive measures, continuous improvement, and a dedication to safeguarding data and infrastructure.

Take this opportunity to transform your SaaS business’ security practices, fortify your defenses, and create a secure digitalized environment.

How NordLayer can help

As a network security provider, NordLayer offers tools and services to help SaaS providers achieve NIS2 compliance by:

  • Access control policies. Implement strong Network Access Control (NAC) policies using NordLayers Virtual Private Gateways with a dedicated IP address. Additionally, adopt advanced features like Cloud Firewall for granular network segmentation, and Device posture security to ensure only known and compliant devices can enter the company’s network. Elevate your network protection with multi-layered authentication methods such as 2FA (SMS & TOTP) and biometrics to access your network.

  • Effective incident handling. Utilize threat prevention features like traffic encryption, IP masking, DNS filtering, and Always-On VPN to mitigate various threats that can infect your network. Improve threat detection with Device Posture Security and activity monitoring to maintain a resilient network infrastructure.

  • Solid cryptography policies. Utilize NordLayer’s VPN gateways with quantum-safe encryption of data in transit. Provide a secure environment for browsing online and accessing sensitive resources or hybrid networks.

With NordLayer, SaaS providers can simplify infrastructure security management and demonstrate compliance with some of the stringent requirements of the NIS2 Directive.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.