Skip to content

How Accrete Inc. prepared for failover to protect the sensitive data of high-profile clients

Accrete Inc. is an artificial intelligence company that specializes in a variety of sectors. Its wide range of products supports government, entertainment, financial services, and consumer packaged goods. The company has established a reputation for its innovative supply chain analysis and social media aggregation solutions. 

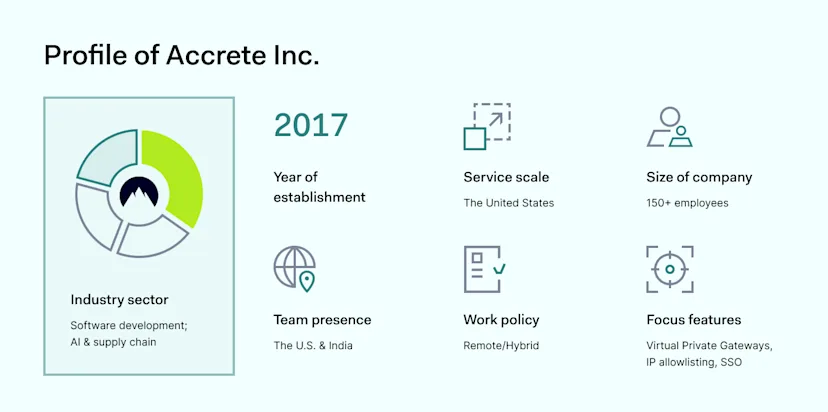
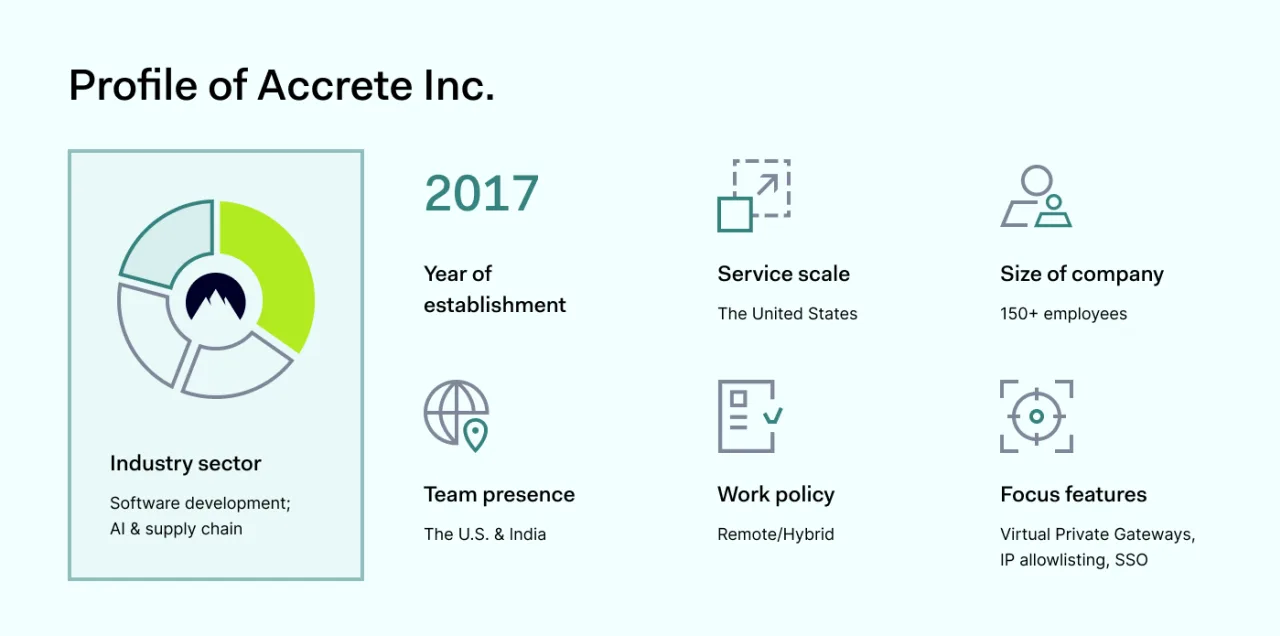
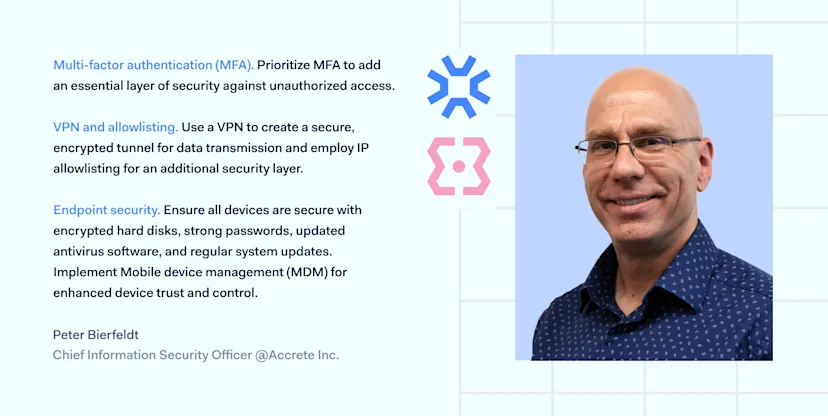
Profile of Accrete Inc.Peter Bierfeldt, the Chief Information Security Officer, oversees the security of the company’s intellectual property, customer data, and overall reputation. He shared how working with governmental and other high-risk clients requires a focus on layered security and how Accrete Inc. achieved it using NordLayer.

The challenge

Securing cloud environments for high-risk data clients

Accrete’s unique position in the market, dealing with sensitive government contracts and a global workforce, posed significant cybersecurity challenges.

The company works with a diverse range of clients, including the US Department of Defense. This requires them to follow stringent security standards like FedRAMP and NIST 800-171.

“We knew it’s a good practice to have a VPN solution in place to have everybody enter our client cloud network through an allowlisted IP, whether you’re talking AWS GovCloud or AWS commercial production.”

Click to tweet

The primary concern was securing a virtual, cloud-based network environment against potential threat actors, particularly in high-risk countries.

“We are a virtual company with no on-premise network. We don’t have anything like that. We are 100% in the cloud, and protecting that cloud is really, really important.”

Click to tweet

Additionally, Accrete faced challenges in managing a globally dispersed team with offices in the U.S. states and India, requiring secure and reliable access to the network from various locations worldwide.

The solution

Combining multiple security functionalities for the best result

Accrete Inc. chose NordLayer as their cybersecurity partner, transitioning from their previous VPN provider.

“Accrete Inc. needed one more piece of the puzzle for getting into our network, an additional layer of security that you can put in place to protect your production and entire network.”

Click to tweet

The company’s network security combines layers of different capabilities and functionalities. It includes virtual private gateways, IP allowlisting, SSO and MFA implementation, strong passwords, and antivirus protection. Thus, it must have been not only just a VPN but a solution that does more.

“Our old VPN didn’t do anything beyond being a VPN. We looked for a solution that secures the network when connected to untrusted Wi-Fi and is reliable regarding performance.”

Click to tweet

As Peter notes, different from free tools, the company is paying for the service to protect their information. Having government customers dealing with financial services and insurance, Accrete Inc. must ensure that nobody’s snooping on their traffic, and with a company like NordLayer, they don’t have to worry about it.

Why choose NordLayer

NordLayer was selected for its robust VPN solutions, global points of presence, and seamless integration with existing systems like Okta SSO providers.

“Our clients must know that we don’t relax our security. An outage and going down temporarily is an issue with high-sensitivity data, but with failover, we don’t need to worry about it.”

Click to tweet

One of the main objectives for Accrete Inc. was to establish a failover in case of an outage. Deploying at least two private servers ensured high service availability. This approach means security isn’t compromised, even if one of the virtual gateways flatlines for a few minutes.

A solid mesh of security and business continuity measures established with the NordLayer tool

The key reasons for this choice were:

  • NordLayer’s global network infrastructure provided low-latency, secure connections for their international team, which was particularly beneficial for the office in Mumbai.

  • The ability to establish failover systems ensured uninterrupted access and network resilience.

  • NordLayer’s reputation for reliability and security compliance aligned with Accrete’s needs for protecting sensitive government-related data.

  • The ease of onboarding and user-friendly nature of NordLayer’s services minimized IT overhead and facilitated smooth integration into Accrete’s operations.

The outcome

Complete team protection to enable full network security

Implementing NordLayer resulted in a strengthened cybersecurity posture for Accrete Inc. The new system enhanced network security without compromising on performance, even for remote and international team members.

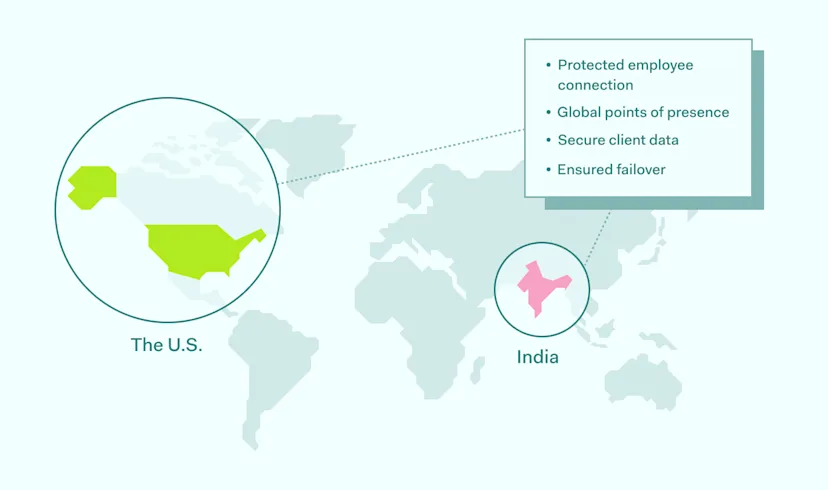
Accrete Inc. added VPN gateways to cover both the United States and India, supporting all staff.  VPN usage mitigates the risk of leakage of even relatively benign information like email addresses and user names.

“Investing in 100% user coverage in the organization makes sense. When people get used to using the VPN, it limits network exposure  and mitigates the impact of compromise to our network even if an endpoint is compromised.”

Click to tweet

Accrete Inc. successfully met the compliance requirements for their government contracts and ensured the integrity of their intellectual property and customer data.  FedRAMP requires that only trusted devices access the network.  By combining allowlisting via the VPN to access the network via Okta, Accrete Inc. was able to address several FedRAMP controls.

“NordLayer plays very nicely with Okta. It integrated well with the onboarding process, making it easy and simple as we’ve got other systems with much more overhead and hand-holding.”

Click to tweet

The shift also demonstrated a commitment to utilizing leading-edge technology solutions to address complex security challenges.

Pro cybersecurity tips

We talk with our clients not only to learn their experience using NordLayer but also to understand how cybersecurity experts perceive online security. Thus, we asked the Chief Information Security Officer at Accrete Inc. to share his personal favorite tips for building digital hygiene habits.

Accrete Inc. is a perfect example of how a layered approach to security can ease and improve your network protection journey. NordLayer is a solution that takes granular control of establishing different security measures, so they create a robust mesh against digital threats.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Spy Skills for Your Business: Threat Intelligence Explained

Ever wanted to be a spy? With such a great deal of espionage operations happening online, gathering threat intelligence might feel like being a modern-day James Bond.

Think about cyber threat intelligence as having a spy network working to protect your business online. It’s all about gathering information on potential cyber threats — understanding how bad actors operate, what areas of business they might target, and what tools they use. Companies cannot effectively defend themselves from cyberattacks without well-researched, reliable data. With threat intelligence, businesses can stay one step ahead of cybercriminals, know what to look out for, and have a clear understanding of how to protect their assets.

A brief history of threat intelligence and its role in cybersecurity

Without cyber threat intelligence, a company is “blind and deaf.” It would not be an exaggeration to say that it is an essential part of cybersecurity. However, its shape and role in cybersecurity have changed over the years as a result of the internet’s evolution and the growth of worldwide interconnectivity. New cyber threats arise daily, making security experts develop innovative defensive strategies and tactics.

Initially, companies focused solely on basic security measures such as IP and URL blacklists and antivirus solutions. However, with the spread of malware, worms, and viruses in the early 2000s, they found themselves in need of more sophisticated threat detection and response capabilities. As cyber criminals got smarter and more organized, it became evident that security experts needed to collaborate and share information. Consequently, the President of the United States established the Information Sharing and Analysis Center (ISAC), a non-profit organization dedicated to facilitating the sharing of threat intelligence within specific industries.

In the 2010s, the rise of data automation and the emergence of Threat Intelligence Platforms (TIPs) resulted in organizations having the right tools to manage and analyze large volumes of data. These platforms are technological solutions that can manage data collected from multiple sources and presented in various formats.

Later on, TIPs were integrated into Security Operations Centers (SOCs), providing security analysts with a unified interface for accessing and utilizing cyber threat intelligence seamlessly in a company’s day-to-day operations. Threat Intelligence Platforms also became an integral part of Incident Response (IR) processes, delivering actionable scenarios for managing and mitigating the impact of a security incident on an organization. This integration made the response to cybercrime faster and more efficient.

Nowadays, the role of machine learning and AI in cyber threat intelligence grows stronger every day, helping to analyze and predict cyber threats. We can also see a shift in the cybersecurity objectives — from threat detection to cyber resilience, focusing on the business’s ability to recover quickly from cyberattacks. Fortunately, throughout the years of the digital revolution, the cybersecurity community has recognized the importance of collaboration, data sharing, and the integration of threat intelligence into the overall cybersecurity strategy.

Threat Intelligence Lifecycle

Gathering threat intelligence is a complicated process that involves collecting, processing, and analyzing large volumes of data. The outcome of this process should focus on vulnerabilities specific to your organization. It should be detailed and contextual and, last but not least, be actionable.

Let’s examine the six phases of the threat intelligence lifecycle:

1. Direction

The direction phase is a crucial part of the process: you cannot perform a secret service operation without specifying its objectives. Therefore, you should follow in the footsteps of the character played by Jodie Foster in the 4th season of “True Detective” and ask questions such as:

  • Who are the attackers?

  • What motivates them?

  • Which data assets and business processes need to be protected?

  • Protection of which aspects of the organization is our priority?

  • What happens if we fail to protect them?

  • What types of threat intelligence do we need to protect the company’s assets and respond to emerging dangers?

2. Collection

After setting goals and objectives, we can move to the next phase: data collection. The security team gathers raw data from various sources, including open-source intelligence (OSINT), commercial feeds, internal logs, and information shared within the cybersecurity community. At this stage, it’s important to validate our sources of information and the accuracy of collected data. This will allow us to avoid missing severe cyber threats or being misled by false positives.

3. Processing

Remember that nowadays, threat analysis relies on processing huge volumes of data, which is automated and requires data to be standardized and formatted. When our collected data are compatible, we can identify relationships and connections between different pieces of information to better understand the cyber threat landscape.

4. Analysis

Threat intelligence analysis is a human process that turns processed information into actionable intelligence, enabling data-driven decision-making. The analysis should prioritize risks, resulting in the creation of a threat management roadmap. It should also provide a context for collected threat intelligence by understanding the motives, capabilities, and tactics of cybercriminals. What’s important here is to present threat analysis in a way that decision-makers will easily understand.

5. Dissemination

Dissemination is a crucial part of threat intelligence management. Analyzed data must be transformed into actionable intelligence reports, alerts, or indicators of compromise (IOCs) that the security team can use to strengthen the company’s defense system. Then, those should be shared with relevant teams and decision-makers within the organization and, in some cases, with trusted external partners.

6. Feedback

Threat intelligence management and effectiveness must be evaluated. Did the intelligence have the impact you expected? Did it improve the company’s safety? What went wrong in the entire process? Answering those questions helps your business move forward and improve its threat intelligence program.

Four types of threat intelligence

We need to understand the types of threat intelligence to fully grasp its impact on overall business cybersecurity. Usually, cyber threat intelligence is divided into four categories, ranging from high-level information to specific technical details about cyber threats.

Strategic

Strategic threat intelligence is non-technical information focused on understanding the broader context of cyber threats. It may come in the form of reports describing hackers’ motives and capabilities, geopolitical influences, or industry-specific risks. Usually, this type of threat intelligence is presented to high-level stakeholders, e.g. the board of directors.

Tactical

This type of threat intelligence includes information that can be used by security experts to make data-driven decisions and actively defend the organization. Tactic intelligence is more detailed than strategic. For example, it may describe cybercriminals’ tools, attack avoidance tactics, or weak points in the company’s security infrastructure.

Operational

It provides real-time information on specific threats, ongoing crime operations, and emerging attack patterns. This type of intelligence enables the company to respond to specific cyberattacks immediately; it can also help mitigate the damage made by hackers.

Technical

Technical threat intelligence may come in the form of evidence that an attack is happening or specific indicators of compromise (IOCs). Ideally, it’s provided in real-time before the hackers can cause any significant damage. Examples of tactical cyber threat intelligence include phishing emails detected by AI tools or real-time data breach notifications sent by an advanced enterprise password manager.

How NordPass can help protect organizations

A country needs all kinds of security measures to protect its citizens: the border guard, the police, an army, and special agents. It can be safe only if all parties work together. The same rule applies to keeping your business safe. It requires all types of threat intelligence — every single one of them is an important part of the cybersecurity landscape. They are interconnected, and only together can they provide comprehensive defense against cybercrime. Even the best strategic plans won’t stand a chance if the company fails to recognize data breaches in real-time.

Luckily, there are tools available that can make gathering technical threat intelligence easier and more efficient. The NordPass built-in Data Breach Scanner automatically scans leaked databases and compares them with information stored in your and your employees’ password manager vaults. It generates password breach reports with detailed information about data leaks that have affected your company. Most importantly, it notifies you or your security team in real time about every new breach so you can act and protect your company immediately. Give it a try, and don’t let cyber threats slip through your company’s defense anymore!

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

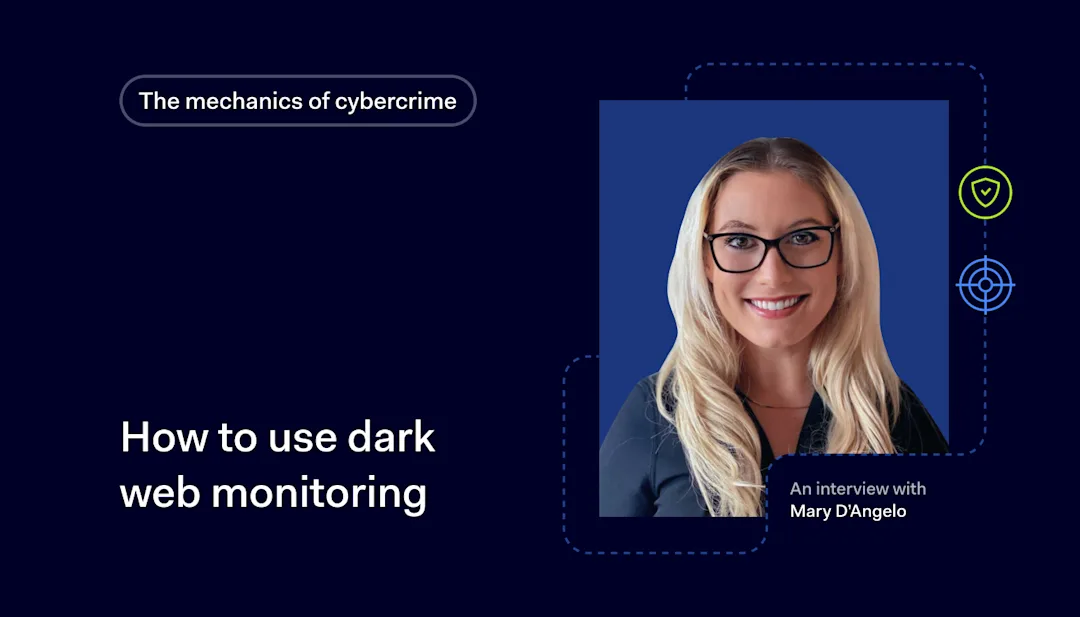
How to use dark web monitoring: a talk with Mary D’Angelo

Today is just like any other day at the office. You are going through emails and laying out plans for your company’s upcoming big project when suddenly, your screen freezes. None of the troubleshooting steps work. Quickly, your IT team becomes anxious; the company’s network has stopped working. The reason is a security breach tied to stolen credentials from RIPE, an organization that assigns IP addresses across numerous countries.

This situation is similar to what Orange Spain experienced, suffering an outage due to a hacker who improperly accessed their RIPE account. Researchers at Resecurity have noticed a troubling trend: the dark web now houses millions of stolen network operator credentials, which cybercriminals are poised to misuse.

The dark web serves as a hidden space where these stolen credentials remain unseen. It is also where attackers coordinate their plans and recruit accomplices for future breaches. 

For businesses, keeping an eye on the dark web is vital. It helps uncover new threats and trends as they arise. 

Equally important are cybersecurity practices. They shield businesses from an increasing array of cyber threats. 

By combining dark web monitoring with solid cybersecurity, businesses can establish a protective strategy to remain secure.

That’s why we talked with Mary D’Angelo, a leading Cyber Threat Intelligence and Dark Web Advisor. We discussed how the dark web works and explored why businesses might need dark web monitoring.

The interview’s highlights

  • The deep web makes up 80% of the internet, while the dark web and clear web each make up 10%.

  • The US Navy originally created the Tor network for good reasons, but now less than 1% is for whistleblowers and journalists.

  • Dark web monitoring lets businesses see planned attacks, indicating the immediate need for protection.

  • Ransomware groups are growing, and threat actors are switching to platforms like Telegram.

  • Companies should combine dark web monitoring and cybersecurity practices for early threat detection.

Key insight #1: the clear web makes up only 10% of the internet

NordLayer: To start, what is the dark web?

Mary D’Angelo: When I discuss the dark web, I refer broadly to its distinction from the deep web and the clear web. The dark web is a segment of the internet accessible only through specialized software, typically Tor, which I’ll mostly reference. It’s because Tor is the most commonly used. The deep web and clear web are other internet segments. The clear web includes anything findable via Google and other search engines. The deep web, while still accessible through search engines, comprises sites that are very hard to enter. Statistics indicate that the deep web constitutes 80% of the internet, with the dark web and the clear web each accounting for only 10%.
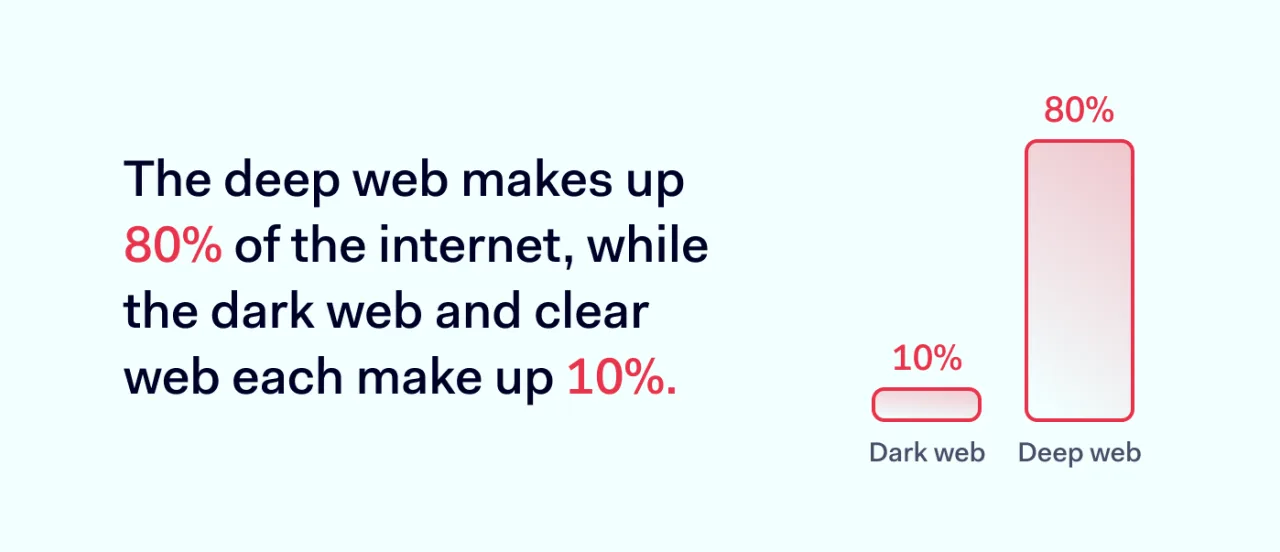
Dark web takes up to 10% of the internet

NordLayer: The dark web ensures anonymity and is technically limitless. How does the Onion Router contribute to this anonymity?

Mary D’Angelo: The Onion Router, a type of software made to connect to the dark web, encrypts messages in multiple layers, similar to an onion. These messages, when sent, pass through various relays or nodes, mixing up communications. Upon receiving a message, each relay cannot trace its origin, making it extremely difficult to track the messages and users’ activities.

Key insight #2: the original purpose of the dark web, initiated by the U.S. Navy, now makes up just 1% of its current content

NordLayer: Could you explain the legal and illegal aspects of the dark web?

Mary D’Angelo: It’s a common misconception that the dark web is entirely illegal. Initially, the Tor network was developed by the US Navy research team to enable secure communications. 

The primary purpose of the dark web was to assist journalists and whistleblowers in remaining anonymous and using encrypted messaging on a privatized platform. Over time, it has evolved to host a significant amount of illegal activity. 

It’s estimated that 40% of the dark web is comprised of child sexual exploitation material, with less than 1% now dedicated to whistleblower and journalism activities. The majority involves illegal marketplaces, threat actor forums, ransomware groups, and similar entities.

NordLayer: But the dark web also has positive uses for privacy and free speech. Can you discuss them?

Mary D’Angelo: The dark web is valuable for media organizations and individuals in censored countries, providing a secure communication channel. Organizations like ProPublica use the dark web for secure communications, offering a platform for whistleblowers and those reporting from repressive regimes.

NordLayer: Considering its origins, does the dark web offer more security than platforms like Amazon?

Mary D’Angelo: The comparison depends on what you mean by security. The dark web provides anonymity, encrypted messaging, and privacy, even for websites. Users on the dark web enjoy encrypted and anonymized communication unseen by others. Conversely, Amazon tracks all user information, making the dark web, in some respects, more secure. However, this anonymity also contributes to the prevalence of illegal activities.

NordLayer: Is regulation of the dark web a significant challenge?

Mary D’Angelo: Yes, law enforcement faces considerable difficulties in tracking down illegal activities due to the dark web’s structure. Although recent efforts have improved, the process is complex and time-consuming.

NordLayer: Can dark web marketplaces be shut down successfully?

Mary D’Angelo: Marketplaces like Silk Road and Alpha Bay have been taken down by law enforcement, involving extensive international investigations. Often, the downfall of these sites is due to the carelessness of threat actors. However, new marketplaces frequently emerge, creating a continuous cat-and-mouse game between law enforcement and dark web users.

NordLayer: How does law enforcement investigate the dark web?

Mary D’Angelo: Investigations involve collaboration with various agencies and platforms like ours that can index and search the dark web efficiently. Law enforcement builds cases on threat actors, tracking their movements and communications, often capitalizing on their mistakes to dismantle operations.

Key insight #3: dark web monitoring helps to detect the threat on its planning stage

NordLayer: How did your interest in the dark web begin?

Mary D’Angelo: My journey into the dark web began with my background in cybersecurity and network detection. Joining Searchlight Cyber, I deepened my understanding of threat intelligence and the significance of dark web monitoring to identify potential security threats to organizations.
Dark web is a hub for threat actors to plan attacks

NordLayer: Why is it important for businesses to monitor the dark web?

Mary D’Angelo: The dark web is a hub for threat actors to plan attacks. Dark web monitoring allows businesses to detect potential threats early in the planning stage, giving them more time to prevent attacks.

“You can also try NordLayer’s ThreatBlock to prevent threats. It automatically blocks access to harmful websites, making it easier to avoid entering a malicious site. You won’t see harmful ads and pop-ups, and you will be prevented from accessing websites linked to illegal activities or those marked as unsafe in trusted databases. This tool makes life easier.”

Martyna Gaidelė, Product Marketing Manager at NordLayer

Click to tweet

NordLayer: So how can organizations monitor the dark web effectively?

Mary D’Angelo: Companies like Searchlight Cyber provide services to monitor the dark web safely and efficiently, helping businesses to protect themselves without risking exposure to malicious content.
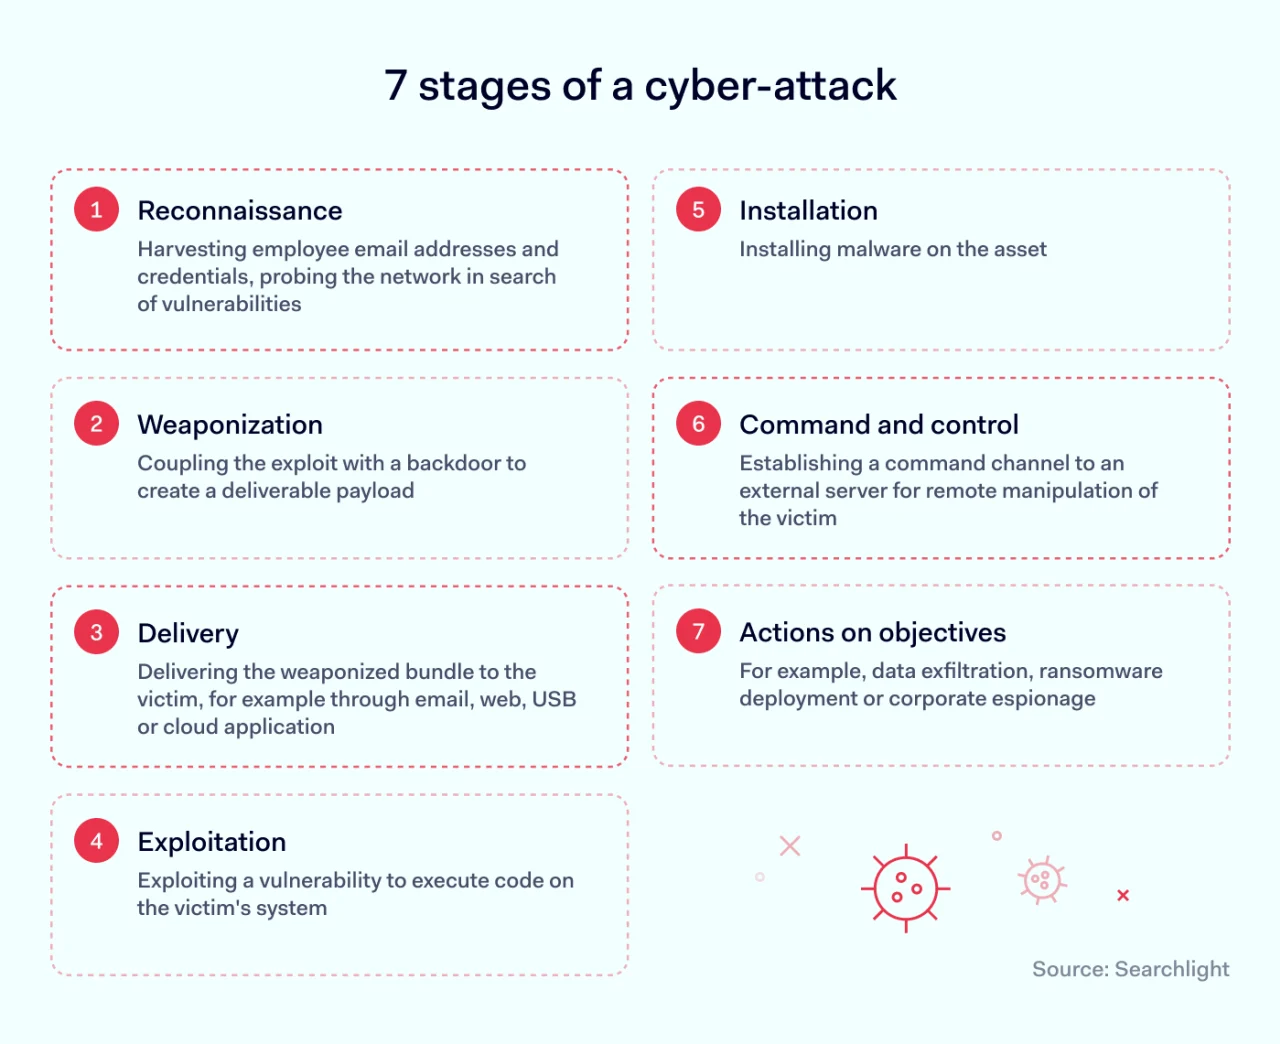
7 stages of cyber-attacks

NordLayer: Can you share a success story related to dark web monitoring?

Mary D’Angelo: Our human intelligence team does a lot of the undercover work. Accessing some dark web sites is tough; it requires specific permissions. Our team managed to enter these sites and found someone selling domain access control credentials for a large US airline. They didn’t name the airline to avoid detection but shared details like the revenue size, location, and access type. High pricing often indicates legitimacy. Upon discovering this, I contacted the airline’s security team to alert them, despite them not being our client. We then discussed the intelligence, which was new to them, and together, we devised a plan to enhance their security.

NordLayer: That’s impressive. What security measures do you generally recommend to introduce? 

Mary D’Angelo: We generally suggest enforcing multi-factor authentication (MFA) across all platforms. The approach depends on the attack type, but ensuring MFA is in place is crucial so that only authorized individuals have access.

“Multi-factor authentication (MFA) is an essential part of NordLayer. However, we advocate for a broader range of multi-layered authentication solutions and encourage our customers to implement more comprehensive Zero Trust Network Access (ZTNA) strategies.

Multi-layered network access control minimizes the risks of data breaches and aids in achieving compliance certificates, contributing to business credibility as well.

My favorite NordLayer features for network access control are the Cloud Firewall and Device Posture Security. They are easy to use and powerful solutions, ensuring advanced network access control.”

Martyna Gaidelė, Product Marketing Manager

Click to tweet

Key insight #4: Ransomware groups are hiring, which means even more attacks in 2024

NordLayer: Have you observed any trends in the dark web, such as an increase in ransomware groups?

Mary D’Angelo: Last year, we saw ransomware groups increase their recruitment. This means that they only plan to increase their attacks. They now have larger budgets because they were so successful last year in terms of the ransom payments. And so now they have more purchasing power, they can buy better exploits and better credentials. Bad actors also have their AI tool, called fraud GPT, which can just more easily and quickly make very sophisticated attacks.

Related articles


In Depth

NordLayer insights: the making of a Black Friday cyber scam

14 Nov 20238 min read

NordLayer insights: the making of a Black Friday cyber scam


Partner Program

Capitalizing on threats & opportunities – now is the time to venture into cybersecurity

17 Aug 20236 min read

Taking advantage of threats and opportunities web cover 1400x800


NordLayer: How can businesses and law enforcement adapt to the evolving threat landscape on the dark web?

Mary D’Angelo: Understanding the tactics, techniques, and procedures (TTPs) of threat actors allows organizations to build more effective defenses. Monitoring threat actor movements helps in developing predictive security measures.

NordLayer: There is also a kind of “Robin Hood” mentality among some ransomware groups. Can you elaborate on this?

Mary D’Angelo: Interestingly, some ransomware groups adhere to a moral code, avoiding attacks on hospitals and focusing on other targets. This nuanced behavior among threat actors highlights the complex ethical landscape of the dark web.
Ransomware groups have been increasing their recruitment and budgets

NordLayer: Despite some groups avoiding healthcare targets, the sector remains highly vulnerable. Why is that?

Mary D’Angelo: The healthcare sector often faces the highest ransom demands, with many hospitals lacking the security infrastructure to defend against sophisticated attacks. The sale of access credentials to healthcare institutions is alarmingly common.

NordLayer: There’s also a trend where threat actors are shifting from dark web forums to encrypted messaging platforms like Telegram. Why do you think threat actors are choosing these platforms?

Mary D’Angelo: The shift to encrypted platforms like Telegram reflects threat actors’ increasing paranoia and desire to evade detection. As law enforcement and security firms improve their monitoring capabilities, actors seek new ways to communicate securely.
Healthcare sector and ransomware

NordLayer: How do you conduct research on the deep web and platforms like Telegram?

Mary D’Angelo: Our team utilizes a combination of human intelligence and proprietary automated technologies to gather intelligence from various platforms. This allows us to monitor threat actor activities across the deep web and dark web comprehensively.

NordLayer: What future research directions do you see for dark web intelligence?

Mary D’Angelo: Collaborating with security practitioners and academic researchers can lead to innovative strategies for mitigating risks and combating cyber threats. Future research will likely focus on predictive analysis and the development of more sophisticated defense mechanisms.
Encrypted platforms need increase

Key insight #5: for businesses to stay safe, they need all employees to be aware of possible attacks

NordLayer: What general advice would you give businesses to enhance their security?

Mary D’Angelo: Businesses should prioritize early detection of threats by monitoring for reconnaissance activities. Leveraging threat intelligence to understand the landscape and adopting a proactive security posture can significantly reduce the risk of attacks.

NordLayer: How important is cybersecurity awareness?

Mary D’Angelo: Cultivating a culture of security throughout an organization is crucial. Integrating cyber threat intelligence across all levels can inform strategic decisions and prioritize security measures, ultimately making it more difficult for threat actors to succeed.
Proactive security costs less

NordLayer: In conclusion, investing in cybersecurity is more cost-effective than facing the consequences of a ransomware attack.

Mary D’Angelo: Absolutely. The cost of proactive security measures is significantly lower than the potential losses from a successful cyber attack.

How NordLayer can help

NordLayer offers a comprehensive security approach, protecting your team with Threat Prevention from harmful sites, securing online activities with VPN, and ensuring appropriate access with Cloud Firewall. Beyond these tools, we advocate for adopting Zero Trust Network Access (ZTNA), Security Service Edge (SSE), and other cybersecurity frameworks to strengthen your defense. Our sales team is always here if you need any help along the way. 

Beyond NordLayer’s offerings, it’s essential to create a culture of cybersecurity, maintain up-to-date software, and use secure communication tools. Additionally, assessing your vendors through a Third-Party Risk Management Plan and restricting their access can significantly mitigate risks.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

How to reset or change a Spotify password

The music doesn’t have to stop just because you’ve forgotten your Spotify password. This streaming service offers everything from personalized playlists to pop culture podcasts. For many of us, it’s the first stop to hear the latest music from our favorite artists. Knowing how to perform a Spotify password reset is a must, just as remembering to change your Spotify password regularly to keep your account well-protected.

How to reset your Spotify password

If you’ve forgotten your Spotify password, resetting it is the quickest option to regain access to your account. To do so, you’ll need to use your browser because it won’t work on desktop or mobile apps. Head to the Password Reset page on your browser and follow these simple steps.

  1. Type your Spotify username or email address into the text box and click “Send.”

  2. Open a new tab, navigate to your inbox, and look for an email with the subject “Reset your password.” Check your spam folder if you don’t see it within a few minutes. For Gmail users, look in the “Social and Promotion” sections.

  3. In the email, click “Reset password.”

  4. You’ll be redirected to the “Reset” page. Enter and confirm your new password.

  5. Click “Send.”

  6. You can now return to the browser or the app and log in with your new password.

It’s imperative to keep passwords secure across all your devices and profiles, but too many people still use the same login details for multiple accounts.

That can be convenient and make credentials easy to remember, but it also increases the threat posed by cybercriminals and hackers. You could be in trouble if someone broke into one of your accounts and that password was reused across many different profiles.

For this reason, you must change your password regularly and differentiate it from others.

One of the easiest and quickest ways to equip all your favorite online accounts with strong and unique passwords is by using a password generator. The NordPass Password Generator can create custom, virtually uncrackable passwords instantly.

How to change a Spotify password

Still, remember your Spotify password but want to change it today? Here’s how:

  1. Open Spotify on your browser (again, this won’t work on desktop or phone apps).

  2. Log into your account.

  3. Click on the profile icon in the upper-right corner of the screen.

  4. Click “Account.”

  5. Click “Change password.”

  6. Input your current password and your new password.

  7. Click “Set new password.”

Now you can open your app and input your new password if you’ve been automatically logged out.

Frequently asked questions


Does Spotify send emails to reset passwords?


How often should I change my Spotify password?


May I use special characters in my password?


What if I can no longer access the email linked to my Spotify account?


Is there a limit to the number of password reset attempts?


Keep your passwords safe with NordPass

Changing your password with ease is always helpful, and it’s an integral part of best practices in digital security.

To avoid this problem of having to change or reset your passwords, you can and should use a password manager.

NordPass is a secure and intuitive password manager built to make your life easier. With NordPass, you can securely store your login details for your favorite online accounts, credit card details, personal information, and secure notes.

One of the best things about NordPass is the Autofill enhanced by machine learning, which automatically fills out online forms, credit cards, and passwords for you.

Additionally, NordPass comes equipped with advanced security features. One of those goes by the name of Password Health and helps you detect weak, old, or reused passwords. Another one, known as a Data Breach Scanner, allows you to find out if any of your personal information has been compromised in a data breach.

These days, with cybercrime on the rise, having a password manager should be a no-brainer.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

The role of machine learning in cybersecurity

Humans simply can no longer tackle the exponential growth of sophisticated online security threats in a timely and effective manner. Hence, automating cybersecurity processes with artificial intelligence (AI) and machine learning (ML) powered systems becomes vital. 

So, does that mean IT teams will become redundant soon, as AI-based security tools can do it all? Simply put, no. But for a more in-depth answer, we’ll need to first understand what machine learning in cybersecurity is and what this technology holds for businesses in the future.

What is machine learning?

Machine learning refers to the ability of algorithms to learn patterns from existing data and use this knowledge to predict outcomes on new, previously unknown data without explicitly being programmed. The more information you feed to the machine learning engine, the more data it can analyze and, consequently, become more accurate.

But what does it mean to say that a machine is learning from the existing data? While traditional programming performs simple and predictable tasks by strictly following detailed instructions, machine learning allows the computer to teach itself through experience. In other words, it mimics human behavior in how to solve problems.

However, the fact that machine learning can improve itself isn’t the only reason why it’s so easy to find its models in the online wilderness. The sheer amount of information that businesses in different industries currently have to manage has become too vast for humans to tackle alone. As a result, companies rely on machine learning to process that data and quickly generate actionable insights.

For instance, an ML technique called a decision tree solves classification dilemmas and uses certain conditions or rules in the decision-making process. This particular technique is widely used in fintech (for loan approval and credit scoring) and marketing.

Machine learning solutions are also helpful for businesses in harvesting, organizing, and analyzing large volumes of customer data. This can include purchasing history or individual customer’s typical behavior, such as online browsing habits. With such analyzed data, companies can then recommend relevant products tailored to their customers’ preferences. Think Netflix: With an ML-driven model, it examines its users’ histories on the platform to compile appropriate content recommendations for them to choose from. This increases the time users spend watching Netflix content and their overall satisfaction. Similarly, ML models pick up information relevant to the unique user on the Facebook feed and even moderate content on Instagram.

In addition, in most customer support self-service tools, users usually interact with a machine rather than a fellow human being. Such chatbots can answer basic questions and guide a person to relevant content on the website.

Lastly, even in the medical field, machine learning plays a huge role. These models can be trained to examine medical images or other information and then search for illness characteristics.

Four types of machine learning

Machine learning traditionally has four broad subcategories that are defined by how the machine learns:

  • Supervised machine learning models rely heavily on “teachers”, meaning models that are trained with labeled data sets, which allow them to learn and become more accurate over time. For instance, if you want to teach the algorithm to identify cats, you’ll have to feed it with pictures of cats and other things, all labeled by humans.

  • Unsupervised machine learning looks for patterns and common elements in data. In turn, such machine learning can find similarities and trends that humans aren’t explicitly looking for.

  • Semi-supervised machine learning falls somewhere between supervised and unsupervised learning. In this case, the model is trained on a small amount of labeled data and lots of unlabeled data. Such a way of learning is beneficial when there’s a lot of unlabeled data, and it’s too difficult (or expensive) to label it all.

  • Reinforcement machine learning is where an algorithm learns new tasks by interacting with a dynamic environment. Here, it is rewarded for correct actions, which it strives to maximize, and punished for incorrect ones. Such machine learning is widely used in cybersecurity, as it enables a broader range of cyber attack detection.

Machine learning use cases in cybersecurity

As cybersecurity is a truly fast-paced environment where threats, technologies, and regulations constantly evolve, it’s the agility of machine learning that comes in handy.

ML-powered models can process massive amounts of data and, therefore, rapidly detect critical incidents. This means that machine learning enables organizations to detect various types of threats like malware, policy violations, or insider threats by constantly monitoring the network for anomalies. It is so because ML-driven algorithms learn to identify, for instance, new malicious files or activity based on the attributes and behaviors of previously detected malware.

In addition, using machine learning proves to be a good method for filtering your company’s inbox from unsolicited, unwanted, and virus-infected spam emails, which may contain pernicious attachments such as malware or ransomware. For instance, the machine learning model used by Gmail not only sifts through spam but also generates new rules based on what it has learned in the past. ML methods, coupled with natural language processing techniques, can also detect phishing domains by picking on phishing domain characteristics and features that distinguish legitimate domains.

Last but not least, machine learning can significantly support online fraud detection and prevention. By using ML algorithms, companies can identify suspicious activities in transactional data. These algorithms are trained to recognize normal payment processes and flag suspicious ones. Also, ML-driven engines can be trained to spot when cybercriminals change their tactics as they automatically will retrain themselves to recognize a new fraud pattern.

These examples illustrate just a few use cases of machine learning in cybersecurity. But there are many others, such as vulnerability management, that can greatly impact business cybersecurity.

So, is it AI, machine learning, or deep learning?

Oftentimes, these terms – artificial intelligence, machine learning, and deep learning (DP) – are used interchangeably. We already defined machine learning, so now, let’s see how it relates to artificial intelligence and deep learning.

Artificial intelligence, in the broadest sense, is a set of technologies that enable computers to perform various advanced tasks in a way similar to how humans solve problems. This makes machine learning a subfield of artificial intelligence.

In turn, deep learning is a subset of machine learning. It mimics the structure and functions of the human brain. Such systems use artificial neural networks that function like neurons in the brain. These neurons, also referred to as nodes, are used in chatbots or autonomous vehicles.

Difference between machine learning, artificial intelligence, deep learning, and cybersecurity

Even though machine learning brings some challenges when applied to cybersecurity (for instance, the difficulty in collecting large amounts of certain malware samples for the ML machine to learn from), it remains the most common approach and term used to describe AI applications in this industry.

In cases where shallow (or traditional machine learning) falls short, deep learning should be used. For example, when dealing with highly complex data such as images and unstructured text or when temporal dependencies have to be taken into account.

inner asset machine learning


The future of machine learning in cybersecurity

In the current AI tool-filled climate, it’s easy to see how this technology can become better at specific tasks than we humans are. Luckily (or not), machine learning is not a panacea to all things cybersecurity. However, it provides and will continue to provide a great deal of support to cybersecurity or IT teams by reducing the load off of their shoulders.

Since many devices (like phones and laptops) connect to the company’s networks daily, it is almost impossible for IT teams to monitor every single gadget. With AI-powered device profiling, you can improve the fingerprinting of endpoint devices and better understand the type and quantity of endpoints connecting to your network. This will help you create effective segmentation rules and stop unwanted devices (potentially including bad actors) from connecting.

Also, employing machine learning can improve your cybersecurity game by helping your IT team develop policy recommendations for security devices such as firewalls. In this case, machine learning learns what devices are connected to the network and what constitutes normal device behavior. In turn, ML-powered systems can make specific suggestions automatically — instead of your team manually navigating different conflicting access control lists for each device and network segment.

So, embracing more ML-driven cybersecurity practices into your daily company’s processes seems vital if you want to improve your cybersecurity in the future. With more devices and threats coming online daily, the human resources available to tackle them are becoming scarce. In such an environment, machine learning can step in by helping sort out various complicated cybersecurity situations and scenarios at scale while maintaining constant surveillance 24/7.

How does NordPass use machine learning?

Machine learning offers a wide range of applications for businesses, from applying it to cybersecurity to simply enhancing customer satisfaction. With artificial intelligence still making headlines, we’ll likely see even more use cases in the future that will benefit the company’s cybersecurity as well.

NordPass is one of the companies that use machine learning. We do so to offer more accuracy and convenience for our customers. Our autofill engine relies heavily on machine learning to accurately categorize the field that it needs to fill in on a website or app – no matter if it is a sign-up, credit card, or personal information form. Remember those artificial neural networks? It has been trained using exactly those!

If you’re interested in improving your employees’ online experience and enhancing overall company security, explore what enterprise password management can offer for your company.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.