Skip to content

Quantum encryption: a new era of cybersecurity innovations

As we embrace the digital world, the threat of cyber-attacks grows, and so does our need for robust cybersecurity measures. Innovative and powerful solutions like quantum encryption are carving out their cybersecurity niche.

This groundbreaking technology leverages the complex principles of quantum mechanics to offer seemingly impregnable security. But what is quantum encryption, and how does it impact our digital security? Let’s find out.

What is quantum computing?

Quantum computing is a key principle underpinning quantum encryption. Traditional computers use bits (0s and 1s) to process information. However, quantum computers use quantum bits, or “qubits”.These “qubits’ can exist in multiple states at once thanks to a quantum phenomenon known as superposition. This allows quantum computers to process an astronomical amount of data at mind-boggling speeds, far beyond the capabilities of traditional computers.

Let’s use quantum computing in a light switch analogy to understand the superposition better.

classic computing and quantum computing comparison💡 If a regular bit is like a light switch that can be either on (1) or off (0), then “a qubit” is like a dimmer switch that can blend different levels of on and off at the same time. This superposition property allows a qubit to hold and process an enormous amount of information compared to a classical bit.

When a quantum system is in a superposition state, it is in multiple states at once, each with its probability. However, once a measurement is made, the “qubit” collapses from this superposition into one of the probable states and gives an output accordingly.

This unique characteristic of “qubits”—being in multiple states at once—enables quantum computers to process countless outcomes simultaneously, providing them with potentially immense computational power.

What is quantum encryption?

🔑 Quantum encryption is a cutting-edge approach to securing information transfer, built on principles of quantum mechanics. This method utilizes quantum bits, or “qubits”, rather than traditional binary bits, to encrypt and decrypt data.

Click to tweet

Quantum encryption uses another quantum concept – entanglement. Entanglement is a phenomenon where two particles, regardless of distance, are linked so that the state of one immediately influences the other.

This principle is applied in Quantum Key Distribution (QKD), where the key for encrypted data decryption is shared through entangled particles. Any attempt to intercept the particles triggers a change in their state, thus alerting the intended recipients to a possible breach.

Benefits of quantum cryptography

The invulnerability to interference provides quantum encryption with an unprecedented level of security. Because of the complexity, traditional cryptographic systems can’t match the new upcoming standard.

Instant detection of breaches

Eavesdropping, or man-in-a-middle attacks, concerns current encryption methods, become nearly impossible in a quantum encryption setup.

👂 Eavesdropping, in the context of encryption and cybersecurity, refers to an attack where a malicious actor intercepts and listens in on private, encrypted communication without the knowledge or consent of the communicating parties.

Click to tweet

The ultimate goal is to steal sensitive information, such as personal details, login credentials, or encryption keys. Interruption of a third party alters the status of the particles and alerts the sender and receiver about the attempted attack because it’s impossible to observe a quantum system without disturbing it.

The complex power of physics

The sheer computational power of quantum computers could be used to break traditional encryption algorithms, making the development of quantum-resistant algorithms necessary.

Mathematics-based and Physics-based cryptography comparison

Pioneering research is currently underway to develop these quantum-resistant algorithms. The aim is to create encryption techniques robust enough to withstand attacks from quantum computers.

Many organizations, including prominent tech corporations and government entities, invest significantly in these cutting-edge initiatives, preparing for the quantum computing revolution.

Challenges of quantum encryption

The implications of quantum encryption for the cybersecurity industry are profound. It could revolutionize how data is secured when fully realized, making some of today’s most sophisticated cyber-attacks obsolete.

Business adoption to change

Quantum cryptography sets a new security standard, compelling organizations worldwide to adapt or risk becoming easy targets for quantum-powered attacks. Flexibility and easy transition to new technologies become essential requirements.

Early stages of technological development

The path to universal quantum encryption is full of challenges. Quantum computers are still in their developmental stages, with only a handful of operational prototypes. Underdeveloped concepts keep encryption in a premature, almost theoretical stage, meaning quantum cryptography isn’t available any time soon.

Extreme storage conditions

Quantum computers also require frigid environments and careful handling of “qubits” to prevent decoherence – a premature loss of quantum states. Additionally, creating a global network of quantum computers for widespread quantum encryption is a mammoth task requiring substantial investment and technical breakthroughs.

Quantum cryptography and NordLayer

While quantum encryption holds great promise for the future of cybersecurity, its implementation is a significant undertaking. The journey is riddled with technological challenges and substantial costs. However, given the immense potential benefits, pursuing quantum encryption is critical in this ever-evolving digital age. Get ready to witness a quantum leap in cybersecurity innovation.

In the meantime, NordLayer offers services utilizing AES 256-bit encryption, the industry’s highest cryptographic standard. This approach is more accessible as it’s widely implemented, mature and can be operated on existing digital infrastructures. Combined with other network access securing features, AES 256-bit encryption minimizes the risk of a data breach. Reach out to learn more about NordLayer’s security solutions for your organization.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

NordLayer 客戶案例 DataWalk 如何在 20 分鐘之內部署安全網絡

重點內容:

  • DataWalk 是一家位於波蘭、英國和美國的商業情報公司,每天需要處理大量來自企業和政府機構的敏感數據資源。
  • 正尋求一個低維護成本的企業級資訊安全方案,特別是對於初創和快速擴張的企業而言,他們常常面臨資源匱乏的情況。
  • NordLayer 提供了一個快速、輕鬆、有效的解決方案,減輕了 IT 部門的工作負擔。
  • 具有簡單的集成標準,確保與其他系統的兼容性,增強而不是破壞公司的生態系統。
  • 在最終用戶和 IT 管理員之間達到平衡,能夠輕鬆安裝和管理,提高整體效率。
  • 20 分鐘部署網絡基礎架構升級,簡單無縫地融入現有的公司基礎架構中。

資訊安全議題往往只著重於處理惡意行為和威脅解決方案,卻鮮少關注到 IT 經理的角色。然而,IT 經理的決策以及他們對於安全需求的重視,往往會對資訊安全的優先排序和時間管理產生影響。尤其對於初創和快速擴張的企業而言,它們常常面臨資源匱乏的情況,並且將開發可信賴且高效的產品視為當務之急。

DataWalk 是一家位於波蘭、英國和美國的商業情報公司,每天都必須處理大量來自企業和政府機構的數據資源。該公司擁有由 130 多名員工組成的團隊,主要專注於開發數據分析軟件,旨在揭示商業營運中詐欺和洗錢的隱藏模式和聯繫。在追求可信賴和高效產品的同時,他們的DevOps 工程師兼部署架構師 Thomas Vodrazka 分享了他在建立和執行資訊安全路線圖方面的見解,並討論了公司自成立以來所面臨的挑戰。

面臨的挑戰
DataWalk 尋求低維護成本的企業級資訊安全方案

DataWalk 是一家處理相對敏感大數據資訊的公司,因此資訊安全是他們的首要關注項目之一。作為一個軟件供應商,他們在 AWS 雲端服務上運行,並使用各種配置來展示試用、測試和離線資料處理環境。隨著國際團隊成員的增加,公司網絡的流量負載也隨之增加。起初,對於一家小型公司來說,內部的 VPN 和伺服器足以應對需求。然而,隨著公司的服務範圍擴大和內部使用者數量增加,本地 VPN 面臨著流量快速增長的巨大壓力。

在尋找替代方案的同時,DataWalk 選擇將部分流量轉移到共用 IP 環境以減少本地伺服器負載,這是一個合理的快速解決方案。此舉不單成本效益高,且維護工作由第三方負責。然而,儘管公共伺服器可能是最佳選擇,但仍存在與其他伺服器使用者發生腳本衝突的風險。此外,共用閘道器也具有配置限制,對於一家需要安全環境以提供服務的公司來說,這可能成為一個不確定因素。

「作為一名 IT 系統管理員,你必須負責監督許多不同的領域,以確保業務運作和安全政策能夠順利且充分執行。尤其在小型工作團隊中,時間成為至關重要的資源,因此理所當然地,我們會優先尋找能夠保護我們的解決方案。」Thomas Vodrazka 說道。

在安全服務供應商中,提供具有專用 IP 選項的 VPN,介乎於自主維護的本地伺服器和公共閘道器之間。這種解決方案提供了安全性,同時減輕了維護的負擔。然而,如何將額外的安全性整合到公司的基礎架構中,同時不會給內部使用者帶來繁雜的操作和困惑呢?

NordLayer 提供了一個「增強而不是破壞公司的生態系統」的解決方案
以減輕 IT 經理的工作負擔

作為公司開發流程的先驅者,IT 經理在這個過程中擁有最大的自由度,但也承擔相應的責任。他們可以嘗試在企業層面引入有影響力的解決方案。然而,一旦這些解決方案被實施,系統就需要額外的安全措施。因此,DataWalk 最終轉向更為簡單易用的解決方案,以確保系統的安全性。

Thomas Vodrazka 補充說:「我和公司的 CTO 一起開始使用 NordVPN,該服務提供了我們所需的一切功能和界面。這激發了我對商業版本的好奇,我開始向周遭詢問是否有相應的商務解決方案。很快,我們就全面轉向了NordLayer,讓不同地方的員工能夠安全地存取公司的資源。」對於 IT 經理來說,如果新工具的設置對其他員工而言過於複雜,這可能會造成一些不便。

這個解決方案需要在最終用戶和 IT 管理員之間達到平衡,讓他們能夠輕鬆安裝和管理工具,從而提高整體效率。同時,該解決方案需要具有簡單的集成標準,以確保與其他服務供應商的兼容性,並增強而不是破壞公司的生態系統。

NordLayer 解決方案的其他功能,例如遙距桌面協議(RDP),在需要更頻繁地進行遙距疑難排解和存取同事終端的情況下,也顯得非常有價值。當 IT 管理員位於不同地區,且遙距團隊缺乏解決問題所需的知識或技能時,虛擬協助對於 IT 管理員來說是一個極其重要的支援工具。

20 分鐘之內部署安全網絡
快速、輕鬆、有效的網絡基礎架構升級

IT 系統管理員本身就是最終用戶之一,這使得他們能夠輕鬆進行公司系統的技術升級和整合。這種自主性為他們留出更多的空間來規劃和測試定制的資訊安全策略,以應對各種安全場景,包括最佳和最糟的情況。

「只需 20 分鐘的配置時間,就可以封鎖公共存取並更改 IP 地址。它就是那麼簡單。我不再需要擔心 VPN 了,這讓我節省了時間,並能夠更好地運用這段時間。」Thomas 說道。

NordLayer 的一個優勢是它可以在幾分鐘內進行部署,簡單的安裝過程能夠無縫地融入現有的公司基礎架構中。DataWalk 在美國和歐洲使用了兩個虛擬私有閘道器,所有管理員需要做的就是進行一次配置,然後就可以不再擔心它了。透過集中控制面板協助 IT 系統管理員,促進內部審計的進行。此外,如果您的團隊遇到任何問題,他們可以依靠全天候 24/7 的客戶支援團隊提供協助。

產品資料:
https://version-2.com/nordsecurity

下載「DataWalk 如何在 20 分鐘之內部署安全網絡」使用案例:
https://version-2.com/nordlayer-landing-page-datawalk-usecase/


關於 NordLayer
NordLayer 是現代企業的自適應性網絡存取安全解決方案,來自世界上其中一個最值得信賴的網絡安全品牌 Nord Security。致力於幫助 CEO、CIO 和 IT 管理員輕鬆應對網絡擴展和安全挑戰。NordLayer 與零信任網絡存取(ZTNA)和安全服務邊緣(SSE)原則保持一致,是一個無需硬件的解決方案,保護公司企業免受現代網絡威脅。通過 NordLayer,各種規模的公司企業都可以在不需要深入專業技術知識的情況下保護他們的團隊和網絡,它易於部署、管理和擴展。

關於 Version 2 Digital
Version 2 Digital 是亞洲最有活力的IT公司之一,公司發展及代理各種不同的互聯網、資訊科技、多媒體產品,其中包括通訊系統、安全、網絡、多媒體及消費市場產品。透過公司龐大的網絡、銷售點、分銷商及合作夥伴,Version 2 Digital 提供廣被市場讚賞的產品及服務。Version 2 Digital 的銷售網絡包括中國大陸、香港、澳門、台灣、新加坡等地區,客戶來自各行各業,包括全球1000大跨國企業、上市公司、公用機構、政府部門、無數成功的中小企及來自亞洲各城市的消費市場客戶。

A complete guide to WordPress security best practices in 2023

Most of the web content that you come across online is made possible by a content management system (CMS). WordPress is probably one of the best-known CMS platforms, which powers a staggering 43% of all websites globally. 

Its scalability, user-friendly interface, and robust customization options have catapulted it to the forefront of content management systems. However, as its popularity has grown, so has the interest of cybercriminals.

This article guides you through best security practices for your WordPress site. By adopting beginner-friendly practices such as secure hosting, regular updates, strong usernames/passwords, and two-factor authentication, you can significantly bolster your site’s defenses against threats.

Assessing WordPress security

Just like any other system, WordPress isn’t immune to security vulnerabilities. The distinction should be made between two things: the security of WordPress as a product and various factors like third-party plugins and extensions. While the majority of them are developed by reputable sources, the sheer volume of plugins means that some may have exploitable loopholes.

As an open-source platform, WordPress boasts a vibrant community dedicated to the ongoing mission of patching vulnerabilities and enhancing security. Yet, over the years, numerous threats have emerged, from cross-site scripting (XSS) attacks to SQL injections, placing WordPress security at the top of user priorities.

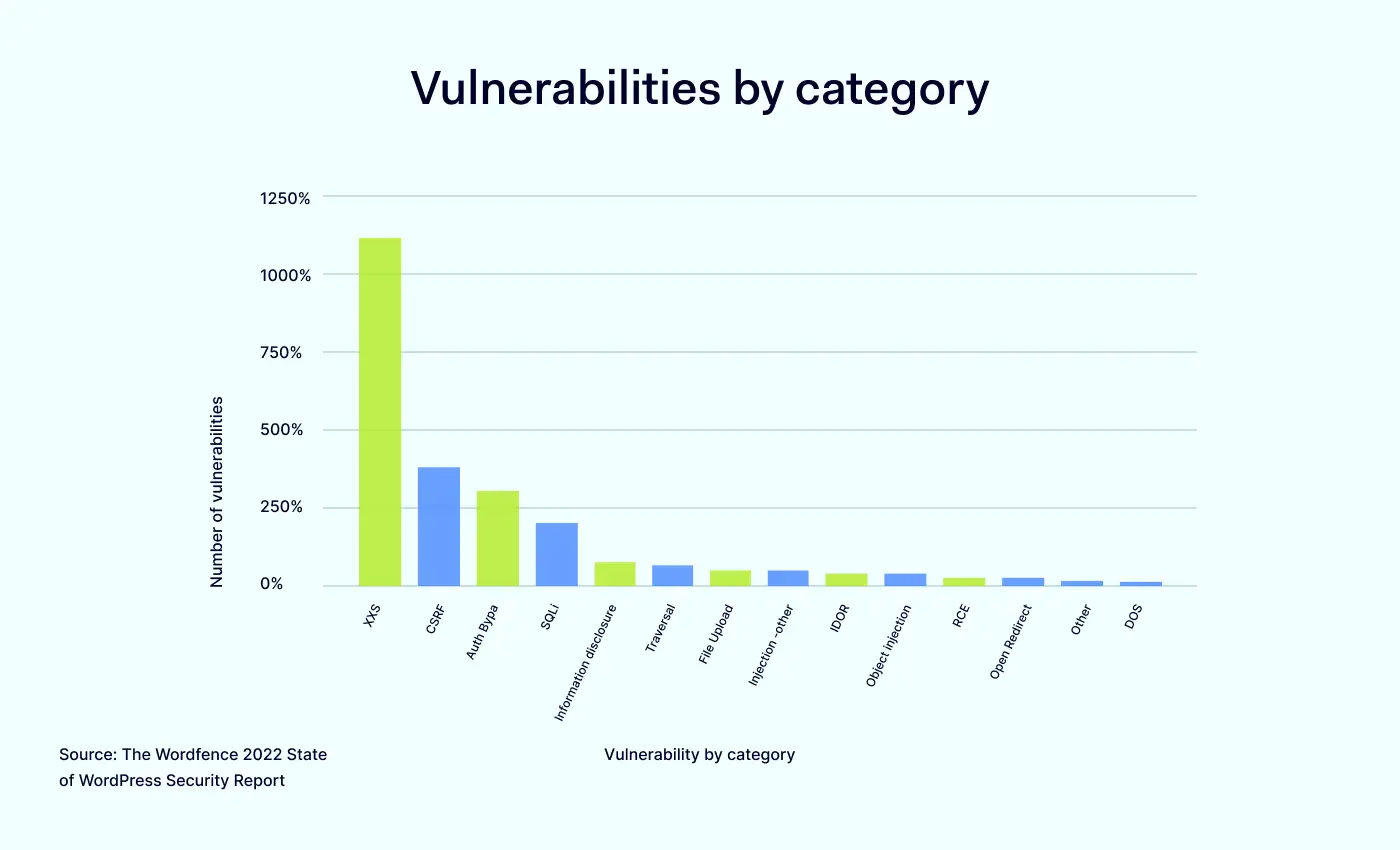
The bad news is that these vulnerabilities aren’t theoretical, and they can bring actual harm, resulting in data breaches and severe reputational damage. A study conducted in 2022 by Wordfence shows that XSS and CSRF vulnerabilities have significantly increased in volume. These statistics are alarming enough to be a wake-up call for network administrators to prioritize comprehensive website protection.

Main WordPress vulnerabilities

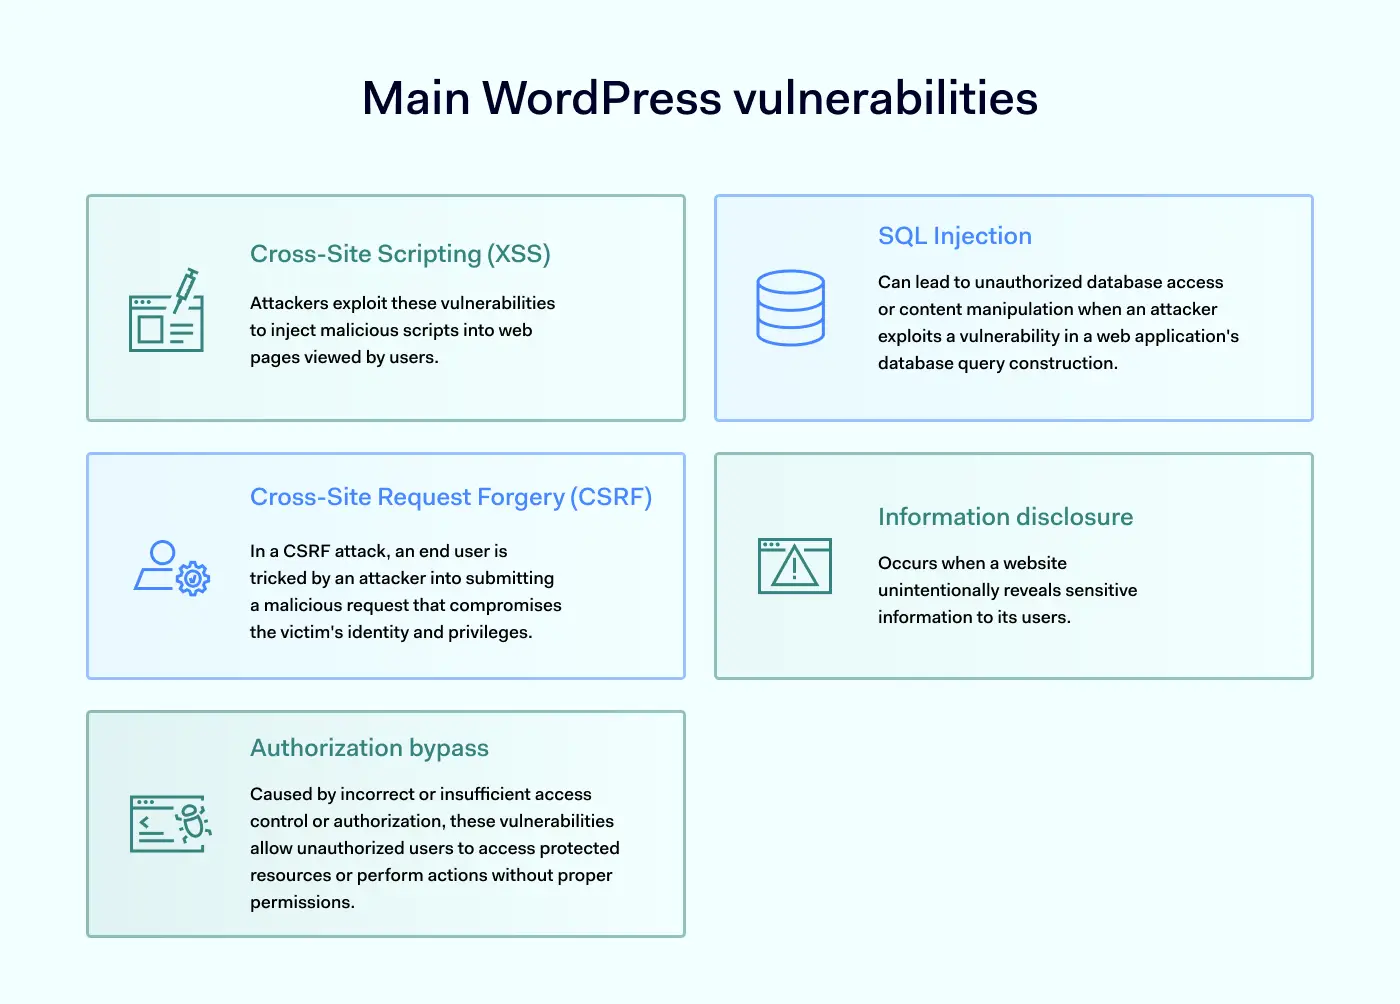
To ensure your WordPress site’s security, it’s important to have a basic understanding of common vulnerabilities. In 2022, several types of vulnerabilities were prominent, and it’s essential to delve deeper into each of them to prepare ourselves against possible threats.

Cross-site scripting (XSS)

Cross-site scripting, or XSS, accounted for nearly half of all vulnerabilities disclosed in 2022, with 1,109 submissions. These types of vulnerabilities can allow attackers to inject malicious scripts into web pages viewed by users. However, it’s worth noting that a significant number of these vulnerabilities, 408 to be exact, required administrative permissions to exploit, making them less severe than typical XSS vulnerabilities.

Cross-site request forgery (CSRF)

The second most common vulnerability was cross-site request forgery (CSRF), with 377 disclosed vulnerabilities. In a CSRF attack, an innocent end user is tricked by an attacker into submitting a malicious request. It inherits the victim’s identity and privileges to perform an undesired function on its behalf.

Authorization bypass

Authorization bypass vulnerabilities ranked third in the list of common vulnerabilities for 2022. This category includes vulnerabilities primarily caused by incorrect or insufficient access control or authorization. They could potentially allow unauthorized users to access protected resources or perform actions without proper permissions.

SQL injection

SQL Injection vulnerabilities were the fourth most common, with 200 cases disclosed. In these types of attacks, an attacker exploits a vulnerability in a web application’s database query construction, leading to unauthorized database access or content manipulation.

Information disclosure

Finally, rounding out the top five is Information Disclosure, with 73 disclosed vulnerabilities. It refers to instances where a website unintentionally reveals sensitive information to its users. This could range from technical details of the web application to users’ personal information.

Understanding the significance of WordPress security

Every WordPress user, from individual bloggers to multinational corporations, must understand what compromised website security means. For businesses, it translates into massive financial losses, a dent in customer trust, and potential compliance penalties. Individuals are also at risk of having their personal information stolen and used by cybercriminals, so the stakes are equally high.

In an era defined by digital connectivity, website security is an absolute necessity, not a luxury. It is time to shift our mindset from reactive to proactive. By taking the initiative and implementing robust security measures, we can significantly lower the risk of our websites falling victim to cyberattacks.

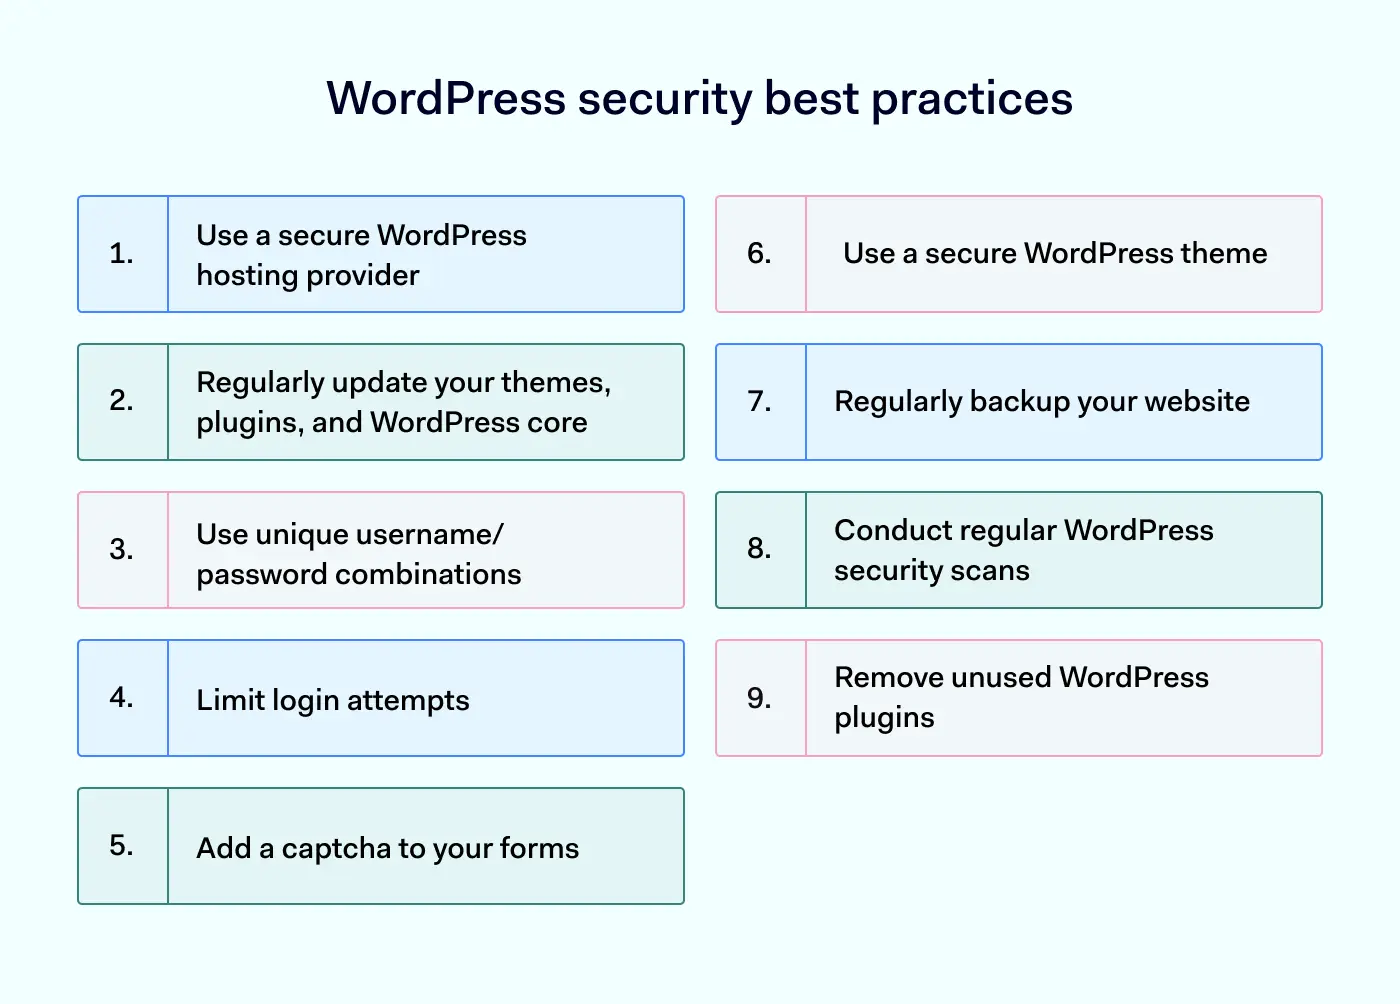
WordPress security best practices

Navigating through the labyrinth of WordPress security can seem daunting at first. This is due to the fact that overall security tips can be categorized into practices involving plugins and without plugins. As a third-party software that can be installed on a WordPress site to extend its functionality, they can provide various additional security measures. However, like any software, security plugins themselves can have vulnerabilities or backdoors that hackers could exploit.

On the other hand, security tips without plugins focus on manual implementation or modifying the WordPress installation directly. Both approaches have their own advantages and disadvantages. Therefore, striking a balance between relying on security plugins and following general security practices is crucial.

Use a secure WordPress hosting provider

Choosing a WordPress hosting provider is the first line of defense against potential cyber threats. A reputable hosting provider prioritizes data security and implements measures to safeguard your website’s data, including backups, encryption, and secure data storage. A good host ensures that your website is well-protected at the server level.

Regularly update your themes, plugins, and WordPress core

Software, including WordPress themes, plugins, and the core itself, can contain vulnerabilities. Updates often include patches for known security vulnerabilities, so updating all the mentioned components is crucial. This is the only way to ensure that you have the latest security patches and fixes, reducing the risk of your website being exploited by hackers or malware.

Use unique username/password combinations

Simple login credentials can be an open door for hackers. Avoid using ‘admin’ as your username, and ensure your passwords are complex and unique. A good password includes uppercase and lowercase letters, numbers, and special characters. A password manager like NordPass can help you create strong passwords and store these safely.

Limit login attempts

Limiting the number of failed login attempts can prevent brute-force attacks. WordPress offers various plugins that can lock out a user’s IP address after a certain number of failed login attempts is reached. This makes it more difficult for hackers to try username/password combinations to log in.

Add a CAPTCHA to your forms

Adding CAPTCHA (Completely Automated Public Turing test to tell Computers and Humans Apart) to WordPress can help prevent spam and bot submissions on your forms. Bots are often used to launch various types of attacks, such as submitting spam comments, brute-forcing WordPress login page, or submitting malicious code. CAPTCHA makes it harder for automated systems to engage with your site and potentially cause harm.

Use a secure WordPress theme

Not all themes are created equal. Choose themes from reputable sources that prioritize security. Opt for themes that have well-structured, clean, and secure code. Themes that follow coding best practices reduce the likelihood of security vulnerabilities. Always check ratings, reviews and update frequency before deciding on a theme.

Regularly backup your website

Regularly backing up a WordPress website is a safety net. If something goes wrong, you can always revert to a previous WordPress version of your site. Regular backups ensure that your website’s content, including posts, pages, images, and databases, are securely stored and can be recovered. Remember, it’s important to store backups securely, preferably off-site or in a separate location from your live website.

Conduct regular WordPress security scans

Regular security scans help detect vulnerabilities and malware that have slipped through the cracks. Once identified, vulnerabilities and other weaknesses in your website’s security can be addressed with fixes. This process provides a pace of mind and knowledge that proactive measures are being taken to protect not only the website, but also its visitors.

Remove unused WordPress plugins

Like most, you probably have tried different WordPress plugins but didn’t remove them after you tried them out. Yet, outdated or unused plugins can pose a security risk to your website. If a plugin is not regularly updated by the developer, it may contain vulnerabilities that can be exploited by hackers. Going through them and removing unused ones will reduce the number of openings a malicious actor can use to access your site.

How to secure access to WordPress

WordPress security best practices provide a solid foundation for improvements. However, it’s also a good idea to implement a wider range of security features beyond WordPress itself. While plugins and built-in control can help a lot, more sophisticated solutions may sometimes be required. Here are actionable steps you can take when securing your digital environments.

Secure Access with a VPN

WordPress site security can be improved by using a Virtual Private Network (VPN). A VPN encrypts exchanged data traffic, making it difficult for hackers to intercept your information between your user devices and WordPress servers. By routing your traffic through a VPN, you add a layer of security to your WordPress access, protecting your site from potential attacks.

Implement SSO and MFA

Implementing single sign-on (SSO) and multi-factor authentication (MFA) SaaS access control solutions can significantly enhance the security of your WordPress website. SSO allows users to authenticate once and gain access to multiple systems or applications without needing to log in separately. Meanwhile, MFA adds an extra layer of security by requiring users to provide additional verification factors beyond a password to access their accounts. These solutions make it much more difficult for unauthorized users to gain entry into your WordPress resources.

Allow connections only from trusted IP addresses

Restricting access only to allowed connections helps to enhance the security of your WordPress website. By limiting connections only to trusted IP addresses, you prevent unauthorized individuals or bots from gaining access to the WordPress administrative area. IP Allowlisting can play a significant role in adopting a Zero Trust security posture. However, it’s essential to carefully assess your specific security requirements, user base, and potential limitations as not to introduce additional limitations for your user base.

Segment your network into smaller parts

Consider implementing network segmentation, which involves dividing your network into smaller parts. By segmenting the network (for instance, with a web application firewall), you can separate different components of your WordPress infrastructure, such as the web server, database server, and application server. This isolation ensures that if one component is compromised, the attacker’s access is limited to that specific segment, reducing the potential impact on other parts of the network.

Encrypt your held data

Data encryption plays a crucial role in enhancing WordPress security by providing a layer of protection for sensitive information. By encrypting the data, it becomes scrambled into an unreadable format that can only be deciphered with the appropriate decryption key. This prevents unauthorized individuals from intercepting and understanding the data, significantly enhancing the overall security posture.

Implement access management controls

Access management controls allow you to define who can access your WordPress website and what level of access they have. By properly assigning roles, you can limit access to critical functions and sensitive areas of your website. For example, you can have administrators who have full control over the site, editors who can manage content, and subscribers who only have basic access. With such tools you gain granular control over who has access to what within your WordPress site, enhancing your site’s security profile.

FAQ

Can I secure my WordPress website without technical expertise?

Yes, implementing basic security practices like using strong passwords, keeping WordPress updated, and enabling two-factor authentication can be done without extensive technical knowledge. However, for advanced security measures, it is advisable to seek assistance from a professional.

How often should I update my WordPress website?

Regular updates are crucial for maintaining security. Update your WordPress installation, themes, and plugins as soon as new versions become available. Aim to check for updates at least once a week.

Are free themes and plugins safe to use?

Not all free themes and plugins are unsafe, but caution is advised. Stick to reputable sources like the official WordPress repository or trusted third-party marketplaces. Always review user ratings, read reviews, and ensure they receive regular updates and support.

What should I do if my WordPress website is hacked?

If your WordPress website is hacked, take immediate action. Change all passwords, restore your website from a recent backup, and scan your site for malware using security plugins. Consider consulting with a professional to ensure all vulnerabilities are addressed.

Can a security plugin alone protect my website?

While security plugins provide valuable features, they should be seen as part of a comprehensive security strategy. Combine security plugins with other practices, such as regular updates, strong passwords, and secure hosting, to create a robust defense against threats.

How can NordLayer help?

Securing your WordPress site involves an ongoing effort and frequent upgrades. It means taking care of your WordPress core and installing strong protections like IP allowlisting to enhance your resistance against potential cyber-attacks. However, this is only the start, since the security environment is enormous and difficult to traverse alone.

This is where NordLayer can help. One of the features we offer is IP allowlisting, which enables organizations to control access to internal resources by specifying trusted IP addresses. Simultaneously, we also provide fixed IP addresses, ensuring that you can implement IP allowlisting effectively and maintain a more secure environment.

Additionally, we understand the importance of network segmentation to enhance security further. By dividing your network into smaller, isolated segments, we help create barriers limiting potential threats from spreading laterally within your infrastructure. We also offer the ability to provide exclusive access rights for those who specifically need to access your WordPress work environment within your organization.

However, we don’t stop there. We go the extra mile to secure your WordPress environment by implementing a robust two-factor authentication (2FA) process. With 2FA, even if someone has access rights, they will need to undergo an additional layer of verification beyond the standard login credentials.

Contact us now to discover how we can boost the security of your WordPress site while ensuring simplicity of use and seamless operations.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Futurespective 2033: cyber threats in 10 years, according to AI

Knowing what will happen in the future is rather a balance between a guessing game and precise algorithmic estimations.

Driven by curiosity about technology advancements, Ray Bradbury’s “Fahrenheit 451” predicted earbuds, Douglas Adams’ “The Hitchhiker’s Guide to the Galaxy” hinted at audio translating apps, and William Gibson’s “Neuromancer” foresaw cyberspace and computer hackers. Then science fiction, now a reality – it’s human nature to speculate on what will happen next.

Let’s embrace a paradox, and just like in a sci-fi setup, ask Artificial Intelligence (AI), a technological evolution staple defining our era, how cyber threats will look in the future.

The cyber threat landscape in 10 years

The cyber threat landscape in 10 years

The types of cyber threats will likely evolve with the advancement of technology. As new technologies such as quantum computing, artificial intelligence, the Internet of Things (IoT), and advanced biometrics become more widespread, they will likely become targets for cyber threats.

Quantum computing

With quantum computers potentially on the horizon, we might see the advent of quantum-based cyber-attacks that could render current encryption methods obsolete.

Quantum computers use principles of quantum mechanics to process information. If they become practical and widespread, they could potentially break the cryptographic algorithms that secure online communication today.

Just last November, IBM revealed its 433 qubits quantum computer Osprey news to the public. This hyper-powerful machine is a successor to the last 2021’s attempt to develop a quantum computer, which was 3 times less effective than the latest device.

Today science reached only the brink of quantum computing due to technological limitations. But cybersecurity would necessitate new encryption methods once the quantum computing revolution potential is released.

A quick check on definitions 

💡 Quantum computing is a new type of computation that uses the principles of quantum mechanics.

💡 Quantum mechanics is the theory that explains how the smallest particles in the Universe behave.

💡 Quantum computers use quantum bits (qubits), which, unlike classical bits (that can be either 0 or 1), can be in a state of superposition, where they can be both 0 and 1 simultaneously.

💡 Because of superposition, quantum computers perform many calculations in parallel and solve certain types of problems faster than classical computers.

Click to tweet

Artificial intelligence

The growth in AI could lead to AI-generated attacks. AI-backed threats could involve machine learning algorithms to navigate to security measures, making them harder to prevent or detect.

Automated attacks and methods to create malware that can learn and adapt to its environment pose huge risks to the cybersecurity landscape. As AI technology advances, these threats will likely become more sophisticated and harder to mitigate.

Among these AI-projected risks are AI-enhanced phishing attacks. By using natural language processing, deep-fake technology, and machine learning algorithms, attackers can craft personalized and context-aware phishing emails that are difficult to identify as malicious. This can increase the success rate of phishing attacks and social engineering, leading to potential compromise of sensitive information.

Artificial intelligence can also enable the creation of botnets. AI algorithms can help botnets evade detection, automate attack techniques, and dynamically adapt to defenses. This can lead to larger and more resilient botnets that can carry out coordinated and sophisticated attacks.

Internet of Things (IoT)

As more devices connect to the internet, each becomes a potential vulnerability. Sophisticated large-scale attacks on infrastructure could become more common.

IoT devices are notoriously lacking in security, often being designed for convenience over safety. The IoT ecosystem lacks universal standards and regulations, leading to inconsistent security practices across devices and platforms, making them easy targets for malicious actors to exploit.

Data privacy concerns fall under the scope of IoT devices that collect vast amounts of personal and sensitive data. Location information, health data, and behavioral patterns under improper handling or unauthorized access to this data can lead to privacy breaches and potentially enable identity theft or targeted attacks.

IoT devices integrated into critical infrastructure, such as smart grids, healthcare systems, or autonomous vehicles, introduce the risk of physical harm if compromised. An attacker gaining control over such systems could cause disruptions, accidents, or even loss of life.

Biometrics

The increased use of biometric data, which involves using unique biological or behavioral characteristics for identification and authentication purposes, could lead to new types of identity theft, where hackers target biometric databases to impersonate individuals.

Potential biometric data tampering is another high-risk threat if biometric data is not securely stored or transmitted. An attacker gaining unauthorized access to the stored biometric data could modify it, leading to authentication failures or unauthorized access to secured systems.

Ultimately, gained biometric data can lead to cross-matching attacks that involve combining stolen biometric data from different sources to impersonate individuals across multimodal systems. If one modality is compromised, an attacker could use another modality to gain unauthorized access.

Distinctive changes in cybersecurity threats

The integration of cyber-physical systems and increasing digitization of everyday life will likely lead to a broader scope for unseen cyber threats. Cybersecurity could become a more significant concern in sectors that previously didn’t prioritize it as much, like manufacturing, agriculture, and healthcare.

Cyber-physical systems

Cyber-physical systems blend physical infrastructure with digital controls. Cyber threats could thus directly affect physical reality, for example, tampering with self-driving vehicles or smart city infrastructure. Integrating physical and digital systems is becoming increasingly common in the manufacturing, energy, and transportation sectors. This is creating new opportunities for cyber threats.

An attacker compromising a cyber-physical system could cause real-world harm. For instance, if an attacker could take control of a self-driving car’s system, they could cause an accident. Similarly, threats to smart grids could disrupt power supplies, and threats to smart manufacturing systems could disrupt production or cause physical damage.

As cyber-physical systems increase, we can expect cybersecurity threats to become more physical and potentially more dangerous. This trend will necessitate a greater focus on securing our data and the digital systems interacting with the physical world.

Greater interconnectedness

The continued growth of global connectivity means an attack in one place can quickly spread elsewhere. This may lead to more coordinated global responses to cyber threats.

The digital world is becoming more interconnected, making it easier for cyber threats to spread. This interconnectedness can also amplify the impact of attacks. For instance, a single successful attack on a cloud service provider could impact thousands of businesses that use that service.

In an increasingly interconnected world, it’s also more likely that threats will cross national borders. This could lead to greater international cooperation on cybersecurity, with countries working together to defend against threats and to track down and prosecute cybercriminals. We may also see the development of international norms and regulations related to cybersecurity.

The trends suggest that the cybersecurity landscape will become more complex and potentially more dangerous over the next decade. Protecting against future threats will require technological advances, better cybersecurity practices, and possibly increased international cooperation.

Unchanged aspects of cyber threats

While the specifics of cyber threats will change, several underlying principles will likely remain constant. The shared tendency is not purely technological fundaments of the threats but more on personal motivation and individual mindset.

Human error

Many cyber threats, even sophisticated ones, rely on exploiting human error or human psychology. For example, phishing attacks trick people into revealing sensitive information, such as passwords.

Similarly, ransomware often infiltrates systems because someone clicks on a malicious link or attachment.

Despite technological advances, the human element is often the weakest link in cybersecurity. This is unlikely to change in the foreseeable future. Human nature is a constant, and cybercriminals will likely continue to exploit this to their advantage.

Basic principles

Some basic principles of cybersecurity are timeless. For example, the principle of least privilege, which says that users should be given the minimum levels of access necessary to perform their tasks, is a fundamental principle of cybersecurity that helps to limit the potential damage if a system is breached.

Similarly, keeping software up-to-date is crucial for cybersecurity, as updates often include patches for known security vulnerabilities. These principles will likely remain important regardless of how the specifics of cyber threats evolve.

Economic motivations

Cybercrime will continue to be driven by financial gain. Where there’s value (like in personal data or corporate secrets), individuals or groups will seek illicit ways to acquire it.

Cybercriminals often seek to steal data they can sell, such as credit card numbers, or extort money directly from their victims, such as through ransomware. As long as money is to be made from cybercrime, and the perceived risk of getting caught is low, people will likely continue to engage in it. Therefore, the economic drivers of cybercrime are unlikely to disappear.

These factors underline the ongoing need for cybersecurity awareness, education, and robust security policies. While technology and specific threats will evolve, the human element, basic cybersecurity practices, and the motivations behind cybercrime will likely remain constants in the cybersecurity landscape.

Technology to mitigate and handle cyber threats

Advancements in technology will also shape cybersecurity measures. Or, as people say, fight fire with fire.

AI and machine learning

These technologies will become crucial in identifying and responding to threats, potentially in real-time. They can also help predict and mitigate future threats based on pattern recognition.

The role of AI and Machine Learning in enhancing cybersecurity defenses is key. AI is a powerful tool to detect abnormal behavior and identify threats in real-time based on patterns and irregularities that might be too subtle for a human to notice. Machine learning, a subset of AI, continuously learns from each attack and improves detection algorithms, enabling defenses to evolve along with the threats.

Moreover, AI could potentially be used for predictive threat intelligence, foreseeing cyber threats before they happen using historical data to predict future attack patterns.

Quantum cryptography

In response to potential quantum threats, quantum cryptography and post-quantum cryptography methods may become common to secure data.

With the potential arrival of quantum computers, current cryptographic algorithms could become obsolete. Quantum cryptography, particularly Quantum Key Distribution (QKD), offers a possible solution.

QKD allows two parties to generate a shared secret key that can be used to encrypt and decrypt messages. According to quantum mechanics principles, if an eavesdropper tries to measure the quantum particles used to form the key, their state will be changed, alerting the parties involved to the breach

Decentralized systems

Blockchain and other decentralized systems could provide more secure data storage and transmission alternatives.

A blockchain is essentially a distributed ledger that records transactions across multiple computers so that the record cannot be altered retroactively. This makes it resistant to tampering, which is why it could significantly improve cybersecurity.

Blockchain can provide improved security for IoT devices, supply chain security, secure private messaging, identity verification, and more.

Cybersecurity skill development

While not a technology in itself, the importance of human expertise in cybersecurity is paramount. Therefore, educational and training programs that equip people with the necessary skills to handle evolving cyber threats will be crucial. This might involve traditional educational programs, online courses, simulation tools, and AI-driven personalized learning platforms.

Remember that while these technologies will certainly help enhance cybersecurity defenses, there is no magic solution that can solve all challenges. The cyber threat landscape continuously evolves, and defending against these threats requires technological solutions, sound cybersecurity practices, robust policies, and a well-educated user base.

Summary

After exploring potential future scenarios in the evolving cybersecurity landscape, one thing is clear – staying ahead of the game is important.

To be completely sure, we asked if the future ahead was bright. The AI being an AI, couldn’t provide a Yes or No answer, yet it referred that the future ahead is in a grey area.

“The future will likely be a mix of remarkable advancements and challenging issues. It will be shaped by our ability to manage these opportunities and challenges, policy decisions, cultural shifts, and many other variables. The key lies in harnessing the benefits of technological progress while minimizing its potential negative impacts.”

Thinking strategically about business cybersecurity is crucial to prepare for upcoming challenges. NordLayer is designed to grow with your organization’s network security needs. Ensure authorized-only connections, enable threat-blocking features, and make cybersecurity user-friendly by implementing integral and easy-to-assess network access for all ways of working.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Cybersecurity tips for small businesses

When a massive data breach happens, large companies usually grab the headlines. However, it’s often the case that small businesses are attacked more often and are more vulnerable to cyberattacks. Their limited security measures due to their smaller size create better odds for an attacker.

For this reason, prioritizing security against these threats should be crucial for business owners. Effective security measures can help safeguard vital data, maintain customer trust, and prevent costly cyber incidents. This article discusses essential cybersecurity tips for small businesses to enhance their security posture.

Best practices for small businesses

A successful cyberattack puts business revenue, data, and equipment at risk, but it doesn’t stop there. Cybercriminals may also use their access as a launchpad into the networks of other companies connected to your business.

Small businesses lack the resources of corporations, but cybersecurity must still protect data, internet connection and network resources. With a lot at stake, here are some industry best practices to help you navigate the world of cyber threats.

Conduct a thorough risk assessment

Your cybersecurity plan should start with assessing the risks your business faces. Timely identification of potential vulnerabilities helps put the risk in perspective and assess the impact of cyber threats on critical data. This is the foundation for all further actions.

A comprehensive risk assessment helps prioritize security efforts and effectively allocate resources. That way, the key areas will be taken care of sooner rather than later, which enables businesses to patch up the weakest points first and then move on to less critical areas. It lays the groundwork for a solid cybersecurity strategy.

Create an Incident Response Plan

Preparing for a cybersecurity incident can help reduce the impact when a business falls under a cyberattack. While neutralizing active threats is a priority, so is restoring normal working conditions. This allows it to continue business operations as if the cyberattack was merely a setback.

To prepare, there are two main areas to focus on:

  • Calculate risk probability for threats. Include an assessment of where critical data resides. Assign an individual responsible for protecting important data and connecting every resource with risk-reduction strategies.

  • Create a recovery plan for all critical assets. This should include security scans to identify malware or virus infections. Document access requests during security alerts and determine whether data loss has occurred.

An Incident Response Plan (IRP) is vital for prompt and effective handling of cyber incidents. It should also include contact information for key stakeholders, guidelines for containing and investigating the incident, and a plan for communicating with customers and authorities.

Keep software and systems up to date

Regularly updating operating systems, applications, and software is necessary to avoid cyber threats. Cybercriminals often exploit gaps in outdated software, so staying current with patches is a sure way to stop some attacks right in their tracks.

Software updates also address bugs and glitches that may affect the software’s performance, stability, or functionality. So, in addition to increased security, updates typically include bug fixes that improve the overall user experience and resolve known issues.

Implement a strong password policy

Weak passwords are common entry points for cyberattacks as they’re easy to guess or brute force. That’s why it’s important to make sure that your employees use strong passwords: a combination of uppercase and lowercase letters, numbers, and special characters.

Passwords should also be unique for each account. Enterprise-wide password management tools can help. They make storing and changing passwords easier, eliminating the risk of human error. This allows to avoid password reuse, which could compromise a user account if other accounts sharing the same password are breached.

As an additional precaution, passwords should be periodically updated to limit the time when criminals could exploit them.

Limit access to sensitive data and systems

Access to sensitive information and critical systems should be provided only on a need-to-know basis. This means that users should have minimum access rights. Elevated privileges should be assigned under special conditions and for separate user account types. Such a setup minimizes insider threats and contains damage in case of a data breach.

User permissions should also be regularly reviewed, ensuring only authorized personnel can access sensitive data over an internet connection. Quickly disposing of inactive and zombie accounts helps clean up your user base and establish that only authorized users can access sensitive data.

Implement two-factor authentication or multi-factor authentication

Small companies need to secure the network edge with robust authentication procedures. Two-factor authentication or multi-factor authentication are the best options here. These methods require multiple identification factors whenever users connect to network assets. This makes it far harder to obtain access illegitimately.

If MFA is too burdensome for employees, consider using it solely for administrator accounts. Alternatively, try user-friendly 2FA options such as fingerprint scanning. Balance user experience and security. But always go beyond simple password protection, as even strong ones can benefit from additional layers of protection.

Use network security measures

Technological solutions can help to secure business networks, making it harder for external penetration. A robust firewall, antivirus software, intrusion detection systems, and virtual private networks (VPNs) are a good starting point to tighten security around your network perimeter.

The network is the main channel for data exchanges and communication, so its security is key for business continuity. Firewalls provide a barrier between your internal network and the internet, while intrusion detection systems can alert you to potential cyber threats. VPNs encrypt internet connections, ensuring data privacy and protecting against unauthorized access. Meanwhile, antivirus software is a good all-rounder that helps to deflect simple network threats.

Implement protection for sensitive information

No matter where sensitive information is kept or transferred, appropriate security measures should be in place.

  • Encrypt high-value data such as personnel records and customer financial information. If you rely on SaaS or PaaS tools, use any cloud data protection tools provided by your Cloud Service Provider.

  • Use privileges management to limit freedom within network boundaries. Confidential data should only be available to users who need it for their tasks. That way, attackers struggle to access and extract data when a data breach occurs.

  • Minimize the number of users with administrative privileges. Avoid giving single users the authority to make fundamental network changes.

  • Consider using Data Loss Prevention tools as well. These tools track the location and state of important data. They block data transfers to unauthorized devices and log potentially dangerous access requests. DLP could be a sound investment if you handle high-risk and high-value data.

These measures add an extra layer of security and prevent sensitive data from falling into the wrong hands.

Train employees on cybersecurity best practices

Digital cybersecurity controls rely on human knowledge and behavior. How employees act when encountering cyber threats is crucial to a small business security setup. That’s why it’s vital to focus on what is known as the human firewall.

Strengthen the human firewall by instructing employees how to spot phishing emails and malicious links. Invest in employee cybersecurity training to create a security-conscious culture within your organization. Educate them about common cyber threats, phishing attacks, and social engineering techniques (don’t forget the importance of strong passwords).

Remote workers should also understand secure connection practices and the risks of using an insecure public Wi-Fi network. Regular training sessions and reminders will help foster a security culture within and outside the organization.

Stay compliant

Stay informed about relevant data protection and privacy regulations for your industry and location. Ensure your business complies with laws such as the General Data Protection Regulation (GDPR) or the California Consumer Privacy Act (CCPA). Compliance helps protect your business from legal consequences and demonstrates your commitment to data privacy.

Regulatory requirements are subject to change, so monitoring their developments should be ongoing. This allows to be prepared for any relevant changes in advance and align with applicable data protection and privacy regulations.

Schedule regular backups

Cyber attacks can lead to the deletion of data or system failures that compromise workflows. This makes it vital to back up high-priority data regularly. Use secure cloud services or external locations outside your core network for automated data backup.

The data recovery process should be periodically tested to ensure the integrity and availability of your backups. If this system is effective, it will quickly bounce back from all internal and external threats with minimal downtime.

Manage third parties securely

Small businesses rely on third-party vendors, but these partnerships can be vectors for cyber attackers. For example, CRM providers may not encrypt data securely, putting client data at risk. Virus checkers or low-quality VPNs may transmit spyware.

Check all third parties and ensure they have rock-solid security policies. Trust nobody and always ask for security assurances when in doubt. Evaluate their security practices, including data handling, access controls, and incident response procedures. Establish clear cybersecurity expectations in vendor contracts and regularly monitor their compliance.

Regularly review and update the cybersecurity plan

As cyber threats rapidly evolve, your cybersecurity plan should be periodically reviewed to address various changes. Small businesses, in particular, should stay informed about emerging threats and security best practices.

Conduct periodic audits and risk assessments to identify any gaps or weaknesses in your security strategy and take prompt action to address them. If done consistently, this helps to keep threats at bay and your business operations uninterrupted.

Key takeaways

Let’s recap some of the key insights on cybersecurity for small businesses.

  • Small businesses are often more vulnerable to cyberattacks than large corporations due to limited security measures. Small businesses must prioritize cybersecurity to protect their vital data, maintain customer trust, and prevent costly cyber incidents.

  • A thorough risk assessment should be step one of your cybersecurity plan. It helps to identify potential vulnerabilities and assess the impact of cyber threats on critical data.

  • Incident Response Plan (IRP) helps to prepare for cybersecurity incidents. It should include risk calculations, data protection responsibilities, recovery plans for critical assets, and guidelines for containing and investigating incidents.

  • The majority of cybersecurity risk management deals with ongoing maintenance. Keep software and systems updated, use network security measures, and conduct regular employee training sessions.

  • Implement industry-wide best practices such as the principle of least privilege, multiple-factor authentication, and rules for strong passwords to navigate the dangerous cyber landscape.

By following these cybersecurity tips, small businesses can enhance their security posture, mitigate risks, and protect their data and assets from cyber-attacks.

How can NordLayer help?

Nordlayer is the ideal partner for small businesses seeking to secure their data. We offer a variety of solutions to strengthen network defenses and manage employee identities.

Device Posture Checks make working from home safer. NordLayer’s systems assess every device connection. If devices fail to meet security rules, posture checks deny access. Users will instantly know about access requests from unknown or compromised devices.

IP allowlisting lets you exclude unauthorized addresses at the network edge. IAM solutions use multi-factor authentication and Single Sign-On to admit verified identities. Virtual Private Gateways anonymize and encrypt data, adding more remote access protection. And our Cloud VPN services lock down hard-to-secure cloud assets that small businesses rely on.

NordLayer makes achieving compliance goals easier and provides a safer customer experience. To find out more, get in touch with our sales team today.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.