A phishing attack is a form of social engineering in which the attacker mimics a legitimate contact to trick an unsuspecting user into clicking on a malicious link, luring out their sensitive data, or infecting their device with malware. Over the years, phishing scams have become increasingly sophisticated, making it harder to identify them.
There are a few things you can do to secure your business from a phishing attack. First, you need to get the entire staff on the same page. Educate them about the intricacies of phishing and provide avenues to report any suspicious events. You should also enable anti-phishing filters within your company’s email and consider installing additional security software optimized to detect fraudulent emails.
During a ransomware attack, data on the affected computer is almost instantly encrypted, making it unusable in any context unless it is decrypted. Once the files are encrypted, the attackers demand a ransom—hence the name—in return for the decryption procedure.
One of the best ways to defend your company’s data from a ransomware attack is by making regular software updates and data backups. Software updates, including OSs, ensure that no security gaps can be exploited by bad actors. At the same time, data backups allow you to be safe even if any of your data is compromised. Another step is deploying company-wide antimalware and antivirus software that can detect any malware before it does any harm to your company’s network.
Viruses
Viruses are perhaps some of the most common cybersecurity threats affecting businesses and individuals alike. They’re pieces of software that, when installed upon a device and activated, start executing various malicious commands.
Viruses can be transmitted to a device via hardware and software. Connecting a suspicious USB flash drive containing a virus to a device is a common strategy for spreading malware. Phishing is also frequently combined with viruses—if a user downloads a suspicious attachment or opens a scam website, their device can be infected.
The damage that a virus causes depends on its programmed purpose. Some viruses might slow down a device and use its resources to mine cryptocurrencies in a process known as cryptojacking. Others lurk in the system, granting access to all inner files without the victim noticing. Keyloggers are a type of virus that can read the user’s keyboard input, allowing them to steal credentials and similar sensitive information.
Businesses are often targeted using viruses that can take over the whole internal network of computers, leading to ransom demands. Trojans, in particular, are dangerous, as they can destroy the entire system from within.
For small businesses, viruses can cause irreparable damage, starting from compromised and lost data to hardware damage and replacement demands. As viruses become increasingly sophisticated, they require more expensive measures than regular antivirus software. They might also exploit out-of-date software with security vulnerabilities.
Preventing an organization’s devices from acquiring viruses calls for similar measures and phishing or ransomware protection. Companies must ensure all devices are up-to-date to avoid zero-day exploits or similar security gaps. All devices should be regularly monitored by antivirus software, and IT teams should be informed if suspicious programs or files appear on the device or if a user has opened a phishing email or website. Companies can also use anti-phishing and anti-malware plug-ins for their email services to prevent employees from accidentally downloading viruses.
Weak passwords
As far as market research is concerned, weak passwords are the biggest threat to cybersecurity for small businesses. Here’s just a handful of studies and reports that reveal password vulnerabilities in practice:
Verizon’s 2024 Data Breach Investigations Report (DBIR) notes that 77% of hacking-related breaches are linked to stolen credentials.
A study into the password habits of Fortune 500 companies highlighted that even the biggest players out there struggle with password security, with 20% of the passwords being the exact name of the company or some variation.
Ensuring password security in a business environment is not that complicated. A password management solution should be on the company’s must-have list, no matter its size or market. A password manager such as NordPass allows businesses not only to securely store valuable login information but also share it within the confines of the organization. Additionally, it increases employee productivity and helps you meet compliance requirements.
Cloud computing
Cloud computing products are a huge part of today’s business. Nearly all SMBs use cloud-based applications in one way or another, whether for productivity or security benefits. In many instances, cloud computing solutions are highly scalable. However, as helpful as cloud computing solutions are for business IT security, organizations must understand that such products have their risks.
When it comes to cloud-based applications, it is essential to evaluate their security posture. For instance, zero-knowledge architecture is one thing to look for in applications, as it ensures the privacy and security of any data that the application handles. To reap all of the cloud’s benefits, such as scalability, flexibility, and reduced IT costs, SMBs must develop a cloud security plan to clearly define security policies and procedures for using cloud-based applications.
Cybersecurity tips for small businesses
Establishing the right cybersecurity practices in an SMB does not have to be a costly affair. A large chunk of what makes small business IT security function like a well-oiled machine is down to employee awareness and correct credential management practices. Here are some cost-efficient ways you can employ safe practices in your organization:
Ensure employee education. As you can tell, password mismanagement is a massive problem for company data security. This misuse often stems from a lack of employee awareness. Provide your team with regular training on cybersecurity practices, digital threats, and how to keep themselves protected from bad actors.
Perform routine security checks. Zero-day exploits are beloved by hackers as an easy way in to systems. The best way to protect your company devices from unwanted visitors is to lock the backdoors by keeping all systems and software up-to-date and running regular checks for vulnerabilities.
Install a strong antivirus. If you or another employee find a suspicious .exe file on your desktop, the first course of action is to quarantine it. This can be easily done by installing antivirus software on every company-run computer. SMB and enterprise antivirus solutions simplify this process by keeping all computers in the same network protected.
Add spam filters to company email. Scammers who use social engineering are efficient at producing realistic emails that can trick even professionals. To avoid incidents of opening fishy attachments or logging in to a spoof portal, add a spam filter to your organization’s email inboxes that lets employees easily flag and report suspicious emails.
Use a password manager. Contrary to popular belief, password managers aren’t just useful for generating complex, unique passwords. Business password managers like NordPass also offer centralized controls, such as setting up password policies, observing all organizational activity, or managing shared access between all employees.
Enforce multi-factor authentication (MFA). In the 2020s, a password is no longer enough to protect your organization’s sensitive information. To improve their security measures, many companies enforce multi-factor authentication use for all work-related accounts. NordPass Authenticator even lets you store your MFA codes with your login credentials and autofill everything at once.
About NordPass NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.
The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
Though this information might be news to you, it’s not to cybercriminals. Weak and reused passwords are a reliable gateway to businesses’ sensitive data. Depending on the type of cyberattack, up to 80% of successful data breaches can be attributed to weak or stolen credentials.
You might consider implementing a password policy to encourage your team to use stronger passwords. But how can you create a policy that works, and what should you include? Today, we’re talking about best practices for password policies.
What is a password policy?
A password policy informs your team about how to make decisions around creating and managing passwords.
A password policy aims to improve cybersecurity by preventing cyberattacks that rely on weak and reused passwords. That usually means establishing conventions around passwords that make them difficult to hack.
Password policies can also refer to rules and guidelines around setting passwords internally. This gives businesses administrative control over which password criteria an internally developed system can accept.
Because these policies can be enforced automatically by software, the advice below focuses on external-facing password policies. In other words, it will offer advice for establishing the guidelines employees should follow when creating passwords for external accounts or software for corporate use, such as Outlook, Google Workspace, or Zoom.
Why do you need a password policy?
To understand the need for a password policy, let’s consider the alternative — looking at the default behaviors around password management in a corporate setting.
Weak passwords can be easily guessed or hacked with minimal effort. “Password,” for instance, is as weak as they come. And yet our research reveals that this is the most common password in 2022. This password has been used millions of times around the world.
If you suspect that internet users adopt more secure behavior when creating corporate credentials, a study of breached Fortune 500 companies has shown this is not so.
Predictable passwords such as “123456” topped the list of most common passwords, with others like “abc123” and “sunshine” making their way to the top 10 by industry. As mentioned, the company’s name is also a common choice.
Overall, the percentage of unique passwords was only 31% for all industries – to say nothing of the unique passwords’ strength.
A different study of management, owners, and C-suite executives’ credentials demonstrated that even leadership team members are no better at using strong, secure passwords.
Suffice it to say: People use weak passwords at work.
Weak passwords represent a massive cyber vulnerability
Weak passwords, like those mentioned above, can be hacked in less than one second. So it’s no surprise that according to Verizon’s most recent Data Breach Investigation Report, credentials are involved in nearly 50% of all breaches — more than twice as often as phishing attacks.
To make matters worse, using weak passwords is often combined with poor password hygiene. The most common password hygiene sins are storing passwords in insecure locations and reusing the same passwords for multiple accounts.
Passwords stored on sticky notes on your desktop or in Excel spreadsheets are two particularly egregious examples of improper password storage. A password written in plain sight is all too convenient for an intruder in your workspace.
On your virtual desktop, a list of passwords is low-hanging fruit to cybercriminals who have secretly gained access to your device.
As you can tell, poor password hygiene can defeat even the strongest, longest password. That’s why a good password policy must address both.
Password policies and cybersecurity compliance
That password authentication is so standard, yet often, such a weak security barrier is a widespread and well-known issue known a the “password problem.” For that reason, all cybersecurity standards either directly or indirectly offer guidance on passwords.
CIS Password Policy Guide
The Center for Internet Security (CIS) is a non-profit organization with a mission to safeguard organizations against cyber threats. It publishes recommendations that, if followed, will improve businesses’ cybersecurity posture.
The CIS Password Policy Guide offers two tiers of password recommendations: one when passwords are the only authentication method and another when passwords are just one of multiple authentication methods.
Elements
Password-only authentication
Multi-factor authentication
Length
14+ characters
8+ characters
Strength
Require at least one non-alphabetic character
No requirement
Hygiene
Change frequency: only when an event occurs, such as staff turnover or a data breach.
Change frequency: only when an event occurs, such as staff turnover or a data breach.
The logic is that passwords should be stronger when passwords are the only measure between a cybercriminal and your accounts.
The HIPAA Security Rule
The HIPAA Security Standards for the Protection of Electronic Protected Health Information (the Security Rule) establishes a standard for protecting electronic protected health information (ePHI).
The Security Rule states that healthcare organizations should follow basic information security principles. In other words, the “confidentiality, integrity, and availability of all e-PHI” should be upheld for all protected health data created, stored, or shared by the organization.
Upholding these tenets involves protection against anticipated threats or breaches. While the Security Rule does not define specific password protocols, proper password policies and hygiene are implicit in many requirements — under administrative and technical safeguards.
In principle, the Security Rule can be met by following the agreed-upon best practices for cybersecurity and information security which, inevitably, involve a strong password policy.
The PCI-DSS password guidelines
The Payment Card Industry Data Security Standard (PCI DSS) is a global security standard that applies to all entities that process, store, or transmit personal and payment information. It consists of 12 requirements. Like HIPAA’s Security Rule and the CIS Controls, it mirrors the best cybersecurity practices that mitigate cyber risk and safeguard data.
Requirement two of the Standard stipulates that businesses should change all default system passwords. Not doing so, the document states, is the equivalent of “leaving your store unlocked when you go home for the night.”
Requirement eight is to “identify and authenticate access.” Strong passwords and multi-factor authentication are encouraged as essential measures to protect cardholder data.
The NIST Password Policy
The National Institute of Standards and Technology (NIST) is a U.S. federal agency that has become a significant authority on password guidelines. The NIST password policy provides several recommendations for creating secure passwords and managing them safely. Unlike traditional advice, NIST focuses on user-friendly policies while maintaining strong security.
For instance, NIST recommends allowing longer passwords (up to 64 characters), supporting a diverse character set (including spaces and emojis), and eliminating periodic password changes unless there is evidence of compromise.
In essence, NIST encourages the creation of unique, easy-to-remember phrases instead of complex, hard-to-recall alphanumeric combinations. Their guidelines further emphasize the need for multi-factor authentication (MFA) as an additional security layer and discouraging the practice of password hinting and knowledge-based authentication questions (like your first pet’s name) which can be easily exploited.
NIST’s comprehensive approach to password security underscores its commitment to balancing user experience with robust data protection. This is why its standards are widely adopted across industries globally.
ISO/IEC 27001
The International Organization for Standardization/International Electrotechnical Commission 27001 (ISO/IEC 27001) is a voluntary certification on information security, cybersecurity, and privacy protection.
Annex A is among the best-known annexes of the ISO standard. It includes recommendations that strengthen data security. More specifically, section A.9 pertains to access control, where you’ll find guidelines for password management.
To protect the confidentiality of sensitive data, the ISO guidelines recommend “strong passwords” and a “password management system” in addition to multi-factor authentication.
Password policy recommendations
All well-known cybersecurity standards recommend using strong passwords and good password management or hygiene. But what exactly does that mean?
Strong passwords
Strong passwords make a hacker’s job difficult. They are complex, long, and difficult to guess. The following guidelines can help to create passwords that meet these criteria.
Keep in mind your password policy should be calibrated by standard password criteria. Otherwise, you’ll end up with a policy that’s impossible to follow. For example, cybersecurity experts say the strongest passwords should allow spaces. However, it’s common for spaces to be prohibited.
Tip: Use a password generator to get super strong passwords instantly without testing your creativity.
Good password hygiene
Good password hygiene also aims to keep your passwords out of intruders’ reach — making it difficult or impossible to steal them and mitigating the damage if they are.
SHOULD involve
SHOULD NOT involve
Using unique passwords for each account
Storing passwords in plain text
Changing passwords regularly or after a breach or staff turnover
Repeating passwords
Secure, end-to-end encrypted storage
Sharing passwords over instant messaging or email
Keeping any default-issued passwords
Writing passwords down where they can be accessed
Use a data breach scanner to determine whether your credentials have been compromised. If so, change them immediately.
Why password policies (alone) are doomed to fail
There’s a reason it is so common to use weak passwords and practice poor password hygiene. And it’s not a lack of awareness. By now, few among us can claim not to know that passwords like “password” and “123456” represent a security threat.
The truth is that the average user is in a tough spot. You know that you should use strong passwords, especially at work. But the same features that make passwords “good” also make them impossible to remember.
And if you can’t remember them, you have to store them somewhere handy. But unfortunately, this “handy spot” often becomes equally convenient for cybercriminals.
That’s why it isn’t reasonable to expect that penning a policy is all it takes to bolster your business’ password health. Your team members are likely already aware of basic security principles but lack the tools to apply them. On top of everything else, they are likely to prioritize speed over security to get work done.
The Active Directory Password Policy
Active Directory (AD) is a Microsoft product that manages users and computers within a network. The Active Directory Password Policy is a set of rules defined by system administrators to govern password creation and maintenance in an organization.
The password policy generally includes directives such as minimum password length, password complexity requirements (including uppercase, lowercase, numeric, or non-alphanumeric characters), and password history settings to prevent users from reusing old passwords.
The policy also sets a password’s maximum age, forcing users to create new passwords after a defined period. Other considerations might include account lockout policies that disable a user account after a certain number of failed login attempts.
AD provides two types of password policies: the default domain policy and fine-grained password policies. The latter allows different policies for different user groups within the same domain, providing flexibility for different security requirements.
How to set up a password policy that works
With NordPass Business, you can set a password policy at the administrative level that you can implement automatically — offering your team all the support it needs to maintain excellent password hygiene without slowing down the workflow.
In the NordPass Business Admin Panel, you set the criteria for strong passwords that the Password Generator follows.
With just one click, users can generate strong passwords with the built-in Password Generator and save them just as quickly. When needed, the passwords pop up automatically into form fields thanks to autofill powered by machine learning.
That means you can unburden your team from the mental load of trying to create and remember complex passwords. And from a storage standpoint, your team’s passwords stay safe in an ultra-secure, end-to-end encrypted vault. All in all, credentials are easy to access for your team but entirely out of reach to intruders.
Members can conveniently and securely share multiple passwords and other sensitive data stored in their vaults with various members at once using the Groups and Shared Folders features.
Meanwhile, you can monitor your team’s password progress with a bird’s-eye view of your company’s Password Health metrics, with a rundown of all vulnerable (weak or reused) passwords that can compromise your cybersecurity.
Avoid choosing between security and convenience. Instead, implement a password policy that works with NordPass Business.
About NordPass NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.
The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
GLPI is a free IT Service Management (ITSM) solution that allows you to manage assets, incidents and requests within an organization. It works as an incident tracking and service desk system, optimizing technical support and technological resources.
It also includes hardware and software inventory, contracts and licenses, offering a centralized view of the whole infrastructure. Its intuitive web interface and customization options ensure flexibility and scalability for businesses of any size.
GLPI is ideal for organizations looking to improve the management of their technology resources, automate processes and optimize IT service management.
All the advantages of GLPI together with Pandora FMS
GLPI has an integration in Pandora FMS that some customers are already enjoying.
With it you may automate ticket creation, for which you may use a plugin that you may find in the library . This plugin allows integrating Pandora alerting of ticket creation in your GLPI environment through the rest API available to the service.
Each time an alert is executed and triggers the plugin, it opens a ticket in GLPI with information about the module that triggered the alert: agent, module data, IP address, timestamp and description of the module, with a title for the ticket, category, assignment group and priority, which may vary depending on the alert action.
Running the plugin with its parameters, in a configurable time interval, allows you to automate the whole process of creating a ticket that would normally be performed by a user. It is necessary to use credentials to authenticate with your environment (username and password or a token, which must be generated beforehand). The plugin configuration allows you to specify a title, description, priority, category, group, type of query. In addition, it will check whether there is already a ticket created with these features so that in case it is already created, it is only necessary to add its corresponding follow-up.
The plugin makes use of a parameter called “–recovery” that sets two different paths in its execution. If used, the plugin will check the status of the specified ticket and if it is not closed add a comment on it, if it is closed, it will not do anything else. If it is not used, the performance will be the same, but it will change if the ticket is closed or does not exist. If closed, it will create a new ticket. If it does not exist, it will create the ticket if there is a computer with the same name as the agent specified with the “–agent_name” parameter.
The plugin does not need additional dependencies for its use, since these are already incorporated. But it is necessary for in the GLPI environment to have rest api enabled, since the plugin makes use of it for ticket creation.
For that, access, in your GLPI environment, Setup → General
The “Enable Rest API” option must be enabled. From that menu you may also enable whether you want to be able to authenticate with credentials, with tokens or both.
Once done, it will be possible to use the plugin, for that, it will be necessary to configure an alert command. By creating alert commands, you may specify and automate ticket creation.
This can be done from the alerts menu, in commands:
Enter a name, group, and the command, using as values for the parameters the macro _fieldx _, where x is the number of the parameter (they do not distinguish any order, each macro just needs to have a different number).
Once configured, you may configure the macro value below in the description fields.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About PandoraFMS
Pandora FMS is a flexible monitoring system, capable of monitoring devices, infrastructures, applications, services and business processes.
Of course, one of the things that Pandora FMS can control is the hard disks of your computers.
Summary: This guide outlines key cybersecurity practices for law firms, highlighting risks, real-world examples, and tailored solutions to protect sensitive client data.
The legal industry is built on trust, confidentiality, and carefully handling of sensitive client information. However, this reliance on sensitive data has made law firms a prime target for cyber-attacks. From personally identifiable information (PII) to financial records and intellectual property, the data managed by law firms is invaluable—and vulnerable.
A single cybersecurity incident can lead to devastating consequences: loss of client trust, legal repercussions, and significant financial penalties. Yet, many legal professionals remain unsure about how to strengthen their cybersecurity.
In this guide, we’ll explore cybersecurity for law firms, focusing on essential steps to protect your law firm’s data, maintain client trust, and ensure compliance with regulatory standards.
Key takeaways
Understand the unique cybersecurity risks law firms face.
Implement strong passwords and secure access management.
Develop a robust incident response plan.
Leverage advanced technology like Virtual Private Networks (VPNs) and cloud security tools.
Stay compliant with data protection regulations.
The cybersecurity threat landscape for law firms
Cybercriminals increasingly target the legal industry, and the numbers are alarming. According to an American Bar Association (ABA) study, 29% of law firms experienced a cybersecurity breach in 2023. These incidents lead to downtime, lost revenue, and long-term damage to a firm’s reputation.
Phishing attacks
According to the Verizon Data Breach Investigations Report, phishing is one of the most prevalent cyber threats, accounting for 36% of data breaches. These attacks typically involve fraudulent emails that trick employees into sharing sensitive information, such as passwords or client details.
Ransomware
Ransomware attacks involve malicious software encrypting a firm’s data, rendering it inaccessible until a ransom is paid. Even after payment, there’s no guarantee that data will be restored.
Insider threats
Insider threats can arise from employees or contractors misusing their access to sensitive information. This may be intentional, such as data theft, or accidental, like falling for a phishing scam. Insider threats can compromise client confidentiality and result in significant financial or reputational damage.
Advanced Persistent Threats (APTs)
APTs involve prolonged and targeted attacks where hackers gain access to a firm’s network and remain undetected for extended periods. Continuous access and exfiltration of sensitive data make these threats particularly damaging.
Data breaches
Data breaches occur when unauthorized individuals gain access to sensitive information. These breaches can result from weak security protocols, outdated software, or employee negligence. It can lead to legal penalties, loss of client trust, and significant financial consequences.
Business email compromise (BEC)
BEC is a form of phishing attack that involves cybercriminals impersonating a trusted individual or entity to deceive employees into transferring funds or sharing critical information.
Real-world examples: A wake-up call for the law sector
In November 2023, Allen & Overy experienced a ransomware attack that affected a small number of storage servers. The attackers threatened to publish sensitive data unless a ransom—potentially between $51.5 million to $76 million—was paid. Although the firm’s core systems were unaffected, operations were disrupted, and clients had to be informed about potential threat to data security.
Similarly, a cyber-attack exploiting a vulnerability in the MOVEit file transfer software impacted multiple law firms, including Kirkland & Ellis and Proskauer Rose. This attack significantly disrupted conveyancing practices, delaying property completions and causing operational chaos.
The number of successful cyber attacks against US law firms has increased significantly in recent years. In the first five months of 2024 alone, 21 firms filed data breach reports with state attorneys general offices, compared to 28 breach reports filed in total for the previous year. This represents a substantial increase in the frequency of reported incidents.
The legal sector has faced escalating ransom demands from cybercriminals. The average ransom demand following an attack on a legal firm is $2.47 million, although the average ransom paid is lower at $1.65 million. These astronomical figures highlight the severe financial risks law firms face from cyber-attacks.
Why law firms are attractive targets
Law firms occupy a unique position as gatekeepers of highly sensitive and valuable information, making them prime targets for cybercriminals.
Here’s why they’re often in the crosshairs:
Volume and sensitivity of client data. Legal firms handle many personally identifiable information (PII), financial records, and other confidential documents. This makes them a gold mine for attackers looking to commit identity theft, financial fraud, or corporate espionage.
Handling intellectual property and mergers. Many firms manage intellectual property portfolios, trade secrets, and high-stakes mergers and acquisitions. If stolen or exposed, such data could disrupt billion-dollar deals or give competitors an unfair advantage. Cybercriminals, including nation-state actors, often target these assets for profit or strategic gains.
Reliance on cloud platforms. As the legal industry increasingly adopts cloud-based solutions and supports remote work, vulnerabilities in these platforms become exploitable. Without strict data security measures, cloud misconfigurations, phishing attacks, and unauthorized access can expose confidential information.
Weaker security infrastructure. Despite managing high-value information, many law firms—especially smaller ones—lack robust cybersecurity defenses compared to other industries. Limited IT budgets and insufficient awareness of evolving cyber threats increase their vulnerability.
The fallout of a cyber-attack on a law firm can be devastating, both financially and reputationally:
Legal and financial liabilities: Firms may face lawsuits, regulatory fines, and substantial costs to recover lost data
Loss of clients and revenue: A breach erodes client trust, often resulting in loss of business and damaged relationships
Reputation damage: Rebuilding a tarnished reputation in a trust-driven industry like law is exceptionally challenging
By understanding their unique vulnerabilities and implementing strong cybersecurity practices, law firms can reduce risk and protect their clients’ sensitive information.
12 law firm cybersecurity best practices
To protect your firm’s cybersecurity and reputation, consider implementing these law firm cybersecurity best practices:
1. Develop a comprehensive incident response plan (IRP)
A robust IRP outlines the steps to take during a cyber-attack or data breach, ensuring a swift and effective response. Include clear roles, communication protocols, and procedures for mitigating damage. Regularly test and update the plan to reflect evolving threats and organizational changes.
2. Train employees on cybersecurity awareness
Human error is one of the leading causes of cyber incidents. Conduct regular training sessions to teach staff how to identify phishing emails, handle sensitive information securely, and adhere to data security policies. Tailor training to address specific threats that law firms face, such as social engineering attacks targeting confidential data.
3. Enforce strong password policies and use password management tools
Weak or reused passwords are a common vulnerability. Require employees to create strong, unique passwords and encourage the use of password managers to simplify secure authentication. For example, NordPass’ password management solutions provide easy-to-use tools that ensure compliance with password best practices.
4. Secure remote access with VPNs
As remote work has become standard, ensuring secure network access is crucial. Use VPN solutions like NordLayer’s Site-to-Site VPN to create encrypted tunnels that protect your firm’s systems and data from external threats. This safeguards both remote employees and sensitive communications.
5. Regularly back up critical data
Frequent backups protect your firm from data loss due to ransomware or accidental corruption. Store backups in secure locations, such as offsite servers or encrypted cloud platforms. Test backup integrity periodically to ensure data can be restored quickly if needed.
6. Implement multi-factor authentication (MFA)
MFA adds an essential layer of security by requiring users to verify their identity using two or more factors, such as a password and a one-time code. This makes it significantly harder for attackers to gain unauthorized access.
7. Encrypt data in transit and at rest
Use encryption protocols like AES-256 and ChaCha20 to protect sensitive law firm data while it is transmitted and stored. This ensures that even if unauthorized users get access to the data, they can’t read it.
8. Migrate to the cloud with a security-first approach
Cloud services offer scalability and flexibility but come with unique risks. When transitioning to the cloud, implement robust security measures such as access controls and encryption. NordLayer’s cloud access solutions provide a secure environment for managing and protecting your firm’s resources.
9. Comply with data protection regulations
Adherence to legal frameworks like GDPR, HIPAA, or industry-specific requirements is vital to avoid legal penalties and protect client trust. Conduct regular audits, review compliance measures, and ensure third-party vendors meet regulatory standards.
10. Monitor systems and apply updates regularly
Outdated software is a common target for attackers. Establish a schedule for monitoring, patching, and updating all systems and applications. Use automated tools to identify vulnerabilities and prioritize critical updates.
11. Establish role-based access controls (RBAC)
Limit access to confidential data based on employees’ roles and responsibilities. Implement the principle of least privilege, ensuring that users can only access information necessary for their tasks. This minimizes the risk of insider threats or accidental exposure.
12. Partner with cybersecurity experts
Collaborate with experienced network security providers like NordLayer to implement tailored cybersecurity measures. Their expertise can help you stay ahead of emerging threats and adopt advanced technologies, protecting client data and critical systems.
Technology solutions for law firm security
Technology plays a key role in strengthening cybersecurity for law firms. By using advanced tools and solutions, legal practices can stay ahead of the lurking threats.
Cloud security solutions. As legal practices increasingly migrate operations to cloud environments, it becomes equally important to secure those platforms. Network security solutions like NordLayer ensure that sensitive information remains protected, even remotely accessed. Features such as secure network access controls, data encryption, and activity monitoring help prevent unauthorized access and data breaches, keeping your law firm compliant and safe.
Virtual Private Networks (VPNs) for remote work. Remote work has become a standard in the legal sector, but it also introduces new cybersecurity challenges. VPNs create encrypted tunnels to safeguard sensitive communications and data transfers, ensuring seamless and secure connectivity for legal teams—whether in the office or on the move.
Advanced access control solutions. Access control is a critical component of legal cybersecurity. NordLayer’s flexible access control tools, including Zero Trust Network Access (ZTNA), restrict access to sensitive resources based on user roles and authentication. These tools minimize the risk of unauthorized access, even if login credentials are compromised.
Device Posture Security. Validating endpoints for compliance with security protocols helps reduce risks posed by compromised or unsecured devices. This feature ensures that only trusted devices access a law firm’s network.
Cloud Firewall for enhanced protection.NordLayer’s Cloud Firewall enables firms to define and enforce strict access policies, ensuring only authorized traffic reaches critical systems. This tool prevents unauthorized access, blocks malicious threats, and provides visibility into network activity to safeguard sensitive legal data.
Tailored cybersecurity for law practices
Cybersecurity in the legal sector requires solutions that address the unique challenges of handling law firm’s data, intellectual property, and regulatory compliance. NordLayer cybersecurity solutions for law firms offer tailored tools to meet these needs:
Virtual Private Networks (VPNs): Secure remote access for legal professionals with encrypted tunnels, allowing teams to work confidently from anywhere
Zero Trust Network Access (ZTNA): Restrict access to critical systems and data using a “trust no one, always verify” approach, ensuring only authorized personnel can interact with sensitive resources
Device management and monitoring: Track, validate, and secure all devices accessing your network, ensuring endpoint security across the firm
Cybersecurity is essential for all law firms, regardless of their size. Whether you run a small, medium, or large practice, protecting client trust and critical data is non-negotiable. With NordLayer’s cutting-edge tools, your firm can stay ahead of cyber threats and maintain robust security standards.
About NordLayer NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.
The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
How many Apple devices are in your workplace, school, or home right now?
Do you rely on an iPhone to manage your day, or perhaps a MacBook for work?
Ever wonder how many other people in the world are doing the same?
With 2.2 billion active Apple devices globally, the answer is: a lot.[1]
Apple Endpoint Management
From students browsing away on iPads to businesses running on Macs, Apple’s devices have seamlessly infiltrated our daily lives, becoming indispensable tools for productivity, creativity, and communication. But here’s the catch—as Apple’s influence grows, so does the complexity of managing these devices.
So, who’s in charge of keeping all these devices secure? How do you ensure compliance, prevent data breaches, and keep devices running smoothly—without a team of IT experts working overtime?
The answer lies in Apple Unified Endpoint Management (UEM). It’s the solution that simplifies the complexity of managing Apple devices, ensuring they remain secure, updated, and aligned with organizational policies. Whether it’s a CEO’s iPhone or a classroom full of iPads or you need to manage 10 devices or 10,000, UEM offers the structure needed to oversee a growing ecosystem.
So, how UEM for Apple can transform your device management? Let’s find out.
What is UEM, and why does Apple need it?
Managing a bunch of Apple devices without the right tools is a tricky balancing act. Basic controls aren’t enough. Unified Endpoint Management helps by offering a centralized platform that brings order to the complexity of managing Apple devices (along with other OSs), empowering IT teams to configure, secure, and monitor them all with ease.
Apple mobile device management makes sure every iPhone, iPad, and MacBook operates in sync with organizational needs. From ensuring software is up to date, to secure data, to control what users can and can’t do on their devices, UEM does it all. The better you manage your devices, the smoother your operations will run.
Apple and UEM: A perfect match for every industry
What makes Apple such a great choice across all these industries, and how does UEM play a role in managing them effectively?
Healthcare: Protecting patient data
According to a 2024 KLAS report, 64% of healthcare organizations use Apple devices, making them the most used commercial devices in healthcare.[2] Doctors and nurses rely on iPads and iPhones for accessing patient records, prescribing medications, and communicating within the hospital. UEM ensures that these devices remain HIPAA-compliant and secure, with features like device encryption and secure app management. UEM also allows healthcare organizations to monitor and restrict access to patient data, ensuring that only authorized personnel can view sensitive information.
Education: Managing classrooms of iPads
Schools and universities have embraced Apple devices for education, using iPads, Macs, and even Apple TVs to enhance learning. With Apple UEM, institutions can easily manage a large number of devices, controlling what apps and content are accessible to students. UEM allows schools to roll out software updates, enforce security policies, and ensure that devices are used for educational purposes —preventing distractions like unauthorized browsing or gaming during class.
BFSI: Securing sensitive data
Financial institutions need to ensure that their Apple devices are secure and compliant with industry standards. UEM allows financial firms to manage apps, control data access, and track devices, all while ensuring that they meet compliance requirements like GDPR. By controlling the entire Apple ecosystem, UEM protects sensitive financial data and reduces the risk of costly breaches. Leveraging Apple for BFSI, UEM ensures a secure and compliant environment tailored for the financial sector.
Retail: Seamless operations
In retail, Apple devices are used for everything from managing inventory to running point-of-sale (POS) systems. UEM simplifies the management of these devices, enabling retail businesses to deploy, update, and secure their devices without disrupting operations. With UEM, retailers can ensure that all devices are always up to date with the latest software, providing a seamless experience for both employees and customers.
Key concepts in Apple device management
Before we explore the specific benefits of UEM for Apple devices, it’s important to understand some of the foundational concepts that drive effective device management. These concepts set the stage for why UEM is essential for organizations looking to manage and secure Apple devices at scale.
1. Device supervision: A higher level of control
Device supervision is a critical mode for managing Apple devices in business, education, and institutional settings. When Apple devices are in supervision mode, IT teams gain access to a broader set of controls, features, and configurations, far beyond what is available on unsupervised devices.
For organizations, this level of control means better security, consistent device configurations, and the ability to customize devices according to their specific use cases—whether it’s an employee’s iPhone, a classroom of iPads, or interactive kiosks in retail or hospitality settings. Supervision is achieved through the Device Enrollment Program (DEP) as the primary method, or using tools like Apple Configurator 2 (AC2).
2. Apple Configurator 2: The deployment powerhouse
For large-scale deployments, Apple Configurator 2 is an indispensable tool. This macOS application enables organizations to configure, deploy, and manage multiple Apple devices simultaneously, ensuring that they are ready for use across various environments. Whether you need to supervise a batch of devices or enforce a particular configuration, Apple Configurator 2 is designed for efficiency.
In a UEM context, Apple Configurator 2 enables unsupervised devices to be enrolled into a management system by preparing them for deployment via DEP. It integrates with UEM solutions to configure settings, install profiles, and enforce business-specific requirements, making it ideal for organizations managing high device volumes or frequent turnover.
3. Apple ID vs. Managed Apple ID: Personal vs. organization-wide access
An Apple ID is typically associated with personal use, allowing users to access a variety of Apple services, including iCloud, app purchases, and data synchronization across devices. In an organizational setting, however, an Apple ID can quickly blur the line between personal and work-related use, potentially creating security risks and management complexities.
Managed Apple IDs provide businesses, schools, and government agencies with centralized control and enforced security settings on BYO devices. They maintain data privacy, streamline app distribution, and simplify device management, making them essential for organizations prioritizing secure Apple device usage.
4. APNs: Enabling secure communication between devices and apps
Apple Push Notification Service (APNs) acts as a bridge for delivering push notifications to devices. APNs ensures that any important updates, alerts, or information are securely delivered to iOS, iPadOS, macOS, and watchOS devices in real-time.
For organizations utilizing UEM for Apple, APNs is an essential feature. Not only does it facilitate secure communication between apps and users, but it also allows UEM solutions like Scalefusion to push updates, enforce policies, and notify users about device status, security alerts, or compliance requirements.
In a business context, APNs can be leveraged to ensure that the right messages reach the right devices, whether it’s a security alert, a device configuration change, or a software update.
5. Apple Declarative Device Management: Simplifying and Streamlining Control
Apple Declarative Device Management (DDM) takes device management to the next level by introducing a more proactive and streamlined approach. Apple DDM operates on a declarative model where devices are configured to know their desired state in advance.
This innovative method reduces back-and-forth communication with servers, making updates faster and more efficient. It also ensures devices can proactively adapt to new configurations, even in high-turnover environments.
For organizations using UEM, DDM offers a significant advantage by improving scalability and responsiveness. IT teams can push policies and settings more effectively, ensuring Apple devices remain compliant, secure, and aligned with business objectives.
How UEM simplifies Apple device management
Now that we’ve gone over the basics, let’s see how UEM makes managing Apple devices easier. Apple Business Manager (ABM) helps with setup and provisioning, but it’s UEM that steps in to handle the day-to-day management, secure the devices, and keep everything running smoothly.
With Apple UEM, this job gets a lot easier.
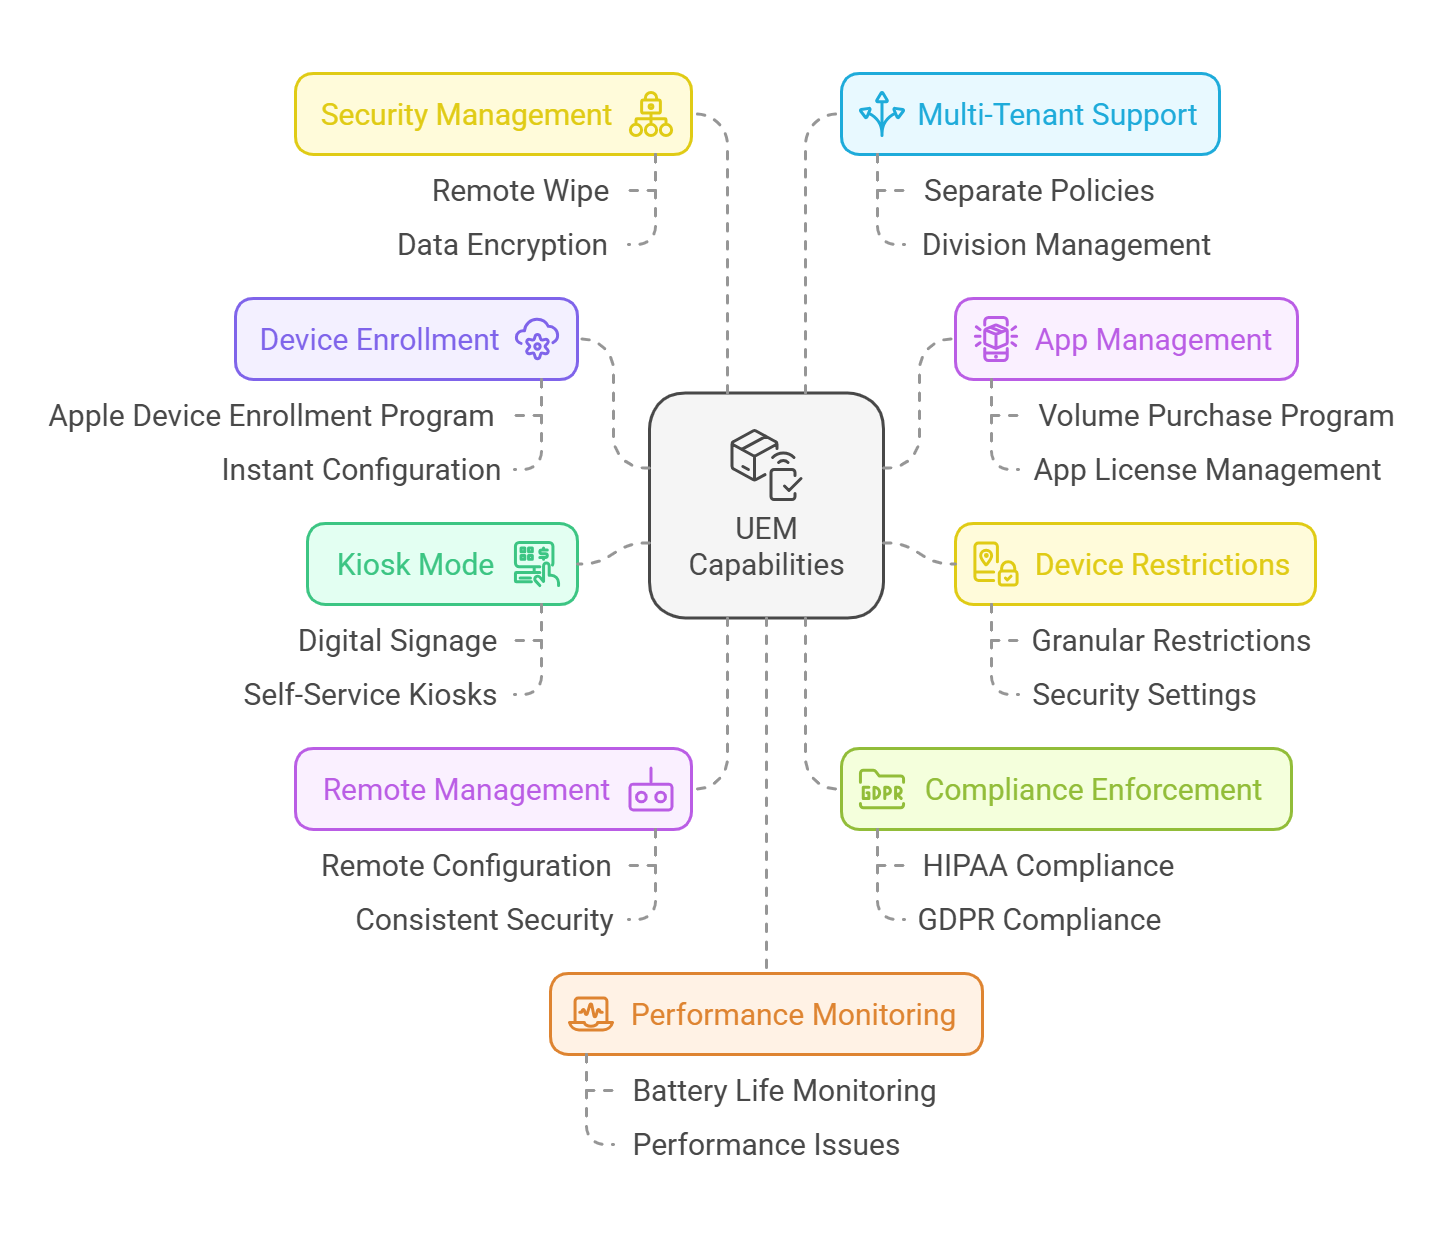
Apple device enrollment program (DEP): Automates the enrollment of devices, allowing IT teams to set up Apple devices straight out of the box. This streamlines large-scale deployments and ensures devices are instantly configured and ready for use without manual intervention.
Volume purchase program (VPP): Enables bulk purchasing and distribution of apps across multiple Apple devices. This feature allows organizations to easily manage app licenses and ensure that every device has the necessary software installed, updated, and maintained.
Granular device restrictions: UEM provides the ability to implement precise device restrictions, such as limiting access to specific apps, disabling certain features (e.g., camera or AirDrop), and enforcing security settings to align with organizational policies. This is crucial in environments like healthcare, retail, or education, where device usage needs to be controlled.
Kiosk mode: UEM allows devices to be locked down into a specific app or set of apps, turning them into dedicated kiosks. This is perfect for situations like digital signage in retail or self-service checkouts, where devices are meant to serve a single purpose and require strict usage control.
Remote configuration, support, and management: IT admins can remotely configure settings, manage devices, and apply updates across all Apple devices, eliminating the need for on-site support and making it easier to maintain consistency in configurations and security policies.
Compliance enforcement: UEM helps ensure compliance with industry standards such as HIPAA, GDPR, and PCI-DSS by enforcing security policies like encryption, password complexity, and data protection. This is essential in sectors like healthcare, finance, and education where regulatory compliance is a priority.
Security management: UEM offers advanced security controls, such as remote wipe capabilities, device tracking, and data encryption, ensuring that if a device is lost or stolen, sensitive data remains protected and inaccessible.
Multi-tenant support: For managed service providers or businesses with different divisions, UEM can provide a multi-tenant architecture, allowing for the management of different Apple device fleets under one system, but with separate policies and configurations for each tenant.
Battery and performance monitoring: UEM offers real-time monitoring of device health, including battery life and overall performance, helping IT teams proactively address issues before they impact productivity.
How UEM improves endpoint security for Apple devices
There’s no end to data breaches, malware attacks, and insider threats but we can definitely prevent them with the help of a UEM solution. Endpoint security is the first line of defense when it comes to securing Apple devices within an organization.
UEM solutions enhance security through several key features:
Device Compliance and Granular Restrictions: UEM solutions enforce security policies such as password rules, encryption, OS updates, and app restrictions. These help ensure compliance with industry regulations (HIPAA, GDPR) while protecting sensitive data from unauthorized access.
Zero Trust Access: UEM platforms enable a zero-trust security framework, where only authenticated users and compliant devices are allowed access to corporate resources, minimizing the risk of unauthorized entry.
Remote Lock and Data Wipe: In the event of a lost or stolen device, UEM solutions allow IT admins to lock or wipe the device remotely, securing sensitive corporate data and preventing unauthorized access.
Secure Network Connectivity with VPN Integration: UEM solutions configure and enforce VPN settings on Apple devices to ensure secure connections, especially for remote workers. This is further strengthened with endpoint security features like split tunneling and traffic filtering.
Proactive Security with Automatic Updates: UEM solutions ensure that devices are always up to date with the latest OS versions and security patches, protecting against vulnerabilities associated with outdated software.
I/O Device Access Control for macOS: UEM platforms allow organizations to manage and restrict the use of external devices like USBs and peripherals, preventing unauthorized data transfers and enhancing security on macOS.
Apple devices, while known for their robust security features, still face potential threats—whether it’s a lost iPhone with sensitive business data or a compromised app on an iPad. UEM solutions like Scalefusion, when paired with endpoint security solutions like Veltar, create an unbreakable defense against these risks.
Why Scalefusion is ideal for Apple device management
Scalefusion goes beyond basic UEM features like supervision, app control, and compliance enforcement. It offers robust tools to simplify and enhance the management of macOS and iOS devices, making it a comprehensive solution for businesses.
Support for all your Apple devices – Scalefusion is compatible with a wide range of Apple devices, from iPhones and iPads to Mac computers. Whether you’re managing mobile devices or desktop setups, you can handle them all from one unified platform, streamlining operations.
Dive deep with DeepDive – From the Scalefusion dashboard, you can get quick, graphical insights into your device inventory. View key metrics like platform-wise enrollment, active/inactive devices, and license usage. This data allows you to make informed decisions and track your device fleet more effectively.
Top-notch security – Keeping your business data secure is non-negotiable, and Scalefusion goes above and beyond to protect it. With features like remote device locking, data wipe, and passcode enforcement, you can ensure Apple devices are always secure and compliant with your company’s policies.
Effortless enrollment – Thanks to integration with Apple’s Device Enrollment Program (DEP), setting up Apple devices is a breeze. Zero-touch enrollment allows you to quickly onboard devices without physical interaction, making the process both fast and hassle-free.
Kiosk Mode and App Control – Scalefusion’s Kiosk Mode lets you restrict Apple devices to just one app or a set of apps, preventing unauthorized access and ensuring the device is dedicated to its intended function.
Granular policy control with Groups and Subgroups – Scalefusion gives you the ability to manage devices at a granular level. By organizing devices into groups and subgroups, you can apply specific policies to different teams or departments, offering greater control and tailoring device settings based on organizational needs.
No-code IT Workflows – Streamline IT tasks by automating and scheduling actions without coding. Create task flows, set execution times, and maintain compliance effortlessly.
Remote Troubleshooting with Remote Cast and Control – With the Remote Cast and Control feature, IT teams can mirror a device’s screen in real-time and take full control of the device to resolve problems. This eliminates the need for physical access, reduces downtime, and ensures your team can quickly address issues.
Seamless integration with Apple’s ecosystem – Scalefusion seamlessly integrates with Apple’s native services, such as iCloud, iTunes, and Apple School Manager. This tight integration ensures smooth syncing of apps, data, and settings across your Apple devices, providing a unified experience for your business.
OS Updates and Patch Management – Scalefusion simplifies OS updates and patch management, automating the process to keep your Apple devices secure and up to date. Scalefusion UEM leverages Apple’s declarative device management (DDM) protocol to further streamline the update process. With DDM, you can schedule updates for macOS devices based on your local time zone, ensuring updates are applied at optimal times. This ensures that devices always install the latest version when multiple updates are available, simplifying the update management process.
Ensure long-term success with Apple UEM
With Apple devices becoming more prevalent across businesses, schools and industries, managing them efficiently is essential. Scalefusion UEM ensures your device management solution evolves alongside your organization, seamlessly adapting to the latest Apple updates.
Scalefusion UEM provides a seamless experience for managing Apple devices, with continuous updates that ensure compatibility with the latest Apple advancements. Its scalability allows organizations to easily manage growing numbers of Apple devices, while its interoperability ensures smooth integration with not just new Apple technologies and updates but also any other OS or device type that your business or employees love and use.
Get in touch with our experts for more details and book a free demo call. Start your 14-day free trial today, with full access to all features, and discover how easy device management can be!
About Scalefusion Scalefusion’s company DNA is built on the foundation of providing world-class customer service and making endpoint management simple and effortless for businesses globally. We prioritize the needs and feedback of our customers, making sure that they are at the forefront of all decision-making processes. We are dedicated to providing comprehensive customer support services, and place emphasis on customer-centric thinking throughout the organization.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.