Skip to content

Essential cybersecurity measures when scaling your business

As businesses grow and expand in the digital era, their security must also advance. Business expansion brings more cybersecurity risks, including cyber attacks and data breaches. Because the cost of data breaches is currently very high, businesses face a challenge: as they grow, they become more attractive to hackers.

This is why it’s vital to consider boosting cybersecurity as your business grows. Let’s explore how a strong cybersecurity plan can safeguard intellectual property, sensitive data, and other crucial business resources.

Key takeaways

  • As businesses grow and expand, their cybersecurity risks also increase

  • To safeguard against increasing threats, a scalable cybersecurity policy should be developed

  • Conducting an internal cybersecurity audit helps identify system strengths and  weaknesses

  • Strengthening IAM ensures users have appropriate access privileges based on their roles

  • Encryption and VPNs safeguard sensitive data, making it unreadable to unauthorized individuals, and prevent data interception

  • Aligning with compliance requirements helps businesses avoid legal complications

  • Network segmentation limits the extent of damage a cyber attacker can cause

Understanding cybersecurity for business growth

Ensuring your business runs smoothly involves giving your team access to networks and IT systems. But as you do this, you also make your business a bigger target for problems. When you have more devices to keep safe and lots of data to handle each day, the chances of a cyberattack increase as your business grows.

Related articles


What is Security Compliance Management

In Depth

What is Security Compliance management?

And it’s not helping that cybercrime is on the rise. Different kinds of attacks can slow down or even stop your business. This can hurt how much your customers trust you, how people see your brand, and how much money you make.
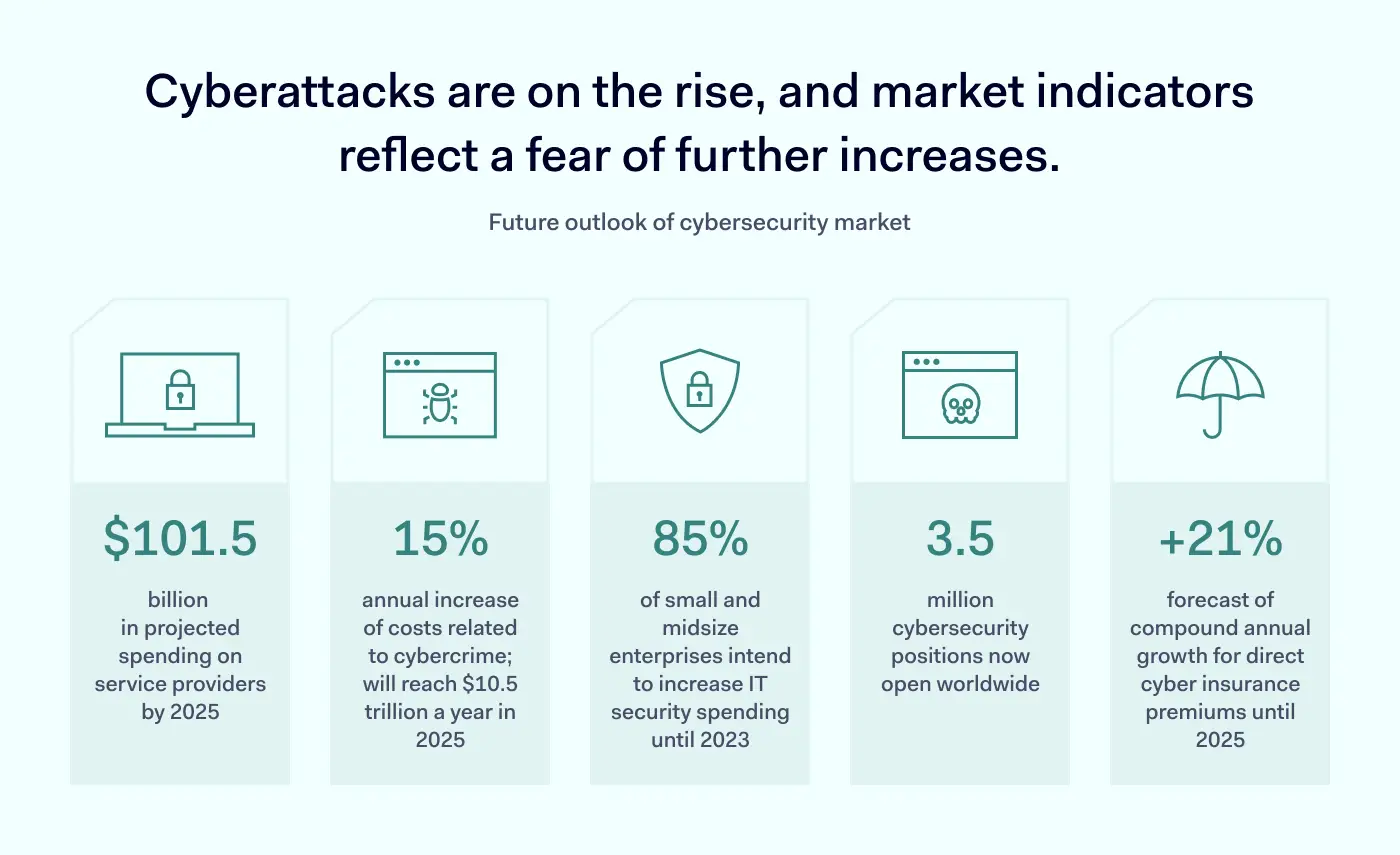
When the key to doing well in business is being able to bounce back, you can’t forget about cybersecurity. These days, keeping your business safe from online problems is just as important as any other basic part of your business. The people who handle IT and the ones who run the business need to work together. If they don’t, your business can’t keep growing because it won’t be safe from new kinds of problems.

What are cybersecurity threats that businesses may face when scaling up?

Expanding a business means making it bigger online, which can lead to more cybersecurity problems. Here are some specific security issues that a business might have while growing:

Cloud problems: When businesses get bigger, they use more cloud services. But these can be weak against cyberattacks. For instance, outsiders might access private data if cloud settings aren’t set up right.

Increased attack surface: When a business grows, its networks, systems, and data increase. Attackers get more chances to break in, causing data leaks.

Insider threats: With more employees, there’s a bigger chance of trouble from insiders. Some might want to intentionally harm the company (like unhappy workers), while others might accidentally cause problems (by clicking on bad links).

Phishing and social engineering: These types of attacks go up as businesses get bigger. Bad actors try to fool employees into sharing secret info.

Third-party vulnerabilities: Growing companies often work with more outside vendors. But these vendors might not have great security. They could open the door to attackers.

Advanced Persistent Threats (APTs): Some attacks never stop and keep trying to break in for a long time. Big companies are often targets for these attacks because they can lead to big rewards.

Distributed Denial-of-Service (DDoS) attacks: Bigger companies might get hit with attacks that flood their systems, causing them to crash.

More complications: Expanding often means adding new tech and software, making things more complex. This can make it tough to keep everything safe and organized.

Regulatory compliance: As businesses get larger, they usually need to follow more rules, especially if they operate in many places. They could expose data and get fined if they don’t follow these rules.

Scaling security: the key to successful growth

When the number of threats increases and their techniques become increasingly sophisticated, this calls for a cybersecurity framework encompassing a scalability and growth plan. This means aligning with current requirements while considering infrastructure modernization for businesses.

Creating a scalable security system ensures that your cybersecurity program can grow with it as your business grows, not lag behind. A scalable security system can anticipate the changing landscape and proactively address potential security risks before they become an issue. Therefore, investing in scalable security is critical to sustainable business growth security.

Scaling your business safely: essential online security measures

As your business grows, it’s important to approach cybersecurity carefully. This helps protect your company from online threats, keep your data private, and follow rules and regulations.

1. Conduct an internal cybersecurity audit
Associative visual for a cybersecurity audit 1400x800

Conducting an internal audit is a crucial first step toward scaling cybersecurity. It helps an organization gain a comprehensive understanding of its existing cybersecurity posture. This includes identifying strengths, weaknesses, and vulnerabilities within the system. Without a clear picture of the current state, it’s challenging to determine where improvements are needed.

The audit also helps to identify potential risks and threats. This involves analyzing the security infrastructure, data handling processes, employee practices, and more. The critical areas that need the most attention can be prioritized by knowing the risks. It ensures that resources are allocated effectively to maximize security.

2. Educate employees
A “human firewall” refers to the idea that employees, through their awareness, knowledge, and actions, can play a crucial role in preventing and mitigating cybersecurity incidents. Employees who are educated about cybersecurity threats, best practices, and policies are better equipped to recognize and respond to potential attacks.

Regular cybersecurity training can help them understand the latest tactics used by cybercriminals and how to avoid falling victim to scams, phishing attempts, and social engineering attacks.

Creating a strong cybersecurity culture within an organization instills the belief that every employee has a role in protecting the company’s data and systems. The organization’s overall security posture improves when cybersecurity is everyone’s responsibility.

3. Strengthen Identity and Access Management (IAM)

As an organization grows, the complexity and scale of its operations also increase. This growth leads to more employees, contractors, partners, and customers accessing various resources and systems within the organization. As a result, the need for effective identity and access management (IAM) becomes paramount.

Different roles and departments have varying access requirements. Therefore, effective IAM ensures that users have appropriate access privileges based on their roles and responsibilities. This avoids granting excessive permissions and reduces the risk of unauthorized access. It’s a fundamental component of any cybersecurity strategy.

4. Use encryption and virtual private networks
Using encryption and virtual private networks (VPNs) is a crucial cybersecurity measure. Encryption helps to safeguard sensitive data by converting it into an unreadable format that can only be decrypted with a specific key or password. This prevents unauthorized access to data, even if it’s intercepted during transit or at rest. Without encryption, sensitive information such as passwords, financial details, and personal details would be vulnerable to theft or unauthorized use.

Meanwhile, a business VPN creates a secure tunnel between the user’s device and a remote server, encrypting all data transmitted. This prevents hackers and cybercriminals from eavesdropping on the data being exchanged. It’s particularly important when using public Wi-Fi networks, where data can be easily intercepted without proper security measures.

5. Step up your organization’s compliance alignment

Aligning with compliance requirements is a non-negotiable aspect of scaling cybersecurity. Laws, regulations, and industry standards dictate compliance requirements. Failure to comply leads to legal consequences, including fines, penalties, and lawsuits.

Compliance frameworks are designed to address specific risks and vulnerabilities in the cybersecurity landscape. Regulations like GDPR and HIPAA set certain data privacy and security standards that businesses must adhere to. By meeting these compliance requirements, your business avoids legal complications and demonstrates to clients and customers that you prioritize their data’s security.

6. Implement network segmentation

Associative visual for network segmentation 1400x800

Network segmentation involves dividing your network into multiple segments, each with its security controls. These segments are then isolated, creating barriers that restrict unauthorized access and the lateral movement of attackers within the network. It limits the extent of damage a cyber attacker can cause if they manage to breach your system. It’s vital to a scalable security strategy, protecting your business scales.

Even if hackers access a segmented network, they cannot move laterally across the network. This means that the hackers are trapped within the network segment, giving companies more time to respond to threats and contain the damage.

Protect your business with NordLayer: your cybersecurity partner

As your business expands, keeping it secure becomes crucial. You can take simple steps to ensure your growth is safe. Educating your employees and organizing your network are some of these steps. Working with partners who can grow with you is also smart.

NordLayer is here to help when your business is growing fast. No matter what is your business size or work model, you can keep your network security up to standard.

With NordLayer, you can enable secure access to your cloud platforms. Additional controls and ZTNA-focused contextual checks can be implemented to improve the organization’s security posture further.

Organizations using NordLayer can set up resource access policies with SSO, network segmentation, site-to-site tunnels, and more. There is an audit log for all actions completed within the Control Panel, including gateway connection timestamps helping to keep track of what’s happening within your network.

NordLayer makes your business more secure. Want to know more? Get in touch with our sales team to learn more about our offerings.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Simplify remote employee onboarding with a complete checklist

Remote working is now a standard feature of the work landscape. From IT support to DevOps, companies rely on armies of remote workers to keep things moving.

As remote work has expanded, companies have had to adapt their onboarding processes. Remote onboarding has become critical when ensuring a smooth transition for new hires. But how does remote employee onboarding work, and what challenges can HR teams expect?

This article presents a comprehensive remote employee onboarding checklist. Our step-by-step checklist simplifies the onboarding process, making challenges easy to overcome. The result will be a more positive experience for IT professionals and remote workers.

Challenges with remote employee onboarding

Remote onboarding integrates new hires into company culture and introduces IT systems that power the organization. But unlike standard hiring procedures, remote employee onboarding is a virtual experience.

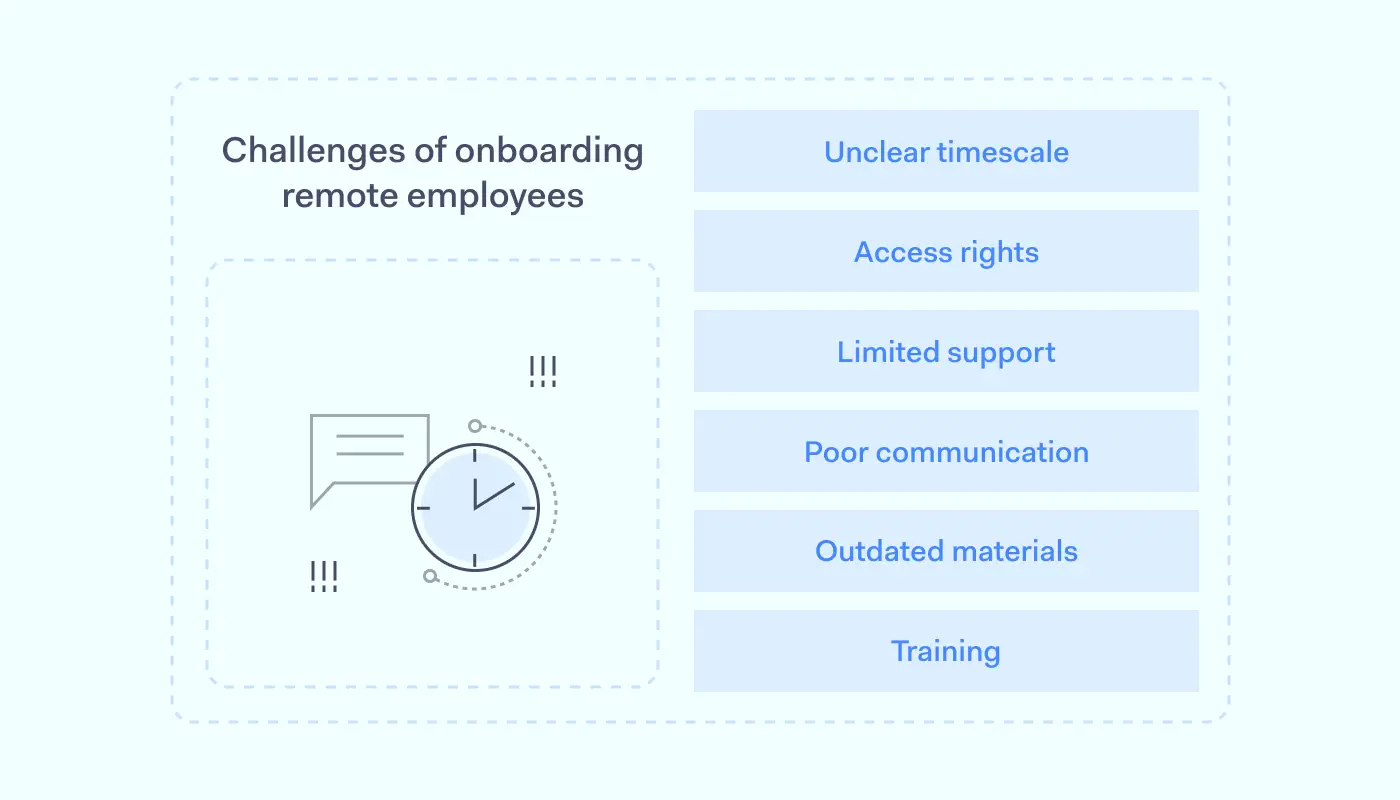
Challenges of onboarding remote employees 1400x800

HR teams do not have face-to-face contact with new hires during remote onboarding. Employees meet managers and colleagues virtually via emails, Teams meetings, and Slack discussions. This creates some unique challenges that companies need to think about.

1. Lack of a clear onboarding timescale

Onboarding tasks like creating access profiles, logging devices, and providing security training takes time. New hires may need to arrange calls with IT teams, HR professionals, and departmental colleagues.

Companies may provide employees with approved hardware like authentication tokens or access cards. And contracts and confidentiality agreements are often part of the process.

As a result, onboarding processes aren’t usually over in hours. They can even extend beyond the first week. New hires can wait over a week before accessing applications and databases. So HR teams must set itineraries for each stage of the remote onboarding process.

2. Managing access credentials and permissions

Each new hire must have an appropriate access control profile before accessing network assets. But establishing access controls for different resources can be challenging.

Security teams must create accurate profiles for new employees and connect permissions to their corporate role. They must also ensure that new hires have suitable credentials and train workers to use enterprise-wide 2FA or Multi-factor authentication systems.

3. Limited technical and administrative support

Remote onboarding can be highly technical. Employees sometimes need to update their hardware and security setups to meet company requirements. Companies often use unique platforms and apps that require orientation training. Collaboration tools can also lead to bottlenecks, making it harder to start work efficiently.

Every remote hire needs support to overcome these issues. But with many new employees entering an organization and limited IT resources, providing this support can be difficult.

4. Communication problems

Ideally, HR teams and managers would introduce new hires to the company via face-to-face meetings. But that’s not possible with remote onboarding. The distance between new hires and central offices can result in communication issues.

Without instant feedback, it’s also easy to lose critical information the new hire needs. And this is even more challenging when workers speak a different language.

New hires may also struggle to create personal connections with their colleagues. Integrating a new hire into the company culture becomes very difficult. Companies thrive when workers are connected and willing to share information. But disconnected remote workers rarely collaborate effectively.

5. Out-of-date onboarding materials

New remote employees require relevant information about technology, access, and cybersecurity. But company policies constantly change. HR teams may not maintain up-to-date onboarding databases. And they often provide the wrong information during remote onboarding processes.

For example, a company might install a data loss prevention (DLP) system to protect critical client data. But new hires may not receive guidance about classifying and handling data. This results in security risks and frustration when they begin work.

6. Delivering cybersecurity training

Cybersecurity in the workplace now extends to home offices. New remote employees need the knowledge required to use company assets securely, wherever they are. Whether you are hiring managers or freelance designers, delivering the correct cybersecurity training is challenging.

Video calls, emails, and downloadable presentations are a robust basis for security training. But they do not always add up to a productive learning environment. New hires may have questions about policies and processes. Technical problems could interfere with training events. And managers may lack assurance that employees retain critical information.

Remote employee onboarding checklist: what you need to know

When done well, remote onboarding allows workers to hit the ground running. It makes sure employees are cybersecurity aware. And it minimizes the workload on IT support teams as hires become familiar with corporate systems.

But a poorly executed remote onboarding program can be disastrous. Companies can lose the social connections that make teams effective. IT staff can become overwhelmed. Poor security practices creep into everyday work, raising the risk of phishing and malware attacks.

A well-structured remote onboarding policy streamlines the process. And creating effective systems relies on IT professionals. The following checklist provides a roadmap to design onboarding systems that integrate new hires without raising security risks or damaging productivity.

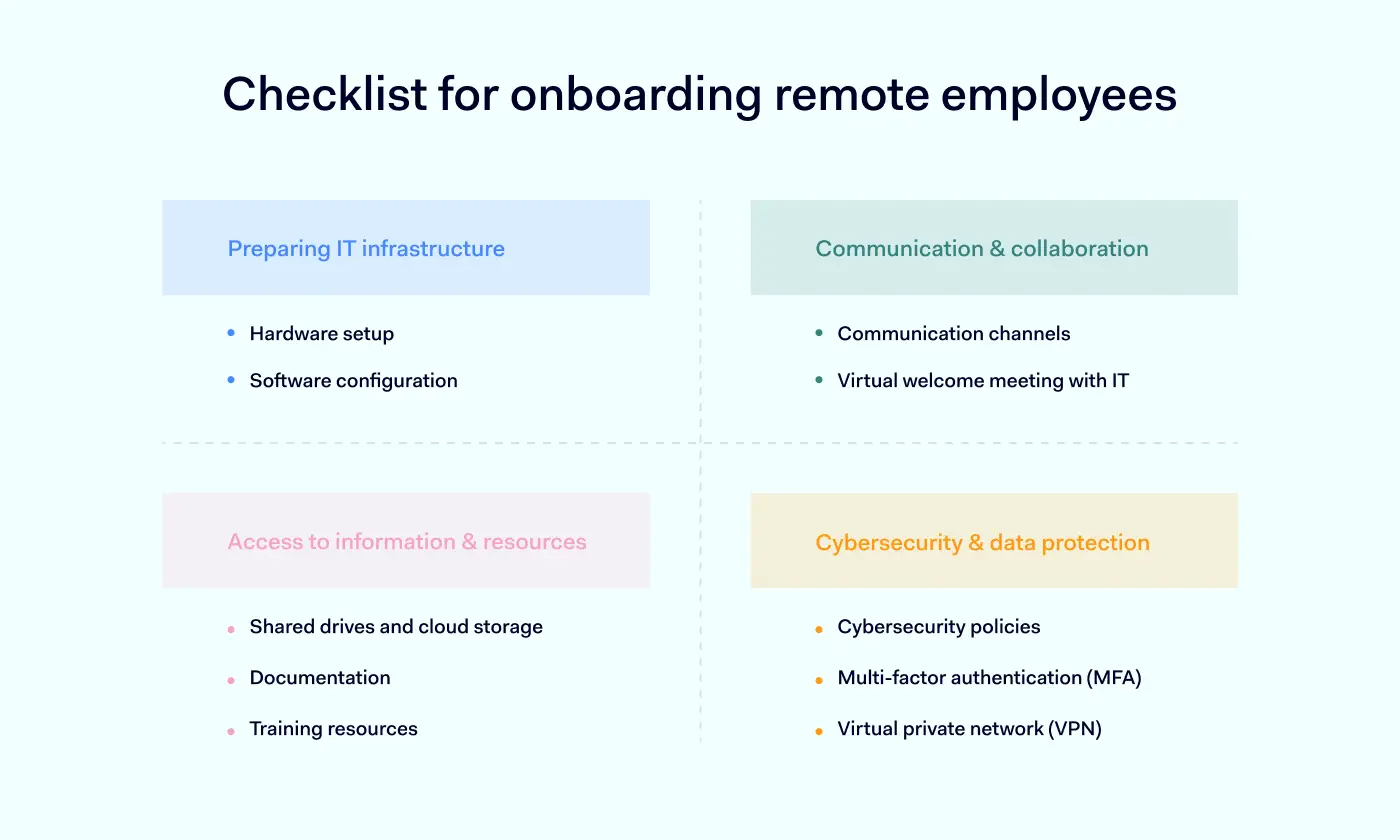
1. Preparing the IT infrastructure

New hires must usually make changes to their home IT setup. IT teams need to ensure staff have appropriate workstations and operating systems. They need to consider cybersecurity, as well as providing critical communication tools. And IT staff must provide proper support to make IT infrastructure operational.

Hardware setup

At the start of the onboarding process, prepare any necessary hardware. Match up new hires with required laptops or authentication peripherals. Prepare the hardware for shipment as quickly as possible.

OSHA can also fine companies that put the health and safety of remote workers at risk. In any case, protecting worker health is crucial. Verify that each workspace meets ergonomic requirements. And provide any necessary furniture to create safe, comfortable environments.

Software configuration

Remote employees need access to essential applications. IT teams should prioritize the configuration of video conference software and communication tools. Set up messaging apps and virtual meeting platforms. This will keep new hires informed and help to integrate them quickly.

IT must check that software supplied to remote devices has the correct licenses. And technicians should test every critical app. Ensure the worker can access central or cloud-hosted resources and that performance meets minimum benchmarks.

2. Cybersecurity and data protection

Remote workers can create cybersecurity risks to both network assets and sensitive data. IT teams need to prioritize security when introducing new employees.

Cybersecurity policies

Review your security policies before onboarding new workers. Security policies should cover all critical risks. For example, they should clearly explain password policies for remote workers. And they should include details about penalties for policy breaches.

Provide cybersecurity training for every hire. Remote workers should understand the main phishing risks and the importance of using updated threat detection tools. They should be aware of corporate data handling policies. Including a list of best practices in the employee handbook is advisable. This list should provide guidelines for critical security issues.

Multi-factor authentication (MFA)

Remote workers should connect via secure authentication systems. Implement multi-factor authentication for all access requests. MFA requires multiple authentication factors for each login request. It can apply to SSO portals or individual messenger apps.

Ensure every employee has correct credentials and that authentication tools connect seamlessly with privileges management systems.

Virtual Private Network (VPN)

Virtual private networks encrypt data passing between remote workers and central network resources. They provide an essential layer of protection for information and should be part of every remote onboarding process.

Inform new hires how to access the company VPN. Provide client software and any required hardware. And check connection speeds to ensure seamless connectivity.

3. Communication and collaboration

Create smooth communication channels between your new hire and the IT department. Onboarding remote workers involves a lot of technical information. And employees usually have queries or issues to resolve. Following these communication best practices will help.

Communication channels

Add remote employees to relevant team chats and email lists. Introduce them to colleagues in team chat rooms, and ensure staff can use communication tools effectively. If you need to provision specialist collaboration tools, go ahead and do so.

Introduce virtual meeting tools and check for bandwidth or configuration issues. Licensing problems can interfere with some video meeting tools. Double-check to ensure everything is up to date.

Virtual welcome meeting with IT

Schedule a virtual introduction meeting with relevant IT professionals. This is an opportunity to explain critical technology issues and reinforce cybersecurity training.

The meeting is a social event that introduces personalities and gives new hires the confidence to raise questions. Take onboard employee feedback and use it to make the onboarding process more efficient. The meeting also allows technicians to test video conferencing tools, allowing IT staff to fine-tune configurations.

4. Access to information and resources

Network resources should be available to remote employees when they complete security training. This should take place as quickly as possible. IT teams should plan so that access privileges slot into place automatically.

Shared drives and cloud storage

Link each new hire to a role-based access management profile. Access management tools document which resources are available to the user. Users should have easy access to data and apps that are relevant to their role, including company intranets and cloud environments. But IT teams should block access to all other resources on shared drives and cloud containers.

Be careful to provide the right privileges for each role. If you are hiring a large group of remote workers for a project, you can use generic RBAC profiles. But hiring managers requires a more tailored approach for each individual.

Documentation

Make security and IT policies available to every new hire. At the introductory meeting, explain how to access documentation and how policies are updated and maintained. If possible, create an employee handbook that includes everything remote workers need to know.

Training resources

Remote employees require virtual training. So prioritize access to digital training materials and resources. From the start, security training is a core part of the company culture. And make access to resources as flexible as possible, allowing workers to fit training into their onboarding routine.

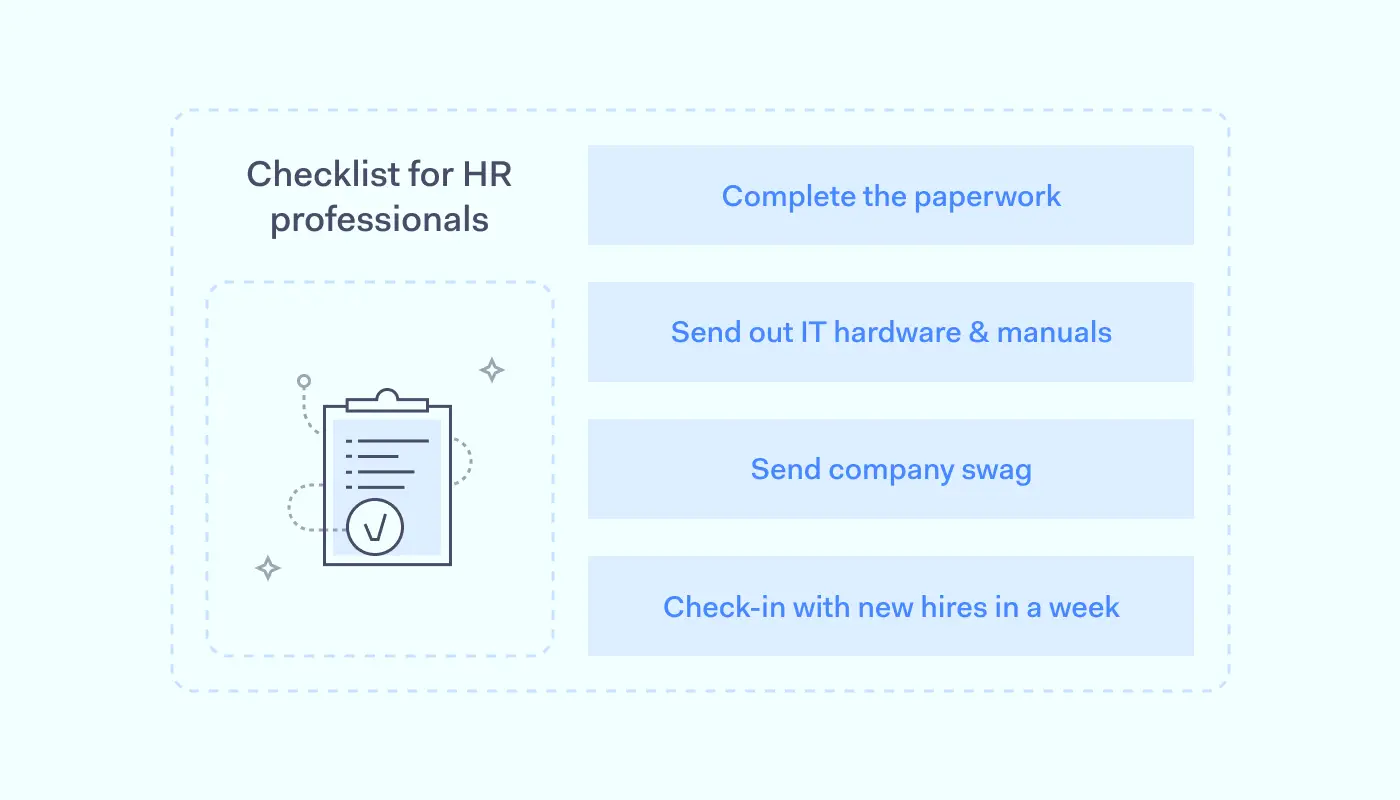
Checklist for HR professionals

The other side of the remote onboarding coin relates to Human Resources teams. HR professionals are critical in introducing new employees and making the onboarding experience more enjoyable.

Company orientation tasks complement the work of IT departments. Here are the key actions that HR officers need to consider:

Ensure paperwork is done

Nothing is more frustrating during onboarding than receiving an endless stream of documents to sign. Make this task pain-free by creating a single cache of necessary paperwork for each onboarding procedure.

Automate the provisioning of key documents. This reduces the number of times the new employee needs to provide digital signatures and makes human error less likely. Assign a team member to field queries about forms or policies. And apply encryption to secure any personal information transmitted during onboarding procedures.

Send pre-boarding IT hardware and manuals

Ensure employees are comfortable and safe by providing ergonomic furniture and peripherals like back supports and ergonomic mice. And field requests for specific hardware. Employees may need more powerful laptops or software upgrades. Provide whatever hires need to work safely and productively.

Manuals are an important part of the HR onboarding process. Produce an appealing employee manual that blends clarity and accessibility. Include information about cybersecurity and how to access critical workloads. But also add sections on company history and employee benefits the company provides.

Send company swag

One of the most important HR tasks during remote onboarding is creating a sense of belonging to the company culture. That isn’t easy to achieve without face-to-face contact. HR professionals need to think creatively about the onboarding experience and make every new employee feel welcome from the start.

Providing company swag in the first week is an easy win. Simple branded items like cups, mouse pads, pens, or diaries can add a human touch. But you can go as far as you like. Some companies like to send hoodies or T-shirts. Others send laptop cases, beach towels, or practical items like reusable water bottles.

Check up on new hires in the first week

HR is the first point of contact for each new employee during their first days on the job. Make HR professionals available to talk via video calls. And proactively check up on remote workers to keep them in the loop.

HR can also encourage staff to complete the onboarding schedule within the agreed timescale. Don’t force new hires to finish the onboarding process too quickly. Everyone adjusts at their own pace. But be clear about what employees must do, and let them know when everything is complete.

Simplify and secure remote onboarding with NordLayer

Remote onboarding is a challenge for businesses in every area of the economy. Workers need to receive training and information. They need the tech to carry out their duties. And they must have the right access privileges and authentication credentials to work securely.

NordLayer will help you create a secure and streamlined onboarding experience. Our solutions make the IT side of remote onboarding much easier.

Companies can use our secure remote access solutions to replace existing Virtual Private Networks. NordLayer’s business gateway encrypts traffic passing from remote workstations to the company intranet. And they scale easily. Organizations can easily add more workers as the need arises.

Our remote access systems facilitate network segmentation for assigning role-based privileges, offering network administrators precise controls over the network. They integrate with all major authentication providers. And they do so cost-effectively. Companies can onboard hires rapidly, safely, and affordably.

If you are struggling with remote employee onboarding, NordLayer can assist. Use our checklist to guide you and feel free to get in touch with our team today.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

The ever-evolving landscape of cloud security trends

In today’s business environment, cloud computing is the most flexible and cost-efficient method to set up operations. Yet, as businesses increasingly rely on cloud-based services to store, manage, and exchange data, this attracts unwanted guests.

Consequently, there has been a significant increase in data breaches, disrupting business operations and jeopardizing companies’ security and compliance worldwide. These breaches often stem from attackers exploiting vulnerabilities and misconfigurations in cloud systems.

This blog will cover the most recent cloud security trends that are shaping the industry. By keeping up with these developments, businesses can enhance the protection of their digital assets and reinforce the security of their cloud computing infrastructure to mitigate potential breaches.

Key takeaways

  • Cloud computing offers businesses cost-efficiency, flexibility, and scalability, but it also introduces security vulnerabilities and risks

  • The shared responsibility model requires cloud providers to secure the infrastructure while customers secure their data and applications

  • The cloud security landscape is constantly evolving and businesses need to keep up with new trends

  • Cloud security has progressed significantly with improvements in data protection, network security, and connectivity

  • The future of cloud security will see more integration of AI and machine learning

  • To keep up with the trends, organizations can regularly update security policies, implement advanced threat detection, embrace automation, and foster a culture of security awareness

Understanding the concept of cloud security and why it matters today

Cloud computing solves many business problems like scalability, cost-efficiency, and flexibility. At the same time, for most businesses, it also means stepping into unfamiliar territory where it’s easy to leave gaps that hackers could exploit.

The shared responsibility model is also something that needs to be established. In it, the cloud provider is responsible for securing the underlying cloud infrastructure, while the customer is responsible for securing their data and applications. Though it sounds simple, it’s not always easy to crystallize a comprehensive cloud security approach.

As more organizations embrace cloud adoption and rely on cloud services, the need for effective cloud security measures has never been greater.

Evolutions in cloud security

Cloud security has come a long way since its inception. Initially, concerns regarding data protection and network security limited cloud adoption (as well as a requirement for stable online connectivity). Fortunately, as cloud technology has matured, so has its security.

The concept of cloud computing emerged in 1950 with the development of mainframe computers, which could be accessed through thin or static clients. Since then, cloud computing has undergone several iterations, progressing from static clients to dynamic ones, from software-based systems to service-oriented solutions.

Security problems started cropping up when businesses began entrusting their data to major companies like Amazon. Despite the numerous benefits and efficiency improvements, storing critical data on servers that customers couldn’t physically access challenged the conventional notion of security. As data storage expanded in type and volume, hosting companies implemented more extensive precautions to safeguard the data.

The current state of cloud security

Today’s cloud service providers go to great lengths to protect the data stored on their servers. This includes thorough employee background checks to minimize the risk of insider attacks and isolation procedures that prevent one company from accessing another’s data. Yet, it’s still the user’s responsibility to ensure secure passwords and connections like they would have if the data were stored locally.

Encryption of data at rest and in transit, network segmentation, and adopting cybersecurity mesh architectures have all enhanced cloud security. As cloud environments become increasingly complex and multi-cloud adoption rises, ensuring consistent security across different platforms and providers becomes challenging. This emphasizes the need for ongoing security training and proactive new technologies adoption.

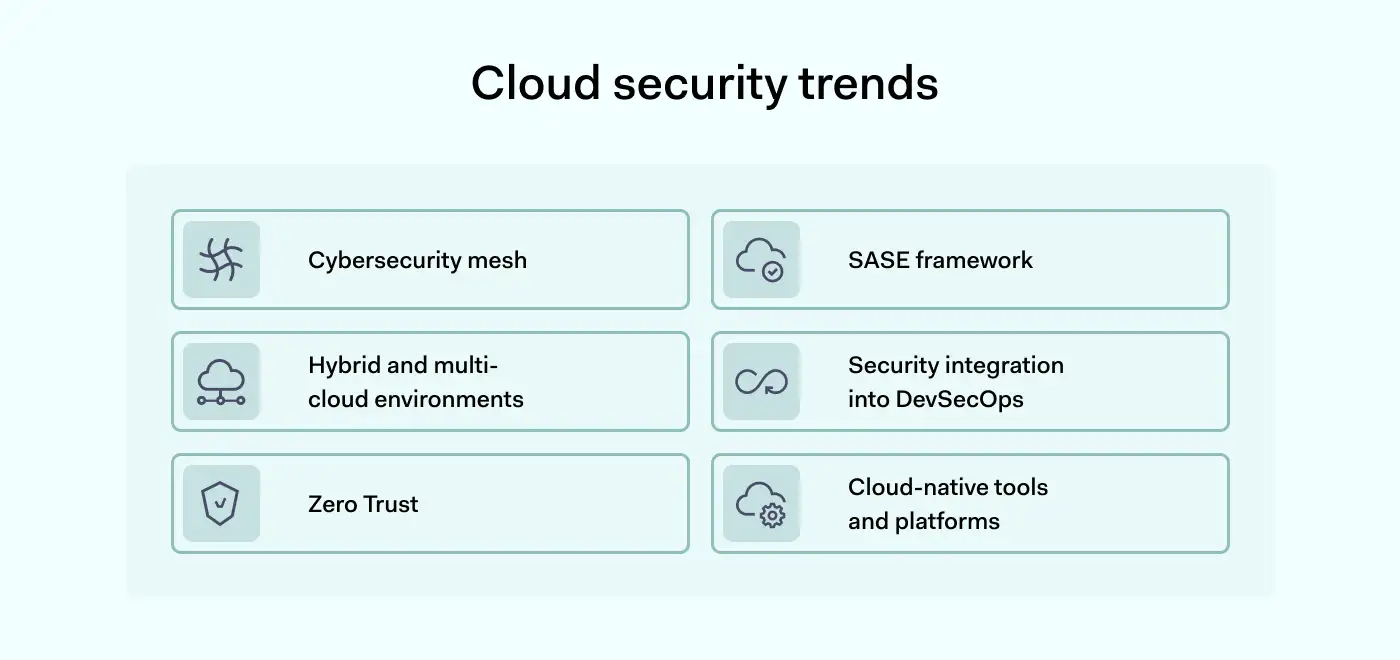
Security teams must be aware of the latest cloud security trends to stay ahead of the ever-changing threat landscape. Here are the main ones you should be aware of:

1. Cybersecurity mesh

Companies are adopting the concept of cybersecurity mesh to ensure the security of data and assets in the cloud. This approach involves creating a distributed network and infrastructure that forms a security perimeter around the individuals and devices connected to the network. By implementing cybersecurity mesh, companies can centrally manage data access and enforce security policies, aligning with Zero Trust architecture principles.

2. Hybrid and multi-cloud environments

The trend in cloud security involves adopting a hybrid approach or leveraging multiple cloud services. Organizations can migrate their data entirely to the cloud or keep some data and services hosted privately. The hybrid approach combines local and cloud-hosted services, allowing for more secure deployments. Additionally, using multiple clouds has gained popularity, with companies adopting a multi-cloud strategy. This approach allows for better utilization of security tools across different environments, such as SIEM and threat intelligence.

3. Zero Trust

The principle of Zero Trust emphasizes verifying rather than blindly trusting anything within or outside an organization’s perimeters. With the increasing reliance on cloud services, Zero Trust should be a priority for all organizations. Traditional perimeter security measures and firewalls are insufficient to protect valuable resources such as user data and intellectual property. Zero Trust enhances security around every device, user, and connection, enabling proactive threat management and comprehensive defense strategies.

4. SASE framework

Gartner has stated that the future of network security lies in the cloud. The Secure Access Service Edge (SASE) framework offers a cloud-based cybersecurity solution that supports digital enterprises’ dynamic and secure access needs. It combines wide area networking (WAN) capabilities with multiple security features such as anti-malware and security brokers to establish a comprehensive security environment within a cloud infrastructure. SASE is an essential framework for securely connecting users, systems, and endpoint devices to a unified cloud environment.

5. Security integration into DevSecOps

DevSecOps is a methodology that integrates security protocols throughout the software development lifecycle (SDLC). Organizations can address threats proactively rather than reactively by incorporating security measures early in the development process. DevSecOps is particularly effective in fast-paced, fully automated software development lifecycles, enabling secure innovation. Collaboration between DevOps and security teams is essential to implement strong security measures throughout the entire supply chain and make security a continuous process within the continuous integration/continuous delivery pipeline.

6. Cloud-native tools and platforms

Cloud-native applications designed specifically for the cloud environment are becoming increasingly prevalent. These applications take advantage of the speed and efficiency offered by cloud platforms. Traditional security tools designed for on-premises applications may not be adequate to protect cloud-based resources. Companies recognize the need to invest in cloud-based security tools and platforms to safeguard their cloud resources against potential attacks.

While cloud security progresses along with cloud computing, it’s crucial to acknowledge the dark side of trends that security teams must address. Attackers are finding new ways to exploit vulnerabilities, and organizations must be cautious. Here are the emerging threats directed at cloud computing security:

Slow patching leaves web services vulnerable

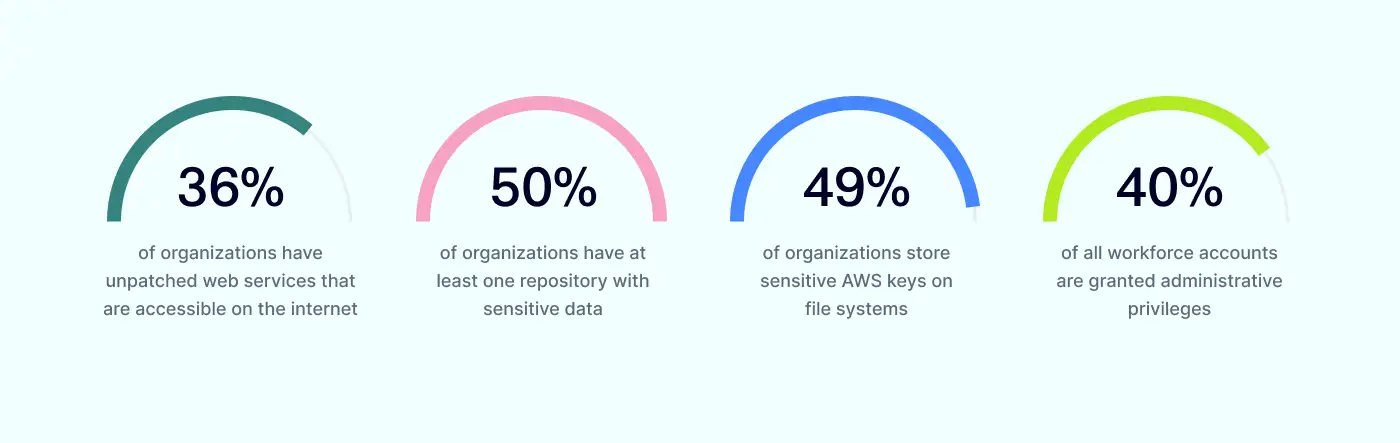
Based on the Orca Security report, 36% of organizations have web services in their cloud environment that are accessible to the Internet but remain unpatched. Such services pose a significant risk as they contain known vulnerabilities and bugs, which can serve as primary entry points for attacks on cloud environments. The absolute majority of cyber-attacks on cloud infrastructure begin with the exploitation of these known vulnerabilities.

Unpatched vulnerabilities provide malicious actors with easy access to cause service downtime, enable remote code execution, or facilitate unauthorized remote access in certain cases. Users must promptly apply fixes through updates or patches to contain potential risks.

Git repositories containing sensitive data

Storing sensitive data in Git repositories should be avoided at all costs. It may include information like database passwords, API keys, encryption keys, hash salts, and secrets, which can be mistakenly pushed into a Git repository. While it deviates from security practices, the inclusion of this data into the source code of an application might inadvertently leak it to hackers. Therefore, repositories must be checked for sensitive information, which should be removed from the repository and its history.

AWS keys storage on file systems

At least 49% of organizations store sensitive AWS keys on file systems within virtual machines. AWS keys can function as backdoors to your system. They can grant access to all your resources and the ability to perform any operation, like launching EC2 instances or deleting S3 objects. Therefore, it’s crucial always to store your AWS keys separately and avoid sharing them with external parties.

Instead of AWS, it’s a good practice to use temporary credentials. They include an access key ID and secret access key that would also include a security token specifying the expiration date of the credentials.

Too many administrators for a single organization

Single sign-on providers suggest putting limits on the administrative privileges. For instance, only 50% of admins should have super admins privileges, if you have more, you’re risking your organization’s security. This is much more than it would be advisable, as administrators have many permissions that directly relate to your information security.

As a rule of thumb, it’s generally inadvisable, except in exceptional circumstances, not to define an IAM role with full administrative privileges. Such a role grants anyone who assumes it the ability to perform any action on any resource within the account. This violates the Principle of Least Privilege (PoLP), significantly expands the attack surface, and increases the risk of a full account takeover.

The road ahead: future of cloud security

Looking ahead, the future of cloud security is full of challenges and opportunities. One of the most obvious courses for development is the continued integration of artificial intelligence and machine learning into cloud security operations. These technologies will enable autonomous threat detection, automated incident response, and adaptive security measures.

The speed at which these developments will reach the end-users depend on the service providers’ initiatives to invest in advanced technologies. Yet, it’s likely that the shared responsibility model will continue to be relevant, and while the user will be provided with more tools, it will still be needed to make sense of the provided data and act on it.

Conclusion

Cloud security is an ever-evolving landscape with new trends and challenges emerging regularly. For this reason, organizations must stay alert and recognize the importance of cloud security and its recent developments.

By adopting advanced technologies, adopting proactive security measures, and fostering collaboration with cloud providers, organizations can navigate the complex cloud environment while safeguarding their data, applications, and infrastructure against evolving security threats.

FAQs

What is the role of AI in cloud security?

AI can be used to enhance threat detection and response capabilities by analyzing vast amounts of data and identifying patterns that may indicate security threats or anomalies. In addition, AI can assist in automating security tasks, such as security patching, vulnerability management, and incident response. This can help prevent various types of attacks like malware, phishing attempts, and data breaches, reduce the workload on security teams, and improve overall efficiency.

What is a cloud access security broker (CASB), and how does it contribute to cloud security?

CASB is an intermediary between an organization’s premises infrastructure or network and cloud service providers. It helps organizations extend their security policies and controls to the cloud environment. Offering a range of security functionalities, it also helps to expand visibility into cloud storage, data loss prevention (DLP), access control, threat detection, encryption, and compliance monitoring.

How does the Zero Trust model enhance cloud security?

The Zero Trust model enhances cloud security by shifting the traditional perimeter-based security approach to a more dynamic and granular model. Instead of blindly trusting users or devices within a network, Zero Trust assumes that all network traffic, whether from inside or outside the network, is potentially malicious and must be verified before granting access. That way, organizations can reduce the risk of lateral movement within their cloud environment, mitigate the impact of compromised credentials, and improve overall security posture.

What strategies can organizations adopt to stay ahead of future cloud security trends?

To stay ahead of future cloud security trends, organizations can:

  • Regularly assess and update security policies

  • Implement advanced threat detection and response capabilities

  • Embrace automation and orchestration

  • Foster a culture of security awareness

All of these actions improve overall business security posture and help stay one step ahead of unauthorized access attempts.

How can NordLayer help?

As cloud computing is at the center of modern business operations building, its security is at the forefront of business priorities. A robust cloud security strategy must include access controls, encryption, firewalls, and auditing. However, finding a reliable partner isn’t always easy.

NordLayer can be a helpful ally when securing public and private cloud infrastructure setups. Using our Virtual Private Gateways, SaaS applications, and other resources can be reached efficiently but securely. With features like IP allowlisting, overall business network security posture is improved, allowing only authorized personnel to access your cloud environments.

Identity checks can be enforced using 2FA and SSO to ensure secure authentication. A tandem of all of these features makes cloud security management safer and easier to manage.

Contact the NordLayer team to learn more about how your cloud infrastructure could be secured.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Decrypting the common misconceptions about encryption

In cybersecurity, encryption is one of the key tools to secure sensitive information against unauthorized access. Nowadays, it’s one of the major components of digital data privacy. It’s also a word often encountered, yet frequently misunderstood. This leads to the proliferation of misconceptions that cause confusion and steer individuals toward poorly-informed security choices.

Therefore, in this article, we aim to raise awareness about potential encryption misconceptions that could expose organizations to cyber threats and data breaches. We’ll decode the risks of inconsistent encryption practices and highlight the best practices for adopting encryption in daily operations. By learning how to distinguish between myths and facts, you can effectively fortify your online security and avoid costly errors in safeguarding confidential data.

Understanding encryption

To understand how encryption works, it’s essential to grasp the principles of cryptography. This is the science and practice of designing secure communication and information systems. It provides the theoretical foundation and mathematical tools for creating encryption algorithms that protect sensitive information from unauthorized access.

Cryptography follows the four main principles:

  1. Confidentiality. Refers to rules and guidelines, ensuring the information is restricted to specific senders and recipients.

  2. Data integrity. Maintains that a message cannot be modified during the transit between the sender and the intended recipient.

  3. Authentication. Verifying that the data claimed by the user rightfully belongs to them.

  4. Non-repudiation. Assurance that associated parties cannot deny the authenticity or the act of sending a message.

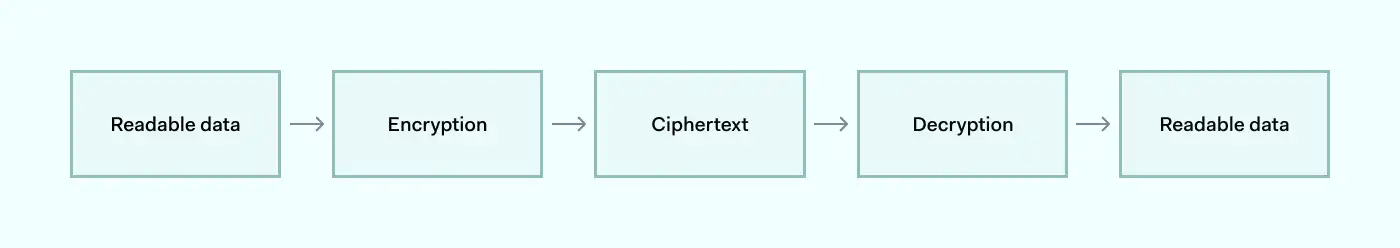
Therefore, encryption is a specific technique within the field of cryptography. It converts plain, readable data into a scrambled, unintelligible form (ciphertext) using an encryption algorithm and key. It can only be decoded to the original form with a decryption key. The primary purpose of encryption is to ensure the confidentiality of data, preventing unauthorized users from accessing the original content.

Encryption involves hashing an arbitrary length value to obtain a fixed-length ciphertext that depends on the algorithm used. Some examples of cryptographic algorithms include Advanced Encryption Standard, Triple DES, Blowfish, and ChaCha20.

The misconception explained

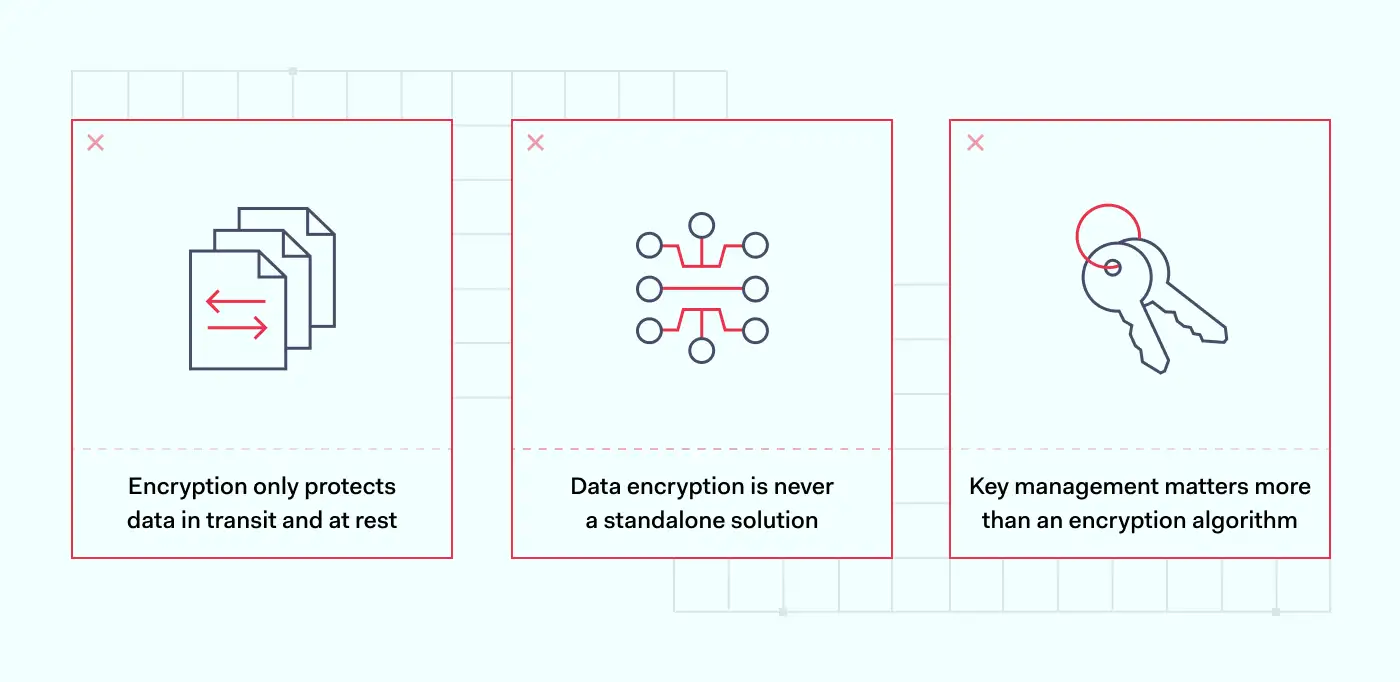
One common misconception about encryption is that it’s an ultimate defense against all cybersecurity threats. While encryption does help against various threats, even if the data is stolen, it’s not a standalone solution. Here are some things that you should consider:

Encryption only protects data in transit and at rest. Encryption is effective in cases when the data is stored or transmitted. This makes it unreadable to anyone without the decryption key. However, it is vulnerable if the end-point device has been compromised and the data is decrypted for use.

Data encryption is never a standalone solution. Encryption should be combined with other cybersecurity measures like multi-factor authentication, firewalls, regular system updates, and more to create a robust defense against cyber threats. This means using multiple layers of security to protect valuable data and assets, with each layer providing more challenges for attackers to breach the system.

Key management may matter more than an encryption algorithm. It’s easy to pick the most complex encryption algorithm for sensitive data and assume it is now protected under nine locks. The problem is that the strength of encryption also depends on the secrecy and security of the keys used to encrypt and decrypt the data. Therefore, proper key management is as important as technological security measures.

The risks of inconsistent encryption practices

Our previous examples show that encryption isn’t enough to guarantee data security. What sometimes matters more than cipher algorithm strength is encryption practices.

Inadequate protection of sensitive information

At its core, encryption transforms understandable information, or plaintext, into unintelligible text, or ciphertext. If an organization inconsistently applies encryption, there’s a chance that some data will not be adequately protected. This inconsistent protection could be due to only encrypting certain data types, failing to encrypt data in transit, or neglecting to encrypt backup files.

As a result, sensitive information such as intellectual property, customer data, or financial records may be exposed. Malicious actors can exploit this information, leading to financial losses and damage to a company’s reputation.

Regulatory non-compliance

Regulations such as the General Data Protection Regulation (GDPR) in the European Union, the California Consumer Privacy Act (CCPA) in the U.S., and many others, require businesses to take specific steps to protect consumer data, often including encryption. Inconsistent encryption practices can lead to regulatory non-compliance, resulting in potential fines and penalties and further damaging an organization’s reputation.

Interoperability issues

Inconsistency in encryption can lead to compatibility problems. For example, if different encryption algorithms or key lengths are used across different systems or departments within the same organization, it can cause difficulty in data sharing and management. This can lead to inefficiency, potential data loss, or the need for resource-intensive data translation.

Best practices for adoption of encryption practices

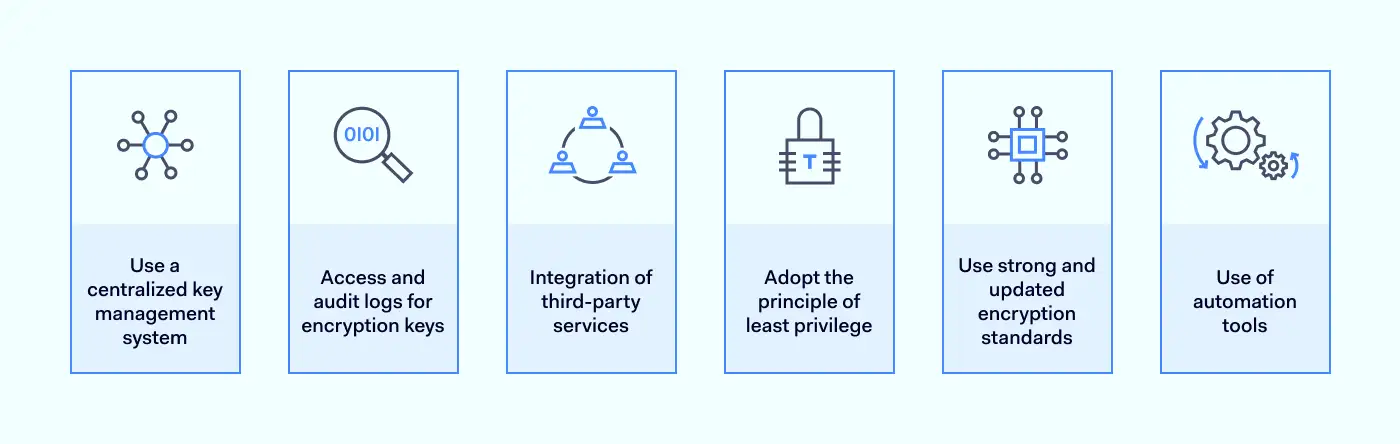
Encryption is vital to any cybersecurity strategy as it adds an essential layer of protection for data at rest and in transit. Here are some of the best practices for adopting encryption.

Centralized key management system

Different encryption keys used can present a significant challenge regarding storage accessibility. A centralized key management system allows storing encryption keys separately from the encrypted data, providing an additional layer of security in case of a data breach, and minimizing the risk of compromise.

The centralization of the key management process offers further advantages in terms of processing. While the encryption and decryption operations occur locally where the data resides, activities like storage, rotation, and generation of keys are performed away from the actual data location. This separation streamlines the encryption-decryption process and enhances overall security.

Access and audit logs for encryption keys

Access to encryption keys should be limited only to those individuals who genuinely need them. This control can be established through a centralized key management process, ensuring only authorized users are granted access. Avoid cases when a single user holds exclusive access to the key, as this could lead to problems if the user loses their credentials or if data corruption occurs.

Additionally, comprehensive audit logs maintenance is critical to encryption key management. These logs must meticulously document the complete interaction logs of each key, encompassing its creation, deletion, and usage patterns. Every operation related to these keys should be recorded, including details about who accessed the key and the timestamp of access. This facilitates compliance requirements and enables efficient investigation during a key compromise.

Integration of third-party services

Organizations frequently rely on external devices distributed across their network to perform various functions. Still, these devices often lack seamless interaction with databases. Consequently, choosing encryption methods compatible with the third-party applications they interact with is essential.

Incorporation of third-party APIs entails significant risks like SQL injection, cross-site scripting, denial of service, spoofing, malware code, and others. This makes API security a major concern. To address this issue, it’s necessary to use API Management Platforms, providing a range of features like monitoring, analytics, alerting, and life-cycle management.

The principle of least privilege

The principle of least privilege advocates that organizations should grant administrative rights based solely on user roles. This restricts the assignment of such rights to applications and minimizes exposure to internal and external threats. As access is limited through role-based control mechanisms, the potential for harm is reduced.

It’s important to note that this principle is not limited to human users. The principle encompasses all interconnected software applications, systems, and devices. For successful implementation, a centralized control system is necessary. It mitigates the risk of “privilege creep” and minimal access levels to human and non-human entities.

Use strong and updated encryption standards

Outdated encryption algorithms are easier to crack because the processing power of computers has dramatically increased. Using robust and up-to-date encryption standards like AES-256 can provide better security. Complex algorithms make it nearly impossible for unauthorized individuals to access the data. This protects sensitive customer information, financial data, trade secrets, and intellectual property.

Use of automation tools

Manual key management not only consumes a significant amount of time but also introduces the risk of errors. This is especially the case when dealing with the scale of large organizations. A more intelligent approach to address this challenge is by implementing automation. For instance, automation can create, rotate and renew keys at specified intervals, proving an effective and prudent practice.

How can NordLayer help?

Encryption is an essential tool in our digital world, providing a robust line of defence against cyber threats. That said, various misconceptions surrounding encryption can undermine its effectiveness. Strong and consistent encryption practices can provide the necessary shield in our interconnected world.

This is also where NordLayer can help. NordLayer establishes connections to a Virtual Private Gateway using OpenVPN, IKEv2/IPsec, and NordLynx protocols that are encrypted with Advanced Encryption Standard (AES) 256-bit or ChaCha20 algorithms. Meanwhile, our single extension for different browsers uses Transport Layer Security encryption for web traffic.

The connections and online browsing can be further secured by enabling features like two-factor authentication, single sign-on, device posture monitoring, ThreatBlock, and DNS filtering.

Most importantly, NordLayer can be set to auto-connect to a Virtual Private Gateway server as soon as an internet connection is detected. This enforces the consistent usage of security tools, as each time an employee turns on a computer, it automatically connects to a Virtual Private Gateway.

Get in touch with the NordLayer team directly to explore innovative data security solutions that make damaging data breaches much less likely.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

NordLayer 於遙距破突獎項計劃 2023 中 獲評為「整體表現最佳之遙距工作安全解決方案」


NordLayer 宣布於 2023 年度遙距破突獎項計劃(Annual RemoteTech Breakthrough Awards)中,獲評為整體表現最佳的遙距工作安全解決方案(Best Overall Remote Work Security Solution)。

在超過 1,250 個提名中脫穎而出,NordLayer 的 CTO Juta Gurinaviciute 表示:「我們對於獲獎感到引以為傲和充滿感激,尤其是在遙距工作領域。疫情迫使人們轉向遙距工作,這個獎項肯定了我們為各種公司企業提供安全可靠的遙距方案所付出的辛勤工作和奉獻。」

NordLayer 是一款針對商業用途而設計的網絡安全工具,其基於 NordVPN 標準開發,旨在為各種規模和工作模式的公司企業提供靈活且易於實施的解決方案。該工具能夠幫助公司企業以「零壓力」的方式保護網絡,通過技術改進提升網絡安全性並實現現代化的網絡和資源訪問,以符合最佳的監管合規標準。NordLayer 是一個功能強大的工具,支援公司企業採用零信任網絡接入(ZTNA)和安全網關(SWG)原則,同時提供安全服務邊緣(Security Service Edge)的網絡安全服務。它與現有基礎設施輕鬆整合,無需硬件並且考慮到易於擴展的設計,以滿足敏捷企業和分散式工作團隊當今不同的增長節奏和即時網絡安全需求。

「遙距破突獎項計劃」是全球技術創新和領導力領先市場情報和認可平台 Tech Breakthrough 的一部分,獎項旨在表彰全球在遙距工作和分佈式團隊領域所提供的卓越技術、服務、公司和產品之成就,共為技術公司和解決方案在消息傳遞和通信、項目管理、虛擬活動、團隊協作、虛擬辦公室、協作設計等領域提供一個公開認可的論壇。

關於 NordLayer
NordLayer 是現代企業的自適應性網絡存取安全解決方案,來自世界上其中一個最值得信賴的網絡安全品牌 Nord Security。致力於幫助 CEO、CIO 和 IT 管理員輕鬆應對網絡擴展和安全挑戰。NordLayer 與零信任網絡存取(ZTNA)和安全服務邊緣(SSE)原則保持一致,是一個無需硬件的解決方案,保護公司企業免受現代網絡威脅。通過 NordLayer,各種規模的公司企業都可以在不需要深入專業技術知識的情況下保護他們的團隊和網絡,它易於部署、管理和擴展。

關於 Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products. Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.