Skip to content

NordLayer features in review: Always On VPN

A stable internet connection is imperative in a digital world setup. More important is to keep those connections secure.

In a proactive move towards fortifying cybersecurity, NordLayer’s Always On VPN helps achieve this goal easily. This security feature ensures a VPN-only connection to company resources connection to company resources, online browsing, IP masking, and traffic encryption. 

The purpose of Always On VPN is straightforward: to guarantee continuous, secure internet access by disallowing unencrypted user connections.

Always On VPN reassures IT managers that the company’s cybersecurity tools are consistently and effectively utilized. When centrally activated via the Control Panel, end users can no longer disable it.

always on VPN screenshot 1The functionality enables effective security policy enforcement that is critical to ensuring adherence to internal company procedures. It helps maximize the efficiency of the deployed cybersecurity strategy.

How does Always On VPN work on NordLayer?

Designed with user convenience in mind, Always On VPN automates the VPN connection, liberating users from the task of manually connecting to the VPN.

enabled always on VPN screenshotThe feature is activated as soon as a user signs into their endpoint using the NordLayer Application with the Always On VPN feature enforced.

Always On VPN guarantees that any disruption to the VPN connection will automatically disconnect from the internet until the VPN connectivity is reestablished. Without any exceptions, every employee can only access the internet via a VPN connection, regardless of their global location.

Always on VPN is easily implemented and configured on NordLayer via the Control Panel to enforce this to all employees or specific users.

How does NordLayer’s Always On VPN feature work?

Always On VPN interweaves with other NordLayer features to offer a comprehensive security package.

enabling threat block screenshot

  • The feature ensures the effective operation of DNS Filtering and Deep Packet Inspection features per their respective settings.

  • It complements the ThreatBlock feature, which filters potentially harmful websites that users may access while connected to the company gateway.

The NordLayer application settings allow employees to toggle the Always On VPN feature on or off, given that the administrator hasn’t centrally activated it.

If the IT administrator wishes to implement the Always On VPN feature across the organization, the end users won’t be able to deactivate it once it has been centrally configured through NordLayer’s Control Panel.

How is NordLayer’s Always On VPN different?

Suppose an organization needs to meet strict security requirements imposed by stakeholders or internal policies and wants to ensure that remote users always maintain an encrypted connection. In this case, the Always On VPN feature is turned on for all users.

On NordLayer, Always On VPN can be disabled for 3 minutes. It’s useful for those needing temporary internet access to log in to the NordLayer app, handle captive portals when connecting to Wi-Fi in places like hotels and airports, and troubleshoot. Although, when the given timelapse is over, the feature restores the VPN connection for the end user.

A team that travels extensively and frequently uses public Wi-Fi would benefit from enabling the Always On VPN. This reduces risks associated with insecure network connections in an airport or while working on a train.

Organizations that deal with highly sensitive information, such as e-commerce service providers, security agencies, or certain governmental bodies, may require stringent measures to prevent data leaks. Enforcing the use of the Always On VPN ensures that internet access only occurs via a secure VPN connection.

Benefits of Always On VPN

The feature has a positive impact on different stakeholders of the organization. From streamlined internet performance for staff wherever the location they work to a larger picture of implementing organizational cybersecurity strategy.

End users (employees)

NordLayer’s Always On VPN ensures that the application connects to the VPN automatically, eliminating the need for users to verify their VPN connection status. This offers peace of mind, as working without a VPN could significantly breach a company’s security policy, resulting in a data leak.

Organizations

Implementing the Always On VPN feature allows companies to bolster their security levels. Moreover, it could potentially lower cyber insurance payments due to heightened security measures.

network organization scheme screenshot

IT administrators

Ensuring users fully utilize their organization’s cybersecurity tools can be a significant challenge for system admins. With NordLayer’s Always On VPN, admins can enforce feature usage policies and configurations, streamlining compliance and reducing risks with one button click.

Importantly, the Always On VPN feature can be enabled or disabled by admins in a few seconds using the Control Panel. This adds another layer of convenience and control to the system admin’s role.

Should you use NordLayer’s Always On VPN?

The Always On VPN feature perfectly aligns with NordLayer’s vision, providing a significant internet access security upgrade. It’s perfect for organizations with a hybrid work model and whose employees frequently travel to other countries. Manual switching of the VPN may introduce security risks, and this feature mitigates such vulnerabilities.

Without Always On VPN, ensuring a secure internet connection can become challenging. This feature enhances security and helps achieve compliance with the organization’s regulatory requirements.

FAQ

What is an Always On VPN?

An Always On VPN keeps your connection secure all the time. Once enabled, it automatically connects to the best server, ensuring continuous encryption and protection without manual intervention.

Is Always On VPN a good idea?

Absolutely! Always On VPN ensures constant security, privacy, and protection. It’s like a vigilant guardian for your internet connection, always working in the background to keep your data safe.

What is the difference between a VPN and Always On VPN?

A standard VPN requires a manual connection and may sometimes disconnect, while an always-on VPN maintains a constant secure connection. Think of it as the next level of convenience and protection – with Always On VPN, your security never takes a break.

For more information on secure and seamless connectivity, visit NordLayer.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

How to sync data from MySQL to Google BigQuery using Debezium and Kafka Connect

Syncing data from a MySQL database to Google BigQuery can be a great way to keep your data up to date and easily accessible for analysis. In this article, we will explore the process of setting up Debezium and Kafka Connect to sync data from MySQL to BigQuery, providing you with all the information you need to get started. 

Why use Debezium and Kafka Connect? 

Debezium and Kafka Connect are open-source platforms that provide a powerful solution for streaming data changes in real-time between systems. That real-time interaction allows you to keep your data in sync and easily accessible for various use cases such as real-time analytics, data warehousing, and data pipeline integrations.

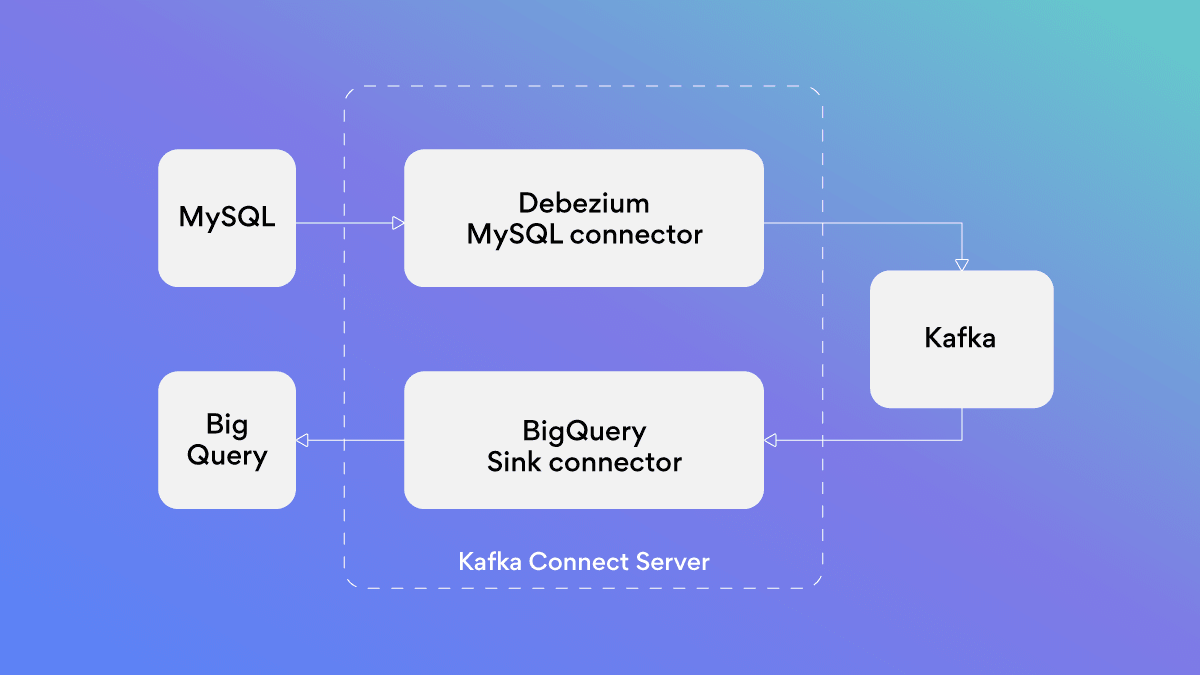
High level solution diagram

solution architecture

solution architecture

Technology used

Before we go into the details of setting up Debezium and Kafka Connect to sync data from MySQL to BigQuery, it is important to understand the technologies that you will be using and how they are connected.

Change data capture

Change Data Capture (CDC) is a technique for capturing and recording all the changes made to a database over time. This allows for real-time data replication, making it easy to keep multiple systems in sync.

CDC does this by detecting row-level changes in database source tables, which are characterized as “Insert,” “Update,” and “Delete” events. CDC then notifies other systems or services that rely on the same data.​

Apache Kafka

Apache Kafka is a distributed streaming platform that is used for building real-time data pipelines and streaming applications. It allows for the storage and processing of streams of records in a fault-tolerant way.

Kafka Connect

Kafka Connect is a framework for connecting Kafka with external systems such as databases, key-value stores, search indexes, and file systems, using so-called connectors.​

Kafka connectors are ready-to-use components that can help you to import data from external systems into Kafka topics and export data from Kafka topics into external systems. You can use existing connector implementations for common data sources and syncs or implement our own connectors.​

Debezium

Debezium is an open-source platform that allows you to easily stream changes from your MySQL database to other systems using CDC. It works by reading MySQL binlog to capture data changes in a transactional manner, so you can be sure that you’re always working with the most up-to-date data.

By using Debezium, you can capture the changes made to the MySQL database and stream them to Kafka. Data on the changes can then be consumed by Kafka Connect to load the data into BigQuery.

BigQuery setup

1. Creating a BigQuery project and dataset:

a. In the Google Cloud Console, navigate to the BigQuery page and create a new project (Creating and managing projects | Resource Manager Documentation | Google Cloud). We will name it “mysql-bigquery” for this tutorial.

b. Within the project, create a new dataset (Creating datasets | BigQuery | Google Cloud). We will name it “debezium” for this tutorial.

c. Note that Debezium will automatically create tables in the dataset that match the structure of the MySQL tables being monitored.

2. Creating a GCP service account with BigQuery editor role:

a. In the Google Cloud Console, navigate to the IAM & Admin page and create a new service account (Creating and managing service accounts | IAM Documentation | Google Cloud).

b. Give the service account a name and description, then select the “BigQuery Data Editor” role

3. Generating and downloading a key for the service account:

a. In the Google Cloud Console, navigate to the IAM & Admin page, find the service account, and click on the three dots on the right, then select “create key” (Create and manage service account keys | IAM Documentation | Google Cloud).

b. Select JSON as the key type and download the key file.

c. Store the key file securely and use it to authenticate the connector in Kafka Connect when accessing the BigQuery dataset.

Tutorial

To start syncing data from MySQL to BigQuery we will need following components:

Start required services

1. Let’s start with creating a new directory. Open Terminal and run:

1

$ mkdir mysql-to-bigquery

2

$ cd mysql-to-bigquery

2. Create a plugins directory

1

$ mkdir plugins

3. Download Debezium mysql plugin:

4. Download BigQuery plugin and put the contents into your plugins directory (in this tutorial we are using version v2.4.3). Now your plugins directory should look like this:

1

$ ls plugins

2

debezium-connector-mysql wepay-kafka-connect-bigquery-2.4.3

5. Create a new file (“docker-compose.yml”) with these configurations:

1

version: ‘2’

2

services:

3

zookeeper:

4

container_name: zookeeper

5

image: quay.io/debezium/zookeeper:2.1

6

ports:

7

2181:2181

8

2888:2888

9

3888:3888

10

kafka:

11

container_name: kafka

12

image: quay.io/debezium/kafka:2.1

13

ports:

14

9092:9092

15

links:

16

zookeeper

17

environment:

18

ZOOKEEPER_CONNECT=zookeeper:2181

19

mysql:

20

container_name: mysql

21

image: quay.io/debezium/examplemysql:2.1

22

ports:

23

3306:3306

24

environment:

25

MYSQL_ROOT_PASSWORD=debezium

26

MYSQL_USER=mysqluser

27

MYSQL_PASSWORD=mysqlpw

28

connect:

29

container_name: connect

30

image: quay.io/debezium/connectbase:2.1

31

volumes:

32

./plugins:/kafka/connect

33

ports:

34

8083:8083

35

links:

36

kafka

37

mysql

38

environment:

39

BOOTSTRAP_SERVERS=kafka:9092

40

GROUP_ID=1

41

CONFIG_STORAGE_TOPIC=my_connect_configs

42

OFFSET_STORAGE_TOPIC=my_connect_offsets

43

STATUS_STORAGE_TOPIC=my_connect_statuses

6. Let’s start the services:

1

$ docker-compose up

You should see an output similar to the following:

1

...

2

2023-01-16 15:48:33,939 INFO || Kafka version: 3.0.0 [org.apache.kafka.common.utils.AppInfoParser]

3

...

4

2023-01-16 15:48:34,485 INFO || [Worker clientId=connect-1, groupId=1] Starting connectors and tasks using config offset -1 [org.apache.kafka.connect.runtime.distributed.DistributedHerder]

5

2023-01-16 15:48:34,485 INFO || [Worker clientId=connect-1, groupId=1] Finished starting connectors and tasks [org.apache.kafka.connect.runtime.distributed.DistributedHerder]

7. Check if Debezium is running with Kafka Connect API.

1

$ curl -i -X GET -H “Accept:application/json” localhost:8083/connectors

An empty array in response shows that there are no connectors currently registered with Kafka Connect.

8. We also have MySQL running with an example database inventory. You can check what tables are there by running:

1

$ docker exec -it mysql mysql -uroot -pdebezium -D inventory -e “SHOW TABLES;”

2

+———————+

3

| Tables_in_inventory |

4

+———————+

5

| addresses |

6

| customers |

7

| geom |

8

| orders |

9

| products |

10

| products_on_hand |

11

+———————+

1

$ docker exec -it mysql mysql -uroot -pdebezium -D inventory -e “SELECT * FROM customers;”

2

+——+————+———–+———————–+

3

| id | first_name | last_name | email |

4

+——+————+———–+———————–+

5

| 1001 | Sally | Thomas | sally.thomas@acme.com |

6

| 1002 | George | Bailey | gbailey@foobar.com |

7

| 1003 | Edward | Walker | ed@walker.com |

8

| 1004 | Anne | Kretchmar | annek@noanswer.org |

9

+——+————+———–+———————–+

Configure Debezium to start syncing MySQL to Kafka

Now let’s configure Debezium to start syncing the inventory database with Kafka.

1. Create a new file (“register-mysql.json”) with these configurations:

1

{

2

“name”: “inventory-connector-mysql”,

3

“config”: {

4

“connector.class”: “io.debezium.connector.mysql.MySqlConnector”,

5

“tasks.max”: “1”,

6

“database.hostname”: “mysql”,

7

“database.port”: “3306”,

8

“database.user”: “root”,

9

“database.password”: “debezium”,

10

“database.server.id”: “184054”,

11

“topic.prefix”: “debezium”,

12

“database.include.list”: “inventory”,

13

“schema.history.internal.kafka.bootstrap.servers”: “kafka:9092”,

14

“schema.history.internal.kafka.topic”: “schemahistory.inventory”

15

}

16

}

You can find information about these configuration properties in the Debezium documentation.

2. Register a MySQL connector:

1

Bash$ curl i X POST H “Accept:application/json” H “Content-Type:application/json” http://localhost:8083/connectors/ d @registermysql.json

3. Verify that “inventory-connector” is included in the list of connectors:

1

$ curl -H “Accept:application/json” localhost:8083/connectors/

2


3

[“inventory-connector-mysql”]

4. You can now see database contents in Kafka. To see topics, run:

1

$ docker exec -it kafka bash bin/kafka-topics.sh –list

2


3

–bootstrap-server kafka:9092

4

...

5

debezium.inventory.addresses

6

debezium.inventory.customers

7

...

8


Let’s check debezium.inventory.addresses:

1

Bash$ docker exec it kafka bash bin/kafkaconsoleconsumer.sh bootstrapserver kafka:9092 topic debezium.inventory.addresses frombeginning

2


3

{“schema”:{“type”:“struct”,“fields”:[{“type”:“struct”,“fields”:[{“type”:“int32”,“optional”:false,“field”:“id”},{“type”:“int32”,“optional”:false,“field”:“customer_id”},{“type”:“string”,“optional”:false,“field”:“street”},{“type”:“string”,“optional”:false,“field”:“city”},{“type”:“string”,“optional”:false,“field”:“state”},{“type”:“string”,“optional”:false,“field”:“zip”},{“type”:“string”,“optional”:false,“name”:“io.debezium.data.Enum”,“version”:1,“parameters”:{“allowed”:“SHIPPING,BILLING,LIVING”},“field”:“type”}],“optional”:true,“name”:“debezium.inventory.addresses.Value”,“field”:“before”},{“type”:“struct”,“fields”:[{“type”:“int32”,“optional”:false,“field”:“id”},{“type”:“int32”,“optional”:false,“field”:“customer_id”},{“type”:“string”,“optional”:false,“field”:“street”},{“type”:“string”,“optional”:false,“field”:“city”},{“type”:“string”,“optional”:false,“field”:“state”},{“type”:“string”,“optional”:false,“field”:“zip”},{“type”:“string”,“optional”:false,“name”:“io.debezium.data.Enum”,“version”:1,“parameters”:{“allowed”:“SHIPPING,BILLING,LIVING”},“field”:“type”}],“optional”:true,“name”:“debezium.inventory.addresses.Value”,“field”:“after”},{“type”:“struct”,“fields”:[{“type”:“string”,“optional”:false,“field”:“version”},{“type”:“string”,“optional”:false,“field”:“connector”},{“type”:“string”,“optional”:false,“field”:“name”},{“type”:“int64”,“optional”:false,“field”:“ts_ms”},{“type”:“string”,“optional”:true,“name”:“io.debezium.data.Enum”,“version”:1,“parameters”:{“allowed”:“true,last,false,incremental”},“default”:“false”,“field”:“snapshot”},{“type”:“string”,“optional”:false,“field”:“db”},{“type”:“string”,“optional”:true,“field”:“sequence”},{“type”:“string”,“optional”:true,“field”:“table”},{“type”:“int64”,“optional”:false,“field”:“server_id”},{“type”:“string”,“optional”:true,“field”:“gtid”},{“type”:“string”,“optional”:false,“field”:“file”},{“type”:“int64”,“optional”:false,“field”:“pos”},{“type”:“int32”,“optional”:false,“field”:“row”},{“type”:“int64”,“optional”:true,“field”:“thread”},{“type”:“string”,“optional”:true,“field”:“query”}],“optional”:false,“name”:“io.debezium.connector.mysql.Source”,“field”:“source”},{“type”:“string”,“optional”:false,“field”:“op”},{“type”:“int64”,“optional”:true,“field”:“ts_ms”},{“type”:“struct”,“fields”:[{“type”:“string”,“optional”:false,“field”:“id”},{“type”:“int64”,“optional”:false,“field”:“total_order”},{“type”:“int64”,“optional”:false,“field”:“data_collection_order”}],“optional”:true,“name”:“event.block”,“version”:1,“field”:“transaction”}],“optional”:false,“name”:“debezium.inventory.addresses.Envelope”,“version”:1},“payload”:{“before”:null,“after”:{“id”:10,“customer_id”:1001,“street”:“3183 Moore Avenue”,“city”:“Euless”,“state”:“Texas”,“zip”:“76036”,“type”:“SHIPPING”},“source”:{“version”:“2.1.1.Final”,“connector”:“mysql”,“name”:“debezium”,“ts_ms”:1673446748000,“snapshot”:“first”,“db”:“inventory”,“sequence”:null,“table”:“addresses”,“server_id”:0,“gtid”:null,“file”:“mysql-bin.000003”,“pos”:157,“row”:0,“thread”:null,“query”:null},“op”:“r”,“ts_ms”:1673446748425,“transaction”:null}}

4

5


For more information on Debezium events, see this Debezium documentation.

Configure Debezium to start syncing data to Google BigQuery

Before you start configuring the BigQuery connector, move the Google BigQuery service account key file (details in previous section) to your working directory and name it “bigquery-keyfile.json”.

1. Once you have the key file, copy it to the Connect container:

1

$ docker cp bigquery-keyfile.json connect:/bigquery-keyfile.json

2. Now create a file register-bigquery.json with these configurations:

1

{

2

“name”: “inventory-connector-bigquery”,

3

“config”: {

4

“connector.class”: “com.wepay.kafka.connect.bigquery.BigQuerySinkConnector”,

5

“tasks.max”: “1”,

6

“consumer.auto.offset.reset”: “earliest”,

7

“topics.regex”: “debezium.inventory.*”,

8

“sanitizeTopics”: “true”,

9

“autoCreateTables”: “true”,

10

“keyfile”: “/bigquery-keyfile.json”,

11

“schemaRetriever”: “com.wepay.kafka.connect.bigquery.retrieve.IdentitySchemaRetriever”,

12

“project”: “mysql-bigquery”,

13

“defaultDataset”: “debezium”,

14

“allBQFieldsNullable”: true,

15

“allowNewBigQueryFields”: true,

16

“transforms”: “regexTopicRename,extractAfterData”,

17

“transforms.regexTopicRename.type”: “org.apache.kafka.connect.transforms.RegexRouter”,

18

“transforms.regexTopicRename.regex”: “debezium.inventory.(.*)”,

19

“transforms.regexTopicRename.replacement”: $1,

20

“transforms.extractAfterData.type”: “io.debezium.transforms.ExtractNewRecordState”

21

}

22

}

You can find information about these configuration properties in the official documentation.

3. To register the BigQuery connector, run:

1

$ curl -i -X POST -H “Accept:application/json” -H “Content-Type:application/json” http://localhost:8083/connectors/ -d @register-bigquery.json

In your BigQuery dataset, you will now be able to see tables matching those in MySQL.

BigQuery table data 1

Now, select data from your customers table. Emails used are for example purposes only and do not correspond to real individuals.

BigQuery table data 2BigQuery table data 2

You can create a new entry in MySQL customers table:

1

$ docker exec -it mysql mysql -uroot -pdebezium -D inventory -e “INSERT INTO customers VALUES(1005, \”Tom\”, \”Addams\”, \”tom.addams@mailer.net\”);”

You will see that a new entry has automatically synced to BigQuery.

Bigquery dataset tables

Conclusion

You should now have a clear understanding of the benefits of syncing data from MySQL to BigQuery using Debezium and Kafka Connect. With the detailed tutorial found in this article, you will be able to set up and configure Debezium and Kafka Connect yourself.

As a reminder, it’s important to test and monitor the pipeline to ensure that data is being synced as expected and to troubleshoot any issues that may arise.

For more information on Debezium and Kafka Connect, you can refer to the following resources:

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Best security tools for remote work in 2023

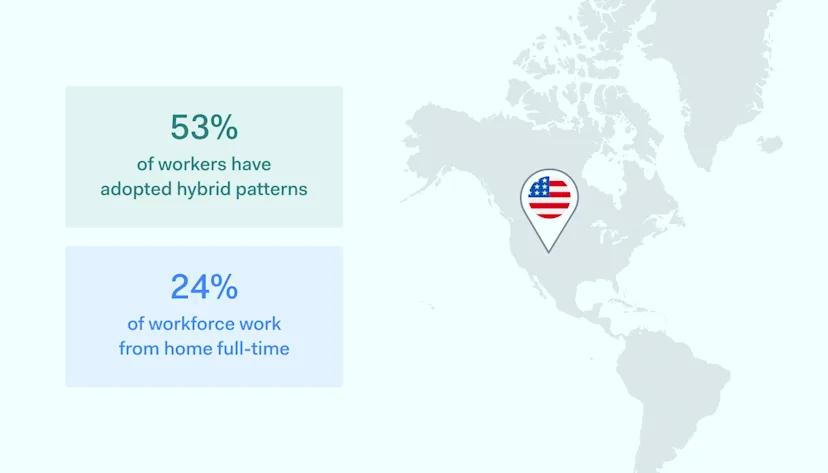
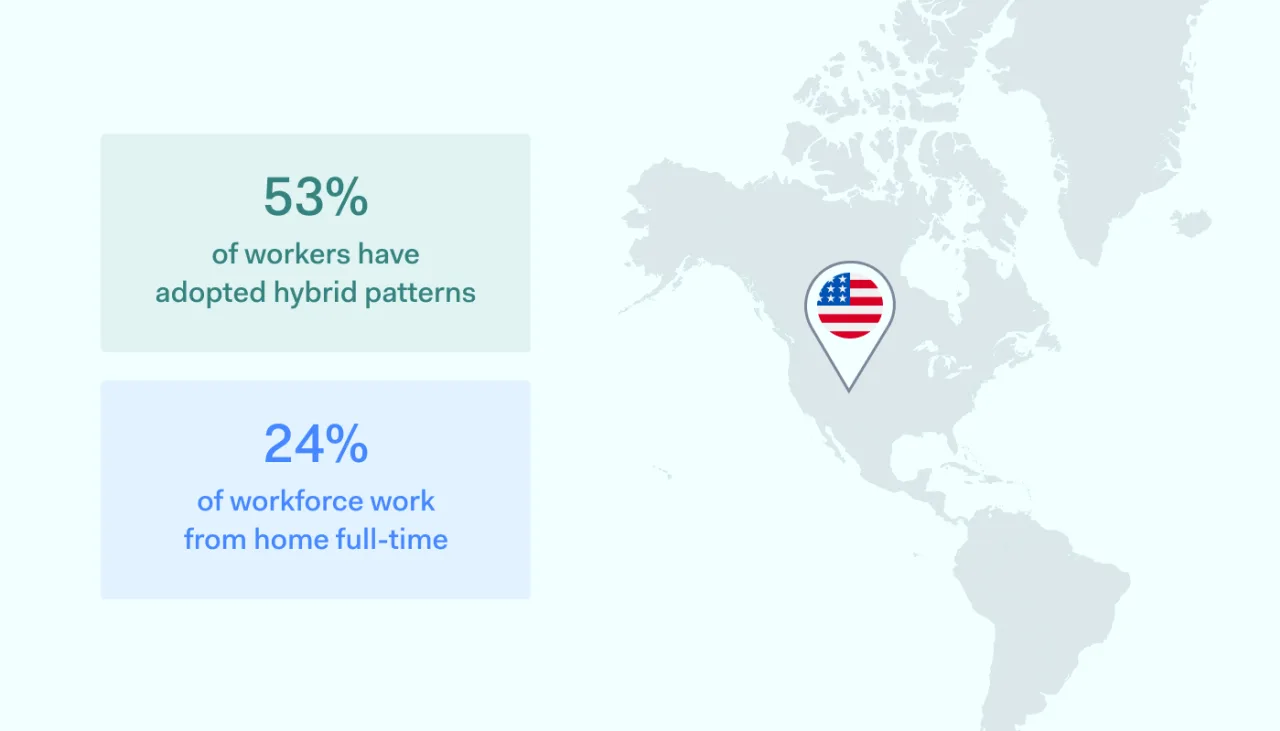
The traditional office is becoming harder to find these days. Across the world, millions of people have shifted to hybrid or fully remote work lifestyles. In the USA, 53% of workers have adopted hybrid patterns, and 24% work from home full-time. Those numbers are likely to rise with employee expectations drifting towards flexible working. 

But how should companies respond? Enabling remote working can be risky, but it comes with many benefits. In this article, we’ll introduce the best security tools for remote work, making it easier to relocate employees without creating extra cybersecurity risks.

Key takeaways

  • Remote working is more popular than ever. Choosing the right software and hardware tools allows off-site workforces to operate safely and productively.

  • Efficient video conferencing solutions connect team colleagues, managers, and third parties seamlessly. And they secure communications against eavesdroppers.

  • Messaging apps ensure consistent information flows between remote employees. They should allow regular updates, quality assurance checks, and assist with team building.

  • Project management systems make it easier to control dispersed teams. Managers can monitor remote workforces and set schedules for project delivery.

  • Secure storage solutions keep critical data safe. Access controls and encryption make data available for team members while preventing illegitimate access.

The evolution of remote work

Remote work is not a new phenomenon. And in the past 20 years, remote work has become routine for occupations like IT support.

However, the number of remote employees was relatively small until the Covid pandemic. When it hit, millions of workers were suddenly barred from workplaces. But companies needed to continue operations, which sparked a search for remote solutions.

Apps like Zoom became household names overnight. And organizations suddenly had to adapt their working practices to accommodate working remotely.

Fortunately, Covid-19 coincided with technological developments that made remote working easier. Internet bandwidth is increasing at a rate of around 29% per year. This allowed employees to collaborate via video conferencing without lag issues. And remote security solutions like Virtual Private Networks (VPNs) and multi-factor authentication enabled companies to create secure remote work connections.

The pandemic and technological change have paved the way for an age of flexible remote working. And this change is mainly driven by employees.

As the Covid pandemic receded, many people didn’t return to their workplaces. Workers became accustomed to spending more time at home. Now, as many as 65% of workers seek full-time remote work, and the employers need to adapt fast.
country statistics for remote work 1400x800However, not all sectors have embraced remote work. Healthcare and care professions still generally rely on face-to-face contact. Manual trades like mining or construction may always require employees to be present on site. Despite that, many industries support remote work strategies.

The IT sector has the highest proportion of home workers right now. But jobs as diverse as accounting, non-profit administration, tutoring, and graphic design are also compatible with home working.

Recent years have also seen the emergence of remote workforce technologies that enable productive and secure remote work. Project management tools, VPNs, collaboration and video conferencing apps, and cloud storage platforms make remote work easier than ever. Thus, the future of remote working seems bright.

Evaluating remote work effectiveness

Remote work is already mainstream. But it isn’t necessarily the best solution for all companies and employees.

On the positive side, statistics suggest that working from home boosts productivity and streamlines corporate operations. Additionally, major companies say that remote work is 35-40% more productive than office-based alternatives.
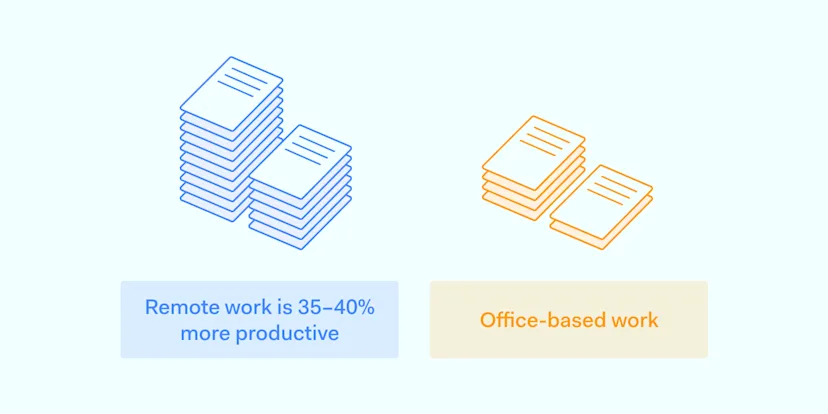
This increase could be due to the absence of distractions. Remote employees put time spent on commutes to better use. Or they might just be happier and energized by controlling their working lives.

On the other hand, remote work isn’t suitable for many occupations. As this list from the New York Times shows, this trend has barely touched plenty of jobs. Education, medicine, and construction are just a few good examples.

The pandemic forced teachers to run classes remotely. Such a method led to frustration and stress for educators and damaged educational outcomes for learners. Therefore, organizations should think long and hard before relocating any jobs involving face-to-face contact.

Companies must be aware of potential problems with remote or hybrid work models. Researchers report that remote work can come with a “promotion penalty.” Employees away from managers and offices may lose out during internal recruitment.

On-site staff also benefit from the assistance of more experienced colleagues. Younger remote workers may be disconnected from sources of knowledge. Isolation hurts productivity and dents the career prospects of remote employees.

Poorly-organized remote working systems can also lead to problems with managing them. As a result, managers may gradually extend surveillance reach to track projects and productivity. Because of that, surveillance can negate the feeling of freedom that makes working remotely so appealing.

To sum up, there are good reasons to embrace remote work. But companies should be careful when designing home working setups as this comes with new risks. Let’s explore some tools to simplify this critical task.

The best remote workforce technologies in 2023

Organizations should employ a suite of technologies for working remotely. These cover critical areas like cloud storage, project management, communication, data security, and secure remote access. Let’s see what are the top options in each category.

Cloud storage tools

Remote work teams should use secure cloud storage to host workloads and communication apps. Secure platforms apply encryption to protect data at rest. Furthermore, firewalls block illegitimate external access, and physical controls protect data centers.
Cloud platforms couple security with ease of use, meaning remote users can share files and databases instantly. Moreover, teams can update work documents, client databases, or code bases in real time. And cloud data protection tools keep the workloads safe from external intruders.

It usually makes sense to build remote work setups around cloud environments. But which cloud services provider should you choose?

Microsoft Azure

This is a popular option for cloud storage. Azure Bastion provides secure shell access for remote connections. It also features the ability to create virtual desktop infrastructure with ease. That way, remote employees can access central resources without storing data locally.

Microsoft’s cloud platform has other remote security benefits. Learn more by reading our Azure best practices guide.

Amazon Web Services (AWS)

AWS is another good cloud storage option and virtual workspace. For instance, it’s ideal for creatives working remotely who need virtual workstations for graphic design or video production.

Users can encrypt data easily and manage data retention policies. And they can track data movements between home and cloud locations.

Finally, cybersecurity is very tight if you follow AWS security best practices.

Google Cloud

Google Cloud offers excellent document storage and editing features. Flexible bucket storage is a core feature of Google’s platform. When cloud services fail in one region, remote workers can access workloads hosted elsewhere.

Google’s storage systems scale smoothly. They are fitted with critical remote security tools like encryption, cloud-native access controls, signed URLs, and data retention locks. By following Google Cloud security best practices, you can design a remote work solution that secures data and serves employee needs.

Project management

Managing projects is a crucial aspect of any remote workplace. Managers need to set targets and monitor employee progress. They need awareness of project achievements. Finally, they require the ability to change plans as projects develop.
Project management tools make these tasks much more manageable. What’s more, they give an overall awareness to their users. Also, some solutions enable detailed worker surveillance via time-tracking tools.

Jira

Atlassian’s Jira platform is a good solution for creating a flexible remote team. Targeted at code developers, Jira enables complete awareness of production status. Managers can track progress with productivity reports and timeline tools. In the meantime, task management hubs allow them to set flexible workflows for each team member.

Jira is a solid option for DevOps teams that depend on distributed remote workers. That’s because it blends flexibility and security. For instance, users can encrypt data at rest and in transit, and they can set permissions for each object. NordLayer’s guide to Jira security best practices offers a comprehensive overview of the product’s remote security features.

Microsoft Teams

Teams is the most popular platform for remote work operations. However, it doesn’t include native project management features.

Instead, users can create integrations with third-party management tools like Monday or Brightworks. These tools link together the video conferencing and messaging functions that make Teams useful. And they let managers schedule events and track progress easily.

Microsoft Teams is part of Office 365. This suite allows easy assimilation of Excel or Word into remote workflows. But this solution might come with security vulnerabilities. Learn more by reading our blog about Office 365 best practices.

Figma

Product designers rely on Figma to collaborate and develop ideas. The platform’s Juncture tool enables in-depth project management for every team and product. Co-creation spaces bring workers together to share prototypes or test apps. And tools like FigJam provide online whiteboards for real-time collaboration.

Figma is an excellent development platform for remote teams. But as with Microsoft Teams, it’s not entirely secure. Therefore, be sure to implement Figma security best practices before teams go online.

Communication and collaboration tools

Communication and collaboration are critical to the success of every remote team. And for that, there are many different tools to choose from.
communication tools for teams

The most secure options are end-to-end encrypted messaging apps. Troop Messenger and Element are designed to suit business communications. They encrypt messages between remote team members without compromising performance.

Other communication tools bring team members together to discuss ongoing projects. For example, Slack features customizable one-to-one, enterprise-wide, or departmental group chats, including live voice communications. It includes encryption, key management, audit logs, and data loss prevention.

Video collaboration is another must-have for most remote work operations. Zoom is optimized for distributed teams, with collaborative whiteboards, up to 100 meeting attendees, and instant team meetings for spur-of-the-moment contact. Zoom Events is another neat feature that helps build togetherness within a distributed workforce.

Video communication tools improve collaboration, but they can bring remote security risks. During the Covid pandemic, there were many cases of attackers recording Zoom calls. That’s because threat actors can steal credentials or hijack calls over insecure connections.

Companies should couple collaboration tools with a reliable B2B VPN and access management systems. They ensure that calls are private and only legitimate invitees will be present.

Access control and data security tools

Remote work setups should always include filters to exclude unauthorized users from corporate resources. Therefore, authentication and access control solutions are critically important. After all, managers will probably want to give the IT admins more freedom than a trainee.
Authentication

Authentication compares user access credentials to secure credentials databases. The gold standard for remote access is multi-factor authentication (MFA). This demands more than one unique identifier when users access work resources.

MFA can involve passwords and one-time codes sent via SMS or email. But more secure versions deliver encrypted codes to mobile apps. This avoids security issues related to email and SMS. Organizations can also switch from passwords to hardware tokens provided to remote workers.

Access management

Access control portals complement authentication tools. Identity and Access Management (IAM) systems verify users’ identities and connect them to the correct privileges.

Remote workers can access resources needed by their team or project. However, under the Zero Trust model, IAM tools limit access to all other network assets. This strengthens the network perimeter and boosts cybersecurity.

Encryption

Encryption is another critical aspect of secure remote working. Companies should leverage encryption features on apps and cloud platforms to safeguard sensitive information. And they should use encrypted channels to connect remote devices and central resources.

Data Loss Prevention (DLP)

DLP tools can also help businesses a lot with their remote workforce. They track sensitive data and prevent misuse by remote users. This way, managers can protect the most important databases and documents. As a result. extracting valuable data will be much more difficult.

In summary, strong encryption is essential when designing remote work setups. Insecure user devices can become entry points for malware and data thieves. Moreover, weak authentication and authorization systems make access easy for anyone with a functioning user ID and password.

Secure remote access solutions

Remote access workforces expand the threat surface and create new cybersecurity risks. This makes it critical to secure every remote connection. Encrypting cloud platforms and implementing MFA is not enough. Companies must lock down connections between remote devices and network assets.
Virtual Desktop Infrastructure (VDI) is one way to do so. It creates centralized servers on the cloud. These servers host workloads and data, meaning nothing is stored locally on employee devices. However, users can run apps hosted on the VDI in their home office.

VDI tools create encrypted connections between local devices and the virtualized environment. This is relatively secure. Unfortunately, attackers can still gain network access if they have legitimate credentials.

Companies can also use Virtual Private Networks (VPNs) to create encrypted tunnels for remote connections. VPN providers operate servers across the world, which can even improve connection speeds.

They apply cutting-edge encryption that is virtually impossible to crack. Moreover, your IP address will stay hidden, increasing anonymity. This makes it harder for hackers to mount interception and other types of attacks.

VPNs are a flexible security and privacy option for on-site and remote workforces. What’s more, these tools can secure access points in public locations. In the meantime, access company networks or attend client meetings while traveling.

NordLayer’s VPN solutions make creating safe remote work setups easier. Our Remote Access VPN encrypts connections via a simple client interface. Users can protect their devices instantly, whether they are accessing cloud platforms or central offices.

Make remote work secure with NordLayer

Remote work should always be protected. However, companies may struggle to secure data as employees shift away from centralized offices. This blog post has introduced key technologies and tools for keeping remote workers safe and boosting productivity.

Businesses should always choose the most secure project management and communication tools. While Azure or Zoom have their own security features, they alone are not enough. Organizations must be able to create gateways, use MFA authentication, protect remote access, and manage team member privileges.

It’s time to make your remote and on-site work safe. Get in touch with NordLayer, and we’ll help you create a solution that fits your business needs.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Key webinar takeaways: Cybersecurity trends to look out for

Modern security needs are constantly changing, so keeping an eye on emerging trends and evaluating them critically is key. As the attackers are getting better, faster, and stronger by utilizing the emerging technologies, so should the organizations.

Gerald Kasulis, VP of Business & Channel Operations, North America at Nord Security, recently hosted a webinar featuring Matt Lee, Senior Director of Security and Compliance at Pax8, and Frida Kreitzer, IT Consultant at FridaIT. Together they shared insights on the tech trends that are shaping cybersecurity into the near future.

Topics discussed included the shift towards Zero Trust architecture, ransomware’s surging menace, and the growing momentum in passwordless authentication.

Watch the full recording below, or keep reading this blog for some of the key takeaways we took from the webinar.

Cybersecurity landscape

Matt Lee believes that changing market conditions demand a heightened focus on cybersecurity: “what changed drastically is that we actually started feeling the pains of threat actors’ endeavors. But the big shift that I think took place is that people are actually trying to solve the cybersecurity problem at the SMB and mid-market level.”

Frida Kreitzer gave a quick overview of the situation on the ground for IT teams in the current threat landscape, where more than 80% of cyberattacks are made possible by human error. For her, the primary concern is: “How can we be as proactive as possible without “breaking” the company?”

Zero trust, but more security

Never trust, always verify

A Zero Trust architecture assumes that all network traffic is untrustworthy, regardless of origin. It’s become an increasingly significant area of interest for business leaders, as it minimizes risk by dividing your assets into walled-off sections.

“Zero Trust is a world where I know the device’s posture is healthy.” Matt suggests not even allowing network connections to be attempted if certain criteria aren’t reached: “If it’s got the right [security] tools, it’s using a layer for access, and it’s coming from the right IP address, then I’ll let someone try a password. Why would I even [allow an attempt] if they’re not meeting those conditions?”

Perimeter model

Matt draws a comparison between fortified castle walls and the perimeter model which has been “the mainstay of network security for decades. In both scenarios, the fortified area has a single gateway for access. But when cannons are rolled up or spies sneak through the gate, the perimeter can no longer adequately protect its inhabitants.

When new means of attack are developed, defenses must adapt. “Business email compromises and social engineering have grown extremely large,” Matt says, referring to the most common methods used by hackers to gain access. “It’s a different world now, that [requires changing] to a different policing model.”

Verify first, then trust

Matt sees Zero Trust as a shift from the attitude of trust first, then verify.

quote bubble

IoT security risks

Security leaders should consider more than just end users when addressing security concerns, Frida observes. With every additional device on your network, your potential attack surface expands. Internet of Things (IoT) devices can be particularly risky:

Ransomware: Not going anywhere

State of ransomware

Ransomware attacks have been surging in recent years. Matt observes that ransomware groups have become so efficient as to resemble legitimate businesses:

Matt explains that ransomware has become a fully-fledged economy unto itself, with various personas, services, and markets operating within. “I could be a bloke that just breaks into companies – that’s an initial access broker. You’ve heard of SaaS or software as a service. Well, now there’s RaaS – ransomware as a service. I can go to a marketplace and not only find a victim. The marketplace has all the infrastructure, all the capabilities to fully enact a ransomware scheme.” The problem has escalated to the point that law enforcement agencies worldwide and the recent US National Cybersecurity Strategy prioritize the dismantling of ransomware gangs.

Should you pay?

Gerald poses a controversial question on the topic – should you pay the ransom?

For Matt, “It depends. For me, it’s typically a balance of the greater good. And I think that that’s where I would try to make that decision of what’s in the best interests of everyone involved: the company, the customers, the patients. So it’ll come down to the sensitivity of the data, the impact, the gravitas of it. All of those things come into the conversation. Each one is a business by business decision.”

Frida suggests that pay or not, companies won’t be guaranteed safety from other attacks in the future. “They will get blackmailed again and again… Now you’re a target. We know that you’re vulnerable.” Frida says baking security into your software in early development should be a priority, but the real challenge is staying proactive on an ongoing basis.

Avoiding complacency is a big point for Matt as well: “Just like any business risk, you’re going to have to deal with it on a continuous basis. This is a continuous improvement model.”

Security leaders should be particularly vigilant when dealing with external contractors or consultants. Frida outlines the risks: “Someone who doesn’t know policy, someone who doesn’t have a company computer, someone who doesn’t use a password manager. Someone who’s easily susceptible to social engineering.”

Frida warns smaller companies not to assume they’ll fly under the radar:

Promises of passwordless: What’s the benefit?

The future of authentication – passwordless

The humble password, used since the early days of the internet, represents an increasingly outdated means of authentication, compromised with growing ease by social engineering or brute force attacks. As Matt says, “Passwords can be tricked or coerced from you.” The golden term for forward-looking, security-conscious organizations is “passwordless”.

Frida Kreitzer weighs in: “Most simply, [passwordless] means you’re not having to type in a password or use a password manager for authentication. That’s very exciting – you’re skipping that portion and just going straight to MFA (Multi-factor authentication, where multiple criteria have to be reached in order for the user to be authenticated). It’s a key that’s being sent to a device – usually a phone.”

Passkeys – a simpler and safer sign-in

Passkeys, digital credentials generated by a device, are invisible to the user, and represent a big step forward for the passwordless future. By removing the need for passwords and relying on user devices or biometrics for authentication, passwordless essentially circumvents the risk of password-related attacks.

Built on public-key cryptographic algorithms, passkeys are virtually impossible to phish or hack. Matt explains: “A [passkey] is a cryptographic representation of you that’s very hard to beat – it’s really large math.”

Closing comment

Getting your cybersecurity into a resilient posture is no mean feat. Matt points out that helpful frameworks exist that can support getting the ball rolling. “Stop trying to be the smartest guy or gal in the room. CIS (Center for Internet Security) has 153 little “do this” statements… if you do each of those you’ll greatly reduce your risk and reduce overspending because you won’t duplicate efforts. Be pragmatic.”

Important to remember is not to exaggerate or overstate security concerns when communicating with stakeholders. This can cause diminishing returns, according to Frida:

quote bubbleAs technology continues to evolve, so do the threats that emerge alongside it, shaping the cybersecurity landscape and the strategies needed to navigate it. Understanding these ever-changing trends is vital for any business aiming to build robust defense mechanisms. They can embrace security strategies like Zero Trust architectures, prepare for the relentless threat of ransomware, and explore cutting-edge authentication methods, such as passwordless systems. Through these strategic measures, organizations can enhance their digital security, preserving trust and ensuring continuity in an era marked by swift technological changes.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Capitalizing on threats & opportunities – now is the time to venture into cybersecurity

In our rapidly digitizing world, the role of cybersecurity cannot be overstated. The increase in online platforms and the adoption of digital solutions by businesses of all sizes have led to a surge in cyber threats. While the scope of online risks is expanding, the need for cybersecurity grows exponentially.

A challenge for some is a golden opportunity for others. Thus, this growing need for cybersecurity solutions presents a lucrative business prospect for Managed Service Providers (MSPs) and resellers to partner with cybersecurity firms and offer their clients robust protection.

Cybersecurity market: threats and opportunities

Despite the escalating cyber threats, virtual work setup offers immense potential for businesses and enterprises. To better understand the risks and, paradoxically, their advantages, let’s review the current cybersecurity setting.

Luring risk of cyber attacks

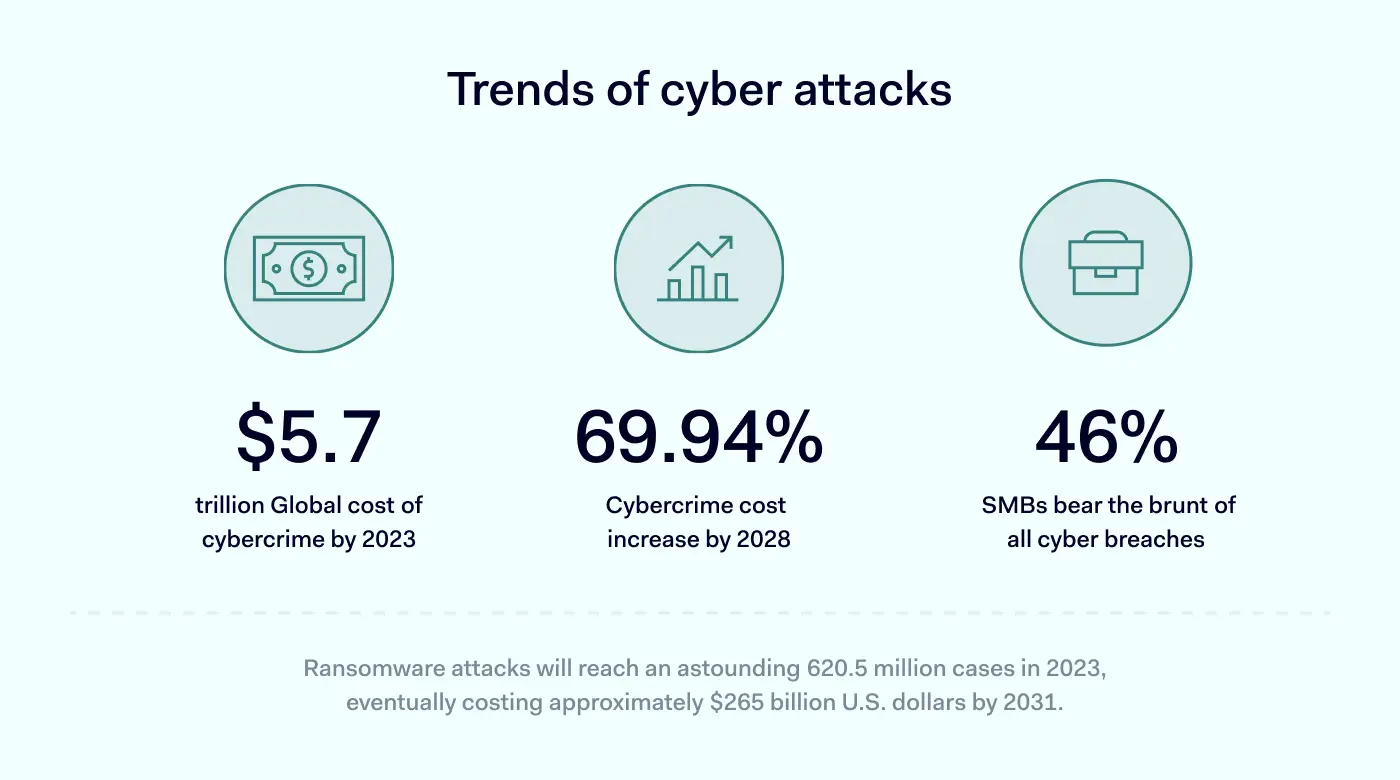
According to Statista, projected from 2023 to 2028, the total global cost of cybercrime is anticipated to surge by 5.7 trillion U.S. dollars, showcasing a notable rise of 69.94%. The latest estimates indicate that by 2028, global expenses related to cybercrime will soar to 13.82 trillion U.S. dollars.

Year after year, data breaches and ransomware attacks have wreaked havoc on the digital landscape. Recent cybersecurity threats research revealed that phishing attacks and malware are top risks businesses of all sizes are exposed to the most. Yet due to the dynamic cyber climate, leading threats constantly evolve, shifting their positions.

For instance, small- and medium-sized businesses (SMBs) are the most vulnerable, as companies with fewer than 1,000 employees bear the brunt of 46% of all cyber breaches. These statistics emphasize that no business is too small to ignore the importance of cybersecurity.

Moreover, analysis shows that ransomware attacks will reach an astounding 620.5 million cases in 2023, eventually costing approximately $265 billion U.S. dollars by 2031. Although it’s only a glimpse into the future digital ecosystem perceptions, the need for fortified cybersecurity solutions is more pressing than ever.

Possibilities dictated by the digital landscape

The silver lining in this situation lies in a boom in the cybersecurity market. This creates an opportune moment for MSPs and resellers to venture into cybersecurity. The global cybersecurity market size is predicted to grow exponentially in the coming years, and those prepared to seize the opportunity now stand to gain immensely.

This opportunity emerges as a prediction for MSP industry revenue to reach €21.18bn in 2023. The anticipated annual growth rate (CAGR 2023-2028) is 2.84%, culminating in a market volume of €24.36bn by 2028.

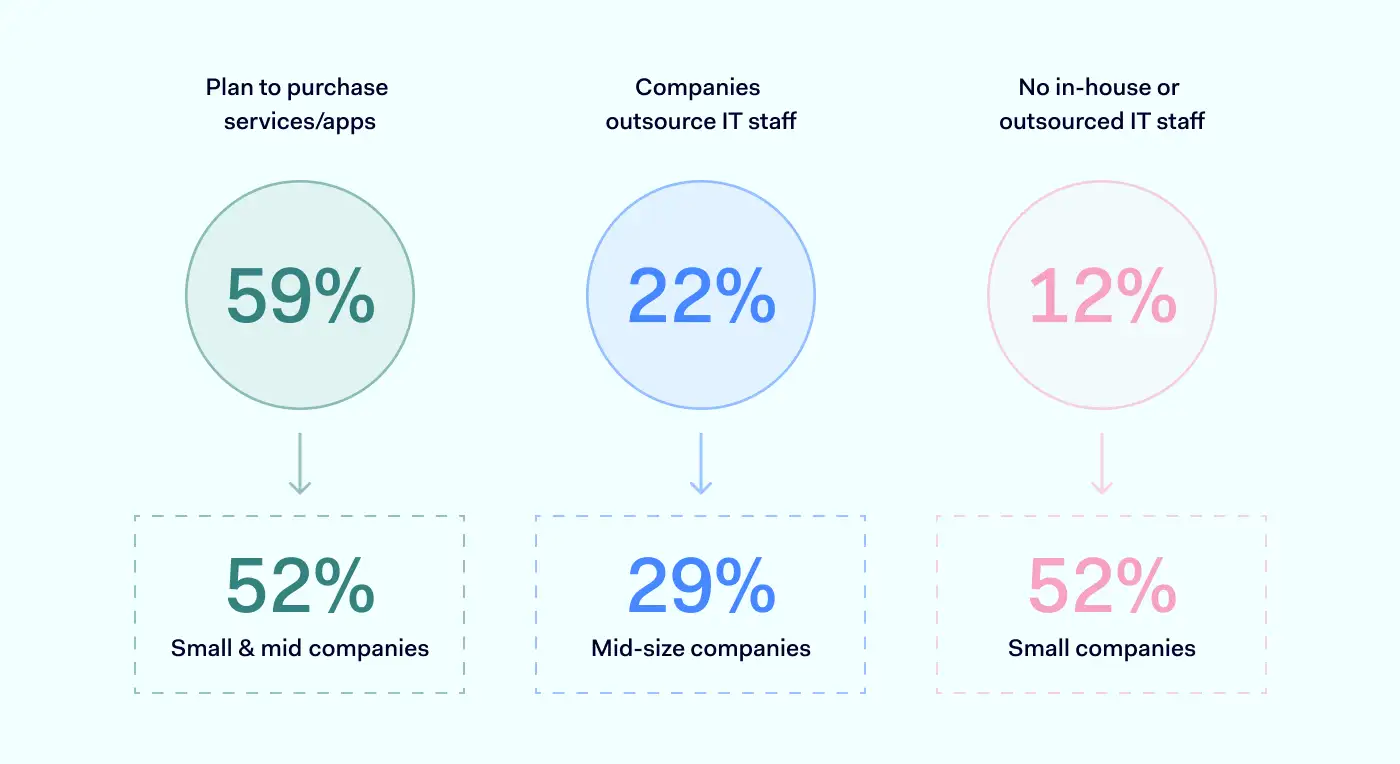
According to cybersecurity investments research, 59% of companies plan to purchase cybersecurity solutions, services, or applications. 52% of those who plan to invest in cybersecurity solutions and services are small– and medium–sized enterprises.Companies 1400x764

In addition, research gives an overview of major markets like the U.S., Canada, and the United Kingdom, revealing that approximately 22% of enterprises outsource their cybersecurity expertise. On average, almost 12% of companies don’t have in-house or outsourced cybersecurity professionals.

Regarding company size, a majority (52%) of small businesses don’t have and don’t outsource skilled cybersecurity staff, while 29% of medium-sized companies tend to outsource these functions.

Challenges faced by most MSPs & resellers

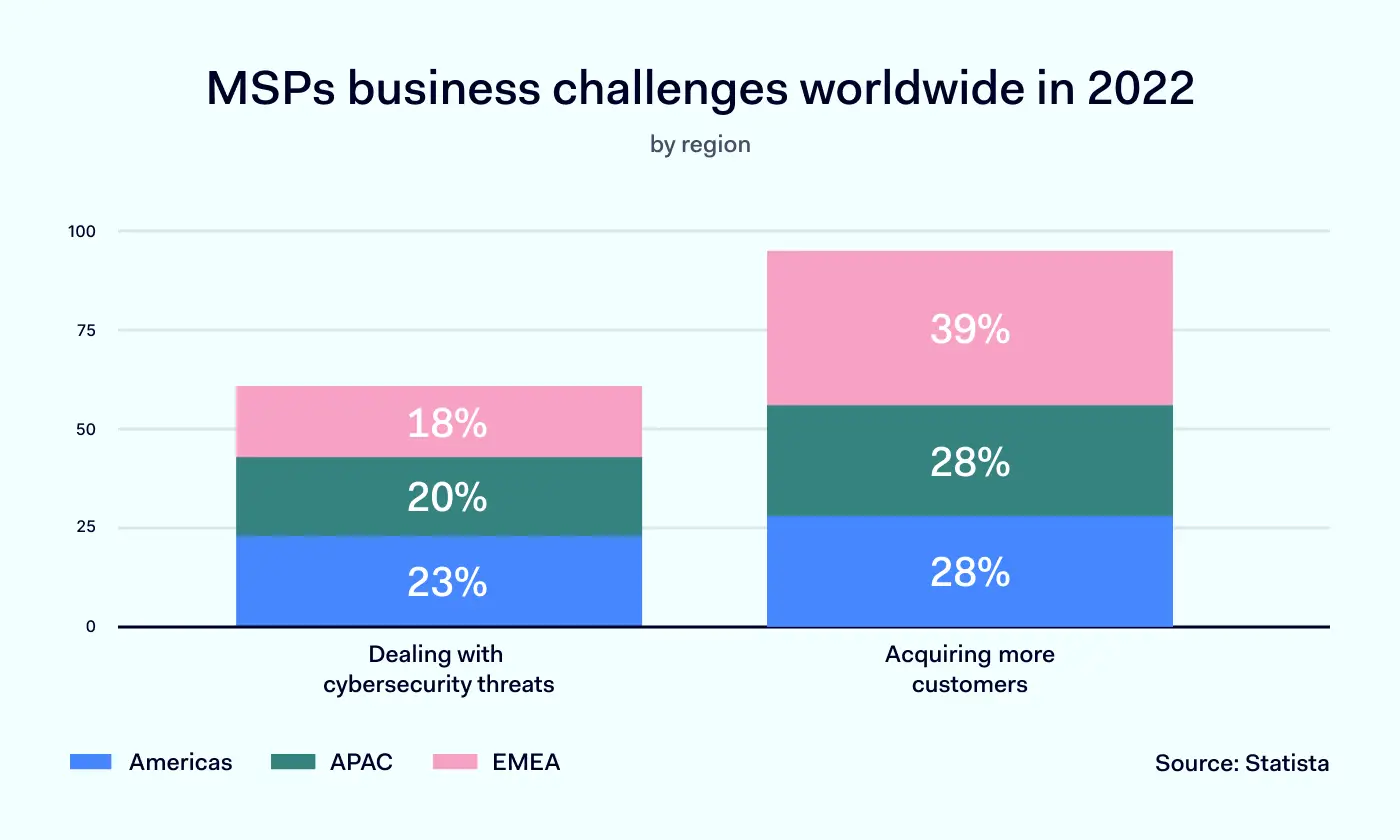
Like every sector has its own challenges, managed service providers and resellers encounter various obstacles in outsourcing business. According to Statista, in 2022, the most prominent impediments were coping with advanced and sophisticated security threats and acquiring more customers.

MSPs business challenges worldwide in 2022 1400x840

In 2022, 30–40% of respondents in EMEA (Europe and Middle East Africa), Americas, and APAC (Asia-Pacific) regions saw gaining new customers as a challenge. By 2023, 29% of service providers still cited the acquisition of new clients as their biggest challenge, followed by revenue growth and profitability.

Besides the struggle to find more clients, handling cybersecurity threats is an issue for a significant number (approximately 20%) of MSP and reseller companies in 2022. Service providers are directly exposed to digital threats like their customers and any other modern company.

NordLayer: your trusted cybersecurity partner

Navigating the cybersecurity landscape might seem daunting for many MSPs and resellers. That’s where NordLayer comes into play.

NordLayer offers a comprehensive partner program to help you tap into this booming cybersecurity market, enhancing your business performance and increasing your profits.

Boost your business performance

With NordLayer, your business can gain a competitive edge through an accessible software-defined solution. Our remote security solution ensures your clients stay safe online, allowing you to stay ahead of the game.

Grow your profits

NordLayer’s easy-to-adapt software eliminates the need for expensive hardware, saving your clients significant costs. By opting for a subscription-based SaaS model, you can enjoy a steady stream of recurring revenue, greatly amplifying your financial gains.

No tech expertise is needed

NordLayer simplifies the process of selling cybersecurity solutions. This means you don’t need a deep understanding of tech and network knowledge or invest in human resources education or competencies to start selling.

24/7 support

We believe that partnership goes beyond selling solutions. With NordLayer, you gain access to a committed, caring, and proficient technical support team available round the clock, helping you identify and close deals and propelling you toward success.

Efficiency is our priority

At NordLayer, we prioritize efficiency. With our solutions, you can onboard clients in under 10 minutes and scale rapidly. No minimum order requirement makes NordLayer ideal for SMBs. Network deployment and administration are simplified, without the need for complex hardware or tedious configurations, saving time and resources while boosting productivity.

Afterword

The time is ripe for MSPs and resellers to seize the opportunities in the cybersecurity market. With NordLayer as your partner, you will be well-equipped to navigate this booming sector and take your business to new heights. The cyber threats are real, but so are the opportunities. Now is the perfect time to start selling cybersecurity solutions.

Future partner, become an enabler securing all ways of working by joining forces with NordLayer.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.