

Skip to content

Industroyer: A cyber‑weapon that brought down a power grid

Five years ago, ESET researchers released their analysis of the first ever malware that was designed specifically to attack power grids

On June 12th 2017, ESET researchers published their findings about unique malware that was capable of causing a widespread blackout. Industroyer, as they named it, was the first known piece of malware that was developed specifically to target a power grid.

Indeed, Industroyer had been deployed to considerable effect a few months earlier – it caused thousands of homes in parts of Kyiv, Ukraine to lose power supplies for about an hour on December 17th, 2016, after the malware struck a local electrical substation. A few days later, ESET malware researcher Anton Cherepanov would start dissecting Industroyer.

A ticking bomb

Once planted, Industroyer spread throughout the substation’s network looking for specific industrial control devices whose communication protocols it could speak. Then, like a time bomb going off, it apparently opened every circuit breaker at once, while defying any attempts of the substation operators to regain easy control: if an operator tried to close a breaker, the malware opened it back up.

To clean up its footprint, the malware unleashed a data wiper that was designed to leave the substation’s computers inoperable and delayed the return to normal operations. Indeed, the wiper often failed, but had it been more successful, the consequences could have been much worse – especially in wintertime when a power outage can allow pipes filled with water to crack when they freeze.

A final malicious act was made by the malware to disable some of the protective relays at the substation, but that failed too. Without functioning protective relays in place, the substation equipment could have been at high risk of damage when the operators eventually reestablished electric transmission.
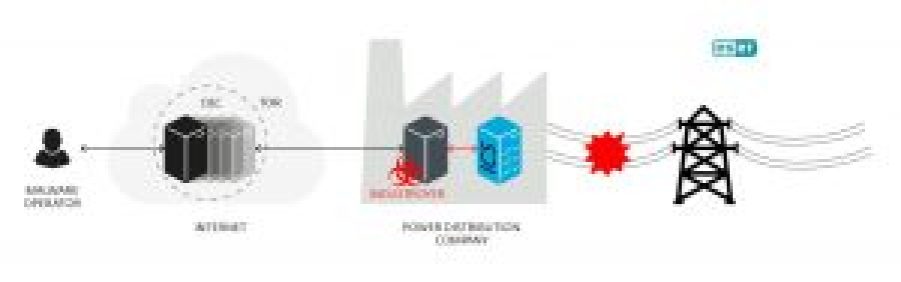
As Cherepanov and fellow ESET researcher Robert Lipovsky said at the time, the sophistication of Industroyer makes it possible to adapt the malware to any similar environment. In fact, the industrial communication protocols that Industroyer speaks are used not only in Kyiv, but also “worldwide in power supply infrastructure, transportation control systems, and other critical infrastructure systems (such as water and gas)”.

On the other hand, considering how sophisticated Industroyer was, its impact was ultimately rather underwhelming, as ESET researchers noted themselves back in 2017. Perhaps it was only a test for future attacks, or perhaps it was a sign of what the group behind it could do.

The work of Sandworm

The shenanigans of the malware, ESET researchers noted, mirror the malicious intentions of the people who created it. At a Virus Bulletin conference in 2017, Lipovsky highlighted that the “attackers had to understand the architecture of a power grid, what commands to send, and how that will be achieved”. Its creators went a long way to create this malware, and their objective was not just a power outage. “Some clues in the Industroyer configuration suggest they wanted to cause equipment damage and malfunction”.

At Black Hat 2017, Cherepanov also pointed out that it “seems very unlikely anyone could write and test such malware without access to the specialized equipment used in the specific, targeted industrial environment”.

In October 2020, the United States attributed the attack to six officers belonging to Unit 74455, aka Sandworm, a unit within Russia’s military intelligence agency GRU.

A comeback for Industroyer

Fast forward to 2022 and it’s no surprise that in the weeks just before and after Russia’s invasion on February 24th, ESET telemetry showed an increase in cyberattacks targeting Ukraine.

On April 12th, together with CERT-UA, ESET researchers announced they had identified a new variant of Industroyer that targeted an energy supplier in Ukraine. Industroyer2 had been scheduled to cut power for a region in Ukraine on April 8th; fortunately, the attack was thwarted before it could wreak further havoc on the war-torn country. ESET researchers assessed with high confidence that Sandworm was again responsible for this new attack.

A harbinger of things to come

In recent years, it’s become more than clear that the world’s critical infrastructure services are at major risk for disruptions. The string of incidents that have impacted critical infrastructure in Ukraine (and, indeed, other parts of the world) have awakened much of the public to the risks of cyberattack-induced power outages, water supply interruptions, fuel distribution disruptions, loss of medical data and many other consequences that can do far more than just disrupt our daily routines – they can be truly life-threatening.

Back in 2017, both Cherepanov and Lipovsky concluded their research blog with a warning that, five years later, still holds true: “Regardless of whether or not the recent attack on the Ukrainian power grid was a test, it should serve as a wake-up call for those responsible for security of critical systems around the world”.

Author: André Lameiras

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

10 reasons to change your monitoring software

Every change is for the better and we give you ten reasons to change your monitoring software.

Cuando se habla de cambiar de software, no sé por qué, me viene a la mente la compra de música. Bueno, yo soy de los de antes: vinilos, cassettes, a principios de siglo los CD y DVD… Claro, ahora es diferente, actualmente existe el pago por suscripción, que reproduce en línea, y donde generalmente se ofrece el álbum de turno o paquetes completos con muchas estrellas musicales…

We could start right there, highlighting the difference between “the cloud and the earth”, running software on the Internet versus having one on your own physical servers. Both have their costs, we know. In fact, we already gave detailed information in another article on the subject. Because before talking about changing your monitoring software we must start there, the money. That’s the reason why you will have to take into account several factors, so let’s go for pencil and paper (virtual) and let’s start numbering!

1) Pandora FMS offers several forms of installation and download, as well as modes of operation. That is one reason to consider switching monitoring software. This mechanism allows you to grow, and, if necessary, reinstall at any time. You don’t have to buy a whole package either: in Pandora FMS you start by installing the Community version and as you see the benefits for yourself, you can move on to installing and testing the Enterprise version, without obligations or hassle. There you will always have the installers, both online and offline, as many times as you need them.

2) Do you have a feature in mind that cannot be found in any monitoring software? Don’t be embarrassed, it happens. I, at the very least, am very picky about how to insert text and data into text or number boxes. When you focus on them, I like for the text to be selected in a specific color, for example. And don’t even let me begin on entering numerical amounts or phone numbers.

And Pandora FMS does not have exactly that requirement either… However, you just have to go through the Community version that is open source and through its forum to get the help you need to develop the idea.

Better yet, you may have already been successful but now you want a more ambitious and highly customized improvement for your company: try the Enterprise version, where they will give you professional advice and offer you extraordinary improvement plans tailored to your needs. After all, only you know what is best for your company and what it needs. An exactly tailored suit or smehting ready-to-wear ? You choose!

3) With Pandora FMS you will be able to monitor at first remotely, without interfering much in your work processes, continue with an advanced remote configuration and, if everything goes smoothly, advance to monitoring with Software Agents, which are installed on each device. While you change -and advance- Pandora FMS has already outlined the path until (for now) June 2023. Exploring and changing monitoring software can be done before it’s necessary, even if it’s late.

4) Using great monitoring software, widely used worldwide and also used by large corporations, is not a guarantee of good security. I invite you to read about the case that took many headlines in the press, social networks, radio and television. Take this chance to have a coffee and take a deep breath to come back, there are still six reasons to change your monitoring software.

5) Because you don’t believe in magic wands. Neither do I, and in Pandora FMS that is very clear for them. Each client has a different problem and it is necessary to adapt to each particular case. But it will not be by magic, you have to invest time and effort, and in that domain Pandora FMS offers decades of proven experience.

6) Because “we just know that we do not know anything”. Without the aim to go in depth into the philosophical field, we must always pay attention to constant learning. Perhaps the documentation of your software is quite poor and it would be a good time to change it. Pandora FMS has forums of users of the Community version, documentation, tutorials and this blog that you are reading today. With all of them you can learn at your own pace, but if you want or rather need a push – certification included – check out our training in monitoring. Psst, with the Enterprise license this last one is included, don’t miss the chance!

7) Another reason to change your monitoring software is indeed not to change anything! Perhaps you simply need a monitoring contingency plan or an alternative of audit or measurement of result comparison. For example, I am a client of DigitalOcean, a company that provides virtual computers and that has both monitoring processes (Software Agent type) in each droplet (virtual machine), as well as at large-scale with Prometheus in its hypervisors. However, remote checks and Pandora FMS Software Agents are more useful for me, which also helps me verify information. It is not that I don’t trust the monitoring software implemented by my own provider, but rather you must always have different options, see the full horizon to be able to choose the way forward.

8) Because two are better than one: eHorus is a remote access program that can later be integrated with Pandora FMS. EHorus remote access software can be integrated into Pandora FMS, so you may combine computer – or client – monitoring, find out the bandwidth consumption of your network, the software installed on your PC, see logs and events and connect to the computers you need from the monitoring console itself. Test without commitment nor cost for up to 10 devices.

9) Because three is better than one. We add another reason to change your monitoring software, Integria IMS. Fully compatible and integrated with Pandora FMS. Integria IMS incorporates your forms for clients in your own Web, feeding Integria IMS directly through API. In addition you will have access to lots of articles, downloadable files, multi language, categorized and with access control to manage incidences. Monitor changes and performances on your machines with Pandora FMS agents!

10) Is the “billiard ball” with the number ten missing? You yourself can add the tenth reason to change your monitoring software. Tell us about your experience with other software, you can leave your comments below, visit our channel at YouTube, Linkedin or Twitter.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About PandoraFMS
Pandora FMS is a flexible monitoring system, capable of monitoring devices, infrastructures, applications, services and business processes.
Of course, one of the things that Pandora FMS can control is the hard disks of your computers.

ESET joins ranks as a CVE Numbering Authority (CNAs)

BRATISLAVA – June 24, 2021 – Working in concert with Common Vulnerabilities and Exposures (CVE®) Program, ESET, the leading Europe-based endpoint protection platform vendor, is authorized by the CVE Program as a CVE Numbering Authority (CNA).

Organizations designated as CNAs are responsible for the assignment of CVE IDs to vulnerabilities, and for creating and publishing information about the vulnerability in the associated CVE record.

The status means that ESET will be able to publish CVE records, including the CVE ID, descriptor, and references concerning vulnerabilities discovered in its own products and those discovered by ESET researchers in third-party products not covered by other CNAs. As a CNA, ESET can better fulfill its leadership role in innovating security technologies and product R&D and promoting high security standards in the broader IT ecosystem.

“Engaging in the international, community-driven Common Vulnerabilities and Exposures (CVE®) Program brings us closer to our goal of supporting ongoing collaboration with the wider cyber security sector, as well as academic, business, and government stakeholders. Simultaneously, it allows our internal security and R&D teams to more efficiently and consistently address security weaknesses wherever they may be, and to remain proactive in fighting vulnerabilities and threats,” says Daniel Chromek, chief information security officer at ESET.

ESET is a strong believer in, as well as a practitioner of, the coordinated vulnerability disclosure process and publicly credits security vulnerability reporters for their efforts (if they do not wish to remain anonymous). If you have interest in hunting for vulnerabilities, or other security issues, in ESET products or websites, read more about our partnership with HackTrophy, or find out more here.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

訊連科技人臉辨識獲微程式資訊採用 打造石化業跨廠區多因子智慧辨識解決方案

【2021年6月15日,台北訊】全球頂尖AI臉部辨識領導廠商訊連科技(5203.TW) 與微程式資訊合作之多因子智慧辨識立柱及智慧門禁管理平台中,導入訊連科技開發之FaceMe® AI人臉辨識引擎。該項解決方案日前獲國內知名石化業者採用,透過人臉辨識技術,打造物聯網智慧門禁管理平台。

微程式資訊為國內知名之產業IoT物聯網科技服務整合商,累積了二十年以上的研發經驗,是台灣少數具有跨產業技術整合能力的科技服務商,解決方案遍及交通、金融、零售、製造、自行車等產業。「石化業跨廠區多因子智慧辨識服務」是微程式針對台灣知名的石化業者提供的解決方案。該服務結合指靜脈辨識、人臉辨識、車牌辨識、eTag辨識等功能,致力於提升人員進出廠的安全性、簡化訪客登記流程,並善用大數據分析,建立便於管理的智慧門禁管理平台。

於本方案中,微程式採用了訊連科技開發的FaceMe® AI人臉辨識引擎技術,整合至多因子智慧辨識立柱 (MP1902)中,於廠區主要出入口進行人員控管及訪客登記等應用。此外,亦透過微程式開發之智慧門禁管理平台,進行人員、承攬商、訪客等資料管理,及廠區工安數據的統計,為石化業者打造整合物聯網技術之數位化、智慧化平台,亦有效減少人力作業之負擔及成本。

「於工廠、倉儲、展覽館、購物中心等大型場域,人員及車輛的進出往往需要仰賴大量的人力進行管制。透過人臉辨識等先進AI影像辨識技術,可大幅提升此類作業之效率。」微程式資訊吳騰彥總經理表示:「訊連科技為台灣AI人臉辨識的指標性廠商,提供準確、可靠的AI人臉辨識解決方案。透過與訊連的合作,可為微程式的客戶打造準確、可靠的多因子智慧辨識解決方案。目前訊連也提供車輛辨識核心予微程式,並實際導入收費停車場,與多因子智慧辨識立柱的整合將更具市場競爭力。」

「近年來,台灣有越來越多大型場域,陸續導入人臉辨識技術進行門禁、工安、承攬商之管理。」訊連科技執行長黃肇雄表示:「訊連很榮幸能與微程式合作,為石化業者打造人臉辨識的先進影像辨識系統之開發,提供廠區零接觸的智慧管理服務。」

FaceMe® SDK為專為邊緣運算(Edge Computing)及伺服器等環境打造的AI人臉辨識引擎,於全球知名之NIST(美國國家標準暨技術研究院,National Institute of Standards and Technology)之FRVT(臉部辨識技術基準測試,Facial Recognition Vendor Test)中,於指標性的VISA Border 1:N(邊境照人臉搜尋比對)及Wild Photo 1:1(實境照人臉比對)中,皆排名全球前六強,並是該兩項測試中,排除中、俄廠商後全球排名第一之人臉辨識開發團隊。

FaceMe®可建置在搭載高階處理器及圖像加速卡的伺服器和工作站、或是搭配輕量化處理器的IoT邊緣運算裝置,皆可針對不同的硬體配置進行優化,並可支援Windows、Linux(Ubuntu、RedHat、Yocto等)、Android及iOS等多種作業系統,可協助智慧城市、智慧建築、智慧安控、智慧零售和智慧家庭等多種應用情境及IoT軟、硬體中,導入快速、彈性且精準的人臉辨識。

About Version 2

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products. Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

關於CyberLink
訊連科技創立於1996年,擁有頂尖視訊與音訊技術的影音軟體公司,專精於數位影音軟體及多媒體串流應用解決方案產品研發,並以「抓準技術板塊,擴大全球行銷布局」的策略,深根台灣、佈局全球,展現亮麗的成績。訊連科技以先進的技術提供完美的高解析影音播放效果、以尖端的科技提供完整的高解析度擷取、編輯、製片及燒錄功能且完整支援各種高解析度影片及音訊格式。產品包括:「威力導演」、「PowerDVD」、「威力製片」、「威力酷燒」等。
