Skip to content

Meet the Team: coffee break with the Managing Director at NordLayer

We had the opportunity to sit down with Donatas Tamelis, the Managing Director at NordLayer, the driving force behind the company’s strategy and vision. He mapped out what sets NordLayer apart in the competitive cybersecurity landscape and how the team plays a crucial role in bringing the company to the top.

Donatas, how many cups of coffee have you already had today?

Only five, and it’s not even the end of the day 🙂

You must be fueled with energy all the time! But, on a more serious note, could you share with us what it takes to be a part of one of the most promising cybersecurity companies in the country and navigate it through the industry challenges?

Well, it happens that I work with companies in their early stages, so NordLayer is no exception. Most early-stage companies share the same denominator – they start from something very small.

I joined the company about four years ago, and even back then, what set it apart was the well-developed product and market positioning. It helped eliminate the unknown factor if the product has any potential and gave the freedom to start strong.

Being there from the beginning has its own magic. Establishing strong foundations and building high-performing teams are key moments for a successful start and ongoing achievements. It’s no secret that jumpstarting a business that develops superior products is an exciting journey for a Managing Director and, I presume, for everyone else involved.

As a leader, how important is the team to you? What are you looking for when you are forming your squad?

I’m happy that now at NordLayer, we have a full leadership team and key people who run the processes and take care of our organization units. Personally, I invest a lot of thought into the hiring process. I carefully interview and select individuals to see if they fit the picture I have for the successful organization direction.

For me, as a manager, the previous experience or future focus fade away compared to what personality traits and attitude the prospect has. It has little to no importance if someone has graduated from Harvard five times. What matters most is our ability to work together and good chemistry.

In a leadership role, it is important to have resilience to stress. Running a business can sometimes lead to very uncertain situations when you don’t know how it’s supposed to be and don’t have an instant solution. And panicking isn’t the way to proceed. So people who manage should listen to others, observe, weather the storm and return to the problem the next day to make informed decisions. When the stakes get high, I choose to work with the team members who exhibit those qualities.

What is your strategy-building process?

My approach is always to have a bottom-up perspective. If you take a helicopter view of the problem, you get a scattered and disjointed overview of priorities. To avoid wasting time, energy and resources, I crystalize the main problems that are really important at the time instead of focusing on a million irrelevant issues that can be addressed later.

I believe that for a leader, it’s important to be present and get their hands deep into the problem. This level of involvement helps clearly understand the situation and manage the expectations for possible outcomes, scope, and the team’s role in it.

Could you name a few top highlights and achievements of NordLayer?

As an organization, we achieve quite a lot in those four years. One of the highlights was creating a fundamental leadership team as the base for organizational growth and progress. From a company evolution perspective, it puts NordLayer in a very good place. The help of balanced leadership enables me to have better insights into the life of every company unit and gauge the team dynamics.

Another achievement is a well-defined product roadmap. We have identified the crucial components, how we validate them, and how we treat external information. Our product management team has introduced a methodical approach to product development strategy.

Knowing that our product solves real customer problems is a huge achievement for our company and all contributors. Through various metrics, such as retention and growth, we can see that there is a  demand for the product we create.

What is your idea of standing out as a product in a saturated cybersecurity market?

Mobility, flexibility, and security are the features that lead to current business needs. NordLayer sets itself apart from other cybersecurity solutions by enabling all ways of working in a digital world.

We aim to help businesses make this shift in the most accessible and organization-friendly way, catering to companies of all sizes and structures. With our flexible and easy-to-implement cybersecurity solutions, NordLayer ensures enhanced protection against cyber attacks, surpassing the capabilities of traditional VPNs.

Our driving force is to make complex things easy, so users can enjoy the benefits of the solved problem rather than struggling with it. NordLayer focuses on three key pillars – internet access security, network and resources access management and achieving compliance. This comprehensive approach ensures business network and device security against cyber attacks and potential risks.

I’ve recently had a nice and in-depth discussion with Security Detectives about NordLayer’s focus and unique offering. I’d really like to encourage you to check it out to gain further insights.

Could you reveal what to expect from NordLayer in the near future?

We recently released the NordLayer Browser Extension, an alternative agent to our application that our team worked tirelessly on. We are happy about the successful launch because the extension provides security on a browser level for users who need a lighter option to use NordLayer in various work scenarios.

Firewall as a Service (FWaaS) is the next thing brewing this year. It’s the most significant project in the product’s history to this date in terms of its complexity, resources and competencies. All our focus and development efforts are concentrated on finalizing and launching another element of the Security Service Edge (SSE) framework.

FWaaS will bring NordLayer to a more unified SSE provider, as we already offer Zero Trust Network Access (ZTNA) and Secure Web Gateway (SWG) functionalities. We constantly improve our product, its solutions, and user experience for our customers and partners. It allows us to maintain a clear direction in the ever-evolving cybersecurity landscape.

What would be your tips and recommendations for envisioning and building a business cybersecurity strategy?

When building a strategy, whether cybersecurity or business development, the most essential element is the team. It’s the foundation for a good starting point.

Then it’s crucial to assess the priorities for securing your business. If it’s unclear where to begin, a helpful practice is to break down the OSI levels and audit your organization’s security practices against them. This will give you a better understanding of what to improve and work on first.

Naturally, everything starts from an idea, but taking a constructive approach to a problem helps achieve the best results with minimum resource waste. Balance the team and start with a plan. We at NordLayer know how difficult it may be to grasp the complexity of effective cybersecurity, so we introduced the Decision Maker’s Kit, a guide that leads you through all the stages of creating a cybersecurity strategy.

Thank you.


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

NordLayer use case: internet access security

Modern businesses heavily rely on internet access for communication and collaboration. This also makes it the #1 channel for cybercriminals trying to access sensitive data. This modern threat landscape is a critical cybersecurity challenge that businesses must be aware of and be prepared to defend against.

Therefore, in this blog post, we’ll discuss the importance of internet access security for businesses operating in all work models, including remote, office, and hybrid. With the number of cyberattacks ramping up, it’s crucial not to hope for the best and believe it will never happen to your company.

What internet access security challenges affect businesses?

Businesses hold and manage large amounts of sensitive data, including customer information, financial data, and trade secrets. If this information isn’t properly secured, unauthorized users can obtain access to it, causing a data breach.

Now, these challenges are even harder to avoid because after the pandemic many businesses have adopted different work models. As a result, secure internet access can mean completely different approaches and unique sets of challenges.

Remote work challenges

During the COVID-19 pandemic, remote work has been the norm for many companies. Even after the quarantines had ended, many businesses kept working from home. While remote work brings benefits and flexibility, it also comes with challenges.

Use of personal devices

The practice of employees bringing their own device for work-related tasks, known as (BYOD), became widespread during the pandemic. Employees hired remotely usually had no personal contact with IT administration, so they worked with their home devices.

The risk lies in the fact that they’re unmanaged and may lack the same level of security as company-issued devices. These circumstances leave them vulnerable to all kinds of attacks, with limited capabilities for IT administrators to stop them.

Unsecure networks

Home networks may not have the same level of security as properly managed corporate networks. Employees using outdated or vulnerable network devices are more susceptible to exploits that hackers could use to gain entry into company systems.

Remote employees are solely responsible for securing their own devices, but they may not always have the necessary knowledge to do it effectively. This also allows hackers to initiate phishing messages or cause disruptions.

Access control

When allowing employees to work remotely, a security policy should clearly state how and who can access sensitive data. Without such a policy, organizations may fall into the trap of being unable to verify who is accessing their networks or data. This is a sure route to costly data breaches and reputational damage.

In addition, compliance regulations like GDPR and HIPAA require organizations to have robust access control policies to protect sensitive data. Failure to do so may result in legal liabilities and hurt business financially.

Office work challenges

While working in the office seems more secure than remote work in most managers’ eyes, it’s not immune to various security threats. In fact, several cybersecurity risks may be more prevalent for employees working in an office than in other models.

Social engineering

Social engineering attacks target the human aspect of security, making them harder to detect and prevent. Very little stands in a dedicated hacker’s way if they plan out a fake identity, impersonating legitimate employees, and using other psychological tactics. For example, tailgating is based on following a genuine employee through the door without authorization.

Employees in an office environment have physical access to sensitive documents and data. This can mean that once a hacker is inside the building, all the sensitive data can be compromised (or stolen).

Insider threats

While network segmentation helps to introduce boundaries that prevent users’ lateral movement in the network, all these boundaries are much more fluid in an office setting. Employees may write their passwords on sticky notes and leave them on their desks, which is something that malicious colleagues could exploit.

In-office identity thefts and malicious leaks may be harder to stop or detect. Additionally, deliberate leaks or theft of physical documents and devices by someone working on-premises are scenarios that an IT manager should prepare for.

Hybrid work challenges

Hybrid work, which combines remote and office models, adds up challenges from both approaches. Employees must be provided with secure methods to connect to hosted resources when working remotely. Meanwhile, when they’re back in the office, they need to be vigilant about risks they could be lurking in shared spaces. This makes the hybrid model the most difficult to secure.

Double the maintenance

Hybrid work puts a huge strain on IT administrators. They must simultaneously support and manage two fronts: office employees must be provided with secure network access when working on-premises and remote employees must be provided with secure routes into their network.

Both modes must be compatible, operate without interruptions, and be secure. It’s an intricate system with many moving parts, so naturally, it’s much harder to supervise.

Increased physical security risks

Hybrid employees carry work devices back and forth between the office and their homes, increasing the risk of theft or loss. A lost device may not be a serious risk if properly secured with strong passwords or encryption. However, if not, it could easily lead to a data breach.

Additionally, working in public areas or during transit increases the potential for shoulder surfing attacks, when an attacker can physically view the device screen. As the attacker needs to be physically close to their victim, this has become quite prevalent with the growing popularity of hybrid work models.

Why is internet access security important for businesses?

Modern-day enterprises heavily rely on the internet to enable all kinds of their operations. As a result, its secure access is important, regardless of the connection method an organization uses. Achieving secure internet access also enables businesses:

  • Protecting sensitive information. Unsecured communication channels may lead to the loss of sensitive information, which could be disastrous for a company’s reputation and cause legal complications.

  • Mitigating cyber threats. Mostly, the internet is a publicly used platform, and it exposes businesses to various risks like malware, phishing, and hacking attempts.

  • Complying with regulations. Many industries are subject to regulations requiring them to maintain strict security measures. Failure to comply can result in heavy fines or legal repercussions.

  • Ensuring business operations continuity. Cyberattacks have the potential to disrupt day-to-day business operations, leading to downtime and lost revenue.

By tackling internet access security challenges, businesses can avoid risks and establish a proper foundation for uninterrupted growth and operational continuity.

How do businesses secure their internet access against various threats?

Securing work environments against threats can vary depending on the business size and risks faced by businesses. Some companies have the manpower and resources to build their own in-house solutions. Others take the simplest approach and turn to a third-party provider adopting their already established tools. Here are two real-life examples.

Whatagraph

A digital marketing reporting platform, Whatagraph transitioned to a hybrid work model when faced with the challenge of local talent shortage. This also meant that they needed to figure out how to allow their remote hires to connect securely to their infrastructure. A comprehensive cybersecurity solution establishing a private gateway to the company’s data and applications was an obvious choice. As Whatagraph is a rapidly scaling company, the solution must also integrate admin features and provide uncomplicated scaling.

To address their needs, Whatagraph turned to NordLayer, using it mainly as a business VPN back when it was still called NordVPN Teams. They leveraged NordLayer’s Virtual Private Gateways with dedicated IP addresses to securely connect to their company network, sealing the sensitive data in an encrypted tunnel.

What also helped was that NordLayer seamlessly integrated with their existing solutions, eliminating the need for additional technical integration. This provided Whatagraph with optimal internet access security within minutes.

Atlantis Games

A mobile game development company, Atlantis Games, found themselves trapped in a corner when manual user handling ways weren’t keeping up with their growth. Initially, their setup was manually allowlisting individual users’ IP addresses, which worked for a small team. However, once a business expanded and developers and customer support specialists needed multiple IP addresses, the manual approach proved to be too much of a task.

NordLayer came to the rescue by providing a smoothly running client with uninterrupted connections. By using Virtual Private Gateways with IP allowlisting for organization members, Atlantis Gamest eliminated the need for manual maintenance or in-house hardware purchases. Plus, they were able to segment teams by projects and allowlist their IP addresses accordingly. The setup mitigated the data breach risk and introduced more granular data access controls.

As the tool seamlessly integrated with their existing company cloud systems, the transition was smooth and freed them from tedious manual management. This resulted in a more efficient and secure connectivity model with additional NordLayer features.

Actionable tips and best practices

Businesses must handle the data that they hold responsibly, not only to fulfill their promise to their clients, but also to meet requirements from the government bodies. By following best industry tips and practices, organizations can help prevent cybersecurity incidents and mitigate the risk of lawsuits and financial penalties.

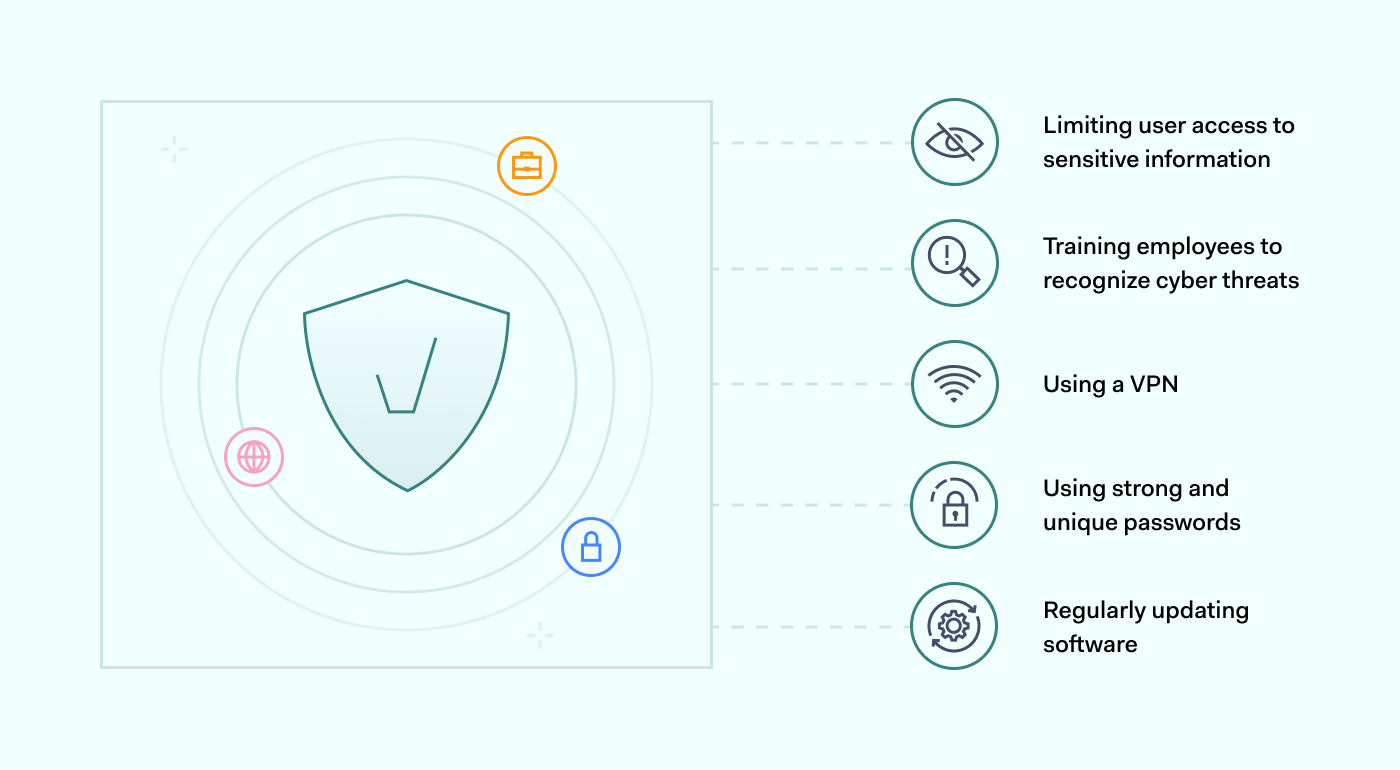
Organizations can take several steps to improve internet access security in all working environments. These include: 
  • Using strong and unique passwords. Online account protection largely rests on the strength of your users’ passwords. Reusing passwords makes it easier for hackers to gain entry into multiple accounts with the same set of credentials. Therefore, requiring a strong and unique password is a simple yet effective way to secure against the simplest threats.

  • Regularly updating software. Periodically updating software is crucial to maintaining a secure system and protecting against cyber threats. As vulnerabilities are discovered daily, using outdated software makes it easier for hackers to exploit known flaws. The only way to avoid those exploits is to patch vulnerabilities to reduce your system’s susceptibility to attacks.

  • Using a VPN. When a user connects to a VPN, its internet traffic is encrypted, protecting all exchanged information under a seal. VPNs also mask your real IP address, making it more difficult for websites and services to track your online activity or location. This alone can make remote working risks less severe.

  • Limiting user access to sensitive information. Enforcing a need-to-know basis for accessing all data. By restricting access to only those who require it, you can reduce the risk of unauthorized access or exposure to confidential information. This can minimize the likelihood of insider threats and ensure accountability for information access.

  • Training employees to recognize cyber threats. Cybercriminals often target employees through phishing emails to gain access to sensitive information. This makes employees a key component of the organization’s defense system. For this reason, they should be equipped to recognize and stop hacking attempts, alongside our technical systems.

How can NordLayer help?

Internet access security is a priority for most companies, no matter what industry they work in. Nowadays, it poses unique security challenges businesses need to address due to various work models like remote, office, and hybrid.

NordLayer can assist enterprises in protecting their connections over the public internet. This is achieved by encrypting the connection between the user’s device and the middleman server using advanced ciphers. It ensures that all data exchanged is kept secure and cannot be read by outsiders.

With cutting-edge security technologies, NordLayer can block access to malicious websites and control entry to specific content categories. Using Public Shared Gateways, NordLayer expands browsing capabilities, allowing global business exploration and guaranteeing the confidentiality of users’ and resources’ true location.

Businesses can enhance their internet access security by implementing best industry practices and regularly training employees on security threats. This is a sure way to protect sensitive information from data breaches, no matter what work model your organization is.

Contact our sales team and discover how to achieve greater internet access security.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Binary memory protection measures on Windows OS

Binary memory protection is a core part of cybersecurity, but there are many different options for implementing it. In this article, we explore common mechanisms and protection measures for Windows OS.

Why is binary memory protection important?

You may remember when the Blaster worm struck the internet, or more recently when WannaCry caused global havoc using a leaked EternalBlue Windows OS exploit. Both are examples of malware that used buffer overflow memory corruption vulnerabilities, causing remote code execution and infecting millions of machines worldwide.

Most operating systems, written in C or C++, have limited memory protection, allowing these attacks to occur. Malware like Blaster and WannaCry manipulate the environment, instructions, and memory layout of a program or operating system to gain control over it.

Security professionals have implemented mechanisms to prevent software exploitation and minimize damage caused by memory corruption bugs. A “silver bullet” solution would be a mechanism that makes it challenging and unreliable for attackers to exploit vulnerabilities, allowing developers to leave buggy code in place while they work on fixing or rewriting it in memory-safe languages.

Common mechanisms and protection measures

Let’s review some of the most common mechanisms and protection measures provided inside Windows OS from Windows XP to Windows 11.

ASLR

Address space layout randomization (ASLR) is a computer security technique that prevents an attacker from reliably jumping to, for example, a particular exploited function in a program’s memory. ASLR randomly arranges the address space positions of a process’s key data areas, including the base of the executable and the positions of the stack, heap, and libraries. The effectiveness of ASLR depends on the entropy of the process’s address space (simply put, the probability of finding a random local variable).

Because of this protection, exploit payloads must be uniquely tailored to a specific process address space.

Vista and Windows Server 2008 were the first operating systems in the Windows family to provide ASLR natively, though this system was first developed back in 2001. Prior to these releases, there were several third-party solutions like WehnTrust available that provided ASLR functionality to varying degrees.

When Symantec conducted research on ASLR in Windows Vista, they found that ASLR had a significant effect when implemented in Windows 8 (or Windows 8.1). It provided higher entropy for address space layouts. The larger address space for 64-bit processes also increased the entropy of the ASLR for any given process.

  Exploit mitigation improvements in Windows 8

Windows 8 added randomization for all BottomUp and TopDown memory allocations, increasing the effectiveness of ASLR, which was not available in Windows 7.

Exploit mitigation improvements in Windows 8   Exploit mitigation improvements in Windows 8

In Windows 8, Microsoft introduced operating system support to force EXEs/DLLs to be rebased at runtime if they did not opt-in to ASLR. This mitigation can be enabled system-wide or on a per-process basis. You can modify the settings of mandatory ASLR through the Windows Security app.

ASLR, like any other security technique, has its weaknesses and attack vectors (heap spray, offset2libc, Jump Over ASLR, and others). Even one memory disclosure can completely defeat ASLR and provide an attacker with a significant opportunity. In addition to this, ASLR is only efficient when all executables and shared libraries loaded in the address space of a process are randomized. For example, research by Trend Micro researchers showed that Microsoft Edge browser exploit mitigations, including ASLR, could be bypassed. You can watch a video from the BlackHat conference to learn more.

DEP

Data Execution Prevention (DEP) is a protection mechanism that blocks the execution of code in memory pages marked non-executable. The NX (No-Execute) bit is a protection feature on CPUs used by DEP to prevent attackers from executing shellcode (instructions injected and executed by attackers) on the stack, heap, or in data sections. If DEP is enabled and a program attempts to execute code on a non-executable page, an access violation exception will be triggered.

Starting with Windows XP Service Pack 2 (2004) and Windows Server 2003 Service Pack 1 (2005), the DEP was implemented for the first time on x86 architecture.

An application can be compiled with the /NXCOMPAT flag to enable DEP for that application. You can also use editbin.exe /NXCOMPAT over a .exe file to enable it on a previously compiled file.

On 64-bit versions of Windows, DEP is always turned on for 64-bit processes and cannot be disabled. Windows also implemented software DEP (without the use of the NX bit) through Microsoft’s “Safe Structured Exception Handling” (SafeSEH), which I will talk about a bit later.

Despite being a useful protection measure, the NX bit can be bypassed. This leaves us unable to execute instructions placed on the stack, but still able to control the execution flow of the application. This is where the ROP (Return Oriented Programming) technique becomes relevant.

GS (Stack Canaries)

Stack canaries are a security feature that helps protect against binary exploits. They are random values that are generated every time a program is run. When placed in certain locations, they can be used to detect stack corruption. The /GS compiler option, when specified, causes the compiler to store a random value on the stack between the local variables and the return address of a function. According to Microsoft, these application elements will be protected:

  • Any array (regardless of length or element size)

  • Structs (regardless of their contents)

In a typical buffer overflow attack, the attacker’s data is used to try to overwrite the saved EIP (Extended Instruction Pointer) on the stack. However, before this can happen, the cookie is also overwritten, rendering the exploit ineffective (though it may still cause a denial of service). If the function epilogue detects the altered cookie and the application terminates.

Example of memory layout during the buffer overflow
 
Example of memory layout during the buffer overflow

The second important protection mechanism of /GS is variable reordering. To prevent attackers from overwriting local variables or arguments used by the function, the compiler will rearrange the layout of the stack frame and will put string buffers at a higher address than all other variables. So when a string buffer overflow occurs, it cannot overwrite any other local variables.

It was introduced with the release of Visual Studio 2003. Two years later, they enabled it by default with the release of Visual Studio 2005.

However, this protection measure is also not bullet-proof, since the attacker can either try to read the canary value from the memory or brute force the value. By using these two techniques, attackers can acquire the canary value, place it into the payload, and successfully redirect program flow or corrupt important program data.

CFG/XFG

Control Flow Guard (CFG) is a highly-optimized platform security feature that was created to combat memory corruption vulnerabilities. Placing tight restrictions on where an application can execute code makes it much harder for exploits to execute arbitrary code through vulnerabilities such as buffer overflows.

CFG creates a per-process bitmap, where a set bit indicates that the address is a valid destination. Before performing each indirect function call, the application checks if the destination address is in the bitmap. If the destination address is not in the bitmap, the program terminates.

How Windows CFG works
 
How Windows CFG works

Microsoft has enabled a new mechanism by default in Windows 10 and in Windows 8.1 Update 3. Developers can now add CFG to their programs by adding the /guard:cf linker flag before program linking in Visual Studio 2015 or newer. As of the Windows 10 Creators Update (Windows 10 version 1703), the Windows kernel is compiled with CFG.

To enhance CFG (Control Flow Guard), Microsoft introduced Xtended Control Flow Guard (XFG). By design, CFG only checks if functions are included in the CFG bitmap, which means that technically if a function pointer is overwritten with another function that exists in the bitmap, it would be considered a valid target.

XFG addresses this issue by creating a ~55-bit hash of the function prototype (consisting of the return value and function arguments) and placing it 8 bytes above the function itself when the dispatch function is called. This hash is used as an additional verification before transferring the control flow.

Getting back to the CFG, there are multiple techniques to bypass it. For example, you can set the destination to code located in a non-CFG module loaded in the same process, or find an indirect call that was not protected by CFG. A brief write-up about the CFG bypass by Zhang Yunhai can be found here.

SafeSEH

SafeSEH is an exception handler. An exception handler is a programming construct used to provide a structured way of handling both system and application-level error conditions. Commonly they will look something like the code sample below:

1
try {
2
}
3
catch (Exception e)
4
{
5
// Exception handling goes here
6
}

Windows supplies a default exception handler when an application has no exception handlers applicable to the associated error condition. When the Windows exception handler is called, the application will be terminated.

Exception handlers are stored in the format of a linked list with the final element being the Windows default exception handler. This is represented by a pointer with the value 0xFFFFFFFF. Elements in the SEH chain before the Windows default exception handler are the exception handlers defined by the application.

Exception handler layout on stack
 
Exception handler layout on stack

If an attacker can overwrite a pointer to a handler and then cause an exception, they might be able to get control of the program.

SafeSEH is a security mechanism introduced with Visual Studio 2003. It works by adding a static list of good exception handlers in the PE file at the timing of compiling. Before executing an exception handler, it is checked against the table. Execution is passed to the handler only if it matches an entry in the table. SafeSEH only exists in 32-bit applications because 64-bit exception handlers are not stored on the stack. By default, they build a list of valid exception handlers and store it in the file’s PE header.

Preventing SEH exploits in most applications can be achieved by specifying the /SAFESEH compiler switch. When /SAFESEH is specified, the linker will also produce a table of the image’s safe exception handlers. This table specifies for the operating system which exception handlers are valid for the image, removing the ability to overwrite them with arbitrary values. If you want to see how this mitigation technique can be bypassed in real-life, this blog post offers more useful information.

Conclusion

Memory corruption vulnerabilities have plagued software for decades. As mentioned in the beginning, there are multiple mitigation techniques to prevent software exploitation and minimize damage caused by memory corruption bugs. However, those protections are definitely not a “silver bullet” solution for all memory corruption vulnerabilities.

For the developer, this means that no one should not blindly rely on the OS-provided protections. Instead, try to propagate secure coding practices and integrate security toolings like fuzzers and static code analyzers.

Lastly, move to memory-safe languages like Rust, if possible. For the attackers, even if the target application has all available mitigation measures, there may still be ways to bypass those protections.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Optimizing your business IT processes

In today’s fast-paced business environment, information technology shapes the way companies operate, compete, and grow. The pace of technological advancements adoption can play a deciding role in a company’s success or failure. However, how this can be achieved within an organization may not always be clear.

For this reason, we’ve invited co-founder and CPO at Kubernetes automation, optimization, security, and cost management platform CAST AI, Laurent Gil. Additionally, our Head of Platform Engineering at NordLayer, Carlos Salas, for his take on improving the current organization’s IT infrastructure.

Let’s take a deep dive into your current IT infrastructure assessment, automation areas identification, the right automation tools selection, its implementation, and the best practices.

Assessing your current IT infrastructure

Laurent Gil shared his valuable insights on how businesses can optimize their IT infrastructure to drive efficiency and productivity. According to him, one crucial step in this process is conducting a comprehensive assessment of your current infrastructure.

“A successful IT optimization strategy always starts with a gaining clarity around the current state of the infrastructure. A thorough assessment helps to identify issues and bottlenecks that are good candidates for automation – and where automation will make the biggest impact. Quick wins are just as important as long-term strategy and keeping your eye on the bigger picture, considering your company’s specific needs and direction.”

Click to tweet

Here’s how your current IT infrastructure could be evaluated in 8 steps:

  1. Define assessment objectives. Assessment objectives can be diverse, and they should focus on particular areas that could use improvements. For some businesses, it may be ironing out security vulnerabilities, while for others, it may be performance improvements. 

  2. Gather information. Regardless of assessment objectives, the next step will always be data collection. This will form a solid foundation for the evaluation process providing useful insights in later steps.

  3. Evaluate your used hardware and software. All used servers, storage devices, routers, switches, as well as operating systems, databases, applications, and security software should be reviewed. Check for potential bottlenecks and clunky setups that are slowing down your operations. 

  4. Perform network checks. Analyze your network topology, bandwidth, and latency. Evaluate your network security measures, such as firewalls, intrusion detection, and prevention systems.

  5. Look into data backups and disaster recovery. Verify that your data backup and recovery plans are up-to-date, reliable, and effective. Test your disaster recovery procedures to ensure that they meet your recovery time objectives.

  6. Analyze your security setup. Assess your security policies and procedures, including access controls, authentication, and authorization. Test your security controls to identify weaknesses or gaps.

  7. Consider the IT budget. Evaluate your IT budget and spending to identify areas for improvement or cost savings. Identify potential areas where technology investments can drive business value and growth.

  8. Document your findings. Document your findings and recommendations in a detailed report. This will serve as a reference document providing actionable recommendations for improving your IT infrastructure.

Identifying areas for automation

Findings from the IT infrastructure assessment should help you identify areas that could benefit the most from automation. As different companies have different IT struggles, going through this process should be a highly individualized approach. That said, here are some common areas that could be easily automated.

Data entry and data processing. Routine maintenance tasks like data entry, migration, and validation can be easily automated using macros, scripts, and other robotic processes.

Network and system administration. Tasks like server monitoring, backup, and patch management can be time-consuming and repetitive. Automations enable the creation of templates to perform the tasks identically, leaving less room for human error. In addition, this frees the staff from manual processes allowing them to focus on strategic activities.

Software deployment. Every software deployment instance involves a lot of repetitive tasks to ensure that it’s deployed correctly and without errors. Automating them can help reduce the time and effort required for deployment and improve the reliability of the process.

Customer support. Simple customer support tasks like answering frequently asked questions, providing account information, and processing routine requests can be solved without human involvement. Leveraging chatbots and virtual assistants can combine convenience and efficiency for businesses and their customers.

Choosing automation tools

When it comes to selecting automation tools, Laurent Gil highlights the significance of putting business needs at the forefront.

“I’ve seen the benefits automation can bring to organizations of all sizes firsthand. However, not all automation tools are created equal, and choosing the right one for your business can be a daunting task.

What you need to consider are first and foremost your specific business requirements. Understanding business needs and matching them to the right automation offering ensures that what you invest in represents the best fit for your company.”

Click to tweet

Here’s a brief overview of the approach that businesses can take when selecting automation tools:

Research what’s available on the market 

Clear business objectives and defined areas for improvement will allow you to fill in the gaps with automation tools. This can involve various routes like reviewing industry publications or consulting with vendors directly.

Evaluate select tool features 

Once a list of potential features has been compiled, it’s important to evaluate its features. Depending on needed functionalities, this can involve scalability, customizability or other ease of use adjustments.

Consider integrations

Industry expert and Head of Platform Engineering Carlos Salas highlighted the importance of considering the bigger picture when selecting automation tools, highlighting their interoperability.

“Whatever automation tools you select won’t exist in a vacuum, so thinking about potential integrations with existing systems and processes isn’t a bad idea.”

“Data security is paramount. Before implementing any automation tool, it’s imperative to thoroughly evaluate its capabilities in protecting sensitive information and adhering to established security protocols.”

Click to tweet

This paves the way for seamless automation implementation without hiccups and ensures optimal performance down the line.

Test and trial 

Before making a final decision, businesses should take chosen automation tools for a test drive. Various methods like setting up a proof of concept or pilot project to evaluate the effectiveness of the tool in real-world scenarios will help to realistically evaluate its usefulness.

Implementing automation

Implementing business IT automation can be a complex task that requires careful planning and execution. Here are some general steps that you can follow to implement business IT automation.

  1. Design the automation process. Start by creating a plan for automation, including a timeline and a list of tasks to be automated. It also helps to break the process into smaller tasks and identify the rules and conditions that must be followed.

  2. Deploy the automation. The exact route of automation deployment will depend on whether it’s an in-house built tool or a third-party provider was chosen. Still, it’s best to test in a production environment initially and, after testing, move on to full-scale implementation.

  3. Train employees. Expect that your workforce will only know how to use it after a while. Expect that there will be a transitionary period during which various training will help staff to familiarize themselves with the tool better.

  4. Evaluate the results. After the automation has been implemented and employees get used to it, it’s worth checking its impact on productivity, efficiency, and accuracy. This information can be highly useful when identifying shortcomings in your current setup as well as planning and identifying new areas for automation.

Best practices for automating IT

To maximize your chances that your automation process goes smoothly, it can be good advice to follow the best industry practices. These include:

Focusing on standardization 

Standardization is critical when it comes to automating IT processes. It also makes it easier to automate routine tasks, reduces the chances of errors, and helps ensure consistency across your IT infrastructure.

Make use of automation platforms

Laurent Gil quote

According to Laurent Gil, automation platforms have the power to enhance business efficiency and streamline operations.

“Automation platforms enable businesses to accelerate and streamline their workflows and processes. Gone are the days of tedious manual tasks and complex coding requirements. With intuitive dashboards and user-friendly interfaces, these platforms empower users to design, create, and implement automation workflows without the need for in-depth technical expertise. And that’s a very good thing.”

Click to tweet

Gil’s words highlight the significant shift brought about by automation platforms in the business landscape. With these powerful tools at their disposal, organizations of all sizes can leverage automation to optimize their workflows, freeing up valuable time and resources for more strategic endeavors.

Adopt a DevOps approach 

Adopting a DevOps approach to automation can help streamline the IT development and deployment processes. Integrating development and operations teams allows the entire software development lifecycle to be automated. This can help you deliver software faster and with fewer errors.

Involving stakeholders 

Stakeholders are the personnel that the automation process will directly impact. Therefore, their input can help to identify potential pain points in advance. This can lead to more effective automation that addresses real problems and is designed to meet the organization’s specific needs.

Bottom line

Optimizing your business IT requires a systematic approach based on evaluating your current setup. The thorough analysis of the current businesses’ IT environment allows them to identify potential automation areas.

The process is finalized by choosing appropriate automation tools and going through the implementation process. It’s important to consider specific needs, evaluate tool features, integration, and test and try the solutions before fully committing. Automation adoption has the potential to make businesses even better adjusted to the current digital landscape.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Elevating healthcare: a definitive guide to robust cloud security in the industry

When compared to other industries, healthcare has remained quite reluctant to digitalization. However, as technology evolves, cloud computing has become vital in streamlining operations and enhancing data accessibility. On the flip side, this also introduces various security concerns that demand attention.

This comprehensive guide delves into the importance of robust cloud security in healthcare. It provides valuable insights to safeguard sensitive patient information, maintain regulatory compliance, and fortify the industry against evolving threats. Join us as we explore all the essential information regarding cloud security in healthcare.

The growing importance of cloud security in healthcare

After the COVID-19 pandemic, the healthcare industry experienced a heightened demand for improved and more modern services. Distributed care and telemedicine pushed healthcare organizations to move to cloud computing, meaning data security had to be considered. The problem is that the same techniques that were valid for data security on-premises don’t translate well into externally kept data.

Some of the challenges facing the healthcare industry transitioning to cloud infrastructure included:

  • Resource and budget strains. Most healthcare providers work with limited IT budgets, so major infrastructure overhauls are long and tedious.

  • Continuity of operations. Data migrations to the cloud shouldn’t disrupt everyday operations, which isn’t something that all healthcare providers can allow.

  • Regulatory compliance. Patient data is highly confidential information so various local regulations sanction its security.

Generally, healthcare organizations want to move to cloud computing to make their services more effective while avoiding unnecessary or unmanaged risks. As patient data is one of the most sensitive data types, ensuring robust security measures is a top priority.

Types of healthcare cloud security solutions

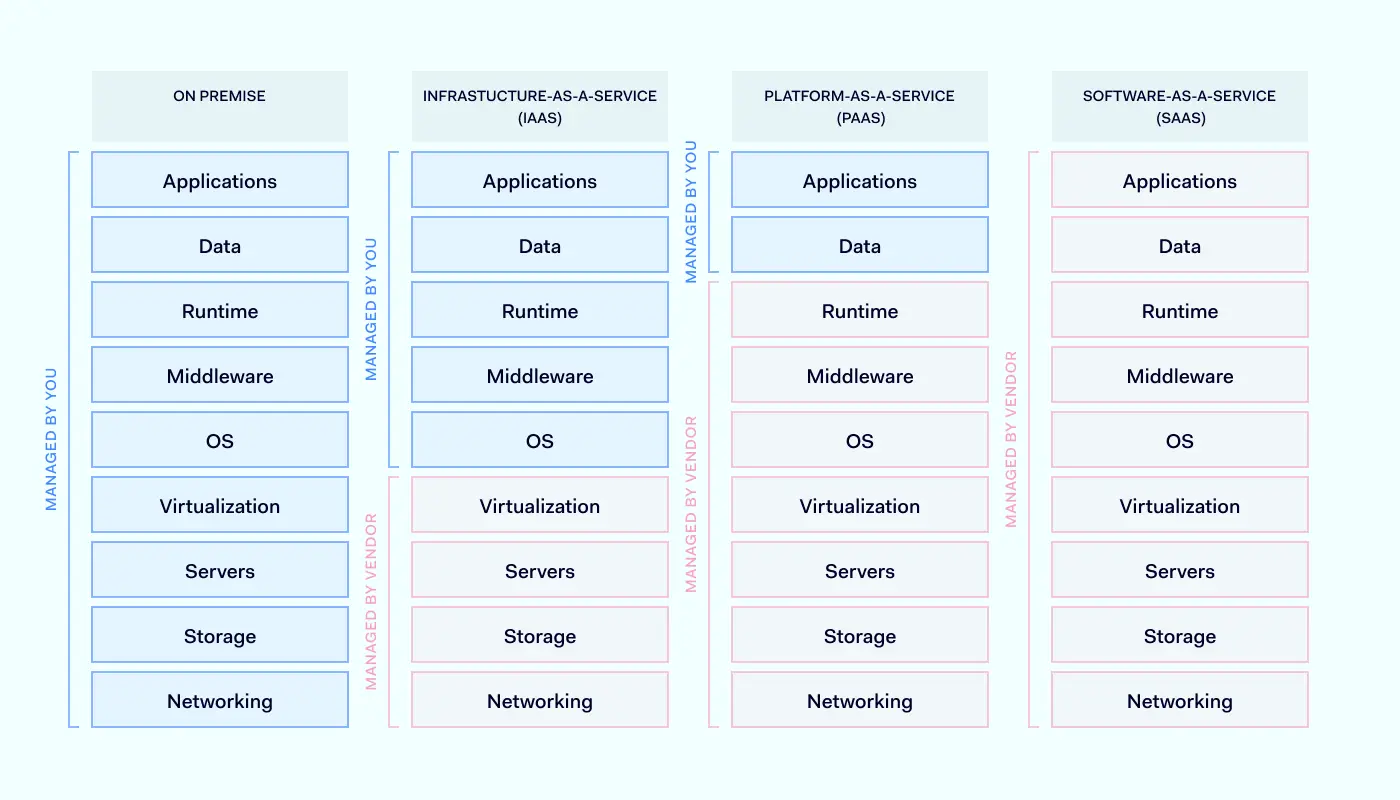
Healthcare providers (and, by extension, most industries) rely on three main types of cloud computing services. This includes Infrastructure-as-a-Service (IaaS), Platform-as-a-Service (PaaS), and Software-as-a-Service (SaaS).

Infrastructure-as-a-Service (IaaS)

Infrastructure-as-a-Service provides virtualized computing resources as services over the internet. In IaaS, the service provider manages and delivers all associated hardware and software components: servers, storage, networking, and virtualization resources. With IaaS, users can provision and control these resources on-demand, scaling them up or down as needed.

Benefits of IaaS in healthcare

Aside from the fact that cloud computing makes it easier to deploy workloads, IaaS has a range of benefits that could be useful for healthcare companies.

  • Scalability and flexibility. By leveraging IaaS, users can rapidly deploy and configure virtual machines, storage, and network components. This allows healthcare organizations to scale their infrastructure up or down based on their actual needs.

  • Disaster recovery. IaaS enables organizations to back up and recover their critical data and remote machines. As critical data and applications are kept in cloud storage, this ensures their availability and integrity.

  • Cost efficiency. IaaS service providers use a flexible pay-as-you-go pricing model allowing users to pay only for the resources they use. This enables cost optimization, eliminating the need for upfront hardware and infrastructure maintenance investments.

Security challenges and how to address them

IaaS security is shared between the service provider and the user. While the service provider is responsible for managing underlying networking, storage, servers, and virtualization, the user is responsible for managing the security of everything running on top of the infrastructure. This involves operating systems, middleware, data, and applications. This setup is not without cybersecurity challenges.

  • Data protection. Sensitive patient data must be protected using encryption and access controls. As the data is physically located in third-party data centers, unauthorized access or breaches are the primary concern.

  • Compliance. Patient data falls under government-protected information, so regulatory compliance applies to it. Organizations must ensure that their IaaS providers adhere to sensitive patient data from unauthorized access or breaches.

For these reasons, IaaS provider selection is crucial to avoid collateral damage. Implementing multi-factor authentication, regular vulnerability assessments, and proactive monitoring can enhance security.

Platform-as-a-Service (PaaS)

Platform-as-a-Service includes everything from IaaS with a dedicated environment for developing, deploying, and managing applications over the internet. It offers tools, frameworks, and services that enable developers to build, test, and run applications. Much like a physical data centre, PaaS providers handle hardware provisioning, operating system management, and network setup, allowing developers to focus solely on application development.

Benefits of PaaS in healthcare

With PaaS, healthcare providers get a platform for developing, testing and deploying applications in the cloud. Here are its main benefits:

  • Rapid application development. PaaS simplifies the application development process, allowing one to skip multiple setup steps and go directly to the deployment. This can accelerate innovation and provide new solutions quickly.

  • Scalability and performance. As with all cloud-based tools, they can automatically scale based on demand, ensuring high availability and optimal performance.

  • Collaboration and integration. PaaS is compatible with existing systems, meaning currently used tools can be integrated into a unified system.

Security challenges and how to address them

When adopting PaaS, organizations need to be wary of its security challenges. Here are some examples:

  • Application security. PaaS environments involve the deployment and running of custom applications. Therefore, businesses should conduct regular code reviews, implement secure coding practices, and perform vulnerability assessments.

  • Secure configuration. Businesses need to make sure that used PaaS platforms are properly configured. This includes firewalls, network access controls, and encryption protocols.

  • Incident response and monitoring. PaaS environments require ongoing monitoring and timely incident response capabilities. By establishing robust logging and monitoring systems and employing detection and prevention mechanisms, we can have a ready system in case of an intrusion.

Software-as-a-Service (SaaS)

Software-as-a-Service is a cloud computing model in which hosted software is delivered over the internet instead of installed on local premises. In this model, the software is centrally hosted by a provider who manages and maintains the underlying infrastructure, database, and updates. Users only pay a subscription fee to access and use the software on a pay-as-you-go basis.

Many healthcare-related applications are delivered via SaaS, including healthcare picture archiving and communication systems (PACs), electronic health records (EHR), telehealth services, and more.

Benefits of SaaS in healthcare

With SaaS, healthcare organizations are provided with the service directly without the need to handle setup and maintenance. Here are its main benefits:

  • Accessibility and mobility. SaaS applications can be accessed from everywhere, enabling healthcare professionals to securely access patient information on various devices, enhancing workflow efficiency.

  • Automatic updates. The responsibility to handle software updates and patches fall on the service provider, meaning that healthcare applications are always up to date and protected against emerging security threats.

  • Fast deployment. SaaS applications are provided instantly and with minimal setup compared to on-premises software. Software updates and maintenance are handled by the SaaS provider, ensuring smooth operation.

Security challenges and how to address them

The problem is that SaaS brings healthcare organizations not only benefits. It does have some security challenges that need to be addressed by IT personnel.

  • Access control. As SaaS applications are externally hosted, managing user access and authentication is critical. This is the only way to prevent unauthorized intrusions.

  • Third-party integrations. Some SaaS applications need to be integrated with third-party services or APIs. These integrations can introduce security risks if not properly managed or if they have exploitable vulnerabilities.

  • Multi-tenancy risks. The same SaaS application can serve multiple consumers, sharing the same underlying structure and resources. This is why logical separation and isolation between tenants are crucial to prevent data leakage or unauthorized access to customer data.

Compliance and regulatory landscape in cloud security

Regulatory landscape and compliance are critical considerations for organizations across various industries. Most countries have recently implemented various data protection and cybersecurity laws. The government regulates the privacy protection of medical data, and breaching the law ensues grave consequences.

Here are some prominent regulations, guidelines that could impact cloud security, and strategies for ensuring compliance.

HIPAA and HITECH

The Health Insurance Portability and Accountability Act (HIPAA) and the Health Information Technology for Economic and Clinical Health (HITECH) Act are crucial regulations in the healthcare industry. They both perform different functions:

HIPAA — sets standards for protecting sensitive patient health information

HITECH — promotes the adoption of electronic health records

Compliance with both is essential when leveraging cloud computing services in the healthcare sector. Organizations need to take care of security measures like data encryption, access controls, and regular audits to safeguard patient data and meet the requirements outlined in these regulations.

GDPR

The General Data Protection Regulation (GDPR) is a comprehensive data protection framework that affects organizations operating in European Union countries or handling EU citizen data. It emphasizes individual privacy rights, consent management, and data breach notification.

Cloud service providers and organizations utilizing cloud computing services must comply with GDPR by implementing appropriate security measures, conducting data protection impact assessments, and ensuring cross-border data transfers adhere to GDPR guidelines. Encryption, pseudonymization, and privacy-by-design principles are critical for achieving compliance with GDPR in cloud computing.

Other regional regulations and guidelines

In addition to HIPAA, HITECH, and GDPR, other regional regulations and guidelines impact cloud security in specific industries or geographic locations. Examples include the Payment Card Industry Data Security Standard (PCI DSS) for the payment card industry and the Federal Risk and Authorization Management Program (FedRAMP) for U.S. government agencies.

Compliance with these regulations requires organizations to align their cloud security practices with specific requirements. Depending on the regulation and area, this may include data encryption, access controls, vulnerability management, and incident response protocols. Staying informed about relevant regional regulations is crucial to ensure compliance and avoid potential penalties or reputational damage.

As it was mentioned previously, cloud services adoption would involve collaboration with third parties. Here are some key considerations of security responsibilities between the cloud service provider and the customer:

Vendor risk assessment

A thorough vendor risk assessment helps to make sure that a cloud provider will be a matching fit for a healthcare organization’s needs. The cloud service provider’s market is saturated, but not everyone has compliant security controls, certifications, incident response capabilities, and data protection practices. The same strict requirements for healthcare organizations also apply to their third-party partners.

By assessing vendor risks, organizations can make informed decisions and select providers aligning with their security requirements and compliance obligations. Provider’s failure to secure the underlying infrastructure can open the gap in the security set up by the healthcare provider.

Understanding the shared responsibility model

The shared responsibility model defines the division of security responsibilities between cloud service providers and customers. While providers are responsible for securing the underlying infrastructure, customers are accountable for securing their data and applications within the cloud.

Organizations must understand and fulfill their share of responsibilities, which may involve tasks such as configuring access controls, encrypting sensitive data, applying patches and updates, and regularly monitoring for security incidents.

Key cloud security strategies and solutions for healthcare

While cloud computing is appealing to make operations more modern and effective, the downside is the potential cybersecurity risks. Safeguarding sensitive patient data and navigating regulatory compliance requirements are the primary concerns for healthcare providers. There are three main cloud security strategies and solutions to consider.

Advanced threat prevention

Advanced threat prevention is one of the key cloud security strategies for healthcare. It involves deploying sophisticated security measures to identify and mitigate potential threats before they cause any damage. Relying on technologies like machine learning algorithms, behavior analysis, Deep Packet Inspection, and real-time monitoring, organizations aim to detect and respond to suspicious activities.

As a proactive approach to cybersecurity, advanced threat monitoring allows healthcare organizations to identify and effectively neutralize threats. This helps businesses to reduce the risk of data breaches and unauthorized access to patient information.

Cloud-based security operations and monitoring

Monitoring is critical in ensuring the integrity and confidentiality of healthcare data stored in the cloud. By providing continuous oversight and proactive detection of potential security breaches or unauthorized access attempts, monitoring enables organizations to secure against security incidents promptly.

In addition, by leveraging cloud-based security tools, healthcare organizations can centralize security operations, streamline incident response, and gain insights into potential vulnerabilities. The systems can be automated, helping organizations detect and mitigate security breaches on time and enhancing overall security posture without human involvement.

Secure remote work

During the COVID-19 pandemic, the adoption of remote work in the healthcare sector accelerated. Secure remote access became critical as healthcare professionals needed to access patient data and collaborate remotely.

Cloud security solutions enable secure sensitive data storage, ensuring healthcare providers can work efficiently while adhering to strict security protocols. Implementing secure virtual private networks (VPNs), multi-factor authentication, and encryption technologies safeguard data transmission and prevent unauthorized access, mitigating risks associated with remote work.

Cloud security in action: enabling new healthcare capabilities

Cloud security not only performs the function of safeguarding patient data, it also empowers healthcare organizations to embrace new capabilities and innovate. Here are some routes in which cloud security can facilitate advancements.

Redundancies to prevent ransomware attacks

Ransomware attacks use malware that encrypts data stored in the device’s hard drive rendering it inaccessible until a payment is made to the attacker. This is extremely disruptive to organizations relying on on-premises infrastructure as this can completely shut down all operations and compromise patient data.

The only solution to this issue is data replication in multiple dispersed locations. That way, there’s no centralized storage that could be tampered with. In an accident, data can be restored from unaffected backups, minimizing downtime and ensuring continuity of care. Cloud servers enable effective mirroring solutions allowing distributed backups.

Delegation of security responsibilities to third-party firms

Cloud security can catalyze operations outsourcing, allowing better work distribution in your organization. Managing and maintaining robust cloud security infrastructure requires specialized expertise. That’s one of the key reasons why many healthcare organizations delegate their security responsibilities to reputable third-party vendors.

Cloud computing partners already possess the knowledge and resources to implement industry best practices, conduct regular security assessments, and respond to emerging threats promptly. This allows organizations to enhance the cloud security posture and focus on quality patient care.

Automation to free up healthcare resources

Cloud security can be improved by adopting various innovations to improve the setup. By automating vulnerability scanning, log analysis, and security policy enforcement, healthcare providers can free up their workforce from manual and time-consuming tasks.

Automation improves efficiency, reduces the risk of human error, and ensures consistent application of security controls. As IT professionals aren’t burdened with recurring manual tasks. This leaves them more time to focus on advanced security measures and stay updated with evolving threats.

Expert insights and resources for healthcare cloud security

Several organizations provide expert insights and resources for healthcare cloud security. Cloud Security Alliance (CSA), the European Union Agency for Cybersecurity (ENISA), and the National Institute of Standards and Technology (NIST) are the main ones providing various recommendations for cloud security in healthcare companies.

CSA

CSA has established requirements for healthcare organizations to ensure secure cloud computing practices. These requirements mainly focus on several key areas:

  • Implement strong access controls and authentication mechanisms to protect sensitive data.

  • Regularly monitor and audit cloud services for security vulnerabilities and incidents.

  • Encrypt data both in transit and at rest to maintain confidentiality.

  • Conduct regular risk assessments and threat modelling to identify and mitigate potential risks.

  • Establish incident response and recovery plans to handle security breaches effectively.

  • Stay updated with the latest security best practices and standards.

By adhering to these CSA requirements, healthcare organizations can enhance the security of their cloud computing environments and protect patient information from unauthorized access or data breaches.

ENISA

ENISA lays out comprehensive requirements for healthcare organizations in the European Union to enhance their cybersecurity measures. These requirements encompass multiple aspects of cloud security:

  • Develop and enforce robust security policies and procedures for cloud adoption.

  • Perform thorough risk assessments to identify and address potential security threats.

  • Ensure the secure configuration and hardening of cloud computing environments.

  • Employ strong access controls and authentication mechanisms to protect sensitive data.

  • Regularly monitor and log cloud computing activities to detect any suspicious behaviour.

  • Establish incident response plans and conduct regular security audits.

Adherence to these ENISA requirements is vital to safeguarding patient data, protecting critical healthcare systems, and maintaining the resilience and trustworthiness of healthcare services within the EU.

NIST

NIST provides guidelines and requirements and guidelines for healthcare organizations to ensure the security and privacy of patient information. These requirements include:

  • Follow the NIST Cybersecurity Framework for risk management and cybersecurity best practices.

  • Employ strong identity and access management controls to protect data and resources.

  • Use encryption to safeguard data both in transit and at rest.

  • Regularly update and patch cloud infrastructure and applications to address security vulnerabilities.

  • Implement robust network security controls, such as firewalls and intrusion detection/prevention systems.

  • Conduct continuous monitoring and log analysis to promptly detect and respond to security incidents.

Healthcare companies must review and adapt these recommendations to their organizational needs and regulatory requirements.

How can NordLayer help?

Securing cloud infrastructure can be challenging for healthcare companies. Still, the benefits outweigh the risks, so it’s worth considering digitally transforming an organization and improving its services. It’s not a bad idea to turn to third-party partners that could help to take a leap.

NordLayer streamlines network access controls to ensure only authorized users can access confidential data. Access to cloud resources happens using encrypted tunnels using AES 256-bit and ChaCha20 cyphers. The service is also compatible with major cloud platforms like Azure and AWS, allowing seamless integration with other solutions and services.

With correct control mechanisms, NordLayer is a valuable ally to follow through with the best cloud environment security practices. With an extensive set of centrally implemented features and monitoring controls that are all managed via the Control Panel, NordLayer allows the implementation of security policies reducing various risks.

Contact NordLayer and discuss your security options today to ensure safe access to patient data and protect your cloud infrastructure.

FAQ

How can healthcare organizations ensure compliance in the cloud?

Healthcare organizations can ensure compliance in the cloud by understanding applicable regulations. Familiarizing with regulations like HIPAA and GDPR will allow organizations to identify specific compliance requirements. This will serve as a basis for cloud provider choice and guide what access controls and other cybersecurity functionalities must be implemented to align with requirements.

What are examples of cloud security?

Cloud security is an umbrella term encompassing various technologies to protect data and systems in the cloud. This includes encryption, access controls, firewalls, intrusion detection and prevention systems, security information and event management, and data loss prevention.

How does the shared responsibility model work in healthcare cloud security?

The shared responsibility model defines the division of security responsibilities between the cloud service provider (CSP) and the healthcare organization. While the specifics entirely depend on the cloud service model, the cloud service provider usually takes care of the underlying cloud infrastructure. At the same time, the healthcare organization is responsible for application data security and access control.

What steps can healthcare organizations take to mitigate third-party risks?

To mitigate third-party risks, healthcare organizations must establish clear contractual agreements outlining security expectations, data handling procedures, breach notification requirements, and liability provisions. Then, a good plan is to perform ongoing maintenance with regular risk assessments. This should help organizations minimize risks associated with third parties.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.