Financial institutions are prime targets for ransomware attacks due to the vast amounts of sensitive customer information they hold. The consequences of these attacks can be devastating, resulting in operational disruptions, financial losses, and long-term damage to reputation and trust.
The Impact of Ransomware on Financial Institutions
Ransomware attacks can have far-reaching effects on financial institutions:
Operational Disruption:
Halted Operations: Ransomware can halt production lines, disrupt supply chains, and cause quality control issues. This can lead to significant downtime and the production of defective products or services.
Essential Services Disrupted: Critical services may become inaccessible, affecting customers and stakeholders.
Sophisticated Attack Methods:
Double and Triple Extortion: Modern ransomware attacks often involve not just the encryption of data but also the threat of releasing sensitive information (double extortion) or adding additional demands even after the initial ransom is paid (triple extortion).
Distributed Denial of Service (DDoS) Attacks: Attackers may also use DDoS attacks to overwhelm and disable online services, adding another layer of disruption.
Economic and Reputational Damage:
Undermining Economic Stability: Ransomware attacks on multiple financial institutions can undermine local, regional, and even national economic stability, eroding confidence in the financial system as a whole.
Loss of Customer Trust: Financial institutions rely heavily on customer trust. A successful ransomware attack can cause lasting damage to the institution’s reputation and erode the trust customers place in them.
Loss of Trust: Customers and partners may lose trust in an organization following a ransomware attack.
Long-term Brand Damage: The organization’s reputation may suffer long-term harm, affecting its competitive position in the market.
The Rising Cost of Ransomware
The threat of ransomware is increasing:
The financial impact of ransomware attacks on the financial services sector is growing:
High Incidence of Attacks: In 2024, 65% of financial services organizations were hit by ransomware.
Increasing Recovery Costs: The average cost to recover from a ransomware attack in this sector increased to $2.58 million in 2024.
Data Encryption: Approximately 76% of ransomware attacks result in data encryption, adding to the complexity and cost of recovery.
Ransomware Containment: Implementing measures to quickly contain and mitigate the impact of an attack once it occurs.
Given the significant impact that ransomware attacks can have on government organizations, it is crucial to take steps to prevent these attacks. Here are a few steps that organizations can take to protect themselves:
1. Implement robust cybersecurity measures:
Government organizations should implement robust cybersecurity measures, such as firewalls, intrusion detection systems, and anti-malware software. Regularly updating software and operating systems can also help reduce the risk of attacks.
2. Conduct regular employee training:
Regular training for employees can help reduce the risk of successful phishing attacks, which are a common method of ransomware delivery.
3. Regularly backup data:
Regularly backing up critical data and storing backups in a secure location can help ensure that data is recoverable in the event of a ransomware attack.
4. Implement multi-factor authentication:
Multi-factor authentication can help reduce the risk of unauthorized access to systems and data, even if credentials are stolen.
5. Develop an incident response plan:
Developing an incident response plan can help organizations respond to a ransomware attack quickly and effectively, minimizing the impact on the organization. A ransomware containment solution is a critical component of such a plan.
Is Your Organization Protected?
Given the increasing threat of ransomware, it’s crucial for organizations to assess their current cybersecurity posture and ensure they are prepared to defend against and respond to these attacks.
Think your organization is protected from the growing ransomware threat? Find out for sure by conducting a thorough review of your cybersecurity measures and updating your strategies to stay ahead of evolving threats.
About Bullwall BullWall is a fast-growing international cybersecurity solution provider with a dedicated focus on protecting critical data during active ransomware attacks. We are the only security solution able to contain both known and unknown ransomware variants in seconds, preventing encryption and exfiltration across all data storage types.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
Let’s talk about Zero Trust Architecture (ZTA), the cybersecurity strategy that has become as popular in boardrooms as it is in IT departments. In the ever-evolving landscape of cybersecurity threats, ZTA has emerged as a game-changer, a buzzword, and—importantly—a necessity. But like all revolutionary concepts, its adoption is anything but straightforward. So, let’s dive into the current state of ZTA adoption among enterprises, explore the strategies organizations are deploying, examine the challenges they face, and highlight the undeniable benefits. And, of course, we’ll take a close look at how Network Access Control (NAC) fits into the ZTA puzzle.
The Promise of Zero Trust: What’s Driving Adoption?
Zero Trust Architecture is based on a simple but radical principle: trust no one, verify everyone. Unlike traditional security models that assume everything inside the network is safe, ZTA assumes that threats could be anywhere—inside or outside the network. This model shifts the focus from perimeter-based security to a more granular approach where every user, device, and connection is continuously validated.
The surge in ZTA adoption is driven by a few key factors:
Increased Sophistication of Cyber Threats: Ransomware, phishing, and insider threats are more prevalent and dangerous than ever. Traditional defenses are proving inadequate against these evolving threats, making ZTA an attractive alternative.
Workplace Transformation: The rise of remote work and BYOD (Bring Your Own Device) policies has blurred the lines of the traditional network perimeter. ZTA’s model, which doesn’t rely on perimeter defenses, is ideally suited for this new environment.
Regulatory Pressure: Compliance standards, such as the GDPR, CCPA, and others, increasingly emphasize data protection and security. ZTA helps organizations meet these stringent requirements by providing more robust and adaptable security frameworks.
Strategies for ZTA Adoption: How Are Enterprises Getting There?
While the benefits of ZTA are clear, adopting it is a journey, not a switch. Here’s how enterprises are navigating this path:
Phased Implementation: Many organizations are taking a phased approach, gradually implementing ZTA principles across their infrastructure. This typically starts with identifying and securing critical assets before expanding to broader systems and networks.
Identity and Access Management (IAM): At the heart of ZTA is the concept of least privilege, which necessitates strict IAM policies. Enterprises are investing in robust IAM solutions to control who has access to what, ensuring that only authorized users can access sensitive information.
Microsegmentation: Microsegmentation divides the network into smaller, isolated segments. This reduces the attack surface and limits the movement of potential threats. Organizations are using this technique to implement ZTA, ensuring that even if a breach occurs, the damage is contained.
Continuous Monitoring: Continuous assessment and monitoring of users and devices are essential to ZTA. Enterprises are deploying advanced monitoring tools to detect anomalies in real-time, enabling them to respond swiftly to potential threats.
The Challenges: What’s Standing in the Way?
Despite its advantages, ZTA adoption isn’t without hurdles. Here are some of the most significant challenges:
Complexity: Implementing ZTA can be complex, especially for large organizations with legacy systems. The transition requires a fundamental shift in how security is approached, which can be a daunting task.
Cost: The initial cost of implementing ZTA can be high, involving investments in new technology, training, and potentially overhauling existing systems. While the long-term benefits are substantial, the upfront investment can be a barrier for some enterprises.
Cultural Resistance: ZTA requires a change in mindset, not just among IT teams but across the entire organization. This can be met with resistance, particularly in companies where security protocols are deeply ingrained in the corporate culture.
The Benefits: Why Move to ZTA?
The benefits of moving to a Zero Trust Architecture are compelling:
Enhanced Security: By continually validating users and devices, ZTA significantly reduces the risk of breaches, protecting sensitive data from both external and internal threats.
Adaptability: ZTA is adaptable to the changing threat landscape and the evolving needs of the business. Whether it’s integrating new technologies or expanding remote work capabilities, ZTA provides a flexible framework.
Regulatory Compliance: ZTA helps organizations meet regulatory requirements by providing a robust security posture that is aligned with data protection laws.
Network Access Control (NAC): The Missing Piece of the ZTA Puzzle?
Network Access Control (NAC) plays a critical role in ZTA by ensuring that only authenticated and authorized devices can access the network. In a ZTA environment, NAC serves as the gatekeeper, enforcing access policies and providing visibility into who and what is on the network. It’s like the bouncer at an exclusive club—no one gets in without meeting the criteria.
Moreover, NAC supports the continuous validation principle of ZTA by monitoring devices throughout their session, ensuring they remain compliant with security policies. If a device becomes compromised, NAC can isolate it, preventing potential threats from spreading across the network.
In essence, NAC is not just a complementary tool in ZTA but a foundational component that enables organizations to enforce the stringent access controls that ZTA demands.
Conclusion: The Future of ZTA
As cyber threats continue to evolve, the adoption of Zero Trust Architecture is not just a trend but a necessity. Enterprises that embrace ZTA will be better equipped to face the challenges of the modern threat landscape, protect their assets, and maintain compliance with regulatory requirements. While the journey to full ZTA implementation is complex and fraught with challenges, the benefits far outweigh the costs.
For those on the fence about ZTA, consider this: In a world where threats are becoming more sophisticated and pervasive, can you afford not to trust anything—or anyone—without verification?
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About Portnox Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。
According to a recent report, breaches involving admin accounts have increased by 17% from 2023[1]. Moreover, approximately 45% of ransomware attacks targeted specifically admin accounts in 2024[2].
These statistics highlight that administrator accounts are prime targets for hackers, as gaining access to such accounts grants full control over administrative actions, including user management, file access, and app installation, posing significant security risks.
Privileged Access Management with Just-in-Time Admin Access for Windows
Traditional administrative access methods are often inadequate in addressing these risks. The lack of automation can result in users retaining extended admin access, which increases the potential for security breaches.
Furthermore, sharing admin credentials among multiple users escalates the issue, heightening the risk of malware attacks and data breaches, and compromising sensitive organizational information.
This underscores the need for a robust privileged access management solution, such as Scalefusion’s Just-In-Time Admin Access feature. This blog will explain what Just-In-Time Admin Access entails and highlight the key capabilities of this feature.
What is Just-In-Time Admin Access?
Scalefusion offers privileged access management with the Just-In-Time Admin Access feature. This feature ensures that users operate with standard privileges, offering a secure way to access temporary admin privileges only when necessary. It significantly reduces the risks associated with excessive user privileges by providing elevated access only when required, maintaining security while minimizing potential threats.
Just-In-Time Admin Access enables users to obtain temporary access to launch applications in admin mod, on managed Windows devices. This feature ensures that users operate with elevated privileges securely and only when necessary, allowing them to perform essential tasks without prolonged admin access.
Key Features of Just-In-Time Admin Access for Windows Devices
1. JIT Admin Configuration
JIT admin configuration allows IT admins to configure:
a. Duration of Admin Privilege
IT admins can specify the duration (in minutes) during which the user can access the applications in elevated mode. Once the duration ends, the app will be automatically closed. Admin can set the duration from 5 to 60 minutes.
b. Allowed number of Requests per Day
IT admin can enable this setting to allow users to elevate the applications with admin privileges by entering other admin’s credentials. Users will be able to elevate applications using only the Scalefusion account if the admin credentials are not available
c. Enforce Request justification text
Administrators can make it compulsory for Windows device users to enter the reason for requesting access to any application with elevated access.
d. Enforce active internet connection
If this setting is enabled, a Windows device user must have an active internet connection to access any application in admin mode
e. Allow users to elevate using other Admin credentials
IT admin can enable this setting to allow Windows users to elevate the applications with admin privileges by entering other admin’s credentials. If the admin credentials are not available, users will be able to elevate applications using only the Scalefusion Account.
f. Configure Disclaimer Note
IT admins can enter a disclaimer note for users that is displayed on the JIT Admin screen to notify them when the set duration ends.
2. Log and Activities
a. Monitor Admin Access and Collect logs
Admins can configure whether logs monitoring the number of times critical operations and applications were started/stopped with admin privileges, should be captured and synced to the dashboard.
3. Elevation Scope
Elevation scope enables IT admins to set a limit of access elevation. It allows them to configure the following settings:
a. Configure Accounts That Can Request Admin Access
IT admins can configure whether all non-admins accounts or specific accounts on the device can request to access the application in elevated mode. If the admins select ‘Specific Accounts’, they must provide the names of user accounts to whom they want to grant access.
b. Select Applications that can be Run as Administrator
Administrators can select which applications should run as an administrator. They can choose from three options:
‘All Allowed Applications’ enables all applications specified in the Select Apps section of the Device Profile.
‘All Applications’ permits any application on the managed device to be run as an administrator.
‘Specific Applications’ restricts administrative access to particular applications. Admins must add the application names by clicking “Add Application” and providing relevant details such as the app name and version.
c. Override Duration of Admin Privilege
Admins can specify the duration (in minutes) after which the admin privileges will be automatically revoked, automatically closing the app. This setting overrides the duration of admin privileges configured as a part of JIT Admin Configuration. The time duration ranges between 1 to 1440 mins.
4. JIT Admin Access Summary
JIT Admin Access summary provides IT admins with the following details:
a. Device Summary
The device summary offers a comprehensive overview, detailing the total number of devices with Just-In-Time (JIT) Admin configuration applied, the count of standard users on these devices, and the number of admin users. This summary provides clear visibility into the user distribution and administrative access across the configured devices.
b. Request Summary
Request Summary gives IT admins an overview of the number of admin requests made during a single day and the total number of admin requests made during the last 60 days.
c. Device Overview
With the device overview section, admins can access a consolidated tabular view of the name of devices where the configuration has been applied, the serial number of devices, the number of requests received from the device today, the total number of admin requests received from the device, the name of the configuration applied to the device.
5. Activity Logs
Activity logs enable admins to view activities done by the users on the device, during their elevation from standard to admin user. Apart from the device name and serial number, activity logs include the names of users requesting JIT Admin Access, the files accessed, the start and end time of the JIT admin activity (indicating when the user was elevated to admin and when they were downgraded back to a standard user), and the justification text entered by the user when requesting JIT admin access.
6. Recommendations
The recommendations section offers a summarized view of the admin accounts available on the devices. It includes the names and serial numbers of JIT-configured devices, the total number of users and admins on each device, the number of managed admins, and the name of the JIT Admin configuration applied.
Optimize User Privilege Escalation for Windows with Scalefusion OneIdP
Scalefusion OneIdP provides organizations with robust identity and access management capabilities. It allows organizations to gain full control over user privilege elevation by offering time-based admin access, preventing users from obtaining extended admin access, securing data, and maintaining system integrity.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About Scalefusion Scalefusion’s company DNA is built on the foundation of providing world-class customer service and making endpoint management simple and effortless for businesses globally. We prioritize the needs and feedback of our customers, making sure that they are at the forefront of all decision-making processes. We are dedicated to providing comprehensive customer support services, and place emphasis on customer-centric thinking throughout the organization.
SonicWall disclosed a vulnerability that affects SonicOS management access and SSLVPN software on SonicWall Gen 5, Gen 6, in addition to Gen 7 devices running SonicOS version 7.0.1-5035 or earlier.
CVE-2024-40766 is rated critical with CVSS score of 9.3, and potentially allows for unauthorized resource access by an attacker. There is limited evidence that this vulnerability is being exploited in the wild.
What is the impact?
Successful exploitation of this vulnerability potentially results in unauthorized resource access and in some cases could lead to a DoS after causing vulnerable devices to crash.
Are updates or workarounds available?
SonicWall recommends restricting management access to trusted sources or disabling WAN management from the public Internet. Additionally, SonicWall has released updated firmware and is available for download from mysonicwall.com.
How to find potentially vulnerable systems with runZero
From the Asset Inventory, use the following query to locate systems running potentially vulnerable software:
hw:"SonicWall" type:"Firewall"
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About runZero runZero, a network discovery and asset inventory solution, was founded in 2018 by HD Moore, the creator of Metasploit. HD envisioned a modern active discovery solution that could find and identify everything on a network–without credentials. As a security researcher and penetration tester, he often employed benign ways to get information leaks and piece them together to build device profiles. Eventually, this work led him to leverage applied research and the discovery techniques developed for security and penetration testing to create runZero.
I’m thrilled to announce the release of Parallels Desktop 20 for Mac – the latest and greatest version of our product!
The biggest highlight is the new Parallels AI package, offering secure, downloadable pre-packaged virtual machines to quickly enhance AI developing skills in an offline environment.
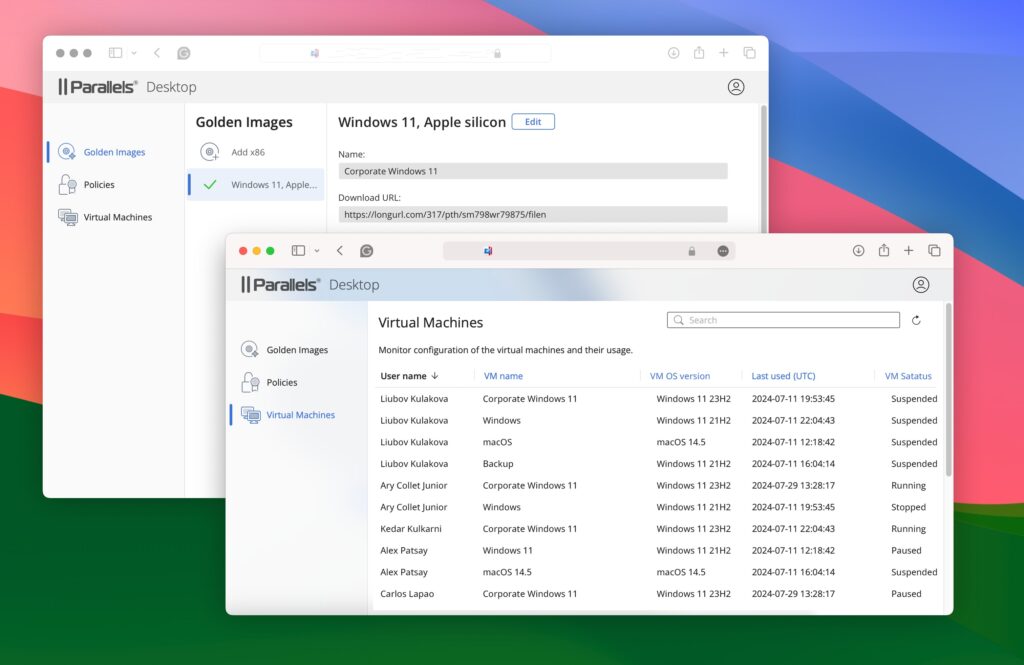
Parallels Desktop 20 is also ready for macOS Sequoia and Windows 11 24H2 and introduces a new Management Portal as a part of the new Enterprise Edition. It offers numerous updates for Windows, macOS and Linux VMs.
PS. Read all the way to the end for a fun Easter egg!
Ready for macOS Sequoia 15
The new Parallels Desktop 20 for Mac supports the upcoming macOS Sequoia (when released), improves the application stability on this operating system, and allows Mac users to enjoy AI-powered Writing Tools with Windows apps (requires macOS Sequoia 15.1).
This version decreases the use of deprecated APIs for content capture (such as CGDisplayStream and CGWindowListCreateImage), which now trigger system alerts that indicate they might be able to collect detailed information about the user. Instead, it moves to the recommended macOS API to ensure security and compliance.
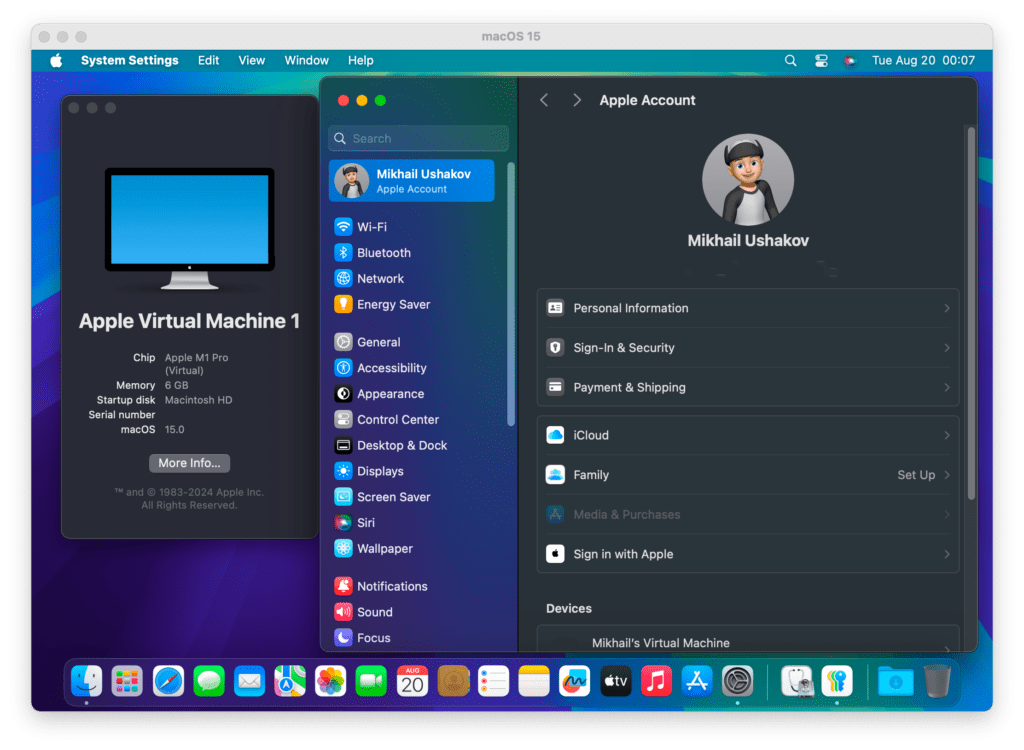
In addition, macOS Sequoia provides the ability to sign in to Apple ID in macOS virtual machines on Apple silicon!
This long-awaited improvement allows developers to fully leverage macOS virtual machines for building and testing software in an isolated environment.
Improving the stability and integration of this major Windows 11 update in a virtual environment has been a major goal since Windows 11 24H2 appeared in the Canary channel in early 2024.
These efforts include fixes for the NVMe driver, express Windows 11 installation on Intel-based Mac computers, mouse cursor positioning, and a fix for the dynamic resolution to sustain the ability to resize a Windows 11 VM window with automatic resolution adjustments.
From the Microsoft side, optimizations for the new major Windows 11 version 24H2 ensure users’ workflows remain uninterrupted while running legacy Windows apps (built for the Intel platform) and get up to 80% performance boost[1] for certain computational workloads thanks to the improved Prism emulator built into Windows 11 on Arm OS.
State of Windows apps on Apple silicon Macs
Contrary to popular belief, most Windows apps run just fine in Windows 11 on Arm – the version of Windows OS users run on a Mac with Apple silicon.
With the increased adoption of Apple silicon, Parallels Desktop became an essential tool for many professionals who need access to the Windows OS ecosystem – our customers happily run more than 200,000 Windows apps on their computers.
Parallels is proud to be the first Microsoft-authorized solution for running Arm versions of Windows 11 on Mac, helping to amplify the adoption of the Arm platform by software developers.
The latest release offers improved compatibility with ArcGIS Pro, LabVIEW, Ninja Trader, and other applications so you can now seamlessly install and run on a Mac with Apple silicon—all with the help of Parallels Desktop for Mac.
It’s also great to see software companies shift their strategy and start delivering product updates that run natively in Windows 11 on Arm which means more apps will soon become available for Apple silicon users. Recent examples include Malwarebytes ThreatDown, Opera browser, Adobe Illustrator, LibreOffice, and others.
Streamline your development workflow
The Parallels Desktop 20 release reflects our ongoing commitment to delivering the best environment for developers to build, automate, and test solutions on every major operating system (Windows, Linux, and macOS).
Let’s start with the Visual Studio Code extension for Parallels Desktop. This tool allows you to create and manage your Parallels Desktop virtual machines from a single user interface — and it’s becoming a popular choice, with over 50,000 downloads and counting.
This release introduces the ability to control virtual machines using natural language with Microsoft Copilot integrated into the Parallels Visual Studio Code extension.
DevOps and developers can use Parallels Desktop GitHub Actions to transform their CI/CD workflows, automating the deployment and management of virtual machines directly from their GitHub repository. Imagine triggering VM provisioning, testing, and configuration automatically as part of your GitHub Actions pipeline, eliminating manual steps, reducing errors, and accelerating your development process.
Enjoy the convenience of the Parallels Desktop DevOps Service to manage and orchestrate multiple Parallels Desktop hosts and virtual machines. Built to cater to the unique needs of DevOps teams, developers, and IT administrators, this service offers robust tools and automation capabilities that simplify the management of complex environments, enabling you to accelerate your software delivery process.
Perhaps the most exciting feature of this release is the introduction of the Parallels AI Package, now available in the extension catalog. These allow developers to start working and experimenting with AI at a low cost, with quick onboarding, and the ability to test on different configurations, including those without network access. Interested? Read more about AI VMs.
You can also join our Discord server to ask questions, share your experience, and get help from the community.
If you’re interested in macOS virtual machines…
For developers and DevOps who run macOS virtual machines on a Mac with Apple silicon, the new version delivers:
New! The ability to use snapshots to quickly save and restore the system state for an even more flexible development and testing process.
An improved Parallels Packer plugin for a faster macOS VM installation in express mode, automating the initial setup process using Apple Vision framework (OCR).
An enhanced Parallels executor for GitLab runner that now allows the use of macOS VMs on Apple silicon Mac computers.
Improvements for Linux fans
The Parallels Desktop team has listened to your feedback about the issues when running the newly released kernels inside Parallels Desktop virtual machines.
It’s well-known that the newest Linux kernels can sometimes be unstable and lead to compatibility challenges. However, we didn’t just acknowledge the issue — we took the first step to solve it.
Through careful analysis, the team discovered that nearly 50% of the reported issues were related to the Shared Folder driver operating within the kernel space.
Tackling this required adopting the high-level FUSE API, which should significantly reduce installation issues caused by kernel API changes in the near future.
This enhancement is designed to improve compatibility and ensure seamless support for future Linux distributions, reaffirming our commitment to providing you with a reliable and consistent virtualization experience.
This change also allowed us to improve performance for certain operations. You will feel the speed improvements when working with the volumes shared from Mac — now up to 4x faster than before[2].
Introducing Management Portal and Parallels Desktop Enterprise Edition — coming later this fall
I’m excited to announce a significant update that transforms how IT administrators manage Parallels Desktop virtual machines across their organizations.
The changes are based on user feedback, particularly how IT administrators have expressed the need for more advanced tools to manage their Parallels Desktop environments.
Common requests included the ability to control virtual machines remotely from a single interface, centralized monitoring of VM performance across the entire organization, and a more convenient way to deploy the virtual machines to endpoint Macs.
The Parallels Desktop team has taken this feedback to heart and are thrilled to introduce the Management Portal, which addresses these needs head-on.
To complement the release of the Management Portal, the Parallels Desktop Enterprise Edition is now available—it’s our most advanced offering yet.
Created for organizations that need more control, visibility, and efficiency in managing their large-scale virtual environments, the new Edition unlocks access to the new Management Portal.
And that’s just the beginning. The Enterprise Edition is packed with enhancements that will empower your IT team to operate more effectively and efficiently than ever before.
Stay tuned for further updates! If you’re eager to be among the first to experience these new capabilities, reach out to our sales team today for more details and to arrange an exclusive demo: https://www.parallels.com/products/desktop/enterprise/.
Streamline the deployment process
In the world of IT management, seamless software deployment is crucial.
However, some IT admins using Parallels Desktop have recently faced a challenging roadblock when deploying the application through some Mobile Device Management (MDM) providers.
The issue stemmed from the bundle structure of the deployment package, which, while powerful, was not widely supported by many MDM providers, e.g., Microsoft Intune.
As a result, admins were forced to find workarounds, such as deploying the software via custom scripts. Additionally, our customers reported the package can’t be run on Mac computers with macOS Sequoia.
The latest release introduces support for converting the existing bundle package into a flat package format, which is compatible with most MDM providers.
This simple yet powerful change ensures that IT admins can now deploy Parallels Desktop without resorting to complex scripts.
The flat package format maintains all the essential capabilities of the original bundle, including the ability to pass a license, configure policies, and deploy VMs with precision.
For MDMs with file size limitations, admins can now link a cloud-stored VM in the package, streamlining large deployments. The option to include the VM file in the package remains available.
To further enhance the deployment experience, Parallels has added the ability to always deploy the latest version of the Parallels Desktop application without needing to bundle the DMG file with each package.
This ensures that IT admins can use the time they used to spend on building a new package on other crucial tasks.
These advancements mark a significant milestone in our ongoing commitment to improving the IT admin experience. With these new features, deploying Parallels Desktop across a network of Macs is simpler and more flexible than ever before.
Parallels Desktop 20: The latest in a long line of innovations
Many years ago, a small group of enthusiasts embarked on a journey to create a product that, year after year, captured the hearts of more and more users worldwide: be it a Windows lover, a student, a developer, or an IT admin – Parallels is proud to serve so many different people worldwide.
Fun fact: Parallels Desktop launched publicly in June 2006 with version 2.5, which makes this release not an anniversary by age but rather yet another round number release. Stay tuned for anniversary easter eggs in 2026 😊.
Years later, Parallels Desktop became the leading solution for running Windows, Linux, and even macOS in a virtual environment – the only solution authorized by Microsoft to run Windows 11 on a Mac with Apple silicon!
And this is only the beginning. Look for more enhancements in the near future, making deployment and management an even smoother process for IT admins worldwide. Stay tuned for what’s next!
New to Parallels Desktop for Mac? Get your14-day free trialof Parallels Desktop 20.0.0 now.
[1] – Performance measurements conducted by Parallels by comparing the score produced by the x86 version of the test Floating Point Math from the Passmark 10 CPU Mark suite in Windows 23H2 (10.0.22621.3593) versus Windows 24H2 (10.0.26120.670) on MacBook Pro (M2 Max, (8+4) CPU, 96GiB RAM) with the virtual machine (4 CPU, 32GiB RAM). Measured using Parallels Desktop public version 19.4.1. The performance may vary based on usage, system configuration, and other factors.
[2] – Performance measurements conducted by Parallels by measuring the time it takes to copy 3000 (three thousand) files in 315 directories from the primary macOS 13.3 (22E252) to the Ubuntu Linux virtual machine (4 CPU, 8GiB RAM, Ubuntu Server 22.04) on MacBook Air (M2, (4+4) CPU, 32GiB RAM). Measured with a prerelease version of Parallels Desktop 20 versus the released version of Parallels Desktop 19. The performance may vary based on usage, system configuration, and other factors.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About Parallels Parallels® is a global leader in cross-platform solutions, enabling businesses and individuals to access and use the applications and files they need on any device or operating system. Parallels helps customers leverage the best technology available, whether it’s Windows, Linux, macOS, iOS, Android or the cloud.