Skip to content

What is an OTP bot, and how to protect yourself from it?

Imagine this: Your new accounting employee receives a call from what seems to be your company’s financial service provider. The caller sounds professional and mentions a suspicious transaction in the company’s account. 

Reassuring your employee that it’s a routine check, they ask for a one-time password (OTP) that has just been sent to secure the account. In a rush to safeguard the business, your employee shares the OTP—unaware they’ve fallen victim to a sophisticated scam involving an OTP bot.

Such real-life scenarios show how serious the threat of OTP bots has become in our digitalized environment. Understanding what OTP bots are and how to protect yourself from them is crucial to safeguarding your personal and business information. Let’s take a closer look at this emerging threat and explore ways to defend against it.

What is an OTP bot?

An OTP bot is a malicious automated software that cybercriminals use to steal one-time passwords (OTPs). OTPs are temporary verification codes sent to a user’s phone or email as part of two-factor authentication (2FA) or multi-factor authentication (MFA) processes. These codes provide extra security for online accounts, ensuring that even if someone knows your password, they still need the OTP to gain unauthorized access.

OTP bots exploit the trust and urgency associated with these security codes, tricking users into revealing their OTPs. Once the bot obtains the OTP, it can bypass security measures and access personal data and accounts.

How do OTP bots work?

OTP bots operate through a combination of social engineering and automated technology. Here’s how they typically work:

  1. The attacker initiates contact with the victim, often posing as a legitimate entity such as a bank, service provider, or even a tech support representative. The goal is to trick a user by creating a sense of urgency and trust, convincing them that sharing their OTP is necessary.

  2. Once the victim is convinced, the attacker uses an OTP bot to trigger a legitimate OTP request from the service provider. The attacker then attempts to log into the victim’s account using their credentials (often obtained through a previous phishing attack or data breach).

  3. The bot waits for the victim to receive the verification code and then relays the request to the victim, often through a phone call or text message. The bot uses convincing language and scenarios to persuade the victim to share their OTP.

  4. Once the bot receives the OTP from the victim, it immediately uses it to complete the login process, gaining unauthorized access to the victim’s account.

By automating this process, attackers can efficiently target multiple victims simultaneously, increasing their chances of success.

Process of OTP bot attacks

Understanding the step-by-step process of OTP-related attacks can help you recognize and avoid them. Let’s consider another example. You receive a call from someone claiming to be from a popular online retailer. They inform you that there is an issue with your recent order and they need to verify your identity to proceed with the correction.

They ask you to provide the verification code sent to your phone to confirm the changes. In reality, the caller is an attacker using an OTP bot. They have already initiated a password reset request on your retailer account, triggering the OTP.

As soon as you share the OTP code, the attacker uses it to change your account password and gain access, potentially making unauthorized transactions with your stored payment information. Here’s how these attacks typically unfold in a particular order:
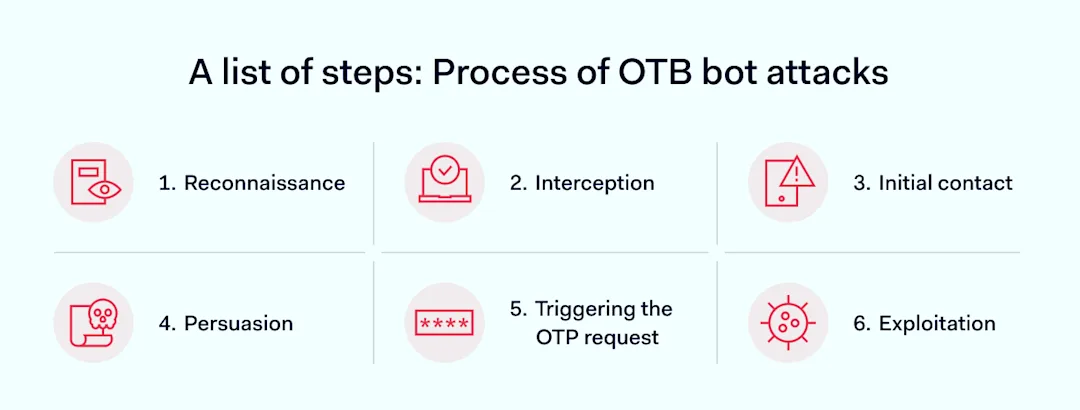
  1. Reconnaissance: Malicious actors gather information about potential targets through phishing emails, social media, and other online sources. This information helps them craft convincing scenarios for the social engineering phase.

  2. Initial contact: The attacker contacts the victim by phone, often using spoofed numbers or email addresses to appear legitimate. They create a sense of urgency or importance, prompting the victim to act quickly.

  3. Requesting the OTP: Using stolen login credentials, the attacker tries to log into the victim’s account, triggering an OTP request from the service provider.

  4. Interception: The attacker’s OTP bot waits for the victim to receive the OTP codes. The bot then contacts the victim, often through a phone call, claiming to need the OTP to resolve a supposed urgent issue.

  5. Persuasion: The bot uses persuasive language and convincing scenarios to convince the victim to share the OTP. This might involve claims of fraud prevention, account recovery, or urgent security updates.

  6. Exploitation: Once the OTP is obtained, the attacker uses it to complete the login process and gain unauthorized access to the victim’s account. This access can lead to unauthorized transactions, financial theft, data breaches, and other forms of cybercrime.

The impact of OTP bot attacks on organizations and networks

OTP bot attacks can have severe consequences for both individuals and organizations. Beyond what was mentioned earlier, here are some potential impacts:

  • Financial loss: Unauthorized access to accounts can result in significant financial losses, particularly for businesses handling large sums of money

  • Data breaches: Access to sensitive data can lead to data breaches, exposing personal and business data to misuse

  • Reputational damage: Victims of OTP-related attacks, especially businesses, can suffer reputational damage, while customers and clients may lose trust in the organization’s ability to protect their digital information

  • Operational disruption: Attacks can disrupt business operations, causing downtime and lost productivity

One notable example is the attack on Twitter in 2020, in which attackers used social engineering and OTP bots to gain access to high-profile accounts. They then used these accounts to promote a cryptocurrency scam, causing financial and reputational damage to the platform.

How to protect your business from OTP bots

Protecting your business from OTP threats involves a combination of technological solutions and best practices. Here are detailed strategies to safeguard your organization:

1. Implement multi-factor authentication (MFA)

Multi-factor authentication (MFA) is a critical safety measure that adds an extra layer of protection beyond passwords. Implement MFA to ensure that unauthorized access is prevented even if a password is compromised.

Consider MFA methods that don’t depend solely on text messages, such as app-based authenticators or hardware tokens, which are more secure alternatives. Additionally, integrate two-factor authentication (2FA) into your regular protocols, as it can significantly enhance your overall security posture.

2. Educate employees

Employee awareness is a key component in defending against all kinds of threats. Regularly train your employees about the risks of OTP bots and social engineering tactics. Ensure they recognize suspicious requests for OTPs or other sensitive information.

Develop clear security protocols for verifying the legitimacy of such requests, and encourage employees to report any unusual or suspicious activity immediately.

3. Monitor & analyze

Keep monitoring your systems for early detection of OTP threats. Use advanced analytics tools to track and analyze user behavior, looking for patterns indicating an ongoing or attempted attack.

Implement monitoring solutions that provide real-time insights and alerts about anomalous activities. By maintaining a vigilant watch over your network and systems, you can quickly identify and respond to potential breaches before they cause significant damage.

4. Secure communication channels

Ensuring the security of communication channels used for OTP delivery is crucial. Choose encrypted communication methods to send OTPs, such as app-based authenticators or secure email services.

By encrypting your OTPs and other sensitive communications, you can prevent attackers from intercepting and using them to gain access to your systems.

5. Regularly audit security

Regular security audits help identify and address vulnerabilities in your authentication processes and overall security infrastructure. During these audits, assess the effectiveness of your current security protocols, review access controls, and test your systems for potential weaknesses.

Regularly auditing your security practices ensures that your defenses remain robust and up-to-date.

Tools that can help mitigate OTP bot risks

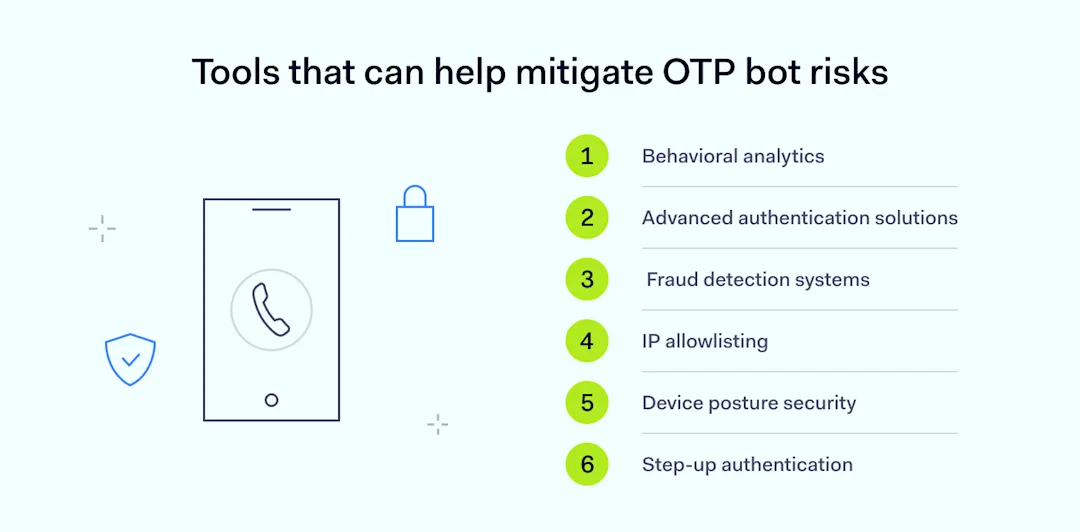
To keep your organizational walls secure, some useful tools and technologies can help detect and prevent OTP bot attacks:
Behavioral analytics

Behavioral analytics tools can be instrumental in identifying and mitigating OTP threats. Tools designed to analyze user behavior and detect anomalies—that may indicate a security threat—provide real-time alerts and detailed reports, enabling organizations to respond swiftly to potential attacks and prevent unauthorized access.

Advanced authentication solutions

Implementing advanced authentication solutions can significantly enhance security against attacks. Tools like Google Authenticator offer more secure methods for generating and verifying one-time passwords.

Such solutions reduce reliance on text messages, which are more vulnerable to interception by OTP bots. Using app-based authenticators or hardware tokens adds an extra layer of security, making it harder for attackers to infiltrate.

Fraud detection systems

Fraud detection systems can help detect and prevent fraudulent activities, such as an OTP bot attack. These systems use advanced algorithms and machine learning to analyze transaction patterns and identify suspicious behavior.

By integrating these systems into your security protocols, you can proactively detect and mitigate potential threats before they result in unauthorized transactions or data breaches.

IP allowlisting

Even if an attacker has access to your credentials, including a one-time password (OTP), they still won’t be able to connect to sensitive databases or tools without the correct IP address. With IP allowlisting, only pre-approved IP addresses are granted access to your network, adding a critical layer of security.

NordLayer supports this by enabling organizations to create virtual private gateways with fixed IP addresses, ensuring that unauthorized users are blocked, even if they possess valid login credentials.

Device posture security

Device posture security helps prevent unauthorized devices from accessing sensitive resources. With features like NordLayer’s Device Posture Security (DPS), organizations can ensure that only approved devices—whether personal or company-issued—are granted access. Even if an attacker has all the correct login credentials, access will be restricted if they’re not using a recognized, authorized device. This adds another layer of protection, ensuring that only compliant devices can interact with your network.

Step-up authentication

Step-up authentication involves implementing additional verification steps when high-risk activities are detected. For example, suppose a user logs in from a new location or attempts a high-value transaction. In that case, the system can require additional authentication methods, such as biometric verification or a hardware token. This approach ensures that only legitimate users can perform sensitive actions, reducing the risk of unauthorized transactions.

These tools and technologies can help businesses significantly reduce the risk of OTP threats and protect their data. Staying vigilant and implementing these security measures is essential to maintaining a robust defense against evolving threats.

Best practices for enhancing security against OTP bots

To enhance your security posture against OTP bots, consider the following practices:

  • Regular software updates. Update all software and systems regularly to fix security holes. Keeping everything up to date helps protect against known vulnerabilities.

  • Implement strong password policies. Enforce complex and unique passwords for different accounts. Use password managers to help you manage and generate secure passwords and regularly prompt password changes.

  • Train your employees. Conduct regular training sessions to inform employees about the latest phishing tactics, social engineering schemes, and specific threats, such as OTP bots. Establish protocols for verifying unusual requests for sensitive information.

  • Encrypt communication channels. Encrypted messaging services or app-based authenticators, including OTPs, are used to transmit sensitive information. Avoid SMS-based OTPs for critical transactions due to their vulnerability to interception.

  • Conduct regular security audits. Perform periodic security audits to identify vulnerabilities and weaknesses in your authentication processes. Work with third-party security experts to conduct comprehensive audits and provide improvement recommendations.

  • Develop a robust incident response plan. Create a well-defined incident response plan for managing and mitigating the impact of security breaches. Include steps for responding to OTP bot attacks, such as isolating affected systems and notifying stakeholders.

  • Implement access controls & the principle of least privilege. Ensure employees have access only to the resources necessary for their roles. Regularly review and adjust access permissions, and utilize role-based access control (RBAC) to manage user permissions.

  • Use threat intelligence & monitoring services. Integrate threat intelligence services for real-time information about emerging threats. Continuous monitoring tools and security information and event management (SIEM) systems should be used to detect suspicious activities early.

  • Stay informed about new threats. Stay updated on new threats, vulnerabilities, and best practices by participating in industry forums, attending conferences, and subscribing to security bulletins. Proactively adapt your security measures based on the latest developments.

Conclusion

While OTP bots pose a serious threat, staying vigilant and proactive puts you in the strongest position to prevent their constantly evolving tactics. OTP attacks will only grow more advanced if we fail to upgrade our defenses. Here are the core items to remember:

  1. Conduct regular employee training to spotlight the latest social engineering techniques. Aware, informed staff are your first line of prevention.

  2. Implement robust, at least two-factor authentication wherever possible. Removing reliance on single-factor OTPs starves bots of their favorite phishing fuel.

  3. Consider additional verification for high-risk events like fund transfers. Extra authentication layers prevent bots’ most enticing break-in targets.

Cybersecurity is an ongoing process that needs effort and adaptation. While challenges will always exist, empowering your organization with strategic security practices makes you resilient against sophisticated online threats. Stay proactive and keep your digital defenses strong.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Why Every CISO Needs to Understand Why NAC is Necessary for Cybersecurity

As cybersecurity threats become more sophisticated, the idea that “NAC is necessary” takes on even greater significance. Network Access Control (NAC) has become a crucial defense in protecting organizational assets from a wide range of attacks. For Chief Information Security Officers (CISOs), understanding NAC’s complexities enables them to make informed decisions that strengthen their organizations’ security strategies. This blog will explore NAC’s essential role in modern cybersecurity, highlighting its integration within the broader Zero Trust framework and its impact on risk management, cost efficiency, and regulatory compliance.

The Rising Importance of Network Access Control in Modern Cybersecurity

The landscape of corporate networks has undergone a seismic shift, transforming from well-defined perimeters to sprawling ecosystems of interconnected devices. This evolution has introduced unprecedented complexity and vulnerabilities, necessitating a more sophisticated approach to network security. Cybercrime is predicted to inflict damages totaling $9.5 trillion USD globally in 2024. Network Access Control (NAC) has emerged as an indispensable mechanism for navigating this intricate environment, offering robust solutions to modern cybersecurity challenges.

The dynamic nature of today’s networked world, characterized by the ubiquity of Bring Your Own Device (BYOD) policies and the exponential growth of the Internet of Things (IoT), has significantly expanded the attack surface. Traditional security measures are no longer adequate to address the nuanced threats posed by this ever-growing array of devices. NAC provides a critical layer of defense by meticulously identifying, authenticating, and authorizing devices that seek to connect to the network, ensuring that only compliant and secure devices are granted access.

The increasing adoption of remote work further amplifies the importance of NAC. As employees access corporate resources from diverse locations and devices, maintaining rigorous control over network access becomes essential. NAC enables organizations to enforce security policies uniformly, irrespective of where or how users connect to the network. This capability is vital in mitigating risks associated with remote work environments, ensuring that security protocols are upheld even beyond the traditional office perimeter.

Additionally, NAC’s real-time visibility into device activity equips organizations with the insights needed to proactively manage security. By continuously monitoring the security posture of connected devices, NAC allows for immediate detection and response to anomalies, thereby curbing potential threats before they escalate.

In essence, Network Access Control is not merely a tool but a strategic imperative in the contemporary cybersecurity landscape. Its ability to adapt to the complexities of modern networks, coupled with its stringent enforcement of security policies, makes NAC a cornerstone of any robust cybersecurity strategy.

How NAC Integrates with a Zero Trust Security Framework

In the increasingly perilous digital landscape, the Zero Trust model has risen as the zenith of security paradigms. Central to this model is the philosophy of “never trust, always verify.” Network Access Control (NAC) is pivotal in manifesting this principle, embedding stringent access controls and continuous verification into the network architecture.

NAC’s sophisticated authentication mechanisms extend beyond mere user credentials, scrutinizing devices for compliance with organizational security policies. By evaluating parameters such as endpoint configuration, software patch levels, and real-time threat intelligence, NAC ensures that only devices meeting rigorous security standards can access the network. This granular level of scrutiny fortifies the Zero Trust ethos, significantly diminishing potential vectors for cyber intrusion.

Additionally, NAC seamlessly complements Zero Trust by facilitating micro-segmentation. This strategic division of the network into isolated segments restricts lateral movement, effectively quarantining threats and preventing them from propagating. By enforcing access controls on a segment-by-segment basis, NAC enables organizations to limit the scope of breaches and contain damage efficiently.

The dynamic adaptability of NAC further enhances the Zero Trust framework. As new vulnerabilities emerge, NAC’s real-time policy enforcement allows for swift recalibration of security measures. This agility ensures that security protocols remain robust against evolving threats, maintaining a proactive security posture.

Integrating NAC with Zero Trust also leverages contextual awareness, whereby access decisions are informed by real-time data and situational analysis. This context-aware access control ensures that network permissions are granted based on the current security posture and threat environment, providing an additional layer of defense. By synchronizing NAC’s capabilities with the overarching Zero Trust framework, organizations can achieve a resilient, adaptive security architecture that stands resilient against sophisticated cyber threats.

Minimizing Cybersecurity Risks with NAC Implementation

Implementing Network Access Control (NAC) is a powerful way to strengthen your organization’s security and reduce cybersecurity risks. NAC provides CISOs with granular control over network access, allowing only authenticated, authorized, and compliant devices to connect. Here are several key techniques NAC uses to minimize cybersecurity risk:

  • Enforcing access control: Only authorized devices can connect, preventing unauthorized access to the network.
  • Automatic remediation: If a device doesn’t meet compliance standards, NAC can automatically quarantine the device, apply security patches, or prompt users to fix issues before gaining access.
  • Real-time visibility and monitoring: NAC continuously monitors device behavior and network activity, using advanced analytics to detect suspicious patterns and potential breaches.
  • Custom security policy enforcement: NAC allows you to tailor access controls to specific needs without sacrificing operational efficiency, maintaining security even as threats evolve.
  • Optimized incident response: NAC enables faster response by correlating access data with threat intelligence, allowing security teams to act quickly and accurately.

By incorporating NAC into your cybersecurity strategy, your organization can adopt a proactive, resilient, and adaptable defense against today’s most sophisticated threats.

Optimizing Your Cybersecurity Budget with NAC

In today’s climate of stringent budget scrutiny, Network Access Control (NAC) stands out as a strategic linchpin for optimizing cybersecurity expenditures. Integrating NAC within your security framework not only fortifies defenses but also enhances the efficiency of existing security investments, offering a dual advantage of robust protection and cost-effective operations.

One of the most compelling financial benefits of NAC is its ability to centralize and streamline security management. By consolidating access control mechanisms, NAC reduces the administrative overhead associated with juggling multiple security tools. This centralization facilitates seamless coordination among different security solutions, enabling automation of routine tasks and freeing up cybersecurity personnel to focus on more strategic initiatives. The resultant operational efficiency translates into significant cost savings and more effective use of human resources.

Furthermore, NAC’s proactive approach to threat prevention diminishes the financial impact of security breaches. By enforcing rigorous access controls and continuously monitoring network activity, NAC helps avert incidents that could lead to substantial monetary losses, whether through direct damage, regulatory fines, or the reputational fallout from compromised data. The return on investment (ROI) with NAC is substantial, extending beyond immediate financial metrics to encompass broader organizational resilience and stability.

NAC also contributes to optimized resource allocation by offering actionable insights through real-time visibility into device behavior and network traffic. These insights empower security teams to prioritize and address vulnerabilities with precision, reducing the need for broad, and often costly, blanket security measures. In essence, NAC enables a more targeted, efficient, and economical approach to cybersecurity, ensuring that your budget is deployed where it is most needed and effective.

By integrating NAC, organizations can achieve a harmonious balance of enhanced security and fiscal prudence, positioning themselves to meet evolving threats with agility and confidence.

Ensuring Compliance Through NAC

Navigating the labyrinth of regulatory compliance demands both precision and diligence. Network Access Control (NAC) emerges as an indispensable ally in this endeavor, ensuring your organization adheres to stringent data protection standards and avoids the crippling repercussions of non-compliance. Network Access Control (NAC) plays a critical role in meeting the stringent cybersecurity requirements set forth by the National Institute of Standards and Technology (NIST) in its Special Publication 800-53 and other major compliance standards.

NAC’s robust access policies are instrumental in aligning with regulatory frameworks such as GDPR, HIPAA, and others. By systematically controlling who can access sensitive data and under what conditions, NAC establishes a verifiable chain of custody over your digital assets. This meticulous oversight is crucial for maintaining compliance and providing irrefutable evidence during audits.

Furthermore, NAC offers unparalleled transparency into network activities, documenting every access attempt and flagging any deviations from established security policies. This level of granularity is essential for compliance reporting, facilitating a seamless audit process, and showcasing your commitment to upholding regulatory standards.

Automated compliance checks are another significant advantage of NAC. These tools continuously monitor and enforce adherence to security protocols, ensuring that your organization remains compliant even as regulatory landscapes evolve. This proactive stance not only mitigates the risk of compliance violations but also positions your organization as a trustworthy custodian of sensitive information.

In addition to satisfying regulatory requirements, NAC’s comprehensive logging and reporting capabilities enhance your organization’s overall security posture. Detailed logs of access attempts and remediation actions offer valuable insights, enabling you to fine-tune security measures and bolster defenses against future threats.

Ultimately, incorporating NAC into your cybersecurity strategy provides a dual benefit: fortifying your defense mechanisms and ensuring unwavering compliance. This strategic integration empowers you to navigate the complexities of regulatory landscapes with confidence and precision, safeguarding your organization against both cyber threats and regulatory penalties.

Conclusion

Network Access Control (NAC) is essential for any CISO seeking to strengthen their organization’s cybersecurity posture. With its ability to enforce stringent access controls, provide real-time visibility, and integrate seamlessly with a Zero Trust framework, NAC addresses the complexities of modern cyber threats head-on. From minimizing risks to optimizing budgets and ensuring compliance, NAC offers a proactive and adaptable solution that empowers organizations to stay ahead of evolving threats and maintain a resilient defense. Understanding and implementing NAC is no longer optional—it’s a strategic necessity for robust cybersecurity.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

Perforce Launches New State of Open Source Survey in Collaboration With the Eclipse Foundation and Open Source Initiative

MINNEAPOLIS, SEPTEMBER 17, 2024 – Perforce Software, the DevOps company for global teams requiring speed, quality, security and compliance at scale along the development lifecycle, today launched its annual survey exploring open source software (OSS) usage in organizations worldwide. The survey’s findings will be the foundation for the 2025 State of Open Source Report, which offers a comprehensive assessment of the current landscape of OSS technologies and trends. This year’s survey was developed through a joint effort led by OpenLogic by Perforce in collaboration with the Eclipse Foundation and the Open Source Initiative (OSI). 

“We are delighted to partner once again with both the Eclipse Foundation and Open Source Initiative,” said Tzvika Shahaf, VP of Product Management at Perforce. “This year, we have added a new section on Big Data infrastructure, since data technologies was identified as one of the biggest areas of investment in the 2024 report. We hope to gain a better understanding of how enterprises are managing their Big Data stacks and the challenges they face.”

The survey, which will close on November 1, asks questions related to the day-to-day use and management of OSS, as well as governance and maturity. Response data will be compiled into a detailed report, with sections focused on different technology categories (i.e. operating systems, databases, programming languages) and topics such as security and compliance. 

The Eclipse Foundation is proud to participate in the 2025 State of Open Source survey and report. We view it as essential to our work of championing open source development and innovation,” said Thabang Mashologu, VP of Community and Outreach at the Eclipse Foundation. “The State of Open Source Report always provides invaluable insights that enable us to better support our community of open source contributors and organizations that rely on OSS for their business-critical applications.”

Since it was first published in 2019, the State of Open Source Report has been cited in numerous industry reports, as well as shared at top open source conferences around the world.

“This is our fourth year being involved in the State of Open Source Report, and there is never any shortage of surprises in the data,” said Stefano Maffulli, Executive Director, Open Source Initiative. “Now, however, the aim of the survey is not to determine whether or not organizations are using open source — we know they are — but to find out how they are handling complexities related to AI, licensing, and of course, security.”

Anyone using open source in their organization is invited to complete the 2025 State of Open Source Survey

About the Eclipse Foundation
The Eclipse Foundation provides our global community of individuals and organizations with a business-friendly environment for open source software collaboration and innovation. We host the Eclipse IDE, Adoptium, Software Defined Vehicle, Jakarta EE, and over 425 open source projects, including runtimes, tools, specifications, and frameworks for cloud and edge applications, IoT, AI, automotive, systems engineering, open processor designs, and many others. Headquartered in Brussels, Belgium, the Eclipse Foundation is an international non-profit association supported by over 350 members. To learn more, follow us on social media @EclipseFdn, LinkedIn or visit eclipse.org.


About the Open Source Initiative
The Open Source Initiative (OSI) is the steward of the Open Source Definition, setting the foundation for the global open source ecosystem. Founded in 1998, OSI protects and promotes open source software, development and communities, championing software freedom in society through education, collaboration and infrastructure. The OSI is a 501(c)3 non-profit, and anyone interested in supporting the defense of Open Source Definitions can join today at https://join.opensource.org.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Perforce
The best run DevOps teams in the world choose Perforce. Perforce products are purpose-built to develop, build and maintain high-stakes applications. Companies can finally manage complexity, achieve speed without compromise, improve security and compliance, and run their DevOps toolchains with full integrity. With a global footprint spanning more than 80 countries and including over 75% of the Fortune 100, Perforce is trusted by the world’s leading brands to deliver solutions to even the toughest challenges. Accelerate technology delivery, with no shortcuts.

New Microsoft macOS Flaws: What MSPs Are Doing to Keep You Safe

Key Takeaways:

  • Critical Vulnerabilities Discovered: New security flaws in Microsoft macOS apps could potentially grant hackers unrestricted access to sensitive systems, posing a significant threat to businesses using these platforms.
  • Increased Risk to Organizational Data: If exploited, these vulnerabilities could allow cybercriminals to bypass security protocols, leading to unauthorized access, data breaches, and severe financial and reputational damage.
  • The Vital Role of MSPs: Managed Service Providers (MSPs) are essential in keeping businesses secure by regularly updating systems, implementing robust cybersecurity measures, and responding swiftly to new threats.

Intro

With digital threats ever-present, the recent identification of significant flaws in Microsoft macOS applications highlights the urgent demand for strong cybersecurity protocols. Managed Service Providers (MSPs) are actively protecting businesses against potential exploitation, ensuring organizational safety from cyber threats. Grasping these vulnerabilities, their consequences, and the essential role of MSPs aids businesses in managing the intricate cybersecurity environment of today.

The Emergence of Critical Vulnerabilities in Microsoft macOS Apps

The cybersecurity landscape has been jolted by the revelation of critical vulnerabilities in Microsoft’s macOS applications. These flaws have the potential to open a backdoor for cybercriminals, granting them unrestricted access to sensitive systems and data. Microsoft has continually strived to fortify its security measures, but this latest discovery underscores a critical reality: no platform is immune to sophisticated cyber threats. As businesses increasingly rely on Microsoft’s macOS apps for their daily operations, the urgency to address these vulnerabilities becomes paramount. This situation highlights the rapid pace at which cyber threats evolve, outpacing even the most robust security measures. Organizations must recognize the inherent risks associated with these vulnerabilities, which could lead to unauthorized data access, theft, and a slew of malicious activities. The impact on businesses could be far-reaching, with potential financial repercussions and long-term damage to reputation. The emergence of these vulnerabilities serves as a stark reminder of the dynamic nature of cyber threats, emphasizing the need for businesses to remain vigilant and proactive in their cybersecurity efforts.

Understanding the Impact of These Vulnerabilities on Businesses

The ramifications of these vulnerabilities for businesses reliant on Microsoft’s macOS applications are profound. When cybercriminals exploit these flaws, they can bypass existing security measures and gain unauthorized access to sensitive data. This kind of breach can trigger a cascade of negative outcomes, including significant financial losses and irreparable harm to a company’s reputation. Regulatory penalties could further compound the financial strain, while the erosion of customer trust can lead to a long-term decline in business. Operational disruptions might also ensue, potentially halting key business functions for extended periods. In a landscape where data integrity is paramount, the exploitation of such vulnerabilities could undermine competitive advantage, impede strategic goals, and necessitate costly and time-consuming remediation efforts. Consequently, robust cybersecurity protocols are essential not just for protecting data but for preserving the very fabric of an organization’s operational stability and market standing.

The Role of MSPs in Cybersecurity Management

Managed Service Providers (MSPs) play a pivotal role in the cybersecurity ecosystem, offering an indispensable layer of protection for businesses, especially those without dedicated in-house IT security teams. By leveraging MSPs, organizations can tap into a pool of specialized knowledge and cutting-edge technologies designed to safeguard against cyber threats. MSPs provide continuous monitoring and management of IT systems, ensuring they are fortified with the latest security patches and protocols. This proactive stance allows them to detect and address vulnerabilities before they can be exploited, maintaining a secure digital environment for their clients.

MSPs excel in their ability to offer tailored solutions that meet the unique security needs of different organizations. Their expertise extends to implementing advanced cybersecurity frameworks, such as intrusion detection systems and firewalls, that form the backbone of a robust defense strategy. Additionally, MSPs perform regular security audits to identify potential weaknesses and ensure compliance with industry standards and regulations.

Beyond technological safeguards, MSPs also focus on the human element of cybersecurity. They provide comprehensive training programs to educate employees on best practices and the latest threat vectors, minimizing the risk of human error leading to breaches. This holistic approach ensures that every facet of an organization’s digital ecosystem is protected.

By staying abreast of the latest developments in the cybersecurity landscape, MSPs can swiftly adapt their strategies to counter new and emerging threats. This agility, combined with their deep expertise and proactive measures, makes MSPs an invaluable ally in the ongoing battle to secure organizational data and maintain operational integrity.

Strategies MSPs Use to Identify and Mitigate Cyber Threats

MSPs deploy a multifaceted approach to shield organizations from cyber threats. One key strategy is continuous monitoring of network activity, which enables real-time detection of anomalies that could indicate potential breaches. This vigilance allows for swift action, mitigating risks before they escalate. Regular system audits are another cornerstone, helping to identify and rectify vulnerabilities ahead of any exploitation. Advanced cybersecurity frameworks, including robust firewalls and sophisticated intrusion detection systems, form the bedrock of their defense tactics. These tools are complemented by the implementation of stringent security protocols that are consistently updated to counter new threats. Additionally, MSPs recognize the crucial role of human factors in cybersecurity. They offer comprehensive training programs designed to educate employees on the latest threat vectors and best practices, significantly reducing the risk of human error leading to breaches. By integrating these diverse strategies, MSPs create a fortified digital environment that proactively defends against a wide array of cyber threats.

Staying Ahead of Emerging Cyber Threats

The digital threat landscape is in a constant state of flux, making it imperative for businesses to stay ahead of emerging cyber threats. MSPs play a critical role in this ongoing battle by leveraging advanced technologies and methodologies to predict and counteract potential risks. One of the key strategies employed by MSPs is the use of artificial intelligence and machine learning to identify patterns and anomalies that could signal new types of cyberattacks. These advanced analytics tools provide real-time insights, allowing for preemptive measures that neutralize threats before they can cause harm.

Moreover, MSPs maintain a rigorous schedule of threat intelligence updates. By subscribing to global threat intelligence feeds, they stay informed about the latest vulnerabilities, attack vectors, and cybercriminal tactics. This information is then used to adjust and fortify security protocols dynamically, ensuring that defenses are always one step ahead. Additionally, MSPs collaborate with cybersecurity communities and forums to share knowledge and gain insights from other experts in the field, fostering a collective defense against sophisticated attacks.

Another crucial aspect of staying ahead involves continuous employee education. MSPs conduct regular training sessions that focus on the latest threat vectors and security best practices. This not only equips employees with the knowledge to identify and avoid potential threats but also fosters a culture of cybersecurity awareness throughout the organization. By combining technological innovation with human vigilance, MSPs create a comprehensive defense strategy that is both adaptive and resilient.

Ultimately, the proactive measures taken by MSPs serve as a critical buffer, ensuring that businesses are not just reacting to threats but are actively prepared to counteract them.

The Essential Partnership Between Businesses and MSPs

The relationship between businesses and MSPs extends beyond a mere service agreement; it is a strategic alliance rooted in mutual trust and a shared commitment to cybersecurity. MSPs bring specialized knowledge, state-of-the-art technologies, and proactive monitoring to the table, offering a level of protection that most organizations would struggle to achieve on their own. For businesses, engaging with an MSP means gaining access to a dedicated team of experts who are constantly vigilant, ensuring that systems are secure and compliant with the latest industry standards.

A key aspect of this partnership is the seamless integration of MSPs into a business’s existing operations. This includes not just the deployment of technical solutions, but also continuous education and training for employees, fostering a culture of cybersecurity awareness throughout the organization. MSPs work closely with businesses to tailor security strategies that align with specific needs and risk profiles, providing a customized defense against cyber threats.

Open communication is another cornerstone of this relationship. Regular updates and transparent reporting from MSPs keep businesses informed about their security posture, potential vulnerabilities, and ongoing efforts to mitigate risks. This collaborative approach ensures that both parties are aligned in their objectives, creating a resilient framework capable of adapting to the ever-changing cyber threat landscape.

At Guardz, we understand the critical role MSPs play in the cybersecurity ecosystem. That’s why we have forged strong partnerships with MSPs to provide comprehensive security solutions tailored to their clients’ unique needs. By leveraging our advanced cybersecurity platform, MSPs can offer their clients robust protection against emerging threats, such as the recently discovered vulnerabilities in Microsoft macOS apps. Guardz equips MSPs with the tools and insights they need to monitor, manage, and mitigate risks effectively, ensuring that their clients’ digital assets remain secure in an increasingly hostile cyber environment. With Guardz, MSPs can confidently protect their clients while enhancing their service offerings, ultimately delivering peace of mind and security at every level.

Conclusion: Ensuring Resilience in the Face of Cyber Adversity

The recent vulnerabilities in Microsoft’s macOS applications serve as a crucial reminder of the ever-present cyber threats that businesses face. Managed Service Providers (MSPs) stand at the forefront of cybersecurity, offering the expertise and proactive measures necessary to counteract these risks. By partnering with MSPs, businesses can leverage advanced technologies and continuous monitoring to stay ahead of emerging threats. This collaboration fosters a resilient digital environment, allowing organizations to focus on their core operations without compromising on security. In this dynamic threat landscape, maintaining robust cybersecurity protocols and engaging with knowledgeable MSPs are essential steps in safeguarding your business’s future.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Guardz
Guardz is on a mission to create a safer digital world by empowering Managed Service Providers (MSPs). Their goal is to proactively secure and insure Small and Medium Enterprises (SMEs) against ever-evolving threats while simultaneously creating new revenue streams, all on one unified platform.

Understanding SaaS compliance: key standards and best practices

Software as a Service (SaaS) has become the backbone of many businesses, offering scalable and cost-effective solutions for various industries. However, with the convenience of SaaS comes the critical responsibility of ensuring SaaS compliance with industry standards and data protection laws.

For those new to SaaS, understanding SaaS compliance can be daunting, but it is crucial for protecting sensitive data, building customer trust, and avoiding legal pitfalls. This guide will walk you through the basics of SaaS compliance, covering key standards, common challenges, and best practices to help you keep your business on the right track.

What is SaaS compliance? 

SaaS compliance means that software-as-a-service providers have to follow various regulatory requirements, laws, and industry-specific standards. These standards are designed to protect sensitive data, ensure financial transparency, and maintain security protocols across cloud-based services. For SaaS providers, compliance is not just a legal obligation but is also about demonstrating their commitment to safeguarding customer data and upholding industry benchmarks.

For instance, consider a company that offers cloud-based solutions for managing healthcare records. To operate legally and securely, the company must comply with the Health Insurance Portability and Accountability Act (HIPAA), which sets strict standards for protecting sensitive patient information. Without HIPAA compliance, the company could face fines, lose customers, and suffer reputational damage.

Why is SaaS compliance important?

Understanding why SaaS compliance is important is crucial for any business operating in the SaaS space. Compliance serves two primary purposes: protecting data security and maintaining customer trust.

Data security

With data breaches becoming an everyday threat, robust SaaS compliance practices help SaaS providers safeguard their customers’ data against security risks. Compliance frameworks like the General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA) impose stringent requirements on how companies collect, store, and process personal data. Failure to comply can lead to severe penalties and legal consequences.

For example, in 2023, Meta was fined $1.3 billion for GDPR violations. The company failed to ensure adequate protections for user data during transfers between the EU and the U.S. This shows how important it is to prioritize data security and compliance to avoid substantial legal penalties.

Customer trust

Compliance also plays a crucial role in building and maintaining customer trust. When customers know that a SaaS provider follows compliance frameworks like PCI DSS (Payment Card Industry Data Security Standard) or SOC 2 (Service Organization Control 2), they feel more confident that their data is secure. This trust is essential for long-term business relationships and customer retention.

Risks of non-compliance

The risks of non-compliance are significant. They include legal penalties, financial loss, reputational damage, and operational disruptions. Companies that fail to meet compliance standards may also find it challenging to attract and retain customers as trust in their services diminishes. In extreme cases, non-compliance can lead to business shutdowns, especially if the violations are severe.

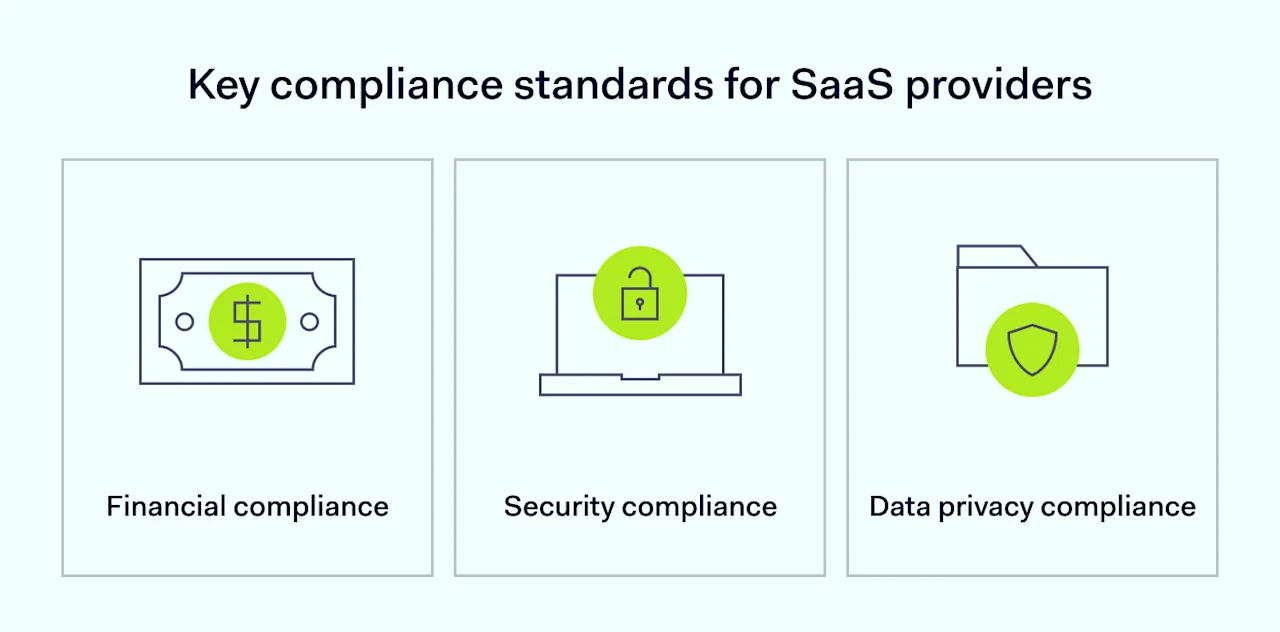
Key compliance standards for SaaS providers

To effectively manage compliance, SaaS providers must understand the types of SaaS compliance relevant to their industry. These compliance standards vary depending on the nature of the service, the type of data handled, and the geographical location of the customers. Here’s an overview of some major compliance frameworks.

Key compliance standards for SaaS providers

Financial compliance

Payment Card Industry Data Security Standard (PCI DSS)

PCI DSS is essential for any SaaS provider that handles payment card transactions. This standard outlines security measures to protect cardholder data, including data encryption, secure storage, and regular monitoring. Implementing solutions to become PCI compliant is crucial for preventing data breaches and maintaining customer trust.

Accounting Standards Codification (ASC 606)

ASC 606 provides guidelines for revenue recognition, ensuring that companies report their financial performance accurately. SaaS providers must comply with ASC 606 to demonstrate financial transparency and avoid legal issues related to revenue reporting.

Sarbanes-Oxley Act (SOX)

SOX compliance is mandatory for publicly traded companies, including SaaS providers. It focuses on corporate governance and financial reporting, requiring companies to implement internal controls and report on their effectiveness. Non-compliance with SOX can lead to severe penalties, including fines and imprisonment for executives.

Security compliance

Service Organization Control 2 (SOC 2)

SOC 2 compliance is a critical standard for SaaS providers that handle customer data. It ensures the company’s information security management systems meet industry standards. SOC 2 audits evaluate controls related to security, availability, processing integrity, confidentiality, and privacy. Achieving SOC 2 compliance is essential for demonstrating that your SaaS solutions are secure and reliable.

ISO/IEC 27001

ISO/IEC 27001 is an international standard for information security management systems. It provides a framework for managing and protecting sensitive information through a systematic approach. Implementing an ISO 27001 compliance solution can help SaaS providers safeguard their data, meet customer expectations, and improve overall security.

Center for Internet Security (CIS) Controls

The CIS Controls are a set of best practices for cybersecurity. They provide a prioritized set of actions to protect organizations from cyber threats. SaaS providers can use these controls to strengthen their security posture and reduce security risks, including breaches.

National Institute of Standards and Technology Cybersecurity Framework (NIST CSF)

The NIST CSF is a voluntary framework that provides guidelines for managing and reducing cybersecurity risks. SaaS providers can adopt it to enhance their security practices and ensure they are aligned with industry standards.

Data privacy compliance

General Data Protection Regulation (GDPR)

GDPR is a European Union regulation that governs how companies handle personal data. It applies to any SaaS provider that processes data belonging to EU citizens, no matter where the company is based. Compliance with GDPR is essential for avoiding hefty fines and protecting customer privacy. Companies can explore GDPR compliance services for tailored support.

HIPAA (Health Insurance Portability and Accountability Act)

HIPAA sets the standard for protecting sensitive patient information in the healthcare industry. SaaS providers that handle health-related data must comply with HIPAA to avoid penalties and ensure that patient information is kept confidential. Implementing HIPAA compliance solutions is vital for any SaaS provider operating in the healthcare sector.

CCPA (California Consumer Privacy Act)

The CCPA is a state law that grants California residents rights over their personal data. It requires businesses to disclose what information they collect, allow consumers to opt out of data sharing, and delete personal data upon request. SaaS providers must comply with CCPA to avoid legal penalties and maintain customer trust.

Data security and privacy regulations

Data security and privacy are at the heart of SaaS compliance. Data protection laws like GDPR, HIPAA, and CCPA are designed to protect individuals’ data from misuse and unauthorized access. These regulations require SaaS providers to implement strict security measures, such as data encryption, access controls, and regular monitoring, to ensure that data is protected at all times.

For example, a SaaS provider offering cloud storage services must ensure that data is encrypted at rest and in transit. This means that even if a malicious actor gains access to the data, they would not be able to read it without the decryption key.

Complying with data security and privacy regulations can help SaaS providers protect their customers’ information and avoid legal consequences.

Challenges in achieving SaaS compliance

Achieving SaaS compliance can be challenging for SaaS providers, especially those just starting. Here are some common challenges and potential solutions:

Complexity of regulations

SaaS compliance requirements can be complex and vary by industry and region. For example, a global SaaS provider may need to comply with multiple regulations, such as GDPR, CCPA, and HIPAA, each with unique requirements. To manage this complexity, SaaS providers can use SaaS compliance management tools that automate tracking and implementing regulatory requirements.

Resource constraints

Small and medium-sized SaaS companies often lack the resources for compliance efforts. Hiring compliance experts or outsourcing SaaS compliance can be expensive. However, non-compliance can be even more costly in the long run. To handle this, SaaS providers can focus on implementing the most critical compliance measures first and gradually expand their compliance efforts as their business grows.

Keeping up with changes

Compliance standards and data protection laws are constantly evolving, and SaaS providers must stay up-to-date with the latest changes to remain compliant. This requires continuous monitoring of regulatory updates and adjusting compliance practices as needed. An effective compliance strategy includes subscribing to industry newsletters, attending webinars, and participating in compliance forums to stay informed.

Benefits of SaaS compliance

While achieving SaaS compliance can be challenging, the benefits far outweigh the effort. Here are some key benefits:

Improved security

SaaS compliance ensures that providers implement robust security controls to protect customer data. This reduces the risk of data breaches and cyber-attacks, safeguarding both the company and its customers.

Enhanced customer trust

SaaS security compliance demonstrates to customers that their data is in safe hands, building trust and loyalty and leading to long-term customer relationships.

Competitive advantage

Compliant SaaS companies can differentiate themselves from competitors who may not offer the same level of security and privacy protection. This can be a significant selling point in a crowded market.

Best practices for maintaining SaaS compliance

Maintaining SaaS compliance is an ongoing process that requires constant attention. Here are some best practices to help:

Regular audits

Conduct internal and external audits regularly as part of your compliance strategy. Audits help assess your compliance status and identify any gaps in your security practices. They can also help you stay on top of compliance requirements and ensure that your SaaS solutions remain secure.

Employee training

Regularly train employees on SaaS compliance requirements and their role in maintaining it. An informed team is better equipped to follow measures and avoid potential compliance risks.

Usage of compliance management tools

Leverage compliance management tools to automate tracking and implementing regulatory requirements. These tools help reduce human error and ensure all compliance obligations are met. Additionally, use only SaaS-compliant tools for daily operations to create a secure environment and minimize risks. The more secure your operational tools, the stronger your overall compliance posture.

Document compliance efforts

Keep detailed records of your compliance activities, including policies, procedures, and audit results. This documentation is crucial during an audit or regulatory inquiry.

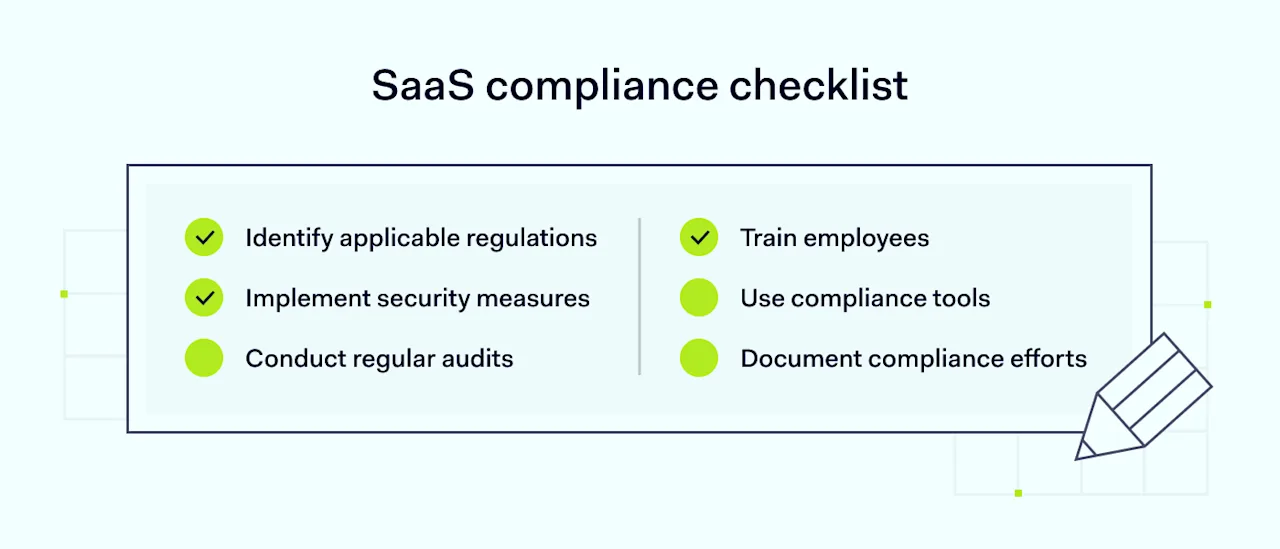
SaaS compliance checklist

To help you get started, here’s the SaaS compliance checklist of key steps.

SaaS compliance checklist

  • Identify applicable regulations: Determine which compliance standards (like GDPR, HIPAA, or PCI DSS) apply to your SaaS business

  • Implement security measures: Ensure your platform meets all security requirements, such as encryption and access controls

  • Conduct regular audits: Schedule regular audits to assess your compliance and identify areas for improvement

  • Train employees: Provide ongoing training to ensure employees understand their compliance responsibilities

  • Use compliance tools: Implement tools to automate and streamline your compliance tasks

  • Document compliance efforts: Keep detailed records of your compliance activities, including financial compliance measures and the implementation of security controls.

How can NordLayer help companies stay compliant?

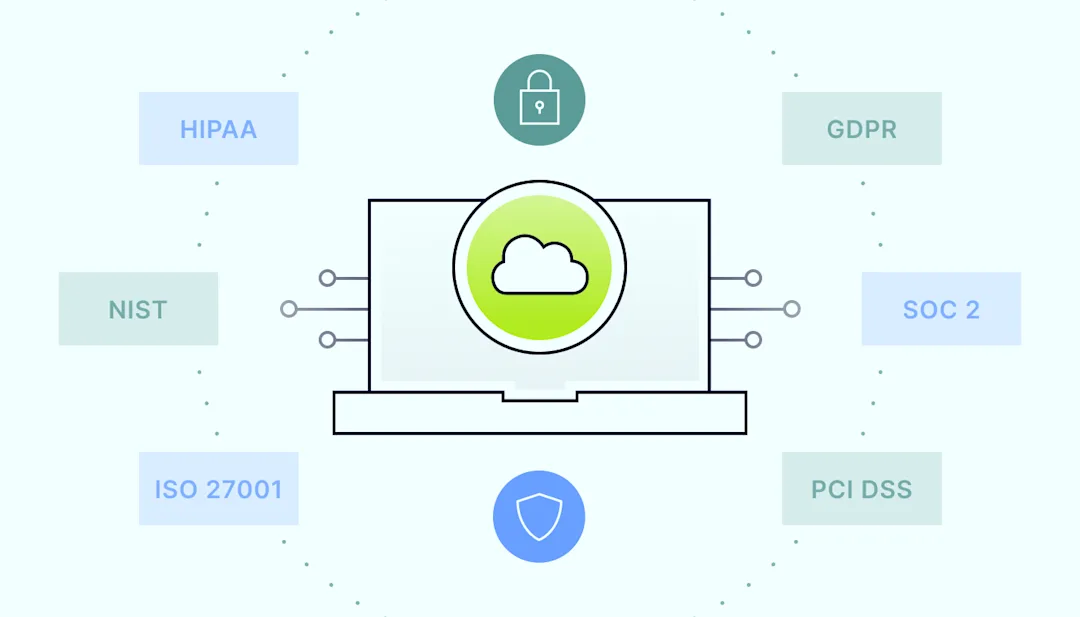
NordLayer itself meets multiple compliance standards for securing applications and services, including GDPR, HIPAA, ISO 27001, and PCI DSS. Compliance often requires specific network security measures, such as traffic encryption, advanced network access control, and multi-factor authentication.

NordLayer addresses these needs by providing robust security features designed to meet these requirements. By integrating NordLayer, you can enhance the security of your SaaS solutions, ensuring they align with compliance standards and protect sensitive data effectively.

Conclusion

SaaS compliance is a critical aspect of running a successful software-as-a-service business. By understanding and adhering to key compliance standards, SaaS providers can protect their customers’ data, build trust, and avoid legal pitfalls. While achieving compliance can be challenging, the benefits—including improved security, customer loyalty, and competitive advantage—make it well worth the effort.

By following best practices and leveraging tools like NordLayer, you can navigate the complex world of SaaS compliance with confidence and ensure your business’s long-term success.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.