Skip to content

New GPU-Enabled Hardware Release Delivers Accelerated Performance From Scale Computing

Introducing the HC3450FG for Data-Intensive Applications and AI Workloads

INDIANAPOLIS — September 4, 2024 — Scale Computing, a market leader in edge computing, virtualization, and hyperconverged solutions, today announced the release of the HC3450FG, the first new appliance in its HC3000 series of Scale Computing Hardware. Designed to deliver exceptional performance, flexibility, and ease of management, the HC3450FG is a cutting-edge hyperconverged infrastructure solution with integrated NVIDIA L4 24GB advanced GPU capabilities.

In today’s rapidly evolving IT landscape, businesses face increasing demands for performance, efficiency, and scalability. Traditional IT infrastructure often struggles to keep pace with these requirements, leading to bottlenecks and costly downtime. Organizations need solutions that can handle processing massive datasets, running simulations, real-time rendering, or managing advanced computational tasks beyond what can be accomplished with CPU resources while still maintaining ease of management and affordability. To meet these demands, Scale Computing remains dedicated to delivering innovative, right-sized solutions that simplify management, optimize performance, and provide exceptional value. The company’s latest offering, the HC3450FG, delivers on this promise.

“The HC3450FG marks a significant milestone in Scale Computing’s HC3000 hardware series,” stated Jeff Ready, CEO and co-founder of Scale Computing. “Unlike traditional servers that can struggle with high-intensity workloads, our newest appliance offers customers a seamless and high-performance experience for demanding applications. The GPU-enabled architecture provides the computational muscle to handle large datasets and complex algorithms with ease, making the HC3450FG the ideal solution for anyone tackling data-intensive workloads and AI inferencing applications. It’s also incredibly flexible in terms of configuration, making it scalable and cost effective. The appliance is a true testament to our commitment to delivering cutting-edge technology for the evolving needs of our customers.”

Designed to meet the escalating demands of modern enterprise environments, the HC3450FG leverages the power of NVIDIA L4 24GB advanced GPU capabilities to seamlessly blend power with efficiency. Recognizing the diverse needs of its customers, Scale Computing engineered the HC3450FG to be highly customizable. With the flexibility to configure individual GPU units and storage options, organizations can tailor the appliance to align with their specific workload requirements. This building block approach enables businesses to optimize their investment while also ensuring infrastructure can effortlessly scale to accommodate future growth.

Key Benefits of the HC3450FG:

  • Unmatched Performance: Leverage the power of market-leading NVIDIA L4 GPUs to accelerate demanding workloads and achieve exceptional results.
  • Optimized for AI: Handle complex AI models and algorithms efficiently with Scale Computing’s GPU-accelerated platform built for data-intensive workloads.
  • Flexibility and Scalability: Customize the HC3450FG to meet specific needs and avoid overprovisioning.
  • Simplified Management: Benefit from Scale Computing’s user-friendly SC//Platform for easy deployment and management.

The HC3450FG represents a strategic investment for organizations seeking to elevate their IT capabilities. By seamlessly integrating advanced GPU technology with Scale Computing’s proven hyperconverged infrastructure, businesses can unlock unprecedented performance, efficiency, and innovation. To explore how the HC3450FG can transform your IT operations, please contact Scale Computing.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Scale Computing 
Scale Computing is a leader in edge computing, virtualization, and hyperconverged solutions. Scale Computing HC3 software eliminates the need for traditional virtualization software, disaster recovery software, servers, and shared storage, replacing these with a fully integrated, highly available system for running applications. Using patented HyperCore™ technology, the HC3 self-healing platform automatically identifies, mitigates, and corrects infrastructure problems in real-time, enabling applications to achieve maximum uptime. When ease-of-use, high availability, and TCO matter, Scale Computing HC3 is the ideal infrastructure platform. Read what our customers have to say on Gartner Peer Insights, Spiceworks, TechValidate and TrustRadius.

Parallels 推出 Parallels Desktop 20 搭載 AI 虛擬機器,簡化 AI 應用程式開發

香港 — 2024 年 9 月 10 日 — 全球領先的跨平台虛擬化解決方案供應商 Parallels 今天正式發布 Parallels Desktop 20 for Mac。這新版本標誌著 AI 技術引入的一個重要里程碑,提供了安全、可下載的 AI 虛擬機器,能夠離線管理和操作,大幅簡化 AI 應用開發流程。Parallels Desktop 20 完全兼容 macOS Sequoia 和 Windows 11 24H2,並在全新企業版中加入管理平台,同時還針對 Windows、macOS 和 Linux 虛擬機器進行多項升級。 

Parallels Desktop 是唯一獲得 Microsoft 授權,可在 Apple Silicon 虛擬化運行 Windows 的解決方案,為開發者和用戶提供更多在其偏好環境中進行開發和操作的選擇。

Parallels 的 CTO Prashant Ketkar 表示:「隨著 AI 技術逐漸成為每台個人電腦的標準,我們相信開發者將需要迅速更新其應用程式,以充分利用這些 AI 功能。因此,我們推出了 Parallels AI 套件,讓無論是專業團隊還是初學者都能輕鬆使用 AI 模型和代碼建議,幫助獨立軟件開發商(ISV)在短短幾分鐘內打造 AI 支援的應用程式,顯著提升使用 Mac 的開發團隊的工作效率。」

Parallels Desktop 20 的主要功能包括:

  • 全新 Parallels AI 套件:一體化的解決方案預載 14 種 AI 開發工具、範例代碼和指導,讓開發者能夠快速實驗並部署 AI 應用。用戶只需一下點擊,即可下載 AI 就緒的 Parallels 虛擬機器,並在完全離線狀態下運行第三方語言模型。該套件提供安全的離線環境,允許自訂資源並禁用網絡存取,強化私隱保護。
  • macOS Sequoia 兼容性:用戶可在 Windows 應用中使用 Apple 的 AI 寫作工具,並在 Apple Silicon 的 macOS 虛擬機器上登入 Apple ID(隨 macOS Sequoia 發布)。
  • 支援 Windows 11 24H2:提升舊版 Windows 應用的性能,某些工作負載在 Windows 11 上的執行速度可提高至 80%。
  • 無縫兼容 Windows 應用:透過全新共享文件夾技術,提升多種應用和安裝程式的性能,讓 Mac 文件在 Linux 虛擬機器上的操作速度提升至 4 倍。

針對企業用戶:

  • 全新企業版及管理平台:這是目前最先進的版本,專為需要更高控制權和可視性的公司企業設計,便於管理 Parallels Desktop 虛擬機器和安全策略。新版本提供進階授權選項,支援單一登入(SSO)和批量授權,並附帶進階支援和入門服務。
  • SOC 2 認證:Parallels Desktop 獲得 SOC 2 Type 2 認證,並定期進行第三方滲透測試,以維持安全性和可靠性。

針對 IT 專業人士和開發者:

  • 增強 DevOps 服務:在 Windows、Linux 和 macOS 虛擬機器上構建軟件,無論您身處何地。
  • Visual Studio Code 的強化擴展:簡化了 AI 套件的使用,並整合了 Microsoft Copilot,讓用戶可透過自然語言控制虛擬機器。
  • Snapshots 和 OCR-powered Packerr:增強了 Apple Silicon Mac 上 macOS 虛擬機器的功能。

Parallels Desktop for Mac 是專業人士、開發者和個人的必備虛擬化工具,無論是用來存取 Windows 應用、開發或測試軟件,還是在 Mac 上同時運行多個操作系統(如 Windows、Linux 或其他版本的 macOS)。

關於 Parallels
Parallels 是全球領先的跨平台解決方案品牌,為公司企業和個人用戶提供簡單的方式,讓他們在任何設備或操作系統上使用和存取所需的應用程式和檔案。無論是 Windows、Mac、ChromeOS、iOS、Android 還是雲端服務,Parallels 都能幫助客戶充分利用最佳技術。Parallels 解決了複雜的工程與使用者體驗問題,讓企業和個人用戶能夠隨時隨地簡單且具成本效益地使用應用程式。

關於 Version 2 Digital
Version 2 Digital 是亞洲最有活力的IT公司之一,公司發展及代理各種不同的互聯網、資訊科技、多媒體產品,其中包括通訊系統、安全、網絡、多媒體及消費市場產品。透過公司龐大的網絡、銷售點、分銷商及合作夥伴,Version 2 Digital 提供廣被市場讚賞的產品及服務。Version 2 Digital 的銷售網絡包括中國大陸、香港、澳門、台灣、新加坡等地區,客戶來自各行各業,包括全球1000大跨國企業、上市公司、公用機構、政府部門、無數成功的中小企及來自亞洲各城市的消費市場客戶。

Removal Notice

本公司之顧客服務中心地址 (提貨地址) 將於 2024 年 9 月 9 日 (星期一) 遷往新地址如下:

Unit 1105, 11/F, AXA Tower, Landmark East, 100 How Ming Street, Kwun Tong, Kln, Hong Kong

電話及傳真號碼維持不變。

Sales Hotline: (852) 2893 8860 / Email: sales@version-2.com.hk 
Support Hotline: (852) 2893 8186 / Email: support@version-2.com.hk
Fax: : (852) 2893 8214

Thank you for your kind attention. 

Yours faithfully,
Version 2 Limited


Proven fingerprinting techniques for effective CAASM

One of the key components of runZero’s ability to provide asset discovery, exposure management, and attack surface management data is its ability to identify an asset’s operating system (OS), hardware, and services aka fingerprinting. This is often performed with very little or even conflicting data.  

In this blog, we explore commonly used fingerprinting techniques and gain insights from the runZero Research Team on their approach to deciphering a real-world fingerprinting challenge. Let’s go!

Fingerprinting concepts

For the purposes of this blog, “fingerprinting” is defined as the process of trying to identify, with as much precision as possible, some aspect of an asset. There can be significant variation in the precision that can be achieved when fingerprinting. With certain data we may be able to identify the operating system and exact build number. With different data, it may only be possible to vaguely bucket the asset into an OS family such as “Windows” or “Linux.” For services we can sometimes even determine the programming language it was written in and perhaps a range of language versions that may have been used. All outcomes can be possible against the same asset depending on which protocols and services we can observe.

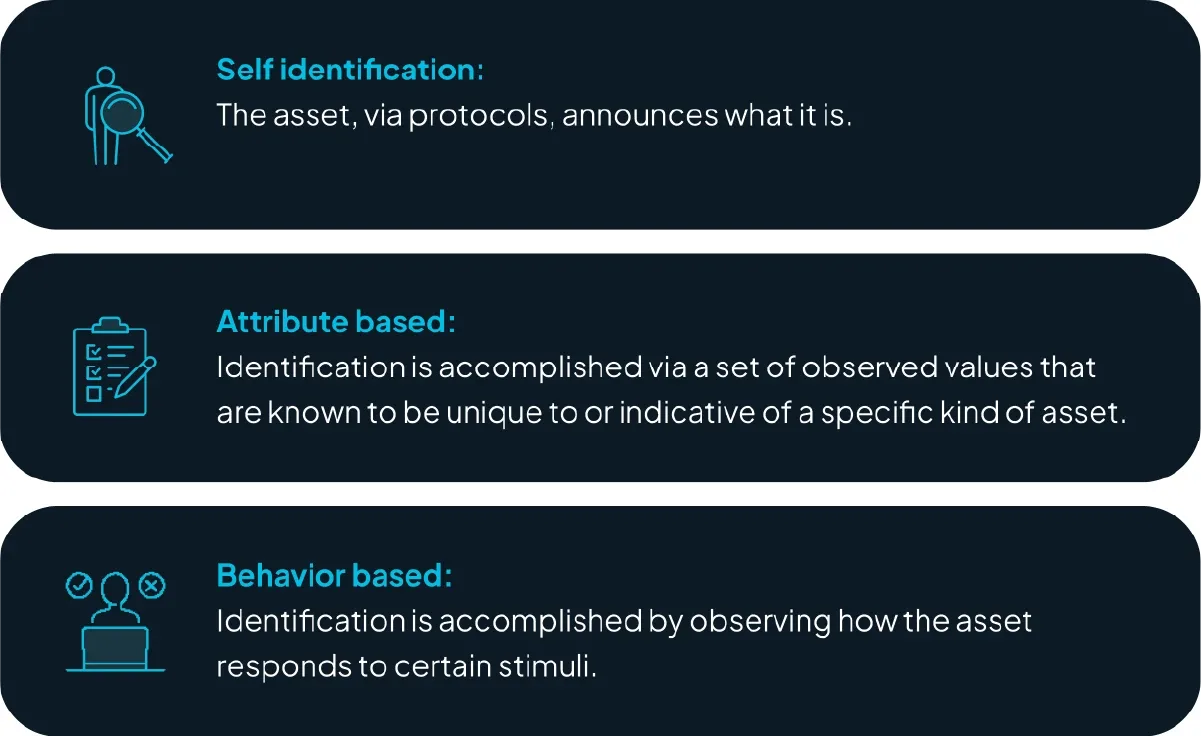
Fingerprinting techniques generally fall into one of three categories:

An example of self identification based fingerprinting would be an SSH MOTD banner of “Red Hat Enterprise Linux Server release 5.11 (Tikanga)”. That is pretty straightforward and doesn’t require any additional data. Attribute based fingerprinting, which we will discuss further in the next sections, includes looking at various response and data attributes such as TCP field values such as MSS or Window Scale. Behavior based techniques typically take more work to find and implement. An example would be when a particular OS or service implementation drops a TCP connection only when sent a certain payload at a particular stage in protocol negotiation.

A hat by any other name #

Identifying the OS of a network-connected system, without credentials, and with minimal services, has always been a game of precision. Some of the trickiest examples are the forks of the Red Hat Enterprise Linux (RHEL) distribution.

CentOS and certain other Linux distributions such as Oracle Linux were originally forks or “bug and binary compatible” redistributions of Red Hat Enterprise Linux. The relationship changed in 2021 when Red Hat, which acquired CentOS in 2014, discontinued CentOS Linux and created CentOS Stream. With this change CentOS would no longer be downstream of RHEL but would instead be the upstream source from which RHEL is created. The logical flow has since changed again and now has Fedora as the root with both CentOS Stream and RHEL downstream. In response to CentOS Linux being discontinued two new distributions were created: AlmaLinux OS and Rocky Linux.

Often, the only real difference between these distributions is the replacement of Red Hat trademarks and branding with that of the particular Linux project. In many cases, these distributions are byte-for-byte identical at the software package and network levels. These present a challenge to remote fingerprinting as a result.

To overcome these challenges, we collect and analyze enormous amounts of data. Our first pass at trying to differentiate the RHEL derivatives used a combination of two attributes, such as SSH version negotiation strings and the TCP Receive Window size. Over time, we realized this wasn’t going to be sufficient and that we needed more and better data.

Analyzing data at scale is useful, but in situations like this it is vital to know exactly what combination of distribution and version leads to what results. For this effort we built hundreds of virtual machines running as many versions of the different distributions as we could. In some cases, these releases were over two decades old!

Verify target, one SYN only #

From each of these virtual machines we collected as much information as we could about how the TCP stack communicated. While it is true that fingerprinting an operating system via TCP stack quirks has been a thing for years, our challenge was to improve our detection while sending the absolute minimum amount of traffic and, importantly, to look for evidence that would persist through common configuration changes by the system administrators.

To explain our findings, we first need to define some terms:

  • TCP Receive Window: Maximum amount of data that a particular endpoint can receive and buffer. The sending host has to stop after sending the maximum amount of data and wait for ACK and window updates.

  • MTU: Maximum Transmission Unit, which is the largest packet that the network interface can accept.

  • MSS: Maximum Segment Size, which is the maximum amount of TCP data that can fit into a single packet, calculated as the MTU minus the protocol headers.

  • TCP Window Scale: An optional factor by which the TCP Receive Window is scaled; this allows receive windows to exceed the maximum of 65535 bytes that can be specified in the TCP Receive Window field.

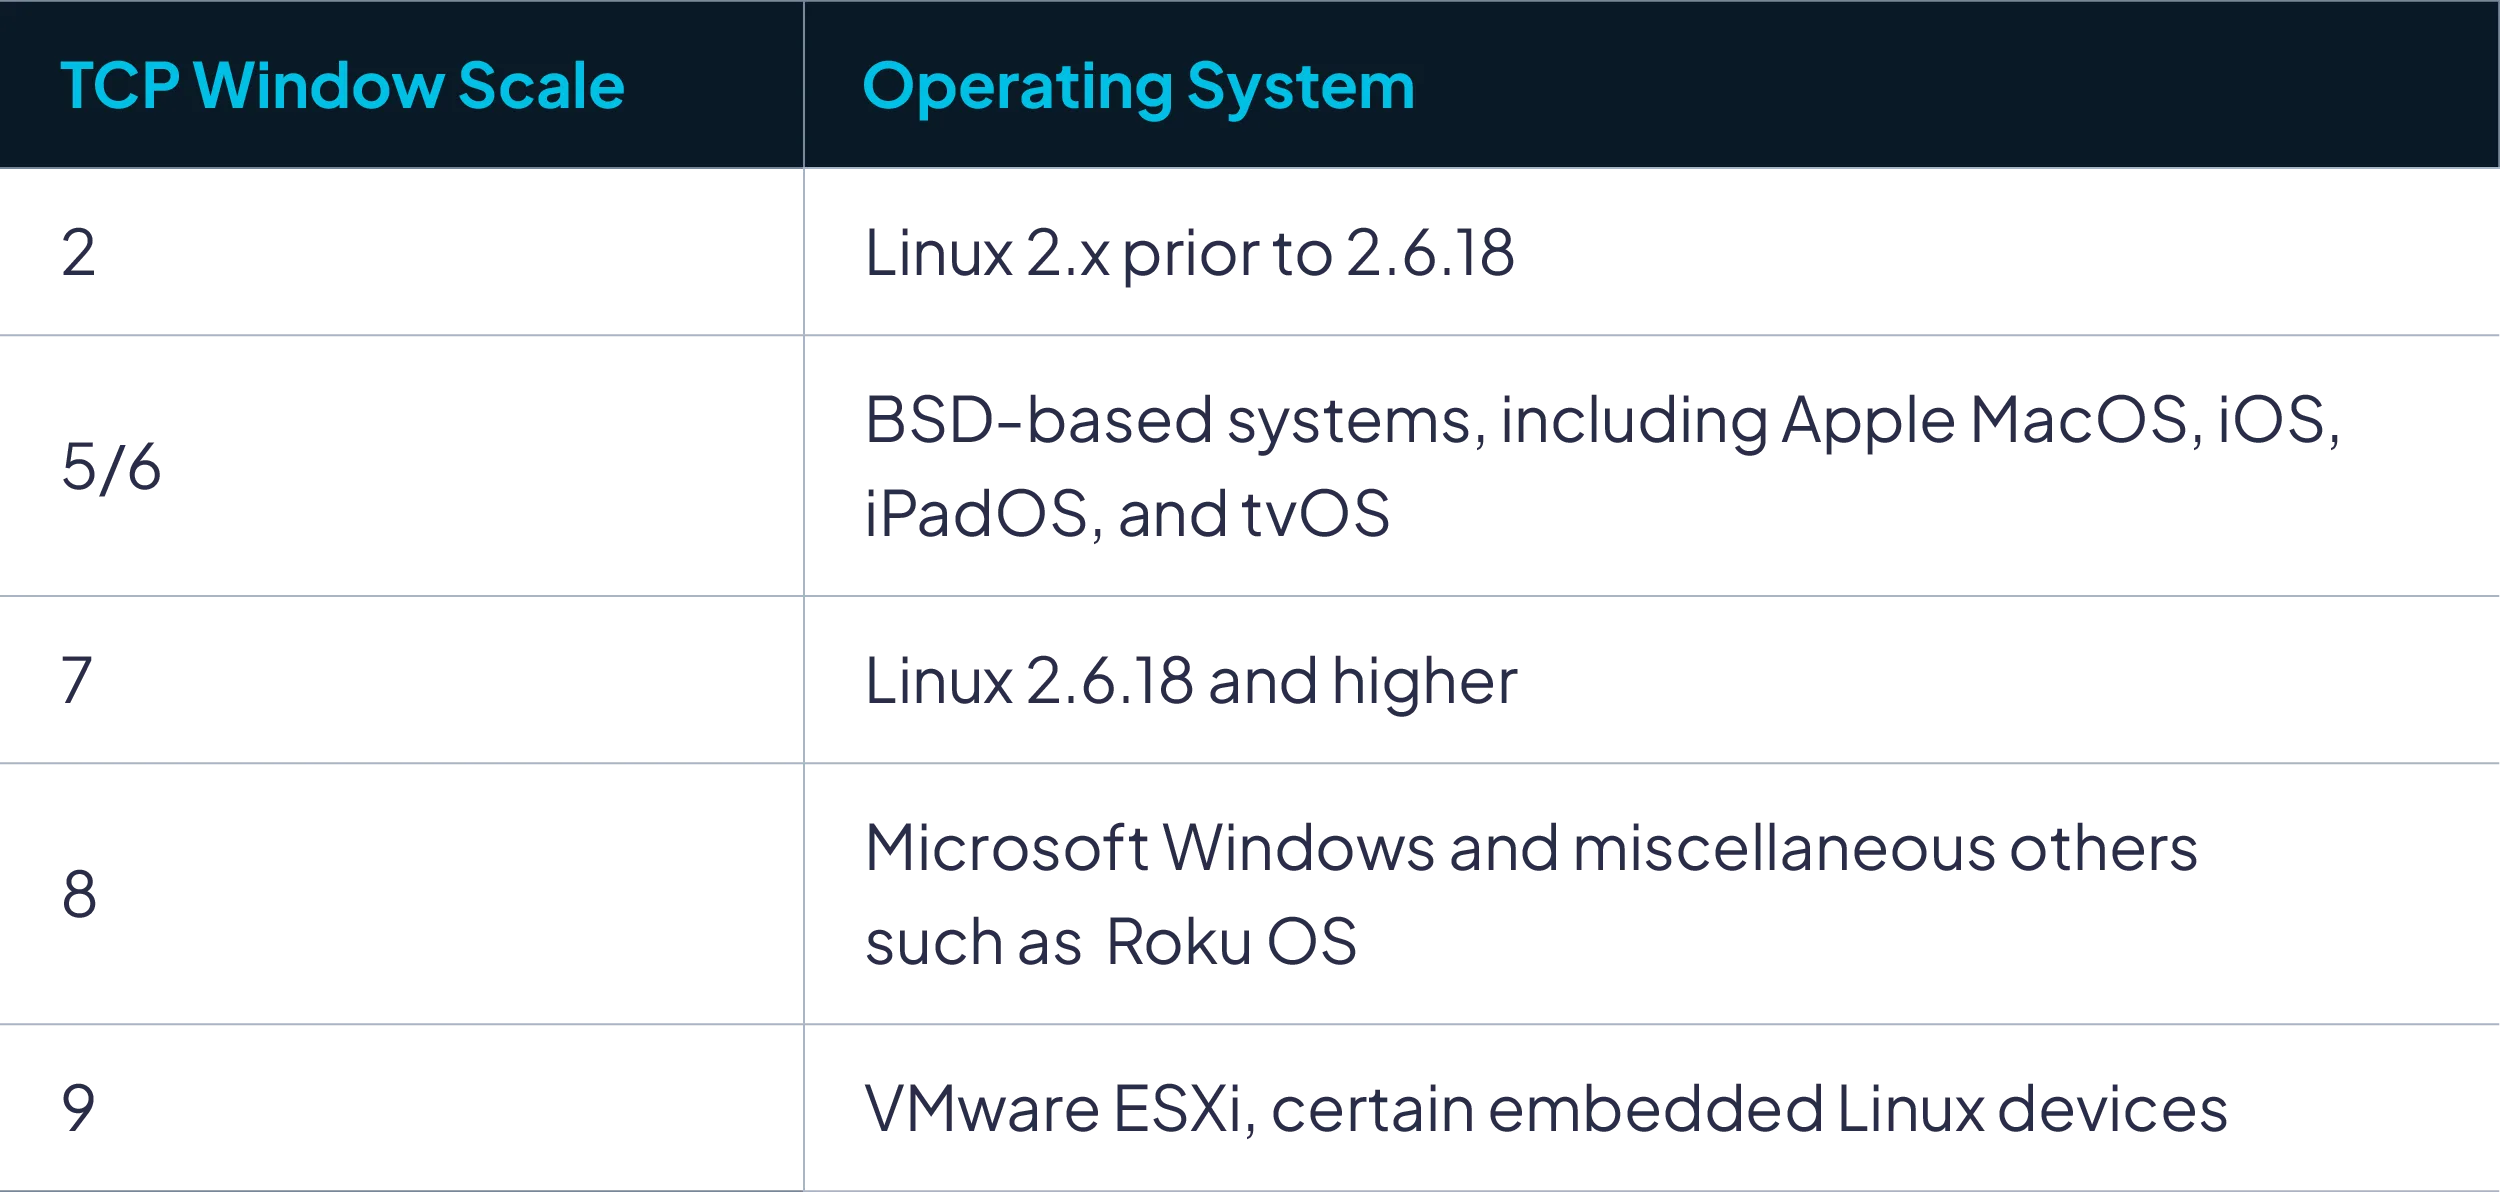
Of the TCP attributes that we observed, the one that provided the murkiest fingerprinting results was the TCP Window Scale. The values for it, when present, range from 0 to 14. With this information, we can usually determine if the target is running a general family of operating systems.

FIGURE 1 – TCP Window Scale by operating system.

Combining the TCP Receive Window and MSS offered the next significant improvement. In our past work, leveraging the Receive Window size sometimes yielded values that seemed to change unexpectedly. The reason why became clear when we looked at the data from the lab.

The key points were:

  • Changes to the link-layer MTU impacts the value of MSS, since MSS is calculated as the MTU minus the size of certain TCP/IP headers.

  • MSS is different between IPv6 and IPv4 due to the IPv6 IP headers being 20 bytes larger.

  • For Linux-based systems, Receive Windows less than the maximum value were almost always an even multiple of MSS. Due to the MSS difference mentioned above this means that the Receive Windows would vary as well.

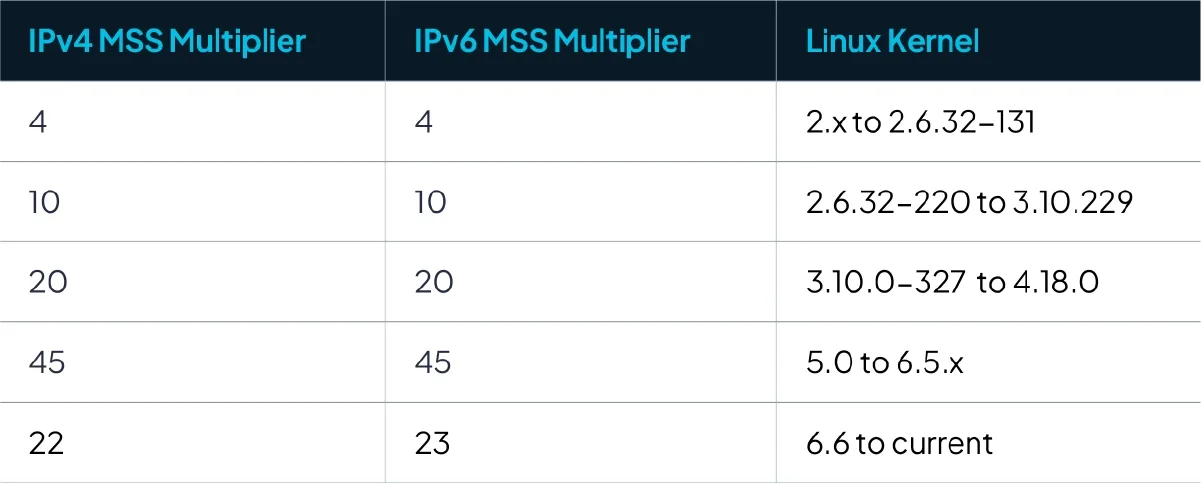
  • Critically, the MSS multiplier for Linux-based OSs correlated with the Linux kernel version.

With the information above in hand, we can organize Linux systems into specific kernel version buckets based on the observed multiplier. That is quite a bit of information from the response to a single SYN packet!

FIGURE 2 – Relationship between IPv4/IPv6 MSS Multiplier and Linux Kernel version.

The kernel version also offers a hint as to the relative age of the system. A MSS multiplier of 4 indicates that the machine is likely running an ancient version of Linux, far beyond EOL, and certainly not something that should still be in production.

A little from column A, a little from column B #

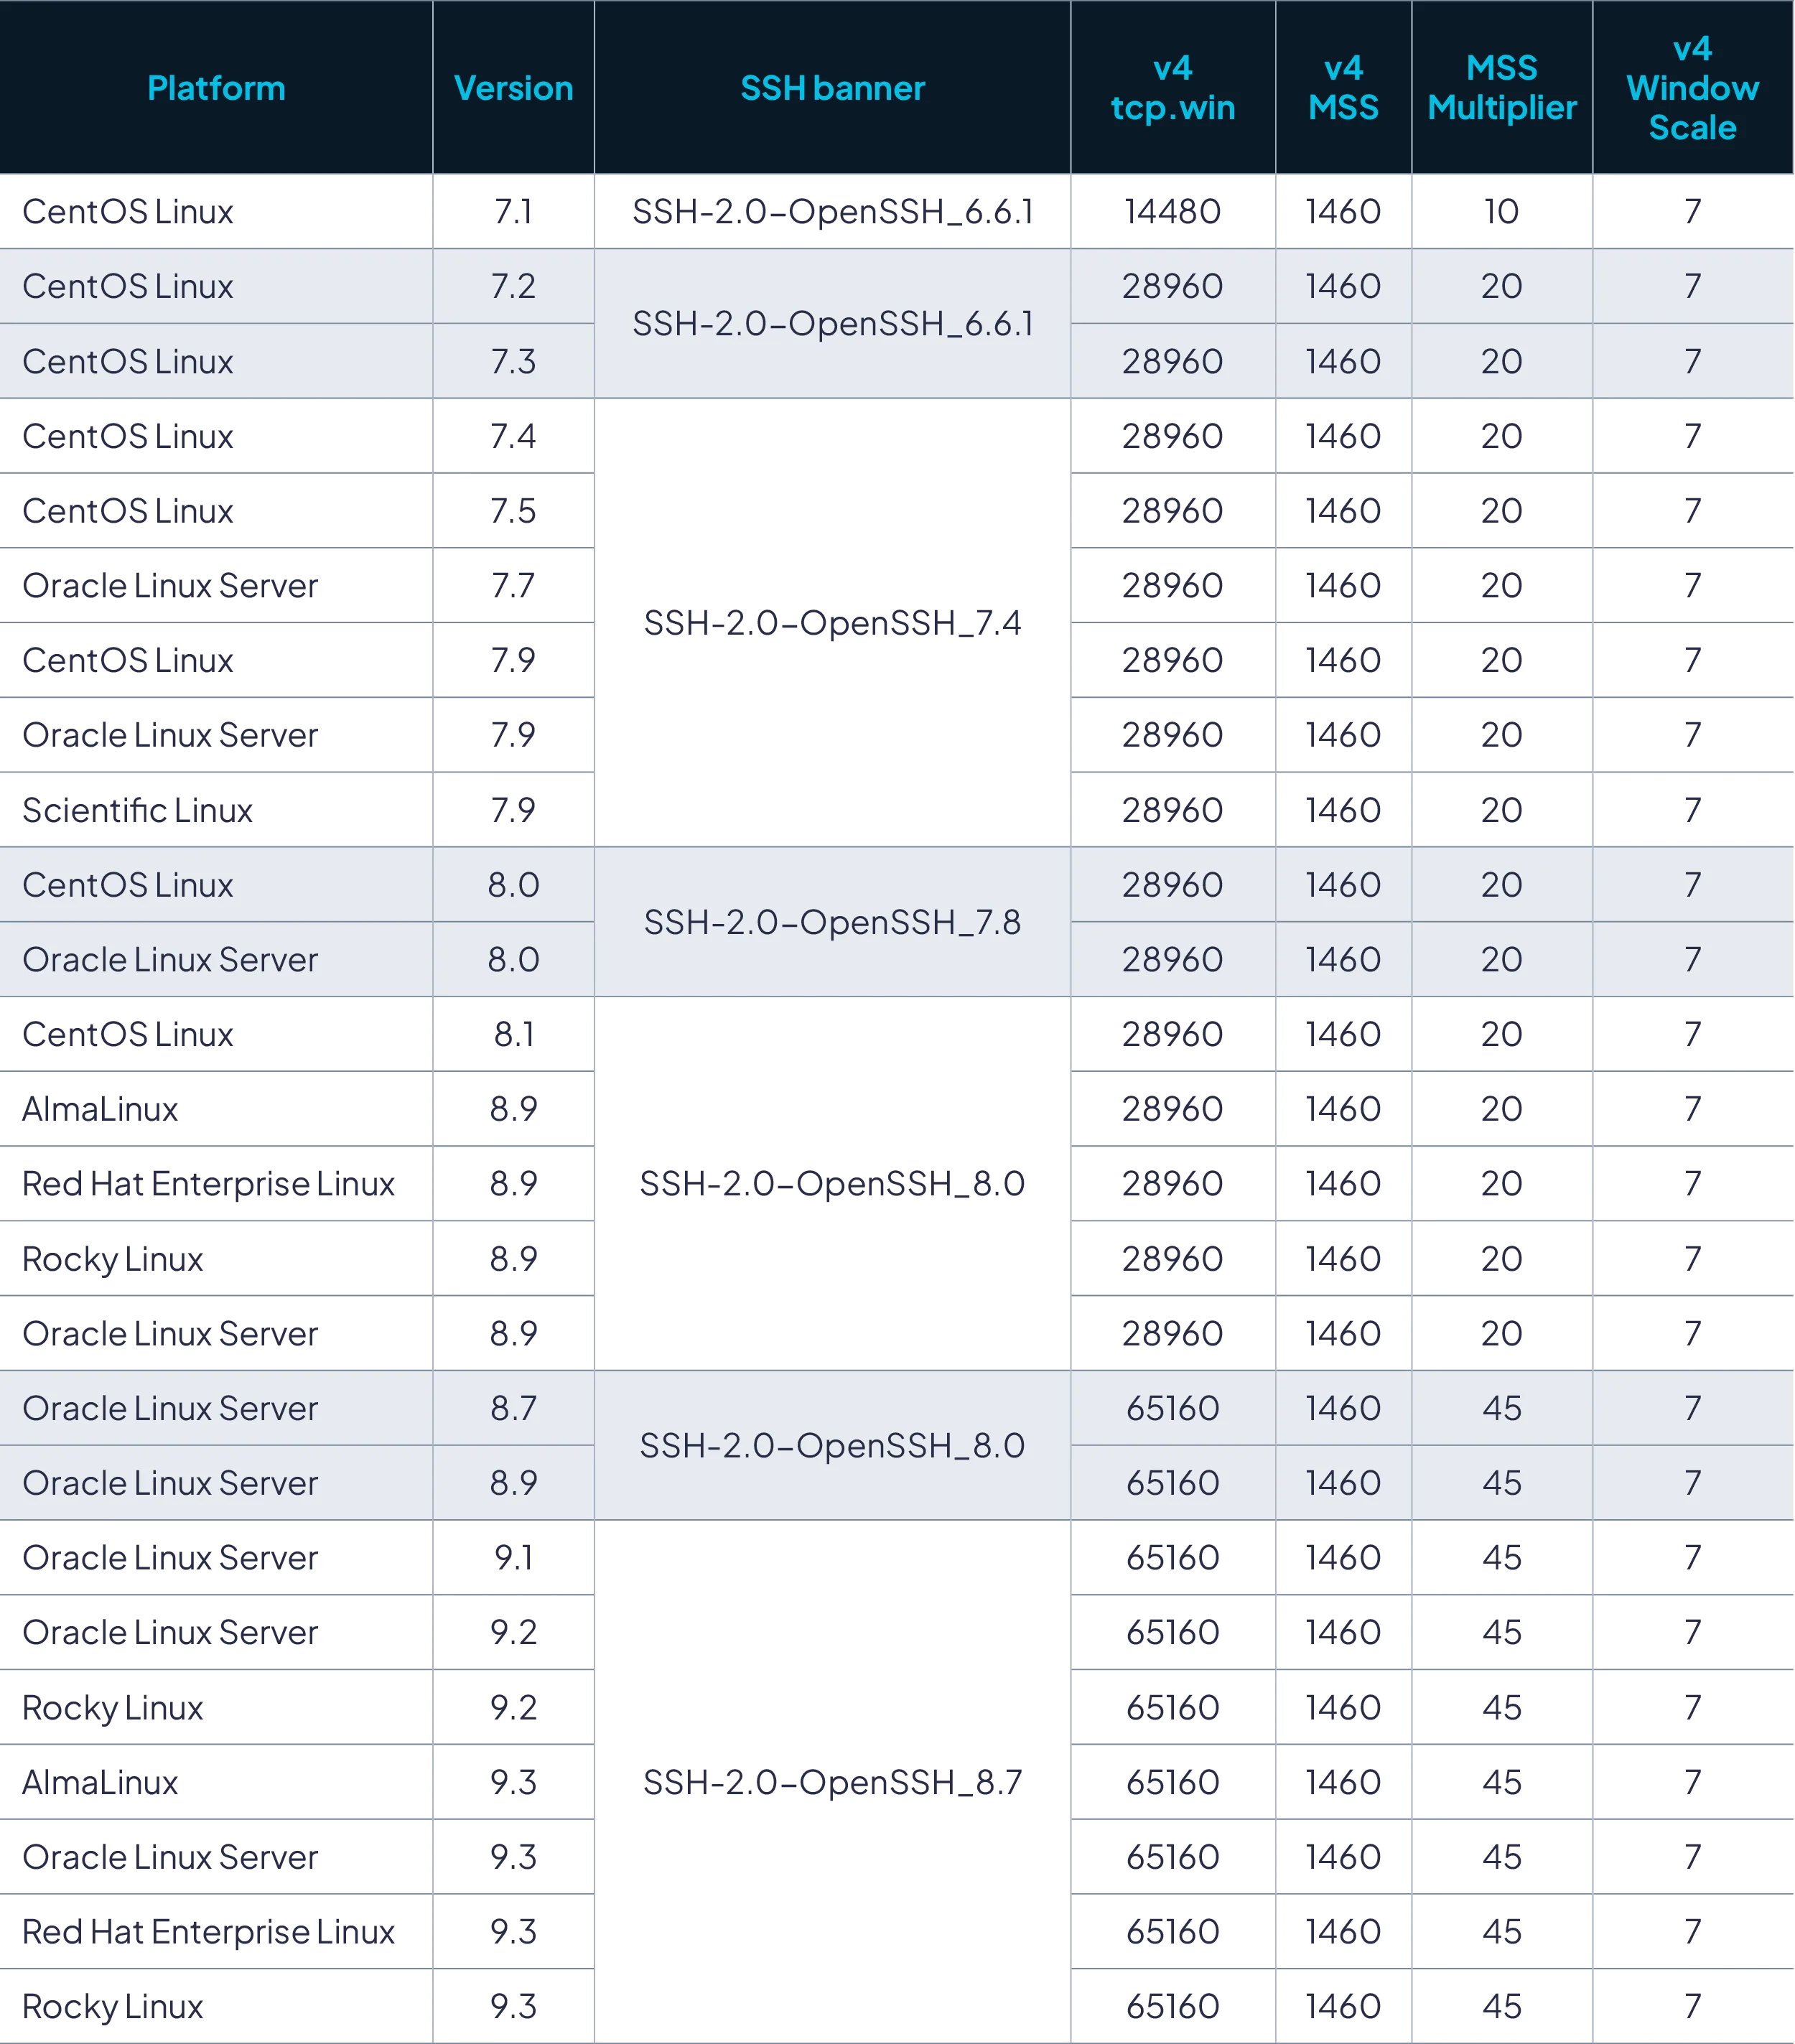
TCP-based fingerprinting by itself doesn’t improve fingerprinting of RHEL derivatives as much as we’d like. Since most of the systems in our analysis had SSH running, we looked for patterns in RHEL-derivative type and version in the light of SSH version negotiation advertisements (for example, SSH-2.0-OpenSSH_8.7) combined with the Linux kernel version. This strategy quickly yielded results. We found that we could generally identify the distribution’s major version, and in some cases, minor version range as well.

The screenshots below demonstrate how specific patterns pop out under bulk analysis.


FIGURE 3 – Relationship between different Enterprise Linux distribution versions and various network attributes.

As we can see in this screenshot, by combining SSH version advertisement and various measured TCP attributes, it is possible to narrow the Linux distribution involved, sometimes down to individual point releases. Even when it is not possible to precisely determine the version, it is almost always possible to determine if the distribution in question is derived from RHEL.

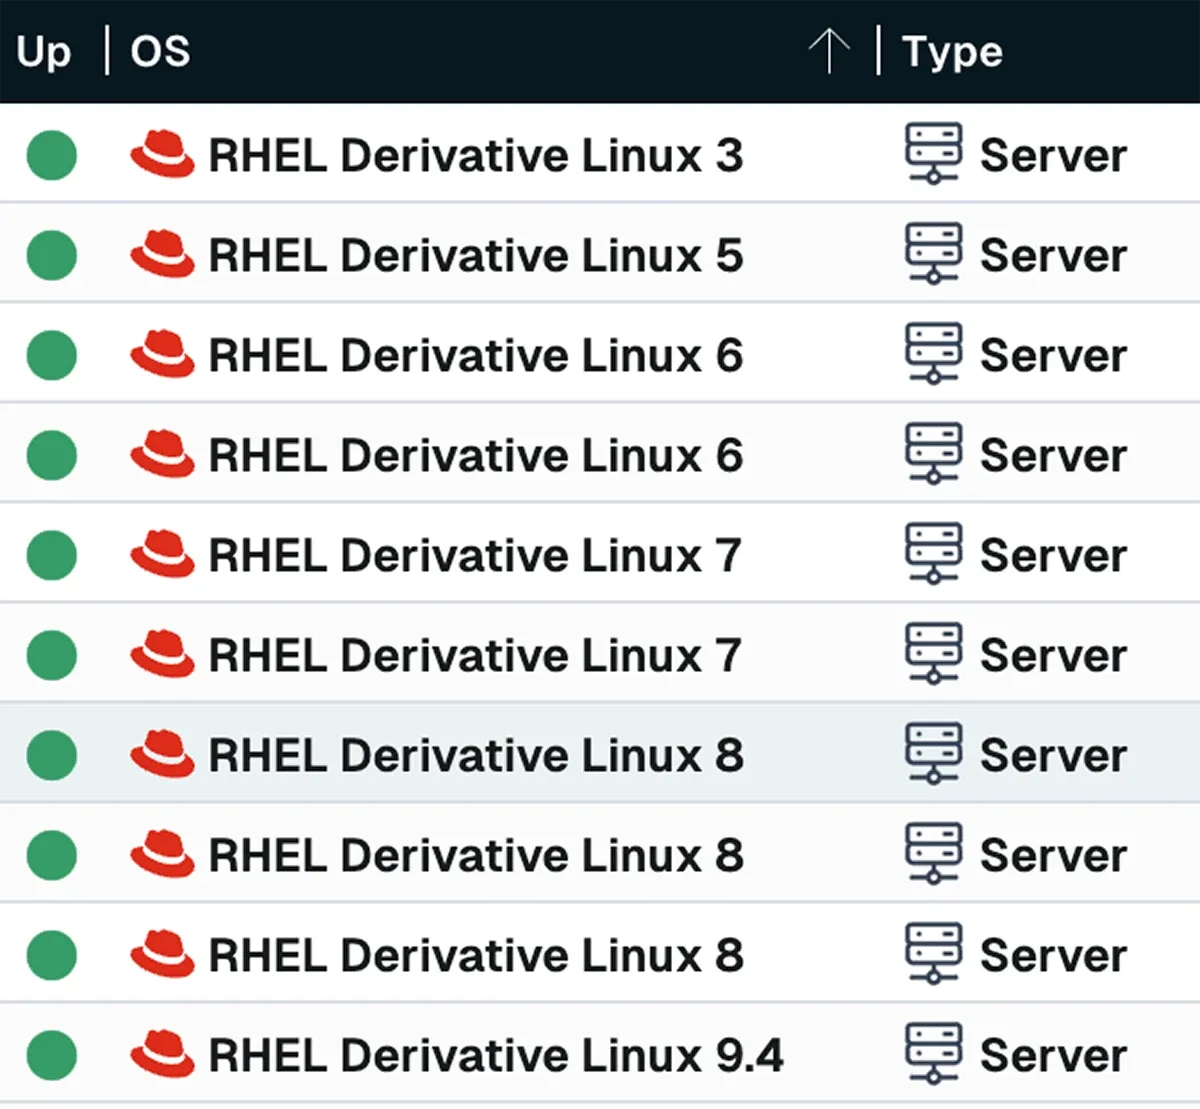
FIGURE 4 – runZero detecting operating systems derived from Red Hat Enterprise Linux.

While determining which RHEL-based distribution an asset is running from just SSH remains unsolved, the work involved resulted in greatly improving the ability to assert the OS family, major version, and sometimes minor versions of the OS. This provides customers insight into the state of their asset fleet as well as the age, support, and end of life status of these assets. The same techniques also allow us to fingerprint other operating systems, such as OpenBSD, down to the specific release version.

Final thought #

Precise fingerprinting is the foundation for delivering actionable asset discovery, exposure management, and attack surface management data to any type of organization. The runZero Research Team’s process behind precise fingerprinting enables security and IT teams to better understand where and when to take action against potential threats in their environments.

Want to learn more about runZero’s unique research on the state of asset security? Check out the runZero Research Report for a deeper look into the drivers behind CAASM.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About runZero
runZero, a network discovery and asset inventory solution, was founded in 2018 by HD Moore, the creator of Metasploit. HD envisioned a modern active discovery solution that could find and identify everything on a network–without credentials. As a security researcher and penetration tester, he often employed benign ways to get information leaks and piece them together to build device profiles. Eventually, this work led him to leverage applied research and the discovery techniques developed for security and penetration testing to create runZero.