Skip to content

NordLayer Partner Program: Klavan Security Services on how one partner supports two different partnership models

A discussion with Andrew Amaro, the Founder and Chief Security Officer at Klavan Security Services, about adapting to client needs, taking different roles, the benefits of the NordLayer Partner Program, and what perspectives are anticipated for different industries.

Highlights

  • About the company. Through its holistic approach, Klavan Security Services merges physical and cybersecurity to offer comprehensive services across industries.

  • Business case. Klavan Security Services serves a diverse clientele, from startups to the military. They focus on vulnerability identification and mitigation for effective defense, especially for SMBs enhancing digital security.

  • NordLayer adoption. By integrating NordLayer’s VPN and secure access tools, Klavan Security Services strengthens its commitment to providing a unified defense strategy against cyber threats.

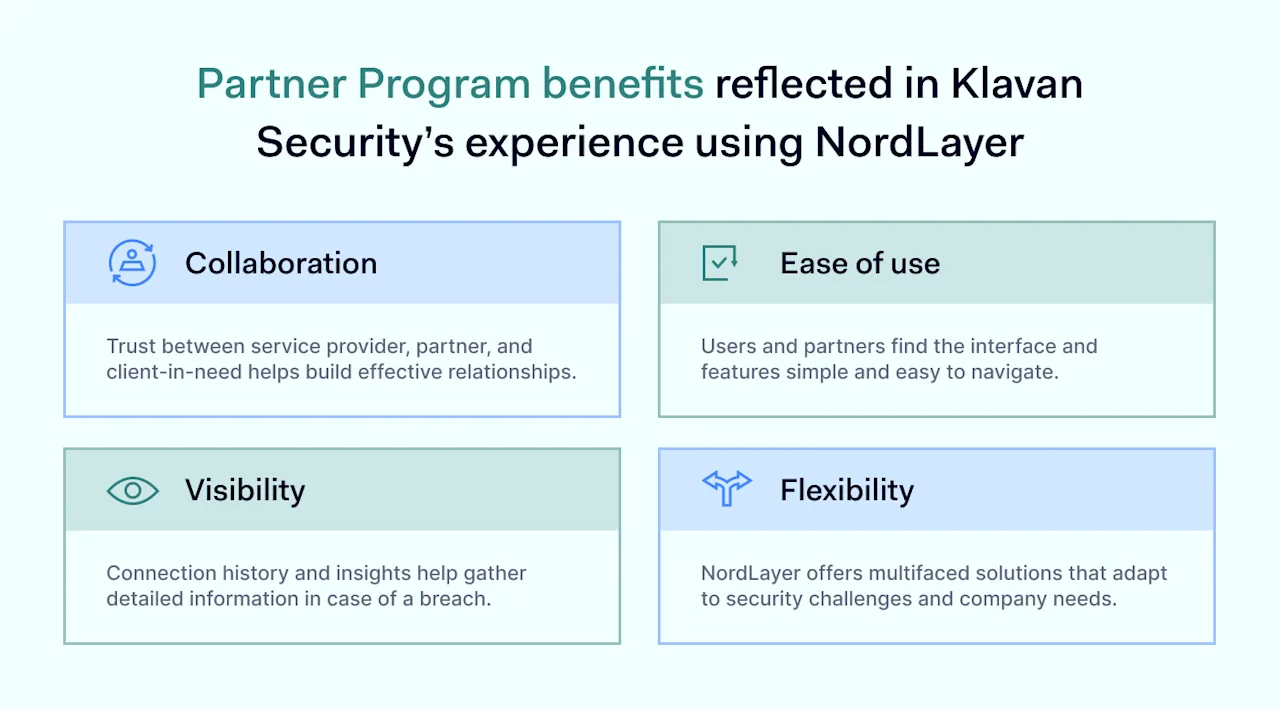
  • Benefits of NordLayer Partner Program. The partnership enhances Klavan’s security offerings, streamlines client onboarding, and supports complex compliance needs with NordLayer’s easy administration and insightful dashboard.

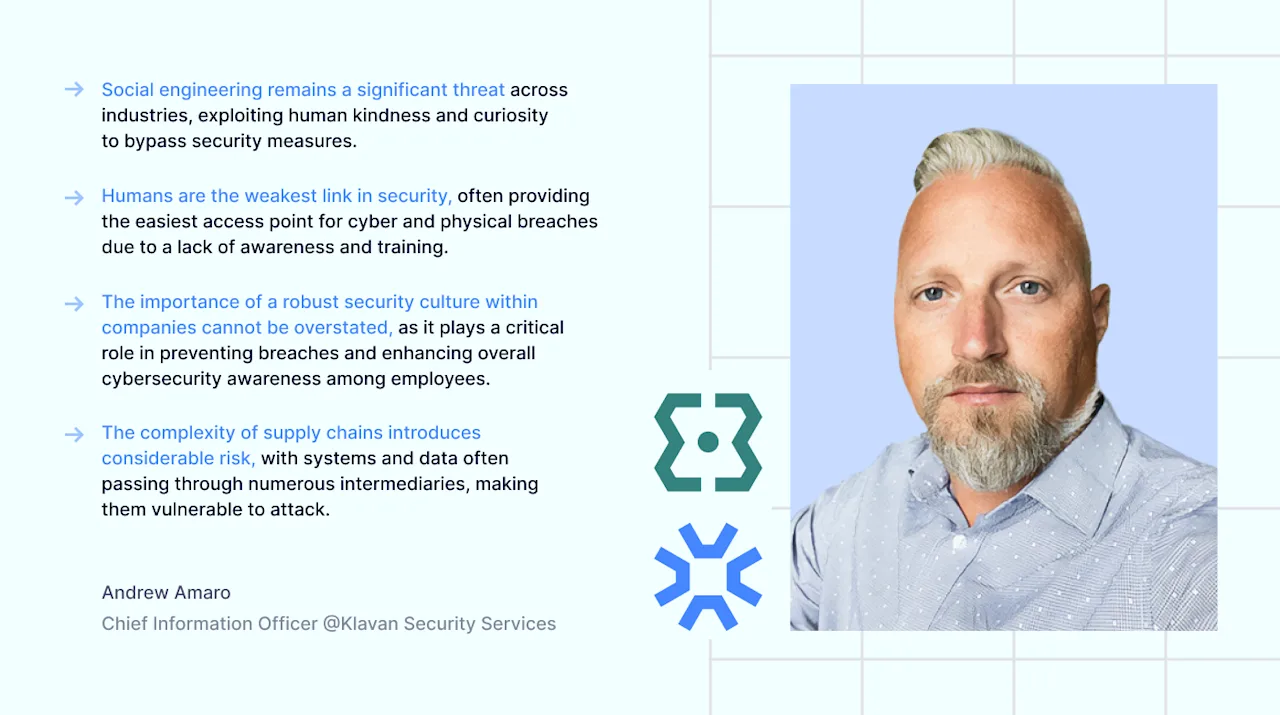
  • Future industry projections. Andrew Amaro highlights the criticality of addressing social engineering, human vulnerabilities, and supply chain risks with a strong security culture and layered strategies in the evolving cybersecurity landscape.

About the company

Klavan Security Services, nestled in the vibrant city of Ottawa, Ontario, Canada, is a beacon of innovation in the security industry. It’s a boutique firm that distinguishes itself by addressing physical and cyber security challenges, offering a full spectrum of protective services.

Klavan Security Services tailors its services to address the most pressing risks first, laying a robust foundation for a scalable security infrastructure from card access systems to ransomware protection. It works with every possible industry, focusing on challenge type rather than a customer profile.

Andrew Amaro, a Chief Security Officer and the Founder of Klavan Security Services, embodies a holistic perspective on safety. He talks about how he navigates the stormy waters of cybersecurity and how NordLayer helps find the right direction.

The business case: addressing diverse client needs via flexibility and holistic approach

With a clientele ranging from startups to military organizations, Klavan Security Services demonstrates versatility. The company’s agility allows it to serve various industries. Its focus is primarily on small to medium-sized businesses (SMBs) seeking to enhance their digital hygiene or shield themselves against sophisticated threats.

“Suppose a threat or a risk is coming towards a person, organization, or facility. In that case, you need to look at which gaps a malicious actor will take advantage of to get in, which could be from any angle depending on their motivation.”

Click to tweet

Klavan Security Services identifies and mitigates vulnerabilities using an attacker’s perspective, ensuring a fortified defense against potential breaches.

According to Andrew Amaro, when it comes to security, you have to look at it from start to finish in a holistic fashion. You can’t examine the physical and cyber subjects separately. You have to view it together.

“It doesn’t matter what a company does but what category of threats it faces based on how an organization operates.”

Click to tweet

When assessing the risks, the Klavan Security Services approach follows a deduction model. First, they define the approach of needed support. Then, by identifying the type of company, how it functions, and what it does, the company can follow up on the common risks and vulnerabilities in that regard.

Different circumstances, the same ultimate goal to secure a business with a helping hand

Various industries, work models, and processed data indicate diverse security strategies and targets when protecting a business. Not only client security needs but a type of needed support urges for flexibility and trust-based partnership to adapt to particular client scenarios:

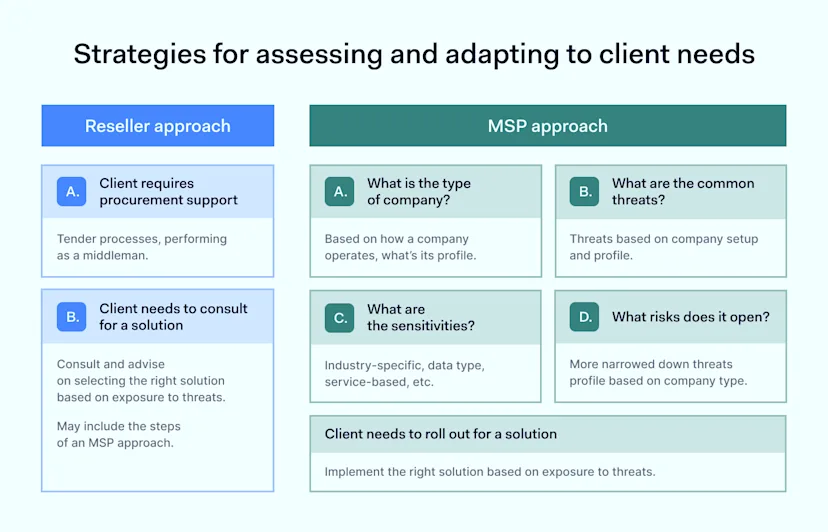
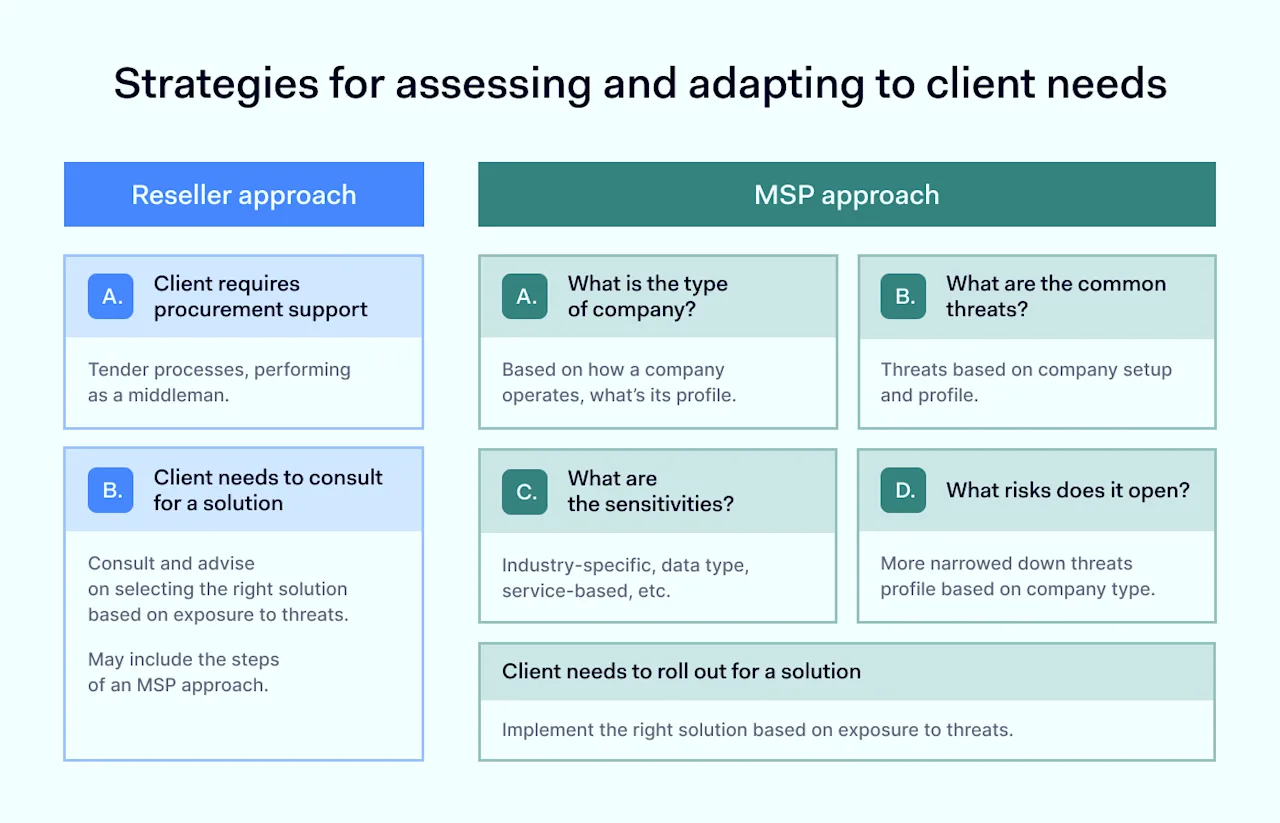
Reseller and MSP strategies for assessing and adapting to client needs

An organization that wants to be a bit more digitally hygienic and a facility that is protecting itself from state-sponsored attackers require different applications of security solutions. On the other hand, some organizations need support in the procurement processes of a selected solution.

Depending on the risks and threats, Klavan Security Services takes an attacker’s perspective of the highest risk and provides a solution, says Andrew Amaro.

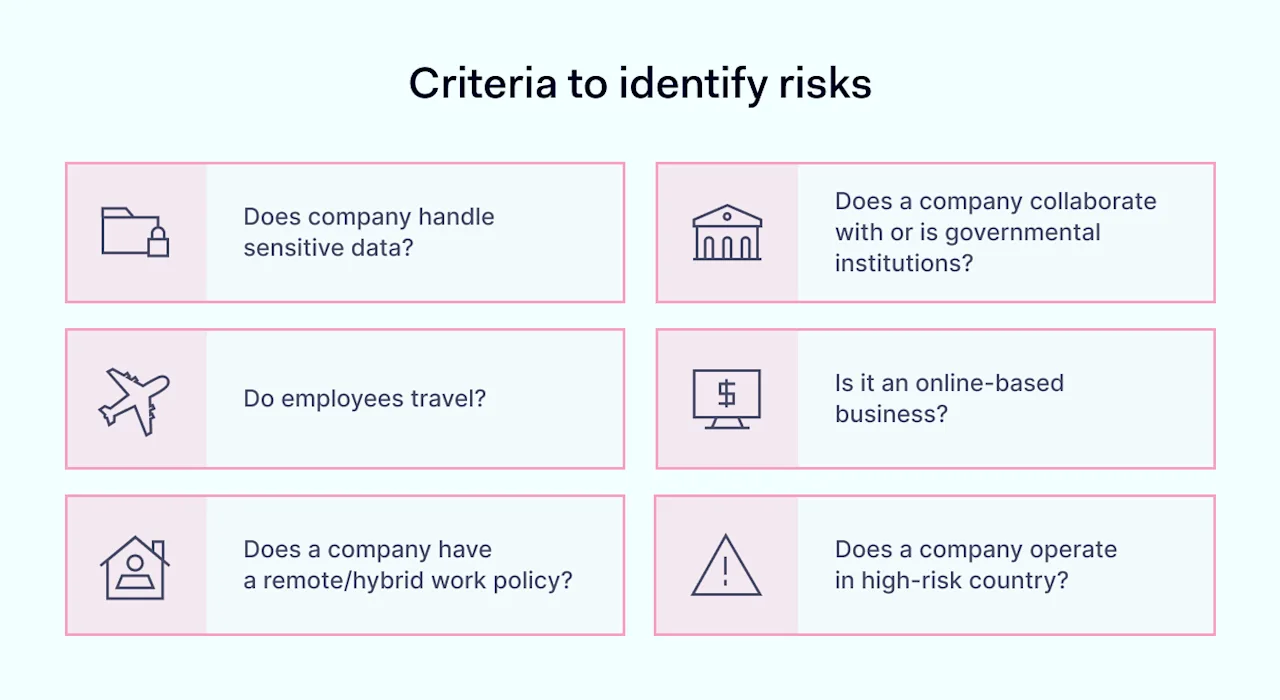
How to identify risks

Bringing together all aspects of the security industry, Klavan Security Services stands out from most security service providers by employing a unique approach to solving a problem with a one-dimensional solution.

Seeing in-depth and handling challenges by layers helps Klavan Security Services identify and tackle the full scope of risks. Implementing bad actor perception and tools of wide spectrum capabilities enables a successful collaboration that brings desired results.

Close-up on the solution

Klavan Security’s collaboration with NordLayer is a testament to its comprehensive security model.

“NordLayer’s solution is a piece of the puzzle providing a much-needed shield. If I want to provide a complete security solution for an organization that includes a VPN, secure access and encryption becomes part of the build of their Batman tool belt to protect them.”

Click to tweet

NordLayer’s suite of services, including VPNs and secure access solutions, integrates seamlessly into Klavan Security Services’s offerings, enhancing its clients’ security postures.

Opposite client profiles, one solution

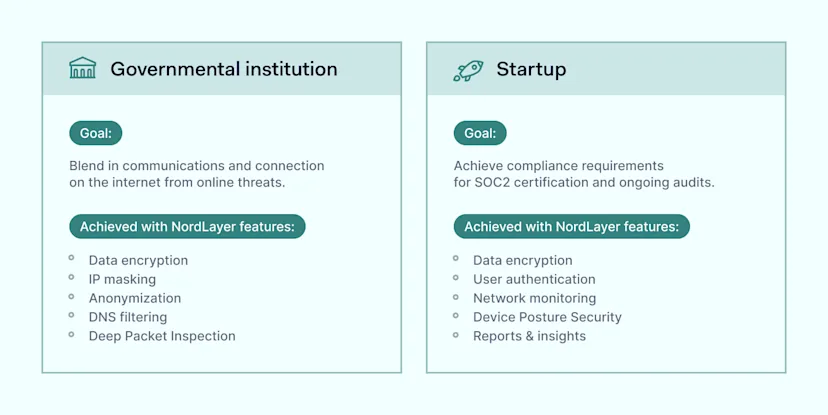
Klavan Security Services has two clients that use NordLayer for different reasons. One is a governmental institution that needs to secure its connections and data. The other one is a startup that needs to achieve SOC2 compliance requirements.

Securing government or startup with NordLayer

Klavan Security Services looks at challenges methodically. Traditional ransomware gangs and different types of malicious actors will probably target organizations on the web. If a company has to deal with sensitive information or government contracts, they’re opening new doors to different types of risks.

Solutions for handling such threats must adapt to fluctuating risks. It’s important to acknowledge that risks are multi-dimensional. They depend on a company type and cybersecurity landscape changes thus, the tools must be available to adapt quickly.

Through cases like a governmental institution and a Canadian startup, Klavan Security Services showcases the flexibility and effectiveness of NordLayer’s tools in supporting diverse operational needs and compliance goals.

Why join the NordLayer Partner Program?

The NordLayer and Klavan Security partnership isn’t a typical partner story. First, NordLayer started collaborating with Klavan as an MSP for its current client. After some time, Klavan Security Services took a reseller role since NordLayer sought a locally managed security service provider (MSSP) to support our client-to-be in a procurement process.

NordLayer benefits for partners

NordLayer team constantly looks for solutions that fit their client’s best interests, from cybersecurity solutions to procurement processes. In this case, a governmental institution needed a partner who could be trusted in the process and provide support. Thus, NordLayer contacted Klavan to introduce them as a fitting middleman for the situation.

The partnership with NordLayer opened a new opportunity and a gateway to advanced security solutions that complement Klavan Security’s holistic approach.

“NordLayer dashboard provides a proper way of controlling and seeing who comes in and out of the network. History information helps if credentials get stolen or misused by providing insights from the start of an attack.”

Click to tweet

The ease of administration, the diversity of network options, and the detailed usage insights NordLayer provides empower Klavan Security to deliver top-tier security solutions.

Besides the technicalities, the partnership with NordLayer led Klavan Security Services to acquire a new client. In instances when clients cannot proceed with direct tenders themselves due to regulations and approved processes, the collaboration between a service provider and a partner becomes a merging point.

Acting not only as an MSP but also as a reseller, Klavan Security Services filled the gap between a client and a service provider. It’s typical for governmental institutions to follow complex and prolonged processes, and collaborations like Klavan Security and NordLayer simplify such procedures by eliminating bureaucratic obstacles.

Thank you, Andrew, for sharing your journey with NordLayer, building trust and resilience in a dynamic cybersecurity landscape.

Future projections: an in-depth look into a multitude of cybersecurity threats

From the subtle art of social engineering to the intricate web of supply chain dependencies, Andrew Amaro offers a glimpse into the multifaceted nature of cybersecurity. Understanding these challenges is the first step toward fortifying defenses and ensuring a safer future for businesses in an increasingly interconnected world:Cybersecurity industry future trends by Klavan Security Services

Share article


Copied

Copy failed


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

How to block employees from accessing websites

Have you heard about the federal employee who browsed 9,000 adult sites in under 7 months? Between 2016 and 2017, this person used their work computer to access thousands of sites with explicit content. Many of these sites were linked to Russian pages that had malware.

On average, this meant visiting about 79 adult sites on each business day. This employee also stored a lot of explicit content on an unauthorized USB drive and their personal Android phone, both of which were connected to the work computer against the rules. The phone ended up getting infected with malware, according to the investigation.

This example highlights why blocking sites with adult-themed media is sensible. However, is it a good idea to block all types of inappropriate websites, such as social media? Would your employees see you as a tyrant, or could you adopt a Google-like approach that effectively improves security?

Let’s investigate whether blocking access to specific websites can benefit your company and how it might be perceived.

Key takeaways

  • It’s important for businesses to learn how to stop employees from using non-work-related or harmful websites. This helps keep the workplace focused and safe, boosts productivity, and protects the company’s online assets.

  • DNS filtering is a great way to keep employees away from sites they shouldn’t visit. It works by blocking certain internet requests, which helps reduce both distractions and security risks.

  • Teaching employees why web filtering matters is key. It helps everyone understand why it keeps the company secure.

  • In July 2023, Google limited internet access for some employees to just Google sites and a few others. This move shows how important it is to control internet use to stay safe from online threats, a practice even adopted by big companies.

  • NordLayer helps companies efficiently block websites that might distract or pose risks. Its DNS filtering service makes it easier to manage what sites can be accessed, supporting productivity and security. This approach ensures employees only visit appropriate websites.

Why restrict internet access in a workplace?

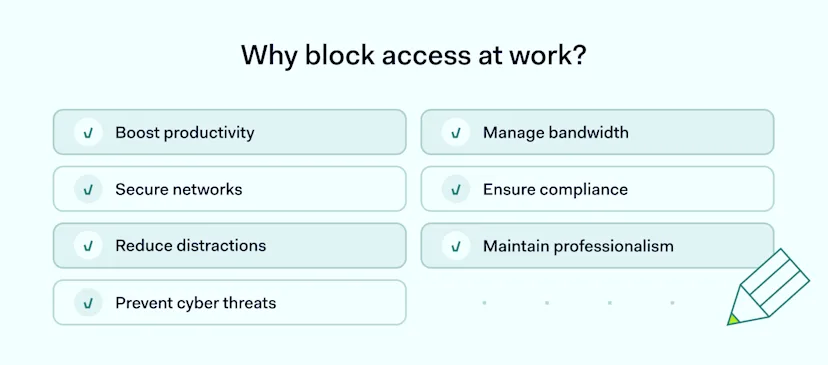
Many businesses find it crucial to restrict internet access at work to boost productivity and secure their networks. Let’s explore the reasons and benefits of such restrictions.

  • A key reason for limiting internet access is to enhance employee productivity. By blocking websites, especially social media and entertainment sites, companies can reduce distractions.

  • Another vital reason is to protect the company’s network security. Accessing insecure websites can increase the risk of cyber threats such as malware, phishing attacks, and data breaches.

  • It’s also important to manage bandwidth usage. Without restrictions, internet access might consume bandwidth for non-essential activities.

  • Compliance with legal and regulatory standards is crucial. Accessing or downloading copyrighted material without permission, or engaging in other illegal online activities, could pose legal risks to the company. DNS filtering and web filtering block websites that could lead to legal issues.

  • Lastly, maintaining a professional work environment involves blocking websites with inappropriate content, such as adult material or sites promoting hate or violence. This ensures a safe workplace where employees are not exposed to offensive content.

What websites should your business block access to?

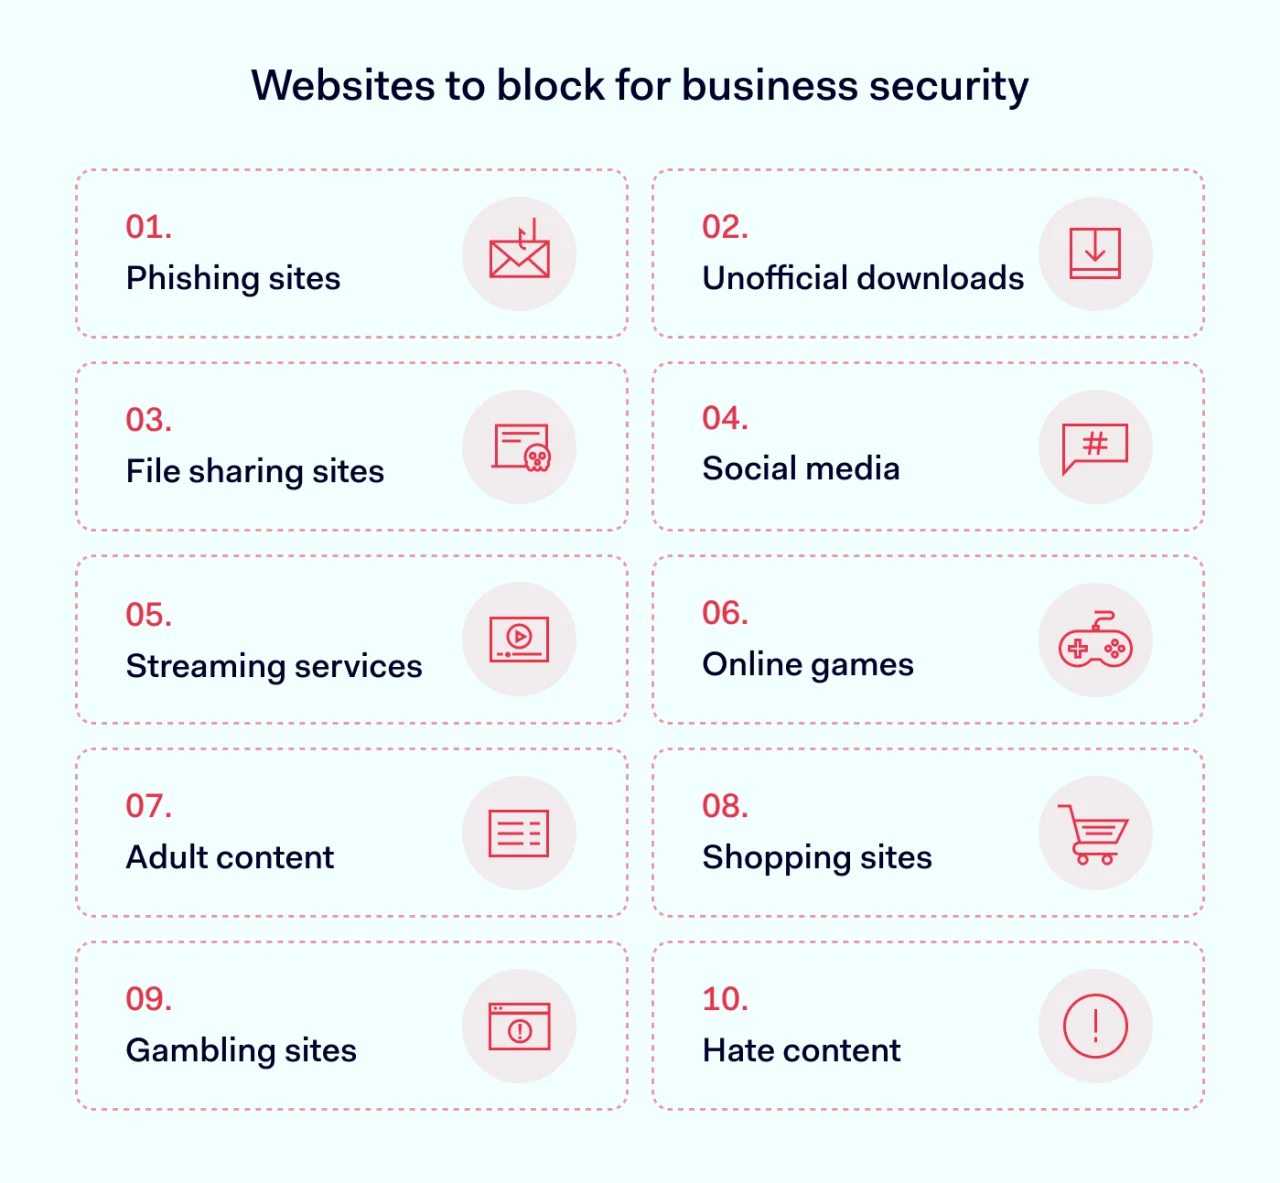
Blocking websites effectively requires a clear strategy. Here’s a comprehensive list of the types of websites your business should consider blocking access to.

Websites your business should block
  1. Phishing sites. These websites are crafted to deceive people into giving away personal or sensitive company information. They often mimic legitimate websites to steal data. Blocking access to known phishing sites is crucial for protecting your employees and your business.

  2. Unofficial software download sites. While these sites may seem like a handy resource for free software, they frequently harbor security risks. These can include malware or software that infringes on copyright laws. Block these sites to protect your network and comply with intellectual property regulations.

  3. File sharing and torrent sites. These platforms are notorious for spreading malware and facilitating data breaches. By blocking these sites, you significantly reduce the risk of infecting your company’s systems with malicious software.

  4. Social media platforms. Well, it’s no secret that social media can be a major distraction in the workplace. Block social media platforms to increase productivity.

  5. Video streaming services. High bandwidth usage from streaming services can slow down your network and affect the performance of work-critical applications. Blocking these services ensures that your internet bandwidth is reserved for business operations.

  6. Online gaming sites. Similar to social media, online games can divert employees’ attention from their work. DNS filtering can prevent access to gaming websites, helping employees stay on track.

  7. Adult content websites. Restrict access to websites with adult content to maintain a respectful and comfortable work environment for everyone, beyond the obvious professional and security reasons.

  8. Online shopping sites. While convenient for personal use, these sites can distract employees during work hours. Block access to e-commerce platforms to keep the focus on work.

  9. Gambling websites. Block access to gambling sites to maintain professionalism and prevent potential legal issues.

  10. Content that promotes hate or violence. Websites that promote hate, violence, or illegal activities should be inaccessible to maintain a safe and respectful workplace.

How to block websites on a network: 5 simple ways

Nowadays, having free access to the internet at work can result in decreased productivity and higher risks to security. This is why it’s important for businesses to find ways to limit access to certain websites.

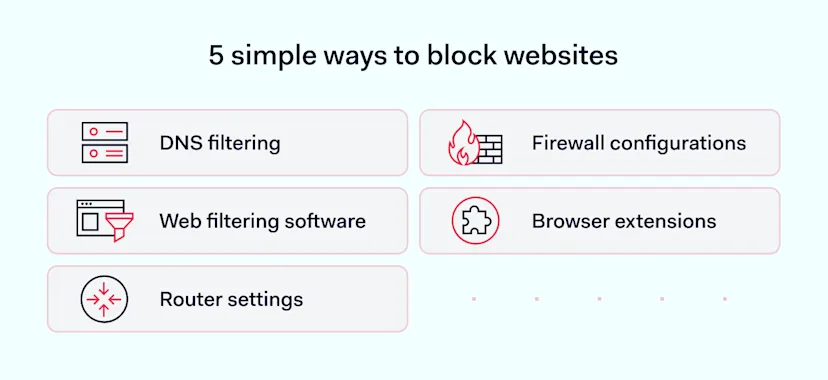
By combining technical methods and clear rules, companies can ensure their employees stay on task, and their networks are safe. Here are five easy-to-understand ways to do this.

Internet access restriction methods

DNS filtering

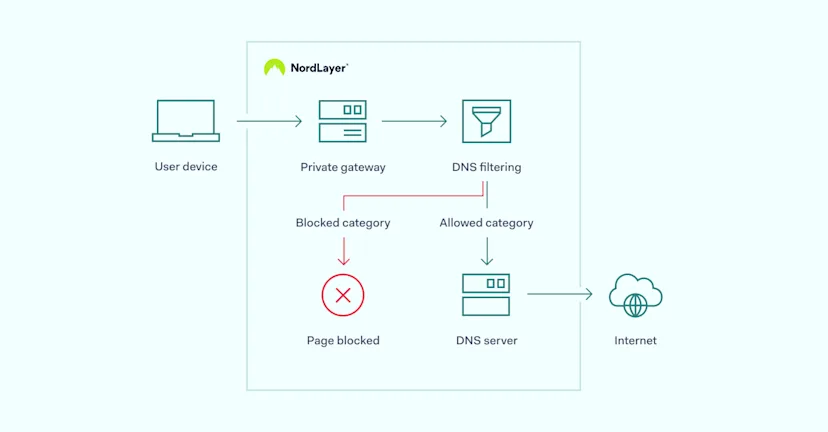
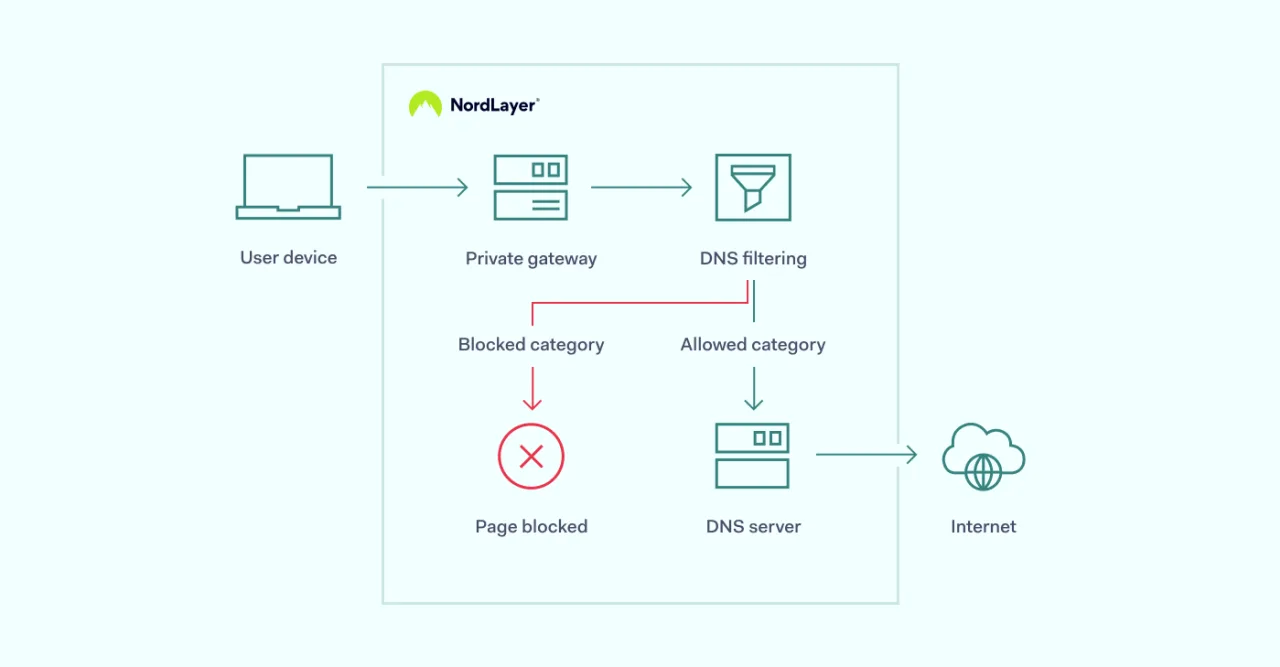
DNS filtering is a powerful approach to prevent access to specific websites. It blocks DNS queries, which is how the internet translates website names into IP addresses.

When a company sets up DNS filtering, it stops these queries for unwanted websites. This means if an employee tries to visit a non-work-related site, the DNS filter will block it.

Think of DNS filtering like a librarian who decides which books are okay to check out. This method inspects the internet’s ‘book catalog’ (DNS queries) and only lets through the requests for websites that the company thinks are okay. If an employee tries to visit a banned site, the ‘librarian’ simply says, ‘This book is not available.’

This method is effective not only for blocking certain sites but also for preventing access to malicious or phishing sites.

Web filtering software

Web filtering software allows businesses to define which websites are not allowed and enforce these rules across the network. Categories like social media, entertainment, or adult content can be restricted.

The software examines the content of web pages and blocks them if they match the prohibited criteria. This ensures employees access only work-related sites.

Router settings

Routers, especially those for business use, often have features to block specific websites. Administrators can enter URLs or keywords related to unwanted websites through the router’s settings.

This method is especially handy for small businesses without the means for more advanced filtering. It’s a bit like making a no-entry list, but it might need updates now and then to keep up.

Firewall configurations

Configuring firewalls to block websites is like having a guardian at the gate that only lets in traffic that follows the rules set by the business. By blocking specific IP addresses or domains, the guardian ensures that only safe and approved content can be entered.

This method, when used with others, strengthens the security. It can be either a hardware or a cloud firewall, so businesses are flexible in protecting the network.

Browser extensions

Install browser extensions that block access to specified websites on individual devices. While this method applies at the device level rather than the network, it’s a straightforward way to prevent access to non-work-related content on company computers.

Besides technical measures, educating employees about the significance of web filtering and the rationale for blocking certain sites is crucial. This education might include training, policies, or regular reminders about proper internet use at work.

Should companies restrict internet access?

Deciding if companies should limit internet access at work is all about finding the right balance. Many companies block websites that are unrelated to work to keep the workplace productive and focused. However, cyber-attacks are a more solid reason.

In July 2023, Google decided to restrict some employees from accessing the internet, except for Google’s own sites and a few essential services. This was part of an experiment to see how well blocking access could protect against cyber threats.

As the use of AI tools grows and brings more risks to data privacy, and as companies like Google aim for high-security government contracts, the reasons to restrict internet access become even stronger.

Limiting internet access can be a crucial step for companies that handle sensitive information or want to safeguard national security. It helps prevent unauthorized access to websites, ensuring the company’s and users’ data stays safe.

How NordLayer can help

NordLayer’s DNS filtering simplifies how to block employees from accessing websites that could harm your company’s network. This system scrutinizes each attempt to visit a website, comparing it to a list of sites that are not allowed. When it finds a website that’s recognized as a threat or is already on the blocklist, NordLayer steps in to block access to that website, ensuring your network remains secure.

DNS filtering by category

By choosing NordLayer, businesses can control and block access to a website across more than 50 varied categories, all while securing sensitive company data with robust AES 256-bit encryption. This approach offers a comprehensive solution for maintaining productivity and enhancing network security. If you have any questions before getting started, feel free to contact our sales team. They’re here to assist you.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

Cyberview #7: Rise of the deepfakes

Deepfakes are back in the news. With widespread social and geopolitical instability and a pivotal election looming in the US, these AI-powered hoax videos are injecting some extra chaos into affairs. Blurring the lines between fact, fiction, politics, technology, and showbiz, deepfakes are an unprecedented wildcard to keep an eye on this year. Cyberview dives in.

What are deepfakes?

Definitions first: Deepfakes are highly realistic synthetic video or audio created with AI models. These deep learning (hence “deepfake”) models are trained on huge quantities of data to mimic a person’s facial expressions, lip movements, and vocal patterns.

Deepfakes are created with Generative Adversarial Networks (GANs), where two models work together (or more accurately, against each other) for optimum results. One model, the generator, creates the fake content, while its partner model, the discriminator, acts as a judge. Low quality fake content is rejected, the convincing material is accepted, and the discriminator constantly pushes the generator to improve across iterations. The result? Convincing videos of people saying or doing things they never did.


The cybersecurity challenge

Deepfakes, unsurprisingly, pose significant cybersecurity risks. Identity theft, fraud, and authentication exploits are all made easier with this technology. A Hong Kong finance worker was fooled into transferring $25 million to fraudsters due to a deepfake impersonation of the company’s CFO.

In another high-tech heist, a company director’s voice was cloned. The cyber conmen got away with $35 million. Vishing (voice phishing) and other social engineering techniques have just received the equivalent of a supercharged power-up with deepfakes.

In the political sphere, deepfakes are being used to influence public opinion. Thousands of citizens in New Hampshire received calls that appeared to use AI to impersonate President Joe Biden’s voice, who urged them to skip voting in the January Democratic primary election. The calls were traced back to a company in Texas with suspicious motives and funding.

Soon after this event, fake videos of megastar Taylor Swift announcing her support for Donald Trump circulated online. In an election year balanced on a knife edge, further devious use of deepfakes could do a lot of damage.


Battling against the fakes

Efforts are underway to combat the deepfake threat. Social media and content platforms like TikTok, YouTube, Meta, and Twitter are implementing policies and features to detect, label, or remove misleading AI-generated content.

OpenAI’s DALL-E generated images now include digital watermarks in image metadata. Google has gone a step further with SynthID, which embeds a watermark directly into the pixels of the image. But none of these methods are infallible. A recent study by University of Maryland students found that “our attacks are able to break every existing watermark that we have encountered.”

On the legislative and regulatory side, the FCC promptly banned AI in robocalls following the election interference calls. Currently only about ten states target deepfake content, and these have generally prioritized non-consensual pornographic material. There’s no overarching federal legislation yet, but the No AI FRAUD Act, if enacted, would “provide individual property rights in likeness and voice.” The EU’s AI Act, which will demand transparency from creators of synthetic content, is currently being finalized.

How you can detect deepfakes

Here are a few tips to spot deepfakes:

  • Unnatural movements, poor lip syncing

  • Shadows in the wrong places

  • Vocal inconsistencies, unusual tone/inflection

A good rule of thumb is to verify information from multiple sources before believing it (or sharing it further). And some timeless advice that applies always and forever: Be skeptical of anything that seems too good (or bad) to be true, especially online.

Check out the new Cyberview episode on your favorite platform:

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

No fun while browsing at work. What content do employers block the most?

Today, the internet is a tool for navigating the world more easily. It’s also an inseparable part of most people’s jobs. The internet helps us find and share information, relax, and understand many topics. But as with many good things, the internet has a dark side.

Bad actors exploit the benefits the online world gives society, and thus, we must protect against such risks. Businesses need to be aware of the threats that lurk on the internet and find ways to battle them.

Domain Name System (DNS) filtering is one of the most effective ways to prevent unwanted content. Companies employ this feature to minimize the potential of online risks. As a side-effect, this even helps improve employee productivity.

NordLayer has researched how their client companies use DNS filtering functionality. For example, organizations tend to block access to manga or underwear websites more than social networks. This report will reveal exciting findings that suggest best practices your company could try out, too. So, let’s go!

About the research

The statistics mentioned below were acquired by analyzing aggregated data gathered by NordLayer’s DNS filtering service in February of 2024. No identifiable business or user information was collected, reviewed, or otherwise involved when the research and compiled results were conducted.

Category statistics in the research contain 54 varieties. The report overviews data from the main markets by country and continent.

What is DNS filtering

DNS filtering is like having a selective gatekeeper for your internet browsing.

Imagine you’re trying to get to a party (a website) in a big city (the internet). Instead of navigating through complex streets (IP addresses), you tell your driver (the DNS) the party’s name (domain name), like NordLayer.com.

Now, imagine some parties aren’t safe to attend for various reasons. They might be hosting shady characters (malicious websites) or engaging in activities you’d rather avoid (harmful/inappropriate content).

DNS filtering steps in as a responsible friend who advises you on which parties are safe and match your preferences, blocking the risky ones and guiding you to secure enjoyable destinations.

Or, put it shortly:

DNS filtering is a security method that uses the DNS to block access to harmful or unsuitable-for-work websites. It acts as an internet filter, screening websites against set security policies or categories to prevent exposure to threats like malware or phishing.

Click to tweet

For businesses, DNS filtering becomes a powerful tool. Managers can set rules on what types of websites employees can visit during work hours on company-managed networks.
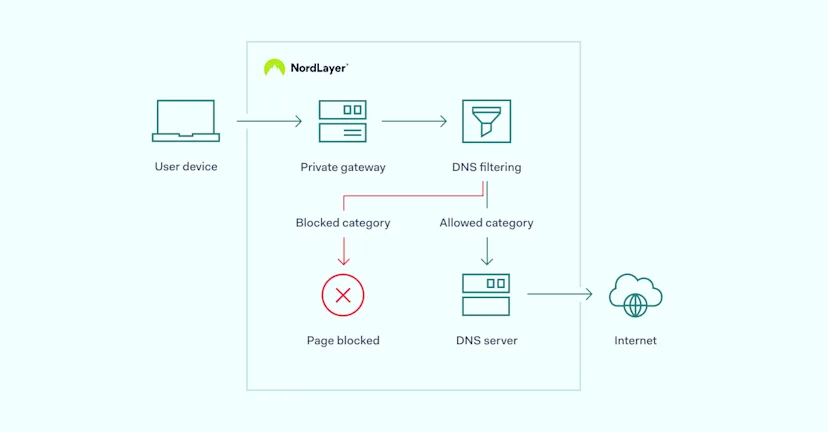
By doing so, they enhance the security of company data and protect employees from stumbling into digital pitfalls like phishing websites. It’s a smart way to ensure the online environment is not only productive but also safe from threats lurking around the internet’s corners.

Most common online threats DNS filtering prevents

DNS filtering helps mitigate the exposure to risks users face while browsing the internet. It includes viruses, spyware and malware, various types of phishing attacks, botnet-escalated threats, and more.

  • Malware. Malicious software, including viruses, worms, Trojans, and ransomware, can cause significant damage to systems or networks. DNS filtering stops these threats by preventing access to websites that distribute malware.

  • Botnets. Networks of infected devices can be remotely controlled to launch attacks. DNS filtering can disrupt the communication between these devices and command-and-control servers, mitigating the threat.

  • Adware. Often annoying and potentially harmful software that displays unwanted ads. DNS filtering can prevent access to adware-distributing sites, enhancing user experience and security.

  • Viruses. They are malicious programs designed to infect and damage computers and networks. DNS filtering prevents access to websites known for distributing viruses, thus reducing the risk of infections and safeguarding system integrity.

  • Spyware. Software that secretly monitors and gathers information from individuals or organizations. By blocking sites known to distribute spyware, DNS filtering helps protect privacy and sensitive data.

Overview of DNS categories

First, let’s overview DNS categories. Grouping these categories will help us better see the tendencies of what types of sites are considered to be malicious or at least avoidable. The goal here is to create clusters that share a common theme or purpose, making it easier to manage preferences or restrictions based on user needs, security protocols, or compliance requirements.
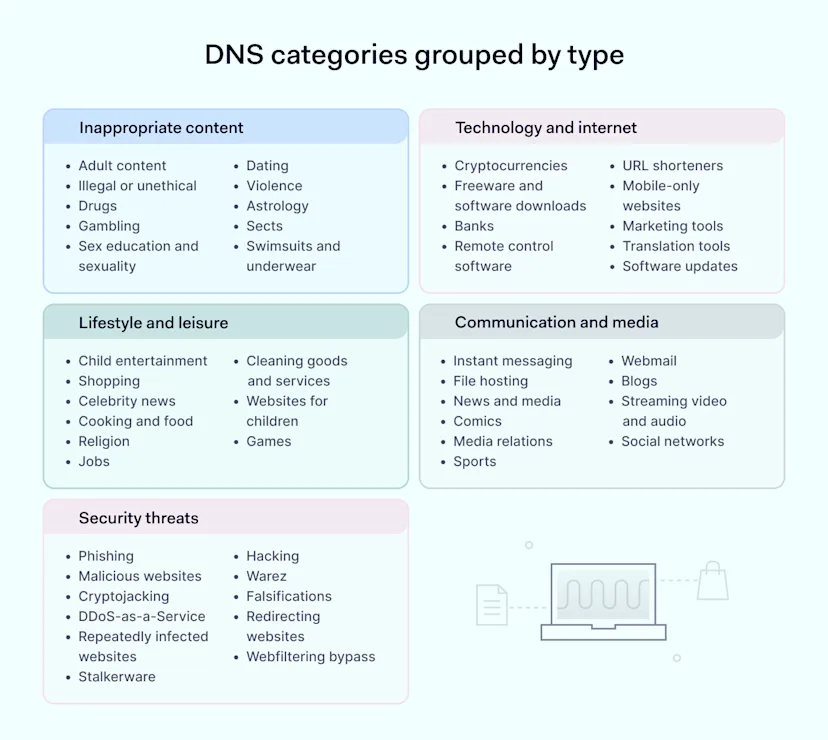
By grouping these categories, we create a framework that aids in designing more nuanced and effective DNS filtering strategies, ensuring a balance between user freedom and network security, compliance, or productivity goals. This approach highlights the diversity of online content and the complexities involved in managing internet access responsibly.

Restricted websites: which categories get blocked the most?

Let’s uncover the digital no-go zones together. From shadowy corners harboring malware to tempting and time-sinking entertainment sites like 9GAG and BuzzFeed, we’ll explore the top categories that companies across the globe consistently consider too risky or distracting for open access.

Trends of blocking DNS categories

The top 10 DNS-blocked categories offer a revealing glimpse into the primary concerns that motivate organizations to filter internet content. Here’s a breakdown, highlighting what each category suggests about current priorities in network security and content management:

1. Malware (72%): reflects the universal concern for protecting networks and devices from malicious software designed to damage or exploit them.

2. Adult content (72%): indicates efforts to maintain a professional work environment, comply with workplace policies, and possibly avoid legal issues related to inappropriate content access.

In a recent NordVPN study related to the Threat Protection tool, it was discovered that adult content sites hide the biggest amount of malware. Thus, blocking this type of content mitigates a huge risk for businesses.

Read more about the research and explore more interesting findings.

Click to tweet

3. Phishing (70%): underlines the emphasis on safeguarding sensitive information against deceitful attempts to obtain it through fraudulent websites.

4. Illegal or unethical (56%): shows the commitment to corporate ethics and legality, blocking access to content that could harm the company’s legal standing or moral integrity.

5. Cryptojacking (54%): highlights the growing concern over unauthorized cryptocurrency mining, which can significantly drain network and device resources.

6. DDoS-as-a-Service (51%): reflects awareness of the threat posed by services offering to disrupt networks through Distributed Denial of Service (DDoS) attacks, emphasizing the need for preventive measures.

7-8. Repeatedly infected websites (44%) and Stalkerware (44%): these categories signal an understanding of the ongoing risks associated with websites known for recurrent malware issues and software that covertly monitors users, stressing continuous vigilance.

9. Hacking (43%) points to the necessity of blocking access to sites that could serve as gateways to hacking tools or knowledge, protecting against unauthorized access or data breaches.

10. Gambling (43%): suggests an effort to prevent potential legal and productivity issues related to gambling, which can also be a source of financial fraud and addiction among employees.
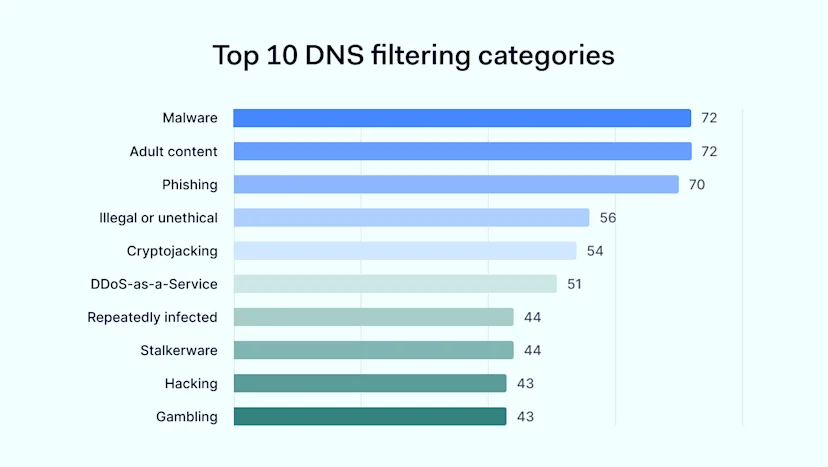
These insights highlight a strategic approach to DNS filtering, balancing between defense against security threats, compliance with legal and ethical standards, and the promotion of a focused and safe work environment.

The prevalence of security-related categories (like malware, phishing, and hacking) alongside those aimed at maintaining workplace standards (such as blocking adult content and gambling) shows a comprehensive effort to mitigate risks and support corporate values.

The landscape of DNS blocking reveals a clear prioritization among organizations, with the most blocked categories—malware, adult content, and phishing—highlighting a strong focus on security and maintaining a professional workplace environment.

Despite maintaining a professional environment, the biggest focus remains on blocking cyber-attack-affiliated content. 7 categories in the top 10 are related to malicious activities of a third party. Here’s why it’s so important:
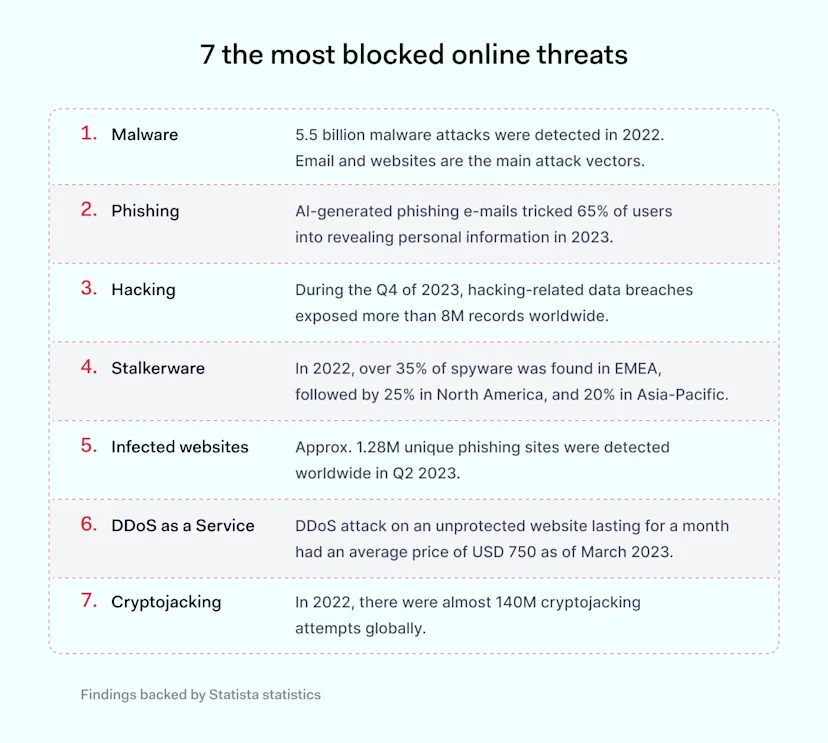
  • In 2022, the digital threat landscape continued to evolve at an alarming rate, with cybercriminals launching 5.5 billion malware attacks using emails and websites as their primary weapons. Fast forward to 2023, and the sophistication of these attacks has only intensified.

  • Artificial intelligence (AI) now aids in crafting phishing emails so convincingly that 65% of users were tricked into disclosing personal information.

  • The closing quarter of 2023 witnessed a surge in hacking activities, culminating in data breaches that exposed over 8 million records globally, underscoring the relentless efforts of cybercriminals.

  • Meanwhile, in 2022, EMEA led with over 35% of spyware (stalkerware) detection, North America followed with 25%, and the Asia-Pacific region accounted for 20%.

  • By the second quarter of 2023, the threat had diversified further, with around 1.28 million infected sites identified, showcasing the ever-expanding arsenal of cybercriminal tactics.

  • The accessibility of DDoS attacks as a service was highlighted by the startlingly low cost of USD 750 for month-long assaults on unprotected websites, revealing a commercial or business-oriented aspect of cyber warfare.

  • Cryptojacking attempts, nearly reaching 140 million in 2022, illustrated another aspect of this complex threat, with attackers secretly harnessing victims’ computing power for cryptocurrency mining.

The research suggests that blocking these categories of websites is a critical component of an organization’s cybersecurity strategy. It helps safeguard the network, protect sensitive data, and ensure the smooth operation of business processes by mitigating risks before they can manifest.

Minimizing distraction, increasing productivity

The percentages of companies blocking various categories provide a fascinating snapshot of the priorities and concerns of modern businesses regarding internet usage. Here’s a deeper dive into what these figures might reveal:
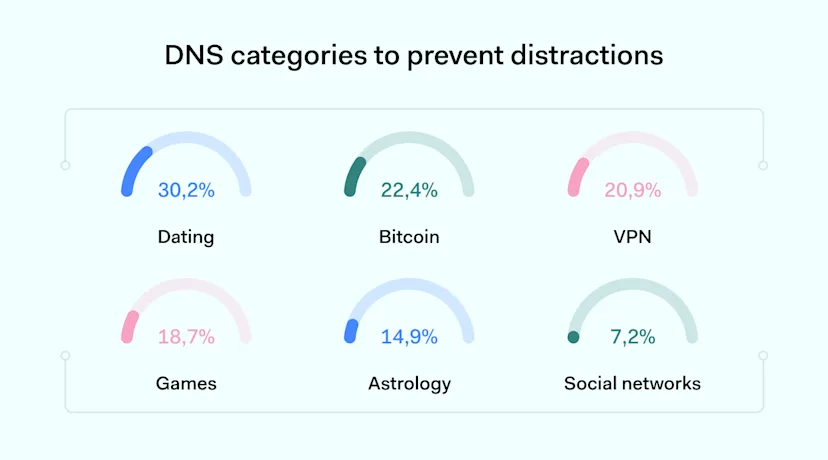
  • Dating sites (30%): this is the most blocked category, indicating a widespread concern among companies about the personal use of company resources and potential distractions. It also highlights efforts to maintain professionalism and focus in the workplace.

  • Bitcoin (22%): blocking cryptocurrency sites, particularly Bitcoin, reflects concerns over security risks associated with cryptocurrency transactions and the potential for these sites to be linked with illegal activities. Additionally, it suggests an effort to prevent employees from engaging in speculative, non-work-related activities.

  • VPN (21%): companies restricting VPN services are likely to prevent employees from bypassing network security measures and accessing restricted content. This emphasizes the importance of controlling network traffic and maintaining security protocols.

  • Games (19%): blocking gaming sites indicates recognition of the productivity drain these sites can cause. It’s a move to minimize distractions and ensure employees remain focused on their responsibilities.

  • Astrology (15%): while it might seem surprising to see astrology websites blocked more frequently than social networks, this decision could stem from a desire to limit access to content considered unscientific or a distraction from work.

  • Social networks (7%): interestingly, social networks are the least blocked category among those listed, suggesting a nuanced approach by companies towards these platforms. This lower percentage may reflect the recognition of social media’s role in professional networking, marketing, and communication strategies, balancing the potential for distraction against the benefits of connectivity.

These trends recognize the evolving role of technology and the internet in the professional landscape while safeguarding company assets and fostering a focused work environment.

DNS filtering differences by regions

Despite various available DNS categories, companies block 10 different types of online content on average. In Asia, we see a more restrictive approach than in Europe and North America. Each region adapts its approach to DNS filtering to meet its unique challenges and objectives best.
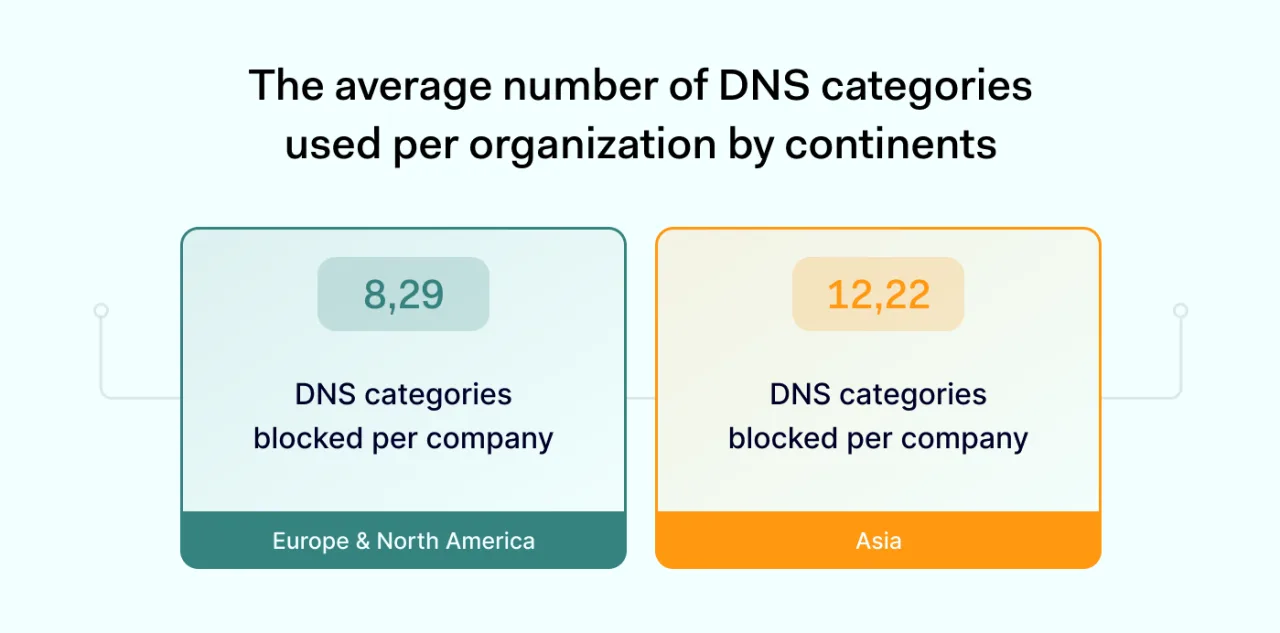
Average number of blocked DNS categories by regions

The variance in DNS categories blocked between companies in Europe and North America versus Asia likely boils down to four main factors:

  • Regulatory differences. Asian countries often have stricter internet regulations, requiring more categories to be blocked for compliance. In contrast, European and North American regulations may allow for more freedom online, resulting in fewer restrictions.

  • Cultural norms. Asian companies might block more categories to align with conservative societal values. In contrast, Western regions may adopt a more liberal stance, focusing on blocking only for security, legal, or productivity reasons.

  • Cybersecurity threats. A different cybersecurity threat landscape could influence the decision to block more categories in Asia, requiring broader preventive measures than the targeted strategies in Europe and North America.

  • Work culture and business practices. Asian workplaces often emphasize a strict separation between work and personal life, leading to more extensive blocking to maintain productivity. Western companies might encourage a balance, needing fewer content restrictions.

Looking at North American, European, and Asian markets, we can see that Western regions equally consider malware as their top priority for blocking, while Eastern regions prioritize blocking illegal or unethical content. Adult content like pornography sites and explicit content is the overall second pick, with Europe leading the group.
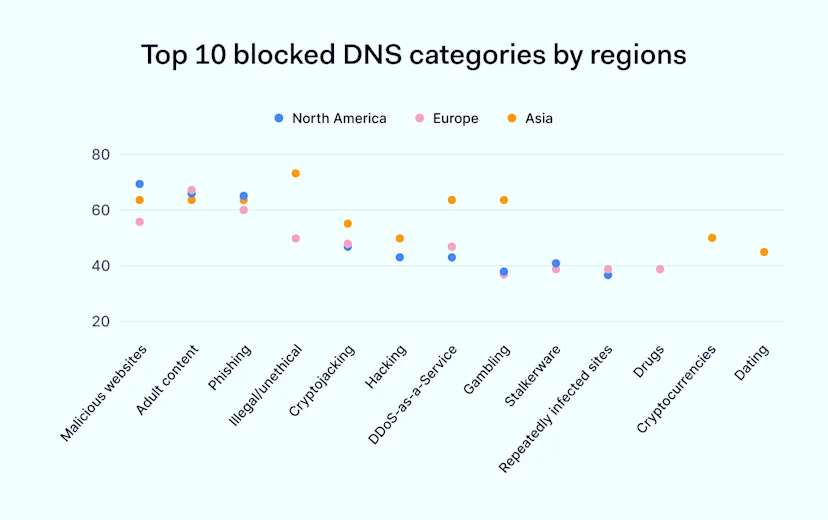
The approach to blocking DNS categories varies across North America, Europe, and Asia, reflecting each region’s unique cybersecurity landscape and cultural nuances.

Malicious websites are a top concern worldwide, with North America leading slightly in terms of proactive blocking measures. This consensus underscores a global recognition of the threats posed by malicious sites, with regional adjustments based on specific cyber landscapes and regulations.

The handling of adult content varies, with Europe’s slightly higher blocking rate likely indicative of its stringent content regulations. North America and Asia also prioritize this category, revealing a common aim to maintain a secure online environment.

Phishing attacks are universally combated, showcasing the necessity of robust defenses against this widespread threat. North America’s marginally higher blocking rate highlights the persistent challenge phishing poses across regions.

Asia stands out for its markedly higher blocking of illegal/unethical content and services like DDoS-as-a-Service and gambling, reflecting its strict legal and cultural frameworks. The lack of emphasis on hacking in Europe suggests a different focus or reliance on alternative defensive tactics.

Stalkerware and repeatedly infected sites show varied attention, pointing to regional differences in perceived threat levels. Europe’s unique focus on drugs aligns with its specific policies, while Asia’s concern for cryptocurrencies and dating sites highlights regional security and social considerations.

Importance of proactive online security

DNS filtering serves three pivotal roles in managing online interactions: security, compliance, and productivity. Each role focuses on a distinct goal, but all link to the idea of controlling access to certain types of online content.

Security: preventing malicious or NSFW activity

At its core, DNS filtering is about keeping users safe from harmful content. This includes blocking access to websites known for phishing, malware distribution, or those hosting adult content unsuitable for all audiences.

The aim is straightforward: to protect users from threats that could compromise their personal information and device integrity or expose them to inappropriate content. DNS filtering acts as a first line of defense against numerous online security threats by preventing access to these sites.

Compliance: blocking content for device and network security

Compliance takes the security concept a step further by enforcing specific regulatory or policy requirements. This might involve blocking access to illegal download sites to comply with copyright laws or restricting gambling sites to adhere to corporate policies or legal frameworks.

DNS filtering for compliance ensures that the organization and its users operate within the bounds of legal and ethical standards, thereby protecting the organization from legal issues and maintaining its reputation.

Productivity: limiting personal matters

The third pillar focuses on enhancing productivity by limiting access to websites unrelated to work or the task at hand. This includes social media platforms, video streaming sites, and other distracting websites that can significantly reduce productivity to stay focused.

By restricting access to these sites during work hours, DNS filtering helps organizations ensure that their resources are utilized efficiently and that employees remain focused on their responsibilities.

Network performance: enhancing internet speed optimization

A critical yet often overlooked aspect of DNS filtering is its role in optimizing network performance and internet speed. This optimization process involves restricting access to high-bandwidth websites.

Video streaming services, file-sharing platforms, and large-scale download sites can significantly consume excessive amounts of internet bandwidth. When left unchecked, these activities can greatly degrade network speeds, impacting the individual’s productivity and overall organizational efficiency.

Each direction serves a specific purpose, yet they all share the common goal of optimizing the online environment according to the organization’s needs.

Why choose NordLayer DNS filtering service?

Choosing NordLayer’s DNS filtering service offers organizations a suite of powerful benefits designed to enhance their network security, improve productivity, and ensure a safer online environment for all users.

Here’s why NordLayer stands out as a preferred option for DNS filtering:
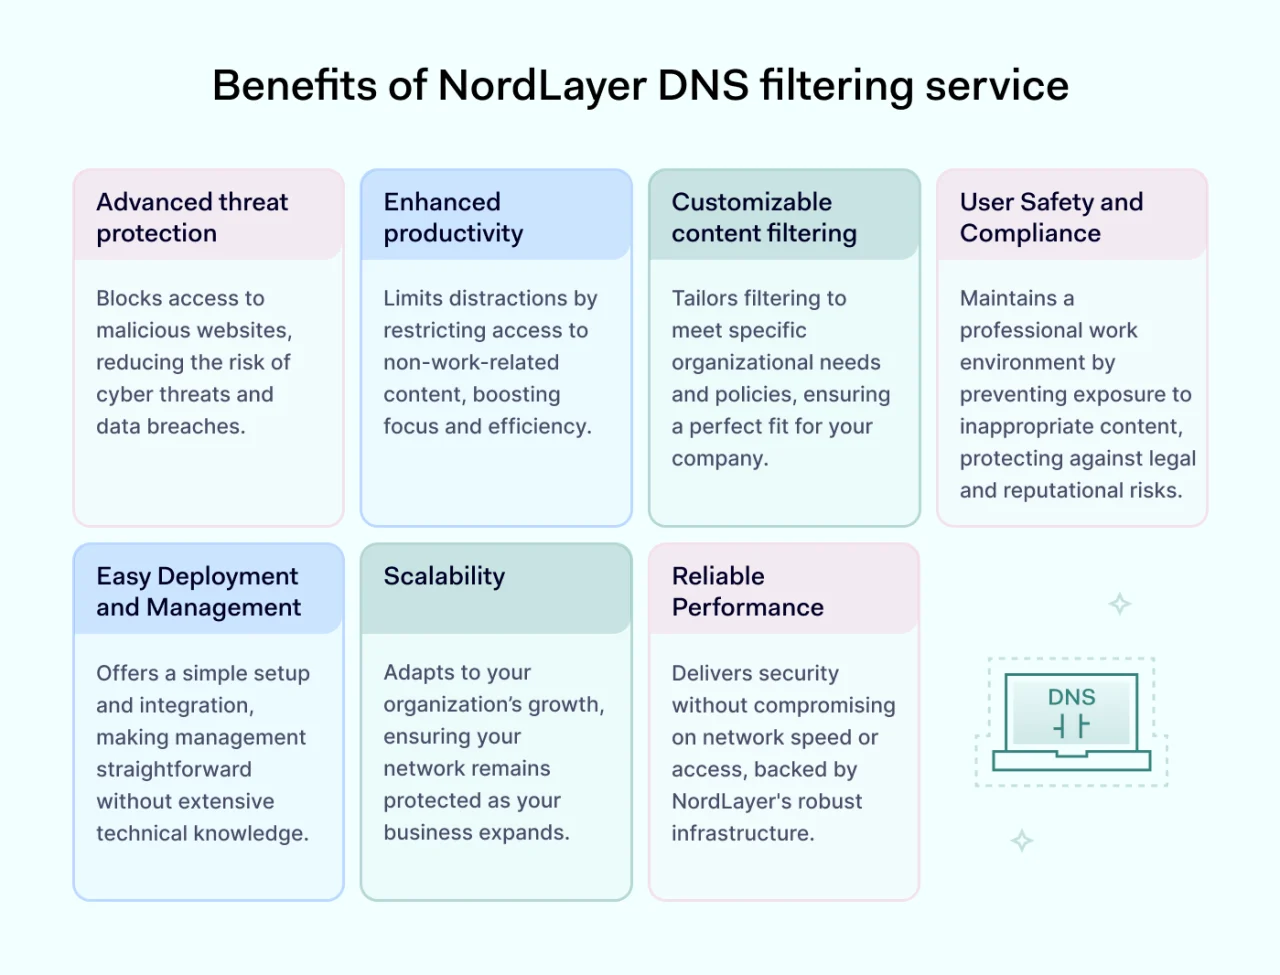
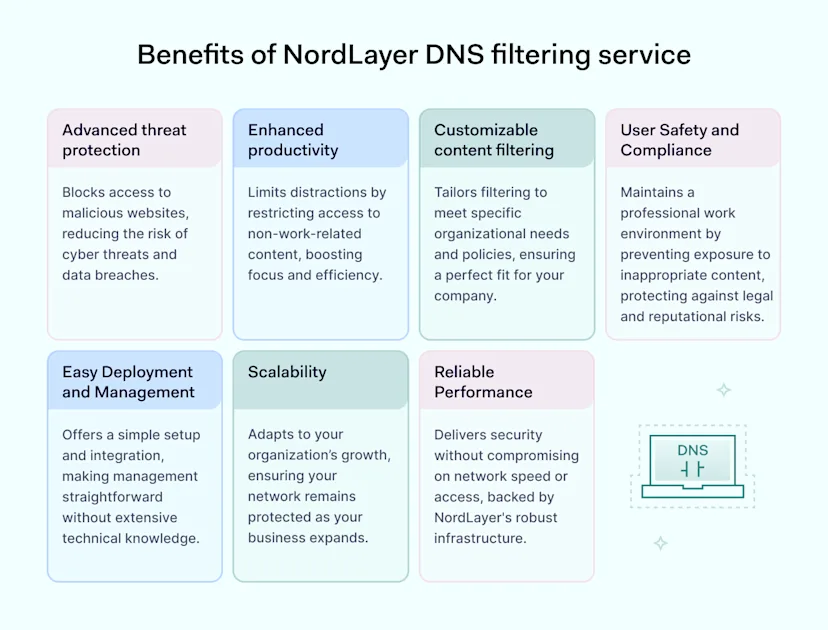
Benefits of NordLayer DNS filtering service

NordLayer’s DNS filtering service offers a comprehensive solution that addresses key organizational needs—from security and productivity to compliance and ease of management.

To keep up with the pace of the evolving internet pitfalls, NordLayer will soon introduce DNS filtering powered by machine learning. What does it mean? Our patented technology makes DNS filtering dynamic. It means that the database is constantly growing, learning, and updating itself.

Click to tweet

Its blend of advanced features, customization options, and reliable performance makes it an ideal choice for businesses looking to strengthen their network security and operational efficiency.

How to block employees from accessing websites

Already have NordLayer but didn’t enable the content filtering feature? Here’s how to do it:

1. Go to Control Panel → Network → Servers or Gateways. Choose the dedicated server, click Configure next to it, and select DNS Filtering by Category (Beta) from the dropdown menu.
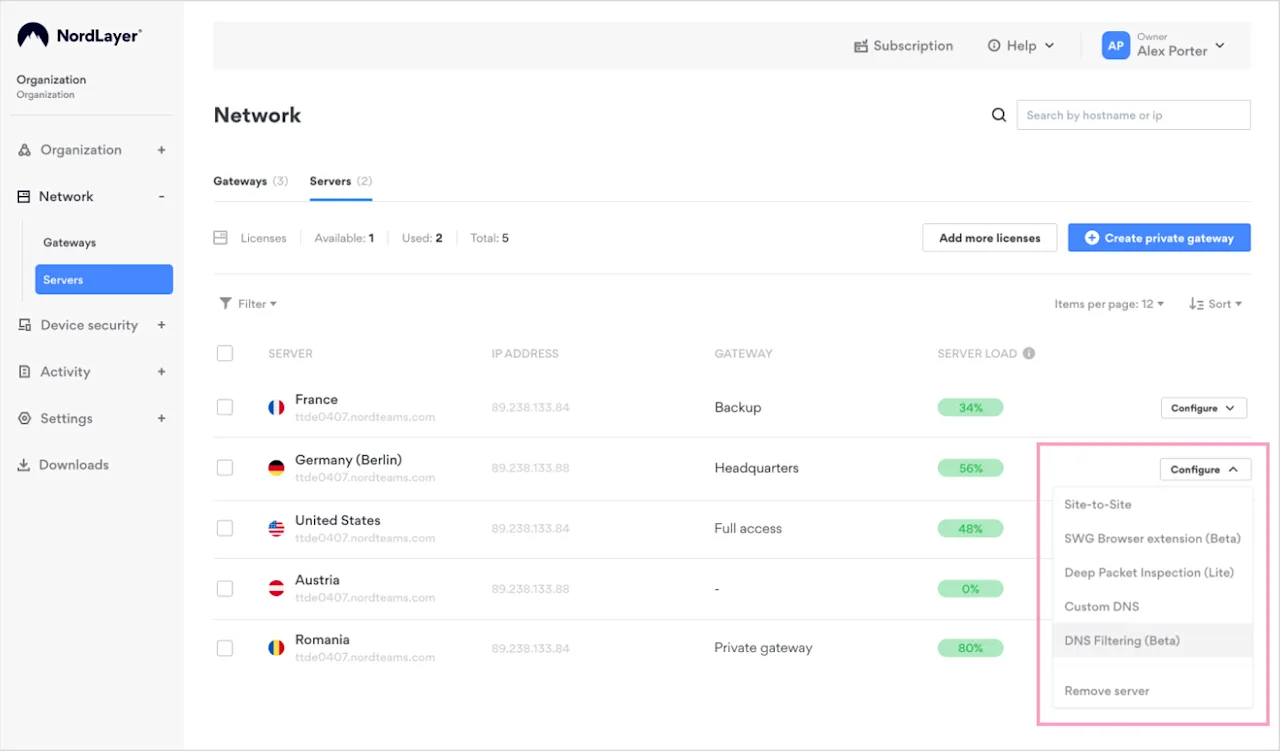
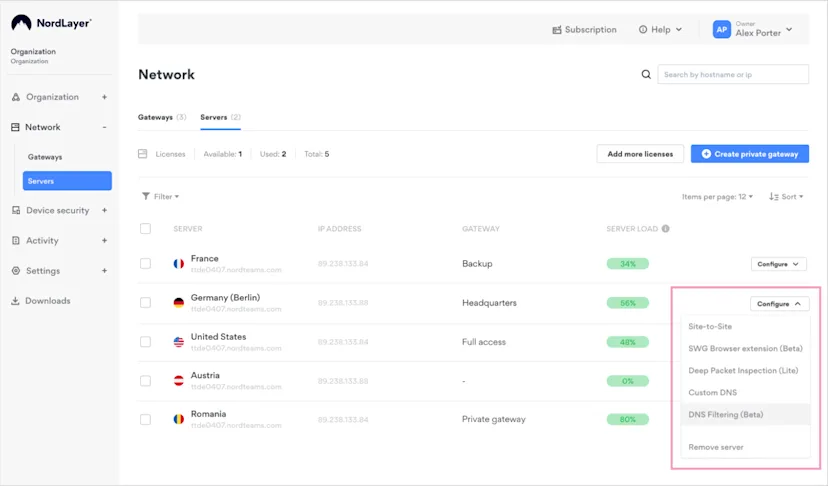
NordLayer Control Panel_DNS filtering

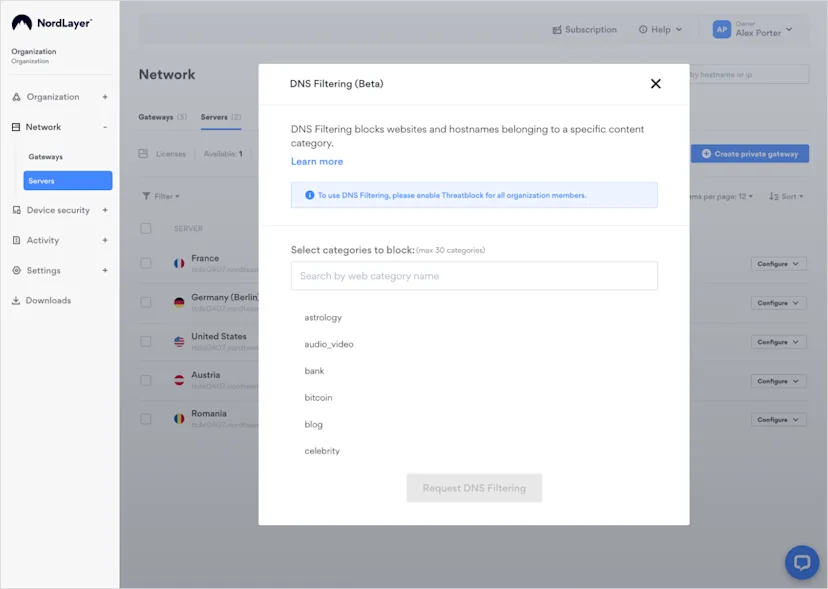
2. In the request form, select which categories you want to filter. With NordLayer, you can currently choose from 53 DNS categories to block (find the list below).

3. Once you’re done, click on Request DNS Filtering by Category. Please allow up to 24 hours for the feature to be enabled. You will get an email with the confirmation once it’s ready.
 

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

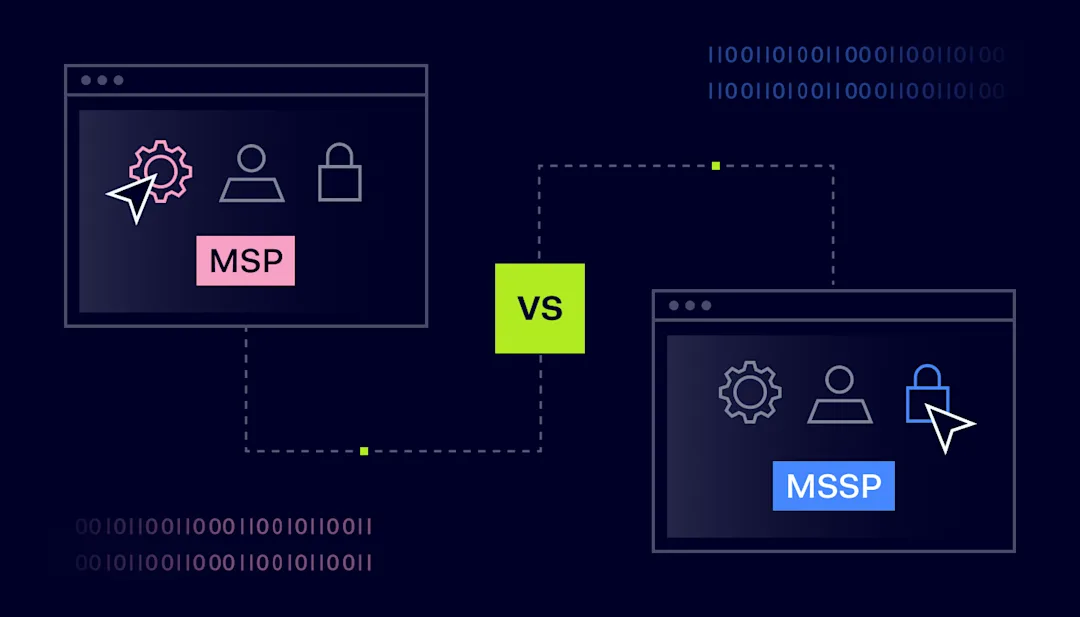
MSP vs. MSSP: what’s the difference?

Navigating the world of IT support and cybersecurity services can feel like exploring a maze. Two terms that often come up are MSP and MSSP. Though they sound similar, their roles in the IT ecosystem are distinct.

Let’s dive in to clarify these differences, helping you identify which service aligns best with your IT and cybersecurity needs.

What is an MSP?

An MSP, or Managed Service Provider, acts as your IT department’s extension or sometimes its entirety.

They manage a spectrum of IT services, from network and infrastructure to software management and support. MSPs aim to ensure your IT operations run smoothly, efficiently, and without interruption, focusing on maintenance and optimization.

What is an MSSP?

MSSP stands for Managed Security Service Provider. While MSPs cover the broader IT landscape, MSSPs focus on cybersecurity.

They monitor and manage your security devices and systems and offer threat intelligence, incident response, and more. Essentially, they’re your cybersecurity guardians, proactively defending your digital assets against threats.

Key differences between MSP and MSSP

MSPs serve as a full IT department, offering various services like network management and software updates. Their primary goal is to ensure the seamless operation and reliability of your IT infrastructure. MSPs are the technology stewards, ensuring your systems are efficient, up-to-date, and scalable to support your business objectives.

MSSPs focus narrowly yet deeply on cybersecurity, acting as vigilant protectors against cyber threats. They specialize in monitoring, managing, and responding to security risks, employing a suite of services designed to protect businesses from digital dangers. Their services range from real-time threat monitoring to incident response and compliance management, all aimed at fortifying your organization’s cybersecurity posture.

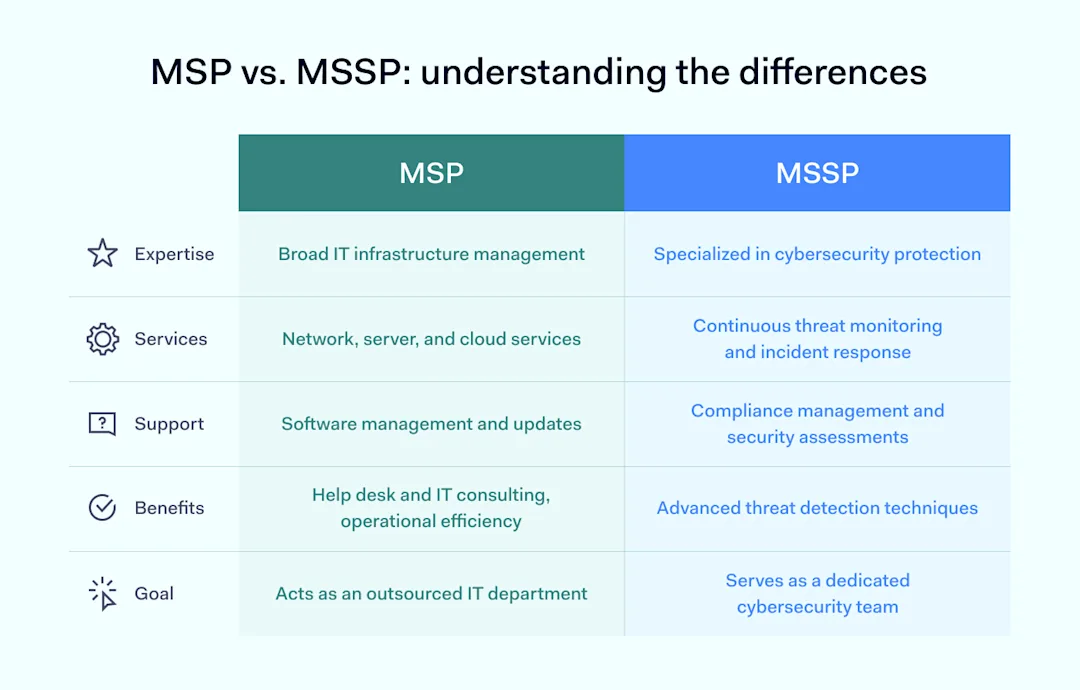
To neatly summarize the distinctions, let’s lay MSP vs. MSSP out in a table:

MSP vs MSSP: the key differencesHere’s a breakdown of their primary differences:
MSPs focus on the broader spectrum of managing and optimizing IT infrastructure and operations. They offer a wide range of services, including:

  • Managing networks, servers, and cloud services

  • Providing software management and updates

  • Help desk support and IT consulting.

The core objective of MSPs is to enhance operational efficiency and support business growth, acting essentially as an outsourced IT department.

MSSPs, on the other hand, specialize in protecting businesses from cyber threats and ensuring data security. Their services are centered around:

  • Incident response

  • Compliance management

  • Security assessments.

They use advanced methods to detect and prevent cyber threats, acting as a dedicated cybersecurity team for their clients.

While MSPs are all about ensuring that the IT infrastructure is running smoothly to support and enhance business operations. MSSPs, on the other hand, dive deeper into the cybersecurity aspect, ensuring that businesses are safeguarded against the increasing number of cyber threats.

Whether a business opts for an MSP or an MSSP depends on its primary needs: comprehensive IT management or specialized cybersecurity protection.

Click to tweet

In many cases, businesses benefit from the combined strengths of both types of providers to ensure both operational excellence and robust security.

What is the difference between MSSP and MDR?

While MSSPs focus on managing and monitoring security services, MDR (Managed Detection and Response) providers take a more hands-on approach to actively hunting, detecting, and responding to threats. Think of MSSPs as your cybersecurity watchdogs, while MDR services are the special forces that detect and neutralize threats.

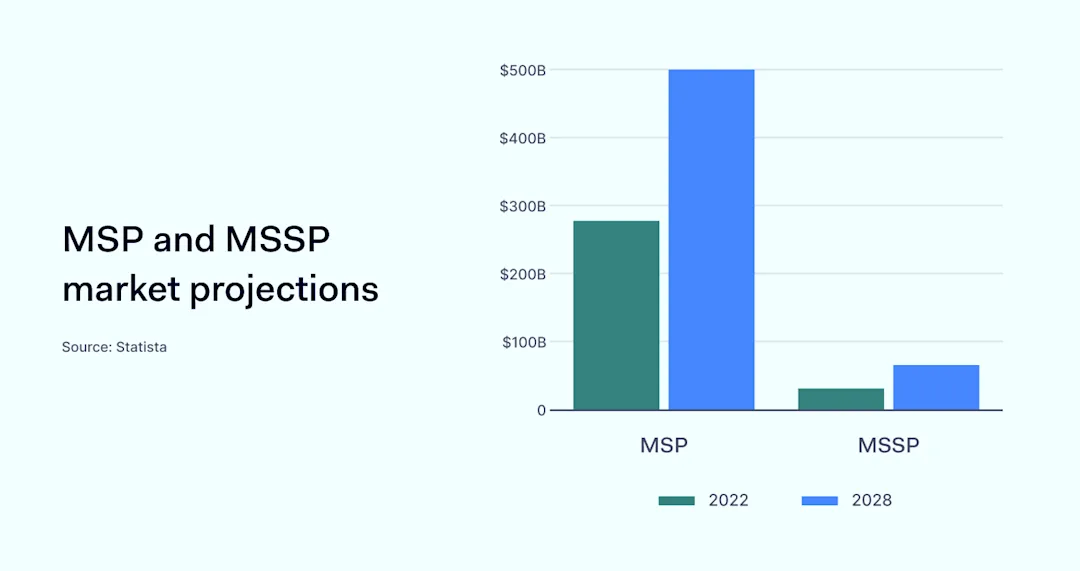
MSP and MSSP: the market growth

The global managed services market has seen consistent growth, driven by businesses’ increasing reliance on IT infrastructure and the need for efficient, scalable solutions.

According to projections, this market could grow significantly, reaching a substantial valuation by 2028. This growth is fueled by the ongoing digital transformation in various sectors, necessitating managed IT services to support operations, data management, cloud services, and customer relations.

The managed security services market is also on a robust growth trajectory, with a specific focus on cybersecurity services.

The escalating threat landscape propels this market’s expansion, regulatory compliance requirements, and the complexity of cybersecurity solutions. Businesses are increasingly outsourcing their cybersecurity needs to MSSPs to protect against data breaches and cyber-attacks and to ensure data privacy and compliance with regulations.

Factors defining MSP market growth

  • Digital transformation: as businesses continue to digitize operations, the demand for comprehensive IT services, including cloud management, data analytics, and network infrastructure, grows.

  • Cost efficiency: MSPs offer a cost-effective solution for businesses to manage their IT needs without the overhead of an in-house IT department.

  • Scalability and flexibility: the ability of MSPs to scale services according to business needs is a key driver, allowing companies to adjust their IT services based on growth and seasonal demands.

Factors responsible for MSSP market growth

  • Cybersecurity challenges: the increasing sophistication of cyber threats drives demand for MSSPs as businesses seek specialized expertise to navigate the complex cybersecurity landscape.

  • Regulatory compliance: With growing regulatory pressures around data protection, businesses turn to MSSPs for compliance assurance and to avoid potential fines.

  • Advanced threat detection and response: the need for 24/7 monitoring and quick response to security incidents has become critical, making MSSPs an essential partner for businesses.

Market differences

While both MSPs and MSSPs are integral to the IT and cybersecurity ecosystem, their markets differ primarily in focus and expertise.

MSPs are broad, covering all aspects of IT management and support, catering to businesses’ operational and efficiency needs. In contrast, MSSPs are specialized, focusing solely on cybersecurity services to protect businesses from digital threats and ensure compliance with data protection laws.

The MSP market is defined by its operational support and infrastructure management role, appealing to businesses looking for end-to-end IT services. The MSSP market, however, is driven by the need for specialized cybersecurity services, attracting businesses focused on enhancing their security posture in the face of increasing cyber threats.

Can an MSP be an MSSP?

Yes, the line between MSPs and MSSPs can blur. Some MSPs evolve to include MSSP functions, offering a hybrid model that covers both IT management and security services. This evolution reflects the growing importance of cybersecurity across all IT operations.

The managed service provider can indeed evolve into a Managed Security Service Provider. Still, this transformation requires a strategic approach, significant investment in skills and technology, and a commitment to adopting a security-first mindset.

Why make the transition?

The move from MSP to MSSP is often motivated by the growing demand for cybersecurity services. Businesses are increasingly aware of the risks posed by cyber threats and are seeking providers that can offer both IT management and robust security measures. By transitioning to an MSSP, providers can meet this demand, offering a one-stop shop for IT and security needs.

Moreover, this evolution allows providers to differentiate themselves in a crowded market, offering added value to clients through specialized security solutions. It also opens up new revenue streams, as businesses are willing to invest significantly in cybersecurity to protect their assets and reputation.


What are the deciding factors when choosing between an MSP and an MSSP for your business?

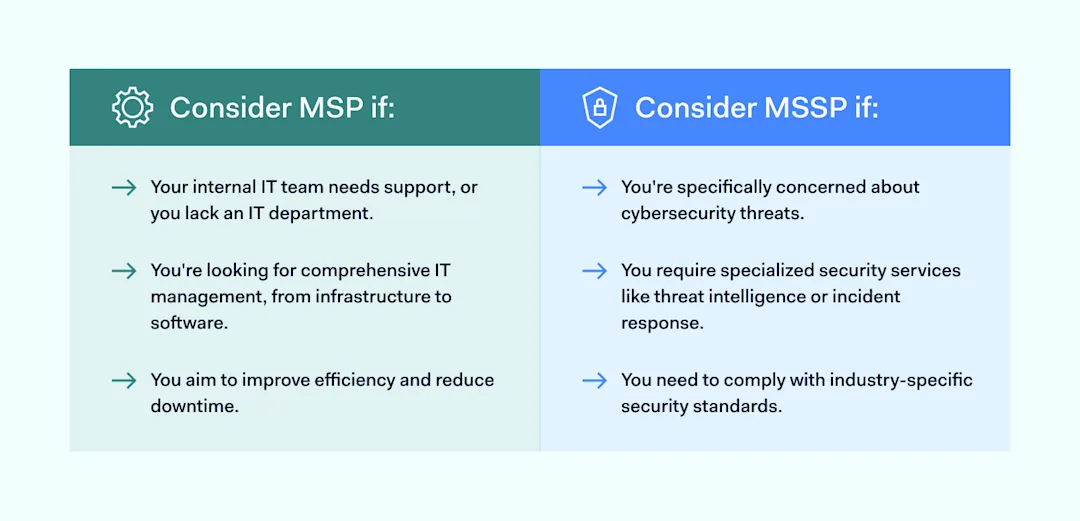
Comparing MSP vs. MSSP for your business comes down to understanding your core IT infrastructure management and cybersecurity needs. Here’s a streamlined approach to making that decision:

  • Assess business IT capabilities: if a business lacks a dedicated IT department or needs to augment its existing IT capabilities, an MSP might be the right fit. MSPs provide comprehensive IT services, ensuring your infrastructure is robust and up-to-date, with increased efficiency supporting your business operations.

  • Evaluate security requirements: if you’re particularly concerned about cybersecurity, face stringent regulatory compliance requirements, or handle sensitive data, leaning towards an MSSP makes sense. MSSPs specialize in protecting businesses from cyber threats with services like real-time monitoring, incident response, and compliance management.

  • Consider business size and sector: small to medium-sized businesses often find MSPs suitable for their broader IT needs, while larger organizations or those in high-risk sectors (e.g., finance, healthcare) may prioritize the specialized security services of an MSSP.

  • Budget and investment: determine the budget for IT and cybersecurity services. MSPs can offer more predictable costs for a range of IT services, while MSSPs might represent a higher investment focused on advanced security measures.

  • Future growth and scalability: think about business future needs. An MSP can help scale the IT infrastructure as your business grows, whereas an MSSP will ensure your cybersecurity posture scales in tandem with your risk exposure.

Selecting either an MSP or an MSSP boils down to understanding your specific needs:

Factors when choosing between an MSP and an MSSP

How NordLayer boosts MSP capabilities

Third-party providers like NordLayer step in as a powerful solution for MSPs, enhancing their capabilities to manage and secure networks with comprehensive security solutions. It offers features like Secure Remote Access, Zero Trust network architecture, and advanced threat protection.

  • Security monitoring. NordLayer amplifies MSPs’ ability to offer continuous security monitoring, which is crucial for early threat detection and maintaining a vigilant cybersecurity posture. This ensures clients are protected around the clock from a broad spectrum of cyber threats.

  • Security operations. With NordLayer’s security solutions, MSPs can enhance their security operations through automation and advanced analytics, speeding up incident response and bolstering defenses against evolving cyber threats, thereby elevating the level of service to clients.

  • Endpoint protection. NordLayer supports MSPs in implementing robust endpoint protection and safeguarding client devices against malware and other attacks, which is essential for the integrity and security of client networks.

  • Data protection. By offering encryption and secure access controls, NordLayer assists MSPs in protecting clients’ sensitive data against unauthorized access, aligning with information security regulations, and enhancing clients’ trust.

  • Cloud services. NordLayer enables secure access to cloud services, protecting data in transit to and from the cloud, an essential feature for businesses leveraging cloud-based solutions and security operations in today’s digital environment.

  • Providing cybersecurity services. Integrating NordLayer allows MSPs to expand their cybersecurity services, covering everything from security monitoring to data protection, meeting the increasing demand for comprehensive cybersecurity solutions.

These tools bolster an MSP’s service offering and ensure clients’ networks are both accessible and secure. By performing risk assessment and integrating NordLayer, MSPs can provide a more robust IT and security infrastructure, reflecting the synergy between comprehensive IT support and dedicated cybersecurity measures.

Are you looking for a trusted partner to secure your clients’ networks? NordLayer offers a Partner Program with a focus on tangible benefits for its partners and simple yet effective solutions to protect businesses in the hectic cybersecurity landscape.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.