Skip to content

The Importance of Upgrading

The Importance of Upgrading 

When thinking about keeping your network safe, upgrading networking hardware is often overlooked. It’s hard enough to get everything to play nicely together, and once it does, the last thing you want to do is disrupt that delicate balance. Plus, there’s a lot of planning, a lot of meetings, and probably a lot of money to spend. No wonder just the thought of upgrading infrastructure makes most admins want to run and hide.

Not upgrading, though, can put you at risk in a variety of ways.

EOL?  EOE?  EOS? SOL!

Nothing gold can stay, and that is as true for networking hardware as much as anything else.  As vendors develop new and exciting feature sets, old hardware gets strained more and more until, finally, it just can’t keep up.  You might not necessarily be interested in those new features – as long as the packets are flowing, who needs the latest and greatest?  And that makes sense – there’s a lot to be said for not being an early adopter.  As cool as cutting-edge innovation often sounds, it sometimes fails to deliver on its promises  (Look at the ill-fated Lily Drone, the Juicero Juicer, and the Cisco Umi – all products that showed great promise, but fell far short of expectations.)

We all understand how important it is to at least keep up with security updates, but products don’t get updates forever.  Watch out for these 3 phases of the product life cycle signify it’s time to get ready for replacements:

EOE: End of Engineering

No new features or fixes will be developed during this phase, although critical security fixes might still be released, and you can still get support….although the answer to most of your support questions will probably be “Upgrade.”

EOS: End of Support

There is no support and probably no security fixes (although if a critical vulnerability is uncovered, you might get a patch). For all intents and purposes, the product is dead. You might be able to get support assistance to upgrade, or they might help you if you run into an already-known bug.

EOL: End of Life

Stick a fork in it; it’s done – no support, no patches, no nothing.  For all intents and purposes, this product no longer exists.

Still Lurking Out There

Why does it matter if something still has vendor support?  Well, just because the vendor has seemingly forgotten about these devices does not mean hackers have.  Here’s an example:  In 2021, six years after Western Digital ended support for their My Drive line of external hard drives, a remote code execution bug resulted in many users losing all of their data.  The worst part is the vulnerability was reported to Western Digitial in 2018, a full three years before the bug was exploited, but since support for the drives had already ended Western Digital chose not to fix it.  

Sometimes those new features become default standards.  Devices in the late 90’s that shipped with 802.1a or 802.1b wireless networks were quickly rendered obsolete when a critical design flaw was found in  WEP.  Anyone not wanting a laughably easy to hack wireless password had to get completely new hardware.  Now all networking hardware ships with some form of WPA enabled.  

If you’re still not covinced, consider this: you could run afoul of the law if you use out-of-date hardware.  Many regulatory standards like GDPR, HIPAA, PCI DSS and more require organizations to take reasonable steps to protect sensitive information.  If you are the victim of a data breach, you will have a hard time justifying the use of old hardware.  It could also impact your certifications – if you maintain SOC 2 or ISO 27001, EOL hardware might put you out of compliance.   

Upgrading networking may not be the most exciting prospect, but as technology evolves and grows, it’s crucial to ensure you’re not falling behind. Proactive upgrades not only enhance your ability to stay secure, but they also keep you safe from regulatory and legal penalties in the case of a data breach.  Investing in the future by keeping your network infrastructure current will ensure you can support your organization’s goals for security, growth, and innovation going forward.  
About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

The Emergence of the Zero Trust Program Manager: A New Role in Cybersecurity

Cybersecurity roles and responsibilities are in a constant state of flux. Just as the defenders adapt, so do the adversaries. Enter the latest evolution in the cybersecurity workforce: the Zero Trust Program Manager. If you’ve been in the cybersecurity field for more than a hot minute, you’re likely aware that “Zero Trust” has become a buzzword so pervasive that it’s now almost as ubiquitous as the phrase “we take your security seriously” in every corporate breach apology letter. But unlike the latter, Zero Trust is more than just lip service. It’s a paradigm shift in how we think about securing our digital environments. And it’s precisely this shift that has given rise to the need for a dedicated role to manage it.

What Exactly is a Zero Trust Program Manager?

At its core, the Zero Trust Program Manager (ZTPM) is the strategic leader responsible for implementing and overseeing an organization’s Zero Trust architecture. This role isn’t just about managing technology; it’s about orchestrating a cultural shift in how an organization approaches security. The ZTPM is tasked with ensuring that no entity—be it user, device, or application—is inherently trusted, whether inside or outside the organization’s perimeter. Instead, everything and everyone must be continuously authenticated and authorized.

This role is a blend of project management, cybersecurity expertise, and change management. The ZTPM must work closely with various stakeholders across the organization, from IT and security teams to business leaders, to ensure that the principles of Zero Trust are understood, embraced, and effectively implemented. They are the evangelist, the educator, and the enforcer of this new security mindset.

Why Does This Role Exist Today?

The rise of the ZTPM is not just a random blip on the cybersecurity radar; it’s a direct response to the changing threat landscape and the realization that traditional perimeter-based security models are no longer sufficient. The days when securing the castle walls could keep the bad guys out are long gone—primarily because the castle doesn’t even have walls anymore. Today, organizations operate in a borderless environment where users and data move fluidly across cloud services, mobile devices, and remote locations. The traditional model of “trust but verify” has been replaced with “never trust, always verify.”

Moreover, the acceleration of digital transformation, spurred on by global events like the COVID-19 pandemic, has further blurred the lines between internal and external networks. As organizations rapidly adopted remote work models and cloud services, the attack surface expanded exponentially. In this new reality, the concept of a trusted internal network is not just outdated; it’s downright dangerous.

Enter Zero Trust—a model that doesn’t assume that anything or anyone is trustworthy just because they’re inside the network. Every request, every access attempt, every interaction is scrutinized. This approach requires a fundamental shift in how security policies are designed, enforced, and managed. And that’s where the ZTPM comes in. Their role is to steer this transformation, ensuring that Zero Trust principles are not just a checkbox on a compliance form, but a living, breathing part of the organization’s security fabric.

Scope of Responsibilities

The responsibilities of a Zero Trust Program Manager are as wide-ranging as they are critical. Here’s a closer look at what this role entails:

  1. Strategy Development and Implementation: The ZTPM is responsible for developing a comprehensive Zero Trust strategy that aligns with the organization’s business objectives. This includes defining the scope, setting milestones, and ensuring that all security policies and technologies are aligned with Zero Trust principles.
  2. Cross-Functional Collaboration: Implementing Zero Trust is not a one-department job. The ZTPM must work closely with IT, security, compliance, and business units to ensure that the Zero Trust framework is understood and adopted across the organization. This includes leading workshops, training sessions, and regular check-ins to ensure alignment.
  3. Technology Oversight: While the ZTPM isn’t necessarily the person configuring firewalls or deploying MFA solutions, they are responsible for overseeing the technology stack that supports the Zero Trust model. This includes evaluating and selecting the right tools, ensuring they are properly integrated, and monitoring their effectiveness.
  4. Change Management: Moving to a Zero Trust model is as much about changing mindsets as it is about changing technology. The ZTPM must manage the human side of this transformation, addressing resistance, ensuring proper training, and fostering a culture that supports continuous verification.
  5. Risk Management and Compliance: The ZTPM plays a crucial role in identifying and mitigating risks associated with the transition to Zero Trust. They must ensure that the organization remains compliant with relevant regulations and industry standards while adopting this new security model.
  6. Continuous Improvement: Zero Trust is not a set-it-and-forget-it approach. The ZTPM is responsible for continuously assessing the effectiveness of the Zero Trust framework, making adjustments as needed, and staying ahead of emerging threats.

Qualifications and Skills

Given the breadth of responsibilities, the ideal ZTPM is a cybersecurity Renaissance person—a Jack or Jill of many trades, with a deep understanding of security principles and a knack for project management. Key qualifications might include:

  • Experience: A strong background in cybersecurity, with experience in implementing security frameworks and leading cross-functional teams.
  • Certifications: Relevant certifications such as CISSP, CISM, or specific Zero Trust certifications can be a strong indicator of expertise.
  • Communication Skills: The ability to articulate complex security concepts to non-technical stakeholders is crucial.
  • Leadership: Proven leadership skills, particularly in driving organizational change, are essential.
  • Strategic Thinking: The ZTPM must be able to see the big picture, aligning security initiatives with broader business goals.

Zero Trust, the ZTPM & Network Access Control (NAC)

One of the critical areas where the Zero Trust Program Manager (ZTPM) must exert influence is in the realm of Network Access Control (NAC). NAC plays a pivotal role in the enforcement of Zero Trust principles, acting as one of the frontline defenses against unauthorized access. In the context of Zero Trust, NAC is not merely a gatekeeper that decides who gets in; it is a dynamic system that continuously assesses and verifies the trustworthiness of every device and user attempting to access the network.

The ZTPM must work closely with network administrators and security teams to ensure that NAC solutions are tightly integrated into the broader Zero Trust architecture. This involves configuring NAC policies to align with the Zero Trust mantra of “never trust, always verify.” For example, NAC policies may need to be updated to enforce strict access controls based on user roles, device health, and contextual factors such as the location and behavior of the device. The ZTPM oversees this integration, ensuring that the NAC system not only blocks unauthorized devices but also actively participates in the continuous monitoring and assessment of devices already within the network.

Furthermore, the ZTPM must consider how NAC fits into the overall user experience. While security is paramount, the role requires balancing stringent access controls with the need for operational efficiency. Implementing NAC in a Zero Trust environment is not just about adding layers of security; it’s about creating an adaptive, intelligent system that can respond to threats in real-time without unnecessarily hindering legitimate business activities. This means the ZTPM must ensure that NAC is fine-tuned to minimize disruptions while still providing robust protection, making it an essential tool in the Zero Trust toolkit.

By effectively managing NAC within a Zero Trust framework, the ZTPM helps to create a more resilient and responsive security posture, one where access is always under scrutiny and never taken for granted.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

The High-Stakes Chess Game: Inside the World of Ransomware Negotiation

In the shadowy world of cybersecurity that faces off with cyber criminals head-on, there exists a unique breed of professionals who spend their days playing high-stakes games with some of the most dangerous people on the planet. No, these folks aren’t undercover agents or secretive hackers—they’re ransomware negotiators. If you’ve ever imagined what it’s like to haggle with a digital pirate who just locked up your company’s crown jewels, you’re not far off. Let’s dive into the nitty-gritty of ransomware negotiation, a job that’s part therapist, part tactician, and wholly unpredictable. 

The Art of the Deal: How Ransomware Negotiation Works

Ransomware negotiation is a delicate dance, one that requires a mix of psychology, strategy, and sheer nerve. The first step in this dance often starts with the arrival of a chilling message: “Your files have been encrypted. Pay $X in Bitcoin, or say goodbye to your data.” At this point, a business has two options—try to restore from backups and hope for the best, or engage with the attackers and negotiate.

When a company chooses to negotiate, that’s when the ransomware negotiator steps in. The role isn’t about simply agreeing to a price. Oh no, it’s much more complex. These professionals assess the situation, gather intelligence on the ransomware group, and try to understand their motivations. Are they in it purely for the money? Are they likely to leak the data if they don’t get what they want? How reliable are they in actually decrypting files after payment?

Negotiators will often start by stalling for time, trying to learn as much as possible while also assessing the victim’s willingness and ability to pay. Then, they’ll typically make a counteroffer—usually lower than the ransom demand but not so low as to insult the cybercriminal’s delicate sensibilities. From there, it’s a back-and-forth, a digital haggling session that might resemble negotiating the price of a used car, if the used car dealer were holding your company’s secrets hostage.

Success Rates: The Good, the Bad, and the Encrypted

You might be wondering—how often do these negotiations actually work? The answer is, frustratingly, “it depends.” Some ransomware groups have a twisted sense of honor and will decrypt files once paid, while others may take the money and run. Negotiators generally aim to minimize the financial damage and ensure the company can get back on its feet as quickly as possible, but the outcome is never guaranteed.

However, ransomware negotiation can be surprisingly successful. Some studies suggest that negotiation can reduce ransom payments by up to 50%, and there’s often a better chance of getting files decrypted if you play your cards right. That said, even a successful negotiation is bittersweet. Paying a ransom, after all, doesn’t just make the problem go away—it can also fund future attacks, perpetuating the cycle.

Surprising Aspects of the Job: More Than Just Haggling

While the essence of the job is negotiation, the reality is that ransomware negotiators do much more than just talk numbers. They are crisis managers, often dealing with companies at their most vulnerable. Part of the job involves calming down panicked executives, explaining complex technical details to people who don’t speak “geek,” and sometimes even playing the role of an ad-hoc therapist. One negotiator might spend their morning haggling with a hacker in Eastern Europe and their afternoon explaining the concept of Bitcoin wallets to a CFO who still thinks cryptocurrency is Monopoly money.

Another surprising aspect is the ethical tightrope that negotiators must walk. There’s always the question of whether to pay or not to pay, a moral dilemma that’s about as clear-cut as a foggy morning. On one hand, paying the ransom might be the quickest way to get a company back on track. On the other hand, it’s essentially funding criminal activity. Negotiators often find themselves in the unenviable position of having to recommend the lesser of two evils, knowing that whichever path they choose, someone is going to be unhappy.

Then there’s the psychology of it all. Negotiators need to understand the mindset of the attackers. These aren’t your average criminals—they’re often highly organized and operating as part of a professional syndicate. Some even have customer support teams (yes, really) to ensure that their “clients” can navigate the payment process smoothly. Negotiators must be adept at reading between the lines, recognizing bluff from bluster, and figuring out what really motivates their counterparts.

The Final Word: A Job Like No Other

Ransomware negotiation isn’t a job for the faint of heart. It’s stressful, unpredictable, and often frustrating. But for those who thrive in high-pressure situations, it can be incredibly rewarding. There’s a certain satisfaction in outmaneuvering a criminal and helping a company recover from what could have been a devastating blow.

So, next time you think your job is stressful, spare a thought for the ransomware negotiators. They’re the unsung heroes (or antiheroes, depending on your perspective) of the digital age, navigating the murky waters of cybercrime with a steady hand and a sharp mind. And who knows—maybe one day, they’ll get their own action movie. After all, “Die Hard: Ransomware Edition” has a certain ring to it, doesn’t it?

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

The Evolution of IT Security Compliance in the Age of GenAI

Just when we thought we had seen it all—from phishing schemes that could fool even the most paranoid, to ransomware attacks that would make your average Bond villain blush—along comes Generative AI (GenAI). If you’ve ever played with one of those AI tools that can write poems, paint portraits, or even generate code snippets, you might have thought, “This is cool!” Well, so did the cybercriminals. And not in a good way.

Welcome to the new frontier of cybersecurity, where GenAI is the latest weapon in the hacker’s arsenal, and conversely, the new shield for those on the defense. It’s a cat-and-mouse game where both the cat and the mouse have just discovered rocket boosters. As we dive into this brave new world, let’s take a look at how IT security compliance is evolving, and where it’s headed.

GenAI: The Cybercriminal’s New Favorite Toy

Remember when hacking used to involve a hoodie, a dark room, and endless lines of code? Those were the good old days. Now, with GenAI, the barrier to entry has lowered significantly. Today’s cybercriminals can deploy AI tools to generate convincing phishing emails, automate the creation of malware, and even simulate entire social engineering scenarios with frightening accuracy.

Take, for example, deepfakes—those AI-generated videos that can make it seem like anyone is saying or doing anything. A little creepy, right? Now imagine a cybercriminal using that technology to impersonate a company’s CEO in a video message, instructing employees to transfer funds or divulge sensitive information. Suddenly, that phishy email from a “Nigerian prince” seems downright quaint.

GenAI can also be weaponized to exploit zero-day vulnerabilities more efficiently. By analyzing vast amounts of data at an astonishing speed, AI can identify weaknesses in systems before they are widely known and patchable. And once those vulnerabilities are found, GenAI can help create and deploy exploits faster than you can say, “Didn’t we just update the firewall?”

Cybersecurity: Fighting Fire with Fire

But all is not lost—cybersecurity companies have their own GenAI tricks up their sleeves. In fact, the same technology that’s making hackers more formidable is also giving the good guys some powerful new tools.

One of the key ways AI is being infused into cybersecurity is through predictive analytics. By analyzing patterns and trends in vast amounts of data, AI can predict potential threats before they even happen. It’s like having a crystal ball, but instead of foretelling who’s going to win the next reality TV show, it’s predicting the next big ransomware attack.

GenAI is also being used to enhance threat detection. Traditional security systems often rely on signatures—known patterns of malicious activity—to identify threats. The problem? Signatures can only detect what they already know, making them useless against new, unknown threats. Enter AI, which can analyze behaviors rather than just signatures, allowing it to identify anomalies that might indicate a cyberattack in progress, even if it’s something the system has never seen before.

And let’s not forget about response times. In the high-stakes world of cybersecurity, every second counts. AI-powered systems can respond to threats in real-time, automatically shutting down attacks as they happen and minimizing damage. It’s the digital equivalent of having an elite SWAT team on standby, ready to storm in and neutralize the threat before anyone even realizes there’s a problem.

IT Security Compliance: Playing Catch-Up

With all this innovation in the cybersecurity landscape, you might think that IT security compliance standards would be sprinting to keep up. Unfortunately, it’s more of a brisk walk. Compliance frameworks, by nature, tend to be reactive rather than proactive. They’re the rules and regulations designed to ensure that organizations maintain a certain level of security, often dictated by what’s come before rather than what’s coming next.

However, the rise of GenAI is forcing a reevaluation. Compliance standards are beginning to recognize that traditional check-the-box approaches are no longer sufficient. It’s not enough to have firewalls, antivirus software, and regular updates. Organizations now need to demonstrate that they’re using advanced, AI-driven tools to proactively identify and mitigate risks.

Moreover, compliance is increasingly focusing on data governance—how organizations manage and protect the data they collect. With GenAI capable of analyzing and generating data on an unprecedented scale, the potential for misuse is staggering. New regulations are emerging that require organizations to not only secure their data but to do so in ways that account for the unique challenges posed by AI technologies.

Another key area where compliance is evolving is in the realm of AI ethics. As organizations deploy their own AI tools, they must ensure that these tools are used responsibly. This includes everything from preventing AI from making biased decisions to ensuring that AI-generated content is accurate and not misleading. In other words, it’s not just about using AI—it’s about using it in a way that’s fair, transparent, and ethical.

The Road Ahead: Where Do We Go From Here?

So, where does IT security compliance go from here? If the past few years are any indication, we’re in for a wild ride.

First, we can expect to see more dynamic and flexible compliance standards. Instead of rigid rules that are updated every few years, we’ll likely see frameworks that are designed to evolve in real-time, incorporating the latest AI technologies and threat intelligence as they emerge. This will require closer collaboration between regulatory bodies, cybersecurity experts, and organizations themselves.

Second, we’ll see a greater emphasis on continuous monitoring and assessment. Rather than relying on periodic audits, organizations will need to demonstrate ongoing compliance through real-time reporting and automated assessments. This is where AI can once again play a key role, enabling continuous monitoring of systems and generating compliance reports automatically.

Finally, as AI continues to evolve, we’ll likely see new forms of compliance emerge that focus specifically on AI governance. This could include everything from ensuring that AI systems are transparent and explainable to implementing safeguards that prevent AI from being used for malicious purposes. In essence, we’ll need compliance frameworks that are as smart and adaptive as the AI technologies they’re designed to regulate.

Welcome to the AI-Powered IT Security Compliance Future

The integration of GenAI into both cybercriminal tactics and cybersecurity defenses marks a new chapter in the ongoing battle between good and evil in the digital realm. While the challenges are significant, so too are the opportunities. As IT security compliance evolves to meet these new realities, organizations will need to be more agile, more proactive, and more innovative than ever before.

So, buckle up. The future of IT security compliance is going to be anything but boring. And if nothing else, it’s a great excuse to finally upgrade that ancient firewall. After all, in the age of AI, you never know when a deepfake CEO might drop by with some “urgent” instructions.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

How NAC Supports NIST SP 800-53 Cybersecurity Requirements Copy

In the ever-evolving landscape of cybersecurity, organizations continuously seek robust mechanisms to protect their networks and data. One effective approach is implementing Network Access Control (NAC), which plays a critical role in meeting the stringent cybersecurity requirements set forth by the National Institute of Standards and Technology (NIST) in its Special Publication 800-53. This publication provides a catalog of security and privacy controls for federal information systems and organizations to enhance their security posture.

What is Network Access Control?

Network Access Control (NAC) is a security solution that enforces policy compliance on devices that attempt to access network resources. NAC can deny network entry, restrict access to certain areas, or place devices in a quarantined area until they meet the network’s security standards. This mechanism is vital in preventing unauthorized access and managing the security of devices over their lifecycle. 

Alignment of NAC with NIST SP 800-53

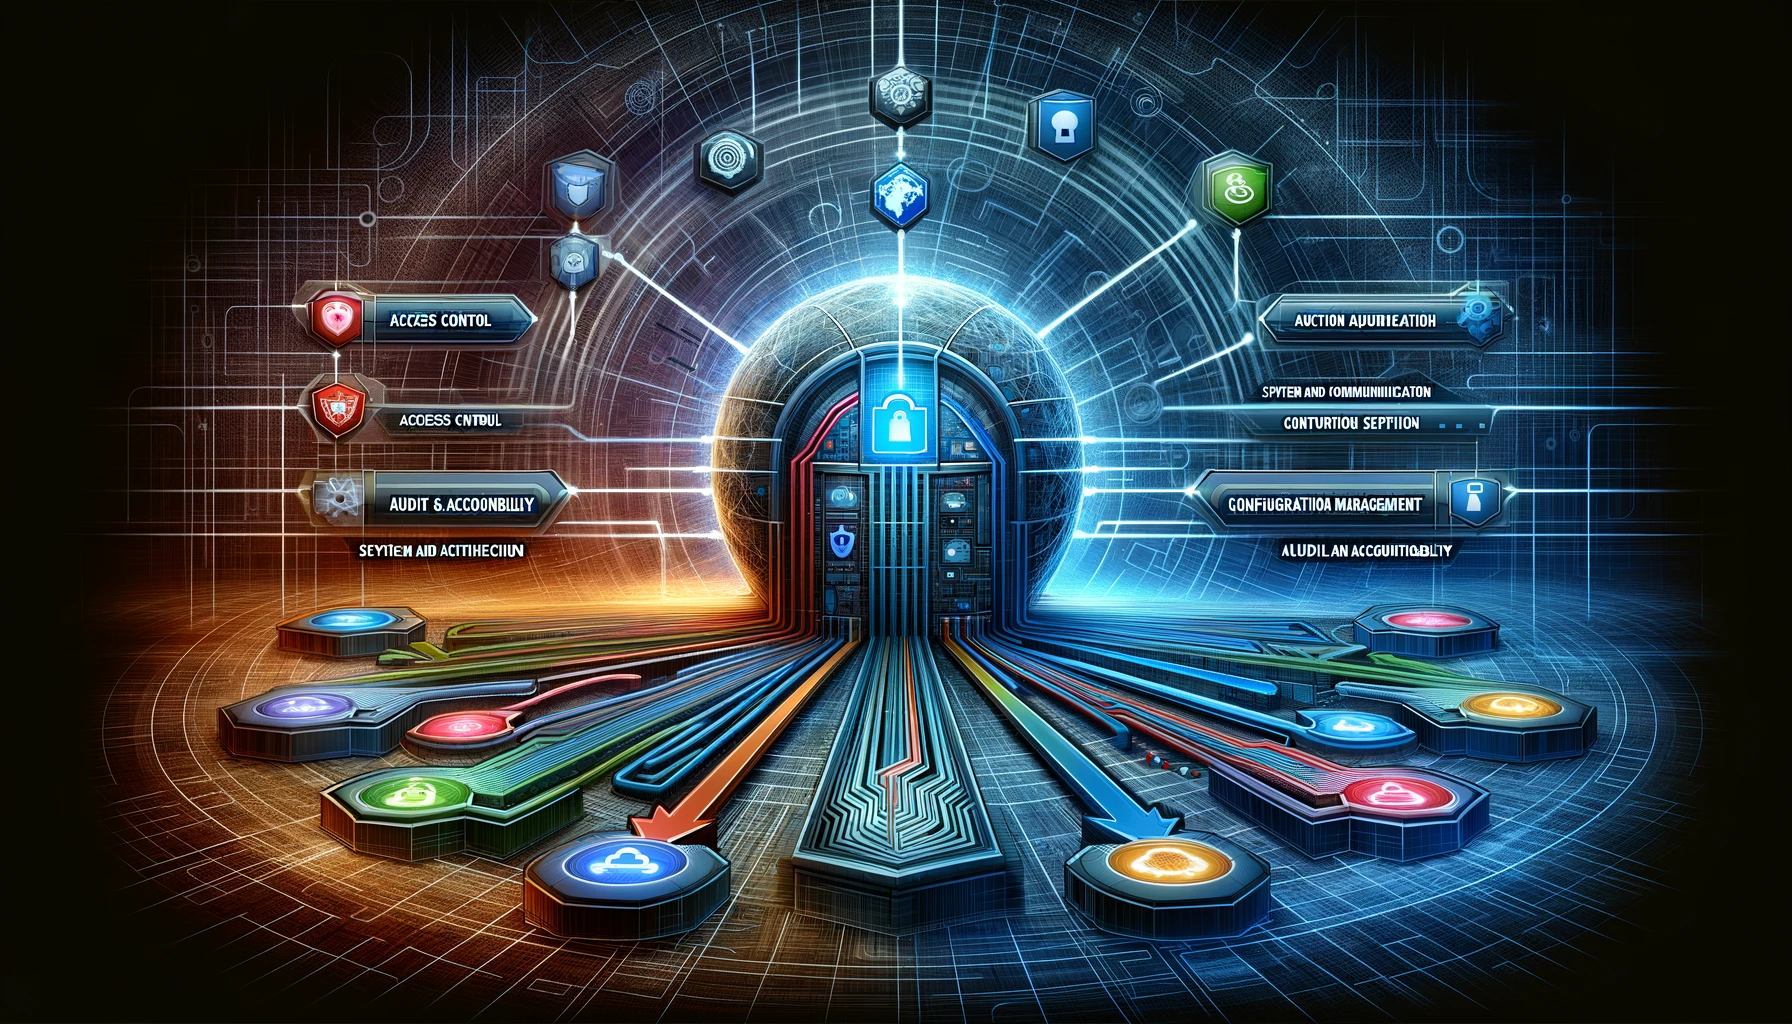
NAC supports several key security controls outlined in NIST SP 800-53, ensuring that organizational networks remain secure and resilient against threats. Here’s how NAC aligns with some of these controls:

1. Access Control (AC)

NAC systems are paramount in enforcing access control policies by ensuring that only authenticated and authorized devices can access network resources. This is in line with AC-3 (Access Enforcement) and AC-17 (Remote Access), which mandate that access to organizational systems is controlled and managed effectively.

2. Identification and Authentication (IA)

By integrating with identity management solutions, NAC ensures that all devices are properly identified and authenticated before gaining network access, aligning with IA-2 (Identification and Authentication). This prevents unauthorized devices from accessing sensitive data and systems.

3. System and Communications Protection (SC)

NAC contributes to the protection of system boundaries through policies that isolate and control the flow of information between networks. SC controls, such as SC-7 (Boundary Protection), are supported by NAC solutions that monitor and control communications at the boundaries of network segments.

4. Audit and Accountability (AU)

NAC systems can log and monitor all attempts to access the network, providing a detailed account of device activities. This supports AU-2 (Audit Events) and AU-12 (Audit Generation) requirements by ensuring that actions affecting security are recorded and available for review.

5. Configuration Management (CM)

NAC aids in maintaining the security configuration of devices throughout their lifecycle. By ensuring devices comply with CM-7 (Least Functionality), NAC restricts software installations and functions that might compromise security.


Benefits of Implementing NAC in Alignment with NIST SP 800-53

Implementing NAC not only supports compliance with NIST SP 800-53 but also brings several benefits to organizational cybersecurity strategies:

  • Enhanced Visibility and Control: NAC provides complete visibility of all devices on the network, including BYOD and guest devices, allowing for better control of who accesses what resources.
  • Automated Response: NAC can automatically respond to non-compliance and security threats by restricting access or quarantining devices, thus reducing the risk of security breaches.
  • Regulatory Compliance: For organizations subject to regulations, NAC helps in maintaining continuous compliance with security policies and regulations.

The alignment of Network Access Control with NIST SP 800-53 requirements is a testament to its value in a comprehensive cybersecurity strategy. By enforcing robust access control, ensuring proper identification and authentication, and supporting system integrity and accountability, NAC not only adheres to but enhances the security controls recommended by NIST. As cyber threats continue to evolve, the role of NAC in securing network environments remains indispensable, ensuring that organizations can protect their critical information assets effectively.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。