ESET launches Version 3.0 of Secure Authentication

Bratislava – ESET, a global leader in cybersecurity, has launched Version 3.0 of ESET Secure Authentication (ESA), a multifactor authentication solution that allows businesses of all sizes to secure mobile devices, prevent data breaches, and meet compliance requirements. This new version of the solution brings a range of updates, including the introduction of the Identity Connector and support for biometric authentication.

The Identity Connector gives customers the option to employ ESA to protect any service or application that uses a third-party identity provider, via the SAML authentication protocol integration. This significantly extends integration capabilities, now allowing customers to use ESA to protect access to a wide range of services and environments, such as email, VPN, Office 365 or Dropbox.

Version 3.0 also introduces support for native biometric authentication in ESA mobile apps, meaning users can now use integrated fingerprint scanners and facial recognition when approving authentication requests.

The new Notification Center gives users the option to configure their own notifications, so they can be proactively informed without the need to be logged in. The update also provides major performance improvements, bringing customers a robust solution to cover larger deployments.

Vladimír Maťovčík, senior product manager at ESET, states: “Business security solutions need to be reliable, be easy to use and cause minimal impact to a company’s processes. With an increasing need for organizations to protect a range of devices and environments, ESET Secure Authentication provides a simple, effective mobile-based solution that secures data and cloud access without affecting employee productivity.”

“The introduction of the Identity Connector increases the solution’s level of security, whilst the improved performance and addition of support of iOS and Android biometrics makes the experience even smoother for users.” 

For further information on ESET Secure Authentication, click here.  


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

ESET to Lead Linux Malware Workshop and Showcase Groundbreaking Amazon Echo KRACK Research at RSA 2020

Bratislava, Slovakia – January 23, 2020 ESET, a global leader in IT security, today announced a number of activities at next month’s RSA Conference 2020 (February 24-28 in San Francisco). 

ESET Malware Researcher Marc-Etienne M. Léveillé will lead a main stage workshop titled “Hunting Linux Malware for Fun and Flags.” The 50-minute workshop will take place on February 27 at 1:30 PM at Moscone West 3002. Attendees will learn to fight real-world Linux malware targeting server environments and to search for malicious processes and concealed backdoors in a compromised web server. Several examples of malware will be demonstrated with increasing layers of complexity, from scripts to ELF binaries with varying degrees of obfuscation.

ESET Senior Malware Researcher Robert Lipovský and Senior Detection Engineer, Štefan Svorenčík will present a 30-minute session on “Kr00k: How KRACKing Amazon Echo Exposed a Billion+ Vulnerable Wi-Fi Devices” on Wednesday, February 26 at 3:00pm PT at Moscone South. 

On the RSA trade show floor, ESET will be located at booth #753 in the South Hall. Senior Malware Researcher Robert Lipovský will discuss ESET’s latest cutting-edge threat research, including Operation Ghost and KRACKing the Amazon Echo. Malware Removal Support Supervisor James Rodewald will be leading demonstrations of ESET’s award-winning enterprise, SMB and consumer products. Malware Researcher Marc-Etienne M. Léveillé will also review his conference presentation and answer questions from attendees. 

Directly outside the conference, ESET will be running a four-day contest. Attend any of ESET’s inspiring presentations or live demos and get a chance to win the newest MacBook Pro 13, an iPhone 11, iPad, or Apple Watch in a prize raffle. Please see here for more details and contest rules. 

“RSA is a fantastic opportunity for our customers – both current and prospective – to see our multilayered suite of security solutions in action,” said Tony Anscombe, chief security evangelist at ESET. “The cybersecurity landscape has evolved drastically over the past decade, and we expect this to continue in the years to come. ESET is proud to be at the forefront of the field, and we are looking forward to showcasing our groundbreaking research, both on stage and at our trade show booth. We’re excited to meet and talk to attendees next month at RSA.”

Want to meet on-site with ESET at RSA? Please visit https://www.eset.com/us/rsac/.


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Amid student protests, Winnti Group targets Hong Kong universities, ESET discovers

BRATISLAVA, MONTREAL – ESET researchers have recently discovered a new campaign by the Winnti group. This time, Hong Kong universities were the desired target. ESET’s machine-learning engine detected a unique, malicious sample on multiple computers belonging to two Hong Kong universities. In addition to the two confirmed compromised universities, ESET has indications that at least three additional universities may have been affected. The attackers were interested in stealing information from the victims’ machines. This campaign of the Winnti Group was taking place as widespread civic protests swept Hong Kong, including the territory’s universities.

The latest research into Winnti Group, previously responsible for high-profile supply-chain attacks against the video game and software development industry as well as attacks against healthcare and education sectors, confirms that the group is still using its flagship ShadowPad backdoors. However, in the campaign against Hong Kong universities, ShadowPad’s launcher was replaced with a new and simpler version detected by ESET products as Win32/Shadowpad.C.

“Both ShadowPad and Winnti, found at these universities in November 2019, contain campaign identifiers and command & control URLs matching the name of the universities, which indicates a targeted attack,” says Mathieu Tartare, leading ESET researcher into the Winnti Group.

“ShadowPad is a multi-modular backdoor and, by default, every keystroke is recorded using the Keylogger module. The use of this module by default indicates that the attackers are interested in stealing information from the victims’ machines. In contrast, the variants we described in our earlier whitepaper didn’t even have that module embedded,” elaborates Tartare on the discovery.

For more technical details about the latest discovery into the Winnti Group, read the blog post Winnti Group targeting universities in Hong Kong on WeLiveSecurity.com. ESET researchers recently published a whitepaper updating our understanding of the arsenal of the Winnti Group as well. Make sure to follow ESET research on Twitter for the latest news from ESET Research. 


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

ESET identifies Latin American banking trojan, Mispadu, targeting victims with malicious Facebook ads

BRATISLAVA – ESET, a global leader in cybersecurity, continues its research into Latin American banking trojans with the identification of another previously unknown malware family, Mispadu.

Similar to the Amavaldo and Casbaneiro malware families recently described by ESET, Mispadu is written in Delphi and targets victims through the use of fake pop-up windows trying to persuade potential victims to share their personal details and credentials. The Mispadu banking trojan, which primarily targets Brazil and Mexico, contains backdoor functionality, can take screenshots, simulates mouse and keyboard actions, and captures keystrokes.

The ESET research team has seen the Mispadu family using two different distribution methods – spam and malvertising. While the former is common among Latin American banking trojans, the latter is quite rare. The threat actor behind Mispadu places sponsored advertisements on Facebook that offer fake discount coupons for McDonald’s. Clicking on the advertisement leads the potential victim to a malicious webpage where a ZIP file containing an MSI installer, masquerading as a discount coupon, can be downloaded. If downloaded and executed, a chain of three scripts follows, resulting in the download and execution of the Mispadu banking trojan. The trojan uses four potentially unwanted applications, all modified copies of legitimate software, to extract the victim’s stored credentials from web browsers and email clients.

In Brazil, Mispadu has been seen also distributing an interesting, malicious Google Chrome extension. The extension claims to “Protect your Chrome,” but instead it attempts to steal credit card and online banking data, and can even compromise Boleto, a popular payment system in Brazil that uses a barcode-based ticketing system to transfer payments. The Boleto component of the Mispadu malware attack is its most advanced feature, as it replaces the legitimate barcode on a Boleto ticket with one connected to the attacker’s bank account, generated via the abuse of a legitimate website.

For more details, read the blog post, Mispadu: advertisement for a discounted Unhappy Meal, on WeLiveSecurity.

About Version 2 Limited

Version 2 Limited is one of the most dynamic IT companies in Asia. The company develops and distributes IT products for Internet and IP-based networks, including communication systems, Internet software, security, network, and media products. Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 Limited offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Tracking down the developer of Android adware affecting millions of users

We detected a large adware campaign running for about a year, with the involved apps installed eight million times from Google Play alone.We identified 42 apps on Google Play as belonging to the campaign, which had been running since July 2018. Of those, 21 were still available at the time of discovery. We reported the apps to the Google security team and they were swiftly removed. However, the apps are still available in third-party app stores. ESET detects this adware, collectively, as Android/AdDisplay.Ashas.

Figure 1. Apps of the Android/AdDisplay.Ashas family reported to Google by ESET
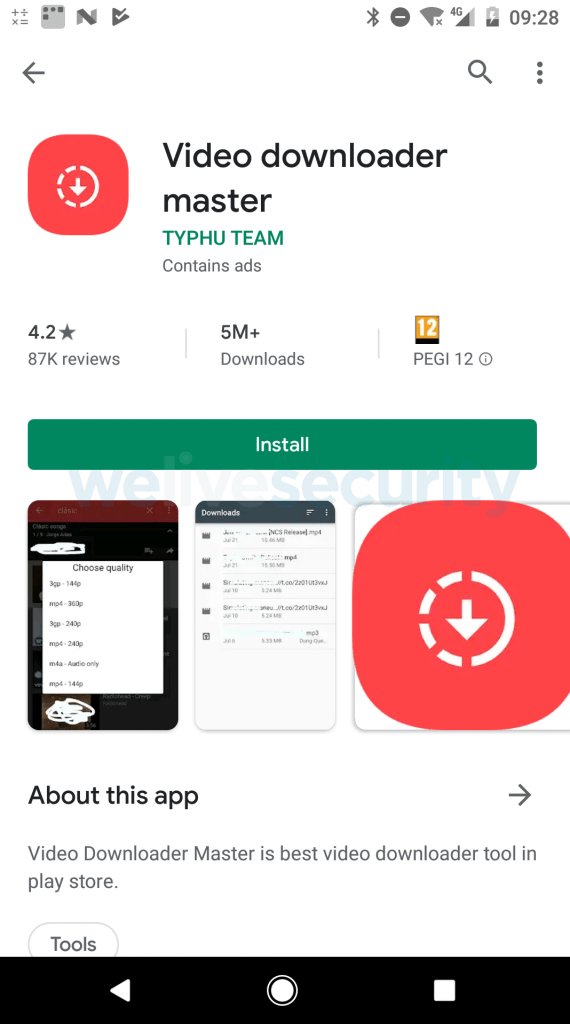
Figure 2. The most popular member of the Android/AdDisplay.Ashas family on Google Play was “Video downloader master” with over five million downloads

Ashas functionality

All the apps provide the functionality they promise, besides working as adware. The adware functionality is the same in all the apps we analyzed. [Note: The analysis of the functionality below describes a single app, but applies to all apps of the Android/AdDisplay.Ashas family.]

Once launched, the app starts to communicate with its C&C server (whose IP address is base64-encoded in the app). It sends “home” key data about the affected device: device type, OS version, language, number of installed apps, free storage space, battery status, whether the device is rooted and Developer mode enabled, and whether Facebook and FB Messenger are installed.

Figure 3. Sending information about the affected device

The app receives configuration data from the C&C server, needed for displaying ads, and for stealth and resilience.

Figure 4. Configuration file received from the C&C server

As for stealth and resilience, the attacker uses a number of tricks.

First, the malicious app tries to determine whether it is being tested by the Google Play security mechanism. For this purpose, the app receives from the C&C server the isGoogleIp flag, which indicates whether the IP address of the affected device falls within the range of known IP addresses for Google servers. If the server returns this flag as positive, the app will not trigger the adware payload.

Second, the app can set a custom delay between displaying ads. The samples we have seen had their configuration set to delay displaying the first ad by 24 minutes after the device unlocks. This delay means that a typical testing procedure, which takes less than 10 minutes, will not detect any unwanted behavior. Also, the longer the delay, the lower the risk of the user associating the unwanted ads with a particular app.

Third, based on the server response, the app can also hide its icon and create a shortcut instead. If a typical user tries to get rid of the malicious app, chances are that only the shortcut ends up getting removed. The app then continues to run in the background without the user’s knowledge. This stealth technique has been gaining popularity among adware-related threats distributed via Google Play.

Figure 5. Time delay to postpone displaying ads implemented by the adware

Once the malicious app receives its configuration data, the affected device is ready to display ads as per the attacker’s choice; each ad is displayed as a full screen activity. If the user wants to check which app is responsible for the ad being displayed, by hitting the “Recent apps” button, another trick is used: the app displays a Facebook or Google icon, as seen in Figure 6. The adware mimics these two apps to look legitimate and avoid suspicion – and thus stay on the affected device for as long as possible.

Figure 6. The adware activity impersonates Facebook (left). If the user long-presses the icon, the name of the app responsible for the activity is revealed (right).

Finally, the Ashas adware family has its code hidden under the com.google.xxx package name. This trick – posing as a part of a legitimate Google service – may help avoid scrutiny. Some detection mechanisms and sandboxes may whitelist such package names, in an effort to prevent wasting resources.

Figure 7. Malicious code hidden in a package named “com.google”

Hunting down the developer

Using open-source information, we tracked down the developer of the adware, who we also identified as the campaign’s operator and owner of the C&C server. In the following paragraphs, we outline our  efforts to discover other applications from the same developer and protect our users from it.

First, based on information that is associated with the registered C&C domain, we identified the name of the registrant, along with further data like country and email address, as seen in Figure 8.

Figure 8. Information about the C&C domain used by the Ashas adware

Knowing that the information provided to a domain registrar might be fake, we continued our search. The email address and country information drove us to a list of students attending a class at a Vietnamese university – corroborating the existence of the person under whose name the domain was registered.
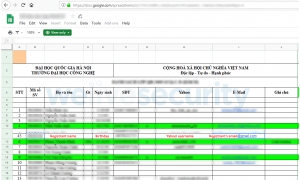
Figure 9. A university class student list including the C&C domain registrant

Due to poor privacy practices on the part of our culprit’s university, we now know his date of birth (probably: he seemingly used his birth year as part of his Gmail address, as further partial confirmation), we know that he was a student and what university he attended. We were also able to confirm that the phone number he provided to the domain registrar was genuine. Moreover, we retrieved his University ID; a quick googling showed some of his exam grades. However, his study results are out of the scope of our research.

Based on our culprit’s email address, we were able to find his GitHub repository. His repository proves that he is indeed an Android developer, but it contained no publicly available code of the Ashas adware at the time of writing of this blogpost.

However, a simple Google search for the adware package name returned a “TestDelete” project that had been available in his repository at some point

The malicious developer also has apps in Apple’s App Store. Some of them are iOS versions of the ones removed from Google Play, but none contain adware functionality.

Figure 10. The malicious developer’s apps published on the App Store which don’t contain the Ashas adware

Searching further for the malicious developer’s activities, we also discovered his Youtube channel propagating the Ashas adware and his other projects. As for the Ashas family, one of the associated promotional videos, “Head Soccer World Champion 2018 – Android, ios” was viewed almost three million times and two others reached hundreds of thousands of views, as seen in Figure 11.

Figure 11. YouTube channel of the malicious developer

His YouTube channel provided us with another valuable piece of information: he himself features in a video tutorial for one of his other projects. Thanks to that project, we were able to extract his Facebook profile – which lists his studies at the aforementioned university.

Figure 12. Facebook profile of the C&C domain registrar (cover picture and profile picture edited out)

Linked on the malicious developer’s Facebook profile, we discovered a Facebook page, Minigameshouse, and an associated domain, minigameshouse[.]net. This domain is similar to the one the malware author used for his adware C&C communication, minigameshouse[.]us.

Checking this Minigameshouse page further indicates that this person is indeed the owner of the minigameshouse[.]us domain: the phone number registered with this domain is the same as the phone number appearing on the Facebook page.

Figure 13. Facebook page managed by the C&C domain registrant uses the same base domain name (minigameshouse) and phone number as the registered malicious C&C used by the Ashas adware

Of interest is that on the Minigameshouse Facebook page, the malicious developer promotes a slew of games beyond the Ashas family for download on both Google Play and the App Store. However, all of those have been removed from Google Play – despite the fact that some of them didn’t contain any adware functionality.

On top of all this, one of the malicious developer’s YouTube videos – a tutorial on developing an “Instant Game” for Facebook – serves as an example of operational security completely ignored. We were able to see that his recently visited web sites were Google Play pages belonging to apps containing the Ashas adware. He also used his email account to log into various services in the video, which identifies him as the adware domain owner, beyond any doubt.

Thanks to the video, we were even able to identify three further apps that contained adware functionality and were available on Google Play.

Figure 14. Screenshots from this developer’s YouTube video shows history of checking Ashas adware on Google Play

ESET telemetry

Figure 15. ESET detections of Android/AdDisplay.Ashas on Android devices by country

Is adware harmful?

Because the real nature of apps containing adware is usually hidden to the user, these apps and their developers should be considered untrustworthy. When installed on a device, apps containing adware may, among other things:

  • Annoy users with intrusive advertisements, including scam ads
  • Waste the device’s battery resources
  • Generate increased network traffic
  • Gather users’ personal information
  • Hide their presence on the affected device to achieve persistence
  • Generate revenue for their operator without any user interaction

Conclusion

Based solely on open source intelligence, we were able to trace the developer of the Ashas adware and establish his identity and discover additional related adware-infected apps. Seeing that the developer did not take any measures to protect his identity, it seems likely that his intentions weren’t dishonest at first – and this is also supported by the fact that not all his published apps contained unwanted ads.

At some point in his Google Play “career”, he apparently decided to increase his ad revenue by implementing adware functionality in his apps’ code. The various stealth and resilience techniques implemented in the adware show us that the culprit was aware of the malicious nature of the added functionality and attempted to keep it hidden.

Sneaking unwanted or harmful functionality into popular, benign apps is a common practice among “bad” developers, and we are committed to tracking down such apps. We report them to Google and take other steps to disrupt malicious campaigns we discover. Last but not least, we publish our findings to help Android users protect themselves.

Indicators of Compromise (IoCs)

Package nameHashInstalls
com.ngocph.masterfreec1c958afa12a4fceb595539c6d208e6b103415d75,000,000+
com.mghstudio.ringtonemaker7a8640d4a766c3e4c4707f038c12f30ad7e21876500,000+
com.hunghh.instadownloader8421f9f25dd30766f864490c26766d381b89dbee500,000+
com.chungit.tank1990237f9bfe204e857abb51db15d6092d350ad3eb01500,000+
com.video.downloadmasterfree43fea80444befe79b55e1f05d980261318472dff100,000+
com.massapp.instadownloader1382c2990bdce7d0aa081336214b78a06fceef62100,000+
com.chungit.tankbattle1630b926c1732ca0bb2f1150ad491e19030bcbf2100,000+
com.chungit.basketball188ca2d47e1fe777c6e9223e6f0f487cb5e98f2d100,000+
com.applecat.worldchampion2018502a1d6ab73d0aaa4d7821d6568833028b6595ec100,000+
org.minigamehouse.photoalbuma8e02fbd37d0787ee28d444272d72b894041003a100,000+
com.mngh.tuanvn.fbvideodownloader035624f9ac5f76cc38707f796457a34ec2a97946100,000+
com.v2social.socialdownloader2b84fb67519487d676844e5744d8d3d1c935c4b7100,000+
com.hikeforig.hashtag8ed42a6bcb14396563bb2475528d708c368da316100,000+
com.chungit.heroesjumpc72e92e675afceca23bbe77008d921195114700c100,000+
com.mp4.video.downloader61E2C86199B2D94ABF2F7508300E3DB44AE1C6F1100,000+
com.videotomp4.downloader1f54e35729a5409628511b9bf6503863e9353ec950,000+
boxs.puzzles.Puzzleboxb084a07fdfd1db25354ad3afea6fa7af497fb7dc50,000+
com.intatwitfb.download.videodownloader8d5ef663c32c1dbcdd5cd7af14674a02fed3046750,000+
com.doscreenrecorder.screenrecordere7da1b95e5ddfd2ac71587ad3f95b2bb5c0f365d50,000+
com.toptools.allvideodownloader32E476EA431C6F0995C75ACC5980BDBEF07C8F7F50,000+
com.top1.videodownloadera24529933f57aa46ee5a9fd3c3f7234a1642fe1710,000+
com.santastudio.headsoccer286d48c25d24842bac634c2bd75dbf721bcf4e2ea10,000+
com.ringtonemakerpro.ringtonemakerapp20195ce9f25dc32ac8b00b9abc3754202e96ef7d66d910,000+
com.hugofq.solucionariodebaldor3bb546880d93e9743ac99ad4295ccaf98292026010,000+
com.anit.bouncingball6e93a24fb64d2f6db2095bb17afa12c34b2c845210,000+
com.dktools.liteforfb7bc079b1d01686d974888aa5398d6de54fd9d11610,000+
net.radiogroup.tvnradioba29f0b4ad14b3d77956ae70d812eae6ac761bee10,000+
com.anit.bouncingball6E93A24FB64D2F6DB2095BB17AFA12C34B2C845210,000+
com.floating.tube.bymuicv6A57D380CDDCD4726ED2CF0E98156BA404112A5310,000+
org.cocos2dx.SpiderSolitaireGamesadbb603195c1cc33f8317ba9f05ae9b74759e75b5,000+
games.puzzle.crosssum31088dc35a864158205e89403e1fb46ef6c2c3cd5,000+
dots.yellow.craft413ce03236d3604c6c15fc8d1ec3c9887633396c5,000+
com.tvngroup.ankina.reminderWater5205a5d78b58a178c389cd1a7b6651fe5eb7eb095,000+
com.hdevs.ringtonemaker2019ba5a4220d30579195a83ddc4c0897eec9df59cb75,000+
com.carlosapps.solucionariodebaldor741a95c34d3ad817582d27783551b5c85c4c605b5,000+
com.mngh1.flatmusic32353fae3082eaeedd6c56bb90836c89893dc42c5,000+
com.tvn.app.smartnoteddf1f864325b76bc7c0a7cfa452562fe0fd413511,000+
com.thrtop.alldownloaderf46ef932a5f8e946a274961d5bdd789194bd2a7d1,000+
com.anthu91.soccercard0913a34436d1a7fcd9b6599fba64102352ef2a4a1,000+
com.hugofq.wismichudosmildiecisiete4715bd777d0e76ca954685eb32dc4d16e609824f1,000+
com.gamebasketball.basketballperfectshote97133aaf7d4bf90f93fefb405cb71a2877908391,000+
com.nteam.solitairefree3095f0f99300c04f5ba877f87ab86636129769b1100+
com.instafollowers.hiketop3a14407c3a8ef54f9cba8f61a271ab94013340f81+

C&C server

http://35.198.197[.]119:8080


MITRE ATT&CK techniques

TacticIDNameDescription
Initial AccessT1475Deliver Malicious App via Authorized App StoreThe malware impersonates legitimate services on Google Play
PersistenceT1402App Auto-Start at Device BootAn Android application can listen for the BOOT_COMPLETED broadcast, ensuring that the app’s functionality will be activated every time the device starts
ImpactT1472Generate Fraudulent Advertising RevenueGenerates revenue by automatically displaying ads

Kudos to @jaymin9687 for bringing the problem of unwanted ads in the “Video downloader master” app to our attention.  


About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

