Skip to content

訊連科技FaceMe®於最新NIST人臉辨識測試名列前茅 為全球排名第6及排除中國廠商之全球第1之開發廠商

【2021年1月26日,台北訊】 全球頂尖AI臉部辨識領導廠商訊連科技(5203.TW) 宣布,旗下FaceMe® AI臉部辨識引擎於2021年1月份最新公布於美國國家標準暨技術研究院(National Institute of Standards and Technology/ NIST)臉部辨識技術基準測試(Face Recognition Vendor Test/ FRVT)中再創佳績,於實境照比對測試項目(WILD 1E-5)中以96.98%辨識率,名列全球第6之開發團隊*,更是排除中國廠商後,於該測試項目全球排名第1。

訊連科技FaceMe®於最新NIST人臉辨識測試名列前茅 為全球排名第6及排除中國廠商之全球第1之開發廠商

「臉部辨識技術基準測試」由美國國家標準暨技術研究院所設立,為全球最具權威的臉部辨識演算法評比,其評比結果受到全世界高度矚目。實境照比對為NIST FRVT 1:1中難度最高、且最具指標意義之測試項目,係比對安控攝影機拍攝之實境照片,通常會有角度不佳、局部遮蓋、光線不佳等較難以辨識之情形,應用場景可涵蓋智慧安控、智慧警政、智慧城市、智慧交通及智慧零售等多樣化場景。

訊連科技FaceMe®在2021年1月最新公布的NIST測試報告中,於實境照比對測試項目(WILD 1E-5)中以96.98%辨識率,以開發團隊排名高居全球第6,更是排除中國廠商後,成為該測試項目全球排名第1的廠商。FaceMe®可提供沒有資安疑慮的臉部辨識技術,是各式專案及標案中採用台灣開發的臉部辨識技術首選,更可幫助IoT/AIoT廠商於面向全球市場的產品中導入無資安疑慮的刷臉技術。

「近年來,臉部辨識技術已陸續於全球各應用領域落地。在台灣市場,也可看到越來越多的智慧城市、智慧警政、智慧安控等相關應用,陸續導入臉部辨識。」訊連科技執行長黃肇雄表示:「臉部辨識除了準確度外,更是重要的資安及國安議題。對於台灣本地專案來說,FaceMe®提供了高準確度的臉部辨識,更可排除資安疑慮,是全球頂尖、台灣第一的臉部辨識解決方案。」

FaceMe®為專為邊緣運算(Edge Computing)打造的臉部辨識引擎,無論是建置在搭載高階處理器及圖像加速卡的伺服器和工作站、或是搭配輕量化處理器的IoT邊緣運算裝置,皆可針對不同的硬體配置進行優化,為系統整合商帶來快速,彈性且精準的人臉辨識解決方案,並可導入各種應用領域中,如智慧安控,訪客控管,公共安全,智慧零售和智慧家庭等。針對COVID-19疫情升溫,口罩辨識及配戴口罩的臉部辨識亦是重點指標,FaceMe®亦提供口罩偵測及配戴口罩進行人臉辨識等功能,可提供高達95%的辨識率,適合運用於醫療院所、辦公室及工廠等地,進行配戴口罩時的人流偵測及門禁管制。

更多關於FaceMe®的訊息,請至: https://tw.cyberlink.com/faceme/

*註:基於2021年1月19日公布之FRVT 1:1 結果。於測試中,單一開發團隊可提交多個臉部辨識演算法。訊連科技FaceMe®於WILD Photo 1E-5項目中,以3.02%拒認率,於所有演算法中排名第7。若以開發團隊(提交多個演算法者仍視為單一團隊) 排名,則於所有開發團隊中名列第6。

About Version 2

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products. Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

關於CyberLink
訊連科技創立於1996年,擁有頂尖視訊與音訊技術的影音軟體公司,專精於數位影音軟體及多媒體串流應用解決方案產品研發,並以「抓準技術板塊,擴大全球行銷布局」的策略,深根台灣、佈局全球,展現亮麗的成績。訊連科技以先進的技術提供完美的高解析影音播放效果、以尖端的科技提供完整的高解析度擷取、編輯、製片及燒錄功能且完整支援各種高解析度影片及音訊格式。產品包括:「威力導演」、「PowerDVD」、「威力製片」、「威力酷燒」等。

High Availability and Contingency and Risk Management in Information Security

Risk management quantifies and qualitatively describes the risk of Information Security, allowing companies to prioritize risks according to their severity and thus ensure business continuity. 

Risk management determines the value of an information asset, identifies the applicable threats and vulnerabilities that exist (or could exist), identifies the existing controls and their effects on the identified risks, determines the potential consequences, and finally prioritizes them.

After this definition, how is it possible to develop a strategy for risk management within a company? What are the main risks associated with Information Security? Also, find out what High Availability and Contingency has to do with risk management and what are their main differences in keeping your system secure.

Keep reading this article and learn how risk management in information security can contribute to your business continuity.

How does Information Security Risk Management work?

Risk management in information security is the process associated with the use of information technology. It involves identifying, assessing, and addressing risks to the confidentiality, integrity, and availability of a company’s assets.

The ultimate goal of this process is to address risks according to a company’s risk tolerance. Companies should not expect to eliminate all risks. Instead, they should seek to identify and achieve an acceptable level of risk for business continuity.

How to develop an Information Security Risk Management strategy?

Managing risks is an ongoing task, and your success will depend on how they are assessed, plans are communicated, and functions are maintained. Identifying the people, processes, and technologies required to help you deal with the steps below will develop a solid foundation for a risk management strategy and program in your company, which can be developed over time.

Identification

This stage is the process of identifying your digital assets that can include a wide variety of information: confidential company information, such as product development and trade secrets; Personal data that can expose employees to cybersecurity risks, such as identity theft regulations. Another example is those companies that handle credit card transactions and need PCI-DSS compliance.

Assessment

This is the process of combining the information you have gathered about assets, vulnerabilities, and controls to define risks. There are many structures and approaches to this.

Treatment

Once a risk has been assessed and analyzed, the company will need to select the risk treatment options. In this scenario, companies can accept the risk or prevent it.

Communication

Regardless of how risk is handled, the decision needs to be communicated within the company. Stakeholders need to understand the costs of whether or not to address risk and the reason behind such a decision. Responsibility and accountability need to be clearly defined and associated with individuals and teams in the company to ensure that the right people are engaged at the right times in the process.

Main risks associated with Information Security

Security risks are inevitable, so the ability to understand and manage risks for systems and data is essential to a company’s success. 

If you are able to address the risks below and respond effectively to security incidents, you can find out how to better resist cyber threats and reduce potential risks in the future.

Privilege Abuse

In most technology environments, the principle of least privilege is not valid. There are many reasons why privileges greater than necessary have been granted to a user.

Granting excessive permissions is problematic for two reasons: approximately 80% of attacks on corporate data are actually performed by active or dismissed employees. Privileges excessively granted or not revoked at the right time make it simple for someone to perform malicious actions.

Third-party Access

A number of third parties, including suppliers, contractors, consultants, and service providers have access to network resources, which allows them to modify, replace, or impact your company’s operational service. This access is considered privileged and needs to be even more protected than the access by an employee.

Companies apply efforts to protect their networks, but forget about third-party access security controls. These controls can protect third-party access to privileged credentials, as well as strengthen security aspects that are normally exploited by attackers to gain access to the corporate network.

Insider Threats

When it comes to data breaches, employees themselves can be one of the biggest risks to an organization. These threats can be: accidental, when personnel is only poorly trained; negligent, when employees try to bypass implemented policies; or malicious (the most dangerous), when an employee is motivated by financial gains, espionage, or revenge.

HA (High Availability) and DR (Disaster Recovery / Contingency) as metrics for Risk Management

Any good system these days must be built to expect the unexpected. No system is perfect and, at some point, something will happen that will cause a system to malfunction (a fire, a hurricane, an earthquake, human error – the list goes on). Since systems can fail in different ways, they need to be designed with the expectation that a failure will occur.

Thus, there are two related, but generally confusing, topics that work on the system architecture that mitigate failures: high availability (HA) and disaster recovery (DR).

High availability simply eliminates single points of failure, and disaster recovery is the process of putting a system back into an operational state when it goes down. In essence, disaster recovery is triggered when high availability fails.

Fundamentally, high availability and disaster recovery have the same goal: to keep systems up and running in an operational state. The main difference is that high availability is designed to deal with problems when a system is running, while disaster recovery must deal with problems after a system failure.

Regardless of a system’s high availability, any system in production, no matter how trivial, needs to have some kind of disaster recovery plan in place. And this should be included in your information security risk management strategy.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Segura®
Segura® strive to ensure the sovereignty of companies over actions and privileged information. To this end, we work against data theft through traceability of administrator actions on networks, servers, databases and a multitude of devices. In addition, we pursue compliance with auditing requirements and the most demanding standards, including PCI DSS, Sarbanes-Oxley, ISO 27001 and HIPAA.

DNSpooq bugs expose millions of devices to DNS cache poisoning

Security flaws in a widely used DNS software package could allow attackers to send users to malicious websites or to remotely hijack their devices

Millions of devices could be vulnerable to Domain Name System (DNS) cache poisoning and remote code execution attacks due to seven security flaws in dnsmasq, DNS forwarding and caching software commonly found in smartphones, desktops, servers, routers and other Internet of Things devices, according to Israel-based security company JSOF, which discovered the security holes.

Collectively dubbed DNSpooq, the vulnerabilities in the open-source utility affect a variety of devices and firmware, including those made by some of the world’s leading tech companies.

“Some of the DNSpooq vulnerabilities allow for DNS cache poisoning and one of the DNSpooq vulnerabilities could permit a potential Remote Code execution that could allow a takeover of many brands of home routers and other networking equipment, with millions of devices affected, and over a million instances directly exposed to the Internet,” warned JSOF. According to Shodan, there are almost 1.2 million dnsmasq servers exposed to the internet, with yet more vulnerable devices confined to internal networks but also at risk.

RELATED READING: DNS attacks: How they try to direct you to fake pages

Researchers identified no fewer than 40 vendors that use dnsmasq in a wide range of products and in various pieces of firmware and software. The list includes big names such as Cisco, Asus AT&T, Comcast, Siemens, Dell, Linksys, Qualcomm, Motorola, and IBM, just to mention but a few. Whether and to what extent devices are affected depends on how they use dnsmasq. 

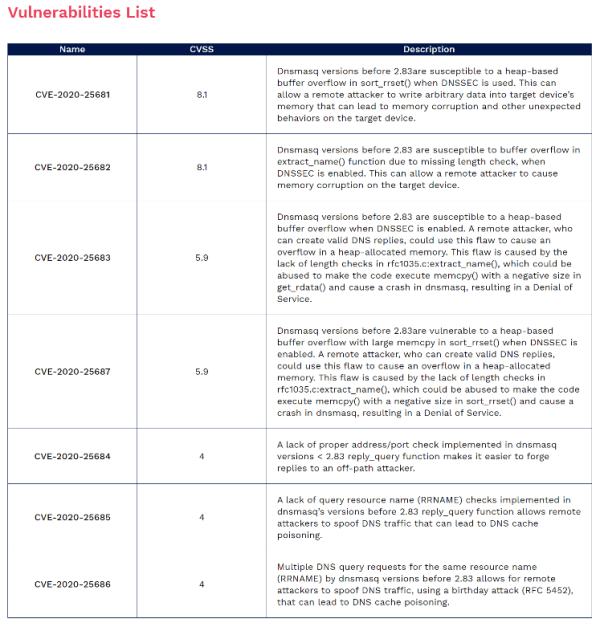
DNSpooq consists of seven vulnerabilities divided into two groups – three that could allow DNS cache poisoning attacks and four buffer overflow vulnerabilities, one of which could lead to remote code execution and device takeover.


An overview of the DNSpooq vulnerabilities (source: JSOF)

“The impact of DNS cache poisoning of the routing equipment DNS forwarding server can potentially lead to different kinds of fraud if users believe they are browsing to one website but are actually routed to another,” the researchers said. They went on to add that each device susceptible to DNS cache poisoning might also be taken over by an attacker.

While on their own the security bugs present a limited risk, once chained and combined they could also be used to conduct Distributed Denial-of-Service (DDoS) attacks as well as wormable attacks that could spread malware between devices and networks.

Researchers disclosed the vulnerabilities in August 2020 and went public with their discovery after the embargo ended this month. While highlighting a number of workarounds in its technical whitepaper to DNSpooq, JSOF advised everybody to apply the best “antidote” – update to dnsmasq version 2.83. In the meantime, multiple vendors have released their respective advisories, mitigations, workarounds and patches, which are now neatly listed on the website of the CERT Coordination Center at Carnegie Mellon University. The Cybersecurity and Infrastructure Security Agency (CISA) also had some advice to share for organizations that use vulnerable products.

In June 2020, JSOF discovered and disclosed 19 security vulnerabilities that were collectively dubbed Ripple20 and were found to affect a popular TCP/IP software library used by millions of connected devices.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Scale Computing Named a Finalist in Storage Magazine, SearchStorage 2020 Products of the Year Awards

INDIANAPOLIS – January 26, 2021 – Scale Computing, a market leader in edge computing, virtualization, and hyperconverged solutions, today announced that it has been selected as a finalist in TechTarget’s Storage Magazine and SearchStorage.com’s annual Products of the Year Awards for 2020. TechTarget named Scale Computing’s HE150, the industry’s smallest and most powerful edge computing appliance. as a finalist in the Hyper-converged & Composable Infrastructures category.

In its announcement, SearchStorage noted that: “Scale Computing’s HE150 appliance brings the HCI paradigm to incredibly low-end power-efficient devices, enabling the Scale Computing hyperconvergence offering to run on devices as small as Intel’s four-by-four inch Next Unit of Computing mini-computer. Hyperconvergence is a natural model for edge computing, and the efficiency of Scale Computing’s HE150 enables IT architects to deploy the HCI model into spaces where the vendor’s competitors simply can’t go for IoT and remote manufacturing or logistics locations.”

“Technology is everywhere, and it’s increasingly important that edge computing be able to support an application-driven world,” said Jeff Ready, CEO and co-founder of Scale Computing. “Because limited IT resources are available at the edge, supporting those apps requires a tricky combination of enterprise-grade application reliability, autonomous management, and self-healing. The award-winning Scale Computing HE150 delivers on all fronts.”

The HE150 appliance combines Scale Computing’s self-healing platform for autonomously running applications at the edge with a small, all-flash NVMe storage-based compute appliance that delivers all of the simplicity, efficiency, and enterprise-ready virtualization associated with Scale Computing’s HC3 platform.

This announcement comes on the heels of other recent industry recognition, including:

The Storage Magazine 2020 Products of the Year Awards recognizes winners in five categories: Backup and DR Hardware/Software/Services, Cloud Storage, Disk and Disk Subsystems, Hyper-converged and Composable Infrastructures, and Storage System and Application Software. All enterprise storage products were judged based on technological innovation, performance, ease of integration, ease of use and manageability, functionality and value. Winners will be announced in February on SearchStorage.com and will also be published in the February issue of Storage Magazine.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Scale Computing 
Scale Computing is a leader in edge computing, virtualization, and hyperconverged solutions. Scale Computing HC3 software eliminates the need for traditional virtualization software, disaster recovery software, servers, and shared storage, replacing these with a fully integrated, highly available system for running applications. Using patented HyperCore™ technology, the HC3 self-healing platform automatically identifies, mitigates, and corrects infrastructure problems in real-time, enabling applications to achieve maximum uptime. When ease-of-use, high availability, and TCO matter, Scale Computing HC3 is the ideal infrastructure platform. Read what our customers have to say on Gartner Peer Insights, Spiceworks, TechValidate and TrustRadius.

訊連科技U會議推出6.5版更新 支援200位與會者同時參與大型線上會議與遠距教學

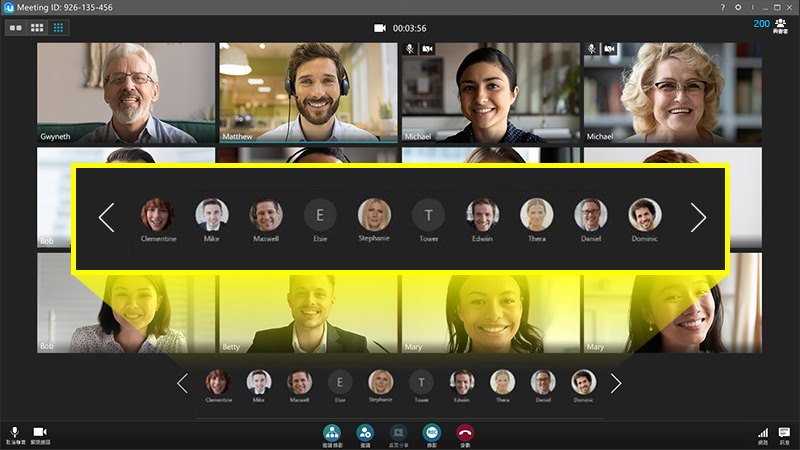
【2020年12月25日,台北訊】多媒體創作軟體及AI人工智慧領導廠商訊連科技(5203.TW)推出「U會議」之6.5版更新。即日起,U會議版用戶可透過選購方式,提升同時與會者人數至200人。企業用戶可舉辦大型線上視訊會議,教育單位則可舉辦大型的遠距教學課程。同時,U會議也強化會議管控和操作功能,提供更安全便利之溝通工具。

訊連科技U會議推出6.5版更新 支援200位與會者同時參與大型線上會議與遠距教學

新冠肺炎(COVID-19)於全球造成重大影響,台灣也於近期啟動秋冬防疫專案,其中教育學習機關及洽公機關皆屬於高感染傳播風險場域。新冠肺炎疫情爆發以來,教育機構已大量採用遠距教學方式避免群聚,而各公、民營機構除控管訪客人數外,亦大量採用視訊會議取代傳統面對面會議、實體行銷活動(如:研討會)。U會議企業版可支援高達200位與會者之線上會議,便於舉辦企業行銷活動、大型跨國會議,或是應用於學校遠距教學等需求。

「本月『U會議』視訊軟體版本更新,可支援企業版高達200位與會者參與之線上會議,提供企業大型會議或行銷活動所需,學校教育單位也可做為遠距教學之溝通工具。」訊連科技黃肇雄執行長表示:「後疫情時代來臨,訊連科技持續優化『U會議』之管理操作功能,提供企業用戶安全易用之視訊會議和線上教學解決方案。」

此外,U會議6.5版亦進一步強化管控和操作功能,會議主持人可管控會議是否開放錄影,保障會議安全。會議進行時,可使用快捷鍵操作主要功能,如開關視訊或者靜音,強化使用便利性。

用戶可於即日起至U官方網站下載最新「U會議」6.5版,或透過程式內建的升級功能取得6.5版更新,體驗最新功能。

U會議6.5版新增功能

  • 企業版支援最高200位與會者同時參與線上會議。(可透過U會議官網選購Pro 200方案,請與訊連業務專員聯繫,進行購買及功能開通)
  • 會議主持人管控是否開放會議錄影,保障會議安全。
  • 會議主要功能(如:開關視訊、靜音等)皆可使用快捷鍵操作。

U會議產品資訊
訊連科技「U會議」,即日起可於U官方網站下載,並內建繁體中文、簡體中文、英文、法文、德文、義大利文、西班牙文、日文及韓文等九國語系。
您可根據與會人數及直播時間需求,選擇不同的U會議訂閱方案。

About Version 2

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products. Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

關於CyberLink
訊連科技創立於1996年,擁有頂尖視訊與音訊技術的影音軟體公司,專精於數位影音軟體及多媒體串流應用解決方案產品研發,並以「抓準技術板塊,擴大全球行銷布局」的策略,深根台灣、佈局全球,展現亮麗的成績。訊連科技以先進的技術提供完美的高解析影音播放效果、以尖端的科技提供完整的高解析度擷取、編輯、製片及燒錄功能且完整支援各種高解析度影片及音訊格式。產品包括:「威力導演」、「PowerDVD」、「威力製片」、「威力酷燒」等。