Microsoft 365 Backup: What it means for SaaS data protection

At the Microsoft Ignite conference back in November 2023, Microsoft announced their release plans for their Microsoft 365 Backup service. Now that they’re in a paid public preview, with general availability being slated for basically now (first quarter, calendar year 2024), I thought “what better time than now?” to share my takeaways and what I believe this milestone means for SaaS data protection now and going forward. Here are three main points I’ll cover:

  • Welcome Microsoft to the backup space; 
  • What Microsoft’s backup service means for the SaaS data protection world; 
  • The Keepit promise.

Welcome to Microsoft into the backup space

First off, let’s give a warm welcome to Microsoft on their entrance to the backup space. As a long-time Microsoft community member, twenty-year Microsoft MVP, and Senior Director of Product Management at an industry-leading data protection vendor, I’d say Microsoft’s entry into the market validates what all the SaaS data protection vendors have long been saying about the strong need for Microsoft 365 data protection.

Ultimately, our mission is to protect critical SaaS data to help companies keep their business-critical data backed up, thereby ensuring continuity and compliance in face of rising ransomware threats. As long-time Microsoft partners — part of the ISV Partner Program — we at Keepit see this as an opportunity to have an even greater impact on the market. How’s that?

Well, we know that an overwhelming percentage of Microsoft’s enterprise customers have no backup. So, naturally, we want to bring that number down to boost cyber resilience of, say, critical infrastructure and critical services, and of course the market in general. So, how does Microsoft releasing their own backup help drive us forward?

Well, for one, it validates what we’ve been doing for more than 20 years. We’re built in the cloud, for the cloud, to protect cloud SaaS data. I guess a bit more practically speaking, another change is that we can now probably drop the top objection we faced from customers over that time: That cloud SaaS data doesn’t need backup.

What does Microsoft 365 Backup change? 

Now, let’s get into point two: What does Microsoft 365 Backup mean for SaaS data backup? Well, all the vendors in this space have long had to challenge the popular notion that data being in the cloud was, by default, automatically and perfectly protected. And many of us have talked at length about Microsoft’s shared responsibility model where Microsoft themselves clearly state that you, the customer, are responsible for backup of information and data, including your devices and accounts and identities.

Microsoft has built an amazing record of service quality and resilience, but their primary focus has been on protecting your data against Microsoft losing it. The Microsoft 365 Backup offering is the start of Microsoft’s journey into protecting your data against other threats, including malicious attacks, mistakes, misbehaving automations, and other misfortunes.

The optimist in me hopes that now, with Microsoft themselves developing their own backup service, we can finally put the shared responsibility model into its proper perspective. Of course you need to back up your Entra ID, M365, and other SaaS application data because clearly you are responsible for your data. Why else would Microsoft release a backup service if you weren’t responsible for it all along?

Now, aside from that original objection that perhaps can be laid to rest, at this point, not that much has actually changed with Microsoft’s announcement. That said, there sure is a newly awakened interest in data protection because of this release. This is how I see the typical train of thought playing out in response to the news:

  • We clearly need to back up our Microsoft SaaS app data. Why else would Microsoft be offering a backup service themselves?
  • Protecting our data is important because it helps us meet our business continuity and compliance requirements, but
  • To meet those requirements, we need our data available 24/7.

Let’s dive down a bit more into that last point there. How does a business guarantee access to their data no matter what happens, be it mistakes, mishap, or malice (like ransomware)? The answer is true backup.

The Keepit promise: True backup for cyber resilience 

To get to the Keepit promise, we first need to consider what the meaning of backup is. You might come across the term true backup (we use it ourselves from time to time) because ‘backup’ alone has been misused to cover things that it shouldn’t.

The canonical meaning of backup refers to storing instances of your data on an infrastructure separate from your primary data. If something should happen to your production data, your backups won’t be affected since they are separated by a physical or logical air gap.

In cloud computing, a lot of what’s being called backup is actually storing data on the same cloud as the primary data. What this means is that whatever risks you’re exposed to in your production environment would also impact your ‘backup’ data since there’s no separation. For example, an attacker who can penetrate your Entra ID tenant and can pivot into your Azure tenant holds all your Azure-based storage — including, and especially, backups — at risk.

The Keepit promise is to always offer the ultimate in data protection for multi-workload SaaS application data. By building our solution from the ground up for SaaS data protection only, we were able to create an optimized data protection solution in line with best practices like the 321 backup rule. Air gapping, immutability, and a fully redundant independent cloud are all things we’re already offering now in our service. So, it’s more the Keepit reality rather than the promise of adding in things later.

Protecting SaaS data is the Keepit mission and has always been — it’s not a feature we’re tacking on. As specialists in data protection, we provide confidence to thousands of customers that their data is here today and will be here tomorrow via our vendor-independent cloud. We look forward to working with Microsoft now and into the future to continue to lead the way in protecting SaaS data.

As we embark on this new chapter in SaaS data backup, I’d like to leave you with a question: What steps are you taking today to protect your control plane (Entra ID and Power Platform)? If you want to learn a bit more about control plane data protection, read my previous article on why you should back up Entra ID (Azure AD) in the cloud.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Keepit
At Keepit, we believe in a digital future where all software is delivered as a service. Keepit’s mission is to protect data in the cloud Keepit is a software company specializing in Cloud-to-Cloud data backup and recovery. Deriving from +20 year experience in building best-in-class data protection and hosting services, Keepit is pioneering the way to secure and protect cloud data at scale.

Keepit Partner Network: Growing partnerships to the next level

Leading the way with vendor-independent data protection

When I started in Keepit in July 2023, I knew that I was joining a very special company. Not only does the company have a great product, but it also has a great partner ecosystem and the two are key to having an impact on the market.

At the heart of data protection specialist Keepit’s success lies indeed a resilient and purpose-built cloud infrastructure — and also many long-lasting partner relationships.

The company’s platform, exclusively owned and operated independently from other cloud vendors, signifies a revolutionary shift in data protection strategies. Serving as the ultimate safeguard against potential data loss resulting from security incidents or unforeseen events, Keepit ensures that its partners empower clients to maintain control over their critical SaaS data.

And it’s not just a few workloads that we cover: Keepit’s unique easy-to-use platform ensures business-critical SaaS data from multiple SaaS applications, like Microsoft 365, Entra ID (Azure AD), Salesforce (and others) is kept immutable, accessible, and compliant with even the strictest of requirements. Learn more about Keepit’s security and compliance.

Keepit’s impressive scaling secures $40 million from HSBC Innovation Banking

On Jan. 9, 2024, Keepit announced that HSBC Innovation Banking has provided Keepit with a $40 million refinancing package together with The Export and Investment Fund of Denmark (IEFO). The fresh capital is earmarked to sustain the impressive growth trajectory and substantial expansion strategy of Keepit.

Keepit CEO and co-founder, Morten Felsvang, shares that the funding “is an infusion of confidence in our capabilities on all levels. And it means that we can continue our growth strategy at full throttle.”

Partners prove invaluable to Keepit’s growth and success

The Keepit Partner Network (KPN) highlights the company’s dedication to its channel ecosystem. Tailored for resellers, managed service providers, and distributors, this program elevates partner engagement with its tiered structure, ensuring customized support for diverse partner needs.

KPN is designed to propel partners toward unparalleled success within data protection together with Keepit. The recognition of Keepit with its addition as a scaler in the Canalys “Global Managed Backup and Disaster Recovery Leadership Matrix 2023” report underscores the program’s rapid growth and our outstanding performance. 


And in support of that commitment to growth, we’re setting our sights on crossing over into the coveted Canalys “Champions” category on our impressive journey by adopting a partner-only model. 


Keepit’s Partner Network emerges not just as a program but as a strategic cooperation for the future. Partners get the chance to be a hero for customers by offering them award-winning, next-level SaaS data protection that’s transparent in cost and incredibly easy to set up, onboard, and use. 

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Keepit
At Keepit, we believe in a digital future where all software is delivered as a service. Keepit’s mission is to protect data in the cloud Keepit is a software company specializing in Cloud-to-Cloud data backup and recovery. Deriving from +20 year experience in building best-in-class data protection and hosting services, Keepit is pioneering the way to secure and protect cloud data at scale.

NIS2 directive: A key to compliance is business continuity

As the timeline to implementation of the NIS2 directive shortens, businesses find themselves contemplating the necessary steps for implementing robust cyber security and IT compliance. The impending deadline of October 17, 2024, necessitates a strategic approach to meet the regulatory requirements outlined in NIS2. 

This article provides actionable insights into how organizations can proactively prepare for NIS2 compliance, with a particular focus on backup management and disaster recovery as integral components for ensuring business continuity — a key focus of the new directive, specifically article 21.

Let’s jump into the essential steps businesses can take now to fortify their defenses against cyber threats by following a best practice framework.

If you’re looking for a general overview of all things NIS2, such as who does NIS2 apply to, read our blog, “What is the NIS2 Directive?”

What to do now: Get your business ready with best practices

Article 21 of the NIS2 directive sets out clear cybersecurity risk-management measures “to protect network and information systems” that focus on ensuring business continuity through “backup management and disaster recovery.”


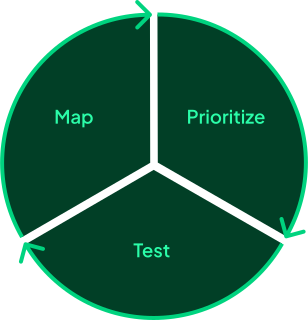
At the minimum, the best practice would be to back up vital data, create a strong disaster recovery plan, and then test these processes to know that they work as expected (meaning you have protected your business-critical data and it can be recovered). Luckily, to help elaborate on this practice, there’s a framework to follow to help guide you through the process: Map, prioritize, test.

Map-prioritize-test framework for NIS2 directive compliance backup and disaster recovery

Map-Prioritize-Test framework to ensure compliance

This framework is helpful for businesses to prepare for compliance with the expected NIS2 requirements by boosting cyber resiliency, most notably by maintaining business-critical functions through protecting key business infrastructure. Here’s more detail about what each leg of the framework entails:

1. Map critical systems

Assess and analyze critical infrastructure across on-premises, native cloud, and public cloud environments. Identify and prioritize crucial data, ensuring business continuity. Don’t overlook SaaS applications like Entra ID; safeguarding identity and credential data is vital.


Neglecting identity and access data can impact business continuity even if other data is fully restored. Microsoft recognizes identity systems as more critical than human life support systems due to how important this data is for businesses: Read what Microsoft has to say about the importance of backing up Entra ID (formerly Azure AD).

2. Prioritize: What is critical to maintain access to?

Understanding the nature of your data is key to strengthening your organization’s data resilience. As you consider the types of data you handle, such as SaaS data from Microsoft 365 (M365) or Entra ID, it becomes evident that not all data holds equal importance. This realization forms the basis for strategic prioritization, a critical step in preparing for NIS2 compliance.


Whether safeguarding CEO emails, logistics data, customer information, intelligence dashboards, or proprietary code, identifying the priority for recovery establishes a strategic foundation. This speeds up recovery time and minimizes downtime, ensuring that your business continuity efforts are precisely aligned with the specific datasets crucial for sustaining your operations.
By determining what needs to be recovered first, you ensure that your business continuity efforts are targeted and aligned with the specific data sets crucial for sustaining your operations. This strategic prioritization not only optimizes your backup plan but also enhances your preparedness for compliance with the NIS2 directive.

3. Test that your backup works

This critical phase of the framework involves validating the effectiveness of your backup and disaster recovery processes. Testing is a key element of continuity, because with regular testing, your business ensures that data recovery is possible in the event of a real crisis — this is best practice data security and compliance in line with the NIS2 framework.


Ensuring the effectiveness of your backup and disaster recovery processes is crucial for maintaining data integrity and business continuity. The following guidelines outline key steps in the testing phase, aimed at validating your organization’s readiness to swiftly recover critical data in diverse scenarios.


From prompt validation of restoration capability to involving relevant stakeholders, this comprehensive testing phase guideline ensures confidence in your disaster recovery plan and ongoing resilience against potential threats:

  • Validate restoration capability promptly:
    Promptly validate that your backup systems can efficiently restore critical data without compromising integrity.
  • Determine acceptable downtime:
    Establish the maximum allowable time for data recovery, aligning with recovery time objectives set during prioritization.
  • Regularly test backups for confidence:
    Frequently test your backups to instill confidence in your disaster recovery plan and promptly address any identified issues.
  • Consider different scenarios:
    Simulate diverse scenarios, testing the recovery of individual files, entire databases, and complete systems to identify weaknesses.
  • Document and analyze results:
    After each testing session, document and analyze the time, accuracy, and challenges encountered to gain insights for improvement.
  • Involve relevant stakeholders:
    Collaborate with IT teams, data custodians, and business continuity managers to ensure comprehensive testing aligns with broader goals.
  • Update and improve:
    Continuously update recovery plans based on testing insights, addressing weaknesses, refining procedures, and adapting to evolving threats.

As organizations diligently adhere to the rigorous testing guidelines outlined above, they pave the way for a robust IT compliance policy essential for NIS2 readiness. The elements of backup management and disaster recovery, as emphasized by Article 21 of NIS2, not only acknowledge its far-reaching impact but also serve as proactive measures against evolving cyber threats.

Keepit as an established expert in EU compliance

Keepit, being a European company based in Denmark, understands the intricacies of EU regulations and their profound impact as we’re also subject to them ourselves. We operate without any sub-processors and maintain our own independent cloud operations within the EU, utilizing data centers in Denmark, Germany, and the UK. With a commitment to excellence in compliance, Keepit holds end-to-end ISO 27001 certification and is audited in accordance with ISAE 3402 type 2.


To guide your company through the complexities of legislative directives such as NIS2, NIS, and GDPR, we invite you to explore a demonstration of how Keepit can assist in ensuring comprehensive compliance.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Keepit
At Keepit, we believe in a digital future where all software is delivered as a service. Keepit’s mission is to protect data in the cloud Keepit is a software company specializing in Cloud-to-Cloud data backup and recovery. Deriving from +20 year experience in building best-in-class data protection and hosting services, Keepit is pioneering the way to secure and protect cloud data at scale.

Keepit Partner Network: Growing partnerships to the next level

Leading the way with vendor-independent data protection

When I started in Keepit in July 2023, I knew that I was joining a very special company. Not only does the company have a great product, but it also has a great partner ecosystem and the two are key to having an impact on the market.

At the heart of data protection specialist Keepit’s success lies indeed a resilient and purpose-built cloud infrastructure — and also many long-lasting partner relationships.

The company’s platform, exclusively owned and operated independently from other cloud vendors, signifies a revolutionary shift in data protection strategies. Serving as the ultimate safeguard against potential data loss resulting from security incidents or unforeseen events, Keepit ensures that its partners empower clients to maintain control over their critical SaaS data.

And it’s not just a few workloads that we cover: Keepit’s unique easy-to-use platform ensures business-critical SaaS data from multiple SaaS applications, like Microsoft 365, Entra ID (Azure AD), Salesforce (and others) is kept immutable, accessible, and compliant with even the strictest of requirements. Learn more about Keepit’s security and compliance.

Keepit’s impressive scaling secures $40 million from HSBC Innovation Banking

On Jan. 9, 2024, Keepit announced that HSBC Innovation Banking has provided Keepit with a $40 million refinancing package together with The Export and Investment Fund of Denmark (IEFO). The fresh capital is earmarked to sustain the impressive growth trajectory and substantial expansion strategy of Keepit.

Keepit CEO and co-founder, Morten Felsvang, shares that the funding “is an infusion of confidence in our capabilities on all levels. And it means that we can continue our growth strategy at full throttle.”

Partners prove invaluable to Keepit’s growth and success

The Keepit Partner Network (KPN) highlights the company’s dedication to its channel ecosystem. Tailored for resellers, managed service providers, and distributors, this program elevates partner engagement with its tiered structure, ensuring customized support for diverse partner needs.

KPN is designed to propel partners toward unparalleled success within data protection together with Keepit. The recognition of Keepit with its addition as a scaler in the Canalys “Global Managed Backup and Disaster Recovery Leadership Matrix 2023” report underscores the program’s rapid growth and our outstanding performance. 


And in support of that commitment to growth, we’re setting our sights on crossing over into the coveted Canalys “Champions” category on our impressive journey by adopting a partner-only model. 


Keepit’s Partner Network emerges not just as a program but as a strategic cooperation for the future. Partners get the chance to be a hero for customers by offering them award-winning, next-level SaaS data protection that’s transparent in cost and incredibly easy to set up, onboard, and use. 

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Keepit
At Keepit, we believe in a digital future where all software is delivered as a service. Keepit’s mission is to protect data in the cloud Keepit is a software company specializing in Cloud-to-Cloud data backup and recovery. Deriving from +20 year experience in building best-in-class data protection and hosting services, Keepit is pioneering the way to secure and protect cloud data at scale.

Ransomware resilience: Why air gapping is your best defense

First, why is ransomware protection such a critical need?

Put simply, ransomware protection is critical because:

  • Your data is vital to your business,
  • Maintaining control of and access to your data is legally mandated to be compliant with directives such as NIS2, GDPR, and others,
  • Ransomware attacks are prevalent, so much so that it’s really become a matter of when you’ll experience an attack rather than if you will.

From a risk assessment standpoint, looking at the importance of data as well as the chance of experiencing ransomware, it’s quite clear that it’s a high-risk scenario. Not only is ransomware (and subsequent data loss) very likely to happen, it’s also very likely to have very serious impacts to your business.

Considering the current levels of cyber resilience against ransomware and the many data protection gaps to be filled — especially in small- to mid-sized companies — ransomware protection should be top of the list.

According to a 2023 ransomware preparedness Enterprise Strategy Group (ESG) report, Lighting the Way to Readiness and Mitigation, only 16% of organizations struck by a ransomware attack were able to recover 100% of their data.

ESG also finds that data recovery post ransomware was lacking, saying, “Unfortunately, the current reality is bleak as only one in seven report they were able to fully restore their data after a successful ransomware attack. This highlights the need to reengineer recovery processes for ransomware attacks.”

This missing coverage found in most of the companies surveyed means recovery to a production-like state is impossible with their current data protection setup. Considering that data is the lifeblood of our digital economy, it’s fundamental to protect this data for business to carry on as usual.

When ransomware strikes and is effective, the main goal is to recover data and minimize losses. This is because data losses not only lead to non-compliance but also pose a risk of losing crucial business transactions.

2023 Ransomware Preparedness: Lighting the Way to Readiness and Mitigation

Access the full report

So, when disaster strikes, what’s the most effective way to protect your data so you can minimize losses and expedite the data recovery process? Air gapping.

What is air gapping and why is it the ultimate in data protection?

Air gapping is a security measure that physically or electronically isolates a computer, network, or backup storage system from external, untrusted networks. The term “air gap” signifies a complete separation between the secured environment and the outside world, making it virtually impossible for digital threats, like malware and ransomware, to infiltrate the protected system.

For backup, this air gap is the vital step of keeping data copies on a logically separate infrastructure from the primary dataset, which is more commonly known as a logical air gap, and from where we derive the definition of true backup. Learn more about true backup.

The significance of air gapping in data protection lies in its unmatched level of security:

  • Absolute protection: Air gapped systems are impervious to online threats, offering the highest level of data protection. Even the most sophisticated ransomware attacks cannot compromise a system that has been effectively air gapped.
  • Preservation of data integrity: It ensures data integrity, as data stored within the air-gapped environment remains unaltered and uncorrupted.

So, how do we understand air gapping most simply? According to Wikipedia, “It means a computer or network has no network interface controllers connected to other networks, with a physical or conceptual air gap, analogous to the air gap used in plumbing to maintain water quality.”

Just like how water from your sink can’t flow back into your faucet to contaminate your clean water, air-gapped networks don’t let malware, ransomware, or otherwise corrupted data flow into your backup data: It’s simply not possible.

Physical air gap for SaaS data

In the faucet example, there’s clearly a physical separation that preserves the health of your water since your tap isn’t submerged in your sink. And while you can have an equivalent physical separation of backup data, this approach is resource demanding, expensive to maintain, and typically not agile enough to meet today’s demands for IT efficiency and speed. Why is that?

In order to keep backups offline, disconnected from any networks, you’d need to transfer data manually every single time you wanted a snapshot. This is costly hardware-wise and resource-wise, especially if you need to keep up-to-date backups — which you probably do for many reasons, not least of all compliance.

As businesses utilize more and more SaaS applications (organizations use an average of 371 SaaS apps), the costs and complexity to protect all of the SaaS data generated grows, too. For the absolute most business-critical data, a physical air gap may be worth the high cost to maintain, but surely not for tens or hundreds of SaaS apps. Imagine if you had to manually move data to a physical air gap twice a day for every single application to have updated backup copies from all your applications.

So, the question is how can you get top-tier data protection in the cloud that’s as secure as a physical air gap but much more agile and cost efficient? Well, we mentioned it above, and that’s the logical air gap.

Understanding the logical air gap: Efficiently countering ransomware threats

At its core, the logical air gap involves the use of advanced digital measures to segregate and protect network-connected digital assets. Through a combination of encryption, hashing algorithms, and role-based access controls, it creates a secure barrier around sensitive data, much like a physical gap.

But unlike its physical counterpart, the logical air gap doesn’t rely on physical isolation, it leverages intricate digital processes to render data incomprehensible and virtually impervious to unauthorized access, theft, or modification. The result is data that’s kept just as securely but with the significant added benefits of agility and efficiency because it’s kept online in a logically separate cloud infrastructure.

It’s really the best of both worlds: Top-tier security paired with modern accessibility, efficiency, and speed.

What are some key features employed in air gapping?

 Encryption as a shield:

The heart of the logical air gap’s defense lies in encryption. By converting data into an unreadable format that requires a decryption key for access, even if ransomware manages to infiltrate the system, it’s met with a cryptographic barrier. This renders the encrypted data useless to unauthorized parties, thwarting the primary objective of ransomware attacks.

Hashing for data integrity:

Hashing functions add an extra layer of protection by generating unique identifiers (hashes) for each piece of data. Any alteration to the data results in a change in the hash, which allows for the verification of data integrity based on these changes. This then provides safeguarding against ransomware silently manipulating files without detection.

Detection is an important part of being ransomware resilient, and so you or your data protection vendor needs to have this ability. Read about Keepit’s data monitoring dashboard.

Role-Based Access Controls:

Through meticulous access management, the logical air gap ensures that only authorized personnel have the requisite permissions to interact with sensitive data. This minimizes the attack surface for ransomware, limiting its ability to propagate and encrypt critical information.

Highlighting the lack of air-gapping adoption:

Surprisingly, despite its effectiveness, air gapping is not as widely adopted as it ought to be given its effectiveness in protecting data. In the 2023 Ransomware Preparedness report by ESG, it can be seen that “slightly more than one in four (27%) organizations have deployed it at this point.”

Altogether, a staggering 67% of organizations do not currently implement air gapping as part of their data protection strategy. This leaves them potentially vulnerable to ransomware attacks and other cybersecurity threats as air gapping is a crucial data protection best practice. Not ignoring the importance of air gapping, more than one third of those surveyed were interested in investing in an air-gapped solution.

For those organizations utilizing air-gapping methodologies, here’s how they’re doing it, according to ESG:

And in the event of data loss due to a successful attack, here’s how companies plan to recover:

Looking at the data above, it’s a logical step to consider what you and your company would do if faced with recovering from a successful ransomware attack. How do you plan to recover data? How confident are you that your mission-critical data is well protected and can’t be corrupted by ransomware?

If you’re looking for inspiration on how to answer those questions, there’s a long-accepted data protection best practice we can turn to. Originating in the on-premises days (but is still very much relevant for cloud data protection) is a backup principle that puts air gapping at the forefront. Let’s look into it.

The 3-2-1 backup principle: A resilient strategy for data protection

The 3-2-1 backup principle stands as a cornerstone in data protection, offering a robust strategy for safeguarding critical data against many threats, including ransomware. This “321 rule” outlines a simple yet highly effective approach to data backup and recovery.

3 copies: The first part of the principle emphasizes the importance of keeping three copies of your data. This includes your primary data and two backup copies. This redundancy is crucial because it ensures that multiple copies of your data are available for recovery in case of data loss or corruption.

2 locations: The second part of the principle recommends that you store two of the backup copies on different devices within your local environment. This diversification, also called redundancy, protects against hardware failures, localized incidents, and even some software issues. The use of different devices/locations adds a layer of security and redundancy.

1 copy air gapped: The final part of the principle advocates for keeping one of the backup copies offsite or in a separate location. What’s that in cloud language though? That means your backup data resides outside of the administrative domain of your production data, such as a vendor-independent cloud, rather than within the same cloud. This would be the logically separate infrastructure.

However, most cloud backup solutions store your backed-up data on the same public cloud infrastructure that also hosts your production data, which potentially exposes your company to several risks. It’s akin to storing your spare car keys inside the car in case you lock yourself out.


It’s vital to find a backup solution that stores backed-up data on an independent cloud since the ‘one’ is your ultimate safety net. It ensures that in the event of a catastrophic failure, natural disaster, or even a ransomware attack that compromises your local environment, you have a separate and secure copy of your data to rely on for recovery. For an in-depth look, read our post about the 3-2-1 backup rule.

Embracing the logical air gap not only fortifies digital assets against ransomware but also positions organizations at the forefront of proactive cybersecurity measures.

Where we go from here


While air gapping presents the best defense against ransomware, its effectiveness is contingent on strategic implementation. Regularly updating encryption protocols, monitoring access logs, and conducting thorough security audits are integral components of maintaining the integrity of this defense mechanism.

If you’re interested in taking the next step toward protecting your SaaS data, get a demo on how Keepit can play a vital role in creating a robust, cyber resilience data protection system.

Learn more about air gapping and other protective measures you can employ to mitigate your ransomware risk with our on-demand webinar co-hosted with Enterprise Strategy Group.

Watch our webinar

This post is part two of a five-part series on ransomware resilience and the role backups play in the protection against ransomware — read part one: Why backups are key ransomware targets. Check back soon to catch the third installment, which will cover the importance of immutability in SaaS data protection.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Keepit
At Keepit, we believe in a digital future where all software is delivered as a service. Keepit’s mission is to protect data in the cloud Keepit is a software company specializing in Cloud-to-Cloud data backup and recovery. Deriving from +20 year experience in building best-in-class data protection and hosting services, Keepit is pioneering the way to secure and protect cloud data at scale.