Skip to content

A Summary of Adversarial Threat Reports – 2022

Sharing authentic information is critical in today’s world of the internet. It becomes more significant if the information shared benefits everyone, including the individual who uses the internet for leisure or the organization dependent on the internet for their operations. The Adversarial Threat Reports are vital bits of information that keep the community aware of the significant cyber threats that appear from time to time. Generally, security agencies and digital establishments issue adversarial threat reports quarterly, highlighting the significant challenges that emerge during the specific quarter. This article summarizes the findings of various such threat reports published in 2022. 

What Are Adversarial Threats?

Adversarial threats generally denote enterprise disruptions or losses caused by the deliberate actions of malicious third parties interacting with their information systems. Any threat associated with accidental human error or environmental or structural failure is not considered an adversarial threat. The deliberate and malicious intention is critical for the threat to qualify as one.

Examples of Adversarial Threats

Adversarial threats are of various types and characteristic features. Ransomware, phishing, and cyber espionage attacks are a few of them. For example, Ukraine’s invasion by Russia has greatly impacted the phishing threat landscape. Since its initiation,  phishing has seen a 10-percentage point increase over the previous year. The increase in the number and types of phishing attacks has been seen as a common concern across security service providers.

(Source: Cofense 2022 Annual State of Phishing Report)

Sophos 2022 Adversarial Threat Report states that ransomware constituted 79% of cyber threats, followed by Cobalt Strike at 6% and Web shells at 4%. Other hazards include data exfiltration and miscellaneous malware. Even the Global Threat Report 2022 by Crowdstrike indicates that ransomware is an ever-increasing threat today, growing 82% between 2020 and 2021.

What Do the Adversarial Threat Reports Signify?

The significance of adversarial threat reports is that they highlight the latest threats the internet communities face from various malicious sources. For instance, the Meta Adversarial Threat Report Q1-2022 focuses on state actors, especially in the backdrop of the Russian Ukrainian War. Thus, it discusses cyber warfare, an ominous large-scale threat in today’s circumstances.

The Meta Adversarial Threat Report aims to highlight coordinated inauthentic behavior (CIB), cyber espionage efforts by Iran, and malicious mass reporting attempts from Russia. Besides reporting inauthentic behavior, such reports also examine the efforts put in by the security community to counter these activities.

The Purpose Behind the Adversarial Threat Reports

The primary reason behind the compilation of these adversarial threat reports is to share information on malicious threats capable of causing significant global damage to enterprise network systems. A glance through these reports can help educate  security teams concerning the latest threats in the internet environment, even if all of them might not pose immediate cybersecurity risks. 

Below are the findings of the Meta Adversarial Threat Report for the first quarter of 2022.

  • Cyber Espionage Operations Linked to Iran

Cyber espionage targets people to gather intelligence, manipulate them into sharing critical information, and compromise their devices and accounts. The Meta Adversarial Threat Report Q1 2022 highlights three groups of malicious actors engaging in cyber espionage. 

  1. A group of Iranian adversaries, also known as UNC788, targeted people from the Middle East, including the Saudi military, dissident groups from Iran and Israel, and US politicians and journalists. The malicious actors used phishing to steal users’ credentials and share links to malicious websites that hosted malware. The modus operandi included social engineering tactics, phishing, and malware injection.
  2. Similarly, an unreported group of threat actors from Iran used spoofing to target various organizations in multiple industrial sectors. They include energy establishments in Russia, Italy, Canada, and Saudi Arabia and targets in the IT industry in UAE and India. Other industrial sectors include the maritime logistics industry in the US, Israel, UAE, Norway, Iceland, etc., the telecommunication industry in the UAE and Saudi Arabia, and the semiconductor industrial sector in the US, Germany, and Israel. The methods of attack include using social engineering and interactive targeting, spoofing of corporate websites, and injecting malware.
  3. It also identified another malicious group from Azerbaijan engaging in CIB and cyber espionage targeting Azerbaijani democracy activists, opposition party leaders, journalists, and government critics. Though the group maintained a low profile and focused on news and social media websites like Twitter, Facebook, and LinkedIn, there were resemblances to a prominent threat actor named ‘Ghostwriter’ that targeted Ukraine. The modus operandi was compromising and spoofing websites, injecting malware, credential phishing, and CIB.  
  • Security Updates on Ukraine

The risk of the ongoing hostilities between Russia and Ukraine escalating into a full-fledged cyber war is omnipresent. Under such circumstances, almost every adversarial threat report includes security updates on Ukraine. The Meta Adversarial Threat Report identifies government-linked Russian and Belarusian actors engaging in online cyber espionage and covert influence operations. For instance, it detected CIB activity linked to the Belarusian KGB spreading misinformation about Ukrainian troops’ withdrawal even before Russia commenced war activities.

This report refers to a spike in Ghostwriter’s attempts to target people through email compromise and use the information to access their social media accounts. The group also attempted to attack the Facebook accounts of various Ukrainian military personnel by posting videos of people calling on the Army to surrender. Meta detected and took down various networks belonging to politically aligned actors for violating its policy on inauthentic behavior by mass reporting their political opponents and spreading hate speech.

As a way to protect users, Meta also suggested Ukrainians and Russians strengthen the security of their online accounts, emails, and social media. The company suggested downloading a VPN (Virtual Private Network) app, enabling MFA (Multi-factor authentication), and avoiding reusing passwords along with practicing other online safety tactics.

  • Continuous CIB Enforcement

CIB includes opening fake social media accounts and coordinating with others to mislead users and manipulate public debate for a strategic goal. Meta Adversarial Threat Report identifies many such people globally, which the company has removed from the network. In addition, Meta monitors these removed accounts to ensure they do not resurface under different aliases. 

The Meta Adversarial Threat Report has identified and removed 14 Facebook accounts, nine web pages, and 39 Instagram accounts in Brazil for violating Meta’s CIB policy. While the malicious actors started misleading people on Covid-19 in 2020, they later shifted their attention toward Amazon deforestation issues in 2021.

Similarly, Meta has removed 233 Facebook accounts, 84 pages, and 27 Instagram profiles in Costa Rica and El Salvador for using fake accounts to post misinformation on both sides of the political spectrum. The report also mentions fake Russian and Ukrainian social media accounts that spread misinformation about the war. Meta has successfully identified and removed 27 of these Facebook accounts and 4 of these Instagram accounts, respectively.  

  • Mass Reporting Network in Russia

Meta successfully identified nearly 200 social media accounts that spread fake information using mass reporting techniques. Besides focusing on Ukrainian and Russian nations, these accounts had users from the US, Poland, and Israel. The modus operandi was spreading fake information regarding the war and making people believe in false reports, thereby misleading them with the intent of causing widespread distrust in the government and local news.

  • Removing Coordinated Violating Networks in the Philippines

Similarly, Meta has discovered a network of nearly 400 accounts and groups in the Philippines involved in DDoS attacks and compromising websites in the country. This network prided itself on bringing down news websites. Besides, it offered cybersecurity services to protect networks from such attacks they initiated. Eventually, they started inviting new members openly to carry out DDoS attacks. 

What Constitutes Inauthentic Behavior?

Inauthentic behavior is usually centered on amplifying and increasing false content distribution to manipulate public debate in order to achieve a strategic goal. The primary objective is to mislead people. If such behavior is financially motivated, it can qualify as spam and scam activity.

IB operators focus on quantity rather than quality. They need large numbers of fake accounts to post their content in order to reach the largest audience possible. Generally, you can also find these accounts monetizing people’s attention by driving them to off-platform websites filled with ads.

The Deceptive Strategies Used by IB Operators

Here are some deceptive strategies IB operators use to boost their engagement artificially.

  • Context Switching

Generally, IB operators mislead their audience by claiming to be dedicated to a specific subject but switching to an unrelated one when the account or post goes viral. They perceive the pulse of their audience and use tactics like sensationalism to deceive people into clicking links to their websites.

  • Posing as Authentic Communities

IB operators trick their audience by making them believe they are operating from a specific country or community when they are actually a different one. This tactic proves helpful to indulge in context switching by posting content related to political crises or natural calamities to attract audiences and monetize their attention. 

  • Mass Posting, Sharing, and Liking of Content to Popularize it

Usually, IB operators use fake social media accounts to mass-post content. This way, their entire chain can start liking or sharing the content amongst their contacts to increase apparent popularity. There is not much actual engagement because there is no interaction with people outside their bubble that is composed of just their members.

While CIB is the trending threat today, especially in the backdrop of the Russian-Ukrainian war, one cannot ignore other adversarial threats. The Blackberry 2022 Threat Report lists various hazards that can affect the daily functioning of businesses globally, as listed below.

  • Ransomware was the most dangerous of all adversarial threats in 2021. Trends indicate that ransomware will also continue to top the charts this year. The year 2021 saw massive ransomware attacks. Two examples are DarkSide crippling the Colonial Pipeline Network and the Russian ransomware threat group REvil attacking Acer and JBS Foods. Another significant attack included the infiltration of the insurer AXA by the Avaddon ransomware group. In a recent 2022 survey by ransomware.org, 80% of the survey respondents accepted that their organization is more likely to be a target of a ransomware attack in 2022 as compared to 2021.

(Source: ransomware.org)

  • A zero-day vulnerability is also a potent adversarial threat, especially with the HAFNIUM group exploiting the Microsoft Exchange Server’s zero-day vulnerability. It allowed other threat actors to reverse engineer the patch and target organizations worldwide. Organizations and individuals can protect against zero-day vulnerabilities by keeping their network systems updated and looking for alternative security approaches like the Zero Trust framework and XDR (Extended Detection and Response) solutions.
  • Supply chain attacks were the flavor of threat actors in 2020, especially with SolarWinds Attack making international headlines. Additionally, 2021 saw the supply chain attacks re-emerging with the compromising of Kaseya’s VSA software affecting over 1,000 businesses. As supply chain attacks betray the trust between service providers and customers, there is a pressing need for companies to adopt a Zero Trust framework. 

Threat actors were rampant in 2021, with many adept at mimicking private sector capabilities by leveraging services like IaaS (Infrastructure-as-a-Service), RaaS (Ransomware-as-a-Service), and MaaS (Metal-as-a-Service, for the deployment of large cloud and Big Data environments) to launch their malicious attacks. 

Final Words

Cyber threats and malicious actors will play around as long as the internet survives. Since one cannot eliminate all threats at all levels, it is a matter of co-existence with the utmost awareness and security. Adversarial threat reports make people aware of the latest threats looming over the horizon and waiting to attack unsuspecting network systems globally. 

Though phishing is considered the earliest of all cyber threats, it is significant even today because almost all the other threats rely on phishing (or its variants) in order to gain global access to network systems. Therefore, while anti-malware solutions are necessary to neutralize threats, cybersecurity awareness is critical in fighting the fundamental stages to avoid bigger contingencies. Documents like adversarial threat reports are handy for the purpose.

Every cybersecurity professional should go through these threat reports and acquire reliable knowledge of the current threat landscape and the modus operandi malicious actors use to carry out the threats. In essence, adversarial threat reports are critical for every industry.

References

  1. Meta. (2022, April). Adversarial Threat Report. Meta. https://about.fb.com/wp-content/uploads/2022/04/Meta-Quarterly-Adversarial-Threat-Report_Q1-2022.pdf
  2. Crowdstrike. 2022 Global Threat Report. https://go.crowdstrike.com/global-threat-report-2022.html
  3. Blackberry. BlackBerry 2022 threat report. 

https://www.blackberry.com/us/en/forms/enterprise/report-bb-2022-threat-report-aem?

  1. Borges, R. Scribd. Meta Quarterly Adversarial Threat Report Q1 2022. 

https://www.scribd.com/document/568491724/Meta-Quarterly-Adversarial-Threat-Report-Q1-2022

  1. Sophos. Sophos 2022 Threat Report: Interrelated threats target an interdependent world.

https://assets.sophos.com/X24WTUEQ/at/b739xqx5jg5w9w7p2bpzxg/sophos-2022-threat-report.pdf

  1. NCC. (2022, June 27). Threat Report 10th June 2022. 

https://www.ncsc.gov.uk/pdfs/report/threat-report-10th-june-2022.pdf

  1. Shier, J. (2022, June 7). The Active Adversary Playbook 2022. Sophos News. https://news.sophos.com/en-us/2022/06/07/active-adversary-playbook-2022/
  2. National Cyber Security Centre. (2022, June 10). Threat Report 10th June 2022. https://www.ncsc.gov.uk/report/threat-report-10th-june-2022
  3. Trellix. Trellix Advanced Threat Research Report: January 2022. 

https://www.trellix.com/en-us/threat-center/threat-reports/jan-2022.html

  1. Cofense. (2022, April 12). Cofense 2022 annual state of phishing report highlights. Cofense. https://cofense.com/blog/three-highlights-from-cofense-2022-annual-state-of-phishing-report

#threatreport #cybersecurity #Russia #ransomware #phishing #espionage #Meta #Ukraine #vicarius_blog

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About VRX
VRX is a consolidated vulnerability management platform that protects assets in real time. Its rich, integrated features efficiently pinpoint and remediate the largest risks to your cyber infrastructure. Resolve the most pressing threats with efficient automation features and precise contextual analysis.

Certificate Management – Stop Worrying About It

The process of digital transformation with the introduction of technologies such as 5G, DevOps and Internet of Things has caused an explosion of connected devices in organizations. According to Cisco, there were more than 20 billion connected devices in 2021, and the expectation is that this number will reach 29 billion by 2023. The management of these devices is carried out through machine identities, such as digital certificates. In fact, in 2021, Gartner named Machine Identity Management as one of the 8 Security and Risk trends to consider. That’s because digital certificates can be compromised through cyber attacks, compromised CAs, or through negligence by employees or third parties.

In this way, ensuring the protection of machine identities should be one of the priorities in organizations’ cybersecurity programs. However, with the explosion in the amount of digital certificates in the infrastructure, their management has become more complex. The lack of proper management of digital certificates prevents administrators from having visibility of the certificates installed in the environment. This fact can lead to downtime due to expiration of digital certificates, which can not only cause loss of revenue, but also affect the trust of partners, customers and employees.

One of the best practices for the proper management of digital certificates is to first implement certificate discovery mechanisms. That’s because it’s impossible to protect what is not managed, and it’s impossible to manage what is not known. In addition, security leaders must periodically rotate digital certificates across the infrastructure to prevent their use by malicious users. It is also a good practice to implement mechanisms to identify and alert the expiration dates of digital certificates. In this way, the Security team is able to renew them and thus avoid downtime caused by certificate expiration.

To address all these aspects related to certificates, it is recommended to implement specific solutions for managing digital certificates. Gartner estimates that by 2022, organizations that implement this type of solution will experience 90% fewer certificate-related issues.

Thus, the implementation of a specific solution allows the discovery, centralized management and renewal of certificates in the infrastructure. In addition, the solution allows automating their entire life cycle, from generation to expiration control. Dashboards and reports also allow real-time alerts on the state of digital certificates in the environment.

Do you want to know more about how a Digital Certificate Management solution works and how it can help your company in operational improvement in the management of digital certificates?

On July 26th at 2:00 PM CET (July 28th 1 to 12:00 PM ET and 11:00 AM HKT) we will be hosting a webinar on the topic Certificate Management – Stop Worrying about it. Sign up now through this link.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Segura®
Segura® strive to ensure the sovereignty of companies over actions and privileged information. To this end, we work against data theft through traceability of administrator actions on networks, servers, databases and a multitude of devices. In addition, we pursue compliance with auditing requirements and the most demanding standards, including PCI DSS, Sarbanes-Oxley, ISO 27001 and HIPAA.

Shifting From a Severity-Focused to Risk-Based Network Security Model

Organizations handle cybersecurity issues from varying perspectives. It is the precise reason they apply different strategies for fulfilling security objectives. The goal notwithstanding, one essential element to consider is combating the compounding surge in vulnerabilities. While fixing all may look like a ‘wild goose chase,’ adopting a sustainable approach is the way to go.

At the moment, top managers of companies are more focused on cyber risk than severity levels for security issues. However, the topic encapsulates all potential business losses – financial, operational, reputation, regulatory, and more. Therefore, it becomes necessary to stress that cyber risks are business risks…hence the shift to risk-based security models.

Analyzing Vulnerabilities, Threats, & Risks

In today’s world, data and its protection involve three critical factors for any business. Customers need security guarantees for their personal information. Every organization needs to focus on the issues bordering on cyber security threats, vulnerabilities, and risks. Therefore, it becomes expedient to understand how the three components intertwine fully. The information helps to give a firm grasp on data security issues, along with a focus on the appropriate area for full-service delivery.

  • Threat: Focuses on a new incident with the potential to harm a system or the entire organization. It could take any of these three forms; natural, intentional, or unintentional. Cybercriminals constantly devise new and creative ways to compromise data. When organizations take measures to assess threats regularly, they become well prepared for them.
  • Vulnerability: Refers to a known weakness of a resource prone to exploitation by cybercriminals. An understanding of this crucial aspect is the first step to managing risks. You can begin with vulnerability testing. It is a great way to ensure the constant security of a company’s system. When the weak point gets identified, developing a strategy becomes easy.
  • Risk: Refers to losing the integrity, availability, or confidentiality of data or information systems when a vulnerability is exploited. It often results in an adverse impact on the operations and assets of an organization.

Cybersecurity risks come in various forms and can evolve at an alarming pace. It is the reason why risk management has become a never-ending responsibility. The goal is to prevent financial or reputational damage in a data breach or cyber-attack.

Risk-Based Security: A Safety & Soundness Process

Data is always the primary target for most cyber actors, and it’s an arduous task to defend against every threat. Over the years, organizations focused their resources and budget on security technologies like anti-virus, firewalls, SIEMs, and more. They have become more concerned with detecting and preventing security incidents.

Subsequently, the level of complexity and the increased threat of mobile and IoT devices have made this focus obsolete. The current level of risk is too high, and it is vital for top management to focus on risk reduction through data analysis and rapid incident response.

A risk-based security approach covers five key elements:

I. Attack Surface Visibility & Context

An attack surface is a collection of all attacker-exposed assets. It covers all resources in areas like the cloud, third-party environments, or the company’s subsidiaries.

One critical security issue is being unaware of the exact location of an organization’s assets or digital infrastructure. As a result, some companies cannot tell whether these assets are fully protected. It is a phenomenon called a shadow risk. The implication is that unmanaged assets become easy access points for attackers. Therefore, organizations must expose all shadow risks by assessing and mapping their attack surface.

The truth is this; you can’t protect what you don’t see. So it’s time to make your data work harder. One effective way to carry this out is through attack surface analysis and management. As a universally recognized approach, it is the foundational step necessary for guiding resource investments and security programs. Moreover, organizations need to implement a context-aware change management approach. That way, there can be a balance for rapid changes in all infrastructure and supporting infrastructure.

II. Breach and Attack Simulation

A breach and attack simulation is an advanced computer security testing method. You may call it the “hack-yourself” approach. However, security is never static, so you stay on top of the ever-changing trends.

Attack simulations identify vulnerabilities by mimicking cyber actors’ plausible techniques and attack paths. The approach provides a continuous, automated penetration test. It also improves the previous limitations of red and blue team testing.

This technology tracks and resolves vulnerabilities, and also gives regular updates and alerts on imminent risks to your network. It also runs on a 24/7 basis and gives organizations deeper visibility of their defense-readiness level.

III. Cybersecurity Risk Scoring

A cyber risk score focuses on the evaluation of a security posture. It aims to convert these evaluations into a simplified, comprehensive risk score. The concept of security posture helps organizations know the level of asset safety they possess. That way, they know the area to focus on for improvements .

An organization that takes such concrete steps shows they are meeting its cybersecurity obligations. In another sense, it leads to increased revenue generation. The reason is that customers and partners view security as a competitive differentiator. Scoring has therefore become an essential aspect.

IV. Cyber Exposure Management

Cyber exposure management helps organizations identify, predict, and take action against risks. The discipline hinges on risk-based vulnerability management. That way, you continuously assess your system’s security posture and health. Additionally, organizations also get to unify business objectives with security goals.

V. Vulnerability Assessments

A vulnerability assessment involves a review of security weaknesses in a system. It evaluates how susceptible a system is and assigns severity levels. There’s also the aspect of recommending remediation or mitigation.

Some of these vulnerability assessments include:

  • Host Assessment: Host assessments focus on the vulnerability of critical servers to attacks.
  • Database Assessment: These involve the assessment of a database for misconfiguration and vulnerability. It also entails classifying sensitive data on a network.
  • Network Assessment: Network assessments involve the assessment of policies and practices as a way to prevent unauthorized access to resources.
  • Application Scan: These use automated scans to identify security vulnerabilities in web applications and their source code.

Risk-Based Security & Risk Reduction

Organizations need to recognize that breaches are inevitable. However, we also see that attackers have become better at what they do than the defenders. Therefore, there’s an urgent need to modify the current paradigm of cyber security towards risk-reduction through risk-based security models.

Where to Start?

  • Assess the status of critical control systems and operations for security vulnerabilities that need addressing.
  • Revisit security and alarm management standards. This requires significant coordination between all players in the system.
  • Develop cross-collaboration between engineers and network administrators

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

How Does PAM Assist in Hiring Cyber Insurance?

Organizations are increasingly exposed to cyber threats, which justifies hiring insurance to cover losses related to hacker attacks, incidents, and human failures.

Nevertheless, ensuring this additional protection can be a major challenge, as insurers require companies to take useful measures for cybersecurity, making it infeasible to hire insurance or increasing the costs of this process.

An excellent solution for these cases is senhasegura PAM, which can provide more security to your IT structure and, consequently, facilitate negotiation with insurers. Check below how this is possible.

Make it Possible to Hire Cyber Insurance with senhasegura PAM

According to the Verizon Data Breach Investigation Report 2021, 61% of cyberattacks involve privileged credentials. In addition, the abuse of privilege has caused 70% of the attacks. 

Therefore, when hiring cyber insurance, it is important to show your credentials are protected by senhasegura PAM, which has the following features:

1. Audit of Accesses Performed 

The audit of functions performed by human users or machines assures that the actions have been, are, and will be performed properly, according to the organization’s security policy, facilitating the acceptance of insurers.

For this, in addition to ensuring the traceability of the actions taken, the audit allows the organization to manage the use of a privileged credential after access. 

2. senhasegura Domum 

Indiscriminate access by third parties and remote users to IT infrastructure can also be considered by insurers when stipulating the values of (and even when hiring) cyber insurance, as it increases the attack surface exploited by malicious agents.

However, with senhasegura Domum, one can strengthen security aspects exploited by invaders, promoting secure remote access to privileged credentials.

3. Remote Session Recording 

If you wish to hire cyber insurance, we also recommend monitoring privileged session activities, which helps prevent the misuse of privileges, as well as identifying malicious activities and facilitating the incident investigation process, providing the assurance that accounts are not compromised.

4. Multi-Level Approval Workflows 

This senhasegura PAM capability allows one to increase control over privileged account credentials, requiring approvals to grant these accesses.

In practice, approval workflows are configured at various levels, which ensure access review and approval, while an audit trail records who requested this access, who authorized it, and why they are needed for the business.

5. Data Theft Prevention 

Exposure to data theft is another factor that prevents insurers from accepting a company as an insured party. 

However, senhasegura PAM assesses which data needs greater protection, limits access to sensitive information, reinforces internal and external controls for data privacy, and uses strong passwords to protect IT devices, eliminating this objection. 

Contact Us

In this article, you saw how senhasegura PAM can contribute when hiring cyber insurance. If you are interested in this solution, please contact us by clicking here. 

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Segura®
Segura® strive to ensure the sovereignty of companies over actions and privileged information. To this end, we work against data theft through traceability of administrator actions on networks, servers, databases and a multitude of devices. In addition, we pursue compliance with auditing requirements and the most demanding standards, including PCI DSS, Sarbanes-Oxley, ISO 27001 and HIPAA.

Gone Phishing – Basics

Intro

We all know what phishing is and how prevalent it is. This is the attack that accounted for more than 80% in 2021! More details can be found here and here.

With such scary numbers, it is an attack vector that warrants our attention. As we know, the security at our company is only as strong as our weakest link, and unfortunately, this is how threat actors leverage phishing attacks against us.

You can have all controls in the world, but you can still get phished; it is virtually impossible to implement an anti-phishing solution that will cover all the bases. Yes, you can have safe links, and a myriad of other controls, but that user interaction that’s at the core of this attack is how you get exploited and it’s just too difficult to account for. There are many tools out there that will do filtering for you (and whatever else), however these emails still can (and probably will) get through. You need to know what to do when that (inevitably) happens.

This all goes to say how important our education and cyber awareness in the organization are since we can be sure that we will eventually get targeted by one of these attacks.

My goal in this series is to look at and explain how a phishing attack works and how to analyse a phishing email. I will only explain some of the most important things briefly in this article. In the upcoming article, I will dive into the technical aspects of the attack.


Some Historical Context

Phishing and Spam are extremely common social engineering attacks, and not that new at all. First spam message dates all the way back to 1978 – you can read more about that here.

In the 4+ decades this attack has existed, threat actors have found creative ways to perfect it, and we’re all witnessing the results of that effort. As mentioned above, phishing is how 80% of breaches had started in 2021. We can’t know with certainty, but don’t expect this attack to fall out of favor. It is just too convenient for the attacker to at least try and phish the unsuspecting employee.

After obtaining those credentials, they’re off to the races.

Types of Phishing Attacks

Below are listed some of the phishing attack variants:

  • Phishing – Emails sent to the target, appearing to be from a legitimate source with the goal to obtain sensitive information
  • Vishing – Attack that’s based on calling the target on their mobile phone. Same logic and goal as for the regular phishing email
  • Smishing – Same as vishing, with the difference being the attacker is now sending specifically crafted SMS messages to their targets
  • Spear phishing – As phishing, but targeted at a specific individual or organization
  • Whaling – As spear phishing but targeted at C-level executives. Also known as CEO Fraud
  • Spam – Sending of unsolicited emails in bulk to a large group of people

The MO here is almost the same for every variant, even though they might leverage different methods.


Typical Phishing Email

A typical phishing email will have some (or all) of these characteristics:

  • Urgency – Almost invariably, the email will be urgent in one way or the other; be it your ‘reward’ that you just got (you claiming it would be on a timer/urgent), or be it something you need to pay to avoid penalty. It will call you to action, hoping you would react immediately
  • Bad grammar/spelling – This one is quite common and is oftentimes a really good indicator. Most of the phishing attacks will have small grammar/spelling errors within the email. Read through everything carefully. Of course, if an email is written perfectly, it can still be a phishing email
  • Mismatched domains – Email is claiming to be from one company (domain) but it is actually sent from gmail.com or another domain. Misspelling is also sometimes use to hide the illegitimate domain by tricking you into thinking the domain’s good. Example: rnicrosoft.com, google.cm, g0ogle.com, etc. also known as Typosquatting – more on that here
  • Suscpicious links/attachements – Unsolicited attachements are sent to you in an email, probably also prompting you to act on them.
  • The sender email address will act and try to appear as a trusted entity – email spoofing
  • The body of the email uses generic addressing such as Dear Sir/Madam, etc.
  • Hyperlinks – oftentimes shortened with URL shortening services so it can hide its true purpose; don’t click on these! Hover over them to see the destination
  • The body of the email is crafted in such a way that it matches a trusted entity (Google, Microsoft, for example)

This is very important to note. There are some good examples out there that illustrate the above nicely, while giving you a practical on the topic. Most companies will use similar stuff when training their employees (most likely with an internal mock phishing test). To see how you fare, you can try the quiz here.

Of course, even if we’re mindful of the above, human error can occur, so you should always pay extra attention when an unknown email pops in your inbox.

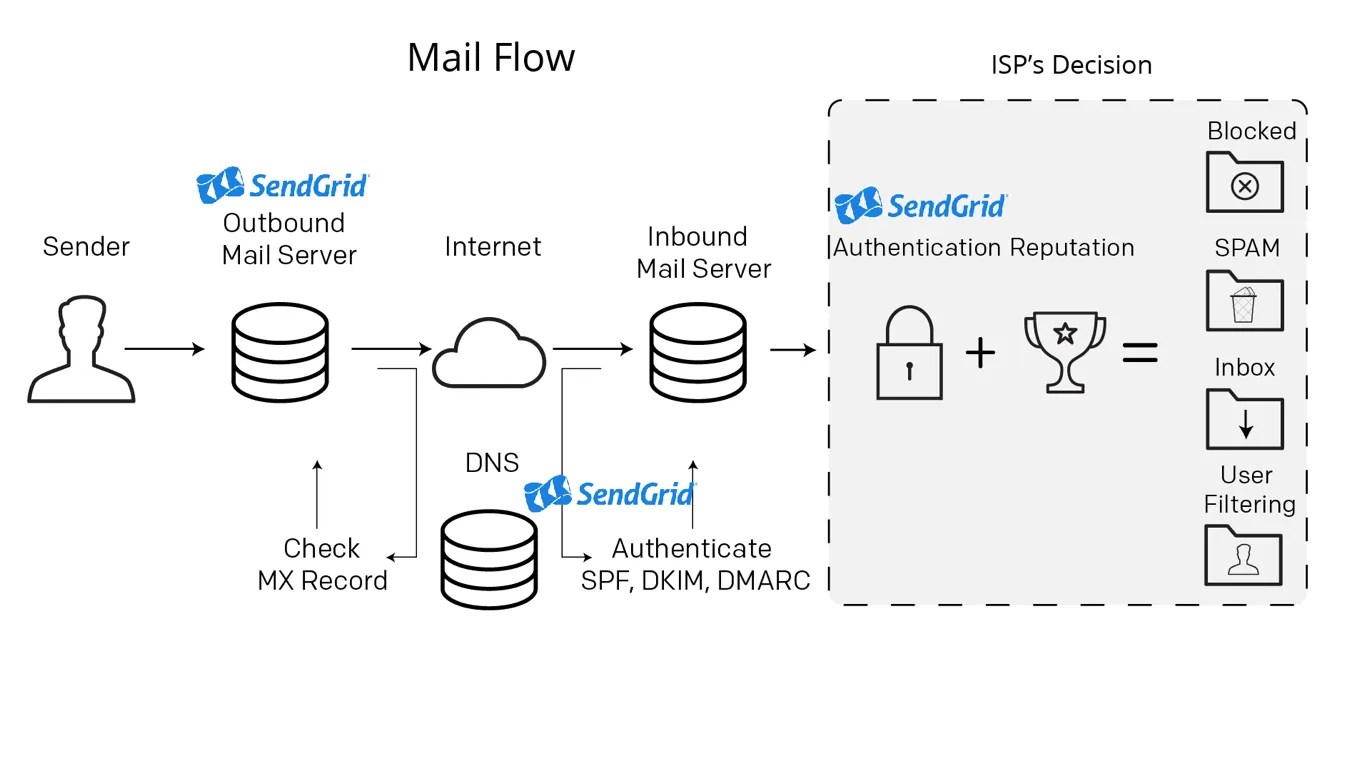
How does an Email Travel

Upon hitting SEND in your favorite email client app, there’s a lot of stuff that happens behind the curtains for your email to arrive at its destination. Three protocols are involved in this: POP3, IMAP, and SMTP.

POP3 – Post Office Protocol – receiving emails, downloading from the server

SMTP – Simple Mail Transfer Protocol – handles the sending of the emails

IMTP – Internet Message Access Protocol – stores messages on the server and syncs them across multiple devices

Slightly longer explanation can be found in this article:

IMAP:

Emails are stored on the server (meaning they can also be downloaded on multiple devices)

Sent emails are stored on the server

Messages can be synced and accessed from multiple devices

POP3:

Emails are downloaded (and stored) on a single device

Sent emails are stored on a single device, from which the email was sent

To keep messages on the server you need to enable “Keep email on server” option, because all the emails would be deleted from the server, once downloaded to the single device

Emails can only be accessed from a single device (where they were downloaded to)

SMTP:

By using SMTP, you’re sending, relaying, or forwarding messages from an email client (thinks MS Outlook) to a receiving email server

Explained here.

Lastly, to summarize, an email travelling would look something like this:

  • You hit send within your email client after composing the message, sending it to someone@example.com
  • The SMTP queries the DNS for records about example.com
  • The DNS server fetches information about example.com and sends it to the SMTP server
  • The SMTP server sends the email to someone’s mailbox at example.com
  • The email goes through many SMTP servers before being relayed to the destination SMTP server
  • Upon reaching the destination SMTP server your email is forwarded and waits in the local POP3/IMAP server waiting on someone
  • Someone logs in to their email clients
  • Their email client queries the local POP3/IMAP server for new emails
  • Your email is copied (IMAP) or downloaded (POP3) to someone’s email client

This is nicely explained here, where you can also find the diagram shown below.

Here you can read more about these three protocols.

Default (un)encrypted ports for these protocols are:

POP3 – (110)995

IMAP – (143)993

SMTP – (25)587/465

Conclusion

Okay, so I talked a bit about phishing, how scary (real) it is, how an email travels, and I mentioned the variants of phishing attacks.

Before concluding, I’d like to emphasize again how important it is to understand/have some plan prepared against phishing as it is the best way attackers gain access, which in turn leads to some real ugly stuff. Prime example is ransomware, which is the most common way in which a ‘simple’ phishing attack evolves. (You can read more about it here, here, and here)

Finally, to let you go on a very dark note, please remember that phishing kits can be bought online quite easily, and that launching a phishing campaign can be done by someone less technical while the true danger remains; what comes after the attack i.e., what was it used for.  They might be less effective, true, but it is scary to think that it can be done in that way with so little effort – in comparison to the impact the attack can have.

Stay tuned for the next piece where I’ll be talking about header and body analysis, and more!

Cover by Mohamed Hassan

#phishing #smtp #pop3 #imap #vicarius_blog

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About VRX
VRX is a consolidated vulnerability management platform that protects assets in real time. Its rich, integrated features efficiently pinpoint and remediate the largest risks to your cyber infrastructure. Resolve the most pressing threats with efficient automation features and precise contextual analysis.